One solution, complete coverage for hybrid networks

Detect, investigate, and contain threats across network, cloud, OT, endpoint, and identity with a single solution that learns your environment from the ground up.
See Darktrace in action

Small gradient quadrant
2025 Gartner ®
Voice of Customer

Voice of the Customer for Network Detection and Response

Hybrid Network in action

What’s hiding across your hybrid network?
Discover how security teams use Darktrace to uncover hidden threats across network, cloud, OT, and identity — and stop attacks before they spread.

Stay protected, even when your team can't be there.

As a practitioner, you have to get it right all the time—but threat actors only have to get it right once. We needed a tool that could act even when we weren’t at the helm.”

Jon Mendoza, CISO, Technologent

See how Technologent did it

Give your security team time back.

99% of threats autonomously investigated, reducing analyst workload."

Vulcan Steel Limited

See how Vulcan Steel Limited did it

10,000

Customers trust Darktrace
The hybrid network security challenge

Modern attackers exploit the gaps between environments

40%

of ransomware attacks now involve a hybrid componentof phishing emails are spear-phishing, tailored to individual recipients

(Microsoft Digital Defense Report 2025)

44%

year-on-year increase in the exploitation of public facing software or system applications
‍
(IBM X-Force Threat Intelligence Index 2026)

21%

year-on-year increase in public CVE volumesof malware breaches are email-driven


(Open Source Security Foundation)
Cross-domain threats

Infrastructure now spans networks, cloud, operational technology, endpoints, and identities. Every new connection between them is another route for attackers to get in, move laterally, and stay hidden.

AI-accelerated attacks

AI lets attackers move quicker, automate more of the attack lifecycle, and adjust tactics across complex environments. Risk spreads fast and quietly across distributed infrastructure, often with little visibility or context.

Prioritization overload

Vulnerabilities keep piling up while attackers exploit them faster. The task is no longer to find every risk but to know which exposures are present, reachable, and most likely to be exploited.

The Darktrace solution

A unified approach to securing hybrid infrastructure

Connected visibility across
every domain

See your entire hybrid estate — network, cloud, OT, endpoints, and identities — through one continuously learned understanding of how your environment actually operates, not a patchwork of disconnected tools.

Detect and contain threats before they escalate

Identify what's genuinely unusual for your organization, from known attacks to novel and AI-accelerated threats, and stop them automatically before they spread across your hybrid network.

Our unique approach is proven to detect zero-day threats on average 8 days before public CVE disclosure.
Scale investigations without scaling headcount

Reduce analyst workload with AI-driven investigations that automatically connect related events and prioritize what matters, helping you build a complete picture of activity across your infrastructure.

Move from reactive defense to proactive resilience

Use behavioral and risk context from your unique environment to proactively reveal attack paths, prioritize remediation efforts on exploitable risks, and enrich investigations with deeper context.

The Darktrace solution

Key capabilities

Capabilities

Contain network threats without disrupting the business

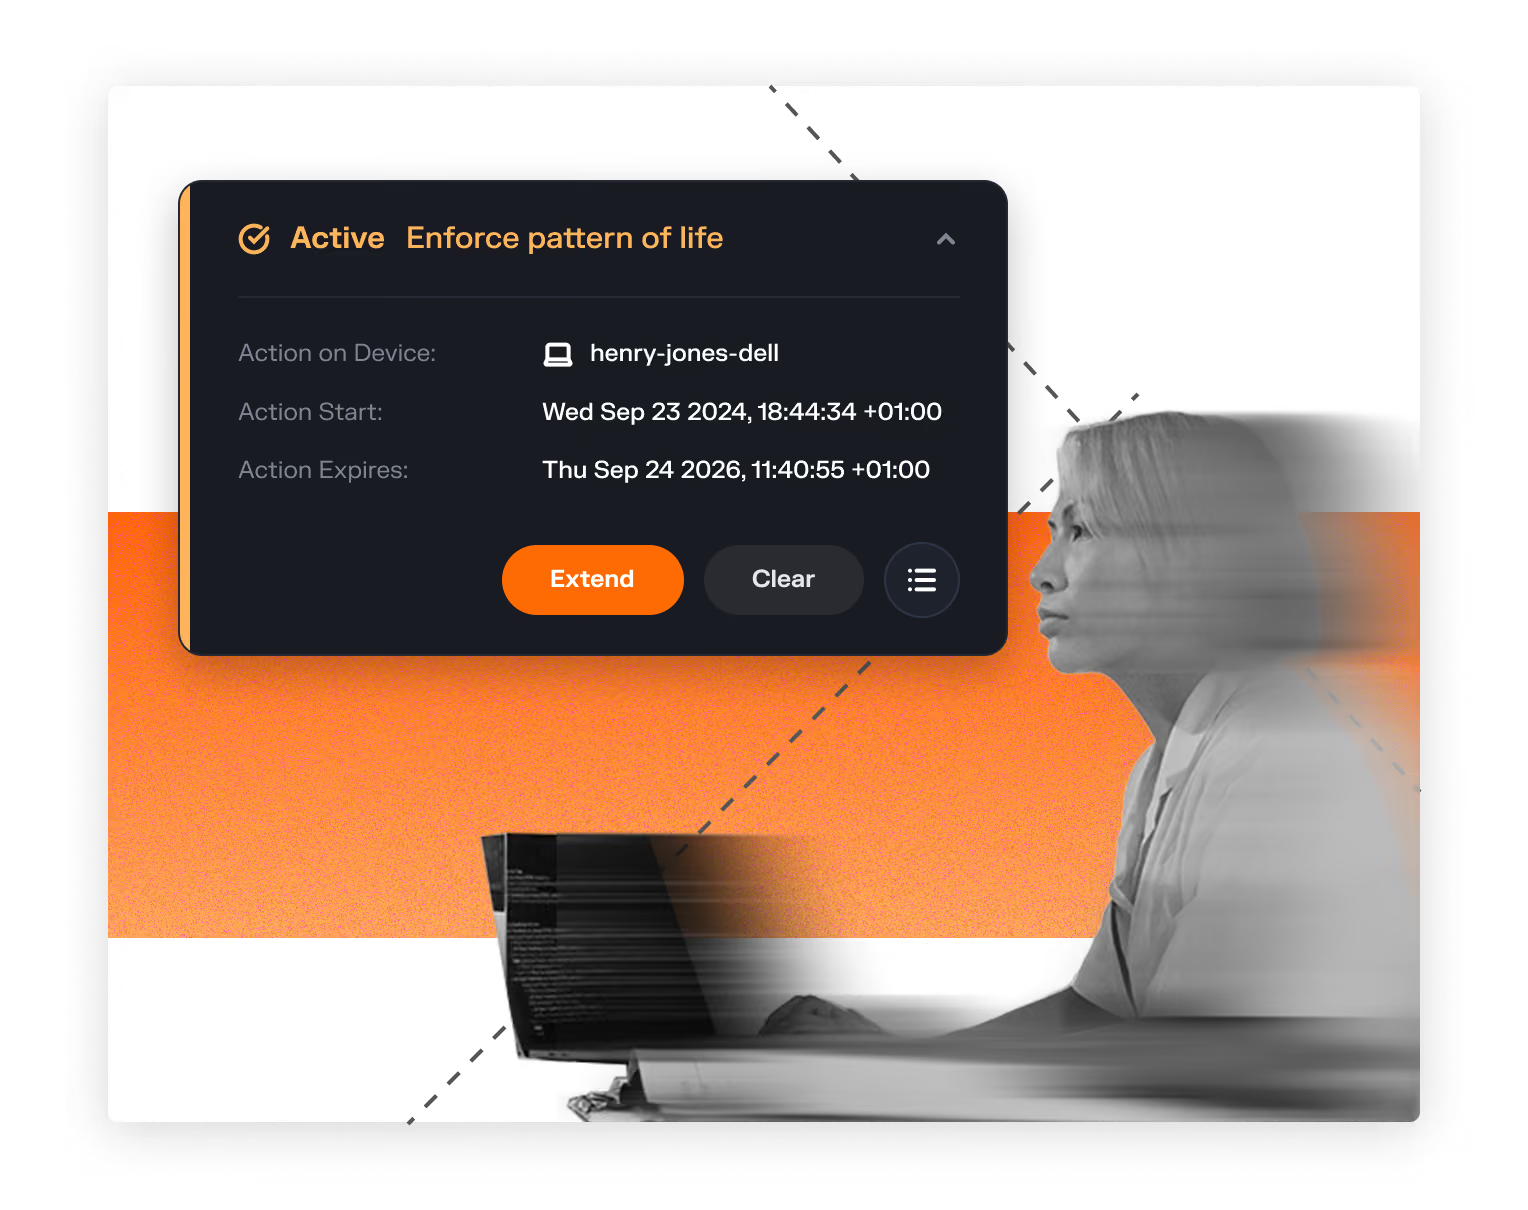
Traffic across network, cloud, and OT, encrypted or not, is analyzed to expose activity that does not belong in your environment. Darktrace can then contain it directly or through your firewalls, EDR, SOAR, and ITSM tools. Policies you configure decide how and when it intervenes, so normal work carries on while threats are shut down.

Capabilities

Extend behavioral understanding to every identity

Account activity is judged against the same behavioral profile as your network and infrastructure, so account takeover, privilege escalation, and insider misuse are flagged as soon as an identity stops behaving normally, even with valid credentials.

Capabilities

Automated evidence capture at the point of detection

The moment a threat is detected, Darktrace collects host and workload artifacts from endpoints, cloud, containers, and SaaS. Analysts can establish scope and impact within minutes, with no manual log requests and no dependence on other teams.

Capabilities

Separate real risk from theoretical risk

Go beyond vulnerability lists. Darktrace tests each exposure against your environment (is it present, reachable, linked to a critical asset, and likely to be exploited) and maps how exposures could chain together, so remediation targets genuine routes to compromise rather than a raw CVE list.

What's hiding across your hybrid network?

Detect, investigate, and contain threats across network, cloud, OT, endpoint, and identity with a single solution that learns your environment from the ground up.

See Darktrace in action

Small gradient quadrant
2025 Gartner ®
Voice of Customer

Voice of the Customer for Network Detection and Response

10,000

Customers trust Darktrace

The hybrid network security challenge

Modern attackers exploit the gaps between environments

40%

of ransomware attacks now involve a hybrid componentof phishing emails are spear-phishing, tailored to individual recipients

(Microsoft Digital Defense Report 2025)

44%

year-on-year increase in the exploitation of public facing software or system applications
‍
(IBM X-Force Threat Intelligence Index 2026)

21%

year-on-year increase in public CVE volumesof malware breaches are email-driven


(Open Source Security Foundation)

The Darktrace solution

A unified approach to securing hybrid infrastructure

Connected visibility across
every domain

See your entire hybrid estate — network, cloud, OT, endpoints, and identities — through one continuously learned understanding of how your environment actually operates, not a patchwork of disconnected tools.

Detect and contain threats before they escalate

Identify what's genuinely unusual for your organization, from known attacks to novel and AI-accelerated threats, and stop them automatically before they spread across your hybrid network.

Our unique approach is proven to detect zero-day threats on average 8 days before public CVE disclosure.
Scale investigations without scaling headcount

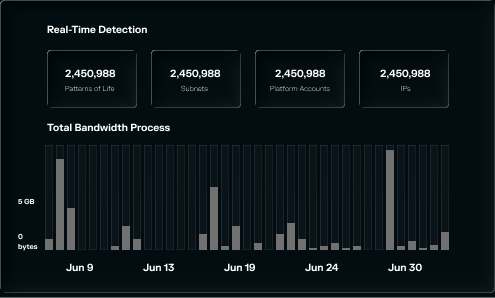
Reduce analyst workload with AI-driven investigations that automatically connect related events and prioritize what matters, helping you build a complete picture of activity across your infrastructure.
Move from reactive defense to proactive resilience

Use behavioral and risk context from your unique environment to proactively reveal attack paths, prioritize remediation efforts on exploitable risks, and enrich investigations with deeper context.

Hybrid Network in action

What’s hiding across your hybrid network?

Discover how security teams use Darktrace to uncover hidden threats across network, cloud, OT, and identity — and stop attacks before they spread.

Stay protected, even when your team can't be there.

As a practitioner, you have to get it right all the time—but threat actors only have to get it right once. We needed a tool that could act even when we weren’t at the helm.”

Jon Mendoza, CISO, Technologent

See how Technologent did it

Give your security team time back.

99% of threats autonomously investigated, reducing analyst workload."

Vulcan Steel Limited

See how Vulcan Steel Limited did it
Cross-domain threats

Infrastructure now spans networks, cloud, operational technology, endpoints, and identities. Every new connection between them is another route for attackers to get in, move laterally, and stay hidden.

AI-accelerated attacks

AI lets attackers move quicker, automate more of the attack lifecycle, and adjust tactics across complex environments. Risk spreads fast and quietly across distributed infrastructure, often with little visibility or context.

Prioritization overload

Vulnerabilities keep piling up while attackers exploit them faster. The task is no longer to find every risk but to know which exposures are present, reachable, and most likely to be exploited.

The Darktrace solution

Key capabilities

Capabilities

Contain network threats without disrupting the business
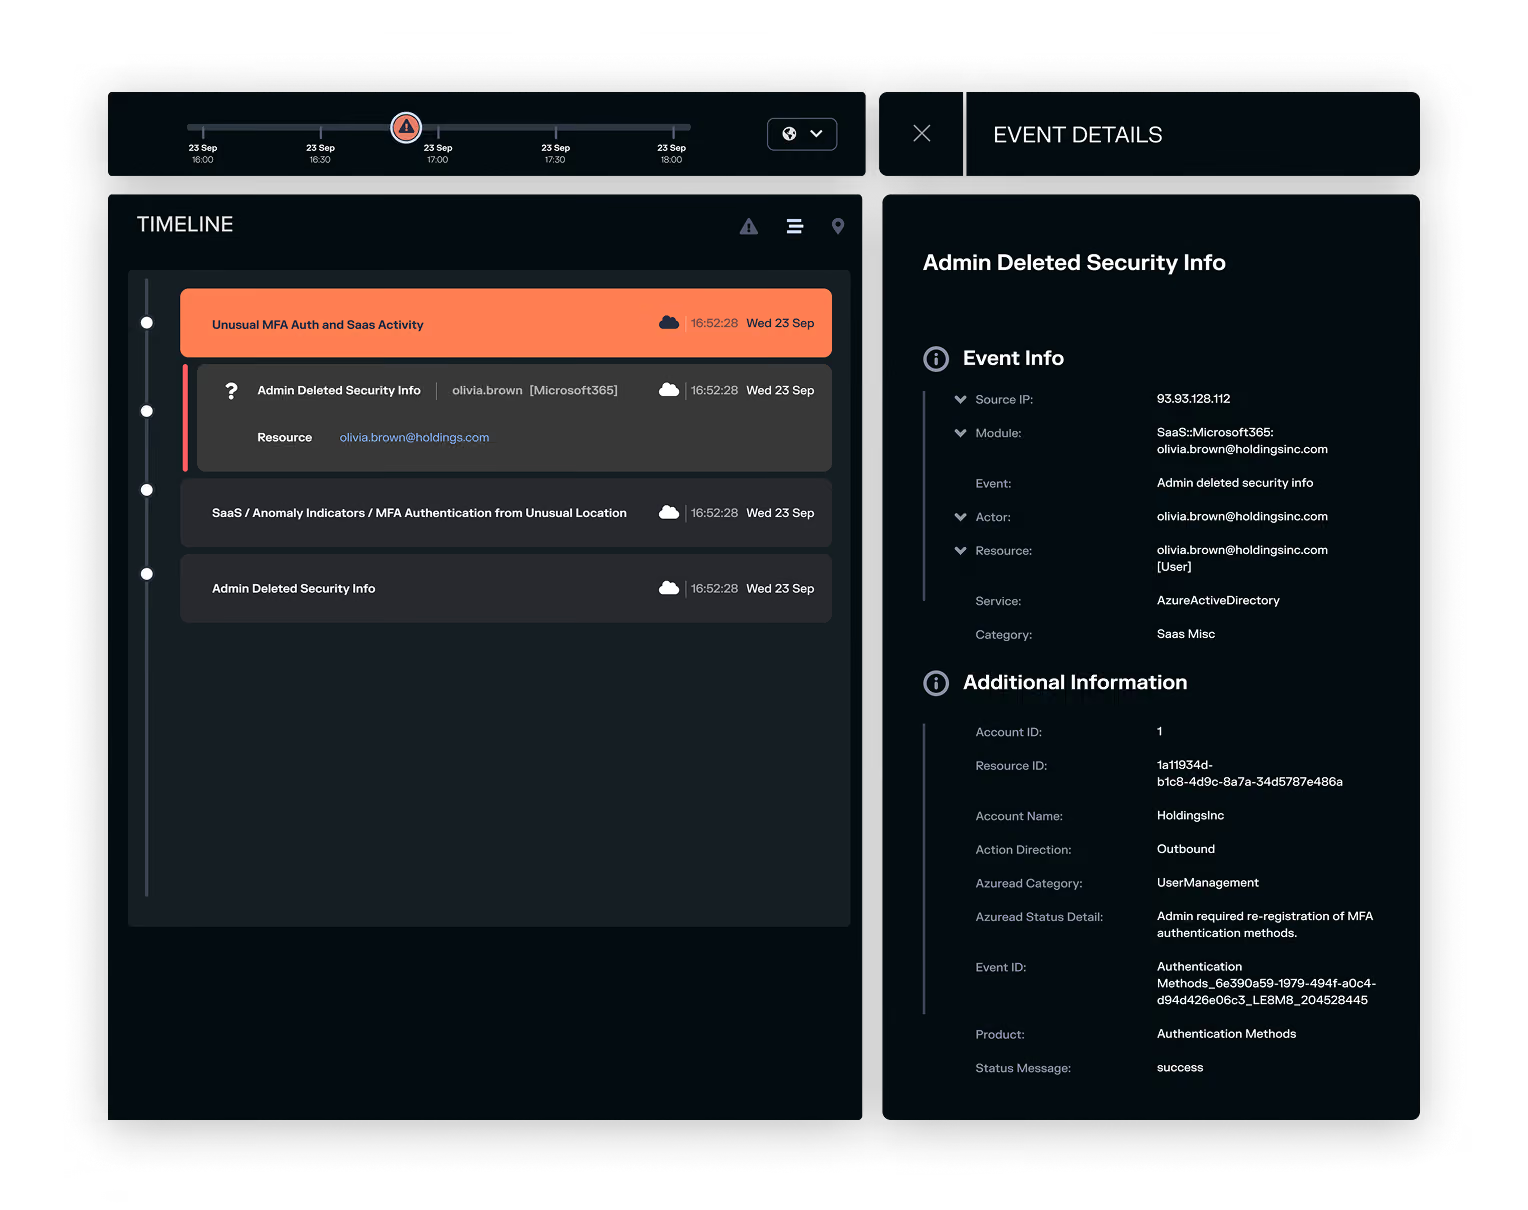
Traffic across network, cloud, and OT, encrypted or not, is analyzed to expose activity that does not belong in your environment. Darktrace can then contain it directly or through your firewalls, EDR, SOAR, and ITSM tools. Policies you configure decide how and when it intervenes, so normal work carries on while threats are shut down.

Capabilities

Extend behavioral understanding to every identity
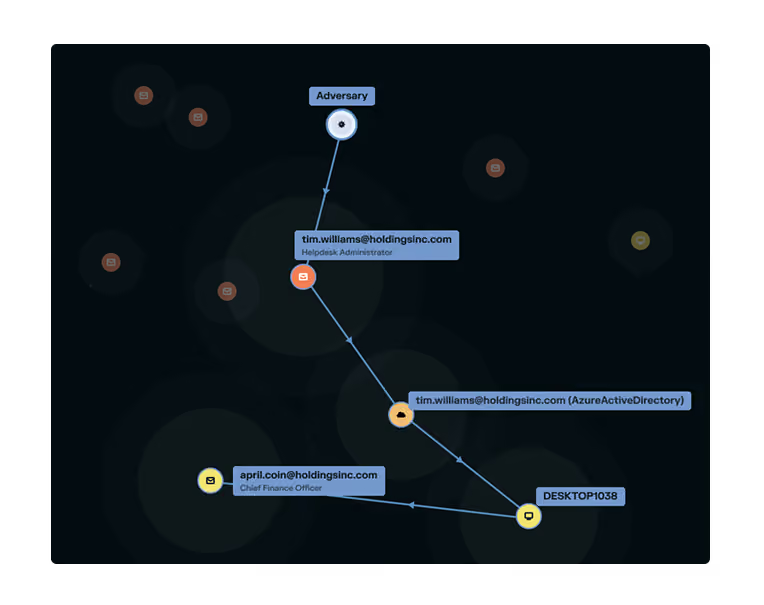
Account activity is judged against the same behavioral profile as your network and infrastructure, so account takeover, privilege escalation, and insider misuse are flagged as soon as an identity stops behaving normally, even with valid credentials.

Capabilities

Automated evidence capture at the point of detection
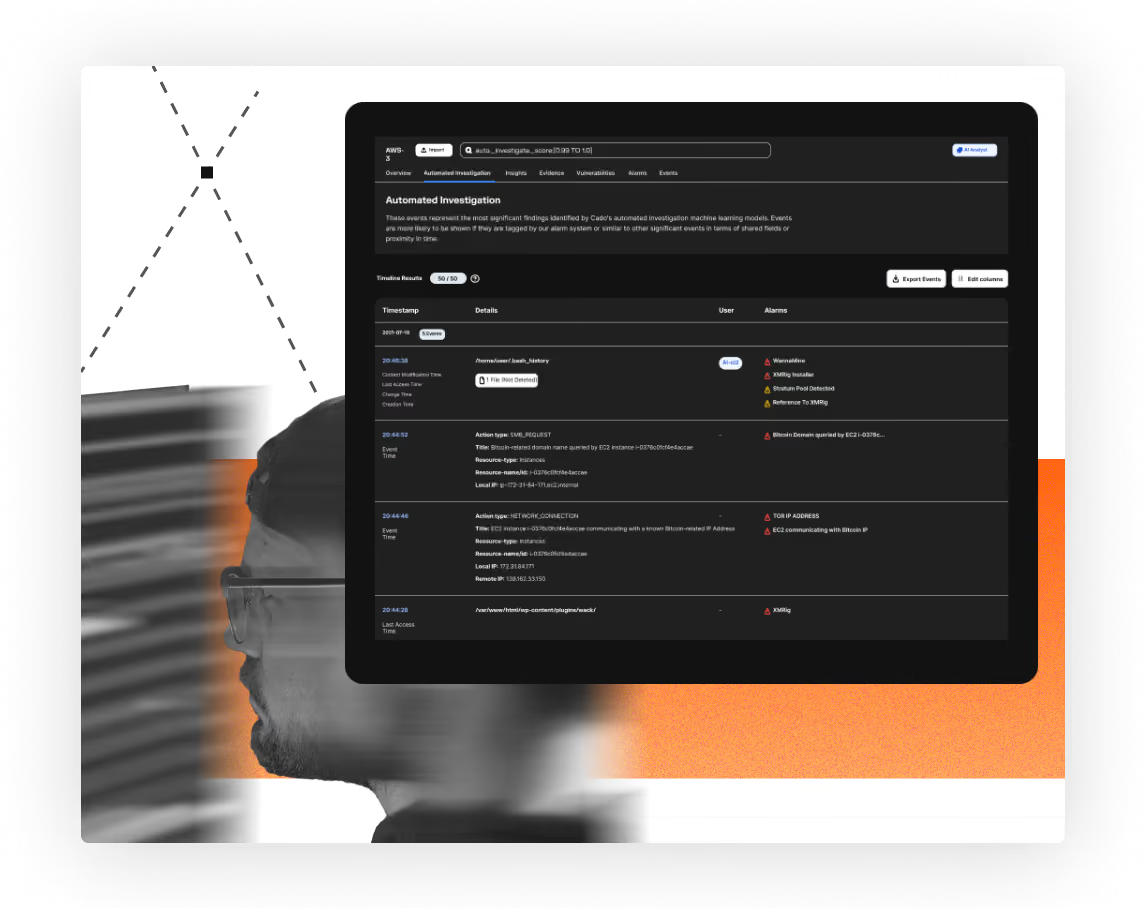
The moment a threat is detected, Darktrace collects host and workload artifacts from endpoints, cloud, containers, and SaaS. Analysts can establish scope and impact within minutes, with no manual log requests and no dependence on other teams.

Capabilities

Separate real risk from theoretical risk
Go beyond vulnerability lists. Darktrace tests each exposure against your environment (is it present, reachable, linked to a critical asset, and likely to be exploited) and maps how exposures could chain together, so remediation targets genuine routes to compromise rather than a raw CVE list.