Real-time inspection of prompts and sessions separates business-aligned activity from jailbreaks, injection attempts, and malicious chaining.
Get a technical overview of Darktrace / SECURE AI
See exactly how Darktrace / SECURE AI's four core capabilities – AI Prompt Analysis, Agent Identities and Actions, Agent Development Risk Management, and Shadow AI Management – catch drift, misuse, and policy violations that static rules can't.

Darktrace Customers





Real-time inspection of prompts and sessions separates business-aligned activity from jailbreaks, injection attempts, and malicious chaining.
Identity-centric oversight maps every agent's permissions and tool access, turning an open-ended investigation into a bounded one.
Catching an over-permissioned agent during build costs a configuration change. Catching it in production avoids a full incident response.
Traditional security was built for deterministic systems, where a control can be written in advance for a condition someone anticipated. AI doesn't work that way. It operates in natural language, can take multiple paths to the same outcome, and increasingly acts on its own — there's no artifact to catalogue in a prompt, no CVE for an agent persuaded to exceed its purpose, and no fixed set of guardrails that accounts for every adversarial interaction. Policies and controls still define what AI systems should do, but they can't tell you whether a sequence of seemingly legitimate actions is actually a jailbreak, a prompt injection, or an agent quietly drifting beyond its intended purpose.
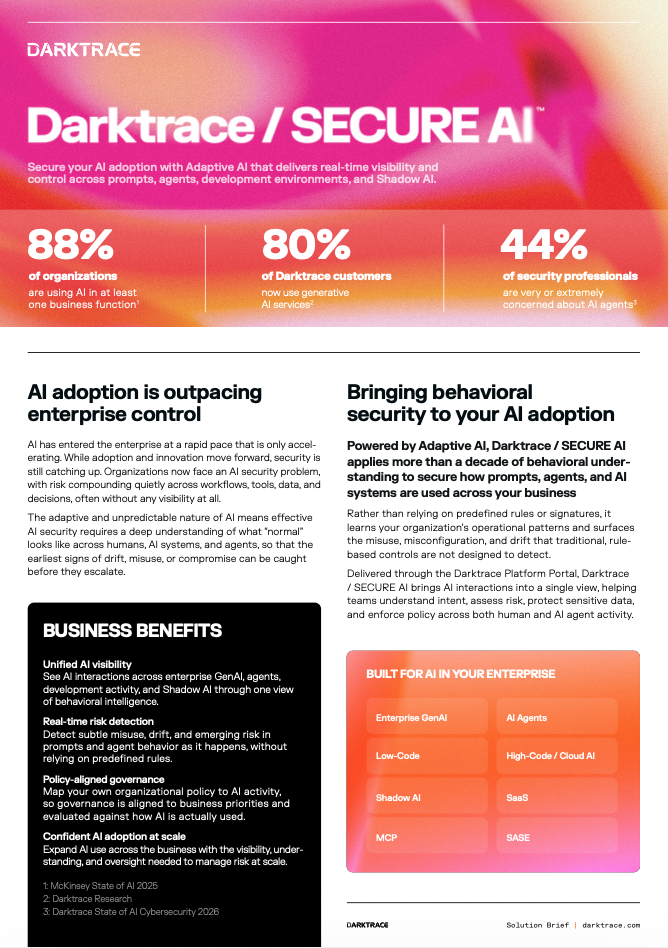
This guide breaks down exactly how Darktrace / SECURE AI closes that gap. Powered by Adaptive AI, it brings together four core capabilities — AI Prompt Analysis, AI Agent Identities and Actions, AI Agent Development Risk Management, and Shadow AI Management — each covering a distinct area of AI risk, while Policy Manager provides a consistent governance layer by connecting your organization's own policy with real-world AI activity. Rather than manually translating governance documents into technical controls, Policy Manager automatically interprets uploaded policy into rules, continuously evaluates activity against them, and links every flagged session back to the relevant rule for audit-ready investigation.
Feature by feature, this data sheet shows how prompt visibility, categorization, and session risk scoring separate business-aligned AI use from jailbreaks and injection attempts; how identity audits and workflow visualization expose exactly what an agent can reach before it becomes an incident; how build-time visibility into low-code and high-code environments catches misconfiguration while it's still a configuration change, not a breach; and how Shadow AI detection — including signals like locally deployed MCP servers — turns an invisible blind spot into a prioritized list of services to control. You'll also find the full list of supported integrations (Microsoft Copilot, AWS Bedrock, Zscaler, and more), delivery model, and technical requirements, including the typical 7–10 day learning period and 12-week prompt data retention.

Deine Daten. Unsere KI.
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.