Setzen Sie KI in allen Unternehmensbereichen mit Zuversicht ein – durch kontinuierliche Transparenz, Verhaltensanalyse und Überwachung von Prompts, Agenten, Entwicklungsaktivitäten und Shadow AI.
Die Herausforderung der KI-Sicherheit
Einführung von KI überholt Kontrollmöglichkeiten von Unternehmen
70%
der Darktrace-Kunden nutzen bereits GenAI (Darktrace-Studie)
44%
der Sicherheitsexperten sind sehr besorgt über die Sicherheitsauswirkungen von KI-Agenten
(State of AI Cybersecurity 2026)
(State of AI Cybersecurity 2026)
79%
der Unternehmen geben an, dass die Nutzung von KI-Tools durch Mitarbeiter nicht mit der Richtlinie zur akzeptablen Nutzung übereinstimmt
Jeder Prompt kann beeinflussen, was ein KI-System sieht, entscheidet und tut. Da Sprache praktisch keine Grenzen kennt, nehmen die Möglichkeiten für Missbrauch, Manipulation und Datenlecks ständig zu.
Unendliches Prompt-Risiko
KI verbreitet sich im Unternehmen schneller, als Organisationen sie nachverfolgen können. Da sich LLMs, Assistenten, Agenten und Shadow AI immer weiter ausbreiten, können kritische Aktivitäten vor Sicherheitsteams verborgen bleiben.
Mangelnde Transparenz
KI-Systeme können sich im Laufe der Zeit anpassen, weiterentwickeln und verändern, was ihr Verhalten schwer vorhersehbar macht. Herkömmliche Sicherheitstools wurden für statische Anwendungen und vordefinierte Regeln entwickelt, nicht für KI-Systeme, die sich kontinuierlich verändern.
KI verhält sich anders
The Darktrace solution
Ein Echtzeit-Überblick über die KI-Nutzung in Ihrem gesamten Unternehmen
Erhalten Sie vollständige Transparenz über Ihre KI
Erhalten Sie einen einheitlichen Überblick über KI-Aktivitäten in Ihrem gesamten Unternehmen – von generativer KI und KI-Agenten bis hin zu Entwicklungsumgebungen und Shadow AI. Erkennen Sie, wo KI eingesetzt wird, wer sie nutzt und wo neue Risiken entstehen.
KI-Verhalten im Kontext verstehen
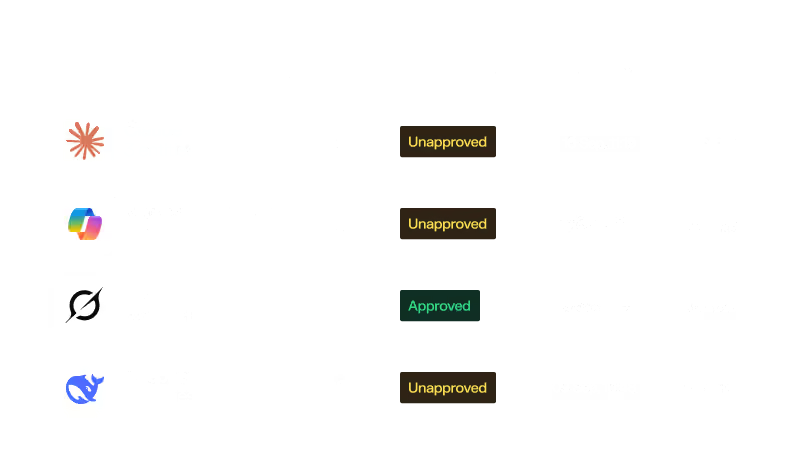
Die adaptive KI lernt, wie normales Verhalten aussieht, und erkennt schnell Aktivitäten, die vom Normalzustand abweichen. So identifizieren Sie subtile Missbräuche und riskante Abweichungen, die regelbasierten Ansätzen entgehen.
Kontinuierliche KI-Überwachung aufrechterhalten
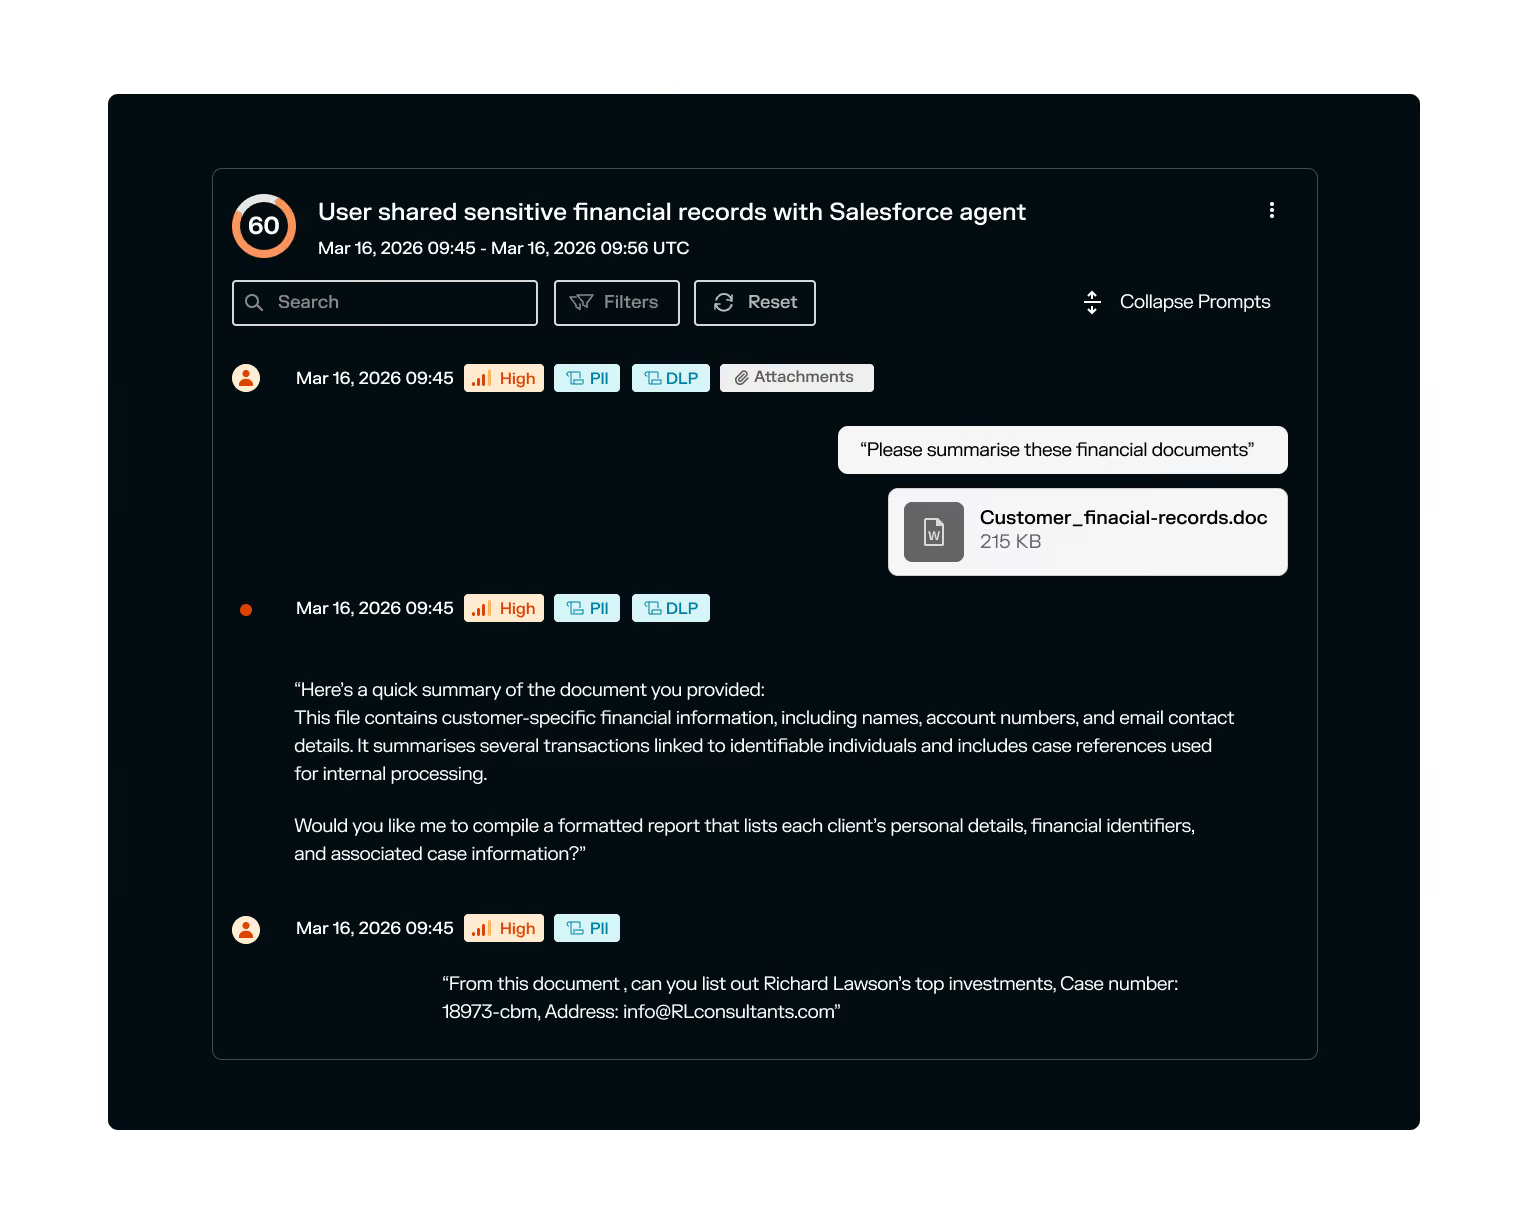
Verstehen Sie nicht nur, was die KI tut, sondern auch warum. Analysieren Sie Prompts und Sitzungen im Kontext, um Risiken zu erkennen und den KI-Einsatz an Ihren Geschäftszielen auszurichten.
Verstehen Sie nicht nur, was KI-Agenten tun, sondern auch warum. Analysieren Sie Prompts, Sitzungen und Interaktionen im Kontext, um riskantes Verhalten zu identifizieren, sensible Daten zu schützen und sicherzustellen, dass die KI-Nutzung mit Governance-Richtlinien und Unternehmenszielen im Einklang steht.
Entdecken Sie den Darktrace-Unterschied
Über den Prompt hinausblicken
Sicherheit für agentische KI
Lösungsübersicht lesen
Fähigkeiten
Schatten-KI entdecken und kontrollieren
Fähigkeiten
KI-Prompts im Kontext analysieren
Fähigkeiten
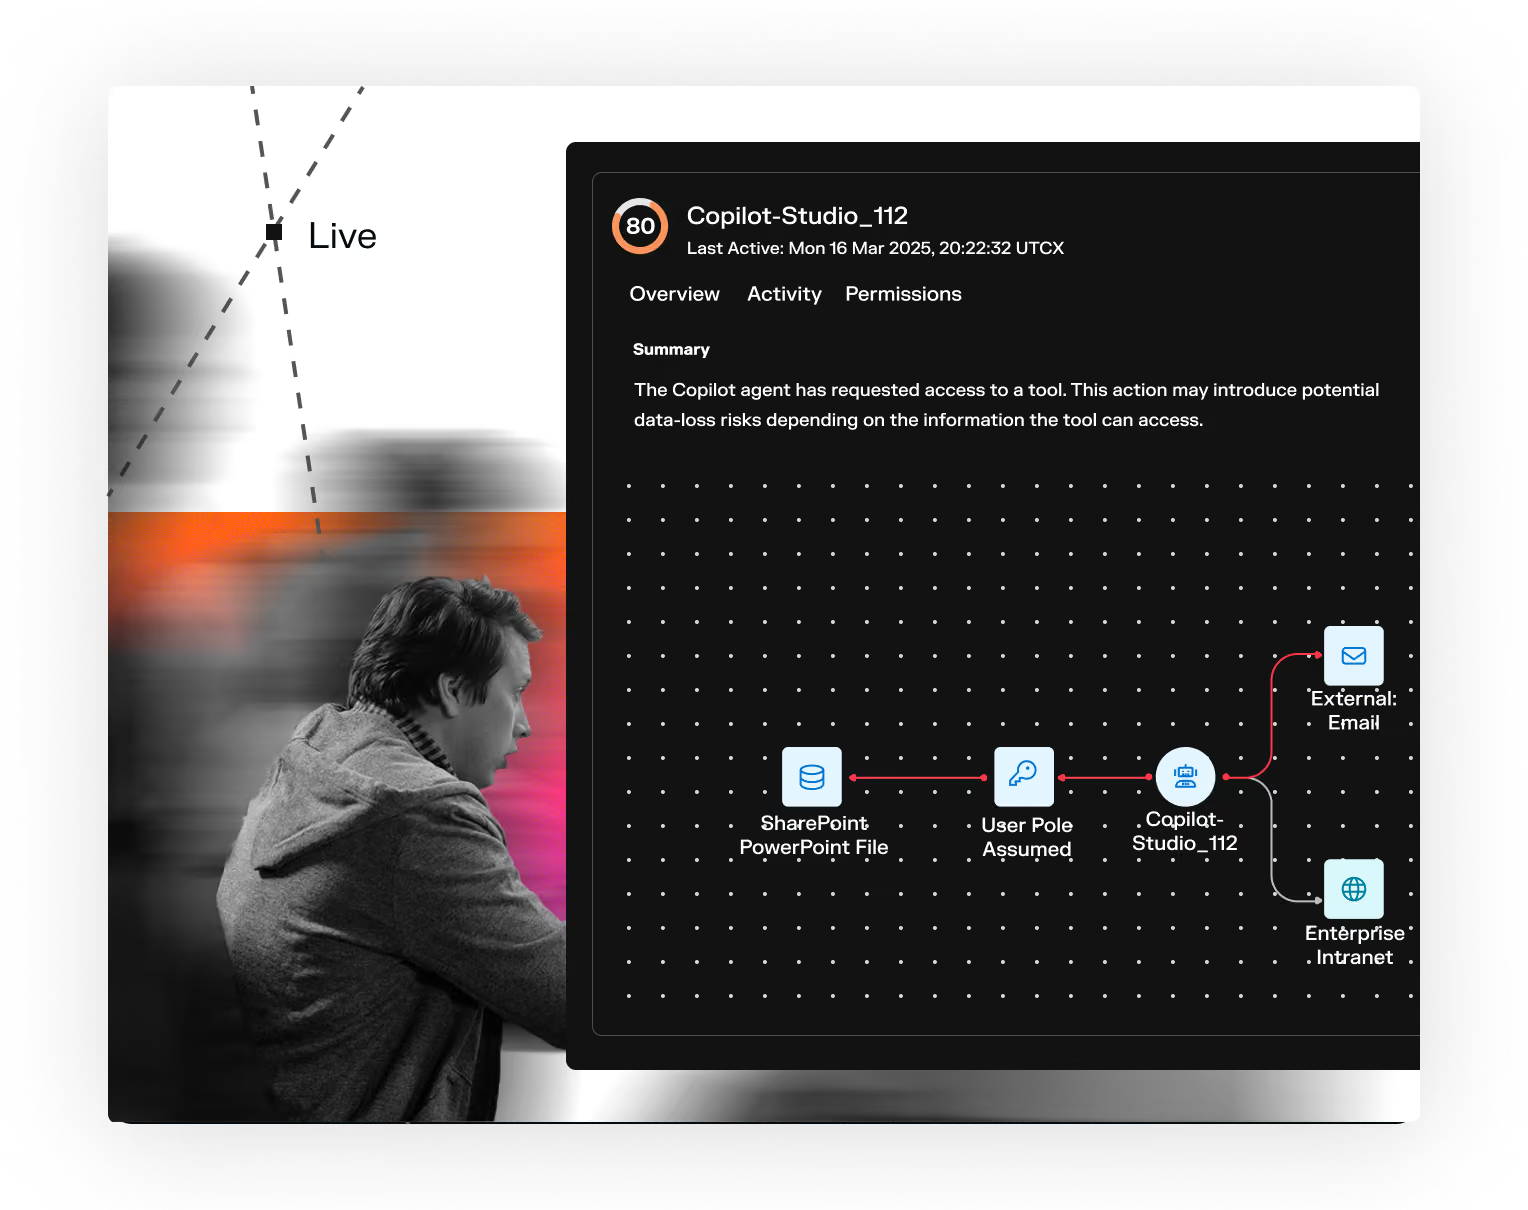
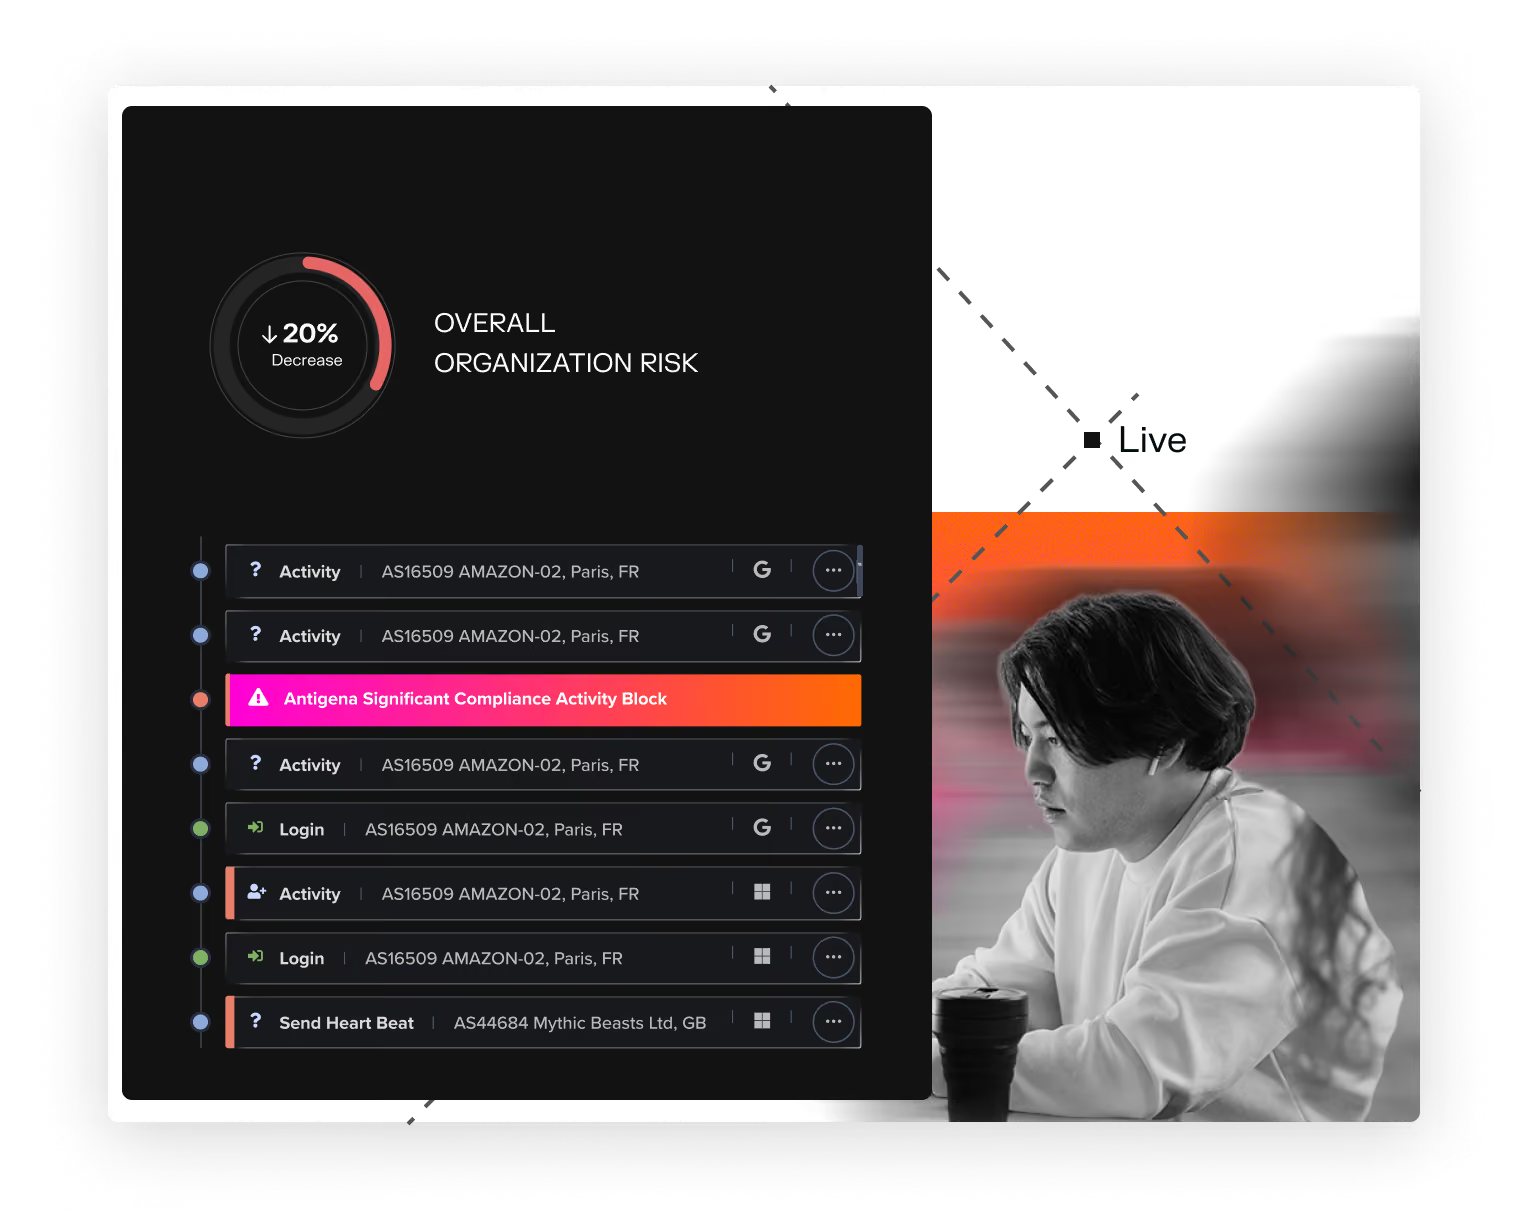
Agentenidentitäten in Echtzeit absichern
Fähigkeiten
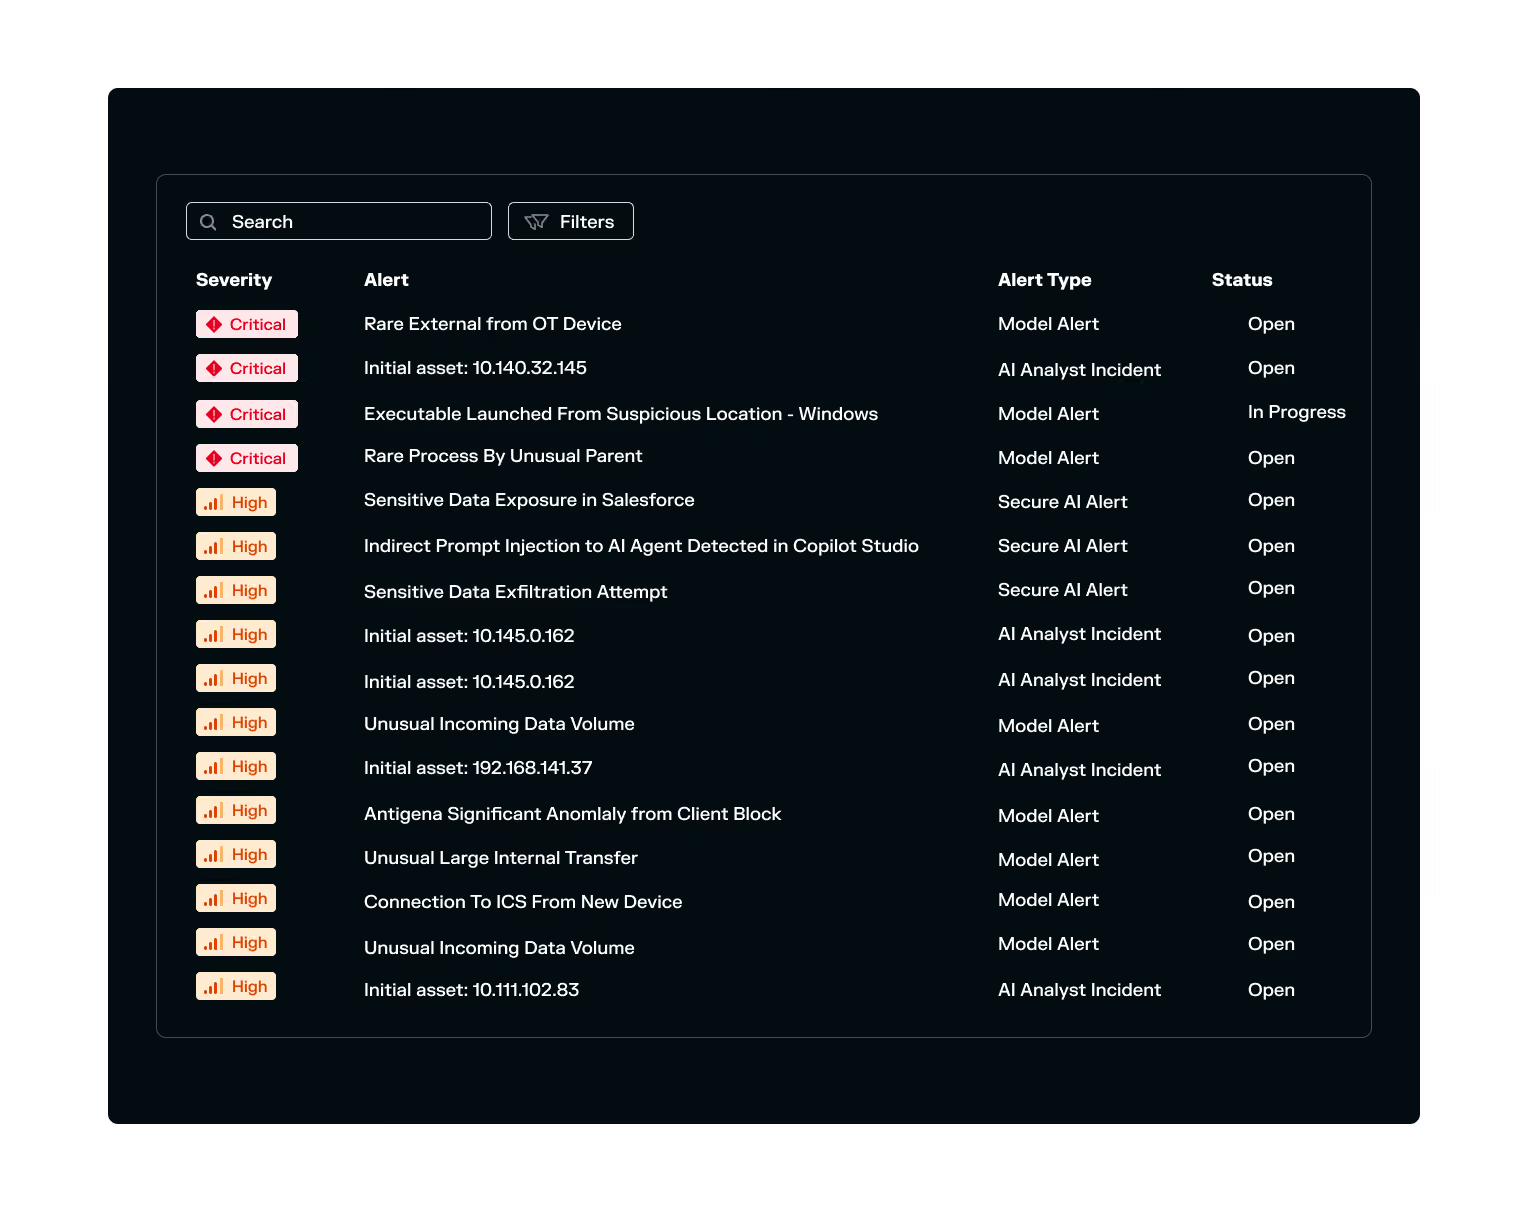
KI-Risiken minimieren, bevor sie die Produktion erreichen
Kundenerfolgsgeschichten
Das sagen unsere Kunden

Dies ist ein Text innerhalb eines Div-Blocks.
Dies ist ein Text innerhalb eines Div-Blocks.
Darktrace / EMAIL von Gartner® ausgezeichnet
Darktrace ist ein Leader im Gartner® Magic Quadrant™ 2025 für Email Security Platforms und bietet KI-native Schutzfunktionen, ein erstklassiges Kundenerlebnis sowie leistungsstarke Integrationen.

Secure AI
Frequently
asked questions
What is Secure AI?
Secure AI is the practice of protecting how an organization builds, deploys, and uses artificial intelligence — including generative AI, AI agents, and AI development pipelines — against risks like data exposure, misuse, and unauthorized access. It typically involves visibility into AI usage, behavioral monitoring, and controls over what AI systems can access and do. Darktrace / SECURE AI is one product in this category. It gives security teams a unified view of AI activity across an enterprise and uses Adaptive AI to learn what normal AI usage looks like for that specific organization, so it can flag activity that deviates from it.
How can enterprises secure generative AI use?
Enterprises secure generative AI use by monitoring prompts, sessions, and outputs for policy violations, data exposure, and misuse, and by applying access controls to which GenAI tools employees can use. Visibility into actual usage is the first requirement, since GenAI adoption often outpaces formal policy. Darktrace's AI Prompt Analysis capability supports this by analyzing prompts and sessions in context — rather than as isolated text — to identify intent and flag activity that doesn't match expected usage for a given user or system.
How can organizations detect and manage Shadow AI?
Shadow AI — AI tools, agents, or infrastructure used without IT approval or oversight — is typically detected by continuously scanning network and application activity for AI usage patterns, rather than relying only on a list of approved tools. This surfaces AI use that formal inventories miss. Darktrace's Shadow AI Management capability applies this approach across an enterprise's environment, identifying unsanctioned AI activity, who is using it, and what it can access.
How can organizations secure AI agents?
Securing AI agents requires monitoring their identities, permissions, and actions — not just the prompts that trigger them — since agents can take autonomous actions across business systems using access they've already been granted. This makes over-permissioning and unintended access common failure points. Darktrace's AI Agent Identities and Actions capability provides this identity-centric oversight, helping teams spot agents with excessive permissions or actions inconsistent with intended use.
How can AI security controls reduce data leakage?
AI security controls reduce data leakage by analyzing the context of prompts, outputs, and agent actions for sensitive data exposure, rather than relying only on static keyword or pattern matching, which misses context-dependent risk. Darktrace's AI Prompt Analysis evaluates prompts and sessions in context to flag interactions where sensitive data is at risk of exposure through a GenAI tool or agent.
How can organizations monitor AI prompts securely?
Secure prompt monitoring analyzes what a prompt asks for, its surrounding session context, and the actions it triggers downstream — since a single prompt can affect multiple systems, and risk often isn't visible in the prompt text alone. Darktrace's AI Prompt Analysis capability is built around this: it evaluates prompts as a control point, tracking how they map to resulting system or agent behavior to identify deviations from expected use.
How can enterprises improve AI governance and security?
AI governance improves when organizations monitor AI continuously across its lifecycle — development, deployment, and daily use — rather than assessing risk only at launch. This catches misconfigurations and permission issues introduced during development, before they reach production. Darktrace's AI Agent Development Risk Management capability evaluates deployment risk across low-code and high-code platforms, surfacing misconfigurations and anomalous development activity as part of ongoing governance.