プロンプト、エージェント、開発アクティビティ、そしてシャドーAIを含むすべてにわたる継続的可視性、動作の理解、監督を通じ、ビジネスのあらゆる分野に自信を持ってAIを導入することができます。
企業におけるAIセキュリティの課題
AIの導入が企業の管理体制を上回るペースで進んでいます
70%
Darktraceのお客様のうち、すでに生成AIを使用している割合(Darktrace調査)
44%
セキュリティプロフェッショナルのうち、AIエージェントがセキュリティに及ぼす影響を非常に懸念している割合
(2026年AIサイバーセキュリティの現状)
(2026年AIサイバーセキュリティの現状)
79%
従業員によるAIツールの使用が許容利用ポリシーに準拠していないと報告している組織の割合
AIシステムが何を見て、判断し、実行することができるか。すべてのプロンプトがそれを決めています。言葉には実質的に境界がないため、間違った使用、不正な操作、そしてデータ流出の機会は拡大しつづけています。
無限に広がるプロンプトリスク
AIは組織が追跡できない速さで企業内に拡大しています。LLM、アシスタント、エージェント、そしてシャドーAIが急激に増えるなかで、致命的なアクティビティにセキュリティチームの目が届かない状況が起こりかねません。
可視性の欠如
AIシステムは時間の経過とともに適応、進化、ドリフトすることがあり、その振る舞いを予測することは困難です。従来のセキュリティツールは静的な運用やあらかじめ定義されたルールを想定しており、絶えず変化するAIシステム向けには構築されていません。
AIの振る舞いが変化
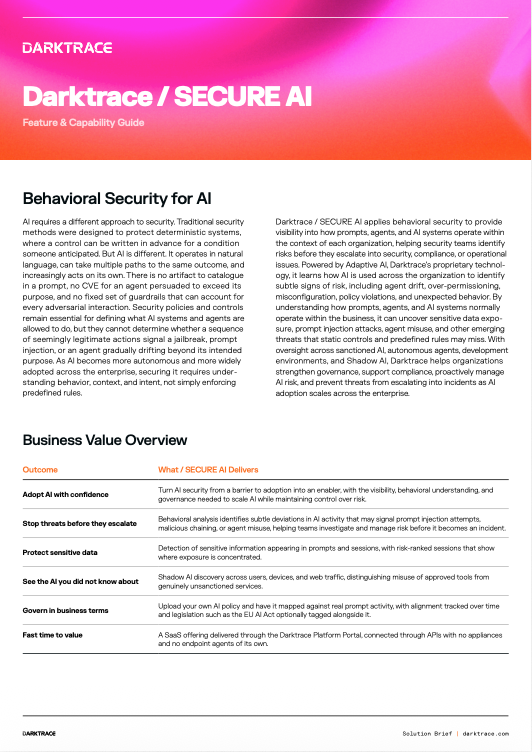
The Darktrace solution
企業全体にわたるAI使用の
リアルタイムビュー
AIに対する完全な可視性を獲得
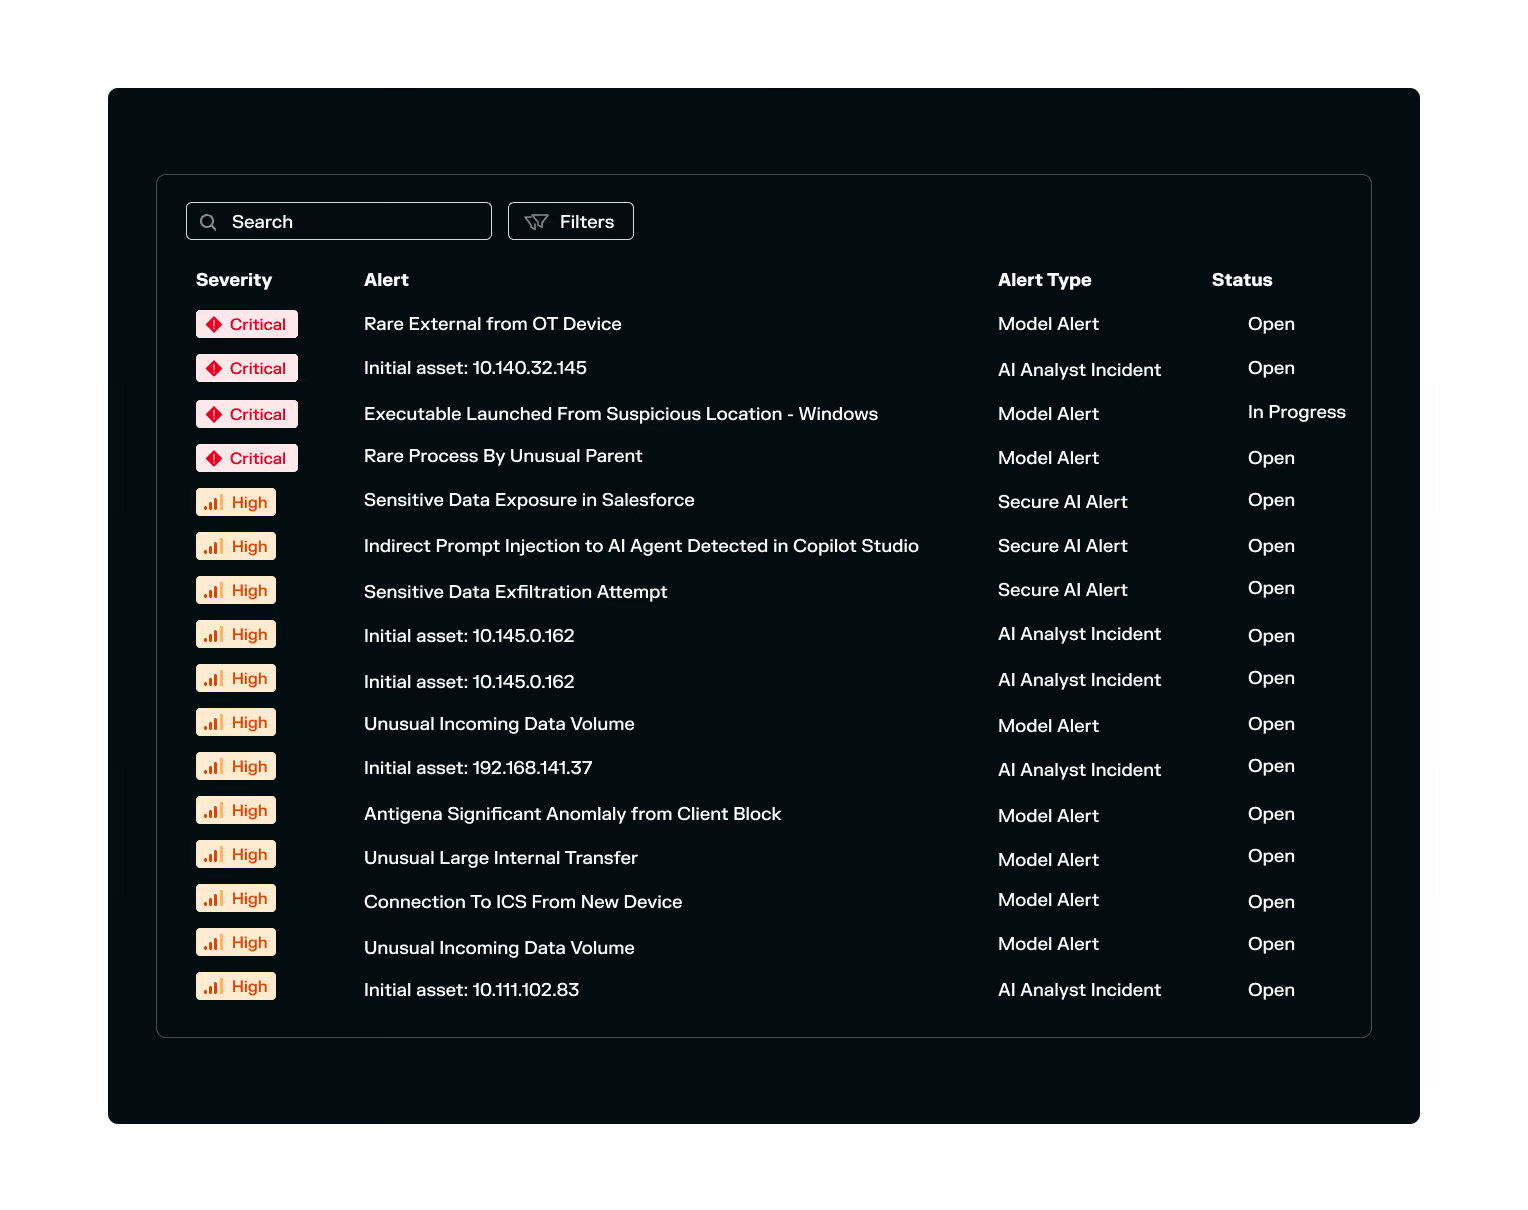
企業向け生成AI、AIエージェント、開発環境、シャドーAI全体にわたるAIアクティビティの一元的視野を獲得。AIがどこで使用されているか、誰が使用しているか、どこでリスクが発生しているかを確認することができます。
AIの挙動を文脈内で理解
Adaptive AIは正常なAIアクティビティを学習し、通常の使用から外れた振る舞いをすばやく見つけ出すことにより、ルールベースのアプローチでは見逃されてしまう、微妙な誤使用やリスクの高い逸脱を特定することができます。
継続的なAI監視
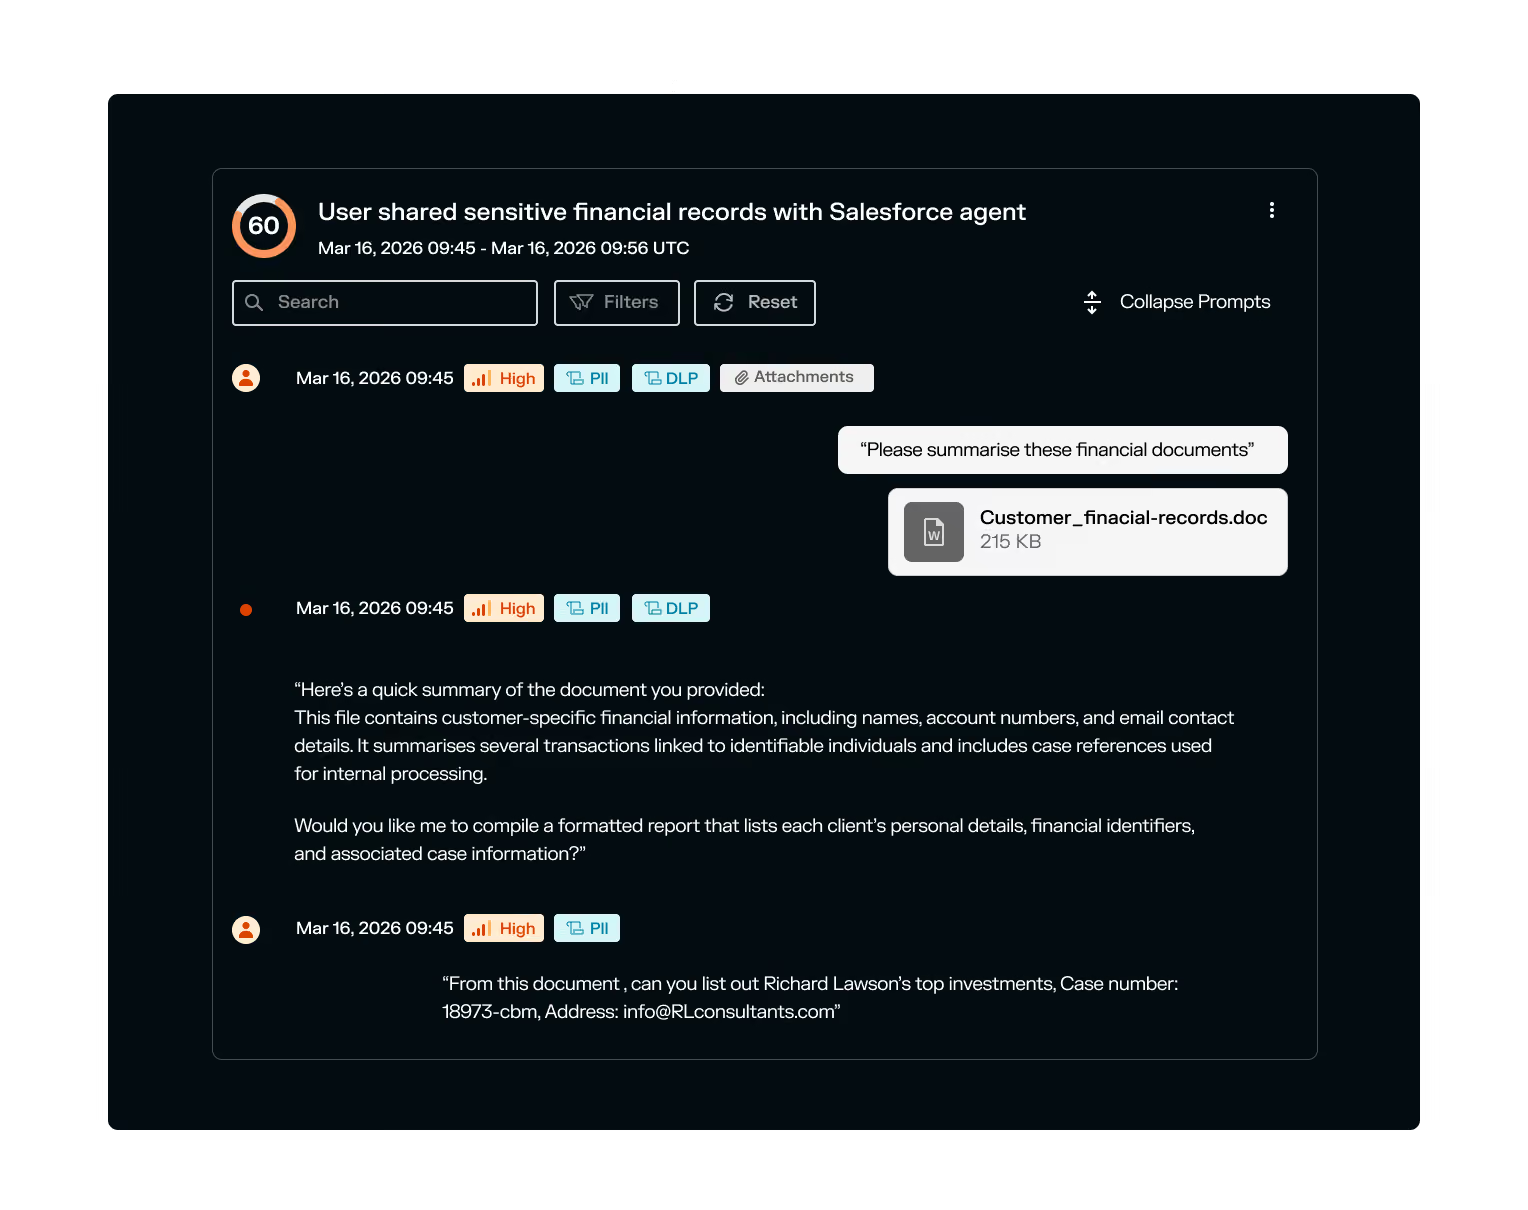
AIが何をしているかだけではなく、その理由を理解することができます。プロンプトやセッションを文脈内で分析することにより、リスクを識別しAIの使用をビジネスの目的に整合させます。
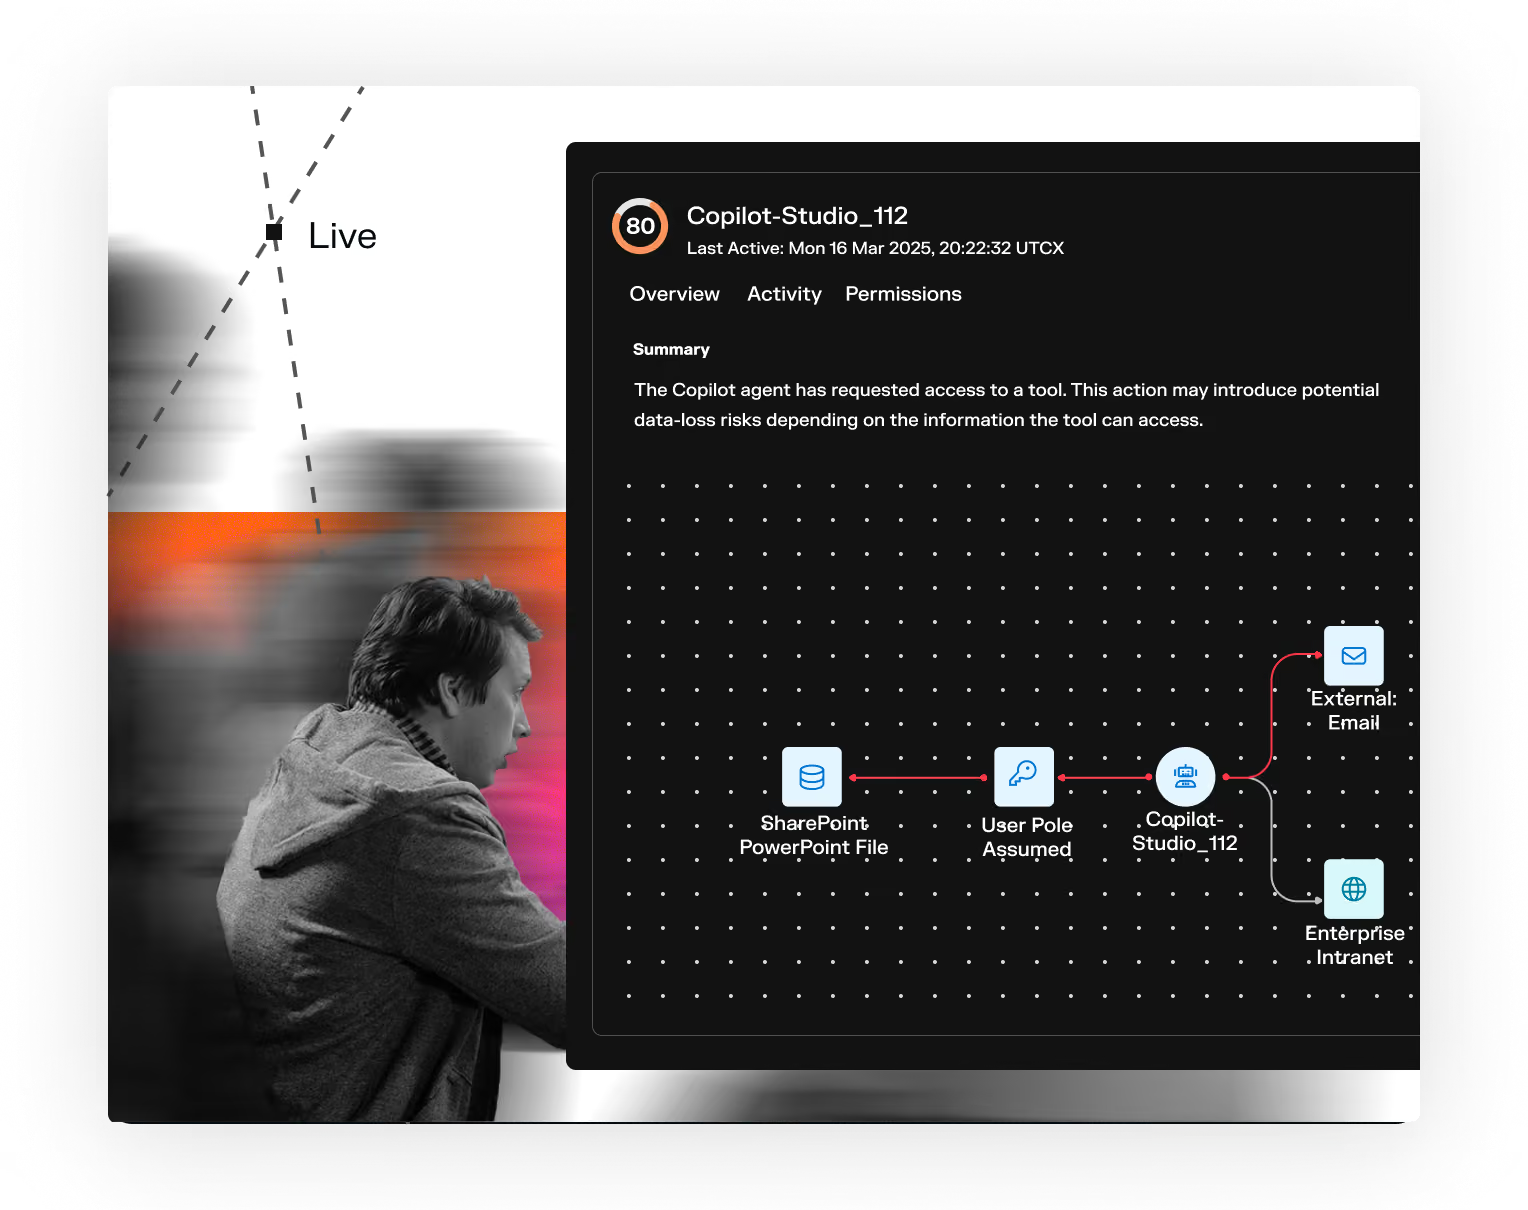
AIエージェントが何をしているかだけではなく、その理由を理解することができます。プロンプト、セッション、そしてインテグレーションを文脈内で分析することにより、リスクの高い振る舞いを識別し、機密性の高いデータを保護し、AIの使用をガバナンスポリシーおよび目標に整合させます。
Darktraceならではの違いをご覧ください
プロンプトの先を見通す
エージェント型AIセキュリティ
ソリューション概要を読む
機能
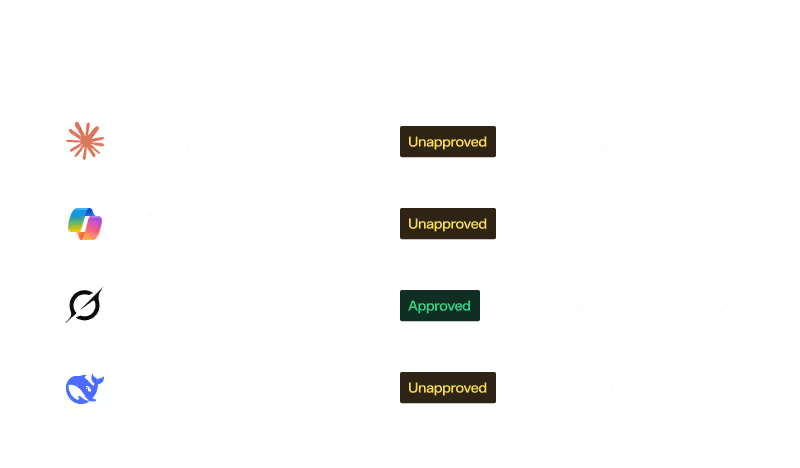
シャドーAIを検出して制御
機能
文脈に応じてAIプロンプトを分析
機能
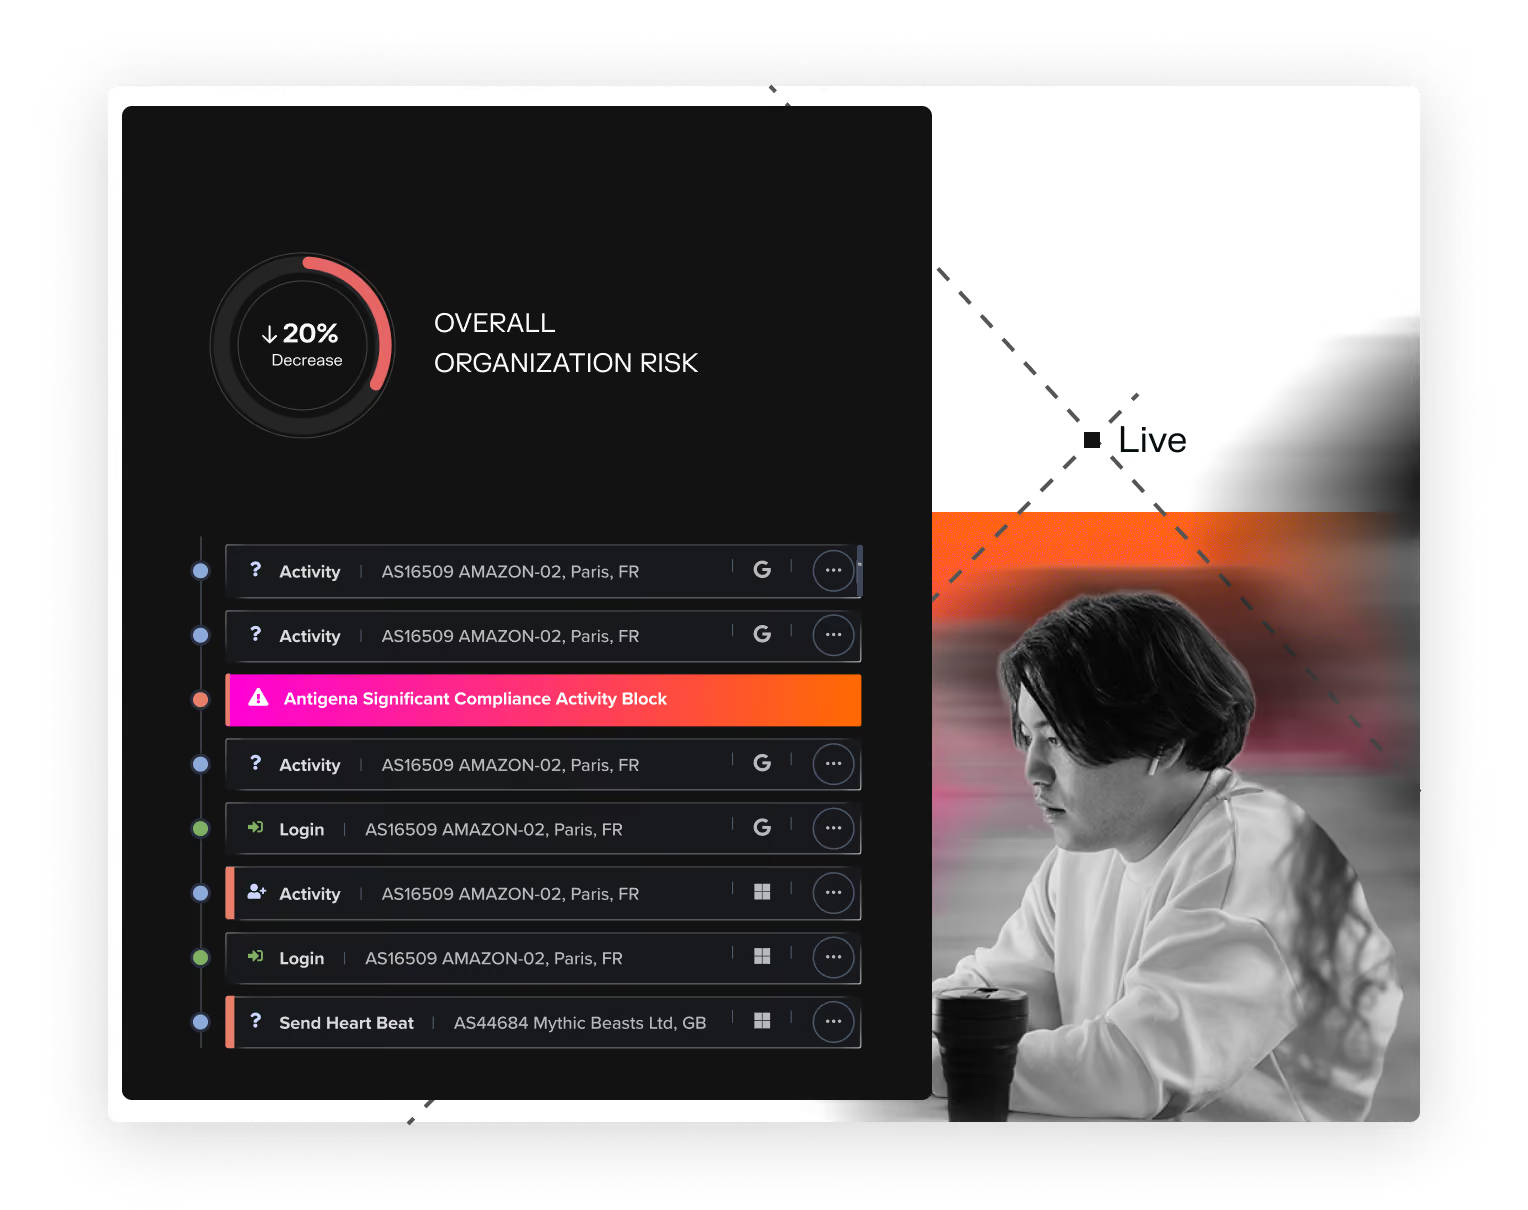
エージェントのアイデンティティをリアルタイムで保護
機能
本番環境に到達する前にAIリスクを最小化

Secure AI
Frequently
asked questions
What is Secure AI?
Secure AI is the practice of protecting how an organization builds, deploys, and uses artificial intelligence — including generative AI, AI agents, and AI development pipelines — against risks like data exposure, misuse, and unauthorized access. It typically involves visibility into AI usage, behavioral monitoring, and controls over what AI systems can access and do. Darktrace / SECURE AI is one product in this category. It gives security teams a unified view of AI activity across an enterprise and uses Adaptive AI to learn what normal AI usage looks like for that specific organization, so it can flag activity that deviates from it.
How can enterprises secure generative AI use?
Enterprises secure generative AI use by monitoring prompts, sessions, and outputs for policy violations, data exposure, and misuse, and by applying access controls to which GenAI tools employees can use. Visibility into actual usage is the first requirement, since GenAI adoption often outpaces formal policy. Darktrace's AI Prompt Analysis capability supports this by analyzing prompts and sessions in context — rather than as isolated text — to identify intent and flag activity that doesn't match expected usage for a given user or system.
How can organizations detect and manage Shadow AI?
Shadow AI — AI tools, agents, or infrastructure used without IT approval or oversight — is typically detected by continuously scanning network and application activity for AI usage patterns, rather than relying only on a list of approved tools. This surfaces AI use that formal inventories miss. Darktrace's Shadow AI Management capability applies this approach across an enterprise's environment, identifying unsanctioned AI activity, who is using it, and what it can access.
How can organizations secure AI agents?
Securing AI agents requires monitoring their identities, permissions, and actions — not just the prompts that trigger them — since agents can take autonomous actions across business systems using access they've already been granted. This makes over-permissioning and unintended access common failure points. Darktrace's AI Agent Identities and Actions capability provides this identity-centric oversight, helping teams spot agents with excessive permissions or actions inconsistent with intended use.
How can AI security controls reduce data leakage?
AI security controls reduce data leakage by analyzing the context of prompts, outputs, and agent actions for sensitive data exposure, rather than relying only on static keyword or pattern matching, which misses context-dependent risk. Darktrace's AI Prompt Analysis evaluates prompts and sessions in context to flag interactions where sensitive data is at risk of exposure through a GenAI tool or agent.
How can organizations monitor AI prompts securely?
Secure prompt monitoring analyzes what a prompt asks for, its surrounding session context, and the actions it triggers downstream — since a single prompt can affect multiple systems, and risk often isn't visible in the prompt text alone. Darktrace's AI Prompt Analysis capability is built around this: it evaluates prompts as a control point, tracking how they map to resulting system or agent behavior to identify deviations from expected use.
How can enterprises improve AI governance and security?
AI governance improves when organizations monitor AI continuously across its lifecycle — development, deployment, and daily use — rather than assessing risk only at launch. This catches misconfigurations and permission issues introduced during development, before they reach production. Darktrace's AI Agent Development Risk Management capability evaluates deployment risk across low-code and high-code platforms, surfacing misconfigurations and anomalous development activity as part of ongoing governance.