Gain continuous visibility across cloud workloads, services, identities and activity with Cloud Detection and Response (CDR) detect threats in real time, and investigate incidents with the context of your hybrid network.
Cloud security capabilities
Secure cloud environments within your hybrid infrastructure
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C

The visibility challenge
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
5.25M
Average cost of a breach that involved cloud misconfigurations affecting AI workloads
(IBM Cost of a Data Breach 2026)
23%
of organizations report full visibility into their cloud environments
(Cloud Security Alliance)
Disarm known and novel cloud-based threats quickly with platform-native response
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
Detect known and novel cloud threats in real time
Adaptive AI continuously monitors activity across cloud assets, workloads, APIs, containers, and identities, building a unique behavioral profile of your environment. By understanding what's normal for your organization, Darktrace can detect known, novel, insider, and AI-accelerated threats that traditional approaches may miss.
Simplify and accelerate the investigation process
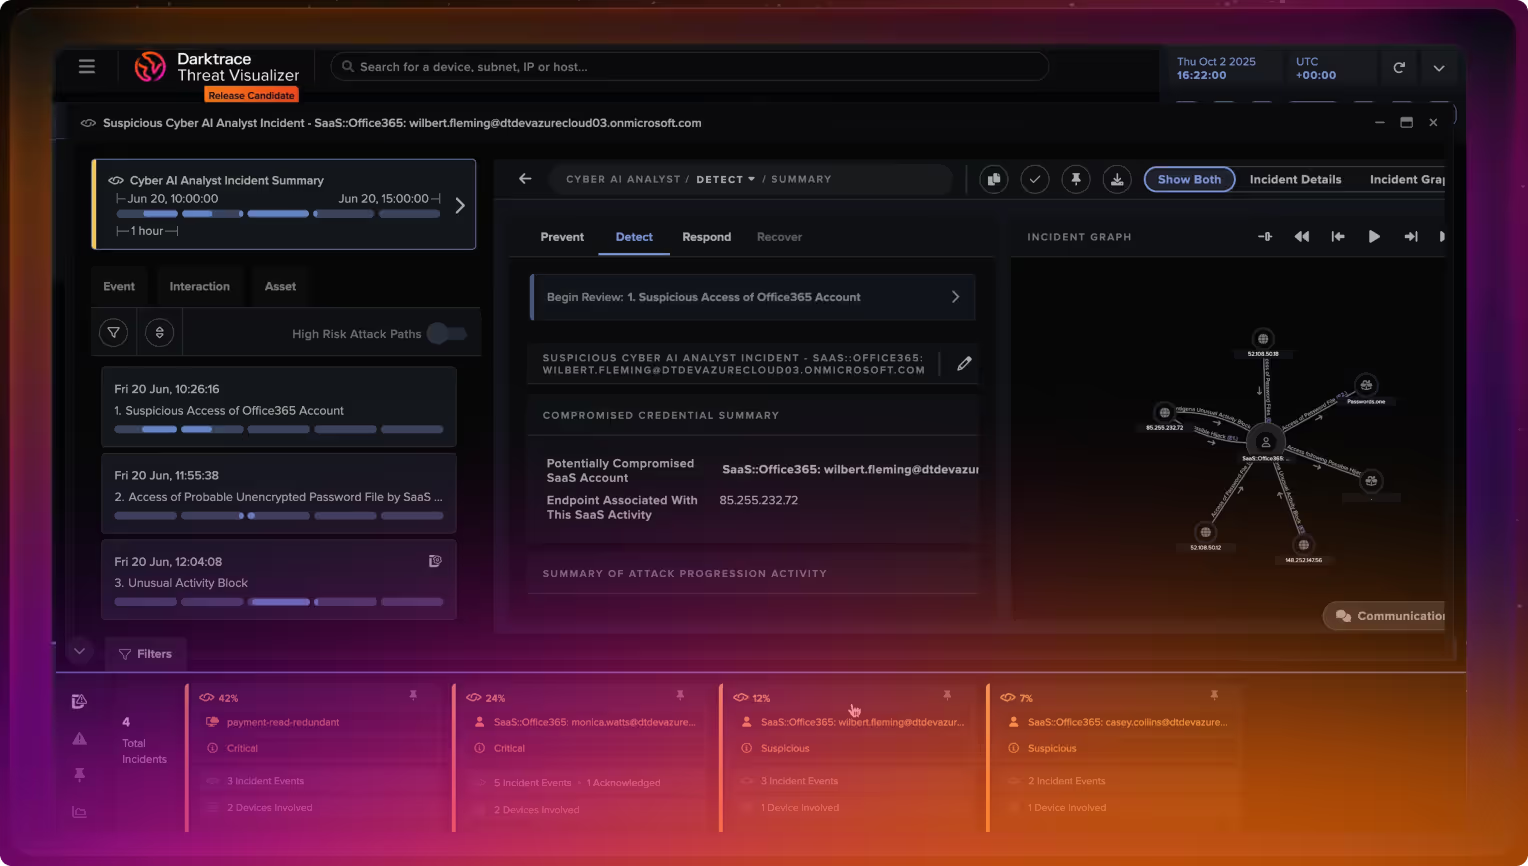
Cyber AI Analyst automatically investigates alerts, connects related cloud and infrastructure activity, and provides security teams with meaningful incident context. By correlating behavior across cloud, identity, network, and endpoint domains, Darktrace accelerates investigations and reduces manual analysis.
Respond to cloud threats with precision at machine speed
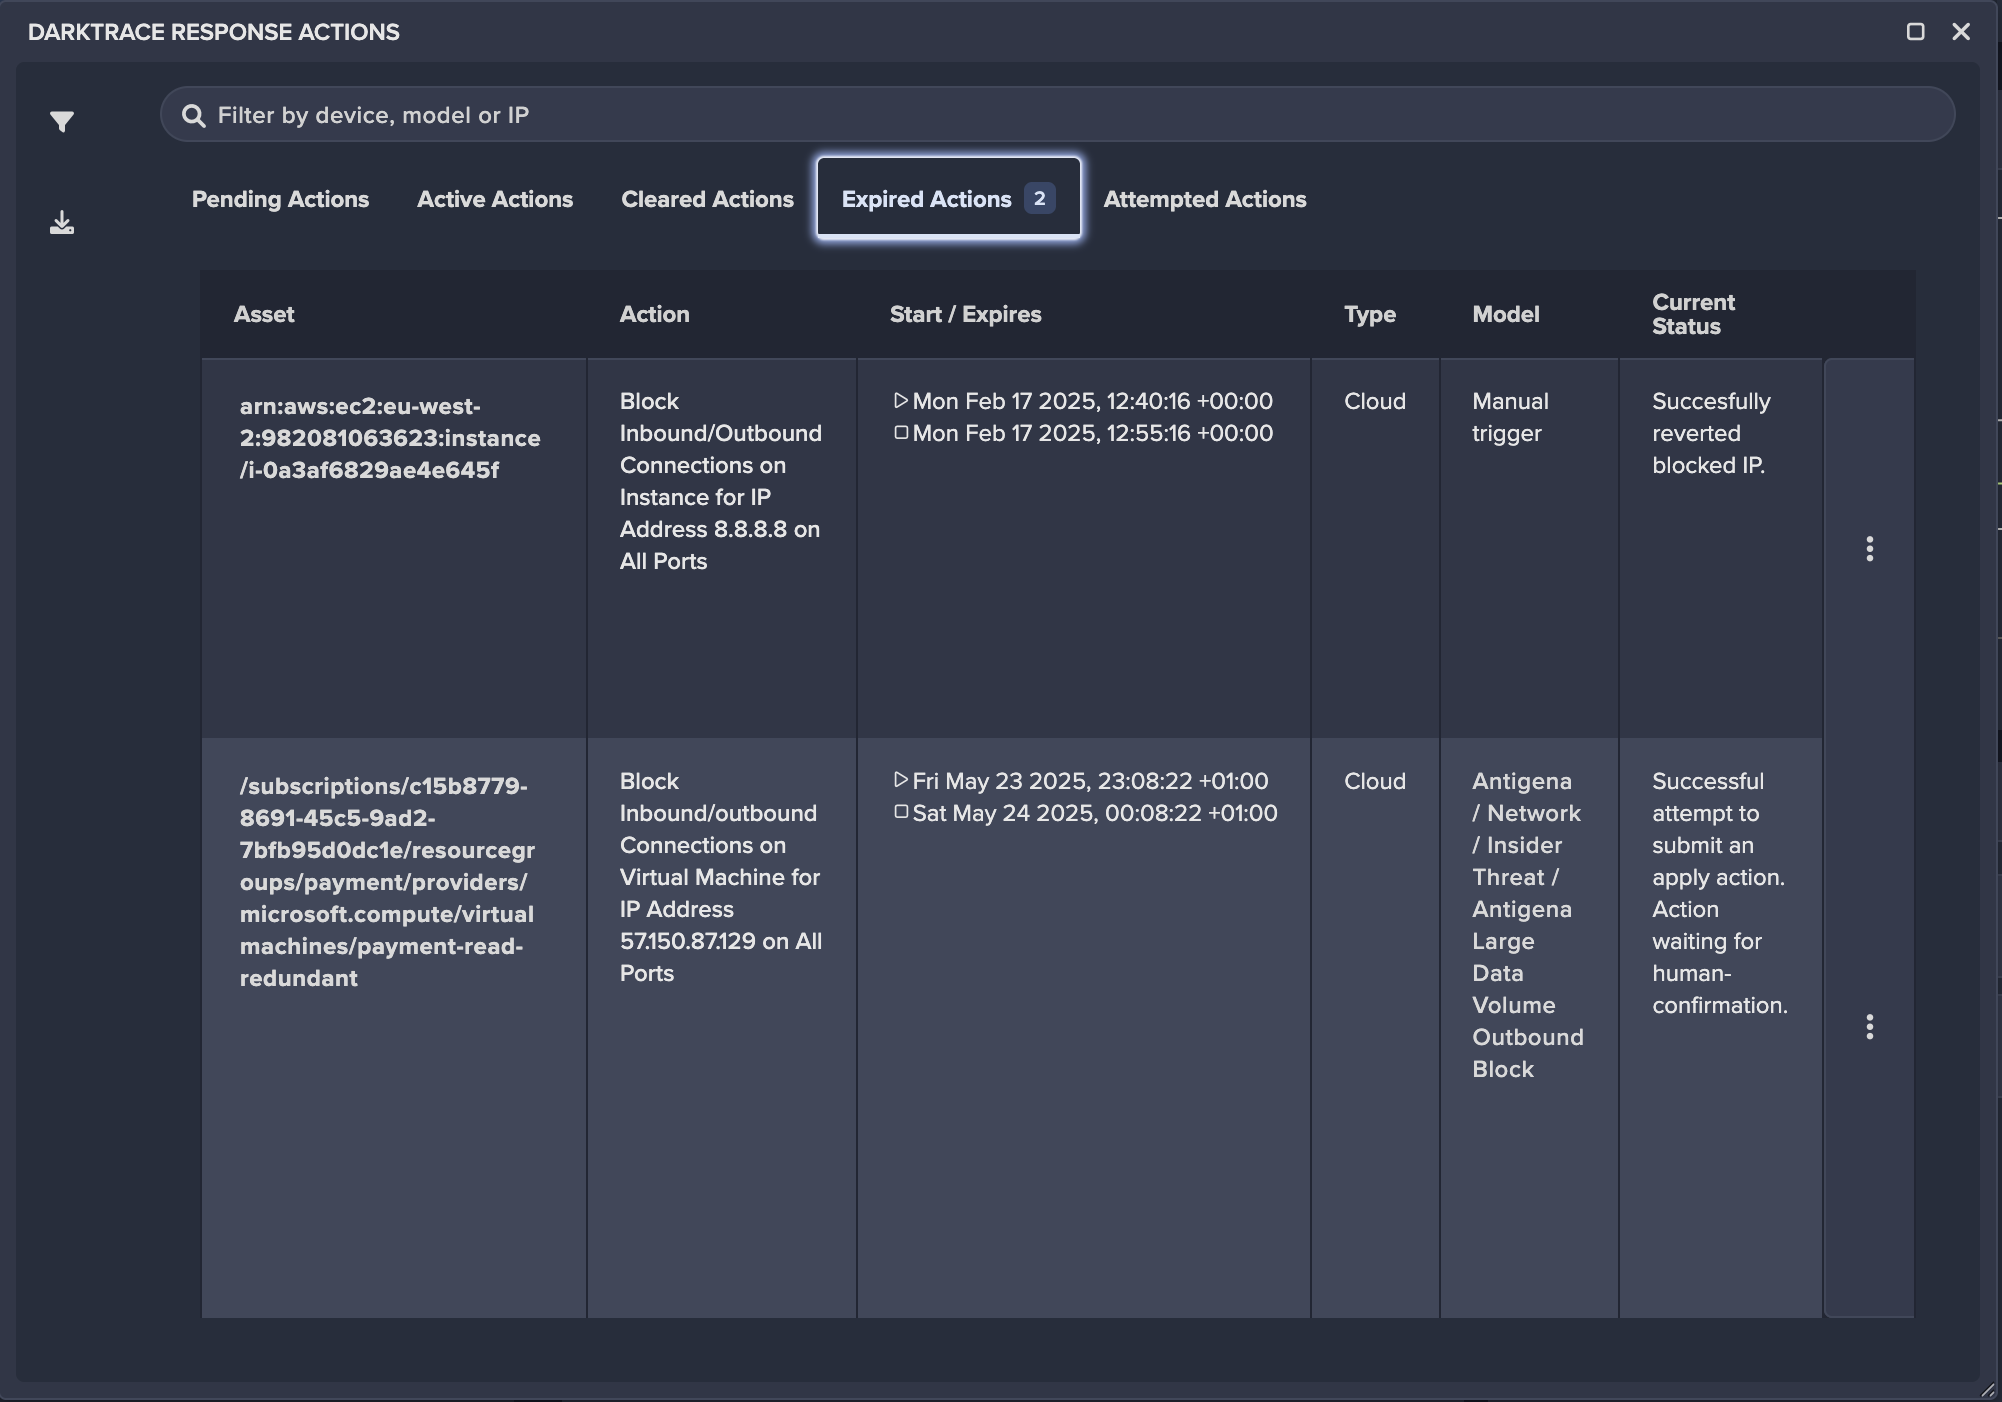
Darktrace autonomously contains malicious activity using behavioral context specific to your organization. Response actions are designed to stop threatening behavior while minimizing disruption to cloud services, workloads, and business operations.


Discover the Darktrace difference
Read the solution brief
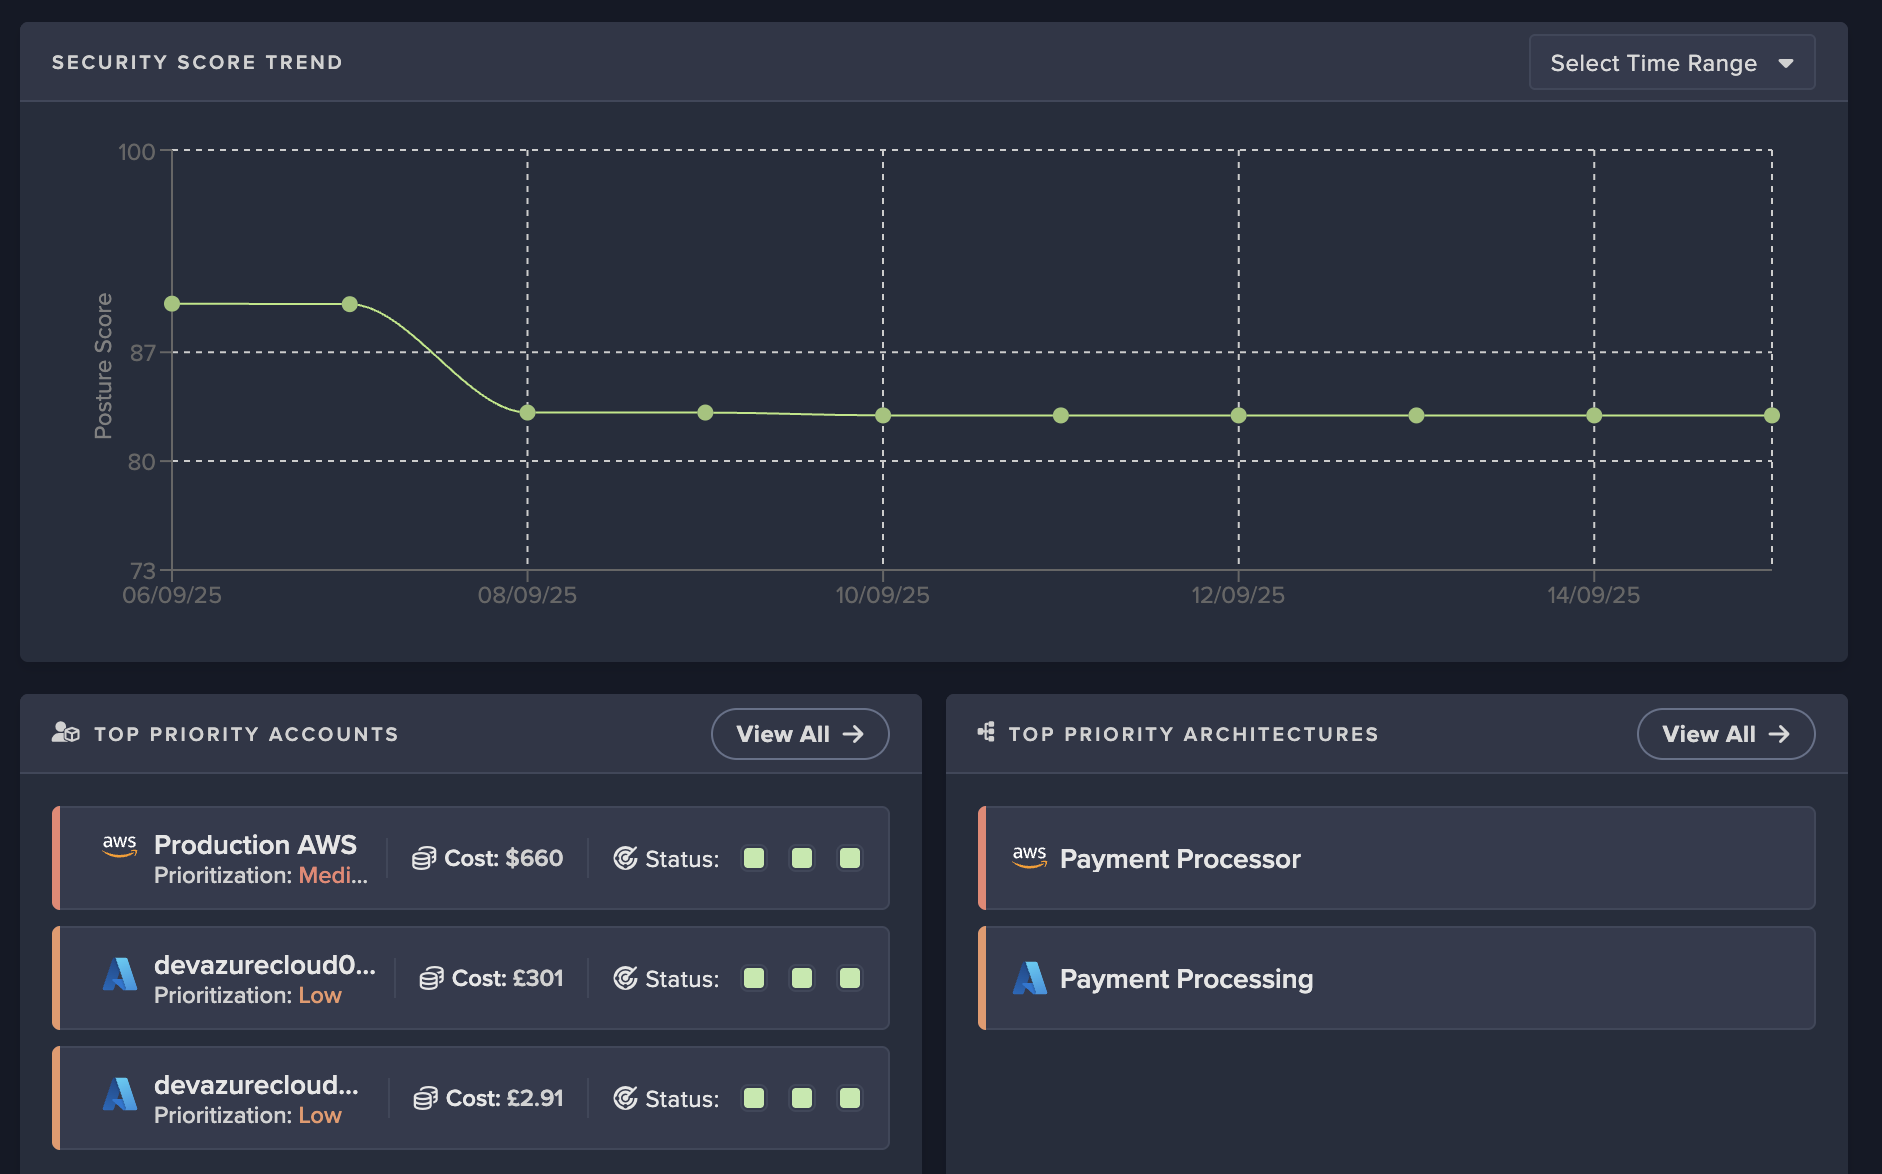
Prioritize your biggest risks based on a deep understanding of your environment
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
Secure user permissions and entitlements
Gain visibility into identities, permissions, access pathways, and privilege relationships across cloud environments. Darktrace helps identify excessive permissions, risky access patterns, and behaviors that could enable insider threats or lateral movement.
Maintain cloud compliance
Continuously monitor cloud environments against evolving risk conditions and operational changes. Darktrace helps teams prioritize remediation efforts based on real-world exposure and business context rather than static findings alone.
Proactively address cloud risks
Darktrace validates and prioritizes exposures using behavioral and risk context unique to your organization. By understanding how assets, users, identities, and workloads interact, security teams can focus remediation efforts where they will have the greatest impact on resilience.
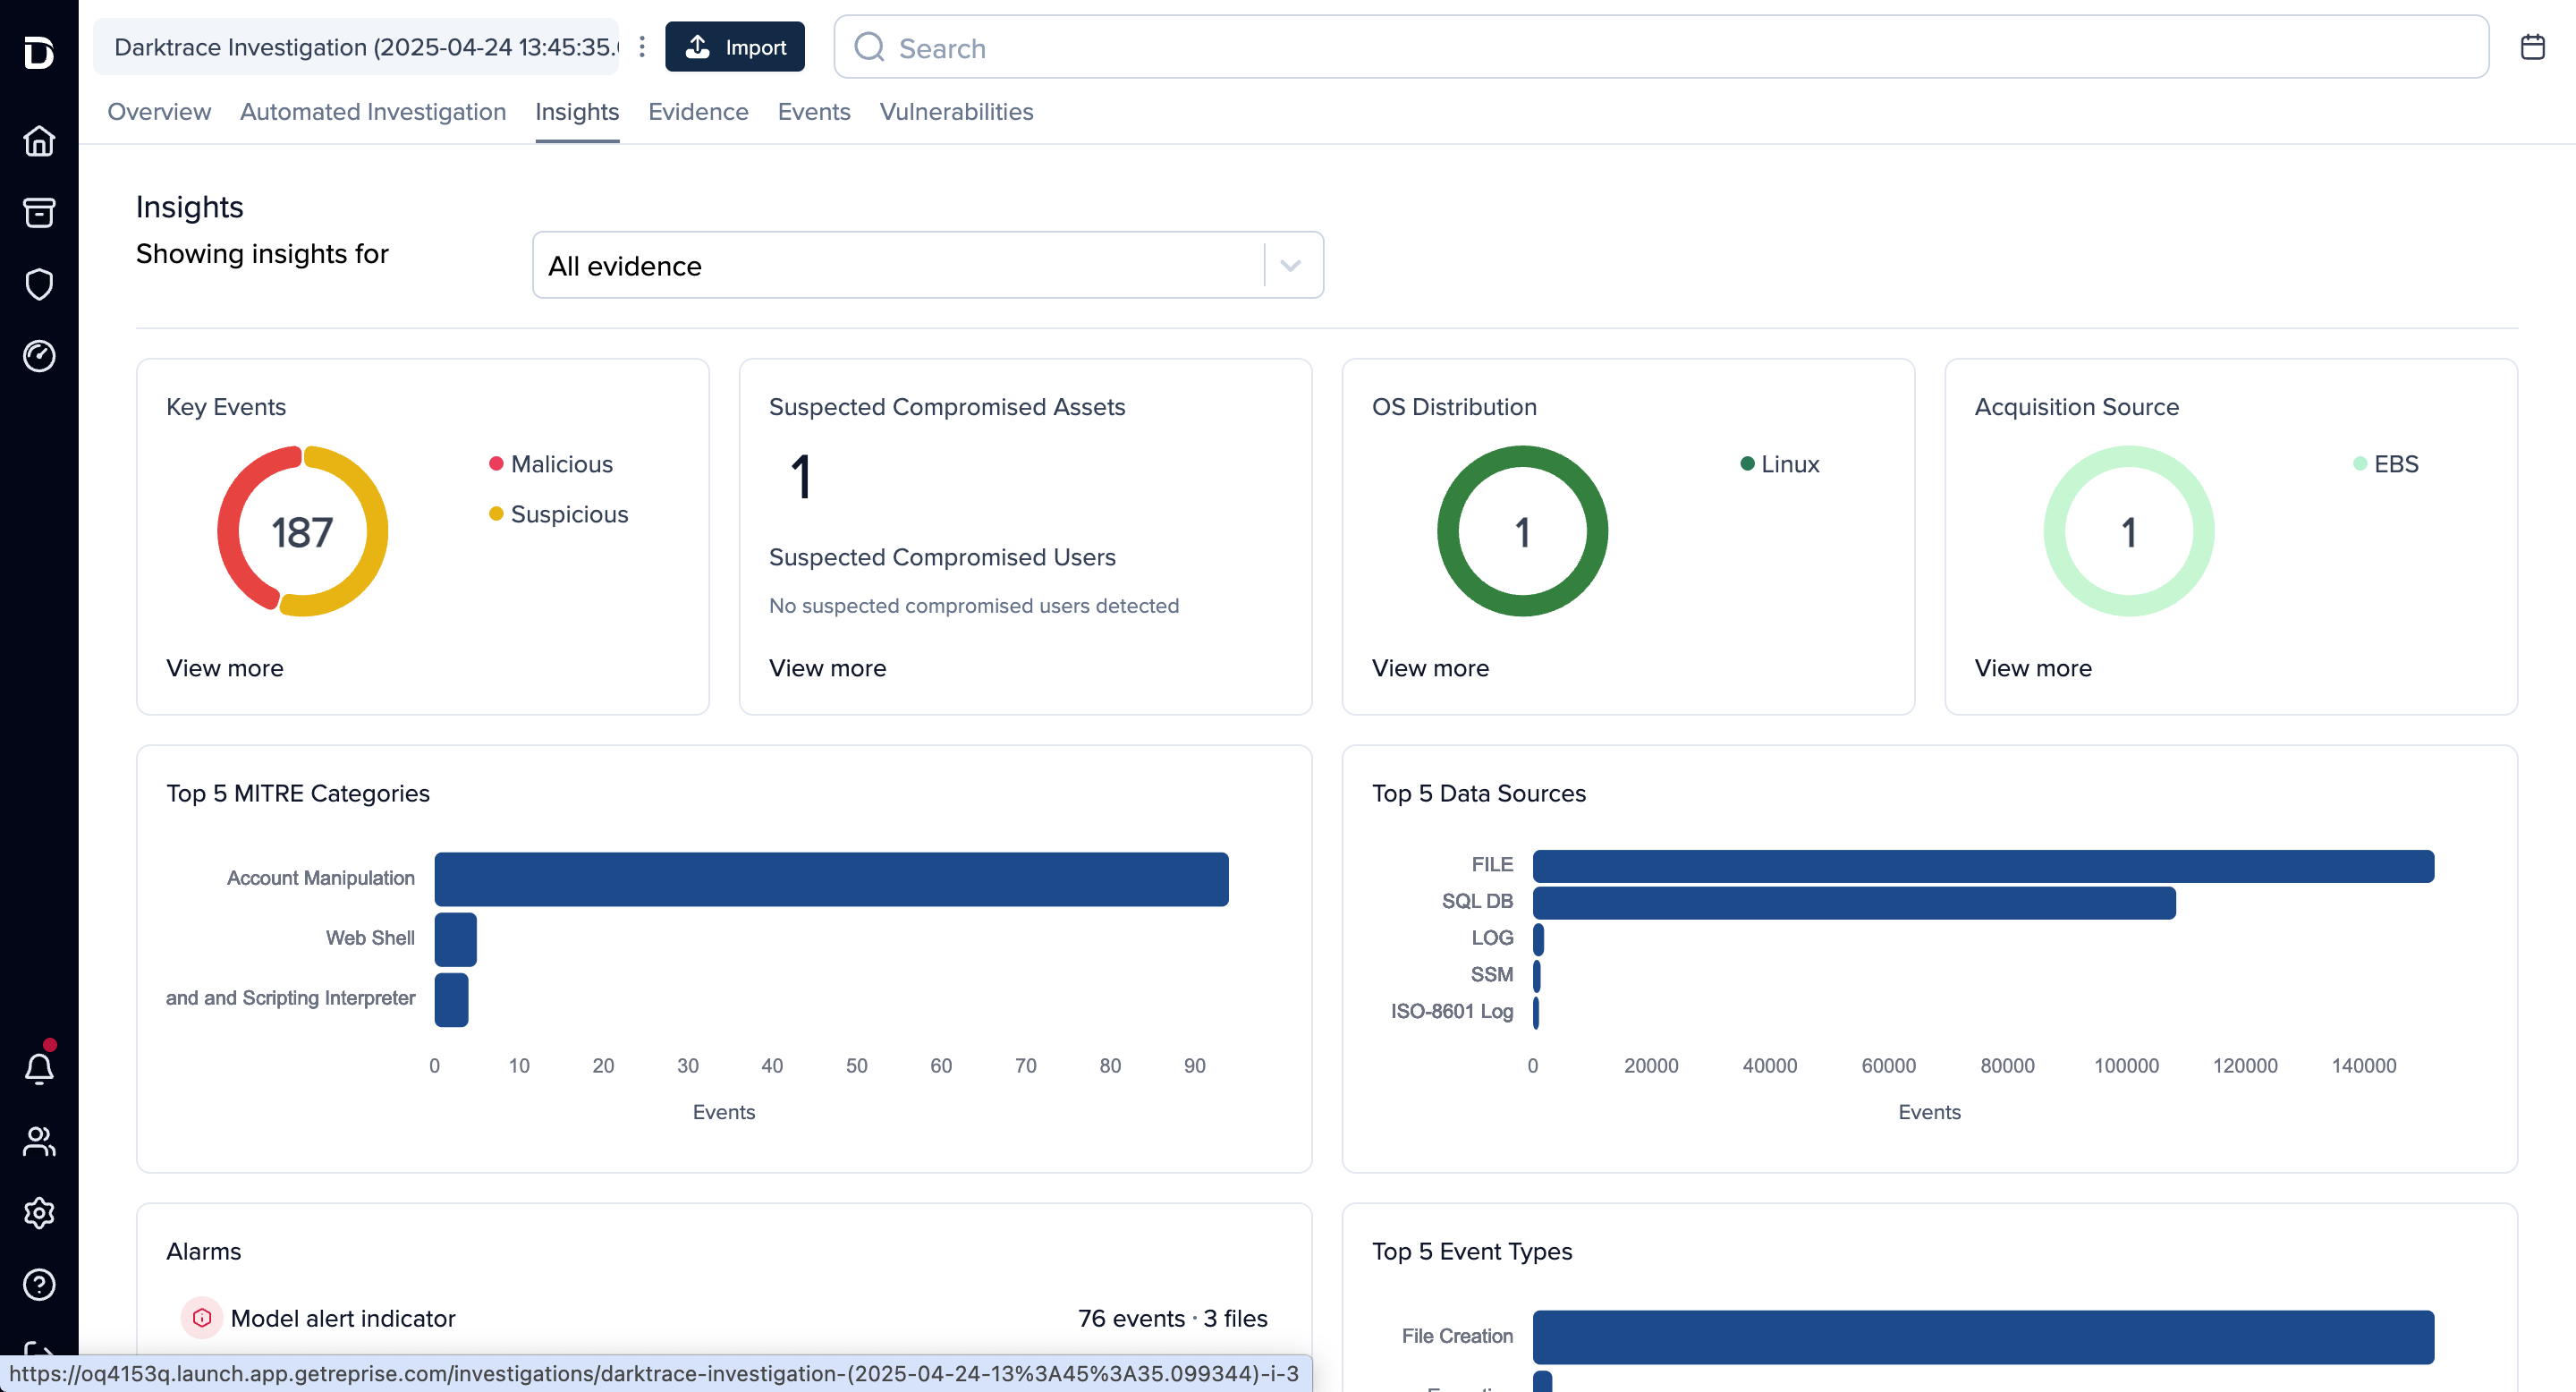
Enrich investigations with automated cloud forensics
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
Automate evidence at cloud speed
Collect cloud-native forensic evidence directly through integrations and APIs, reducing time spent gathering data and enabling faster access to the information needed for investigations.
Get a complete attacker timeline in minutes
Automatically reconstruct attacker activity and investigation timelines by correlating evidence across cloud workloads, identities, services, and infrastructure. This helps teams rapidly understand root cause, scope, and impact.
Cloud-native forensics designed for scale
Deploy forensic capabilities across cloud environments with minimal operational overhead. Darktrace integrates with existing workflows and investigation processes to help security teams respond efficiently across distributed environments.
Understand your complex cloud footprint
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
Demystify your cloud infrastructure
Build a continuously evolving understanding of your cloud environment with visibility into assets, workloads, services, identities, and relationships. Darktrace maps activity and behavior in real time as your cloud infrastructure grows and changes.
Dynamically monitor and secure workloads
Continuously monitor cloud workloads, containers, and cloud-native services using Adaptive AI that learns normal operational patterns. Detect suspicious behavior and emerging threats without relying solely on predefined rules or signatures.
Unite SecOps and DevOps teams with shared visibility
Create a common understanding of cloud activity, security posture, and operational risk across teams. Shared visibility helps organizations secure cloud transformation initiatives while improving collaboration between security and infrastructure stakeholders.
Demo video
See Darktrace / HYBRID NETWORK in action
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
Customer stories
Hear from our customers



Stronger as part of the Darktrace Behavioral Defense Platform
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
ご不明な点はございませんか?
What are the key differences between cloud security posture management (CSPM) and cloud workload protection platforms (CWPP)?
These two categories of security tools address distinct aspects of the cloud environment. They complement each other for effective cloud security but have some distinct differences. CSPM tools secure the cloud infrastructure (control plane), while CWPP tools protect individual workloads (runtime).
CSPM tools automate the assessment and remediation of security misconfigurations and compliance violations across cloud environments, such as AWS and Azure. These tools validate adherence to security benchmarks and compliance frameworks by identifying and addressing misconfigured identity access management (IAM) policies, exposed storage, and noncompliant network configurations. They reduce your attack surface by proactively strengthening your cloud foundation.
CWPPs focus on runtime protection for individual cloud workloads, including virtual machines, containers, and serverless functions. They monitor processes, network connections, and file system activity to detect and respond to malicious behavior, identifying and containing exploits and ransomware. CWPPs complement CSPM tools and provide a real-time defense system.
A comprehensive cloud security strategy combines the strengths of CSPM and CWPP. Integrating these capabilities provides streamlined management, improves visibility, and supports threat prevention and response across your entire cloud infrastructure. However, achieving this seamless integration requires planning. Look for solutions with API integrations, standardized data formats, and intuitive dashboards for managing both CSPM and CWPP functions.
It's also important to find platforms that use multi-layered AI to correlate data from different sources, providing a unified view of risk across your entire cloud environment. This way, security teams can prioritize alerts, streamline cloud investigations, and automate response actions more effectively. Ensure that your chosen platform offers flexible deployment options. It should support agent-based and agentless approaches to accommodate the diverse requirements of your cloud workloads.
AIはクラウドセキュリティにどのように使われるのですか?
クラウドセキュリティに対してAIは検知、対応、予防機能を強化する上できわめて重要な役割を果たします。AI駆動のソリューションは膨大な量のデータを分析し、パターンを検知し、セキュリティ脅威の兆候かもしれない異常を特定することにより、クラウド内でのリアルタイム脅威検知に不可欠な要素となっています。AIクラウドセキュリティソリューションはユーザーの振る舞い、アクセスパターン、ネットワークアクティビティを継続的に監視することにより、有害な意図を示すものかもしれないあらゆる異常を警告します。
さらに、AIクラウドセキュリティソリューションは機械学習を使って過去のインシデントを学習し脅威検知モデルを調整することにより、新しい脅威や進化する脅威に適応します。これは従来のルールベースの手法を使って検知することが困難な、ゼロデイ攻撃や内部関係者による脅威を防止する上で特に有効です。また、AIをクラウドセキュリティに取り入れることで偽陽性が取り除かれ、アラート疲れが軽減されることにより、セキュリティチームは高リスクの脅威に集中できるようになります。AIとクラウドセキュリティ自動化の組み合わせは、クラウド環境の特徴である高い複雑性と急激な変化に適した動的な防御メカニズムを提供します。
クラウドセキュリティの未来は自動化ですか?
す。自動化により、監視や脅威検知等の繰り返しのタスクをセキュリティシステムに処理させ、対処までの時間を短縮し、サイバーセキュリティチームの人出による作業負荷を削減することができます。クラウド環境においては、広大なネットワークを保護しリアルタイムのデータフローを管理するために必要な規模と速度を考えたとき、自動化は特に重要な問題です。
また、自動化により一貫性を向上させヒューマンエラーを最小化することもできます。これは、オンプレミス、ハイブリッド、クラウドインフラを含めた多様な環境にわたってセキュリティポリシーを徹底する上できわめて重要です。サイバーセキュリティにAI駆動の自動化を導入することで、データをより効率的に管理および分析し、異常検知と潜在的脅威に対する警告を即座に行うことができます。
データセキュリティソリューションを選ぶ際に注目すべき重要な機能とは何ですか?
クラウド環境のためのデータセキュリティソリューションを選択するには、クラウドの複雑性を特に考慮して設計されたツールを、注意深く検討する必要があります。優れたソリューションはクラウドアーキテクチャへの可視性を提供し、クラウドリソースの構成、振る舞い、相互動作に対して詳細な情報を確認することができます。クラウドインフラ全体にわたって脆弱性を特定し緩和するためにはこのレベルの可視性が不可欠です。というのも、多くの従来型のセキュリティツールはクラウドネイティブな運用に必要な深い視界が欠けているからです。
スケーラビリティとインテグレーションも重要な問題です。クラウド環境は動的であり、また多くの場合複数のプラットフォームやサービスが含まれているからです。強力なデータセキュリティソリューションはオンプレミスとクラウドベースの環境の両方を管理し、インフラ全体に一貫したポリシーを徹底することができます。クラウドセキュリティプラットフォームと統合することにより、こうしたソリューションはシームレスな監視を実現し、クラウドとオンプレミスシステム間のセキュリティギャップを縮小することができます。
クラウドリソースの展開スピードが速いことを考慮すれば、リアルタイムの検知および対処機能は不可欠です。クラウド環境には、急激に拡大する脅威に対応するため、そして複雑なAI駆動の攻撃や設定ミスにも対応できる、敏捷な脅威検知および自動化された対処機能が必要です。これらのソリューションには脅威の識別と対処を効率化するためのサイバーセキュリティ自動化機能が含まれ、脅威が検知されるとリソースを自動的に再設定、または隔離することができます。
最後に、クラウドネイティブなデータセキュリティソリューションには、GDPR、HIPAAなどの規制への適合をサポートし、詳細なレポートやアナリティクスを提供する、包括的なコンプライアンス管理が含まれていなければなりません。また、直感的なインターフェイスによりこれらの機能を効率的に管理できること、また集中管理型の監視機能によりすべてのクラウドリソースが一貫して保護されるようにできることも重要です。
How can organizations ensure compliance with data privacy regulations in the cloud?
To ensure cloud data privacy, organizations must proactively manage data governance and security. This practice involves establishing a framework that adapts to evolving regulations and cyber-threats. First, gain an understanding of your data landscape by automatically classifying sensitive information across cloud environments and ensuring targeted security, particularly for data subject to regulations such as General Data Protection Regulation (GDPR). Utilize cloud provider features to store and process data within specific regions, ensuring compliance with local data sovereignty requirements.
Another essential element to consider is access control and encryption. Prioritize sensitive information and implement granular access management, along with robust encryption to safeguard confidentiality. Data loss prevention (DLP) prevents unauthorized exfiltration by monitoring data movement and blocking sensitive information from leaving secure environments, enforcing essential data handling policies.
Ensure you can consistently demonstrate compliance by implementing automated compliance monitoring for continuous tracking and generating comprehensive audit reports. Enhance security with multi-layered AI that analyzes data access patterns and identifies anomalous behavior for proactive alerts to address risks.
What are the different deployment options for cloud security solutions?
There are two primary deployment models for cloud security solutions. The most effective security approach combines these models to provide the visibility and granular insights that support informed decision-making.
An agent-based security model incorporates software into each cloud workload, offering granular visibility into workload activity and enabling direct response actions. However, managing agents across large and dynamic environments introduces complexity that may impact performance. Although this approach provides deep, contextual insights, it requires careful planning to ensure compatibility and minimize resource consumption.
The agentless security model gathers data using the cloud provider's native APIs rather than software installation on workloads. Deployment is simplified with no performance impact, providing broad visibility. Keep in mind that this method may provide less detailed information and depends on the cloud provider's API capabilities. It's popular due to its ease of deployment and minimal operational overhead, making it suitable for organizations with limited resources.
クラウドコンピューティングにおけるサイバーセキュリティの重要性とは?
クラウドコンピューティングでは、機密性の高い大量のデータが動的なクラウド環境内で管理されることから、サイバー攻撃の格好の標的となっており、サイバーセキュリティがきわめて重要です。組織がクラウドへの移行を進めるなかで、マルチテナント環境でのデータの保護や、規制へのコンプライアンス管理など、クラウド特有のセキュリティ課題に直面します。クラウド環境では、多くの場合従来のオンプレミスのセキュリティモデルでは不十分であり、専用のクラウドセキュリティ対策が求められます。
従来のツールを超えるものとして、CSPM(Cloud Security Posture Management)やCNAPP(Cloud-Native Application Protection Platform)はクラウドネイティブな環境内で可視性を提供し、設定ミスに対処し、コンプライアンスを維持することにより、クラウド特有のさまざまな課題に対応しています。しかしながら、CSPMとCNAPPソリューションだけでは、包括的なクラウドセキュリティの実現には不十分です。完全なアプローチとしては、これらのツールを他のセキュリティ対策、プロアクティブな監視、そして人間の専門知識と統合し、複雑な脅威ランドスケープに効果的に対応できるようにする必要があります。
クラウド環境を包括的に保護するには、リアルタイムの脅威検知、コンテキストの認識、そしてプロアクティブな対策を含むホリスティックなセキュリティ戦略が必要です。セキュリティ対策をマルチクラウド環境全体で一元化することにより、組織のデータと業務を効果的に保護するために必要なレジリエンスおよび適応力を実現することができます。