Automate deep evidence capture across your hybrid environment, accelerate alert triage, and reconstruct complete attacker timelines in minutes – all within the context of Darktrace / HYBRID NETWORK.
Forensic investigation capabilities
Solve forensic investigations at hybrid speed
The investigation challenge
Investigations across cloud, network, and endpoint environments are manual, slow, and evidence disappears fast
1/3
of alerts in cloud and hybrid environments go uninvestigated due to lack of information
(Darktrace research)
89%
of organizations suffer damage before they’re able to contain and investigate an incident
Darktrace Cloud Security Report
Capture forensic-grade evidence before it disappears
Automate data capture across your business
Integrates with any alert source and deploys via API to enable fast, low-overhead evidence collection within existing workflows.
Support containers and ephemeral assets
Leverage automation to ensure incident data is captured and preserved before it disappears. Automatically collect key data sources and memory from individual processes for forensic analysis.
Parallel collection and processing
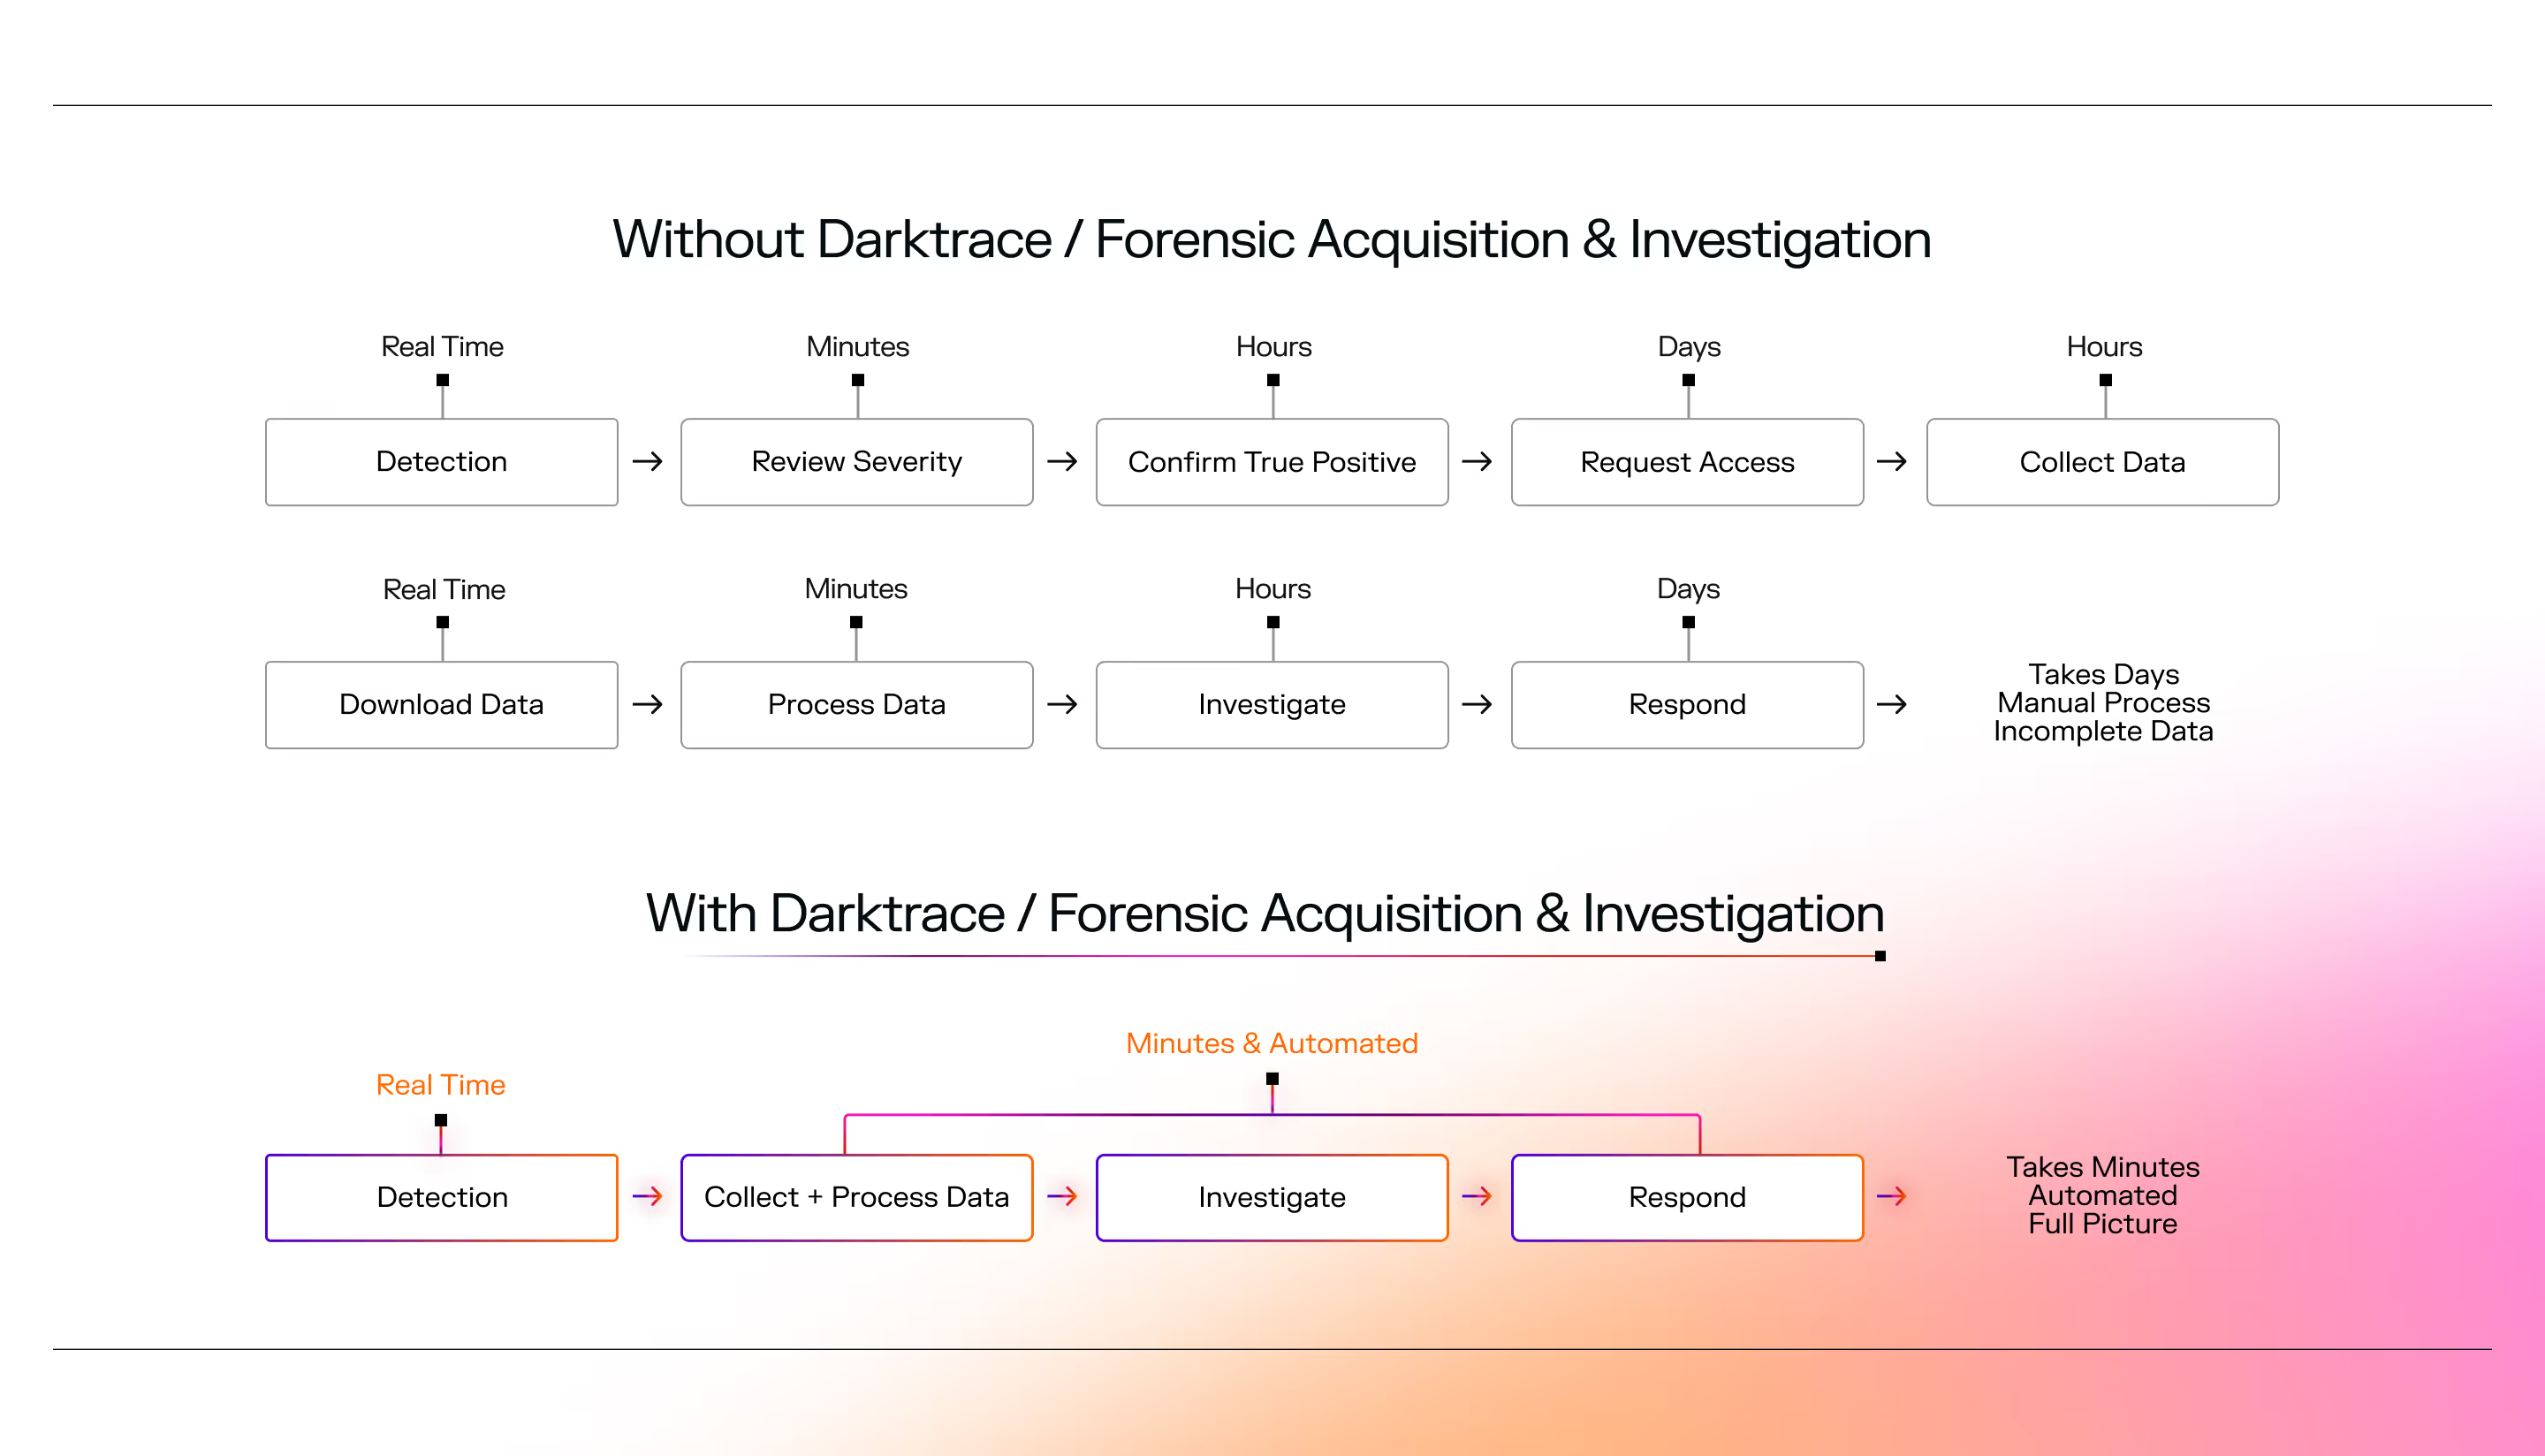
Capture more data in less time, resulting in deep forensic insight delivered in minutes, not days.
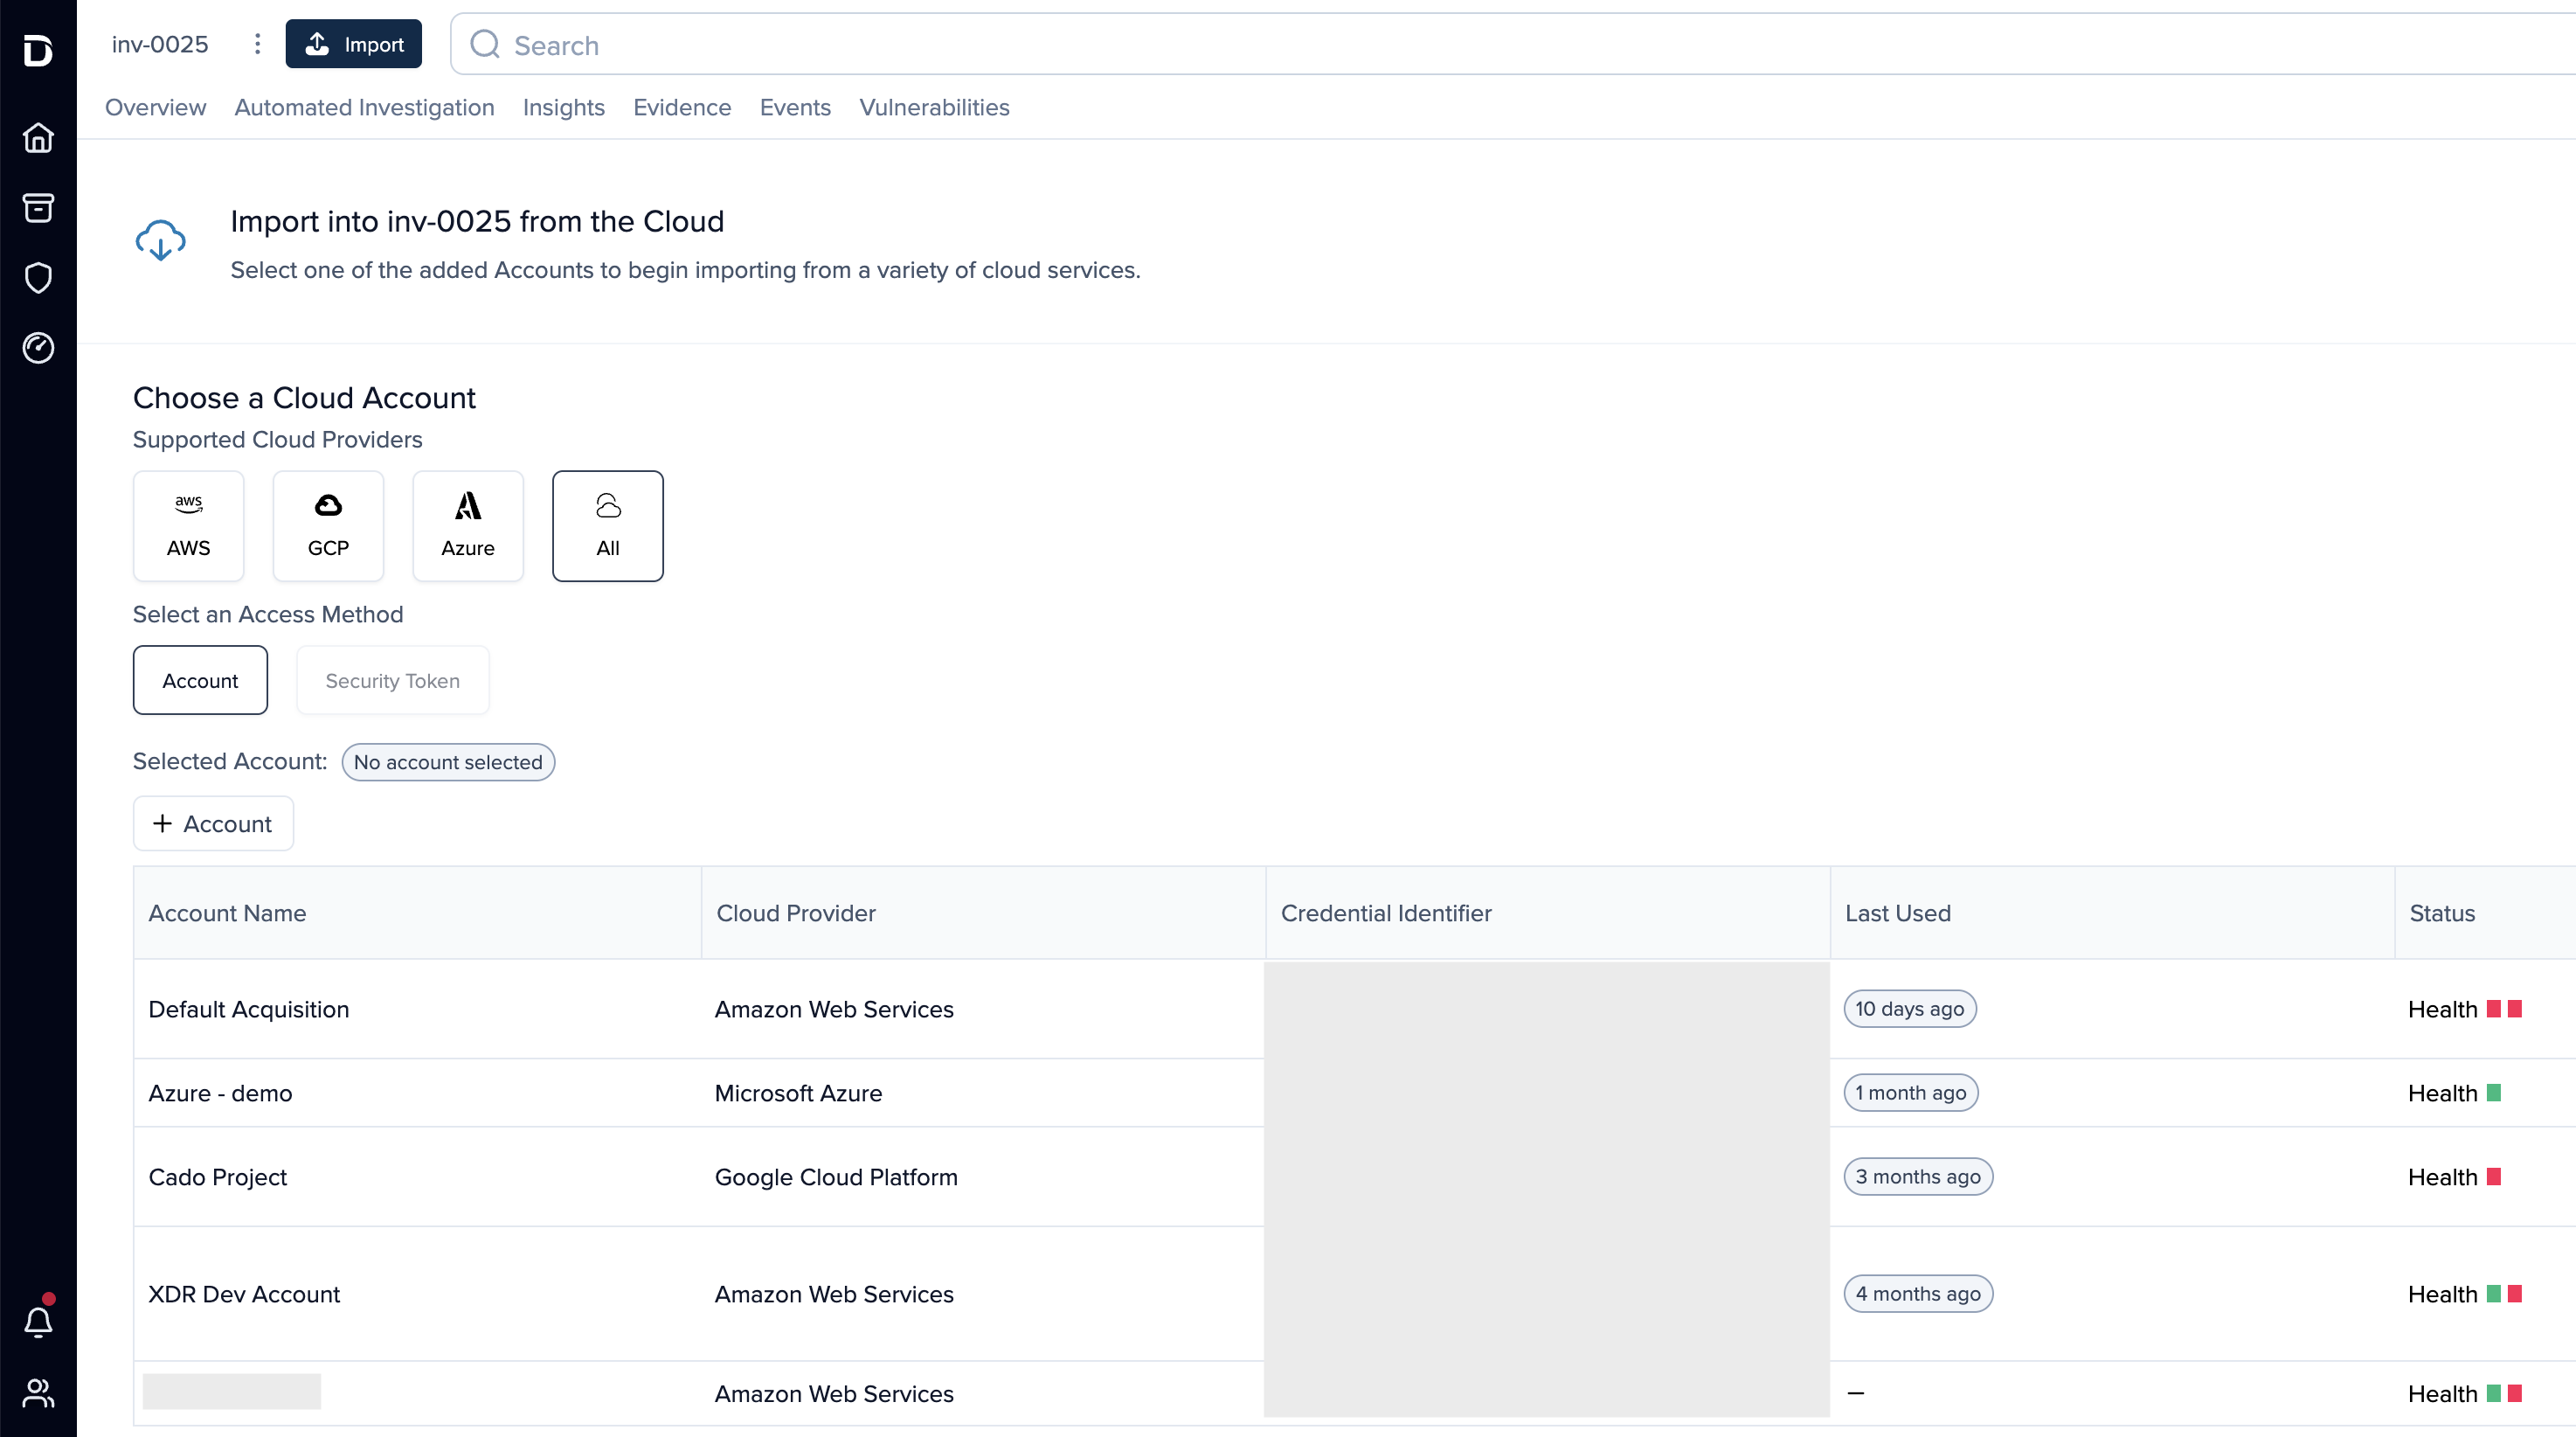


Get full attack timelines in minutes, not hours
Eliminate tedious manual work
Get root cause analysis for security alerts without combing through logs or artifacts manually.
Accelerate investigations
A visual timeline links files, commands, and lateral movement across cloud, network, identity, and endpoint domains.
Reduce uncertainty
Ensure response decisions are informed by a complete and accurate picture of the threat.

From days of manual work to minutes with automation
ユースケース
組織に力を与え
より速く脅威に対応
業界初のテクノロジーで複雑な環境全体のリスクを理解し、MTTRを短縮し、迅速に展開
クラウド横断調査
任意のクラウド環境で見つかったインシデントを単一の画面で調査。検知結果は1つのタイムラインにまとめられ、シームレスな調査と対応が可能です。
コンテナ & Kubernetes の調査
自動化を利用してインシデントデータが消失する前にキャプチャおよび保全を行うことにより、エフェメラル環境で調査および対応を行います。
SaaS 調査
主要なSaaSログをオンプレミスおよびクラウドアセットからキャプチャされた他のソースとあわせて調査し、悪意あるアクティビティの範囲と影響についてのより深い理解を得ることができます。
証拠保全
証拠の収集、処理、分析、保全を自動化することにより、必要なときにはいつでも -それらが消失する前に -すべてのチームがアクセスすることができます。
Hear from our customers
“当社では、何百もの潜在的インシデントを数分で解決しています。アナリストの調査を支援することにより、効率を250%まで大幅に高めることができています。”
世界的ゲーミング企業
セキュリティオペレーション責任者
“当社のクラウドチームは、数えきれないほどの手順を手作業で実施してフォレンジックデータのキャプチャおよび処理を行っています ... これを数クリックで実行できるようになると早く彼らに教えたいです!”
米国のFortune 500掲載企業
DFIRチーム長
“フォレンジック調査に取り掛かる前に24時間待つ必要がなくなったことは、まさに画期的です。”
大手サイバーセキュリティコンサルティング企業
DFIRマネージャー
Discover the Darktrace difference
Read the solution brief
Demo videos
See it in action
Cloud investigations
Cloud
Cloud detection & response
Cloud
Container investigations
Cloud
SOC triage
Cloud