Automate deep evidence capture across your hybrid environment, accelerate alert triage, and reconstruct complete attacker timelines in minutes – all within the context of Darktrace / HYBRID NETWORK.
Forensic investigation capabilities
Solve forensic investigations at hybrid speed
The investigation challenge
Investigations across cloud, network, and endpoint environments are manual, slow, and evidence disappears fast
1/3
of alerts in cloud and hybrid environments go uninvestigated due to lack of information
(Darktrace research)
89%
of organizations suffer damage before they’re able to contain and investigate an incident
Darktrace Cloud Security Report
Capture forensic-grade evidence before it disappears
Automate data capture across your business
Integrates with any alert source and deploys via API to enable fast, low-overhead evidence collection within existing workflows.
Support containers and ephemeral assets
Leverage automation to ensure incident data is captured and preserved before it disappears. Automatically collect key data sources and memory from individual processes for forensic analysis.
Parallel collection and processing
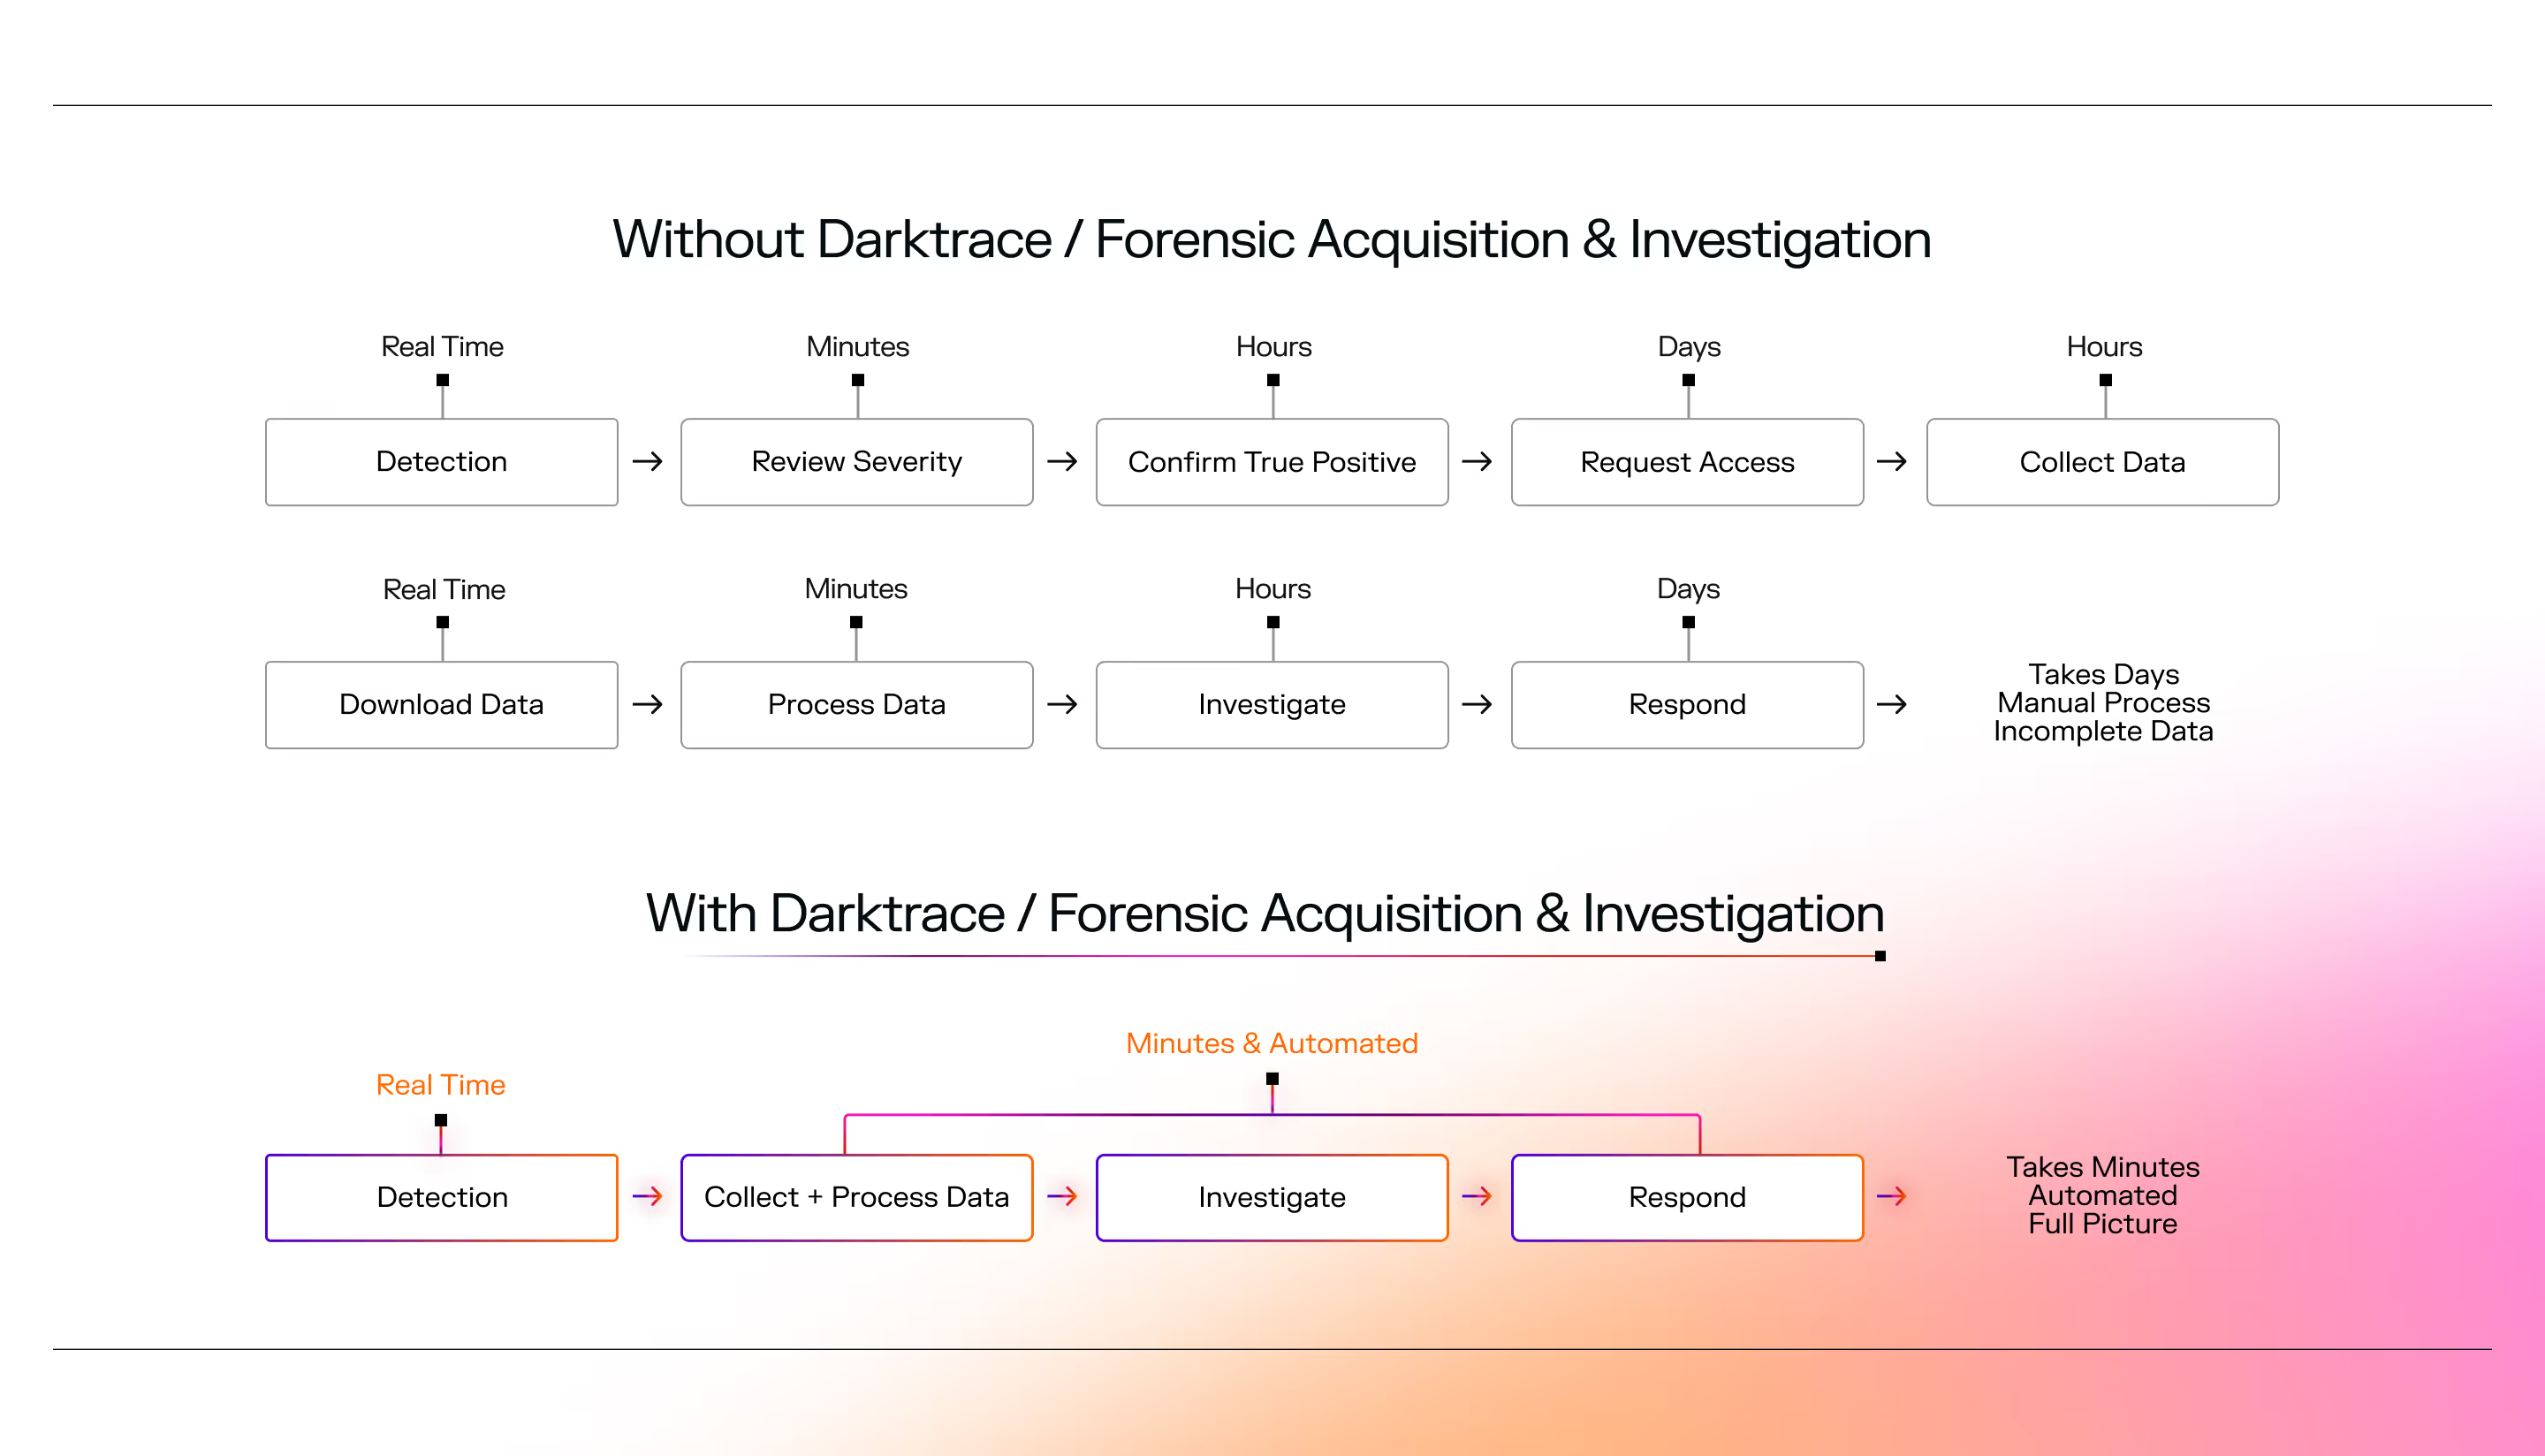
Capture more data in less time, resulting in deep forensic insight delivered in minutes, not days.


Get full attack timelines in minutes, not hours
Eliminate tedious manual work
Get root cause analysis for security alerts without combing through logs or artifacts manually.
Accelerate investigations
A visual timeline links files, commands, and lateral movement across cloud, network, identity, and endpoint domains.
Reduce uncertainty
Ensure response decisions are informed by a complete and accurate picture of the threat.

From days of manual work to minutes with automation
Use cases
Empowers organizations to respond to threats faster
Better understand risk across complex environments, reduce MTTR, and rapidly deploy with this first-of-its-kind technology.
Cross-domain investigations
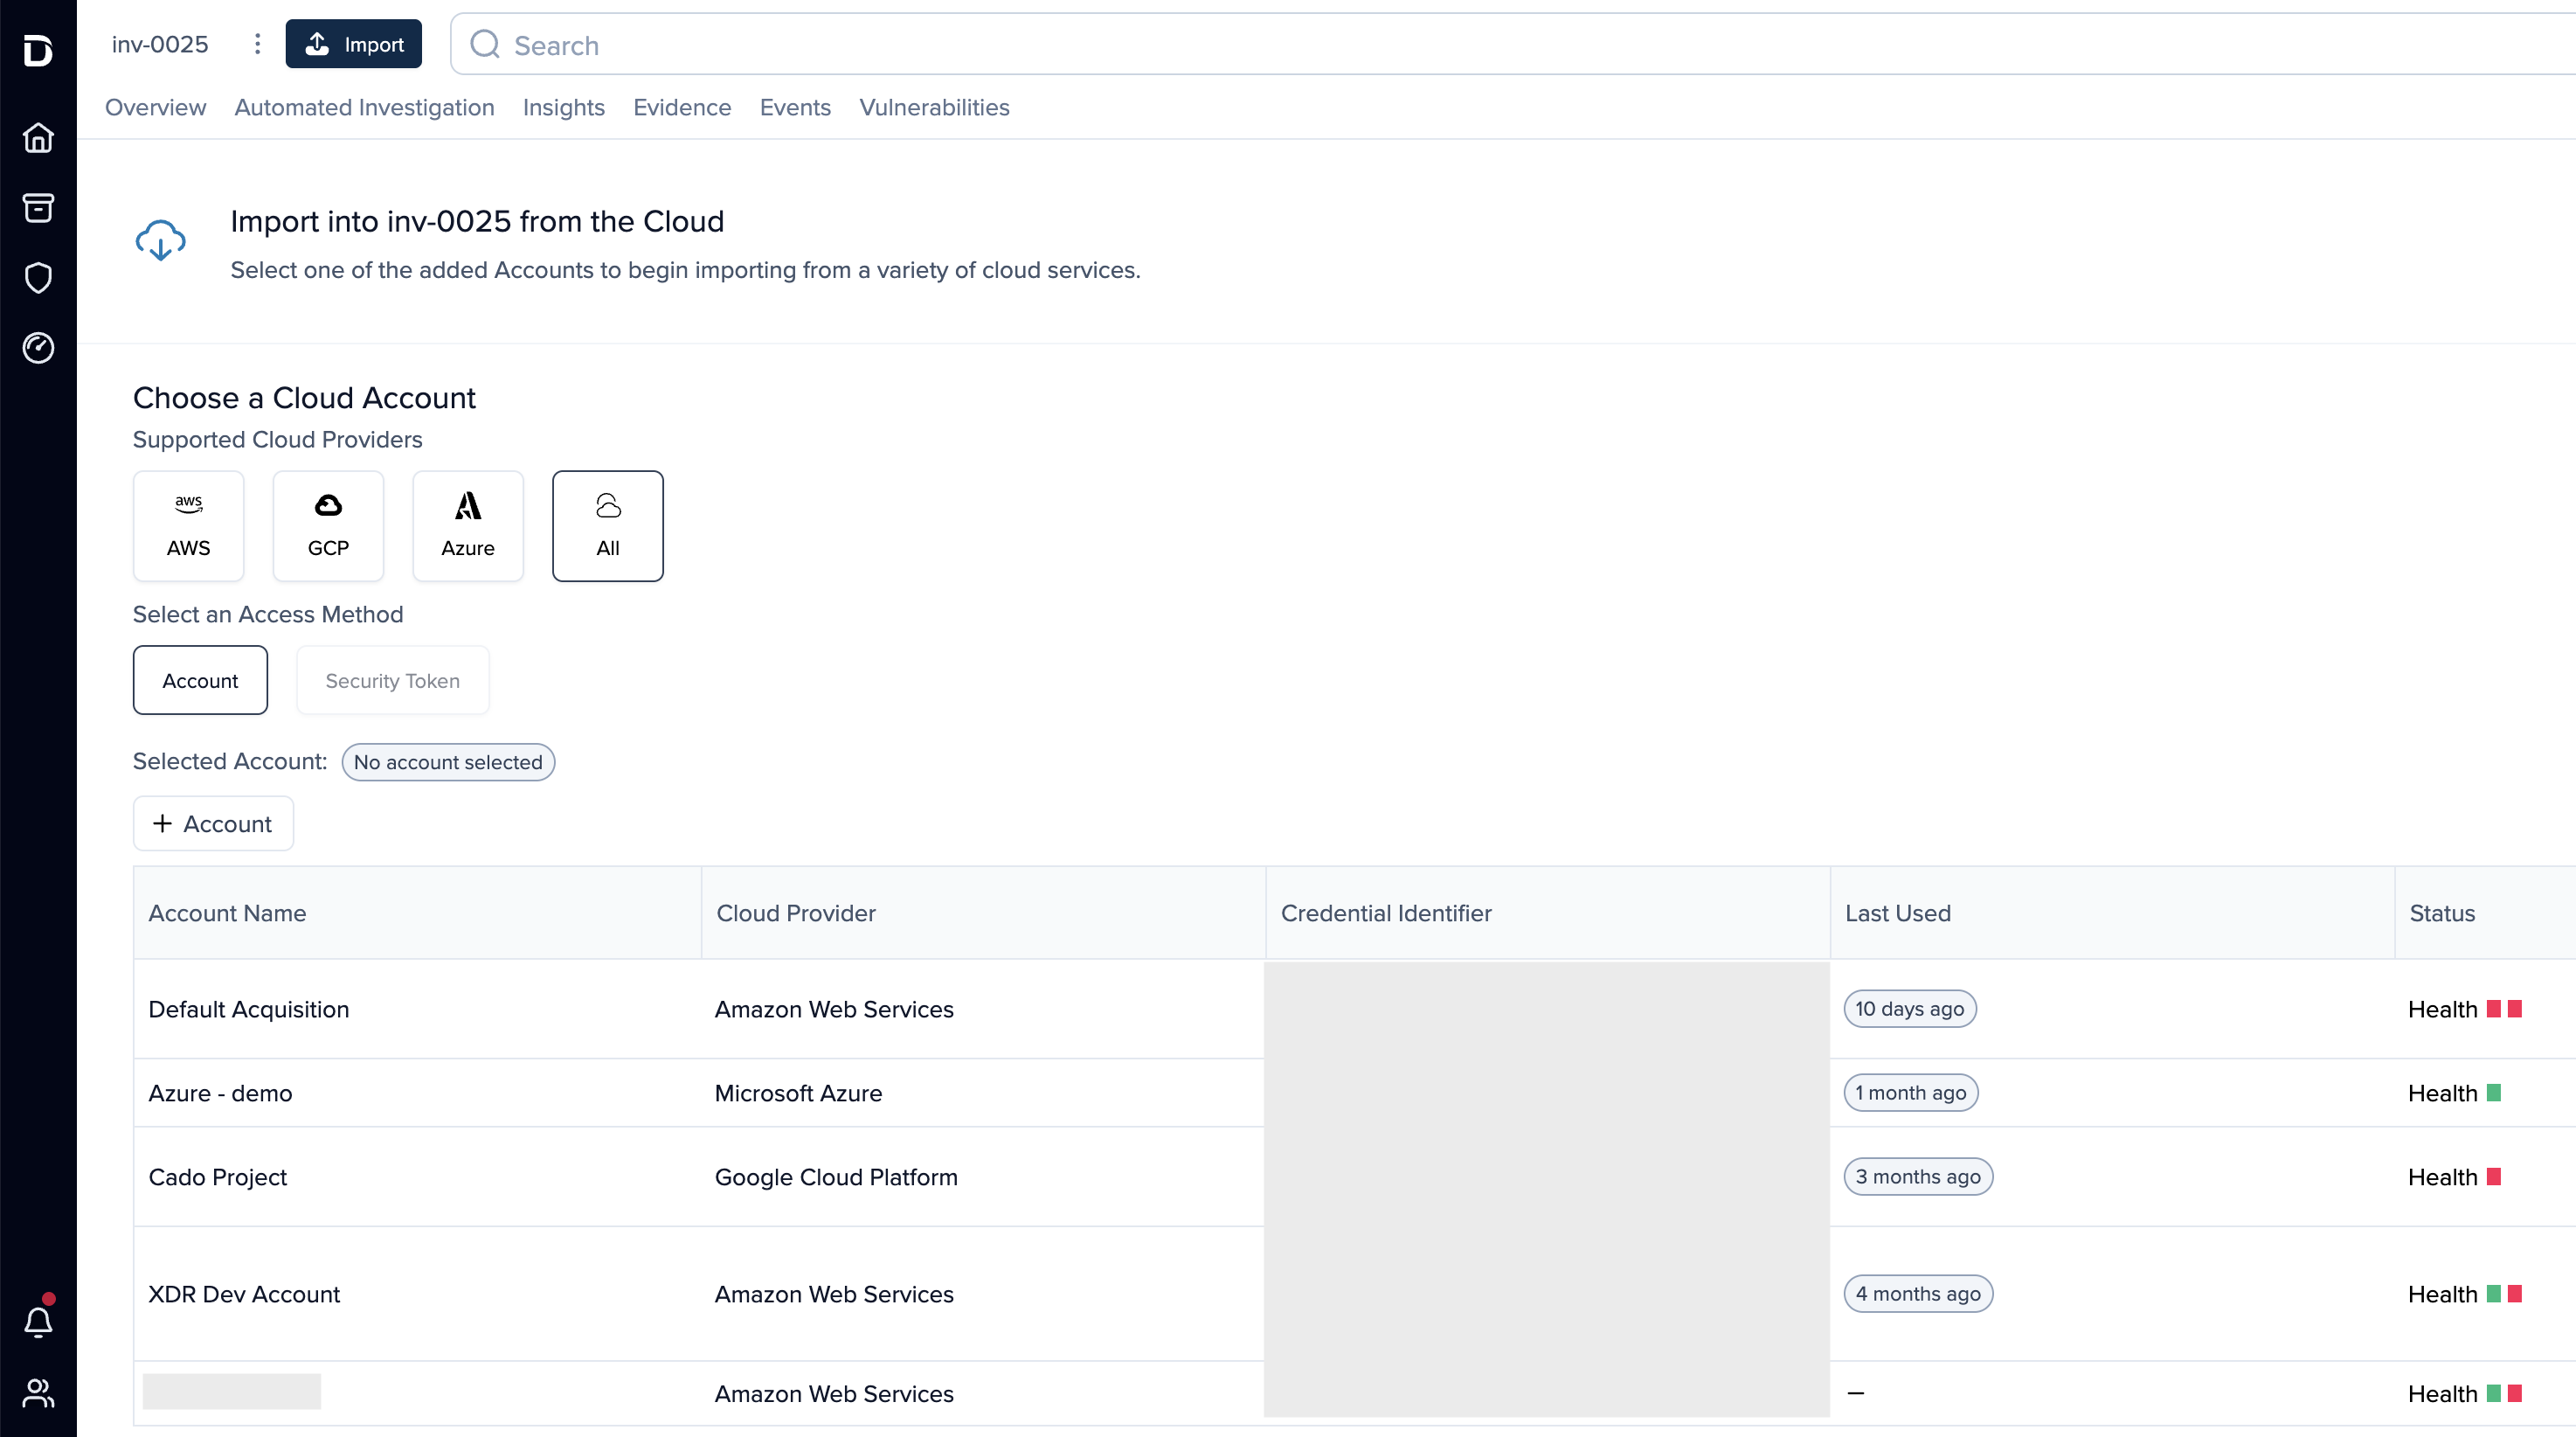
Investigate incidents identified anywhere in the hybrid environment in a single solution, with findings unified in one timeline.
Container & Kubernetes investigations
Perform investigation and response in ephemeral environments, leveraging automation to ensure incident data is captured and preserved before it disappears.
SaaS investigations
Investigate SaaS logs alongside other sources captured across on-premises, cloud, and network assets to understand the scope and impact of malicious activity.
Evidence preservation
Automate the collection, processing, analysis, and preservation of evidence so it’s accessible to every team, every time, before it disappears.
Hear from our customers
“We resolve hundreds of potential incidents in minutes. By assisting analyst investigations, we've been able to drastically increase efficiency by 250%.”
Global Gaming Company
Head of Security Operations
“We have a cloud team that takes countless manual steps to capture and process forensic data...I can’t wait to tell them I can do this in just a few clicks!”
Fortune 500 US Company
DFIR Team Lead
“The fact that I no longer have to wait 24 hours to start a forensics investigation is game changing.”
Top Cybersecurity Consulting Firm
DFIR Manager
Discover the Darktrace difference
Read the solution brief
Demo videos
See it in action
Cloud investigations
Cloud
Cloud detection & response
Cloud
Container investigations
Cloud
SOC triage
Cloud