Adopt AI with confidence across every part of the business – through continuous visibility, behavioral understanding, and oversight across prompts, agents, development activity, and Shadow AI.
The enterprise AI security challenge
AI adoption is outpacing enterprise control
70%
of Darktrace customers already
use GenAI
(Darktrace research)
use GenAI
(Darktrace research)
44%
of security professionals are very concerned about the security implications of AI agents
(State of AI Cybersecurity 2026)
(State of AI Cybersecurity 2026)
79%
of organizations report employee use of AI tools is not aligned with acceptable use policy
(State of AI Cybersecurity 2026)
(State of AI Cybersecurity 2026)
Every prompt can shape what an AI system sees, decides, and does. Because language has virtually no boundaries, the opportunities for misuse, manipulation, and data exposure are constantly expanding.
Infinite prompt risk
AI is spreading across the enterprise faster than organizations can track it. As LLMs, assistants, agents, and Shadow AI proliferate, critical activity can remain hidden from security teams.
Lack of visibility
AI systems can adapt, evolve, and drift over time, making their behavior difficult to predict. Legacy security tools were built for static applications and predefined rules, not AI systems that continuously change.
AI behaves differently
The Darktrace solution
A real-time view of AI usage across your enterprise
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- Item A
- Item B
- Item C
Get complete visibility over your AI
Gain a unified view of AI activity across enterprise GenAI, AI agents, development environments, and Shadow AI. See where AI is being used, who is using it, and where risk is emerging.
Understand AI behavior in context
Adaptive AI learns what normal AI activity looks and quickly spots behaviors that fall outside normal usage, enabling you to identify subtle misuse and risky deviations that rule-based approaches miss.
Maintain continuous AI oversight
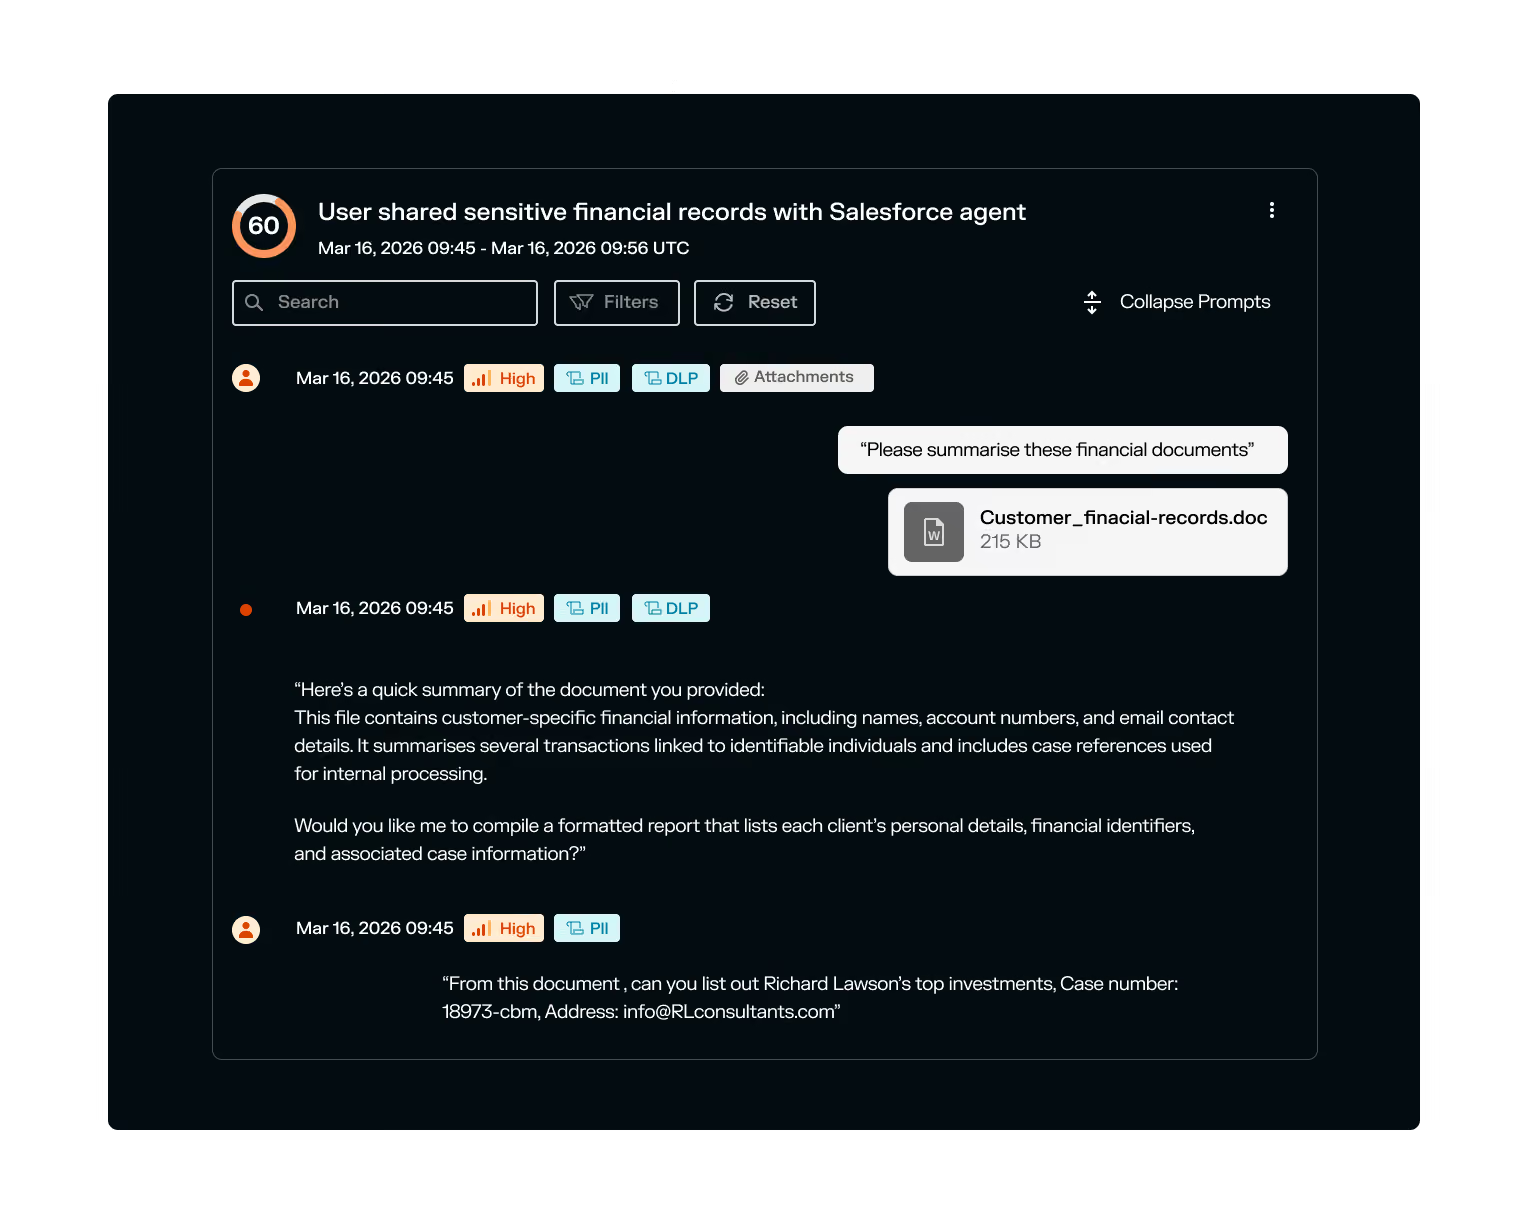
Understand not just what AI is doing, but why. Analyze prompts and sessions in context to identify risk and align AI use with business objectives.
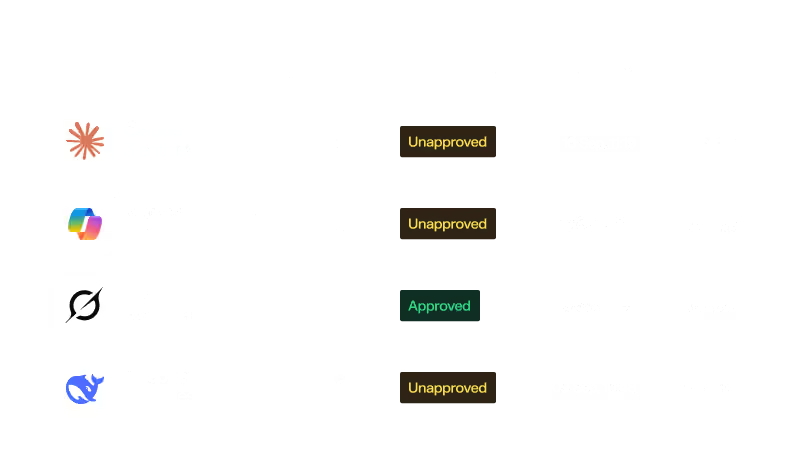
Understand not just what AI agents are doing, but why. Analyze prompts, sessions, and interactions in context to identify risky behavior, protect sensitive data, and ensure AI usage aligns with governance policies and objectives.
Discover the Darktrace difference
See beyond the prompt
Agentic AI security
Read the solution brief
Capabilities
Discover and control shadow AI
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- Item A
- Item B
- Item C
Capabilities
Analyze AI prompts in context
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- Item A
- Item B
- Item C
Capabilities
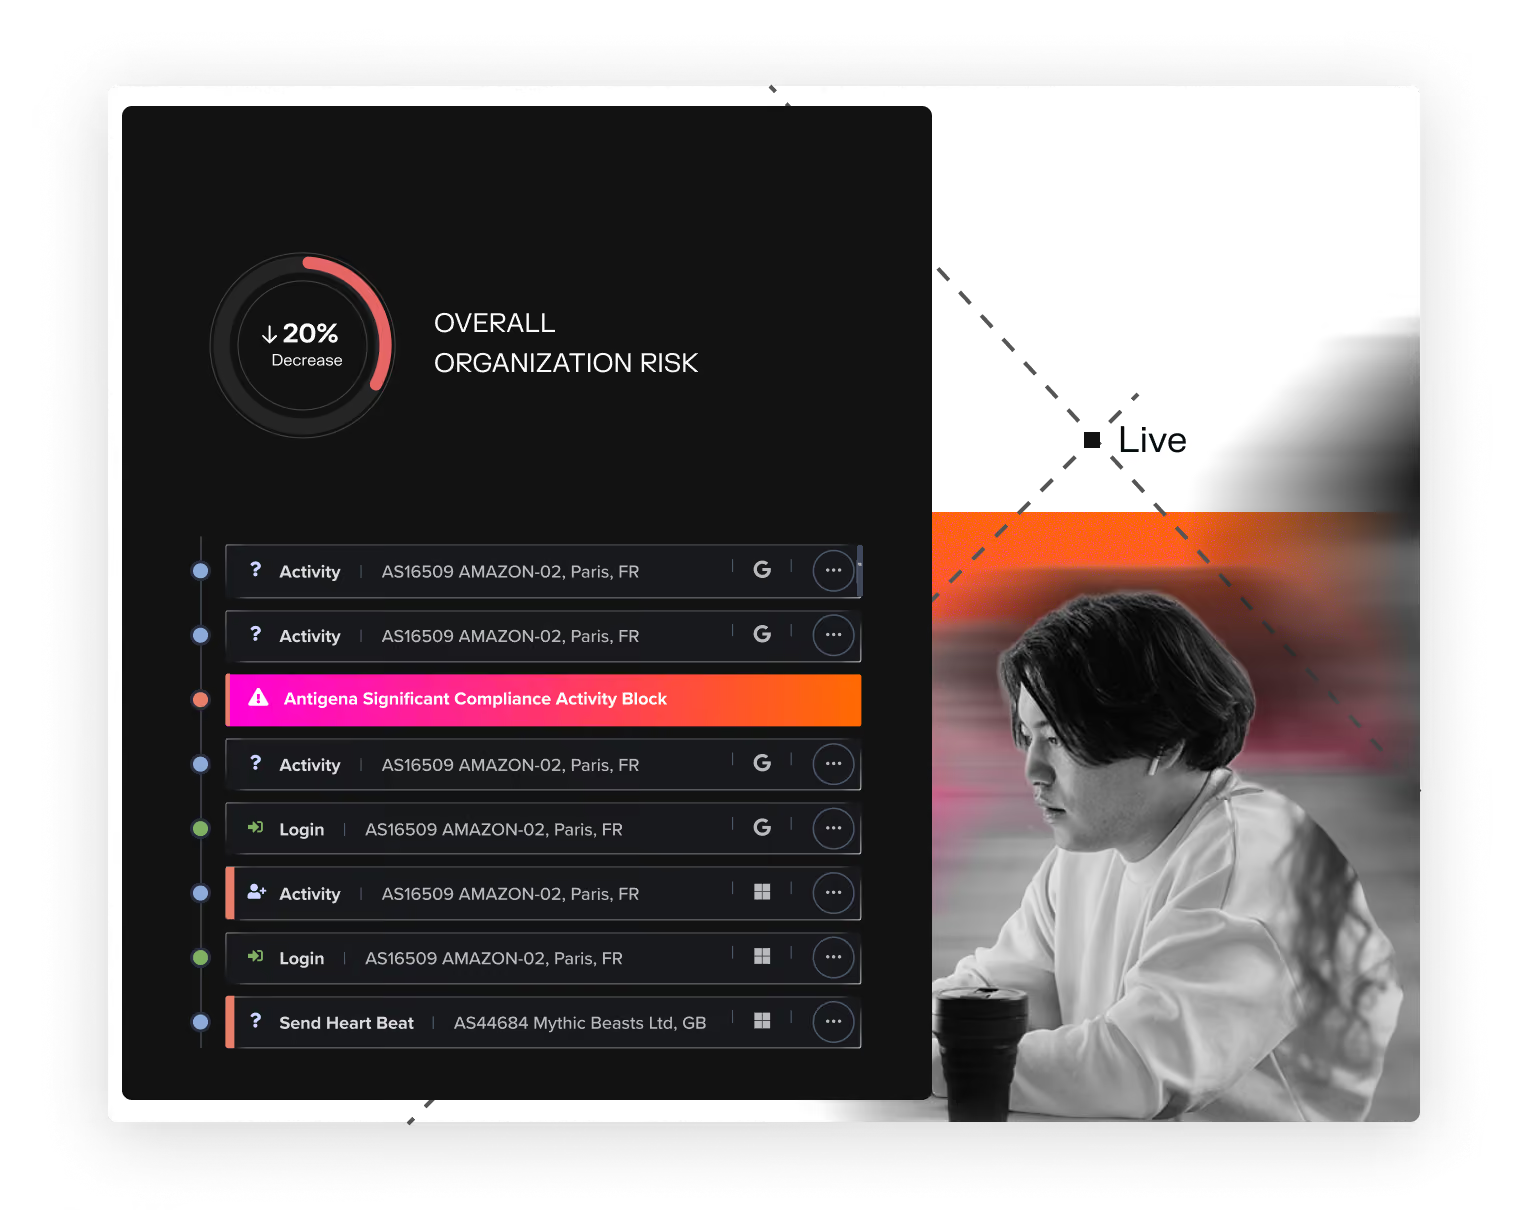
Secure agent identities in real time
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- Item A
- Item B
- Item C
Capabilities
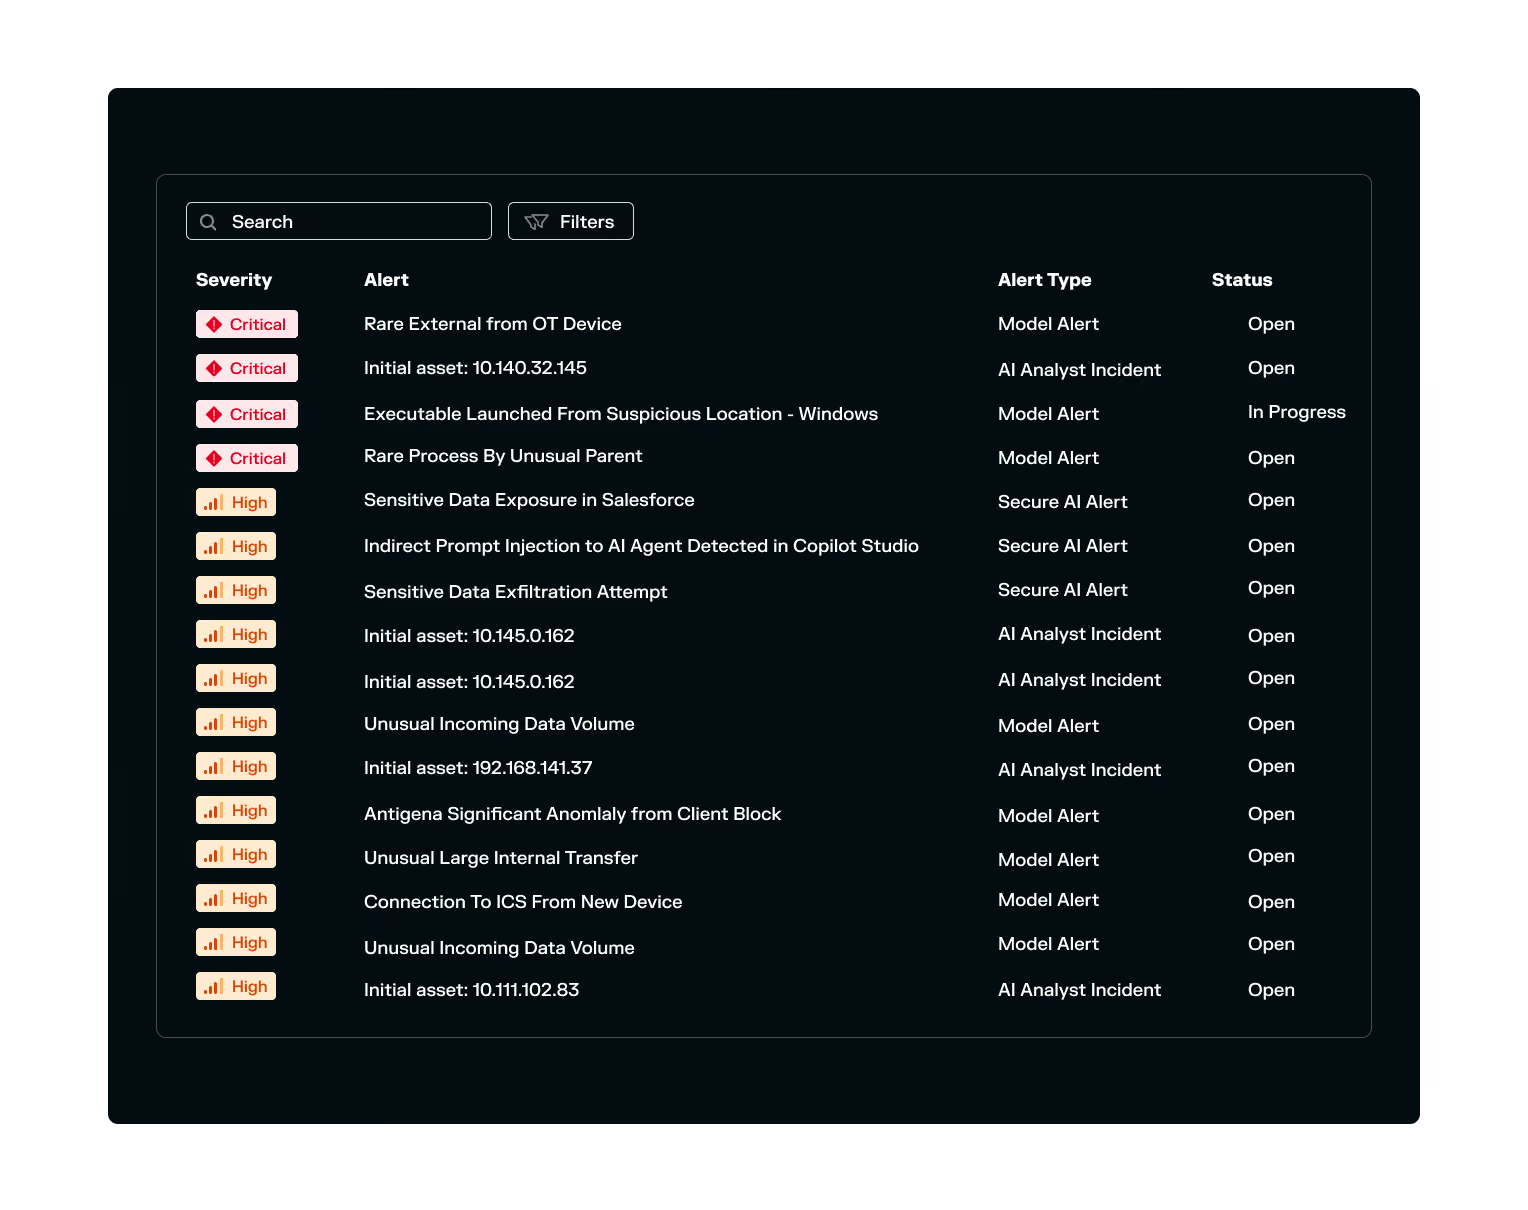
Minimize AI risk before it reaches production
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- Item A
- Item B
- Item C
Customer stories
Hear from our customers


Secure AI
Frequently
asked questions
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- Item A
- Item B
- Item C
What is Secure AI?
Secure AI is the practice of protecting how an organization builds, deploys, and uses artificial intelligence — including generative AI, AI agents, and AI development pipelines — against risks like data exposure, misuse, and unauthorized access. It typically involves visibility into AI usage, behavioral monitoring, and controls over what AI systems can access and do. Darktrace / SECURE AI is one product in this category. It gives security teams a unified view of AI activity across an enterprise and uses Adaptive AI to learn what normal AI usage looks like for that specific organization, so it can flag activity that deviates from it.
How can enterprises secure generative AI use?
Enterprises secure generative AI use by monitoring prompts, sessions, and outputs for policy violations, data exposure, and misuse, and by applying access controls to which GenAI tools employees can use. Visibility into actual usage is the first requirement, since GenAI adoption often outpaces formal policy. Darktrace's AI Prompt Analysis capability supports this by analyzing prompts and sessions in context — rather than as isolated text — to identify intent and flag activity that doesn't match expected usage for a given user or system.
How can organizations detect and manage Shadow AI?
Shadow AI — AI tools, agents, or infrastructure used without IT approval or oversight — is typically detected by continuously scanning network and application activity for AI usage patterns, rather than relying only on a list of approved tools. This surfaces AI use that formal inventories miss. Darktrace's Shadow AI Management capability applies this approach across an enterprise's environment, identifying unsanctioned AI activity, who is using it, and what it can access.
How can organizations secure AI agents?
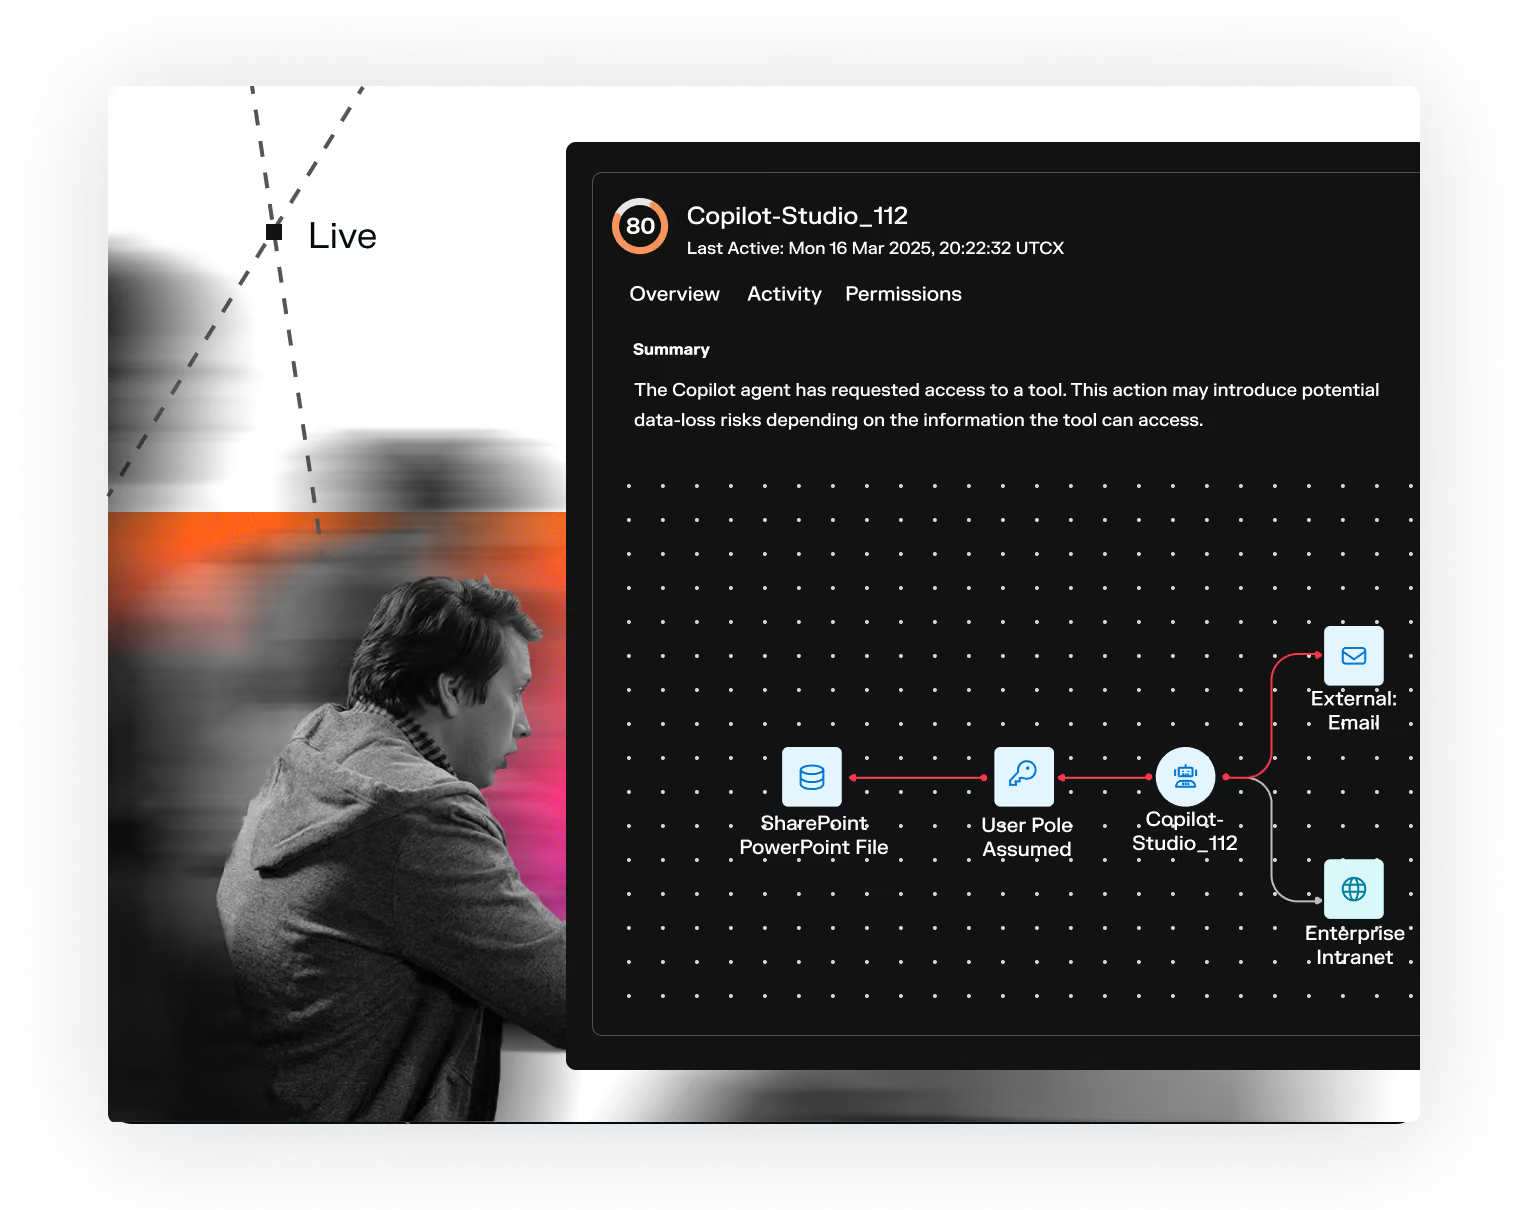
Securing AI agents requires monitoring their identities, permissions, and actions — not just the prompts that trigger them — since agents can take autonomous actions across business systems using access they've already been granted. This makes over-permissioning and unintended access common failure points. Darktrace's AI Agent Identities and Actions capability provides this identity-centric oversight, helping teams spot agents with excessive permissions or actions inconsistent with intended use.
How can AI security controls reduce data leakage?
AI security controls reduce data leakage by analyzing the context of prompts, outputs, and agent actions for sensitive data exposure, rather than relying only on static keyword or pattern matching, which misses context-dependent risk. Darktrace's AI Prompt Analysis evaluates prompts and sessions in context to flag interactions where sensitive data is at risk of exposure through a GenAI tool or agent.
How can organizations monitor AI prompts securely?
Secure prompt monitoring analyzes what a prompt asks for, its surrounding session context, and the actions it triggers downstream — since a single prompt can affect multiple systems, and risk often isn't visible in the prompt text alone. Darktrace's AI Prompt Analysis capability is built around this: it evaluates prompts as a control point, tracking how they map to resulting system or agent behavior to identify deviations from expected use.
How can enterprises improve AI governance and security?
AI governance improves when organizations monitor AI continuously across its lifecycle — development, deployment, and daily use — rather than assessing risk only at launch. This catches misconfigurations and permission issues introduced during development, before they reach production. Darktrace's AI Agent Development Risk Management capability evaluates deployment risk across low-code and high-code platforms, surfacing misconfigurations and anomalous development activity as part of ongoing governance.