Want to learn more about the resource?
How to Secure AI in the Enterprise
Download the AI Security Guide for Secure AI Adoption
Get practical guidance for securing LLM deployments, AI-integrated workflows, and agent-based systems, including the controls security teams need to manage AI risk.

Takes 10 seconds
Download now
100+
Darktrace resources dowloaded in last 30 days
White Paper
How to Secure AI in the Enterprise
How to Secure AI in the Enterprise: A Practical Framework
Most security leaders still lack a clear definition of what "securing AI" actually covers. Broader standards like ISO/IEC 42001 set governance principles but stop short of showing you how to operationalize AI security day to day. This vendor-neutral guide fills that gap.
Why securing AI systems is harder than it looks
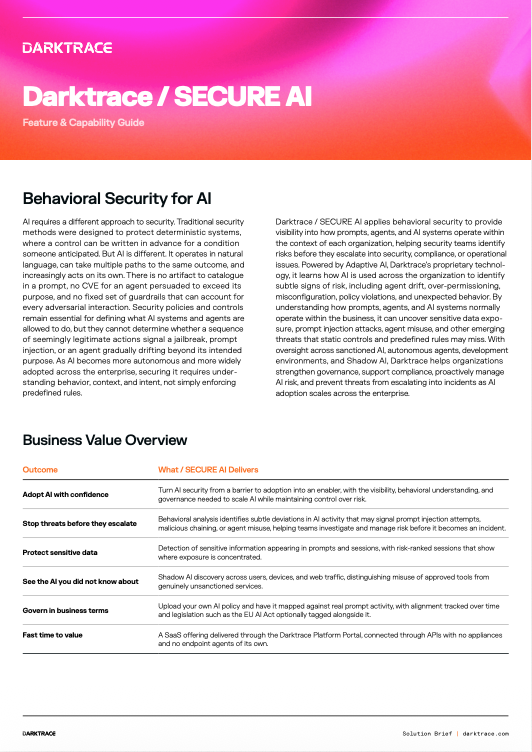
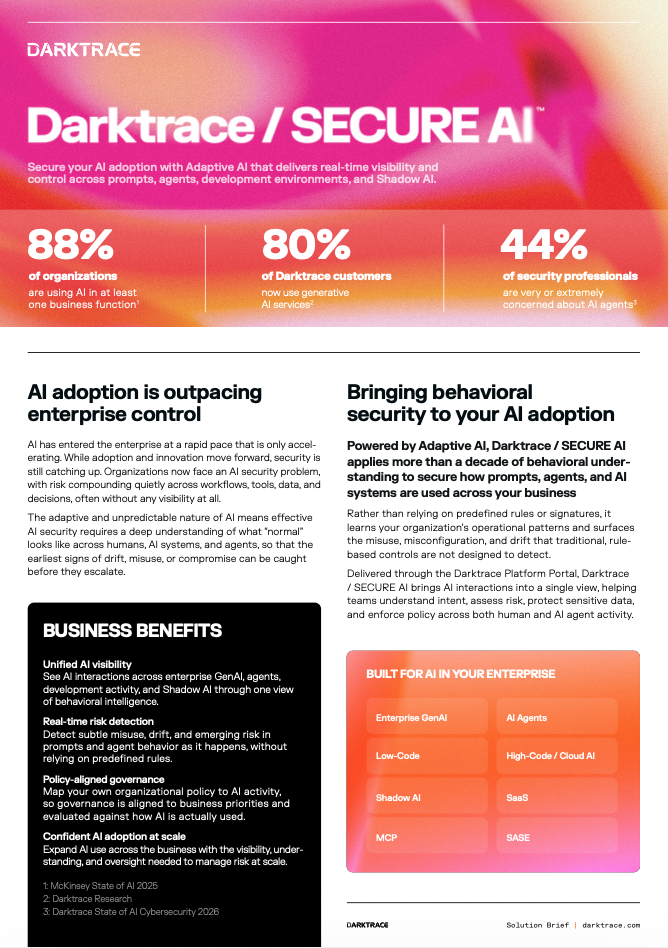
AI enters your organization through more doors than most teams track: AI-enabled SaaS, embedded vendor features, cloud services, homegrown models, and shadow AI nobody approved. Every model, dataset, and agent — plus the APIs and third-party integrations behind them — widens the attack surface and opens fresh paths to compromise.
An AI risk management framework built on five categories
The guide maps each AI security risk to the security function that addresses it:
- Misuse and emergent behaviors — malicious prompt analysis, unintended use cases, prompt history access, hallucinated output
- Monitoring AI in operation — AI agent security across real-time actions, outbound connections, MCP server calls, agent state capture, and AI data transmission
- Development and infrastructure — AI application security through secure configuration, agent architecture analysis, IaC and AI-generated code scanning
- AI supply chain — shadow AI, supplier AI use, securing AI models and verifying training data provenance
- Readiness and oversight — reporting, AI pentesting, red and purple teaming, security team training
Get the full framework
Download the guide for the complete risk-to-control mapping across all five categories, practical guidance on preventing AI data exposure, and a board-ready way to frame AI security around trust, accountability, and resilience.
Built on 10+ years of applying AI to cybersecurity across approximately 10,000 organizations — and Darktrace is one of the first cybersecurity companies certified to ISO 42001.
Download the guide — takes 10 seconds.
Explore related resources
See how others stay one step ahead with Darktrace
10,000
Darktrace customers


Your data. Our AI.
Elevate your Cybersecurity with Darktrace AI
