Key takeaways
- Ransomware is a multi-stage attack that requires detecting and containing malicious behavior throughout the attack lifecycle rather than focusing only on malware signatures or the encryption stage.
- Ransomware operators can enter through phishing, exposed services, stolen credentials, and legitimate administrative tools, then move laterally and exfiltrate data before encryption, making behavior-based detection increasingly important.
- Security teams should evaluate whether defenses can connect signals across initial access, command and control, lateral movement, data exfiltration, and encryption rather than treating each stage as an isolated event.
- Behavioral detection, AI-led investigation, and targeted autonomous response can help security teams identify anomalous activity earlier and contain ransomware while limiting unnecessary disruption to normal business operations.
Ransomware gets its name by commandeering and holding assets ransom, extorting their owner for money in exchange for discretion and full cooperation in returning exfiltrated data and providing decryption keys to allow business to resume.
In this series, we break down this huge topic step by step. Ransomware is a multi-stage problem, requiring a multi-stage solution that autonomously and effectively contains the attack at any stage. Read on to discover how Self-Learning AI and Autonomous Response stops ransomware in its tracks.
Stage 1: How ransomware attacks begin through email
Email-based ransomware attacks often begin with a convincing message designed to steal credentials, deliver malware, or trigger a malicious action. Behavioral AI can identify deviations in sender, recipient, content, and account activity, helping detect compromised suppliers and previously unseen phishing infrastructure that signature- and reputation-based controls may miss. Well-researched, targeted, legitimate-looking emails are aimed at employees attempting to solicit a reaction: a click of a link, an opening of an attachment, or persuading them to divulge credentials or other sensitive information.
Gateways: Stops what has been seen before
Most conventional email tools rely on past indicators of attack to try and spot the next threat. If an email comes in from a blocklisted IP address or email domain, and uses known malware that has previously been seen in the wild, the attack may be blocked.
But the reality is, attackers know the majority of defenses take this historical approach, and so constantly update their attack infrastructure to bypass these tools. By buying new domains for a few pennies each, or creating bespoke malware with just small adaptions to the code, they can outpace and outsmart the legacy approach taken by a typical email gateway.
Real-world example: Supply chain phishing attack
By contrast, Darktrace’s evolving understanding of ‘normal’ for every email user in the organization enables it to detect subtle deviations that point to a threat – even if the sender or any malicious contents of the email are unknown to threat intelligence. This is what enabled the technology to stop an attack that recently targeted McLaren Racing, with emails sent to a dozen employees in the organization each containing a malicious link. This possible precursor to ransomware bypassed conventional email tools – largely because it was sent from a known supplier – however Darktrace recognized the account hijack and held the email back.

Stage 2: How ransomware exploits servers and remote access
Server-side ransomware intrusion typically exploits exposed services, vulnerable systems, stolen credentials, or poorly secured remote access such as RDP. Because attackers may use legitimate credentials and administration tools, behavioral detection is needed to identify unusual access patterns, rare external connections, and activity that does not fit the affected server’s normal behavior.
A number of vulnerabilities against such Internet-facing servers and systems have been disclosed this year, and for attackers, targeting and exploiting public-facing infrastructure is easier than ever – scanning the Internet for vulnerable systems is made simple with tools like Shodan or MassScan.
Attackers may also achieve initial intrusion via RDP brute-forcing or stolen credentials, with attackers often reusing legitimate credentials from previous data dumps. This has much higher precision and is less noisy than a classic brute-force attack.
A lot of ransomware attacks use RDP as an entry vector. This is part of a wider trend of ‘Living off the Land’: using legitimate off-the-shelf tools (abusing RDP, SMB1 protocol, or various command line tools WMI or Powershell) to blur detection and attribution by blending in with typical administrator activity. Ensuring that backups are isolated, configurations are hardened, and systems are patched is not enough – real-time detection of every anomalous action is needed.
Antivirus, firewalls and SIEMs
In cases of malware downloads, endpoint antivirus will detect these if, and only if, the malware has been seen and fingerprinted before. Firewalls typically require configuration on a per-organization basis, and often need to be modified based on the needs of the business. If the attack hits the firewall where a rule or signature does not match it, again, it will bypass the firewall.
SIEM and SOAR tools also look for known malware being downloaded, leverage pre-programmed rules and use pre-programmed responses. While these tools do look for patterns, these patterns are defined in advance, and this approach relies on a new attack to have sufficiently similar traits to attacks that have been seen before.
Real-world example: Dharma ransomware
Darktrace detected a targeted Dharma ransomware attack against a UK organization exploiting an open RDP connection through Internet-facing servers. The RDP server began receiving a large number of incoming connections from rare IP addresses on the Internet. It is highly likely that the RDP credential used in this attack had been compromised at a previous stage – either via common brute-force methods, credential stuffing attacks, or phishing. Indeed, a technique growing in popularity is to buy RDP credentials on marketplaces and skip to initial access.

Figure 2: The model breaches that fired over the course of this attack, including anomalous RDP activity
Unfortunately, in this case, without Autonomous Response installed, the Dharma ransomware attack continued until its final stages, where the security team were forced into the heavy-handed and disruptive action of pulling the plug on the RDP server midway through encryption.
Stage 3: How ransomware establishes command and control
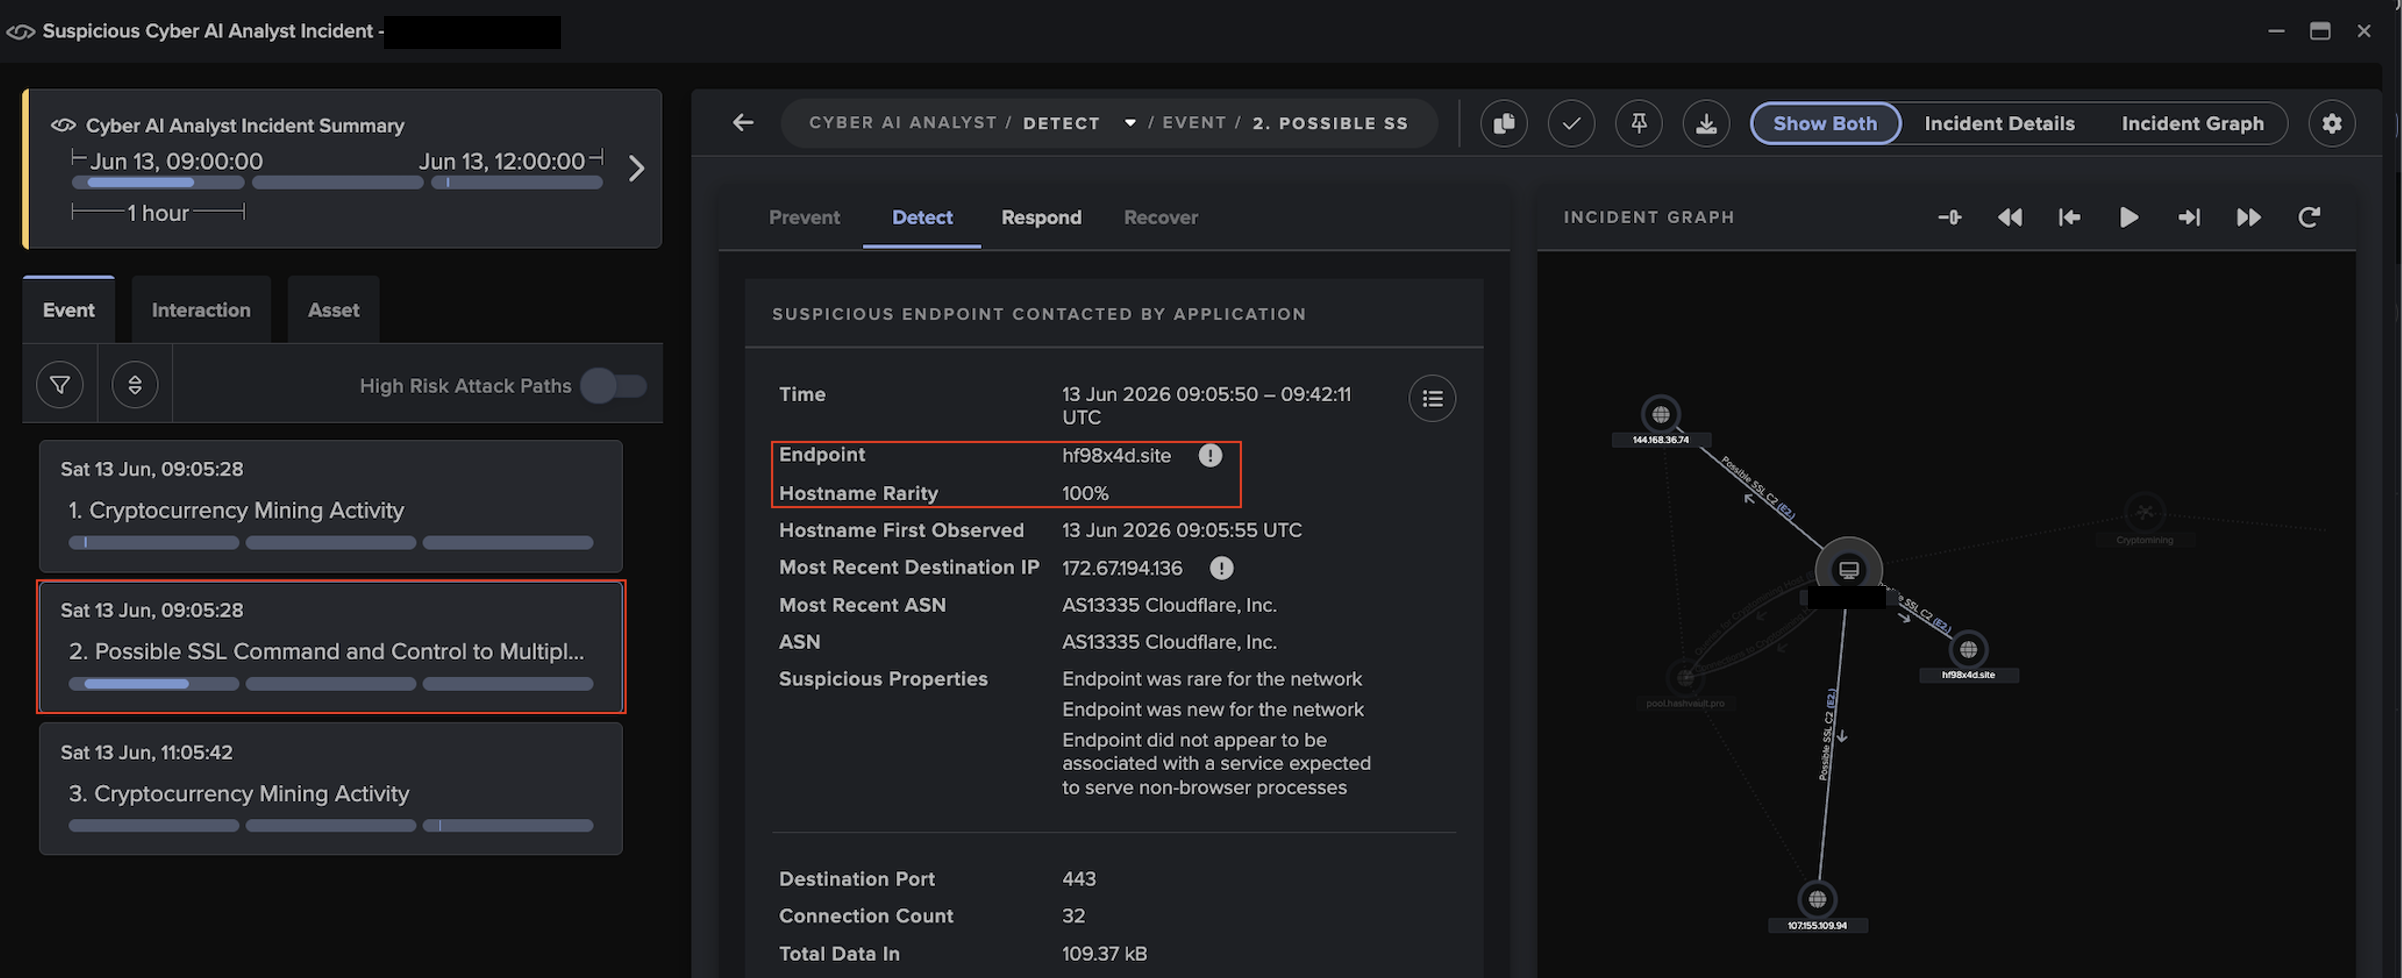
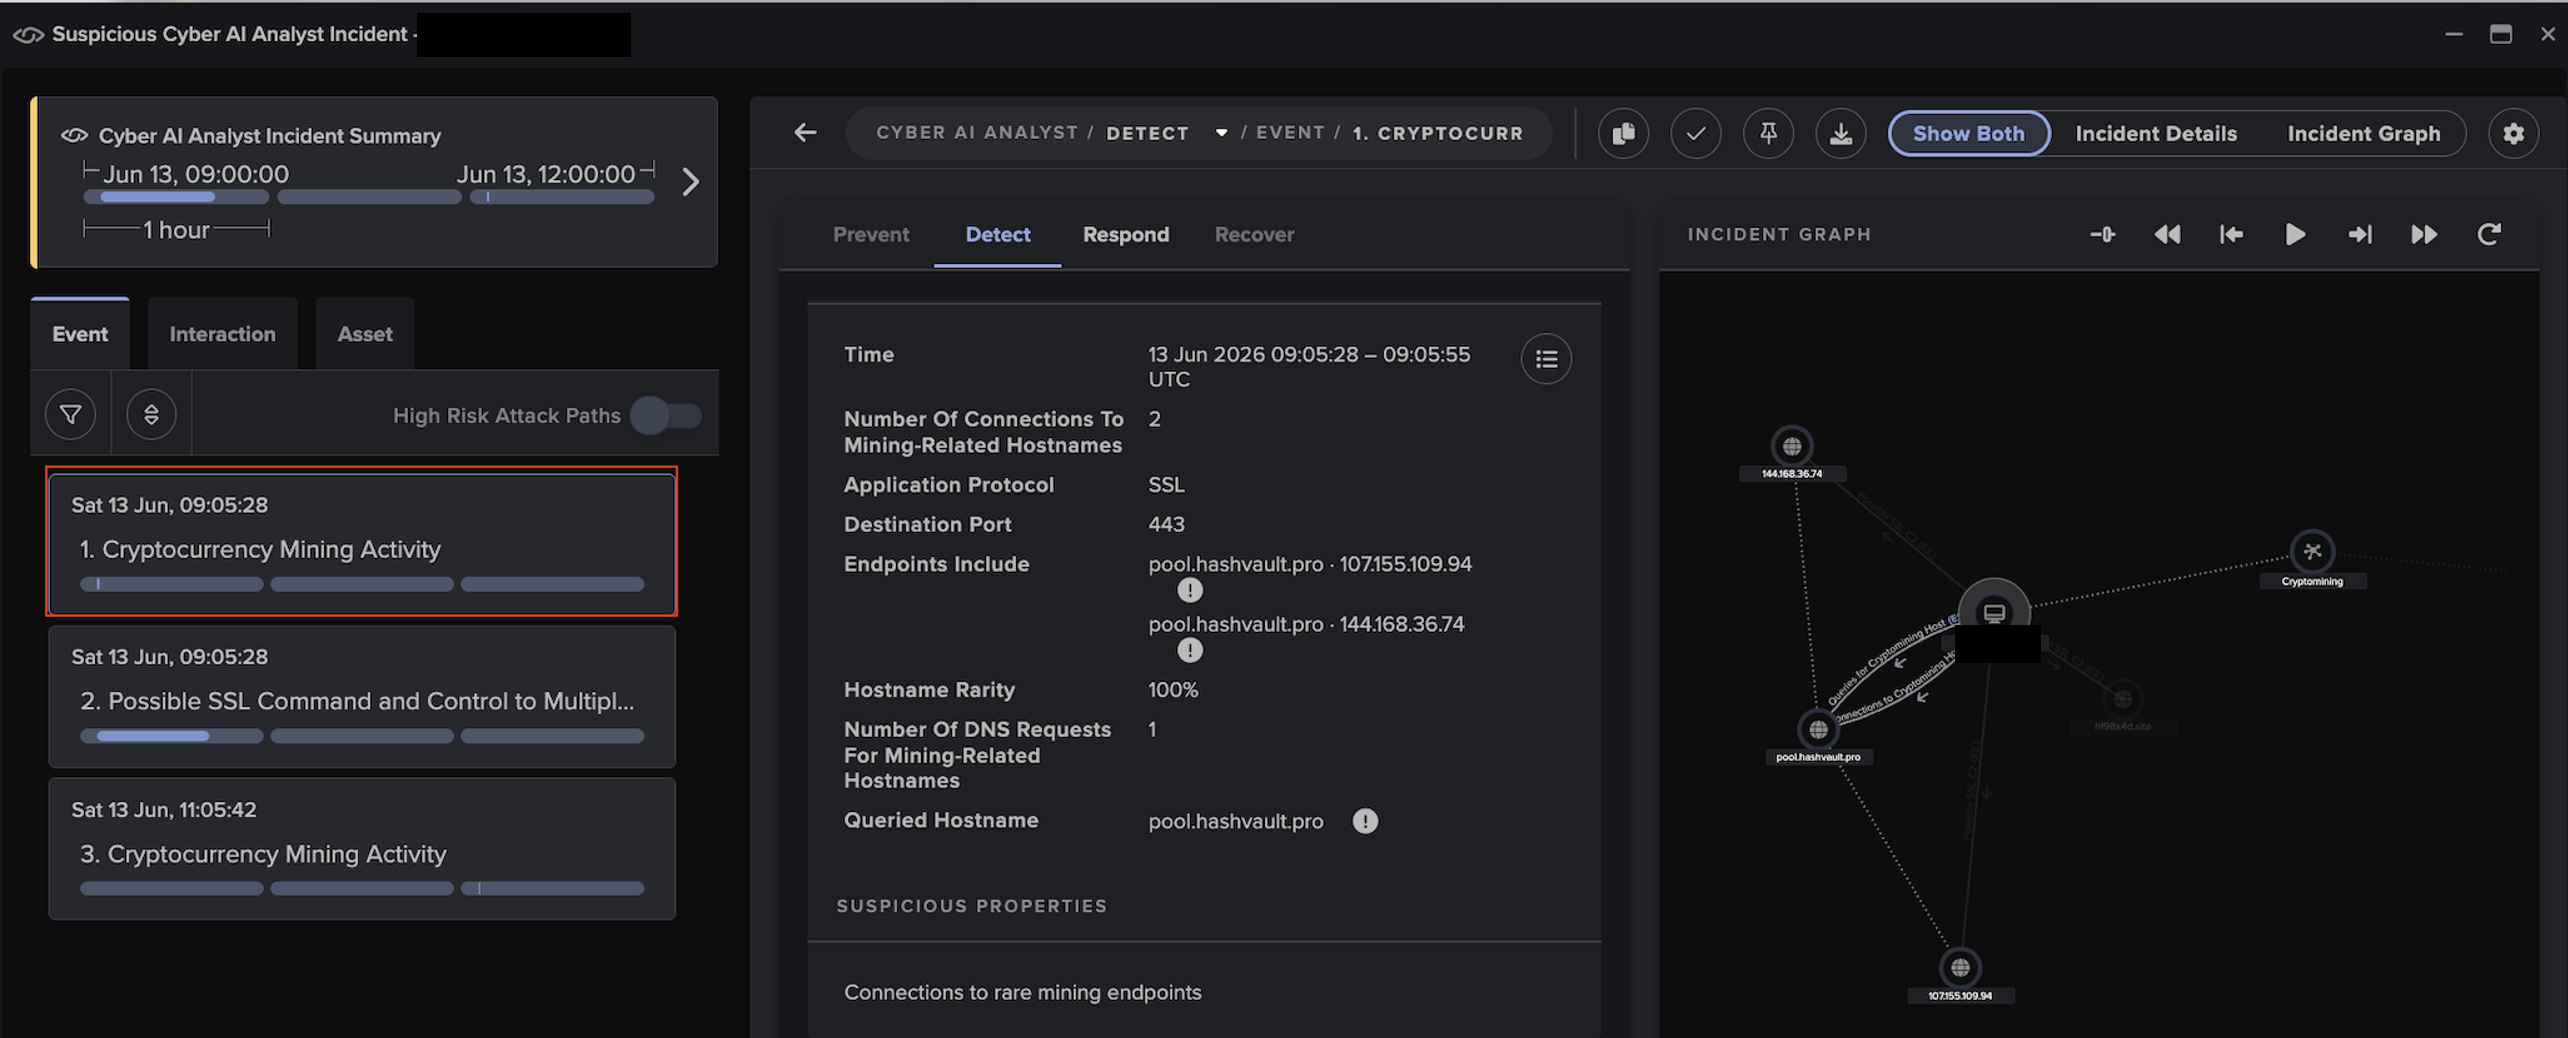
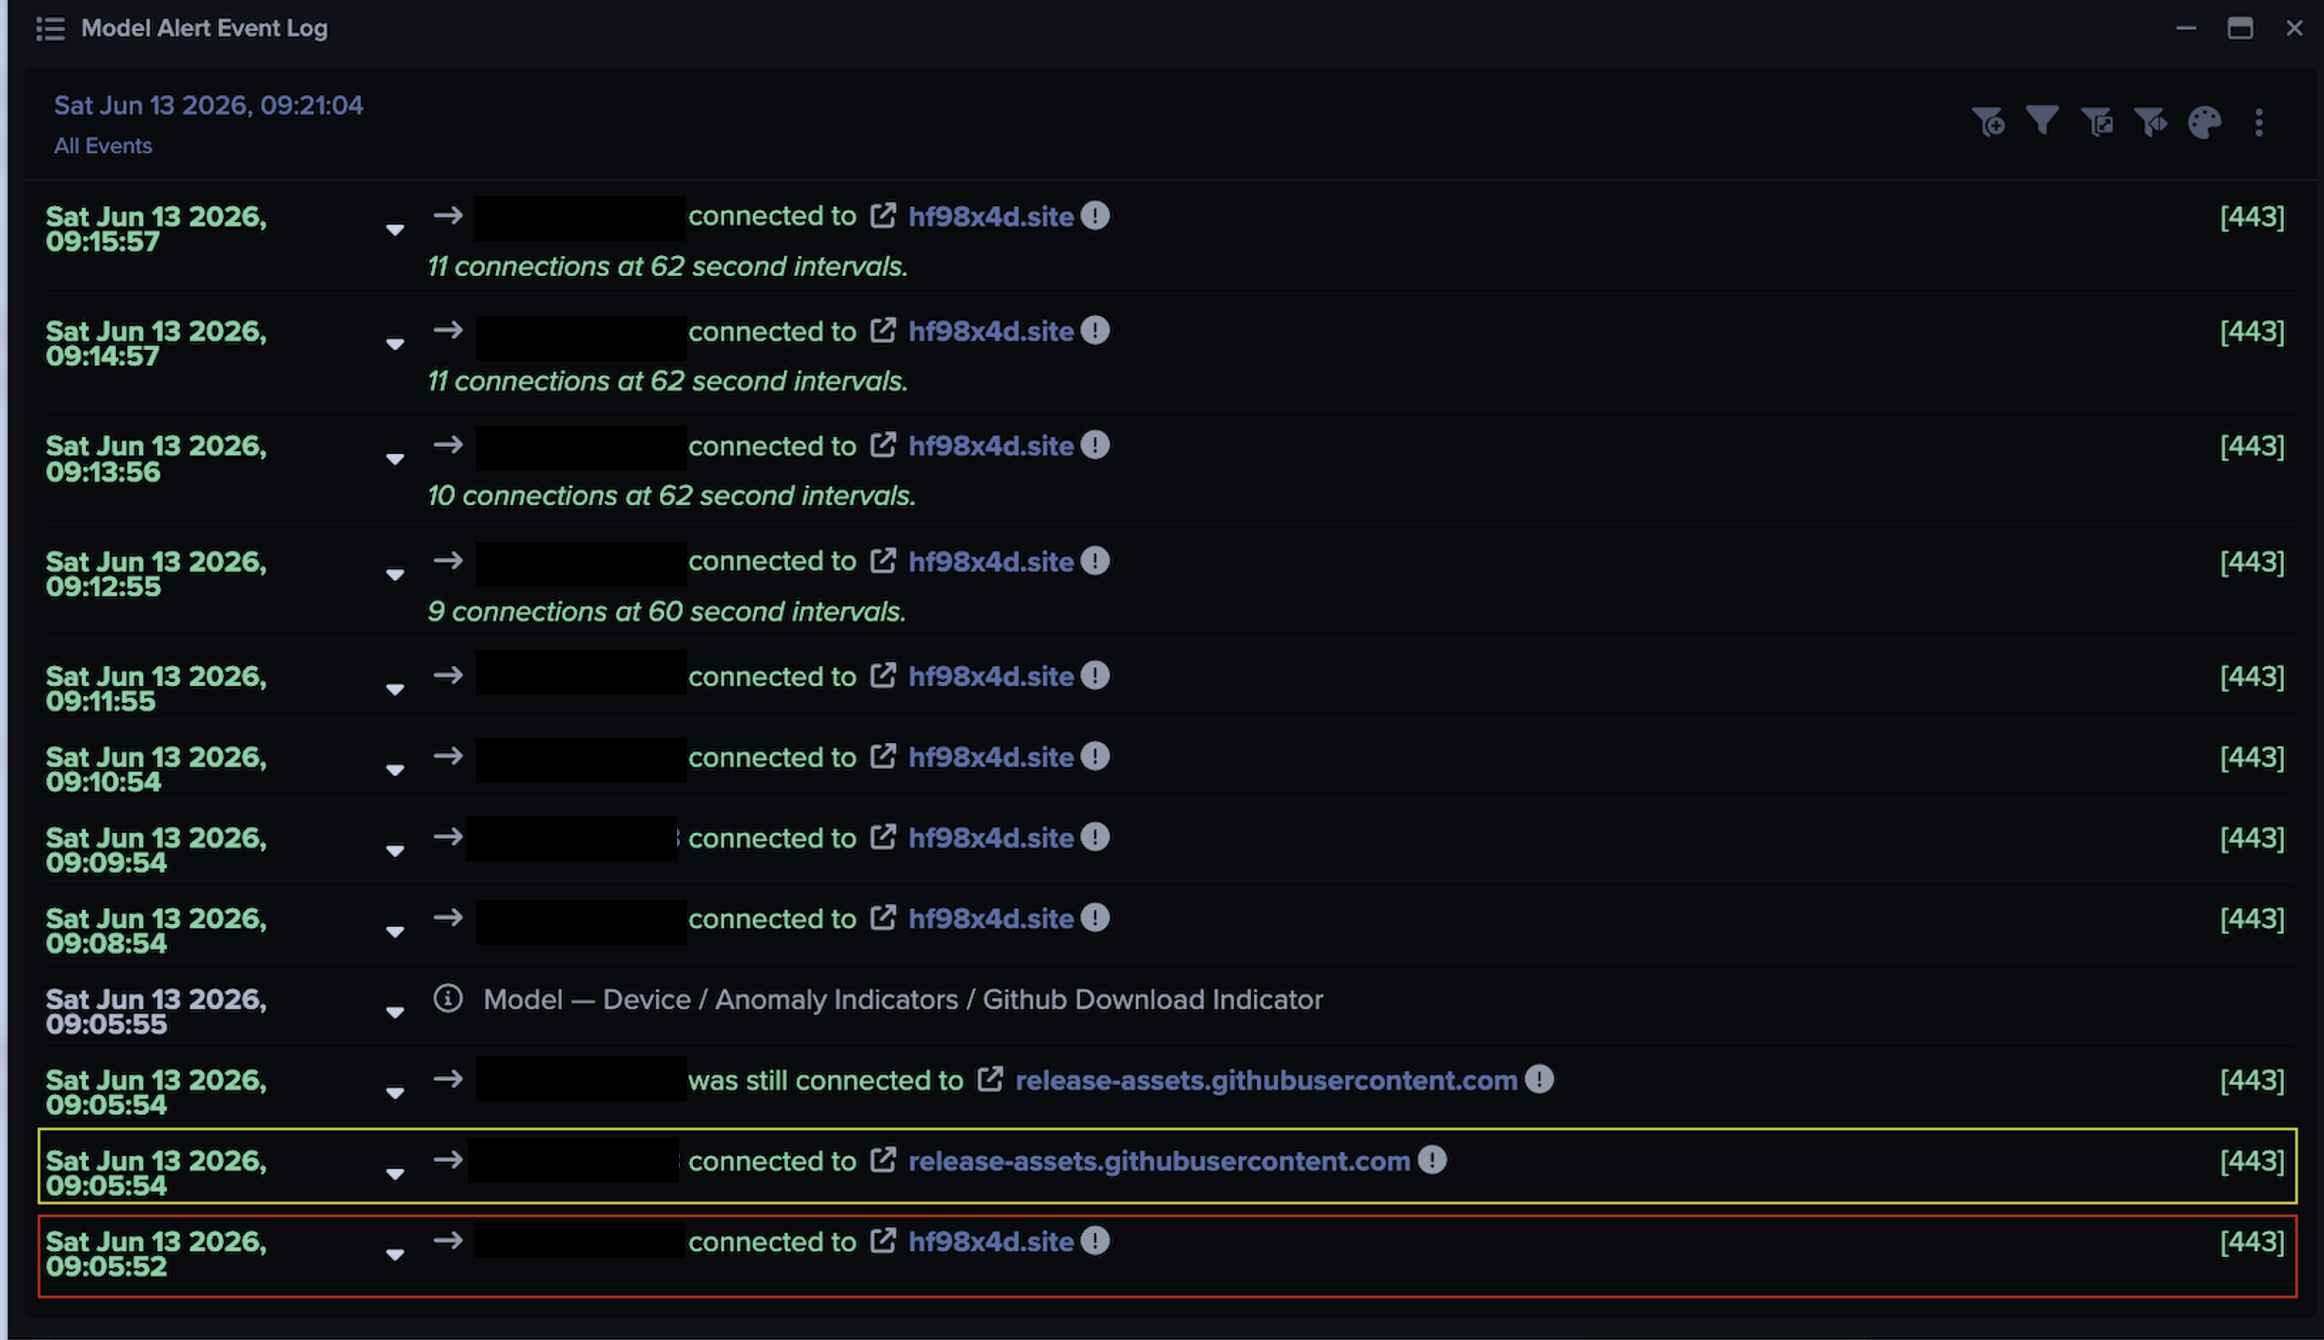
After gaining access, ransomware operators establish command-and-control channels to manage compromised devices, deliver additional tools, and prepare for later stages. AI can identify C2 activity by correlating weak signals such as rare destinations, unusual connection timing, unexpected downloads, and behavior that differs from the organization’s established patterns.
Attackers can adapt malware functionality with an assortment of ready-made plug-ins, allowing them to lie low inside the business undetected. More modern and sophisticated ransomware is able to adapt by itself to the surrounding environment, and operate autonomously, blending in to regular activity even when cut off from its command and control server. These ‘self-sufficient’ ransomware strains pose a big problem for traditional defenses reliant on stopping threats solely on the grounds of its malicious external connections.
Viewing connections in isolation vs understanding the business
Conventional security tools like IDS and firewalls tend to look at connections in isolation rather than in the context of previous and potentially relevant connections, making command and control very difficult to spot.
IDS and firewalls may block ‘known-bad’ domains or use some geo-blocking, but this is where an attacker would likely leverage new infrastructure.
These tools also don’t tend to analyze for things like the periodicity, such as whether a connection is beaconing at a regular or irregular interval, or the age and rarity of the domain in the context of the environment.
With Darktrace’s evolving understanding of the digital enterprise, suspicious C2 connections and the downloads which follow them are spotted, even when conducted using regular programs or methods. The AI technology correlates multiple subtle signs of threat – a small subset of which includes anomalous connections to young and/or unusual endpoints, anomalous file downloads, incoming remote desktop, and unusual data uploads and downloads.
Once they are detected as a threat, Darktrace's Autonomous Response halts these connections and downloads, while allowing normal business activity to continue.
Real-world example: WastedLocker attack
When a WastedLocker ransomware attack hit a US agricultural organization, Darktrace immediately detected the initial unusual SSL C2 activity (based on a combination of destination rarity, JA3 unusualness and frequency analysis). Darktrace (on this occasion configured in passive mode, and therefore not granted permission to take autonomous action) suggested instantly blocking the C2 traffic on port 443 and parallel internal scanning on port 135.

When beaconing was later observed to bywce.payment.refinedwebs[.]com, this time over HTTP to /updateSoftwareVersion, Darktrace escalated its response by blocking the further C2 channels.

Stage 4: How ransomware moves laterally through a network
Ransomware moves laterally as attackers scan the environment, access additional devices, obtain higher privileges, and search for valuable systems and data. Behavioral AI can detect unusual SMB, RDP, SSH, scanning, and credential activity, while targeted autonomous response can restrict suspicious connections before the intrusion spreads further.
Modern ransomware has built-in functions that allow it to search automatically for stored passwords and spread through the network. More sophisticated strains are designed to build themselves differently in different environments, so the signature is constantly changing and it’s harder to detect.
Legacy tools: A blunt response to known threats
Because they rely upon static rules and signatures, legacy solutions struggle to prevent lateral movement and privilege escalation without also impeding essential business operations. Whilst in theory, an organization leveraging firewalls and NAC internally with proper network segmentation and a perfect configuration could prevent cross-network lateral movement, maintaining a perfect balance between protective and disruptive controls is near impossible.
Some organizations rely on Intrusion Prevent Systems (IPS) to deny network traffic when known threats are detected in packets, but as with previous stages, novel malware will evade detection, and this requires the database to be constantly updated. These solutions also sit at the ingress/egress points, limiting their network visibility. An Intrusion Detection System (IDS) may sit out-of-line, but doesn’t have response capabilities.
A self-learning approach
Darktrace’s AI learns ‘self’ for the organization, enabling it to detect suspicious activity indicative of lateral movement, regardless of whether the attacker uses new infrastructure or ‘lives off the land’. Potential unusual activity that Darktrace detects includes unusual scanning activity, unusual SMB, RDP, and SSH activity. Other models that fire at this stage include:
- Suspicious Activity on High-Risk Device
- Numeric EXE in SMB Write
- New or Uncommon Service Control
Autonomous Response then takes targeted action to stop the threat at this stage, blocking anomalous connections, enforcing the infected device’s ‘pattern of life’, or enforcing the group ‘pattern of life’ – automatically clustering devices into peer groups and preventing a device from doing anything its peer group hasn’t done.
Where malicious behavior persists, and only if necessary, Darktrace will quarantine an infected device.
Real-world example: Unusual chain of RDP connections
At an organization in Singapore, one compromised server led to the creation of a botnet, which began moving laterally, predominantly by establishing chains of unusual RDP connections. The server then started making external SMB and RPC connections to rare endpoints on the Internet, in an attempt to find further vulnerable hosts.
Other lateral movement activities detected by Darktrace included the repeated failing attempts to access multiple internal devices over the SMB file-sharing protocol with a range of different usernames, implying brute-force network access attempts.

Stage 5: How ransomware exfiltrates data before encryption
Many ransomware attacks steal data before encryption so attackers can threaten disclosure as well as operational disruption. Behavioral detection can surface unusual transfers, rare cloud-storage destinations, and low-and-slow exfiltration that may remain within static volume thresholds, giving defenders an opportunity to contain the attack before double extortion succeeds.
Modern ransomware variants also look for cloud file storage repositories such as Box, Dropbox, and others.
Many of these incidents aren’t public, because if IP is stolen, organizations are not always legally required to disclose it. However, in the case of customer data, organizations are obligated by law to disclose the incident and face the additional burden of compliance files – and we’ve seen these mount in recent years (Marriot, $23.8 million; British Airways, $26 million; Equifax, $575 million). There’s also the reputational blow associated with having to inform customers that a data breach has occurred.
Legacy tools: The same old story
For those that have been following, the narrative by now will sound familiar: to stop a ransomware attack at this stage, most defenses rely on either pre-programmed definitions of 'bad' or have rules constructed to combat different scenarios put organizations in a risky, never-ending game of cat and mouse.
A firewall and proxy might block connections based on pre-programmed policies based on specific endpoints or data volumes, but it’s likely an attacker will ‘live off the land’ and utilize a service that is generally allowed by the business.
The effectiveness of these tools will vary according to data volumes: they might be effective for ‘smash and grab’ attacks using known malware, and without employing any defense evasion techniques, but are unlikely to spot ‘low and slow’ exfiltration and novel or sophisticated strains.
On the other hand, because by nature it involves a break from expected behavior, even less conspicuous, low and slow data exfiltration is detected by Darktrace and stopped with Darktrace's Autonomos Response. No confidential files are lost, and attackers are unable to extort a ransom payment through blackmail.
Real-world example: Unusual chain of RDP connections
It becomes more difficult to find examples of Darktrace stopping ransomware at these later stages, as the threat is usually contained before it gets this far. This is the double-edged sword of effective security – early containment makes for bad storytelling! However, we can see the effects of a double extortion ransomware attack on an energy company in Canada. The organization had the Enterprise Immune System but no Darktrace, and without anyone actively monitoring Darktrace’s AI detections, the attack was allowed to unfold.
The attacker managed to connect to an internal file server and download 1.95TB of data. The device was also seen downloading Rclone software – an open-source tool, which was likely applied to sync data automatically to the legitimate file storage service pCloud. Following the completion of the data exfiltration, the device ‘serverps’ finally began encrypting files on 12 devices with the extension *.06d79000. As with the majority of ransomware incidents, the encryption happened outside of office hours – overnight in local time – to minimize the chance of the security team responding quickly.
Read the full details of the attack
It should be noted that the exact order of the stages 3–5 above is not set in stone, and varies according to attack. Sometimes data is exfiltrated and then there is further lateral movement, and additional C2 beaconing. This entire period is known as the ‘dwell time’. Sometimes it takes place over only a few days, other times attackers may persist for months, slowly gathering more intel and exfiltrating data in a ‘low and slow’ fashion so as to avoid detection from rule-based tools that are configured to flag any single data transfer over a certain threshold. Only through a holistic understanding of malicious activity over time can a technology spot this level of activity and allow the security team to remove the threat before it reaches the latter and most damaging stages of ransomware.
Stage 6: How AI can stop ransomware encryption
At the encryption stage, ransomware attempts to make files and systems unavailable, often using tools or protocols that may otherwise appear legitimate. AI-led autonomous response can recognize abnormal file-access and connection behavior, then enforce a device’s normal pattern of activity or block only the malicious action to limit disruption.
Using either symmetric encryption, asymmetric encryption, or a combination of the two, attackers attempt to render as much data unusable in the organization’s network as they can before the attack is detected.
As the attackers alone have access to the relevant decryption keys, they are now in total control of what happens to the organization’s data.
Pre-programmed response and disruption
There are many families of tools that claim to stop encryption in this manner, but each contain blind spots which enable a sophisticated attacker to evade detection at this crucial stage. Where they do take action, it is often highly disruptive, causing major shutdowns and preventing a business from continuing its usual operations.
Internal firewalls prevent clients from accessing servers, so once an attacker has penetrated to servers using any of the techniques outlined above, they have complete freedom to act as they want.
Similarly, antivirus tools look only for known malware. If the malware has not been detected until this point, it is highly unlikely the antivirus will act here.
Stopping encryption autonomously
Even if familiar tools and methods are used to conduct it, Autonomous Response can enforce the normal ‘pattern of life’ for devices attempting encryption, without using static rules or signatures. This action can be taken independently or via integrations with native security controls, maximizing the return on other security investments. With a targeted Autonomous Response, normal business operations can continue while encryption is prevented.
Stage 7: How ransomware attacks reach extortion
The ransom note marks the point at which the attacker makes the extortion demand explicit, usually offering a decryption key or nondisclosure in exchange for payment. Modern extortion may also involve stolen data, destroyed backups, domain hijacking, or direct harassment, so encryption is no longer the only path to a ransom demand.
All of the stages up until this point represent a typical, traditional ransomware attack. But ransomware is shifting from indiscriminate encryption of devices to attackers targeting business disruption in general, using multiple techniques to hold their victims to ransom. Additional methods of extortion include not only data exfiltration, but corporate domain hijack, deletion or encryption of backups, attacks against systems close to industrial control systems, targeting company VIPs… the list goes on.
Sometimes, attackers will just skip straight from stage 2 to 6 and jump straight to extortion. Darktrace recently stopped an email attack which showed an attacker bypassing the hard work and attempting to jump straight to extortion in an email. The attacker claimed to have compromised the organization’s sensitive data, requesting payment in bitcoin for its same return. Whether or not the claims were true, this attack shows that encryption is not always necessary for extortion, and this type of harassment exists in multiple forms.

As with the email example we explored in the first post of this series, Darktrace/Email was able to step in and stop this email where other email tools would have let it through, stopping this potentially costly extortion attempt.
Whether through encryption or some other kind of blackmail, the message is the same every time. Pay up, or else. At this stage, it’s too late to start thinking about any of the options described above that were available to the organization, that would have stopped the attack in its earliest stages. There is only one dilemma. “To pay or not to pay” – that is the question.
Often, people believe their payment troubles are over after the ransom payment stage, but unfortunately, it’s just beginning to scratch the surface…
Stage 8: How AI supports ransomware investigation and clean-up
Ransomware clean-up begins with reconstructing how the intrusion started, which systems were affected, and which controls failed to stop it. AI-led investigation can connect activity across the attack timeline, helping security teams identify the initial access point, understand attacker movement, prioritize remediation, and reduce the risk of reinfection.
Legacy tools largely fail to shed light on the vulnerabilities which allowed the initial breach. Like searching for a needle in an incomplete haystack, security teams will struggle to find useful information within the limited logs offered by firewalls and IDSs. Antivirus solutions may reveal some known malware but fail to spot novel attack vectors.
With Darktrace’s Cyber AI Analyst, organizations are given full visibility over every stage of the attack, across all coverage areas of their digital estate, taking the mystery out of ransomware attacks. They are also able to see the actions that would have been taken to halt the attack by Darktrace's Autonomous Response.
Stage 9: Why ransomware recovery remains difficult
Ransomware recovery involves restoring systems and data, validating that the threat has been removed, and returning operations to a trusted state. Recovery may continue even after a ransom is paid because decryptors can fail and files may remain damaged, making early detection, containment, tested backups, and incident readiness essential.
The organization begins attempts to return its digital environment to order. Even if it has paid for a decryption key, many files may remain encrypted or corrupted. Beyond the costs of the ransom payment, network shutdowns, business disruption, remediation efforts, and PR setbacks all incur hefty financial losses.
The victim organization may also suffer additional reputation costs, with 66% of victims reporting a significant loss of revenue following a ransomware attack, and 32% reporting losing C-level talent as a direct result from ransomware.
What is the best solution for preventing ransomware?
The solution category best suited to preventing ransomware is an AI-powered behavioral detection and autonomous response platform. This type of technology can identify unusual activity throughout the attack lifecycle and take targeted action before an intrusion progresses to data exfiltration, encryption, or extortion.
An effective ransomware prevention solution should:
- Use behavioral analysis to identify known and previously unseen threats without relying solely on malware signatures, blocklists, or predefined attack rules.
- Detect suspicious activity across email, network, cloud, identity, and endpoint environments rather than protecting only one stage of the ransomware attack chain.
- Correlate signals such as unusual remote access, command-and-control communications, lateral movement, privilege escalation, and abnormal data transfers.
- Take precise, real-time action against malicious activity while allowing unaffected users, devices, and business operations to continue normally.
- Give security teams visibility into the complete attack sequence so they can investigate the initial intrusion, understand its impact, and strengthen defenses against future attacks.
Darktrace combines Self-Learning AI and Autonomous Response to deliver these capabilities. As the examples involving McLaren Racing, Dharma ransomware, WastedLocker, and unusual RDP activity demonstrate, this approach can identify and contain anomalous behavior that conventional gateways, firewalls, and signature-based controls may miss.
Conclusion
While the high-level stages described above are common in most ransomware attacks, the minute you start looking at the details, you realize every ransomware attack is different.
As many targeted ransomware attacks come through ransomware affiliates, the Tools, Techniques and Procedures (TTPs) displayed during intrusions vary widely, even when the same ransomware malware is used. This means that even comparing two different ransomware attacks using the same ransomware family, you are likely to encounter completely different TTPs. This makes it impossible to predict what tomorrow’s ransomware will look like.
This is the nail in the coffin for traditional tooling which is based on historic attack data. The above examples demonstrate that Self-Learning technology and Autonomous Response is the only solution that stops ransomware at every stage, across email and network.