Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Dave Palmer
Advisor
Share
08
May 2018
Ransomware continues to be one of the most serious and disruptive cyber threats. The business models, motivations, and infection techniques of emerging campaigns have diversified, and new strands of ransomware continue to outpace the release of decryption tools. By 2019, global ransomware damage costs are expected to surpass $11.5 billion per year.
The three most memorable ransomware campaigns of 2017 - Wannacry, NotPetya, and Bad Rabbit - were ground-breaking in their scope, spread, and destructive power, demonstrating that every business, industry, and country is a potential victim. Although the damage caused by these attacks highlighted the importance of good cyber hygiene, many companies have struggled to address even the most widely reported vulnerabilities. As prevention is better than cure, this article will discuss some of the most common infection vectors and how the Darktrace Enterprise Immune System can assist security teams in catching ransomware threats.
Motivations: financial gain or wreaking havoc?
Ransomware is traditionally linked with making a quick buck by getting the victim to pay a set fee to unlock encrypted files. The phenomenon of ransomware-as-a-service has made this easier than ever before, as it has allowed virtually anyone to purchase ever more potent ransomware distribution kits on the Dark Web. The recent growth in cryptocurrencies has also made maintaining anonymity much easier than before, resulting in a definite increase in financially motivated cyber-criminals.
Regrettably, the goal of ransomware is no longer just to make money. NotPetya and other campaigns such as Ordinypt were designed to purposefully destroy data instead. Even though NotPetya provided its victims with payment instructions, it had no way of identifying who had actually made the payment. The uncertainty surrounding the recovery of lost files and the possibility of being associated with funding malicious organizations have therefore deterred many victims from meeting the ransom demands.
No matter how much a business tries to safeguard their assets, incidents are inevitable, and ransom attacks are an increasingly likely choice of criminal action. But it is now possible to identify in-progress attacks and handle them before they become a crisis.
Case Study 1: Executable file download from a compromised website
Many prolific ransomware strands have been distributed by phishing emails, infected file downloads, compromised websites, malvertising, and exploit kits. In many cases, ransomware is often downloaded and installed without the victim’s knowledge. To illustrate the ransomware download mechanics, we will analyze the life-cycle of a GandCrab incident. In the case study detailed below, the Darktrace Enterprise Immune System flagged a customer device retrieving an executable file from a previously unmonitored location following a redirection from another rare site.
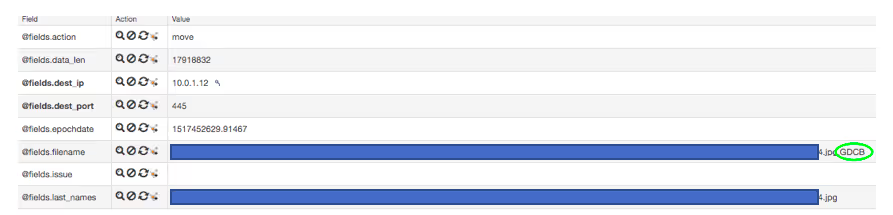
The file containing ransomware was downloaded from a website registered to a Polish domain. Shortly after downloading the file, the customer’s device began reaching out to two locations which had not been contacted by any other network devices, nomoreransom.bit and bleepingcomputer.bit. Both are command and control servers for GandCrab ransomware. Once contacted, the malicious virus proceeded to encrypt files on the SMB server, adding the .GDCB (GandCrab) extension as it moved through the folders.
The virus modified the original file extensions in the encryption process.
Within seconds of the virus appearing on the company’s network, the Darktrace Cyber Analyst team alerted the security team of the threat. Preventative action was then taken, which allowed the threat to be contained within a timely manner.
Case Study 2: Bruteforcing Remote Desktop Protocol access
In addition to devising clever ways of downloading ransomware onto victim’s machines, some hackers have turned to bruteforcing Remote Desktop Protocol (RDP) access instead (HC7 & Lockcrypt). Exposing Remote Desktop services to the Internet is risky, as attackers can force access into a network by guessing login information and remotely exploiting a range of possible vulnerabilities and administrative tools in order to infect other available machines.
In another particularly serious breach, Darktrace detected a series of suspicious activities indicating that a malicious actor had taken control of a key server and was using it as a pivot point in order to move laterally throughout the network and install Remote Access Tools (RATs) on multiple devices.
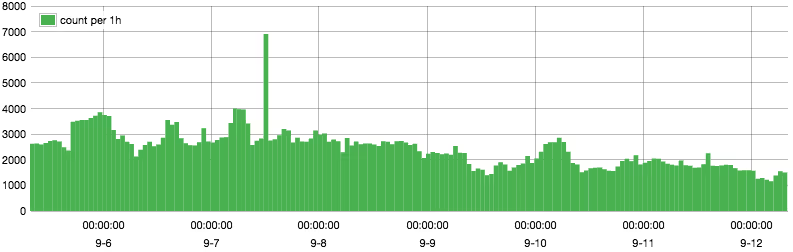
In the initial stage of the attack, the Darktrace Enterprise Immune System observed over 400,000 incoming connections on a port that was targeting devices with RDP turned on and immediately flagged the first signs of a bruteforce attack.
Over 400,000 incoming RDP from multiple rare external devices.
The attack was successful; a compromised server was then used to retrieve malware that granted backdoor access and scanned the network for devices with open RDP channel. The hacker subsequently tunneled through the intermediary, gained control over multiple other machines, and installed third-party remote access software to all available devices.
Although most RDP bruteforcing incidents the Darktrace Enterprise Immune System observes do not escalate this far, the Darktrace Cyber Analyst team are constantly flagging instances of publicly accessible remote management services. To prevent ransomware that specifically exploits insecure RDP configuration, businesses should move these critical services to a virtual private network. Moreover, with Darktrace Antigena, Darktrace’s autonomous response solution, businesses can benefit from an added layer of protection. In this case, it would have blocked any anomalous RDP connections to the server, thus preventing any lateral movement throughout the network.
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Agentic attacks in the wild: Inside three ARTEX investigations
Key insights
· Darktrace observed activity in several customer environments involving infrastructure and behaviors associated with reported ARTEX-enabled campaigns, including activity linked to China-nexus espionage and financially motivated attacks.
· In the higher-confidence cases, known infrastructure appeared alongside beaconing, unusual TLS, reconnaissance, tunneling, script retrieval, SMB activity and external data transfer. One Azure case had no observed network command and control at all, only key listing and application identity activity.
· ARTEX is now used by actors with different objectives. Identifying the framework can help locate relevant activity, while the behavior around the affected system provides the stronger evidence for understanding compromise and attribution.
Introduction
Attackers have moved beyond using AI for phishing and are running agentic frameworks; open-source tools like ARTEX, CAIRN, PentAGI and Hexstrike that let AI agents scan, exploit and move through an environment with little human input [1]. ARTEX has moved quickly from an offensive security project into live intrusion activity. Since at least August 2026, the framework has been associated with espionage, financially motivated attacks and opportunistic campaigns across government, financial services, technology, defense, telecommunications and other sectors. The FBI has documented ARTEX activity spanning reconnaissance, exploitation, credential abuse, lateral movement, collection, command and control, and exfiltration [2].
Darktrace has observed activity in customer environments that overlaps with infrastructure, tooling and behaviors reported in several of these campaigns. The cases below highlight how those intrusions appeared on the network, including the activity visible before an analyst can determine which actor or framework may be responsible.
ARTEX as part of the attacker workflow
ARTEX is an open-source, multi-agent offensive security platform that converts high-level objectives into actions carried out by specialized agents [2]. Operators have used it to automate activity across the attack lifecycle, including scanning, exploitation, credential activity and post-compromise operations. Some reported intrusions moved from initial targeting to privileged access in under three hours [2].
The framework is now associated with actors pursuing different objectives and using different post-exploitation tooling. The original public repository was removed in October 2026, but archived copies and localized versions remain available. For defenders, ARTEX is more useful as context for an investigation than as an attribution shortcut.
Darktrace observations show the same point at network level. Infrastructure linked to reported ARTEX campaigns appeared alongside beaconing, tunneling, unusual TLS, reconnaissance, file retrieval and lateral activity.
Case 1: Espionage-linked activity
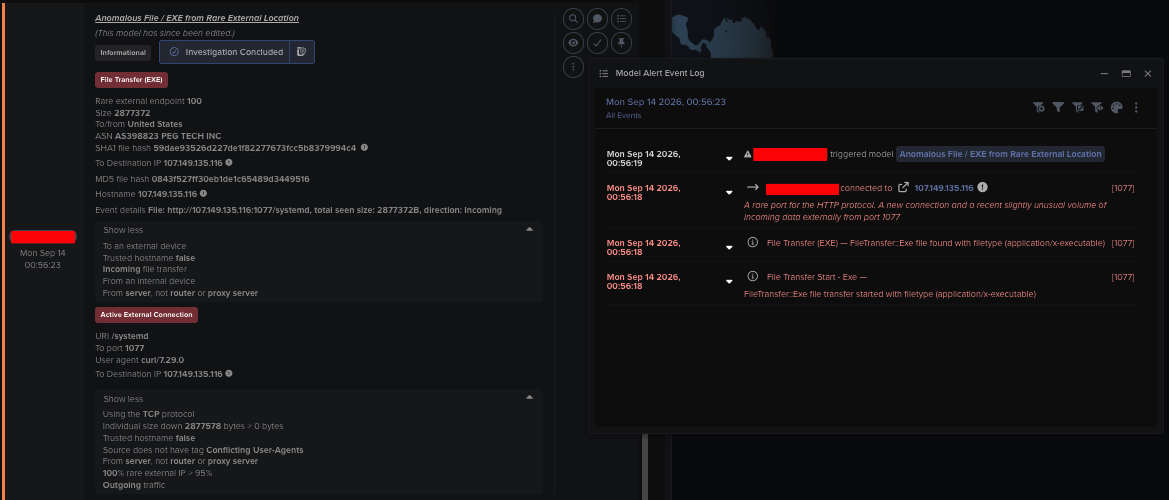
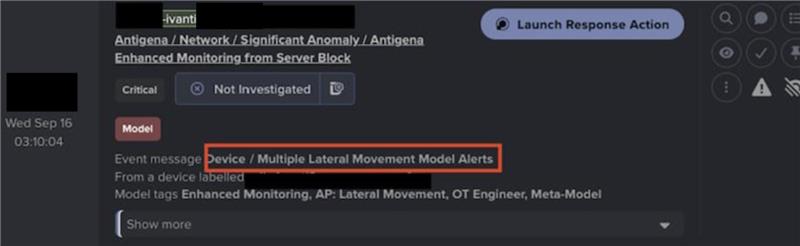
Darktrace observed activity associated with BLOODALCHEMY command-and-control (C2) infrastructure in two customer environments. In one environment, five devices communicated with nginxmysql[.]com and 45.153.126[.]223 between October 23 and November 2. Both indicators had previously been linked to China-nexus espionage activity involving ARTEX [4].
The connections were accompanied by suspicious beaconing, repeated successful connections and unusual self-signed TLS. One system began making suspicious TLS connections to nginxmysql[.]com on October 23. Beaconing followed on October 24, and SMB scanning appeared later in the sequence. Other affected systems subsequently communicated with previously unseen external endpoints.
Prior to the observed C2, Darktrace detected curl requests retrieving executable and script content including /systemd, /wazuh, linux_amd64, u.sh and q.sh. Related telemetry included DRSGetNCChanges activity consistent with DCSync, LDAP enumeration, DNS zone transfers, network scanning, certificate downloads and SMB writes involving start.bat.
Figure 1: Darktrace investigation showing suspicious network activity associated with infrastructure linked to reported ARTEX activity.
Figure 2: Darktrace detection showing anomalous self-signed TLS activity during the espionage-linked investigation.
BLOODALCHEMY has been reported in more than one China-nexus cluster [5]. SoftEther infrastructure observed in one environment provided another point of correlation with reported VAPOR PANDA tradecraft. The moderate-confidence assessment tying this to a Chinese nexus threat actor is based on infrastructure, victim context, tradecraft behavior that followed the initial connection, and public reporting.
Case 2: Financial-sector activity
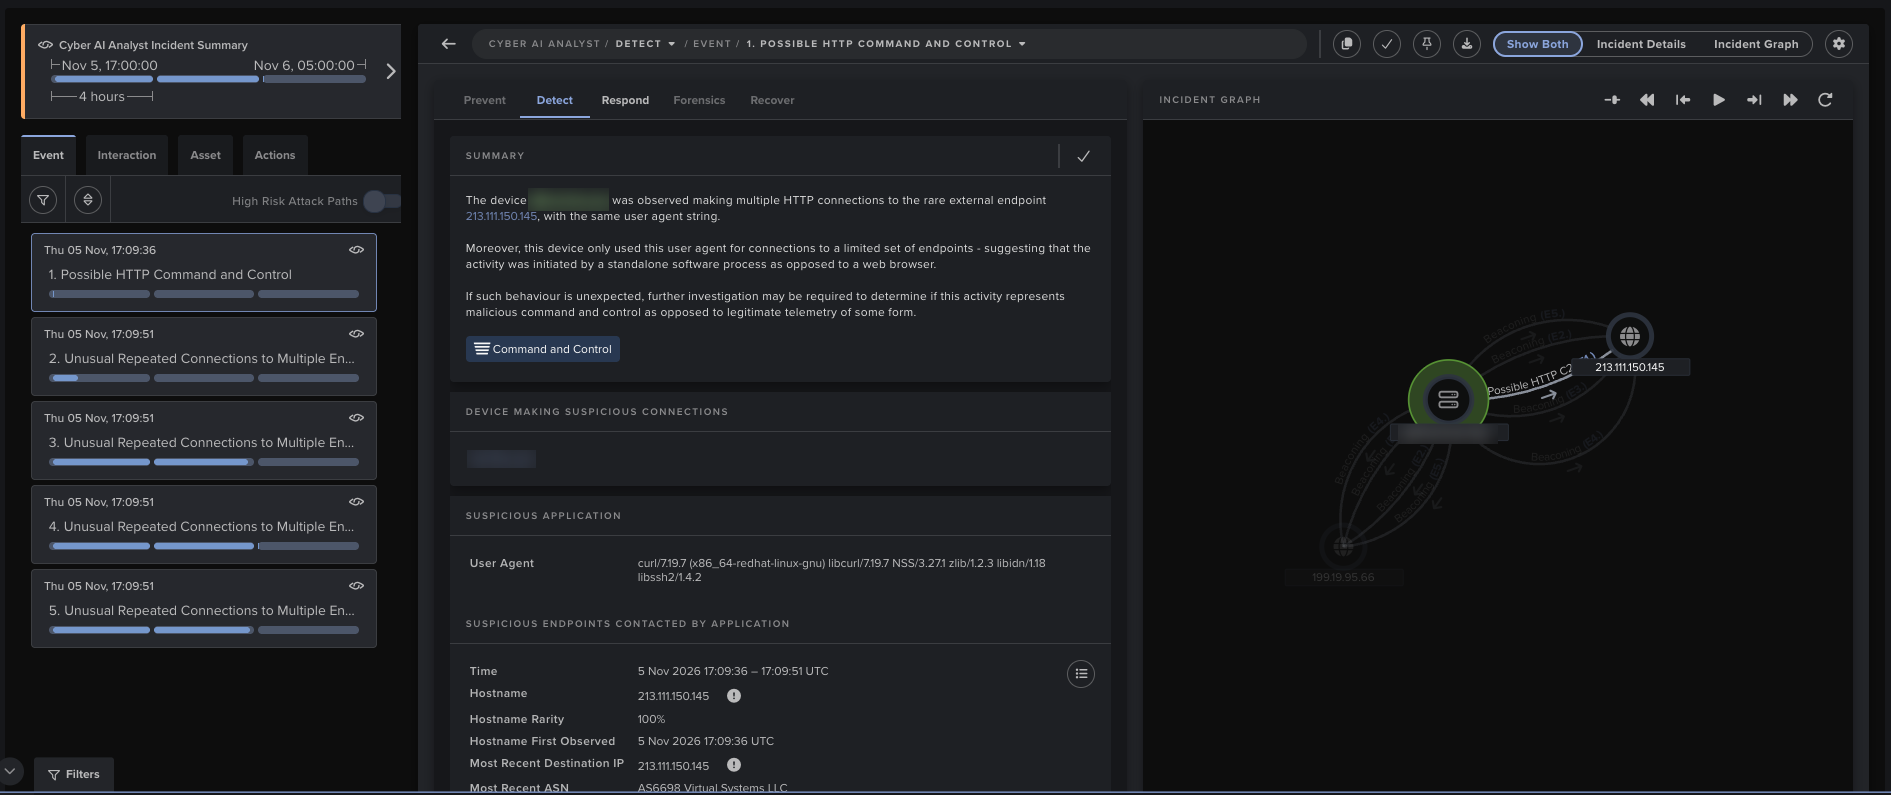
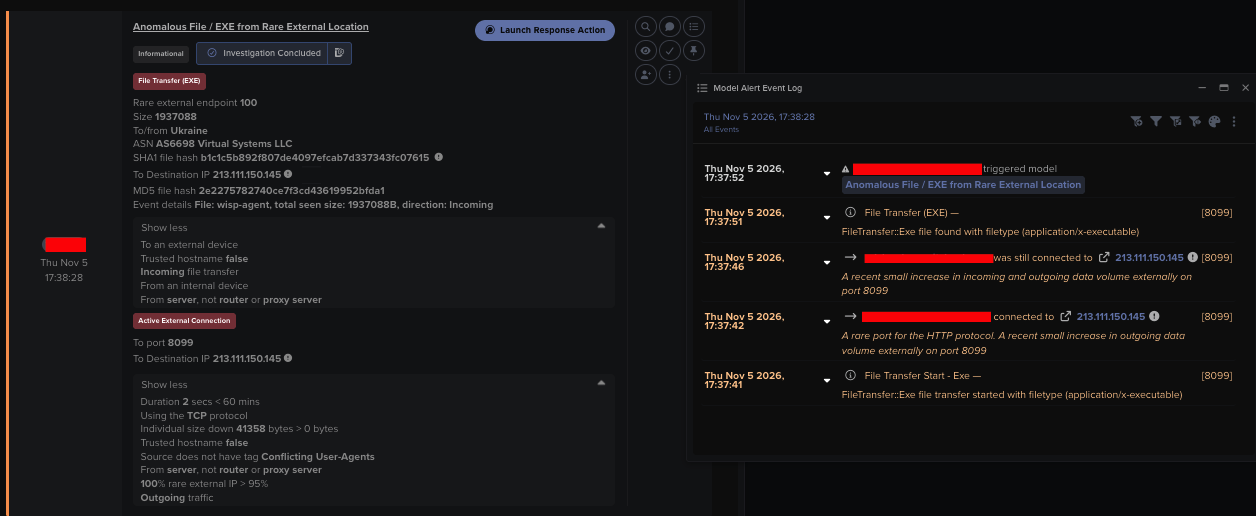
In early November, Darktrace observed activity in two financial-sector environments that overlap with reported ARTEX infrastructure. On November 5, a server connected to 213.111.150[.]145:8099 and downloaded wisp-agent, associated with WISP C2 activity.
Figure 3: Darktrace's Real-Time AI Analyst investigation showing a server making repeated HTTP requests, using a curl user agent, to a rare external endpoint on port 8099.
In a second environment, a device attempted connections to 85.11.167[.]52 on November 1 and 2. The connections occurred alongside beaconing to new and rare destinations, anomalous TLS, possible tunneling and unusual package downloads.
The device also communicated with temp[.]sh, ssh.localhost[.]run, localhost[.]run, termbin[.]com, pastebin[.]com and GitHub-hosted release infrastructure. The sequence showed potential tooling retrieval, C2, tunneling and use of external services capable of staging or moving data.
Figure 4: Darktrace investigation showing connections to new and rare external destinations during the financial-sector activity.
Case 3: Credential collection in Azure
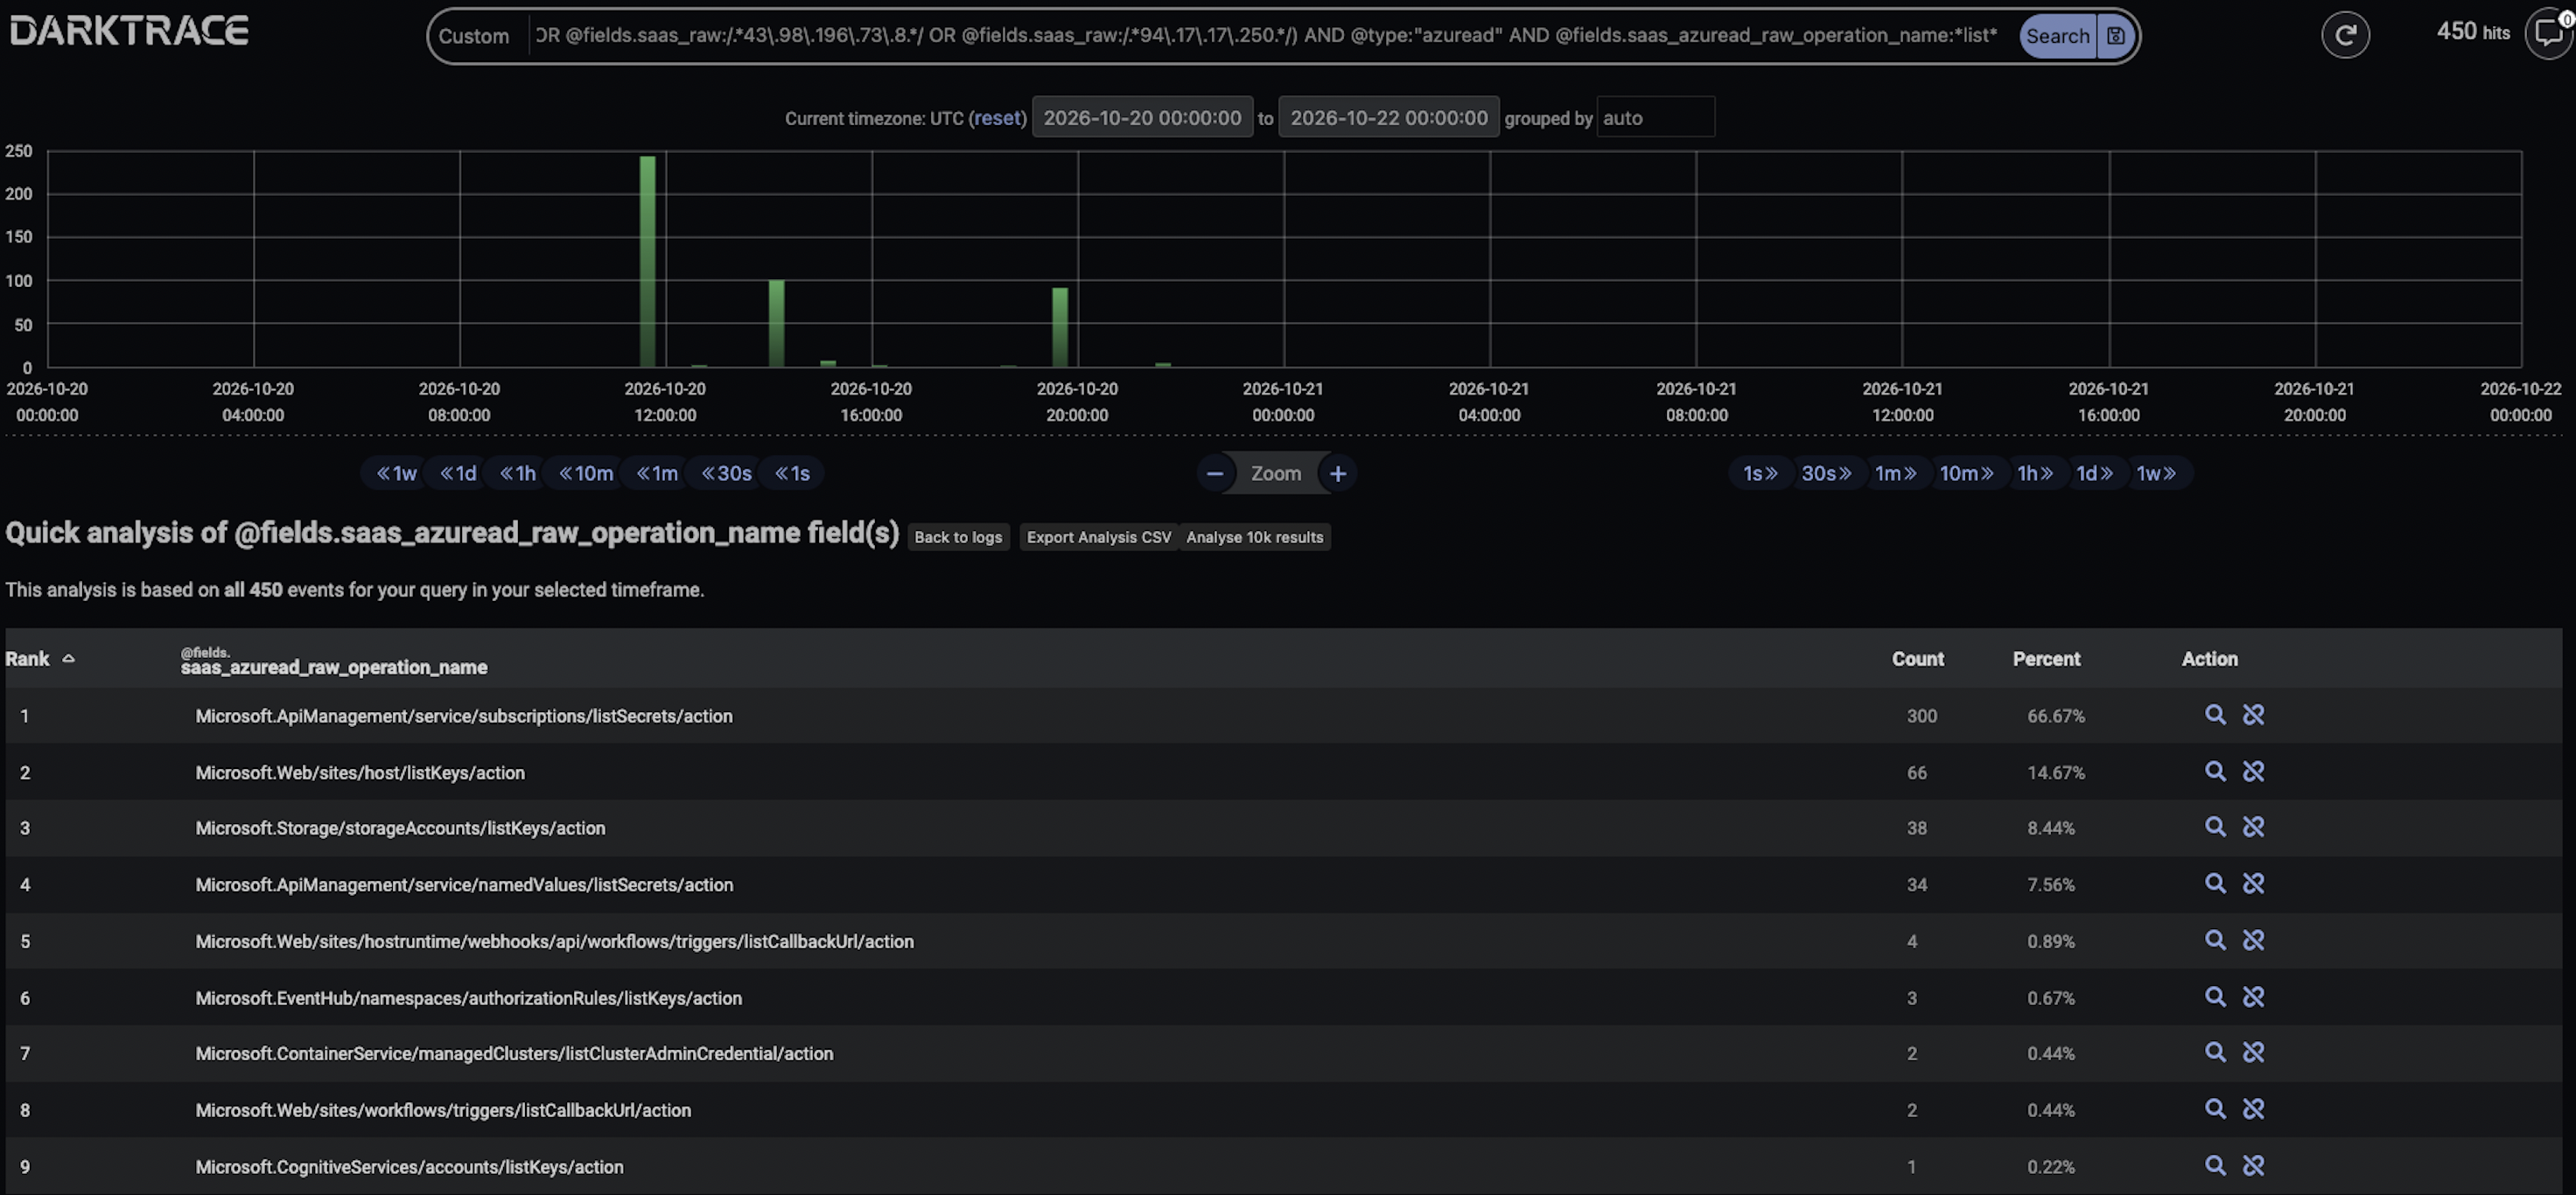
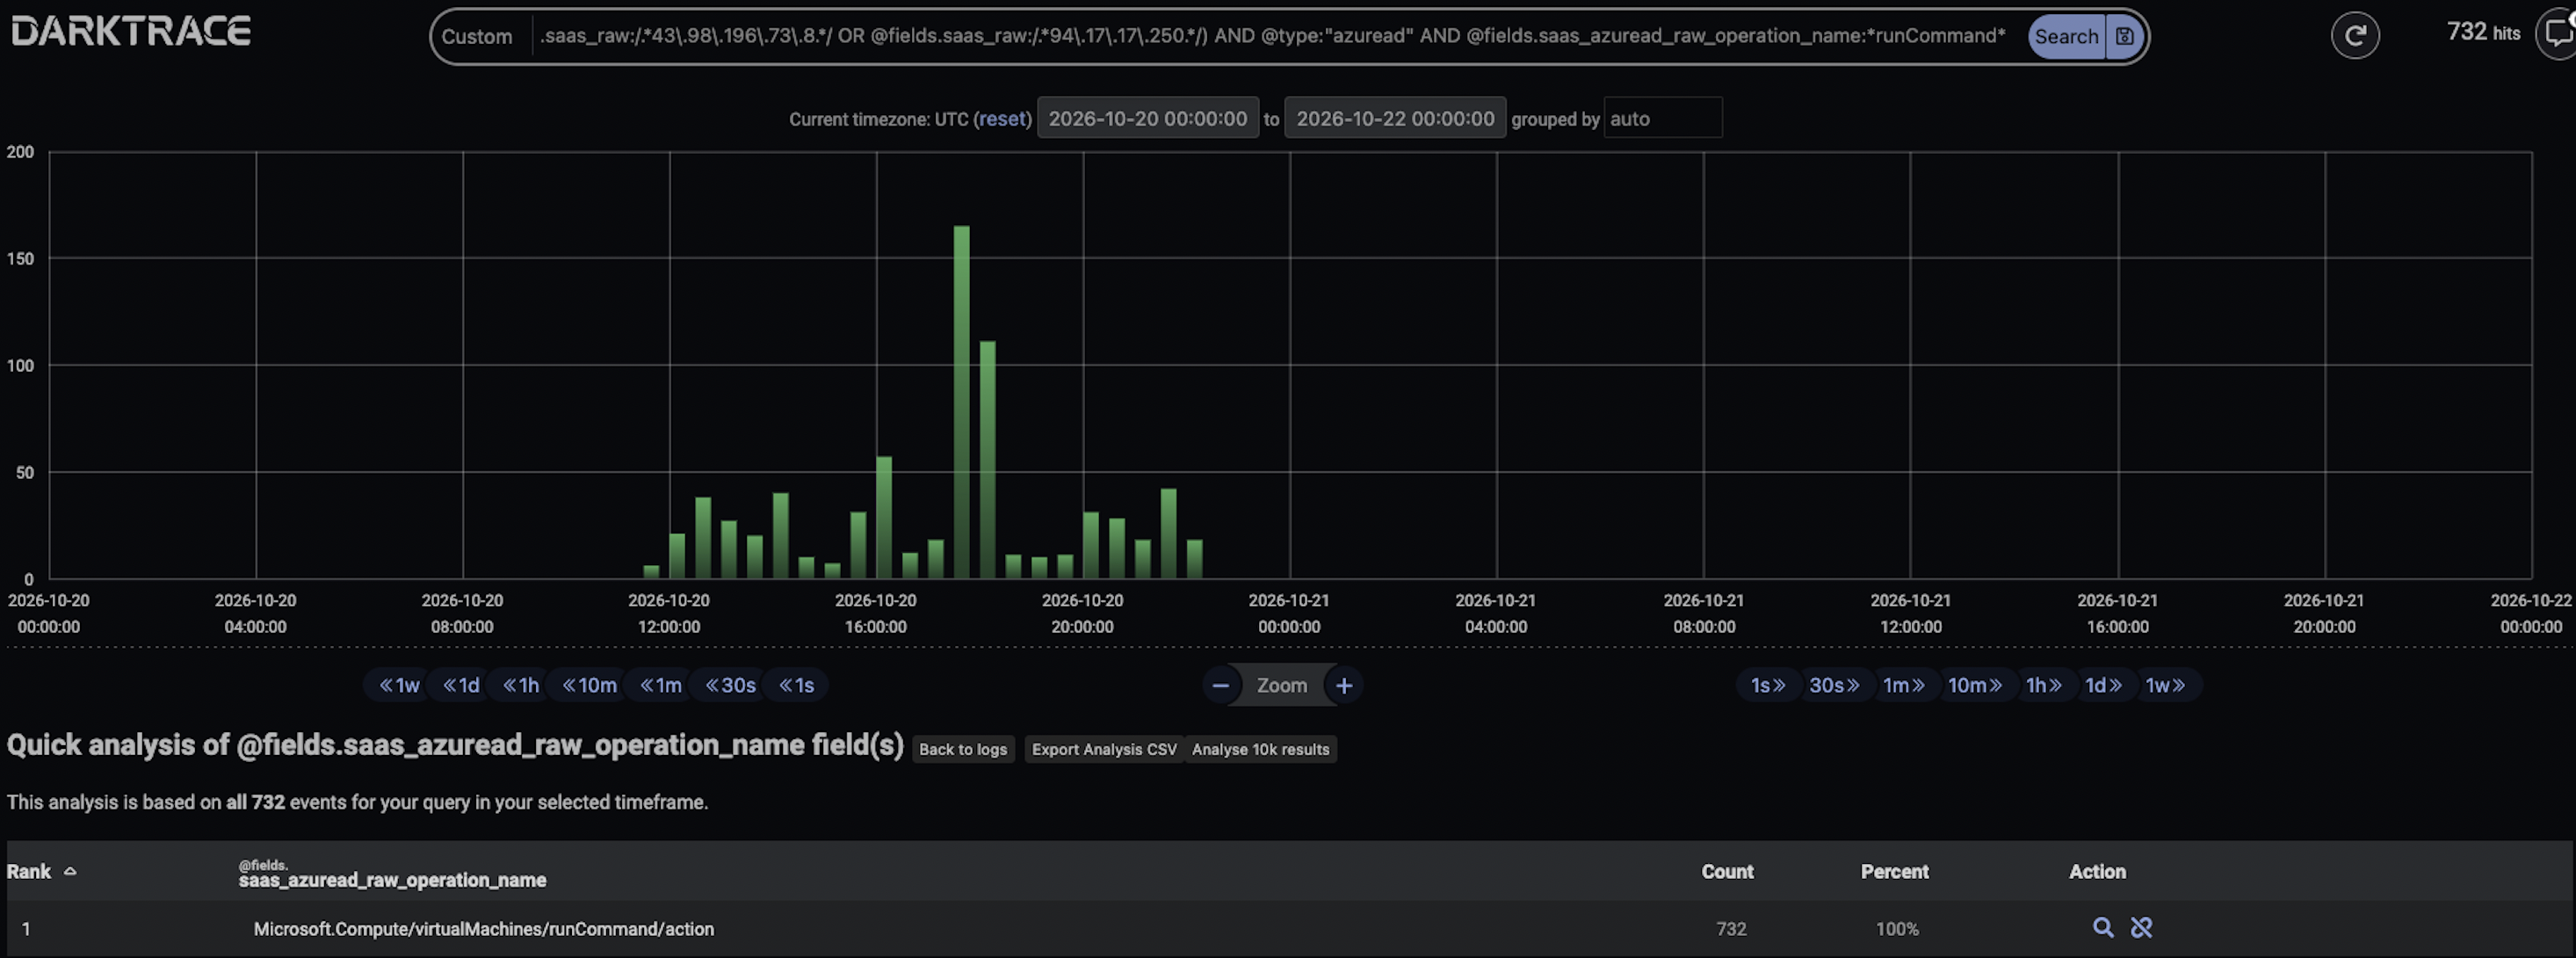
On October 20, Darktrace observed a sweep of credential collection in a customer’s Azure environment that is consistent with ARTEX use. The intrusion began with connections to the virtual network from 43.98.196[.]73 (Alibaba Cloud). Open-source scanning data associates the address with ARTEX.
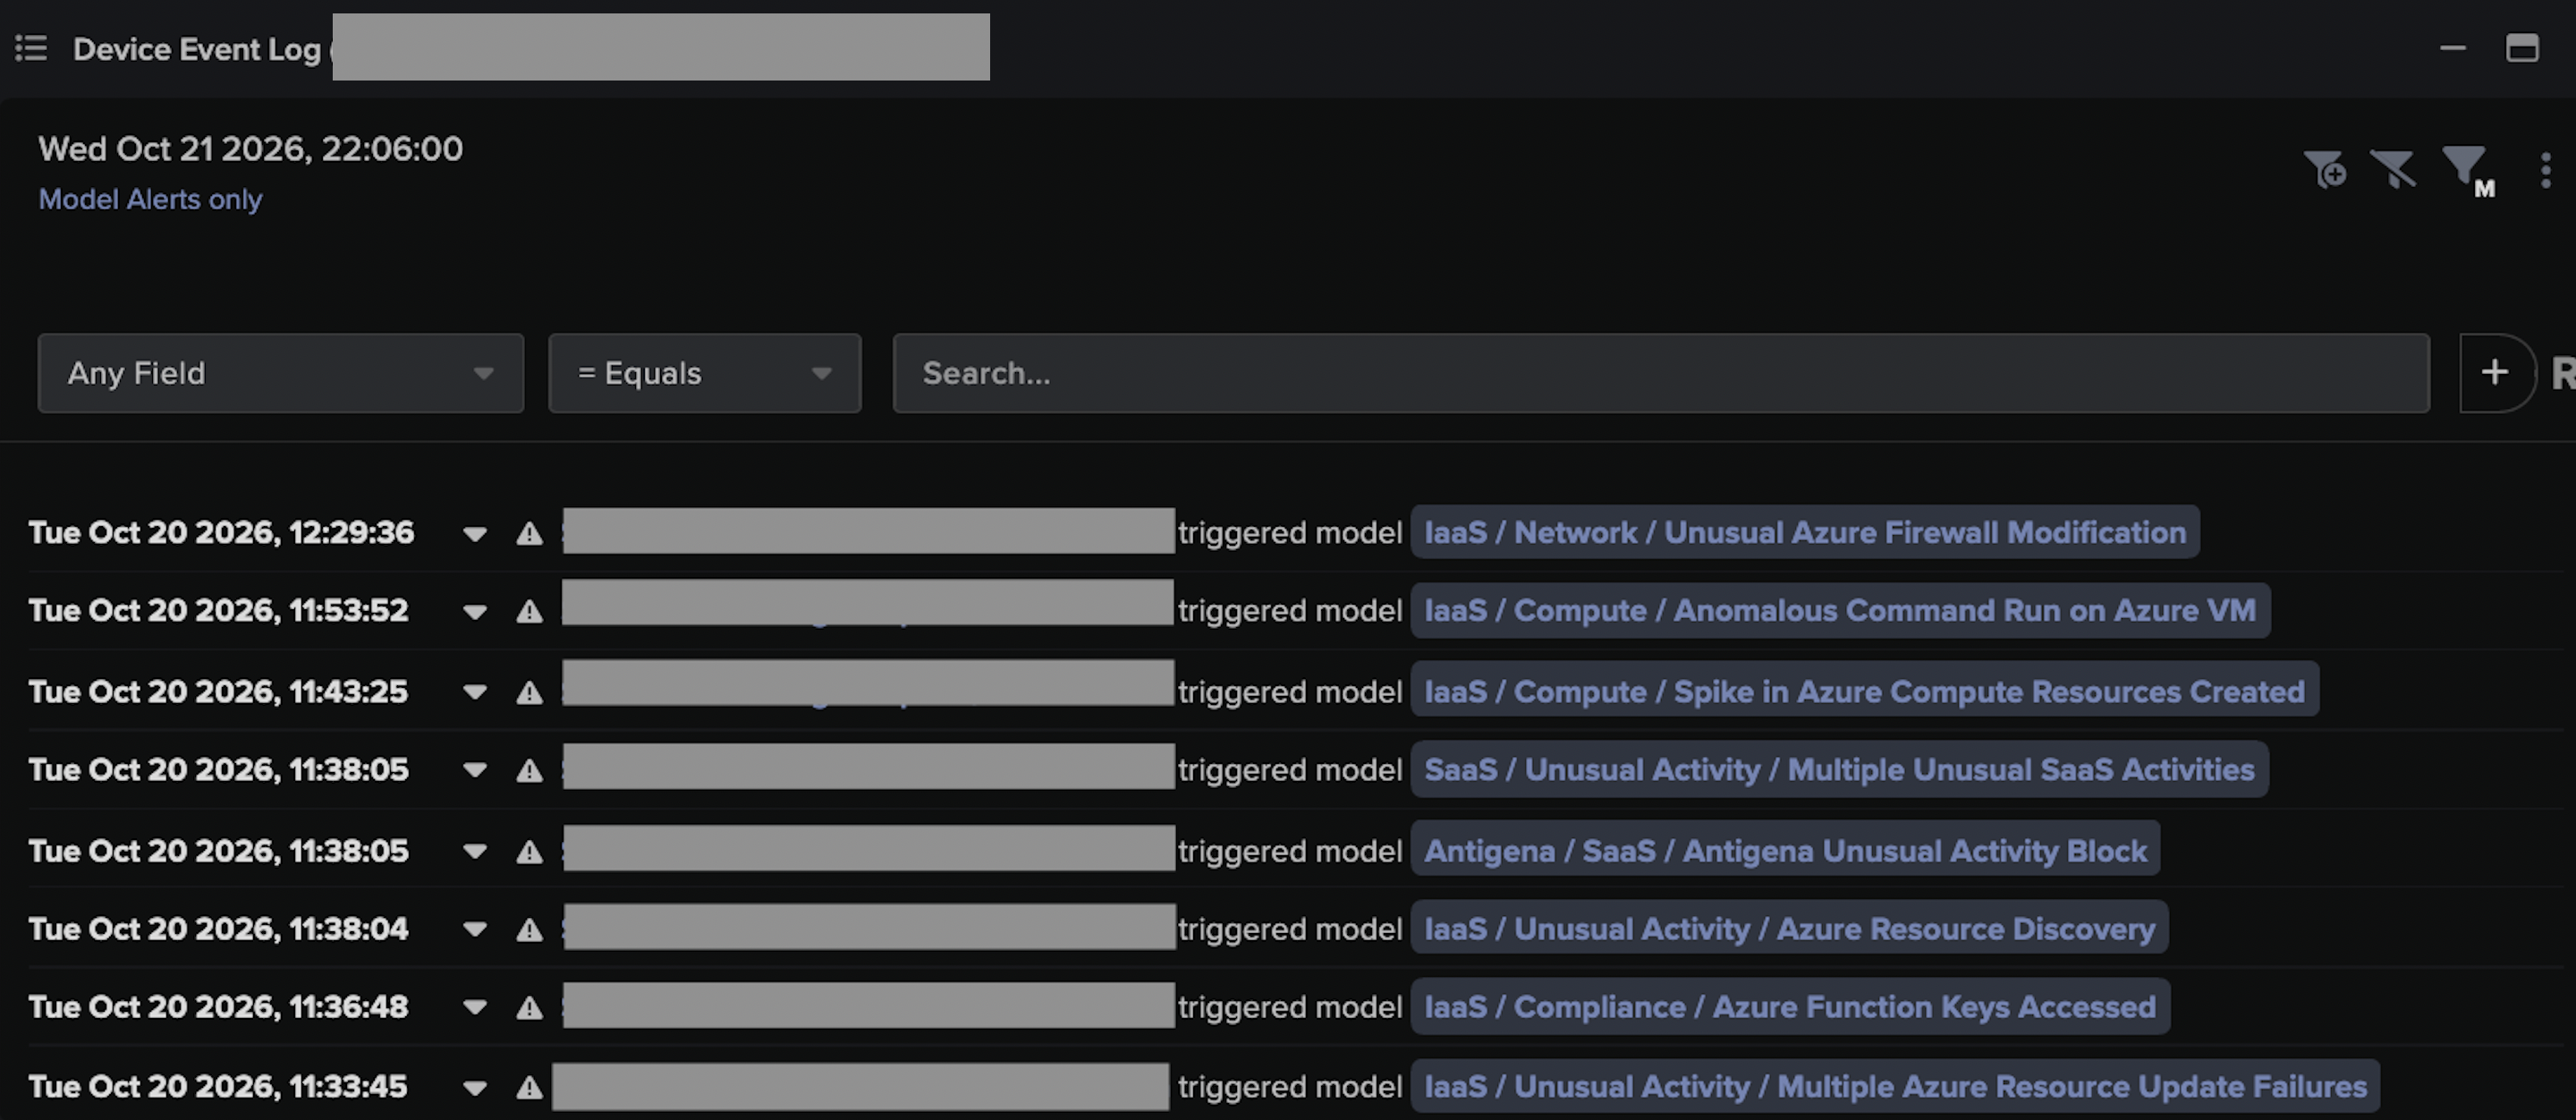
A compromised user identity made requests to the Azure Resource Manager API, though how it was compromised is unknown. The requests listed keys and secrets across API Management, web and function apps, Cognitive Services, Event Hubs, storage accounts and a managed Kubernetes cluster. With those credentials the attacker compromised multiple application identities. The attacker then used the application identities and the user identity to retrieve more credentials, change firewall and security rules and run scripts on virtual machines. Microsoft Defender alerts showed attempted execution of scripts related to Mimikatz and Impacket.
In a cloud environment, such privileged and enumerative operations are potentially indistinguishable from legitimate administrative actions. Consequently, the sequence and context of such operations signified more than any specific API call. There was no C2 traffic to match, and listing keys and using application identities are also what administrators and automation do. A compromised user, credential retrieval across several Azure services, new application identities, more credential collection and changes to security controls only made sense together, and by then access was spreading through the cloud environment.
Figure 5: Darktrace Advanced Search showing Azure AD operation names associated with the activity.
Figure 6: Darktrace Advanced Search showing the Azure Resource Manager action used to execute scripts.
Figure 7: Darktrace Device Event log window showing the triggered models related to the suspicious Azure activity.
Shared tooling weakens attribution signals
The three cases looked different on the network: BLOODALCHEMY infrastructure and espionage-consistent tradecraft, WISP infrastructure in financial-sector systems, and Azure identity and control-plane activity with no C2 at all.
Shared tooling has complicated attribution for years, and ARTEX adds to it because the framework carries out more of the attack, so reconnaissance, exploitation attempts and some post-compromise activity can look the same whoever set the objective. Attribution still needs infrastructure, malware, victimology, timing and the sequence of behavior inside the environment, and an ARTEX link is one input to that. Moreover, the behavior and the agent will still be shaped by the biases, preferences, and tradecraft of its operators.
At its core, ARTEX’s planner and worker agents identify and record facts, while exploring intents. However, the way the Large Language Model (LLM) chooses its next steps toward an objective is shaped fundamentally by the skills and tools available in its context. This includes its starting context, as well as various possible Model Context Protocol (MCP) plugins and user-injected context (e.g. user input mid-operation). Operators still have preferred tradecraft, and this preference shapes the pathways the harness will provide to the LLM in context prompts. Even on the same platform, customization based on operator preferences and goals will remain a key facet of campaign and actor identification.
Detection and response
Across the Darktrace cases, the stronger signals came from behavior after the connection: beaconing, abnormal TLS, reconnaissance, unusual authentication, tunneling, script retrieval, SMB activity and outbound transfer. Automated activity also produced compressed bursts of requests, sequential enumeration and repeated attempts with small changes.
With agentic tools reaching privileged access in under three hours, analysts may have only a short window to connect scanning or authentication activity to credential changes, new administrative access, tooling retrieval or lateral movement. Keeping network, identity and cloud telemetry together shows what happened before and after the first match, and whether a connection was noise or an intrusion moving toward privileged access.
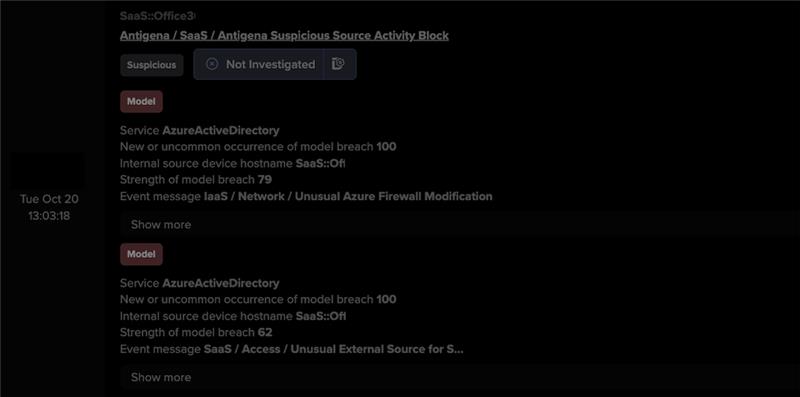
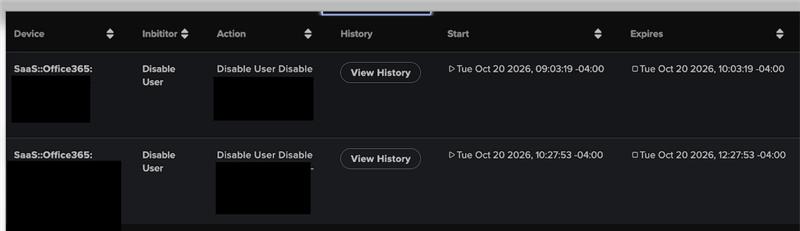
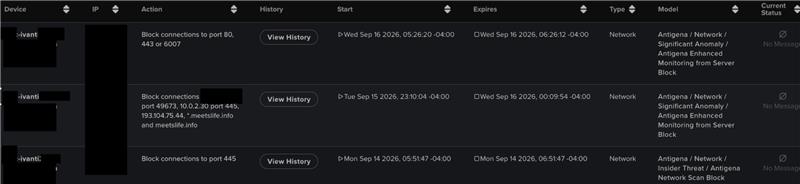
In some of these cases, Darktrace's Autonomous Response took or recommended action against the activity, including blocking internal connectivity over specified ports, inhibiting outbound connections with likely C2 endpoints, and/or disabling SaaS/IaaS user accounts. While many of these recommended actions required human confirmation due to deployment configuration preferences, had these actions been applied autonomously at the time of alert, the scope of activity would have been limited, thereby giving analysts time to investigate and respond.
Figure 9: Autonomous Response summary for affected cloud users during the intrusion.
Figure 10: Autonomous Response taking action against unusual lateral movement activity on an affected device.
Figure 12: Autonomous Response summary for affected network users during the time of the intrusion.
ARTEX won’t be the last of these frameworks. The next ones will come with new capabilities and defaults, but an intrusion still must interact with the target environment, and that shows up in how systems, identities and applications behave even after the indicator has aged out. The harder intrusions to catch will have no infrastructure to match, just ordinary API calls and legitimate identities. Detecting those depends on knowing what normal looks like for each identity and device. Containing abnormal activity at machine speed can stop an intrusion progressing while analysts establish impact and its extent. Autonomous Response does not replace that human analysis, but rather augments defender teams' capabilities by extending the window for investigation.
Credit to Nathaniel Jones (SVP, Global Threat Intelligence), Eugene Chua (Principal Analyst), Sam Lister (Senior Security Researcher), Adam Potter (Associate Principal Cyber Analyst), Daniel Levy (Threat Hunting Data Scientist)
Edited by Ryan Traill (Content Manager)
Appendices
Darktrace model detections
· Anomalous Connection / Multiple HTTP POSTs to Rare Hostname
· Compromise / Large Number of Suspicious Successful Connections
· Compromise / Suspicious Beaconing Behaviour
· Compromise / Agent Beacon to New Endpoint
· Compromise / Beacon to Young Endpoint
· Compromise / SSL Beaconing to Rare Destination
· Compromise / Suspicious TLS Beaconing To Rare External
· Compromise / Possible Tunnelling to Bin Services
· Device / Anomalous Github Download
· Device / Anomalous Package Download
· Device / Initial Attack Chain Activity
Indicators of compromise (IoCs)
nginxmysql[.]com
45.153.126[.]223
213.111.150[.]145
wisp-agent
85.11.167[.]52
43.98.196[.]73
192.121.47[.]20
www[.]ddduuuppp[.]com
89.46.234[.]50
sqlserver-sqlite[.]com
199.19.95[.]66
graphics-hook-filter64.dll
graphics-hook_config.bin
References
1. Google. GTIG AI Threat Tracker - https://cloud.google.com/blog/topics/threat-intelligence/agentic-threat-activity-crosses-a-significant-threshold
2. Federal Bureau of Investigation, Threat Overview of ARTEX Autonomous Penetration Testing Framework, FLASH-20261113-001, 13 November 2026: https://www.ic3.gov/CSA/2026/261113.pdf
3. Microsoft Security Blog, Storm-0940 Uses ARTEX Agentic AI in ConnectWise Supply Chain Compromise: https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/
4. CrowdStrike, VAPOR PANDA Uses ARTEX to Scale Global Campaign: https://www.crowdstrike.com/en-us/blog/vapor-panda-uses-artex-to-scale-global-campaign/
5. Bitdefender, SilkParasite: Tracking a China-Nexus APT Across Central Asia: https://www.bitdefender.com/en-us/blog/businessinsights/silkparasite-tracking-china-nexus-apt-across-central-asia
Darktrace qualifies for NATO’s Cybersecurity Dynamic Marketplace
Darktrace has been selected to join NATO’s Cybersecurity Dynamic Marketplace (CSDM), an initiative designed to give NATO faster, more flexible access to cybersecurity technology and services in support of its missions.
Established by the NATO Communications and Information Agency (NCIA), the marketplace brings together qualified suppliers whose technical capabilities have been reviewed, helping NATO match specialist expertise to project needs and respond more quickly to changing operational priorities.
Qualified across all eight cybersecurity categories
The program’s first phase, known as Lot 1, covers eight cybersecurity categories. Suppliers can qualify in individual categories; Darktrace has qualified to compete for future work across all eight:
Identity, Credential and Access Management
Endpoint Protection and Platforms
Network and Perimeter Security
Cloud Security
Threat Detection and Analytics Platforms
Vulnerability and Exposure Management
Digital Forensics and Evidence Platforms
Professional Services
Darktrace’s qualification across all eight categories reflects the breadth of our technology and services.
Supporting government and defense organizations
Nation-state attacks, compromised suppliers, the rapid exploitation of security weaknesses and attackers’ growing use of AI are increasing pressure on public-sector organizations. At the same time, agencies are adopting cloud services, connecting the technology that runs physical operations, and introducing automation and AI. Security teams must manage these changes while keeping essential operations running and sensitive information secure.
Protecting these environments requires an understanding of how people, AI and connected systems interact, and the ability to recognize when their activity creates risk. Threats can span several systems, making it essential for security teams to connect related activity and respond quickly.
The Darktrace Behavioral Defense Platform™ supports this approach through unified visibility, continuous behavioral monitoring and autonomous response across AI, people and infrastructure.
At its core, Darktrace’s Adaptive AI™ continuously learns how each organization behaves, building a unique understanding of its people, AI agents and connected systems. This enables the platform to help identify activity that does not belong, connect related behavior across the organization, and investigate and respond to threats autonomously in real time, helping prevent disruption to essential operations.
Our selection builds on work to meet government security requirements internationally. Darktrace recently completed an independent assessment under Australia’s InfoSec Registered Assessors Program (IRAP) for Darktrace / NETWORK™ and Darktrace / OT™ against the Australian Government’s Information Security Manual PROTECTED-level controls. In the United States, Darktrace Federal continues to deliver the Darktrace technology to Department of War, Department of State, and Federal civilian organizations via its on-premises and FedRAMP CLASS D (High) Authorization platforms.
Together, these achievements demonstrate Darktrace’s ability to meet rigorous public-sector security requirements and reinforce its position as a trusted provider of mission-critical cybersecurity technology for government environments.
Meet us at NATO Edge 2026
Darktrace representatives will attend NATO Edge 2026, NCIA’s flagship technology event, in İzmir, Türkiye, from 17 to 19 November. We look forward to meeting government, military, and industry partners to discuss their cybersecurity priorities and how we can support them.