ブログ
/
Network
/
August 5, 2025

2025 Cyber Threat Landscape: Darktrace’s Mid-Year Review

Explore key cyber threat trends observed across Darktrace’s customer base in the first half of 2025. As threat actors increasingly adopt AI and diversify their techniques and tooling, anomaly-based detection continues to prove vital in defending against evolving attacks.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Emma Foulger
Global Threat Research Operations Lead
Default blog image
05
Aug 2025

Note: Following initial publication, an error was identified in the previously reported number of QR codes observed in phishing emails in February 2025. This figure was originally stated as over 1 million, when in fact it was over 100,000. The error has since been corrected.

‍

‍

2025: Threat landscape in review

The following is a retrospective of the first six months of 2025, highlighting key findings across the threat landscape impacting Darktrace customers.

Darktrace observed a wide range of tactics during this period, used by various types of threat actors including advanced persistent threats (APTs), Malware-as-a-Service (MaaS) and Ransomware-as-a-Service (RaaS) groups.

Methodology

Darktrace’s Analyst team conduct investigations and research into threats facing organizations and security teams across our customer base.  This includes direct investigations with our 24/7 Security Operations Centre (SOC), via services such as Managed Detection and Response (MDR) and Managed Threat Detection, as well as broader cross-fleet research through our Threat Research function.

At the core of our research is Darktrace’s anomaly-based detection, which the Analyst team contextualizes and analyzes to provide additional support to customers and deepen our understanding of the threats they face.

Threat actors are incorporating AI into offensive operations

Threat actors are continuously evolving their tactics, techniques, and procedures (TTPs), posing an ongoing challenge to effective defense hardening. Increasingly, many threat actors are adopting AI, particularly large language models (LLMs), into their operations to enhance the scale, sophistication, and efficacy of their attacks.

The evolving functionality of malware, such as the recently reported LameHug malware by CERT-UA, which uses an open-source LLM, exemplifies this observation [1].

Threat landscape trends in 2025

Threat actors applying AI to Email attacks

LLMs present a clear opportunity for attackers to take advantage of AI and create effective phishing emails at speed. While Darktrace cannot definitively confirm the use of AI to create the phishing emails observed across the customer base, the high volume of phishing emails and notable shifts in tactic could potentially be explained by threat actors adopting new tooling such as LLMs.

  • The total number of malicious emails detected by Darktrace from January to May 2025 was over 12.6 million
  • VIP users continue to face significant threat, with over 25% of all phishing emails targeting these users in the first five months of 2025 ‍
  • QR code-based phishing emails have remained a consistent tactic, with a similar proportion observed in January-May 2024 and 2025. The highest numbers were observed in February 2025, with over 100,000 detected in that month alone.
  • Shifts towards increased sophistication within phishing emails are emerging, with a year-on-year increase in the proportion of phishing emails containing either a high text volume or multistage payloads. In the first five months of 2025, 32% of phishing emails contained a high volume of text.

The increase in proportion of phishing emails with a high volume of text in particular could point towards threat actors leveraging LLMs to create phishing emails with large, but believable, text in an easy and efficient way.

The above email statistics are derived from analysis of monitored Darktrace / EMAIL model data for all customer deployments hosted in the cloud between January 1 and May 31, 2025.

Campaign Spotlight: Simple, Quick - ClickFix

An interesting technique Darktrace observed multiple times throughout March and April was ClickFix social engineering, which exploits the intersection between humans and technology to trick users into executing malicious code on behalf of the attacker.

  • While this technique has been around since 2024, Darktrace observed campaign activity in the first half of 2025 suggesting a resurgence.  
  • A range of threat actors – from APTs to MaaS and RaaS have adopted this technique to deliver secondary payloads, like information stealing malware.
  • Attackers use fraudulent or compromised legitimate websites to inject malicious plugins that masquerade as fake CAPTCHAs.
  • Targeted users believe they are completing human verification or resolving a website issue, unaware that they are being guided through a series of simple steps to execute PowerShell code on their system.
  • Darktrace observed campaign activity during the first half of 2025 across a range of sectors, including Government, Healthcare, Insurance, Retail and, Non-profit.

Not just AI: Automation is enabling Ransomware and SaaS exploitation

The rise of phishing kits like FlowerStorm and Mamba2FA, which enable phishing and abuse users’ trust by mimicking legitimate services to bypass multi-factor authentication (MFA), highlight how the barriers to entry for sophisticated attacks continue to fall, enabling new threat actors. Combined with Software-as-a-Service (SaaS) account compromise, these techniques make up a substantial portion of cybercriminal activity observed by Darktrace so far this year.

Credentials remain the weak link

A key theme across multiple cases of ransomware was threat actors abusing compromised credentials to gain initial entry into networks via:

  • Unauthorized access to internet-facing technology such as RDP servers and virtual private networks (VPNs).
  • Unauthorized access to SaaS accounts.

SaaS targeted ransomware is on the rise

The encryption of files within SaaS environments observed by Darktrace demonstrates a continued trend of ransomware actors targeting these platforms over traditional networks, potentially driven by a higher return on investment.

SaaS accounts are often less protected than traditional systems because of Single Sign-On (SSO).  Additionally, platforms like Salesforce often host sensitive data, including emails, financial records, customer information, and network configuration details. This stresses the need for robust identity management practices and continuous monitoring.

RaaS is adding complexity and speed to cyber attacks

RaaS has dominated the attack landscape, with groups like Qilin, RansomHub, and Lynx all appearing multiple times in cases across Darktrace’s customer base over the past six months. Detecting ransomware attacks before the encryption stage remains a significant challenge, particularly in RaaS operations where different affiliates often use varying techniques for initial entry and earlier stages of the attack. Darktrace’s recent analysis of Scattered Spider underscores the challenge of hardening defenses against such varying techniques.

CVE exploitation continues despite available patches

Darktrace has also observed ransomware gangs exploiting known Common Vulnerabilities and Exposures (CVEs), including the Medusa ransomware group’s use of the SimpleHelp vulnerabilities: CVE-2024-57727 and CVE-2024-57728 in March, despite patches being made available in January [2].

Misused tools + delayed patches = growing cyber risk

The exploitation of common remote management tools like SimpleHelp highlights the serious challenges defenders face when patch management cycles are suboptimal. As threat actors continue to abuse legitimate services for malicious purposes, the challenges facing defenders will only grow more complex.

Edge exploitation

It comes as no surprise that exploitation of internet-facing devices continued to feature prominently in Darktrace’s Threat Research investigations during the first half of 2025.

Observed CVE exploitation included:

Many of Darktrace’s observations of CVE exploitation so far in 2025 align with wider industry reporting, which suggests that Chinese-nexus threat actors were deemed to likely have exploited these technologies prior to public disclosure. In the case of CVE-2025-0994 - a vulnerability affecting Trimble Cityworks, an asset management system designed for use by local governments, utilities, airports, and public work agencies [3] - Darktrace observed signs of exploitation as early as January 19, well before vulnerability’s public disclosure on February 6 [4]. Darktrace’s early identification of the exploitation stemmed from the detection of a suspicious file download from 192.210.239[.]172:3219/z44.exe - later linked to Chinese-speaking threat actors in a campaign targeting the US government [5].

This case demonstrates the risks posed by the exploitation of internet-facing devices, not only those hosting more common technologies, but also software associated specifically tied to Critical National Infrastructure (CNI); a lucrative target for threat actors. This also highlights Darktrace’s ability to detect exploitation of internet-facing systems, even without a publicly disclosed CVE. Further examples of how Darktrace’s anomaly detection can uncover malicious activity ahead of public vulnerability disclosures can be found here.

New threats and returning adversaries

In the first half of 2025, Darktrace observed a wide range of threats, from sophisticated techniques employed by APT groups to large-scale campaigns involving phishing and information stealers.

BlindEagle (APT-C-36)

Among the observed APT activity, BlindEagle (APT-C-36) was seen targeting customers in Latin America (LATM), first identified in February, with additional cases seen as recently as June.

Darktrace also observed a customer targeted in a China-linked campaign involving the LapDogs ORB network, with activity spanning from December 2024 and June 2025. These likely nation-state attacks illustrate the continued adoption of cyber and AI capabilities into the national security goals of certain countries.

Sophisticated malware functionality

Further sophistication has been observed within specific malware functionality - such as the malicious backdoor Auto-Color, which has now been found to employ suppression tactics to cover its tracks if it is unable to complete its kill chain - highlighting the potential for advanced techniques across every layer of an attack.‍

Familiar foes

Alongside new and emerging threats, previously observed and less sophisticated tools, such as worms, Remote Access Trojans (RATs), and information stealers, continue to impact Darktrace customers.

The Raspberry Robin worm... First seen in 2021, has been repeatedly identified within Darktrace’s customer base since 2022. Most recently, Darktrace’s Threat Research team identified cases in April and May this year. Recent open-source intelligence (OSINT) reporting suggests that Raspberry Robin continues to evolve its role as an Initial Access Broker (IAB), paving the way for various attacks and remaining a concern [6].

RATs also remain a threat, with examples like AsyncRAT and Gh0st RAT impacting Darktrace customers.

In April multiple cases of MaaS were observed in Darktrace’s customer base, with information stealers Amadey and Stealc, as well as GhostSocks being distributed as a follow up payload after an initial Amadey infection.

Conclusion

As cyber threats evolve, attackers are increasingly harnessing AI to craft highly convincing email attacks, automating phishing campaigns at unprecedented scale and speed. This, coupled with rapid exploitation of vulnerabilities and the growing sophistication of ransomware gangs operating as organized crime syndicates, makes today’s threat landscape more dynamic and dangerous than ever. Cyber defenders collaborate to combat these threats – the coordinated takedown of Lumma Stealer in May was a notable win for both industry and law-enforcement [7], however OSINT suggests that this threat persists [8], and new threats will continue to arise.

Traditional security tools that rely on static rules or signature-based detection often struggle to keep pace with these fast-moving, adaptive threats. In this environment, anomaly-based detection tools are no longer optional—they are essential. By identifying deviations in normal user and system behavior, tools like Darktrace provide a proactive layer of defense capable of detecting novel and emerging threats, even those that bypass conventional security measures. Investing in anomaly-based detection is critical to staying ahead of attackers who now operate with automation, intelligence, and global coordination.

Credit to Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones (VP, Security & AI Strategy, Field CISO),  Eugene Chua (Principal Cyber Analyst & Analyst Team Lead), Nahisha Nobregas (Senior Cyber Analyst), Nicole Wong (Principal Cyber Analyst), Justin Torres (Senior Cyber Analyst), Matthew John (Director of Operations, SOC), Sam Lister (Specialist Security Researcher), Ryan Traill (Analyst Content Lead) and the Darktrace Incident Management team.

The information contained in this blog post is provided for general informational purposes only and represents the views and analysis of Darktrace as of the date of publication. While efforts have been made to ensure the accuracy and timeliness of the information, the cybersecurity landscape is dynamic, and new threats or vulnerabilities may have emerged since this report was compiled.

This content is provided “as is” and without warranties of any kind, either express or implied. Darktrace makes no representations or warranties regarding the completeness, accuracy, reliability, or suitability of the information, and expressly disclaims all warranties.

Nothing in this blog post should be interpreted as legal, technical, or professional advice. Users of this information assume full responsibility for any actions taken based on its content, and Darktrace shall not be liable for any loss or damage resulting from reliance on this material. Reference to any specific products, companies, or services does not constitute or imply endorsement, recommendation, or affiliation.

Appendices

Indicators of Compromise (IoCs)

IoC - Type - Description + Probability

LapDogs ORB network, December 2024-June 2025

www.northumbra[.]com – Hostname – Command and Control (C2) server

103.131.189[.]2 – IP Address - C2 server, observed December 2024 & June 2025

103.106.230[.]31 – IP Address - C2 server, observed December 2024

154.223.20[.]56 – IP Address – Possible C2 server, observed December 2024

38.60.214[.]23 – IP Address – Possible C2 server, observed January & February 2025

154.223.20[.]58:1346/systemd-log – URL – Possible ShortLeash payload, observed December 2024

CN=ROOT,OU=Police department,O=LAPD,L=LA,ST=California,C=US - TLS certificate details for C2 server

CVE-2025-0994, Trimble Cityworks exploitation, January 2025

192.210.239[.]172:3219/z44.exe – URL - Likely malicious file download

AsyncRAT, February-March 2025

windows-cam.casacam[.]net – Hostname – Likely C2 server

88.209.248[.]141 – IP Address – Likely C2 server

207.231.105[.]51 – IP Address – Likely C2 server

163.172.125[.]253 – IP Address – Likely C2 server

microsoft-download.ddnsfree[.]com – Hostname – Likely C2 server

95.217.34[.]113 – IP Address – Likely C2 server

vpnl[.]net – Hostname – Likely C2 server

157.20.182[.]16 – IP Address - Likely C2 server

185.81.157[.]19 – IP Address – Likely C2 server

dynamic.serveftp[.]net – IP Address – Likely C2 server

158.220.96.15 – IP Address – Likely C2 server

CVE-2024-57727 & CVE-2024-57728, SimpleHelp RMM exploitation, March 2025

213.183.63[.]41 – IP Address - C2 server

213.183.63[.]41/access/JWrapper-Windows64JRE-version.txt?time=3512082867 – URL - C2 server

213.183.63[.]41/access/JWrapper-Windows64JRE-00000000002-archive.p2.l2 – URL - C2 server

pruebas.pintacuario[.]mx – Hostname – Possible C2 server

144.217.181[.]205 – IP Address – Likely C2 server

erp.ranasons[.]com – Hostname – Possible destination for exfiltration

143.110.243[.]154 – IP Address – Likely destination for exfiltration

Blind Eagle, April-June 2025

sostenermio2024.duckdns[.]org/31agosto.vbs – URL – Possible malicious file download

Stealc, April 2025

88.214.48[.]93/ea2cb15d61cc476f[.]php – URL – C2 server

Amadey & GhostSocks, April 2025

195.82.147[.]98 – IP Address - Amadey C2 server

195.82.147[.]98/0Bdh3sQpbD/index.php – IP Address – Likely Amadey C2 activity

194.28.226.181 – IP Address – Likely GhostSocks C2 server

RaspberryRobin, May 2025

4j[.]pm – Hostname – C2 server

4xq[.]nl – Hostname – C2 server

8t[.]wf – Hostname – C2 server

Gh0stRAT, May 2025

lu.dssiss[.]icu  - Hostname – Likely C2 server

192.238.133[.]162:7744/1-111.exe – URL – Possible addition payload

8e9dec3b028f2406a8c546a9e9ea3d50609c36bb - SHA1 - Possible additional payload

f891c920f81bab4efbaaa1f7a850d484 - MD5 – Possible additional payload

192.238.133[.]162:7744/c3p.exe – URL - Possible additional payload

03287a15bfd67ff8c3340c0bae425ecaa37a929f - SHA1 - Possible additional payload

02aa02aee2a6bd93a4a8f4941a0e6310 - MD5 - Possible additional payload

192.238.133[.]162:7744/1-1111.exe – URL - Possible additional payload

1473292e1405882b394de5a5857f0b6fa3858fd1 - SHA1 - Possible additional payload

69549862b2d357e1de5bab899ec0c817 - MD5 - Possible additional payload

192.238.133[.]162:7744/1-25.exe – URL -  Possible additional payload

20189164c4cd5cac7eb76ba31d0bd8936761d7a7  - SHA1 - Possible additional payload

f42aa5e68b28a3f335f5ea8b6c60cb57 – MD5 - Possible additional payload

192.238.133[.]162:7744/Project1_se.exe – URL - Possible additional payload

fea1e30dfafbe9fa9abbbdefbcbe245b6b0628ad - SHA1 - Possible additional payload

5ea622c630ef2fd677868cbe8523a3d5 - MD5 - Possible additional payload

192.238.133[.]162:7744/Project1_se.exe - URL - Possible additional payload

aa5a5d2bd610ccf23e58bcb17d6856d7566d71b9  - SHA1 - Possible additional payload

9d33029eaeac1c2d05cf47eebb93a1d0 - MD5 - Possible additional payload

References and further reading

1.        https://cip.gov.ua/en/news/art28-atakuye-sektor-bezpeki-ta-oboroni-za-dopomogoyu-programnogo-zasobu-sho-vikoristovuye-shtuchnii-intelekt?utm_medium=email&_hsmi=113619842&utm_content=113619842&utm_source=hs_email

2.        https://www.s-rminform.com/latest-thinking/cyber-threat-advisory-medusa-and-the-simplehelp-vulnerability

3.        https://assetlifecycle.trimble.com/en/products/software/cityworks

4.     https://nvd.nist.gov/vuln/detail/CVE-2025-0994

5.     https://blog.talosintelligence.com/uat-6382-exploits-cityworks-vulnerability/

6.        https://www.silentpush.com/blog/raspberry-robin/

7.        https://blogs.microsoft.com/on-the-issues/2025/05/21/microsoft-leads-global-action-against-favored-cybercrime-tool/

8.     https://www.trendmicro.com/en_sg/research/25/g/lumma-stealer-returns.html

Related Darktrace investigations

-              ClickFix

-              FlowerStorm

-              Mamba 2FA

-              Qilin Ransomware

-              RansomHub Ransomware

-              RansomHub Revisited

-              Lynx Ransomware

-              Scattered Spider

-              Medusa Ransomware

-              Legitimate Services Malicious Intentions

-              CVE-2025-0282 and CVE-2025-0283 – Ivanti CS, PS and ZTA

-              CVE-2025-31324 – SAP Netweaver

-              Pre-CVE Threat Detection

-              BlindEagle (APT-C-36)

-              Raspberry Robin Worm

-              AsyncRAT

-              Amadey

-              Lumma Stealer

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Emma Foulger
Global Threat Research Operations Lead

More in this series

No items found.

Blog

/

AI

/

September 30, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

September 30, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

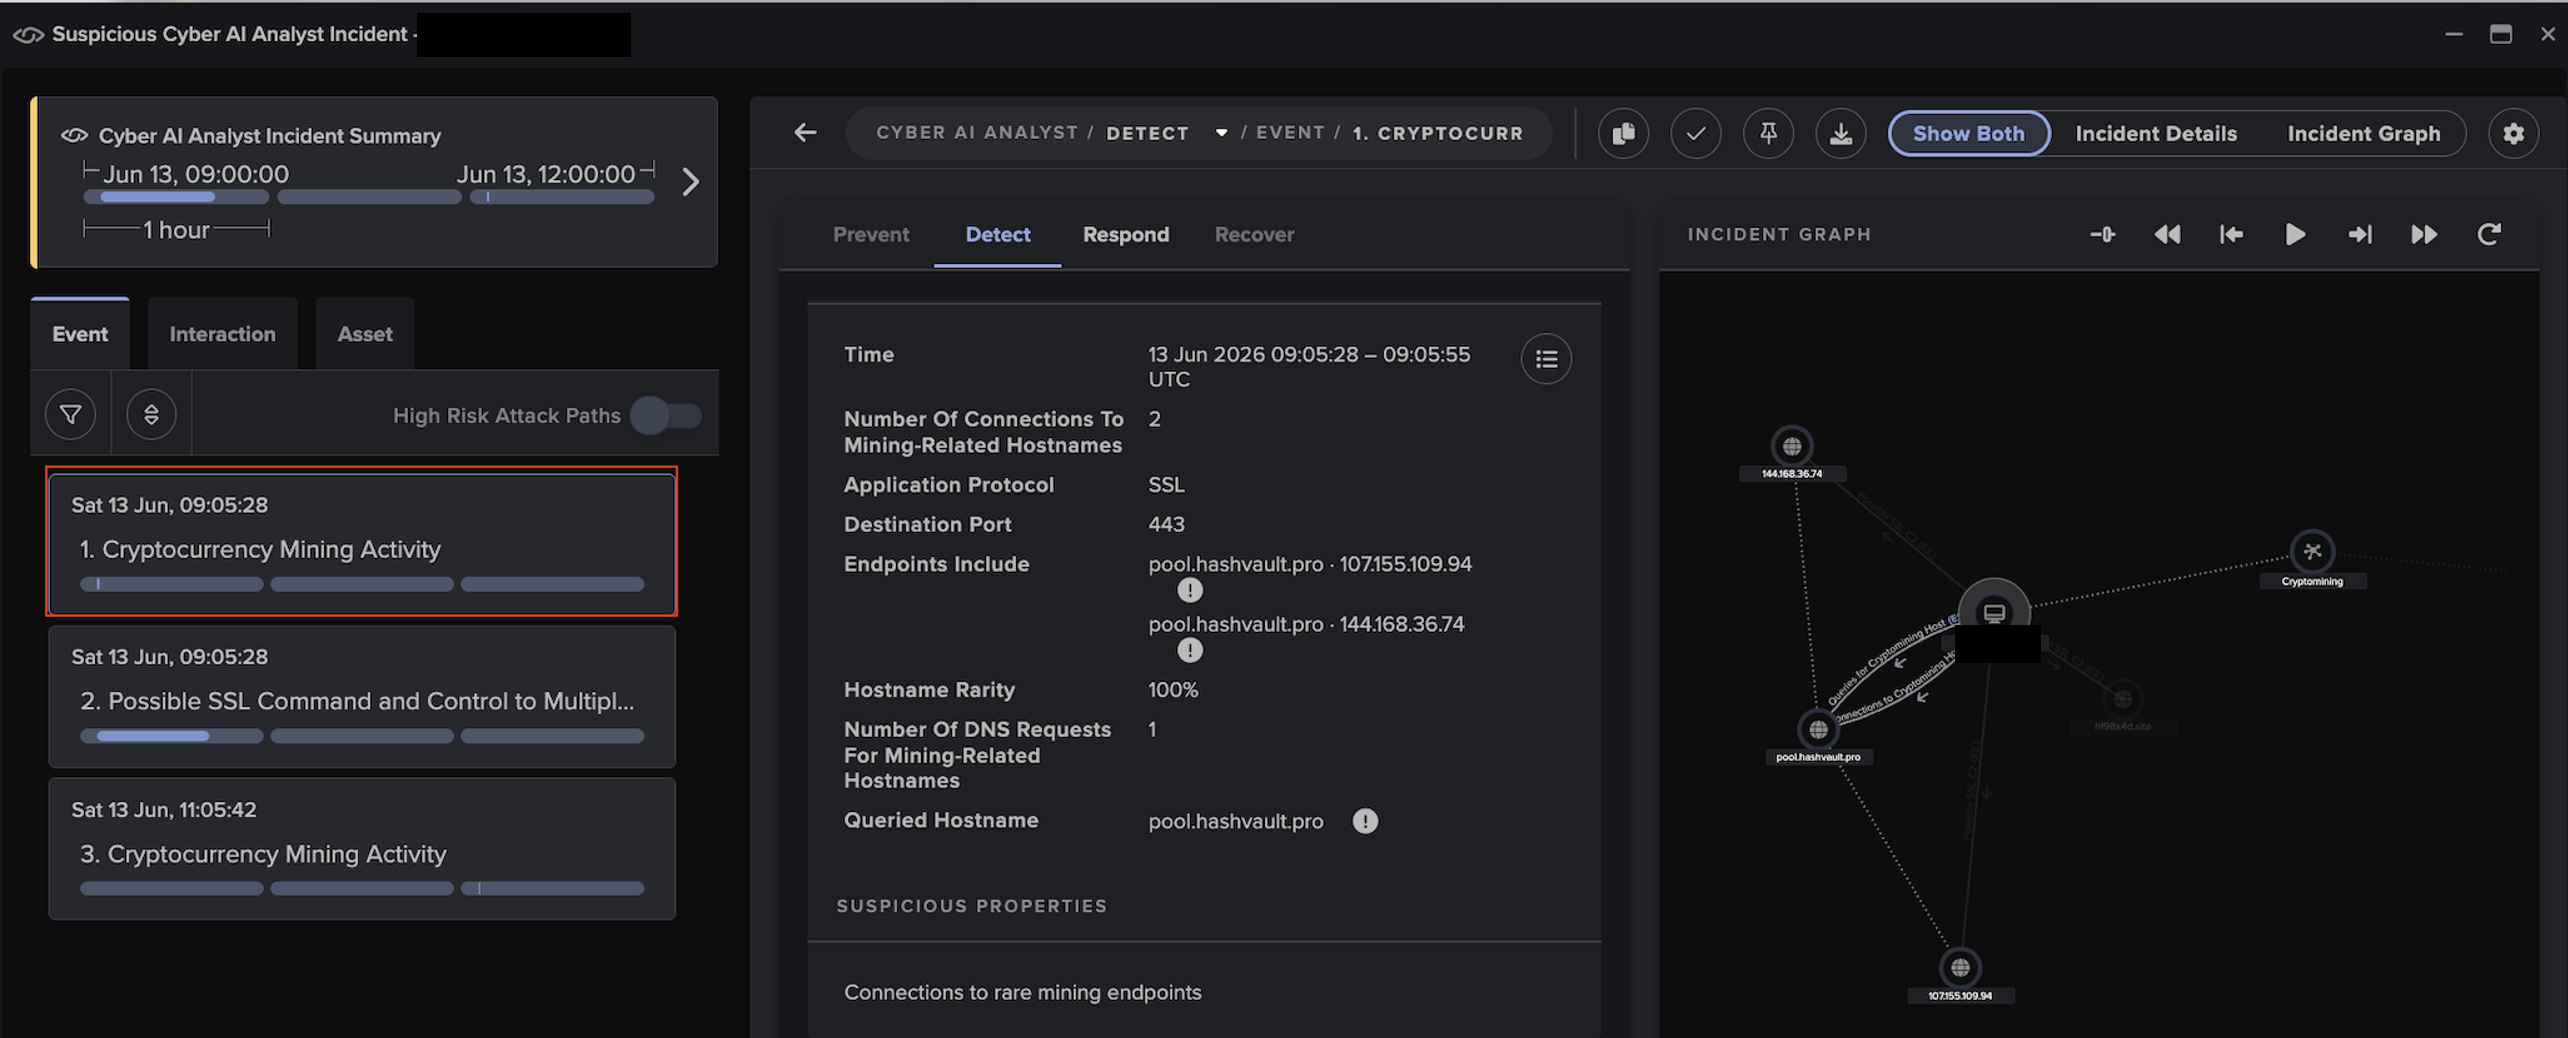
Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

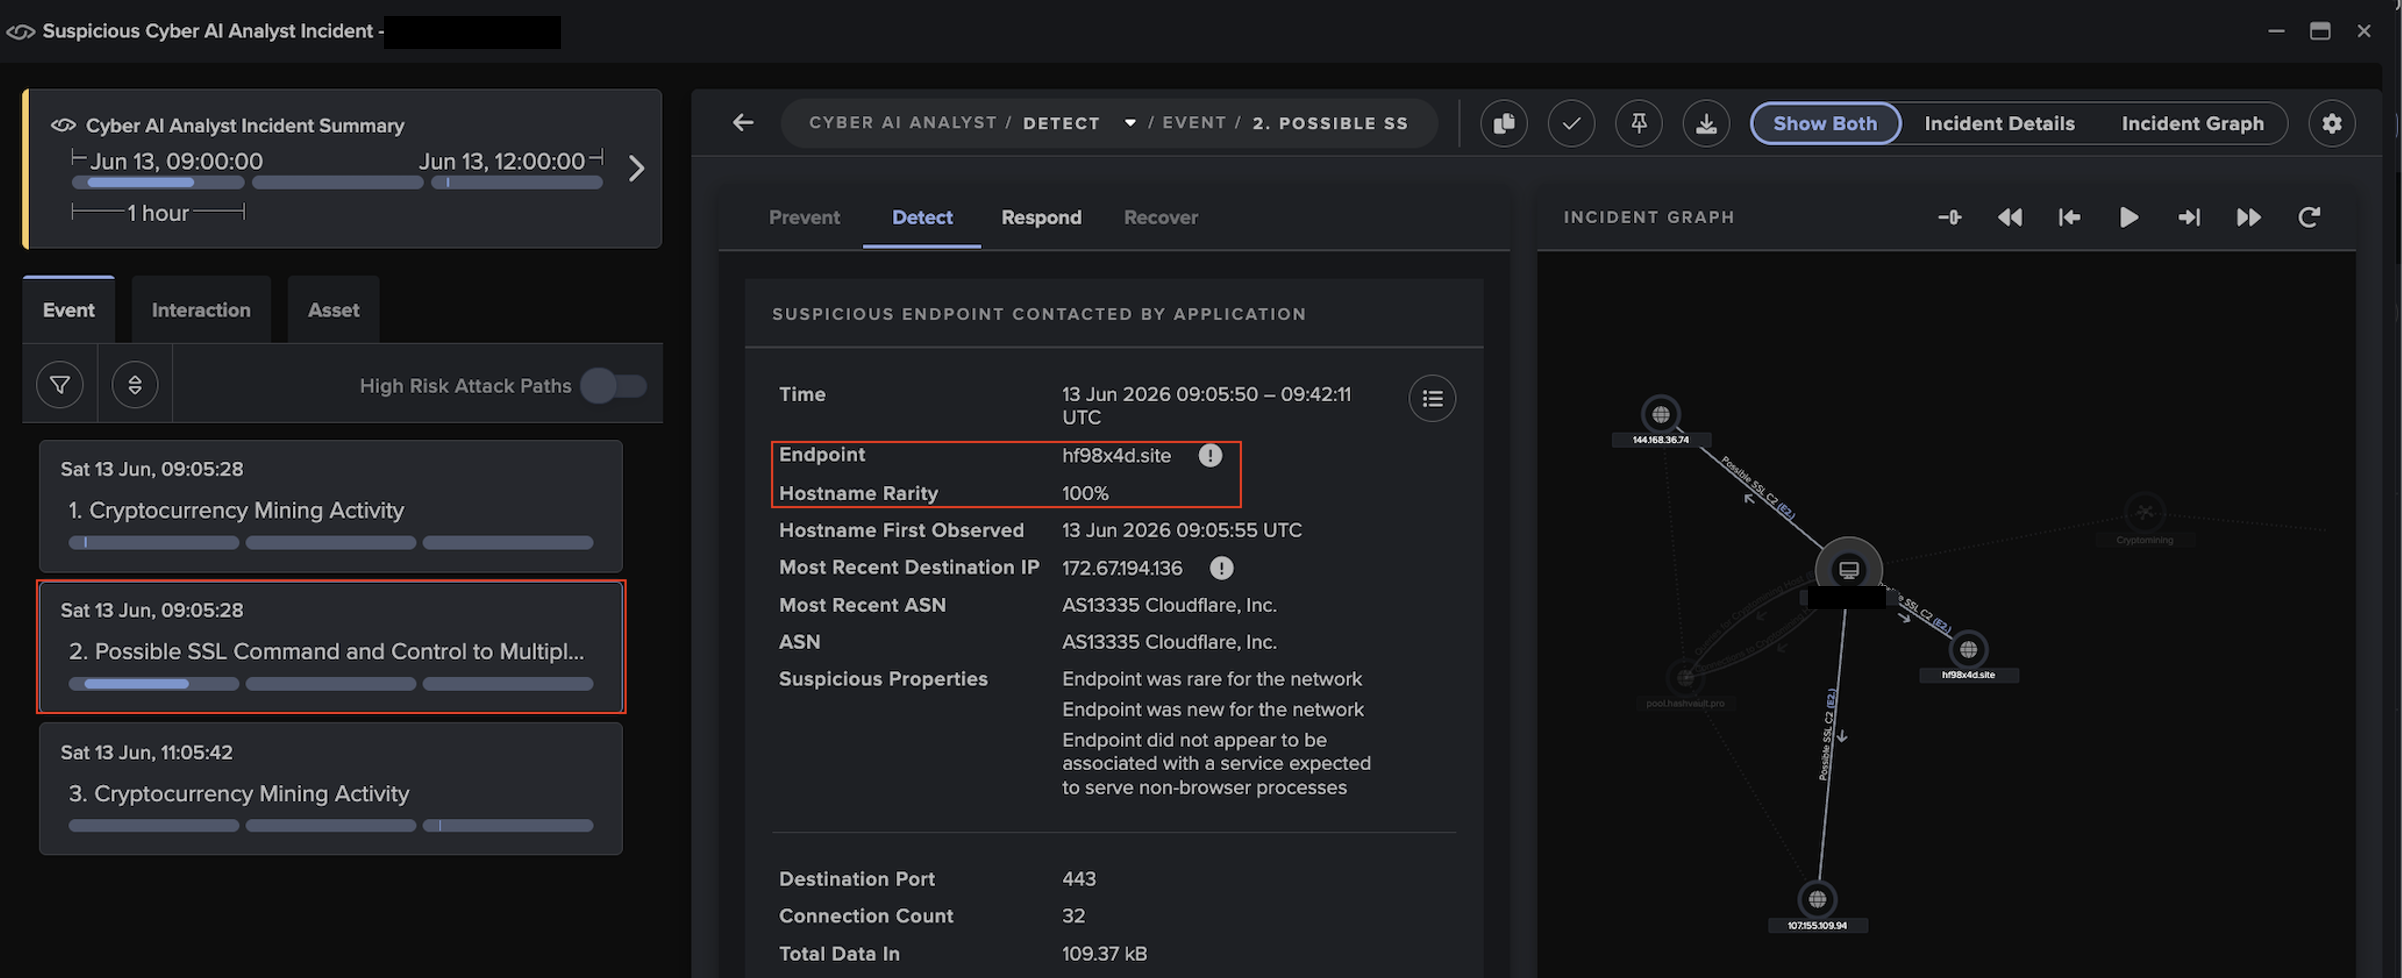
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

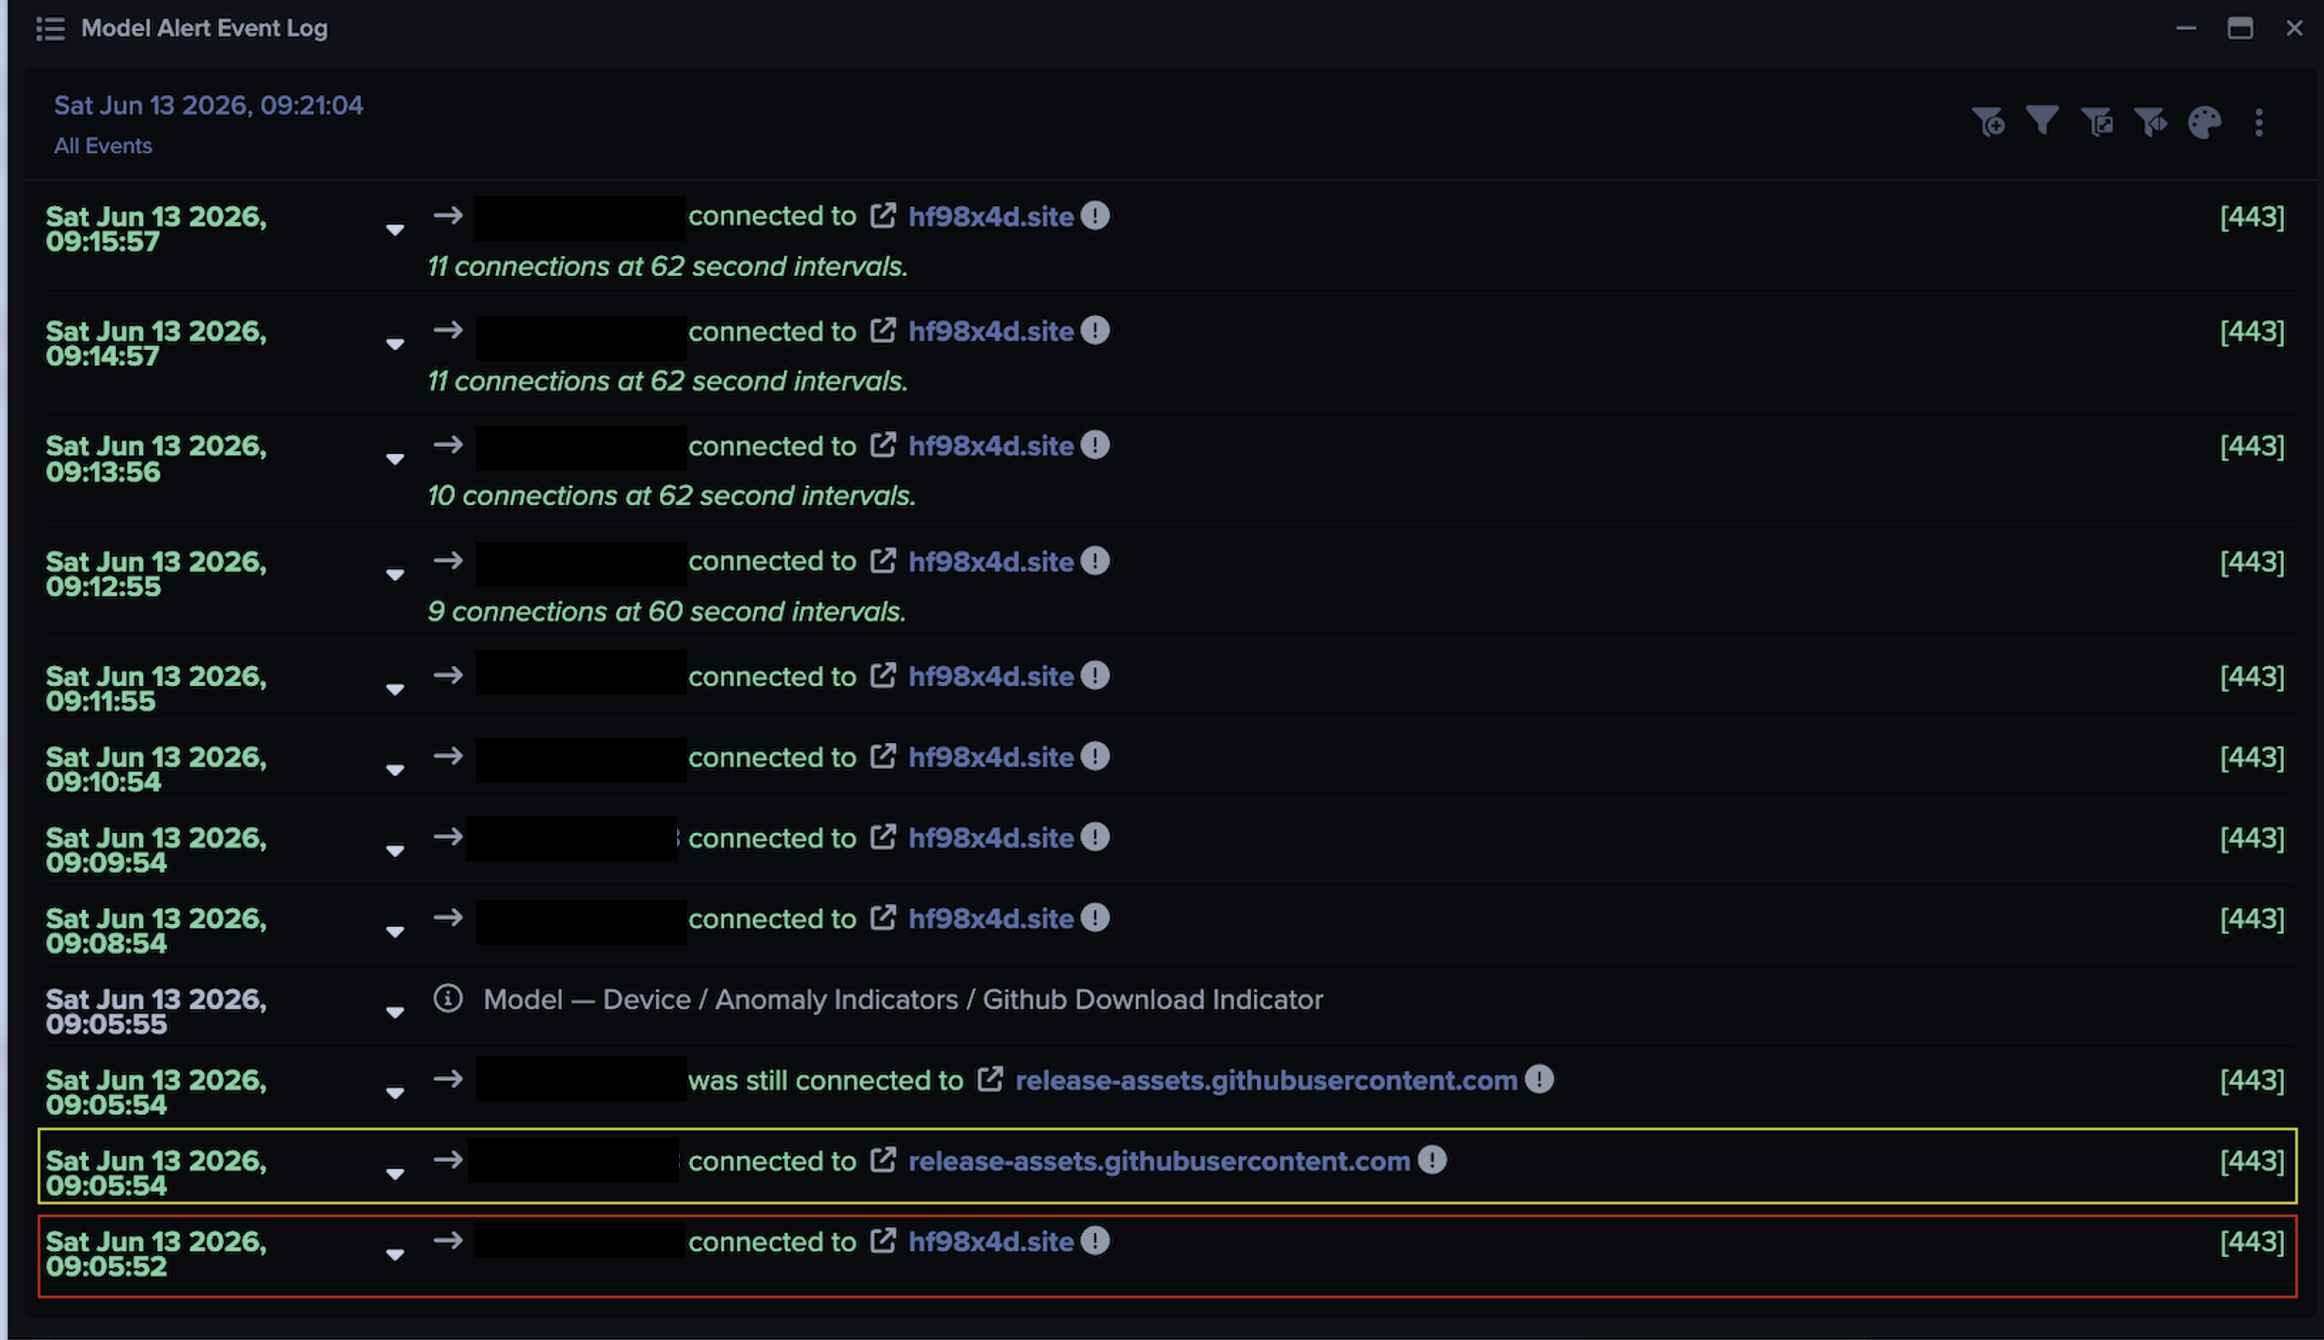
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ