ブログ
/
Network
/
May 21, 2026

ダークトレース、2026年Gartner® Network Detection and Response(NDR)部門のMagic Quadrant™レポートにおいて2年連続でLeaderの1社に認められる

ダークトレースは、2026年Gartner® Network Detection and Response(NDR)部門のMagic Quadrant™レポートにおいて2年連続でLeaderの1社に認められました。 このことは、NDR分野における実績の積み重ね、継続したAIイノベーション、そして世界のお客様に提供してきた安定した成果が反映されたものと当社は確信しています。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Mikey Anderson
Senior Product Marketing Manager
Default blog image
21
May 2026

NDR部門での継続した評価  

ダークトレースは2026年Gartner® Magic Quadrant™レポートのNetwork Detection and Response(NDR)部門において、2年連続でLeaderの1社に認められました。

この継続的評価は、変化を続けるNDR市場における安定した実行力、適応力、成果が反映されたものと私たちは確信しています。

業界のアナリストによりNDR分野のLeaderの1社と認識されたことを大いに誇りに思う一方で、これは当社に対する評価の1部にすぎません。ダークトレースは2025年Gartner® Peer Insights™ のNDR部門において、顧客の直接のフィードバックおよび現実世界での体験に基づき、唯一Customers’ Choiceに選出されています。

私たちはこれら2つの指標の組み合わせが重要であると考えています。1つは市場がどのような評価をしたかを反映しています。もう1つは、テクノロジーが実際にどのように機能しているかを反映したものです。

ダークトレースがリーダーとして評価され続けている理由

当社が2年連続でLeaderの1社との評価を受けたことは、NDR分野での継続した実現力、絶え間ないAIイノベーション、および世界中の顧客やパートナーに対してセキュリティの成果を提供してきた実績が反映されたものであると私たちは確信しています。

私たちはまた、NDR市場におけるリーダーとの位置づけは、当社の独自で多層的なAIアプローチの証であると感じており、このアプローチのためにFast Companyの2026年度Most Innovative AI Companies(最も革新的なAI企業)リストで第7位に選ばれ、さらにCRNのAI 100において最も注目されるAIサイバーセキュリティ企業の1社と認められています。

複雑な現実世界のさまざまな環境に適応

組織が防御しているのはもはや1つのネットワーク境界だけではありません。多様なユーザー、デバイス、アプリケーションの混在、そしてハイブリッド環境間を移動するデータを保護しなければならないのです。

ダークトレースはこうした条件下においても可視性と検知能力を維持し、拡大するアクティビティをセキュリティチームが理解できるようにすることに集中してきました。

世界中の組織を柔軟にサポート

セキュリティの成果は、検知能力と同じように運用とサポートによっても左右されます。

ダークトレースは世界29か国で現地展開への投資を続けており、組織がその地域の要件、社内プロセス、チームの構成に沿った形でNDRを運用できるよう支援しています。

検知を超えてAIを応用

サイバーセキュリティにおけるAIは、多くの場合検知精度を向上させる手法として位置付けられています。しかし、より重要な技術革新はAIを意思決定や対応に生かすことです。

ダークトレースは、リアルタイムのビヘイビア分析と過去の攻撃パターンから得られた情報を組み合わせ、ライブ環境と過去のインシデントデータの両方から学習するモデルの開発を続けています。

インシデントグラフやDIGEST(Darktrace Incident Graph Evaluation for Security Threats)などの技術を利用し、アクティビティは単独で分析されることはありません。ユーザー、デバイス、接続、およびイベント間の関係が継続的にマッピングされることで、システムは過去にあった類似のインシデントの進展も含めてインシデントの進行状況を把握し、再構築することができます。

これらのパターンを評価することにより、Darktraceはインシデントがエスカレートする可能性を評価し、最もリスクの高いアクティビティを優先づけ、最も関連性の高いコンテキストを提示して調査することができます。

これによりセキュリティオペレーションは単に異常を識別することから、それらの軌跡を理解することへとシフトし、潜在的な影響を予期するとともに、より早期に、より正確に対応することが可能になります。

NDRは受け身の検知からプロアクティブなAI駆動のセキュリティへ

従来のNDRへのアプローチは脅威が明らかに確認できるようになってから受動的に識別することが中心でした。しかしこのモデルに頼ることは次第に困難になっています。

攻撃者はもはや、目立つ形で作戦を展開していません。彼らは正規の認証情報や信頼されるツールを利用し、日常の活動に紛れ込むローアンドスロー型のテクニックを駆使しています。何かが明らかに悪意のあるものに見えるとき、その影響は既に進行中であることがしばしばです。

これが受動的な検知の根本的な限界です。既に脅威と見えるものを識別することに依存しているからです。

その結果、最も重大なインシデントの多くが完全に漏れ落ちてしまいます。

内部関係者の活動、漏洩した認証情報、そして新手の攻撃は、従来のアラートをトリガーすることはめったにありません。既知のパターンに沿っていないからです。それらは表面上、正規の動作に見えることがしばしばであり、より深いコンテキスト情報がなければ通常の振る舞いと区別することは困難です。

このことが、今回のGartner社による評価がNDR全体の自律的、プロアクティブかつ先制的なセキュリティオペレーションへのシフトを反映したものと私たちが考えている理由です。

環境内での正常な振る舞いを理解することにより、脅威が発生している中で確認を待つのではなく、かすかな逸脱を識別することができるようになります。

Darktraceの自己学習型AIは行動を理解するために設計されています。それぞれの組織の通常のパターンを継続的に学習することでリアルタイムに逸脱を検知し、セキュリティチームがリスクの初期兆候に対応して攻撃が進行する時間を短縮する、プロアクティブかつ先制的なNDRモデルを実現します。

複数の事例において、このビヘイビアベースのアプローチが早期の脅威検知につながっており、DarktraceはCVE公開前のゼロデイ脅威を含む完全に未知の脅威を検知しています。脆弱性が公開され広く理解される前からわずかな挙動の変化を検知することで、組織は被害が出る前に脅威を軽減することができます。

この違いは目立ちませんが非常に重要です。現代のNDRソリューションは、何が起こったかを説明するシステムから、脅威が発生するのを未然に防ぐのを支援するシステムへとシフトしなければなりません。ダークトレースはこの変革の最前線に立ち、プロアクティブなネットワークレジリエンスの構築および維持を支援しています。

NDRの最前線でイノベーションを継続

私たちは、リーダーとしての評価は現在の市場の状況を反映したものと考えています。そして今後の状況はイノベーションの継続により決まるでしょう。

ビジネスの進化により、AIツールやエージェント等の新たなテクノロジーが新たなセキュリティリスクや課題をもたらしており、セキュリティチームは単なる検知以上のものを必要としています。リスクの進行に対する完全な理解、コンテキストを考慮して調査し、マシンスピードで脅威を封じ込める能力が必要なのです。

Darktrace / NETWORK はこれらを包括的に提供するよう設計されています。自己学習型AIは、それぞれの組織の環境に継続的に適応し、新たな脅威をの兆候であるわずかな挙動の変化を識別します。統合された調査機能と自律遮断により、検知から対応までの時間が短縮され、セキュリティチームはより迅速かつ自信を持って行動できるようになります。

この組み合わせにより、組織は既知および未知の脅威、内部関係者による脅威を発生とともに検知および封じ込めることができると同時に、全体のレジリエンスを強化していくことが可能になります。

Gartner® Magic Quadrant™のNDR部門で2度Leaderの1社と評価され、2025年Gartner® Peer Insights™において唯一のCustomers’ Choiceに選ばれたダークトレースは、現代の多様な環境の要求に応えるためにプラットフォームを進化させ続け、ネットワークセキュリティに対してより包括的かつ適応型のアプローチを提供しています。

‍

[related-resource]

免責事項:The 2026 Gartner® Magic Quadrant™ for Network Detection and Response (NDR) ,The 2026 Gartner® Magic Quadrant™ for Network Detection and Response (NDR), Thomas Lintemuth, Charanpal Bhogal, Nahim Fazal, 18 May 2026.

Gartnerは、Gartnerリサーチの発行物に掲載された特定のベンダー、製品またはサービスを推奨するものではありません。また、最高のレーティング又はその他の評価を得たベンダーのみを選択するようにテクノロジーユーザーに助言するものではありません。

Gartnerの調査出版物はGartnerの調査組織の意見で構成されているものであり、事実の表明として解釈されるべきではありません。Gartnerは、明示または黙示を問わず、本リサーチの商品性や特定目的への適合性を含め、一切の責任を負うものではありません。

GARTNERはGartner, Inc.および/または米国内および国際的な関連会社の登録商標およびサービスマークであり、許可を得て本書に記載されています。All rights reserved.

Magic QuadrantはGartner, Inc. および/またはその関連会社の登録商標であり、許可を得て本書に記載されています。All rights reserved.

レポート全文をダウンロード

2026年の Gartner® Magic Quadrant™ レポートをダウンロードして、ダークトレースが NDR 市場のリーダーとしてどのように技術的イノベーションを続けているかをご確認ください。

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Mikey Anderson
Senior Product Marketing Manager

More in this series

No items found.

Blog

/

AI

/

October 5, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

October 5, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

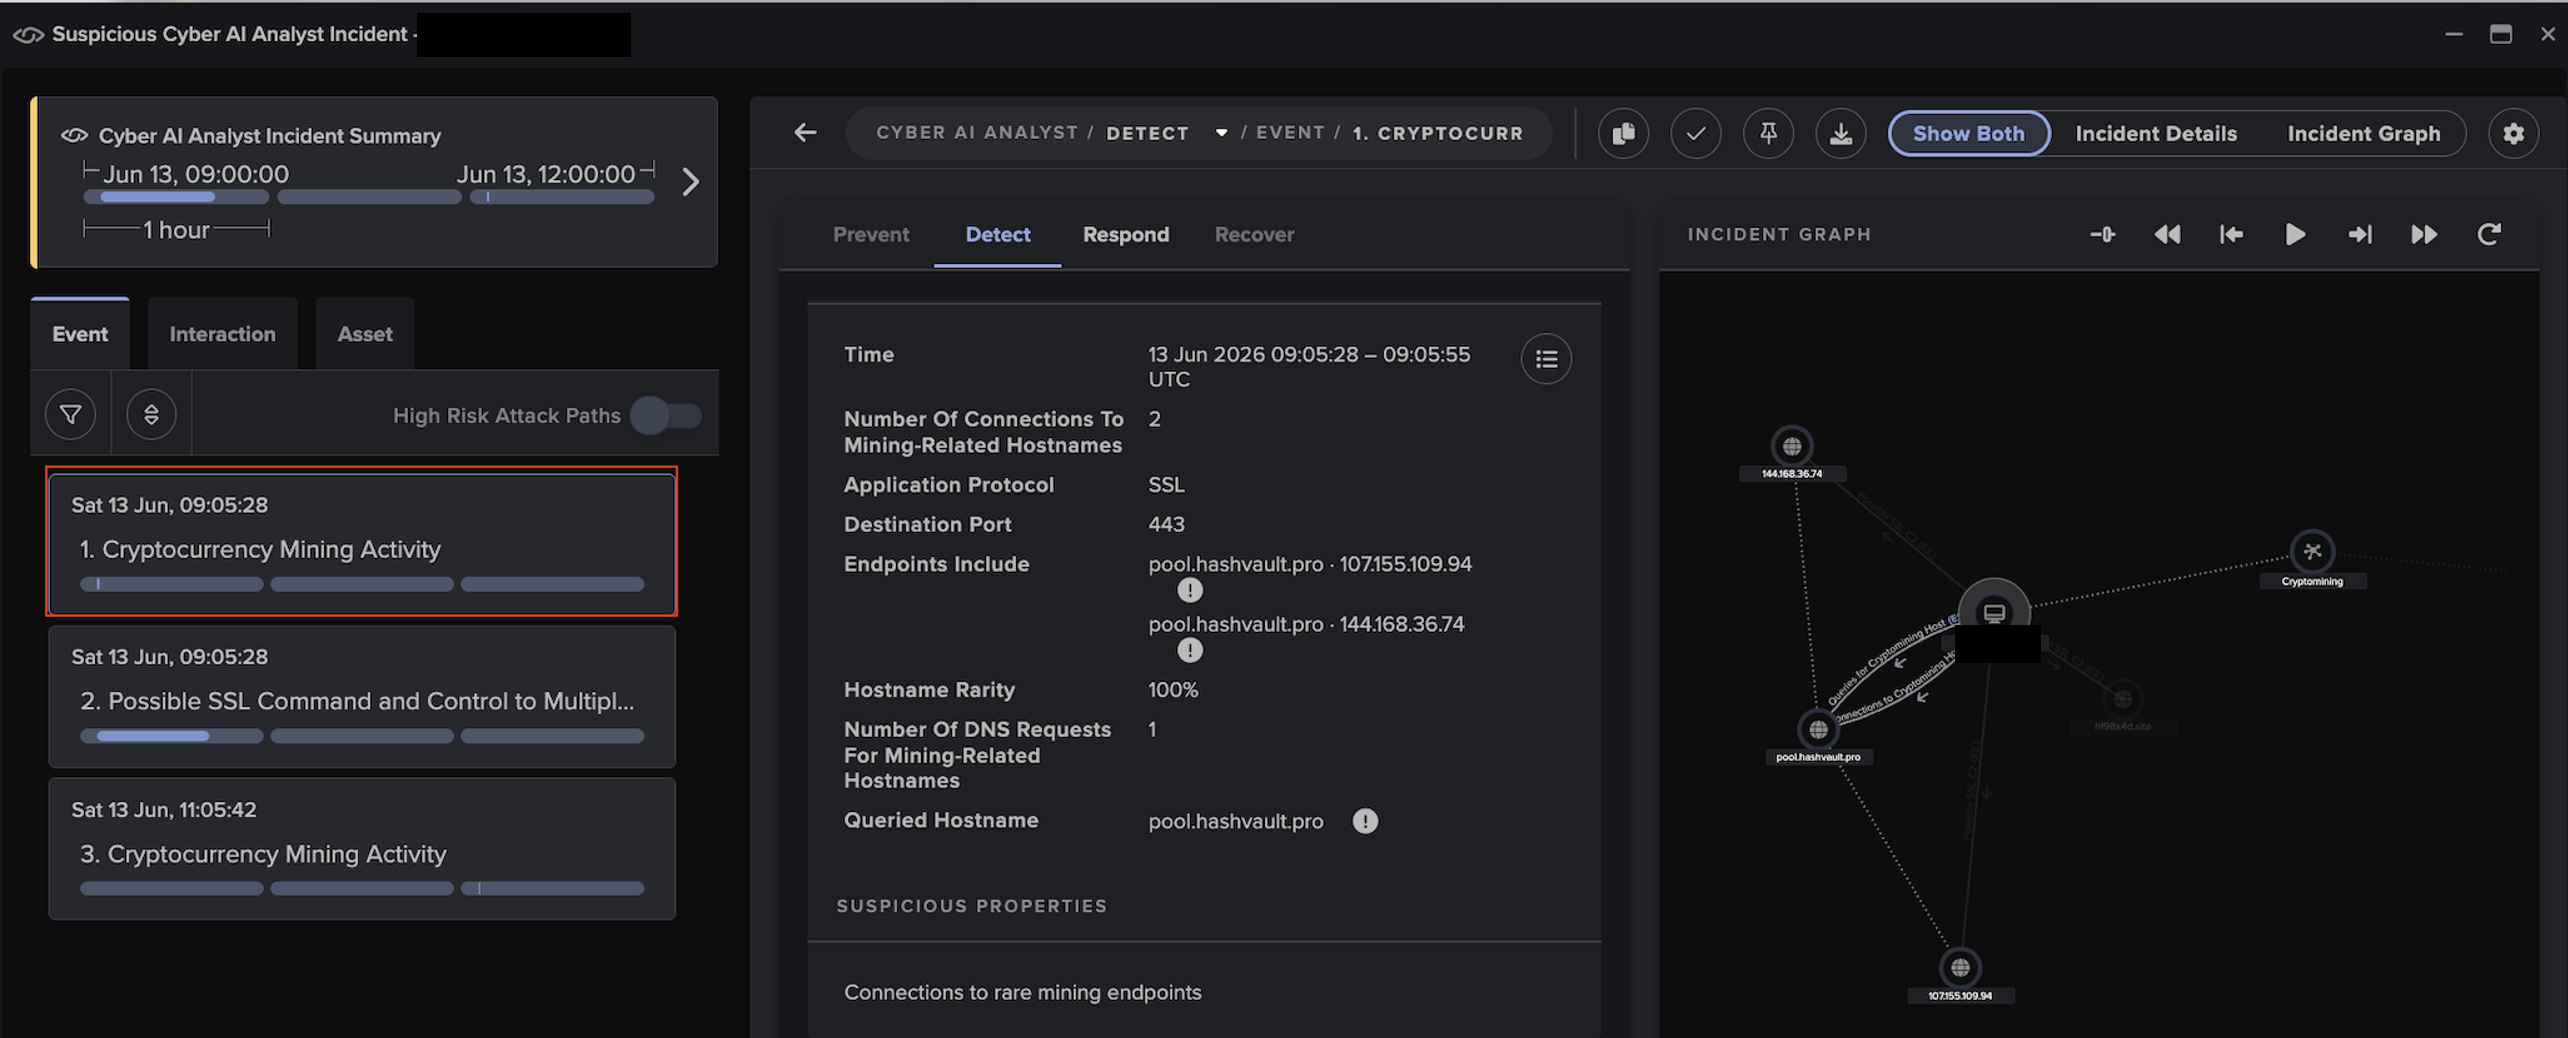
Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

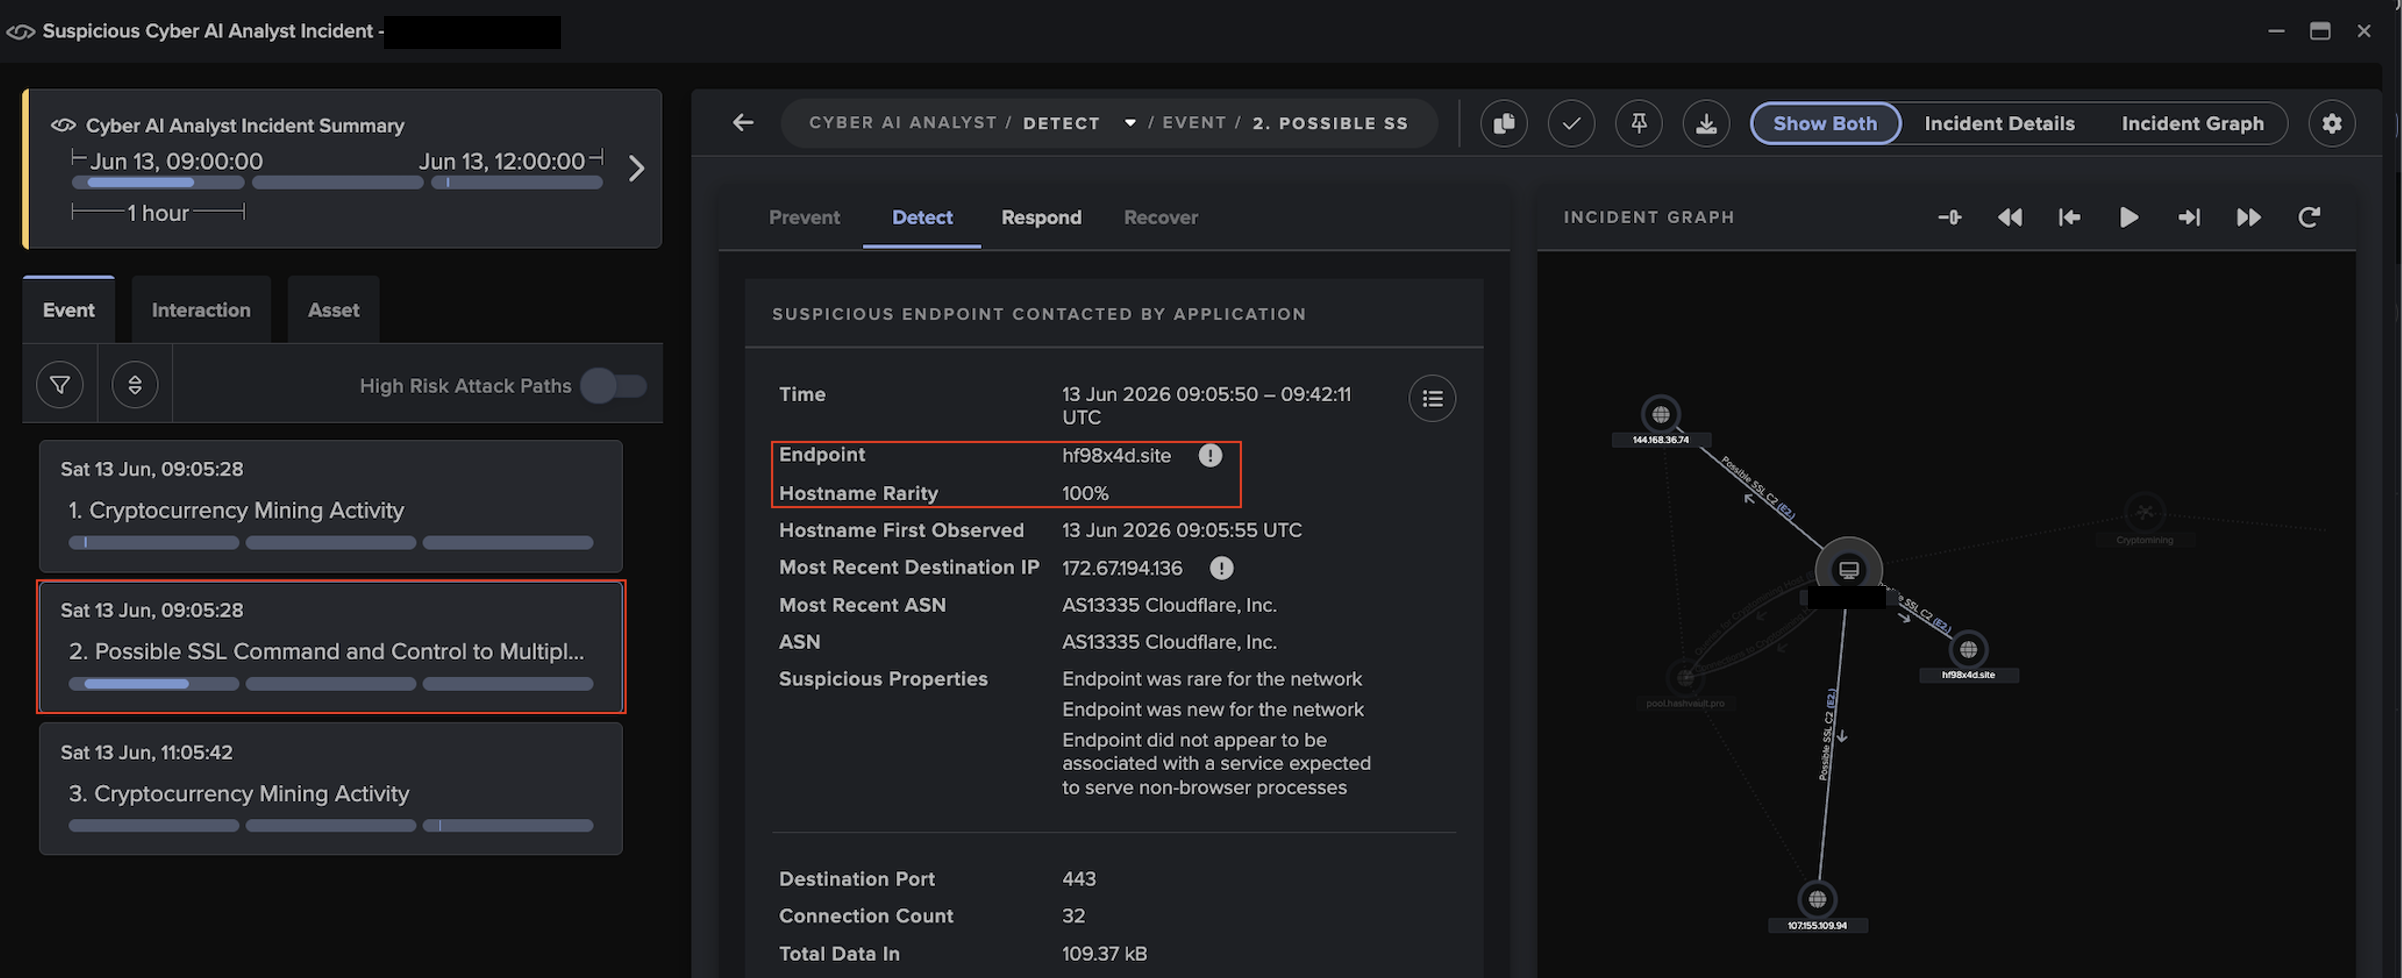
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

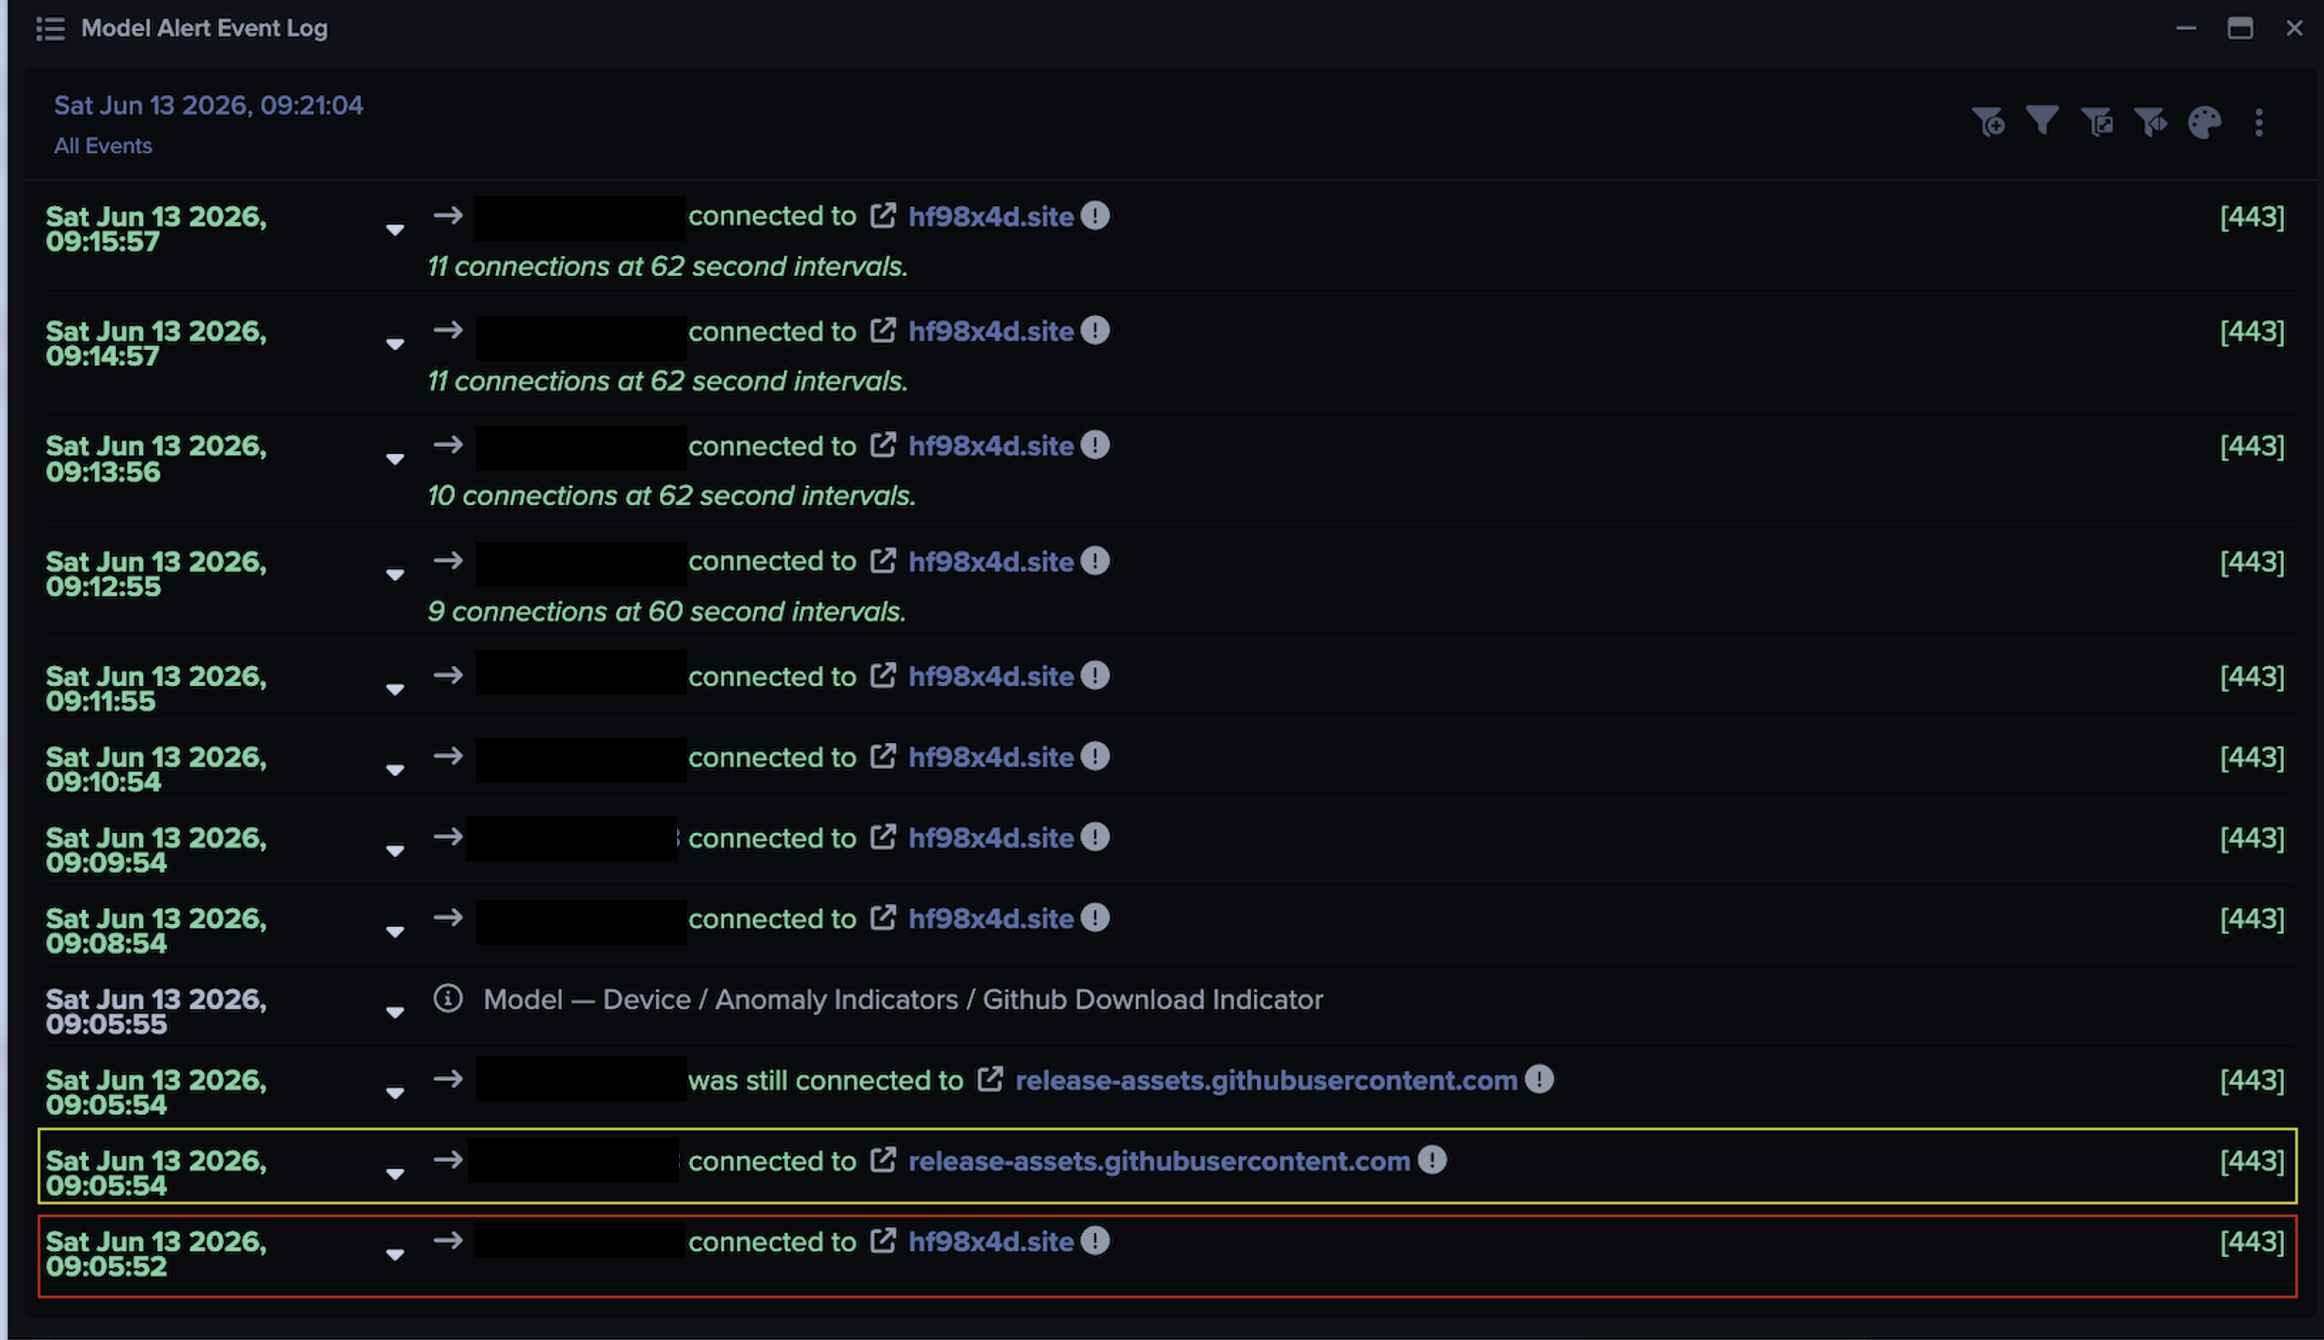
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ