ブログ
/
Network
/
May 5, 2026

When Trust Becomes the Attack Surface: Supply-Chain Attacks in an Era of Automation and Implicit Trust

Software supply-chain attacks dominate the threat landscape in 2026, as adversaries exploit trusted build systems, CI/CD pipelines, and management tools to gain access to target environments. This blog examines Axios, Trivy and Quest Kace compromises observed in the Darktrace customer base, highlighting the need for anomaly detection, assumed breach and continuous visibility.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence
Written by
Emma Foulger
Global Threat Research Operations Lead
Default blog image
05
May 2026

Software supply-chain attacks in 2026

Software supply-chain attacks now represent the primary threat shaping the 2026 security landscape. Rather than relying on exploits at the perimeter, attackers are targeting the connective tissue of modern engineering environments: package managers, CI/CD automation, developer systems, and even the security tools organizations inherently trust.

These incidents are not isolated cases of poisoned code. They reflect a structural shift toward abusing trusted automation and identity at ecosystem scale, where compromise propagates through systems designed for speed, not scrutiny. Ephemeral build runners, regardless of provider, represent high‑trust, low‑visibility execution zones.

The Axios compromise and the cascading Trivy campaign illustrate how quickly this abuse can move once attacker activity enters build and delivery workflows. This blog provides an overview of the latest supply chain and security tool incidents with Darktrace telemetry and defensive actions to improve organizations defensive cyber posture.

1. Why the Axios Compromise Scaled

On 31 March 2026, attackers hijacked the npm account of Axios’s lead maintainer, publishing malicious versions 1.14.1 and 0.30.4 that silently pulled in a malicious dependency, plain‑crypto‑[email protected]. Axios is a popular HTTP client for node.js and  processes 100 million weekly downloads and appears in around 80% of cloud and application environments, making this a high‑leverage breach [1].

The attack chain was simple yet effective:

  • A compromised maintainer account enabled legitimate‑looking malicious releases.
  • The poisoned dependency executed Remote Access Trojans (RATs) across Linux, macOS and Windows systems.
  • The malware beaconed to a remote command-and-control (C2) server every 60 seconds in a loop, awaiting further instructions.
  • The installer self‑cleaned by deleting malicious artifacts.

All of this matters because a single maintainer compromise was enough to project attacker access into thousands of trusted production environments without exploiting a single vulnerability.

A view from Darktrace

Multiple cases linked with the Axios compromise were identified across Darktrace’s customer base in March 2026, across both Darktrace / NETWORK and Darktrace / CLOUD deployments.

In one Darktrace / CLOUD deployment, an Azure Cloud Asset was observed establishing new external HTTP connectivity to the IP 142.11.206[.]73 on port 8000. Darktrace deemed this activity as highly anomalous for the device based on several factors, including the rarity of the endpoint across the network and the unusual combination of protocol and port for this asset. As a result, the triggering the "Anomalous Connection / Application Protocol on Uncommon Port" model was triggered in Darktrace / CLOUD. Detection was driven by environmental context rather than a known indicator at the time. Subsequent reporting later classified the destination as malicious in relation to the Axios supply‑chain compromise, reinforcing the gap that often exists between initial attacker activity and the availability of actionable intelligence. [5]

Additionally, shortly before this C2 connection, the device was observed communicating with various endpoints associated with the NPM package manager, further reinforcing the association with this attack.
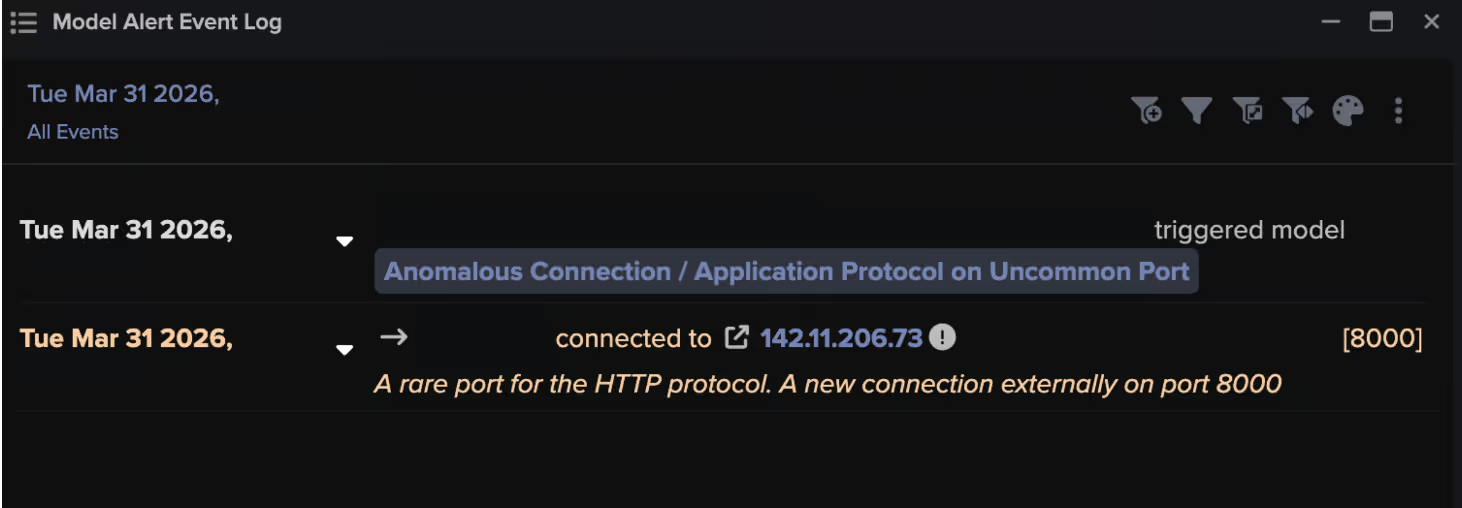
Darktrace’s detection of the unusual external connection to 142.11[.]206[.]73 via port 8000.  
Figure 1: Darktrace’s detection of the unusual external connection to 142.11[.]206[.]73 via port 8000.  

Within Axios cases observed within Darktrace / NETWORK customer environments, activity generally focused on the use of newly observed cURL user agents in outbound connections to the C2 URL sfrclak[.]com/6202033, alongside the download of malicious files.

In other cases, Darktrace / NETWORK customers with Microsoft Defender for Endpoint integration received alerts flagging newly observed system executables and process launches associated with C2 communication.
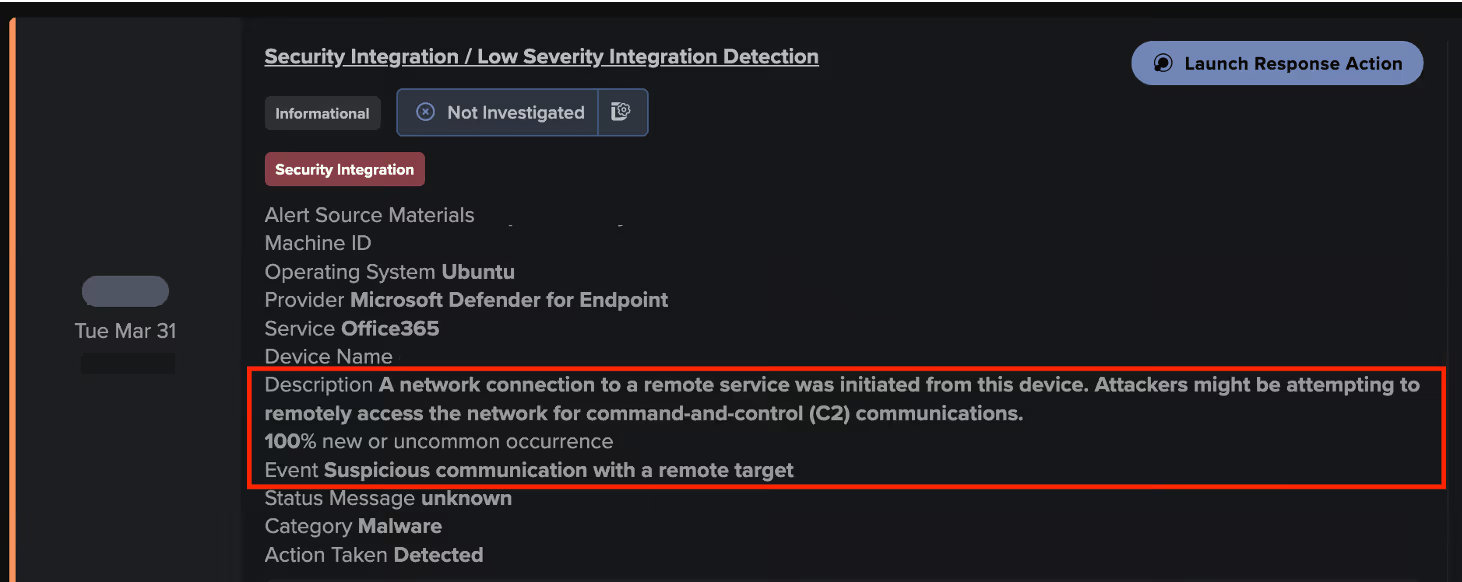
A Security Integration Alert from Microsoft Defender for Endpoint associated with the Axios supply chain attack.
Figure 2: A Security Integration Alert from Microsoft Defender for Endpoint associated with the Axios supply chain attack.

2. Why Trivy bypassed security tooling trust

Between late February and March 22, 2026, the threat group TeamPCP leveraged credentials from a previous incident to insert malicious artifacts across Trivy’s distribution ecosystem, including its CI automation, release binaries, Visual Studio Code extensions, and Docker container images [2].

While public reporting has emphasized GitHub Actions, Darktrace telemetry highlights attacker execution within CI/CD runner environments, including ephemeral build runners. These execution contexts are typically granted broad trust and limited visibility, allowing malicious activity within build automation to blend into expected operational workflows, regardless of provider.

This was a coordinated multi‑phase attack:

  • 75 of 76  of trivy-action tags and all setup‑trivy tags were force‑pushed to deliver a malicious payload.
  • A malicious binary (v0.69.4) was distributed across all major distribution channels.
  • Developer machines were compromised, receiving a persistent backdoor and a self-propagating worm.
  • Secrets were exfiltrated at scale, including SSH keys, Kuberenetes tokens, database passwords, and cloud credentials across Amazon Web Service (AWS), Azure, and Google Cloud Platform (GCP).

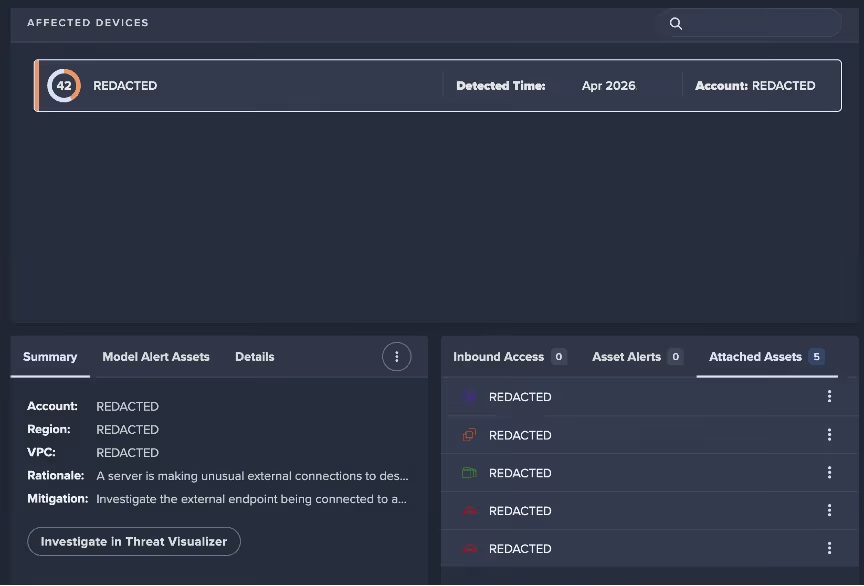
Within Darktrace’s customer base, an AWS EC2 instance monitored by Darktrace / CLOUD  appeared to have been impacted by the Trivy attack. On March 19, the device was seen connecting to the attacker-controlled C2 server scan[.]aquasecurtiy[.]org (45.148.10[.]212), triggering the model 'Anomalous Server Activity / Outgoing from Server’ in Darktrace / CLOUD.

Despite this limited historical context, Darktrace assessed this activity as suspicious due to the rarity of the destination endpoint across the wider deployment. This resulted in the triggering of a model alert and the generation of a Cyber AI Analyst incident to further analyze and correlate the attack activity.

TeamPCP’s continued abused of GitHub Actions against security and IT tooling has also been observed more recently in Darktrace’s customer base. On April 22, an AWS asset was seen connecting to the C2 endpoint audit.checkmarx[.]cx (94.154.172[.]43). The timing of this activity suggests a potential link to a malicious Bitwarden package distributed by the threat actor, which was only available for a short timeframe on April 22. [4][3]
‍

Figure 3: A model alert flagging unusual external connectivity from the AWS asset, as seen in Darktrace / CLOUD .

‍

While the Trivy activity originated within build automation, the underlying failure mode mirrors later intrusions observed via management tooling. In both cases, attackers leveraged platforms designed for scale and trust to execute actions that blended into normal operational noise until downstream effects became visible.

Quest KACE: Legacy Risk, Real Impact

The Quest KACE System Management Appliance (SMA) incident reinforces that software risk is not confined to development pipelines alone. High‑trust infrastructure and management platforms are increasingly leveraged by adversaries when left unpatched or exposed to the internet.

Throughout March 2026, attackers exploited CVE 2025-32975 to authentication on outdated, internet-facing KACE appliances, gaining administrative control and pushing remote payloads into enterprise environments. Organizations still running pre-patch versions effectively handed adversaries a turnkey foothold, reaffirming a simple strategic truth: legacy management systems are now part of the supply-chain threat surface, and treating them as “low-risk utilities” is no longer defensible [3].

Within the Darktrace customer base, a potential case was identified in mid-March involving an internet-facing server that exhibited the use of a new user agent alongside unusual file downloads and unexpected external connectivity. Darktrace identified the device downloading file downloads from "216.126.225[.]156/x", "216.126.225[.]156/ct.py" and "216.126.225[.]156/n", using the user agents, "curl/8.5.0" & "Python-urllib/3.9".

The timeframe and IoCs observed point towards likely exploitation of CVE‑2025‑32975. As with earlier incidents, the activity became visible through deviations in expected system behavior rather than through advance knowledge of exploitation or attacker infrastructure. The delay between observed exploitation and its addition to the Known Exploited Vulnerabilities (KEV) catalogue underscores a recurring failure: retrospective validation cannot keep pace with adversaries operating at automation speed.

The strategic pattern: Ecosystem‑scale adversaries

The Axios and Trivy compromises are not anomalies; they are signals of a structural shift in the threat landscape. In this post-trust era, the compromise of a single maintainer, repository token, or CI/CD tag can produce large-scale blast radiuses with downstream victims numbering in the thousands. Attackers are no longer just exploiting vulnerabilities; they are exploiting infrastructure privileges, developer trust relationships, and automated build systems that the industry has generally under secured.

Supply‑chain compromise should now be treated as an assumed breach scenario, not a specialized threat class, particularly across build, integration, and management infrastructure. Organizations must operate under the assumption that compromise will occur within trusted software and automation layers, not solely at the network edge or user endpoint. Defenders should therefore expect compromise to emerge from trusted automation layers before it is labelled, validated, or widely understood.

The future of supply‑chain defense lies in continuous behavioral visibility, autonomous detection across developer and build environments, and real‑time anomaly identification.

As AI increasingly shapes software development and security operations, defenders must assume adversaries will also operate with AI in the loop. The defensive edge will come not from predicting specific compromises, but from continuously interrogating behavior across environments humans can no longer feasibly monitor at scale.

Credit to Nathaniel Jones (VP, Security & AI Strategy, FCISCO), Emma Foulger (Global Threat Research Operations Lead), Justin Torres (Senior Cyber Analyst), Tara Gould (Malware Research Lead)

Edited by Ryan Traill (Content Manager)

Appendices

References:

1)         https://www.infosecurity-magazine.com/news/hackers-hijack-axios-npm-package/

2)         https://thehackernews.com/2026/03/trivy-hack-spreads-infostealer-via.html

3)         https://thehackernews.com/2026/03/hackers-exploit-cve-2025-32975-cvss-100.html

4)         https://www.endorlabs.com/learn/shai-hulud-the-third-coming----inside-the-bitwarden-cli-2026-4-0-supply-chain-attack

5)         https://socket.dev/blog/axios-npm-package-compromised?trk=public_post_comment-text

IoCs

- 142.11.206[.]73 – IP Address – Axios supply chain C2

- sfrclak[.]com – Hostname – Axios supply chain C2

- hxxp://sfrclak[.]com:8000/6202033 - URI – Axios supply chain payload

- 45.148.10[.]212 – IP Address – Trivy supply chain C2

- scan.aquasecurtiy[.]org – Hostname - Trivy supply chain C2

- 94.154.172[.]43 – IP Address - Checkmarx/Bitwarden supply chain C2

- audit.checkmarx[.]cx – Hostname - Checkmarx/Bitwarder supply chain C2

- 216.126.225[.]156 – IP Address – Quest KACE exploitation C2

- 216.126.225[.]156/32 - URI – Possible Quest KACE exploitation payload

- 216.126.225[.]156/ct.py - URI - Possible Quest KACE exploitation payload

- 216.126.225[.]156/n - URI - Possible Quest KACE exploitation payload

- 216.126.225[.]156/x - URI - Possible Quest KACE exploitation payload

- e1ec76a0e1f48901566d53828c34b5dc – MD5 - Possible Quest KACE exploitation payload

- d3beab2e2252a13d5689e9911c2b2b2fc3a41086 – SHA1 - Possible Quest KACE exploitation payload

- ab6677fcbbb1ff4a22cc3e7355e1c36768ba30bbf5cce36f4ec7ae99f850e6c5 – SHA256 - Possible Quest KACE exploitation payload

- 83b7a106a5e810a1781e62b278909396 – MD5 - Possible Quest KACE exploitation payload

- deb4b5841eea43cb8c5777ee33ee09bf294a670d – SHA1 - Possible Quest KACE exploitation payload

- b1b2f1e36dcaa36bc587fda1ddc3cbb8e04c3df5f1e3f1341c9d2ec0b0b0ffaf – SHA256 - Possible Quest KACE exploitation payload

Darktrace Model Detections

Anomalous Connection / Application Protocol on Uncommon Port

Anomalous Server Activity / Outgoing from Server

Anomalous Connection / New User Agent to IP Without Hostname

Anomalous File / EXE from Rare External Location

Anomalous File / Script from Rare External Location

Anomalous Server Activity / New User Agent from Internet Facing System

Anomalous Server Activity / Rare External from Server

Antigena / Network / External Threat / Antigena Suspicious File Block

Antigena / Network / External Threat / Antigena Suspicious File Pattern of Life Block

Device / New User Agent

Device / Internet Facing Device with High Priority Alert

Anomalous File / New User Agent Followed By Numeric File Download

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence
Written by
Emma Foulger
Global Threat Research Operations Lead

More in this series

No items found.

Blog

/

OT

/

October 21, 2026

Beyond the Fridge: Exposed Industrial Control Systems

Default blog imageDefault blog image

Introduction

In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.

The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.

The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].

Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.

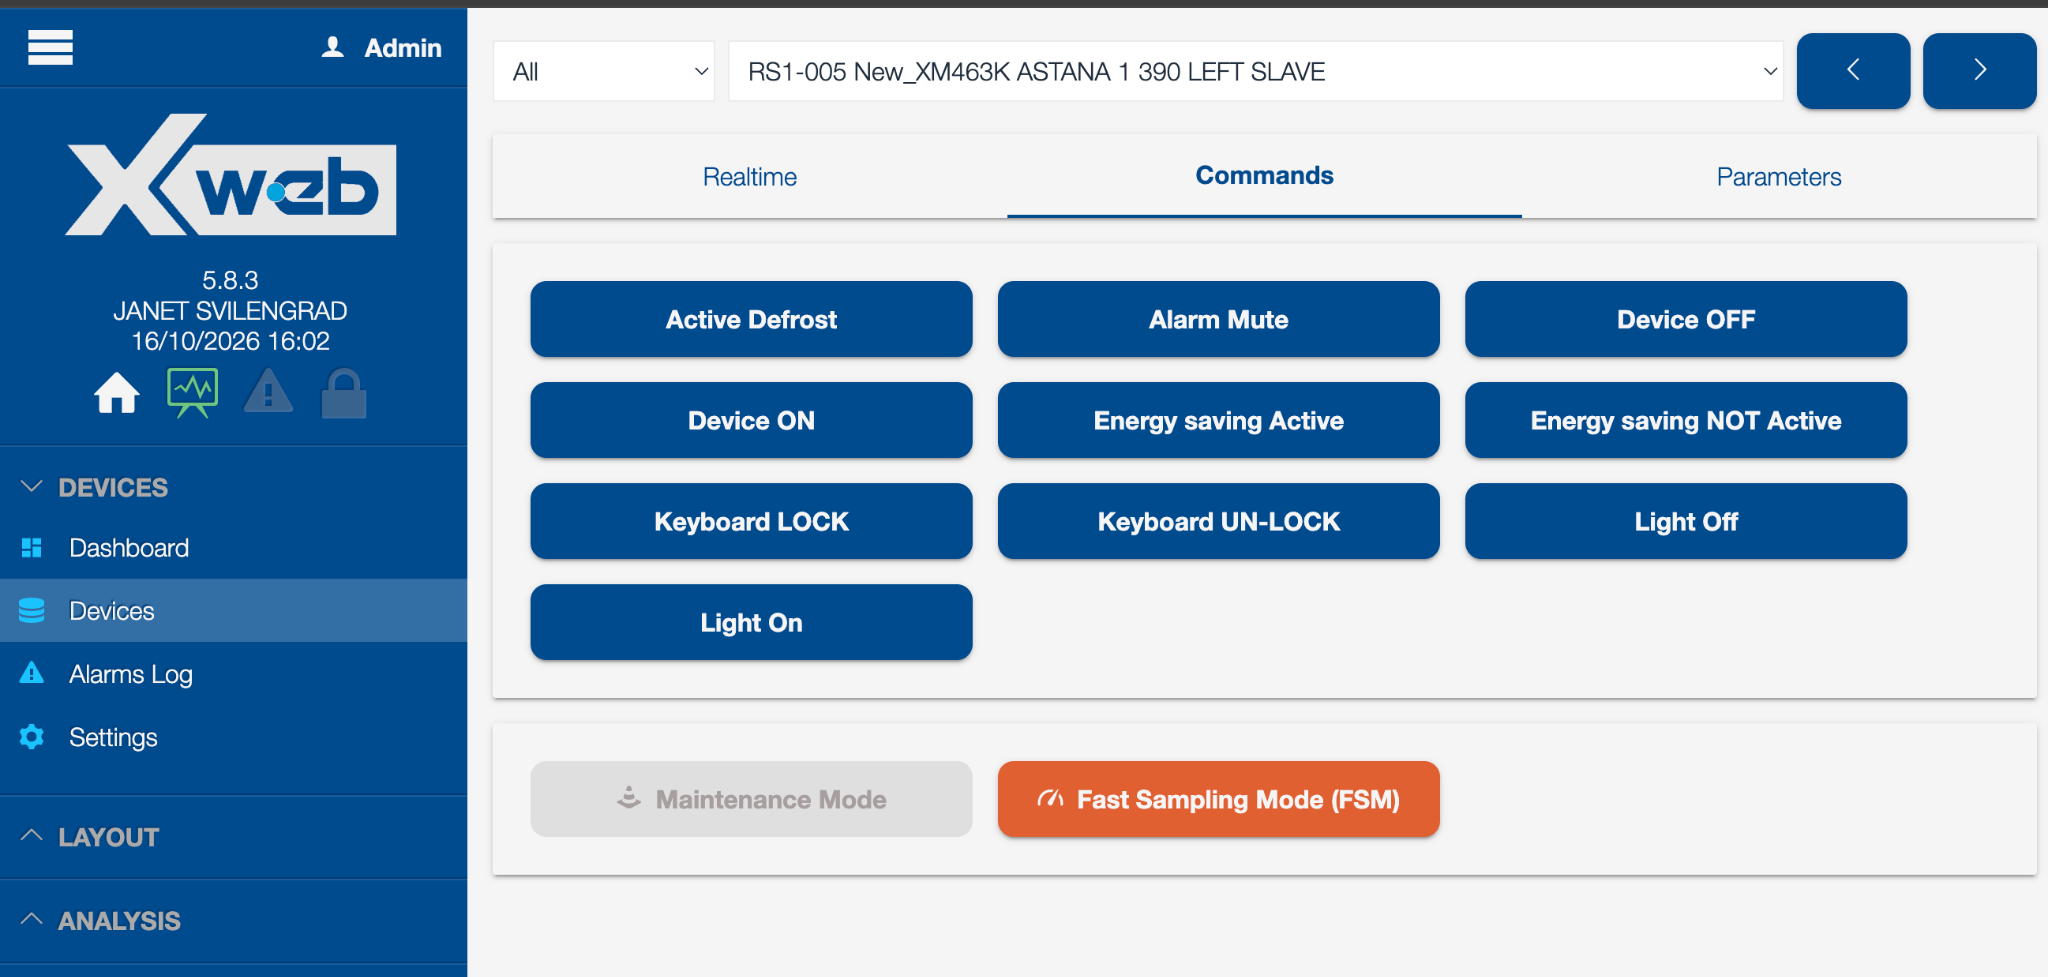
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.

‍

Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.

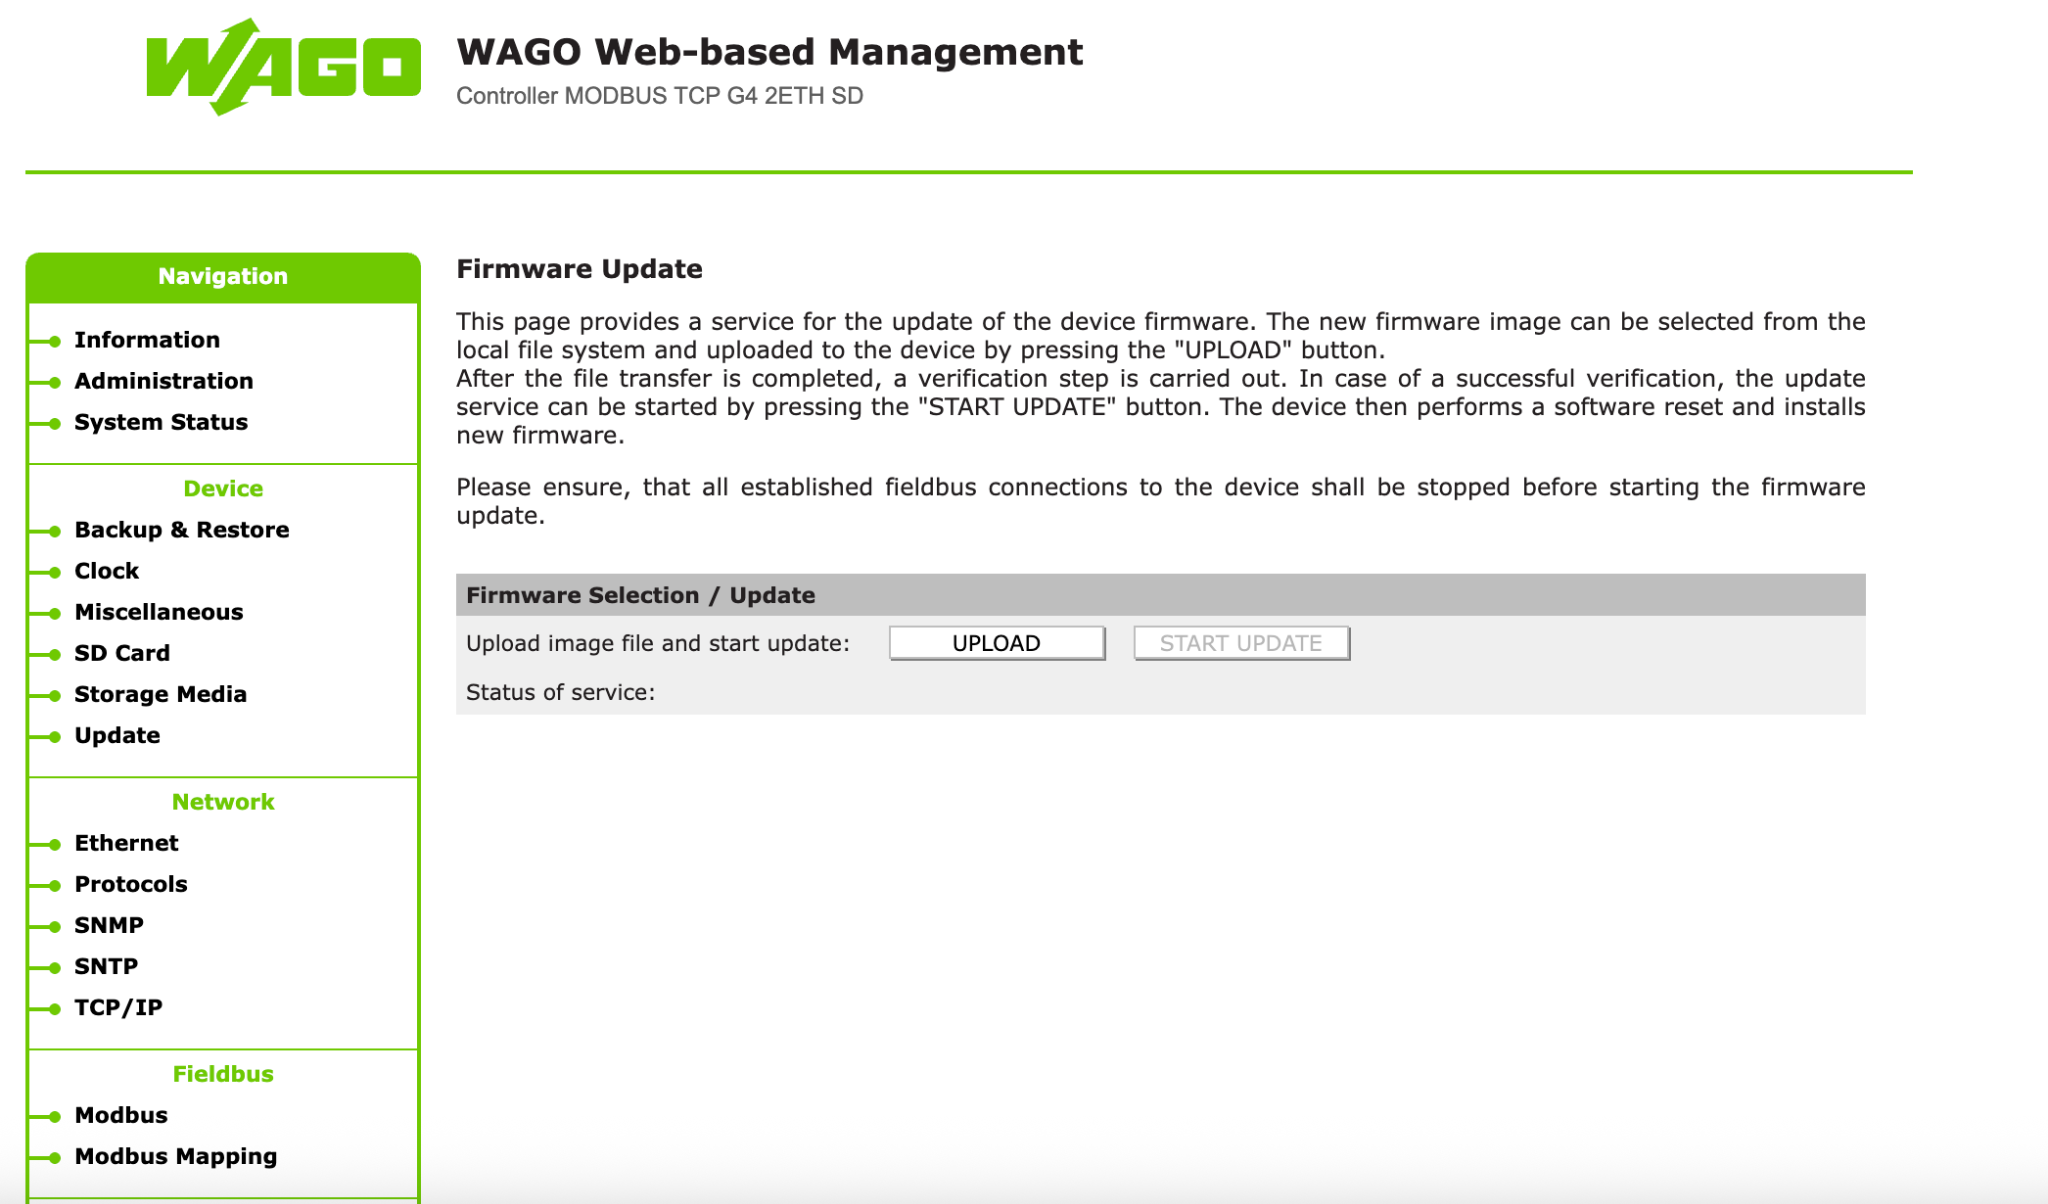
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.

‍

Figure 2: WAGO Management interface.

‍

The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.

‍

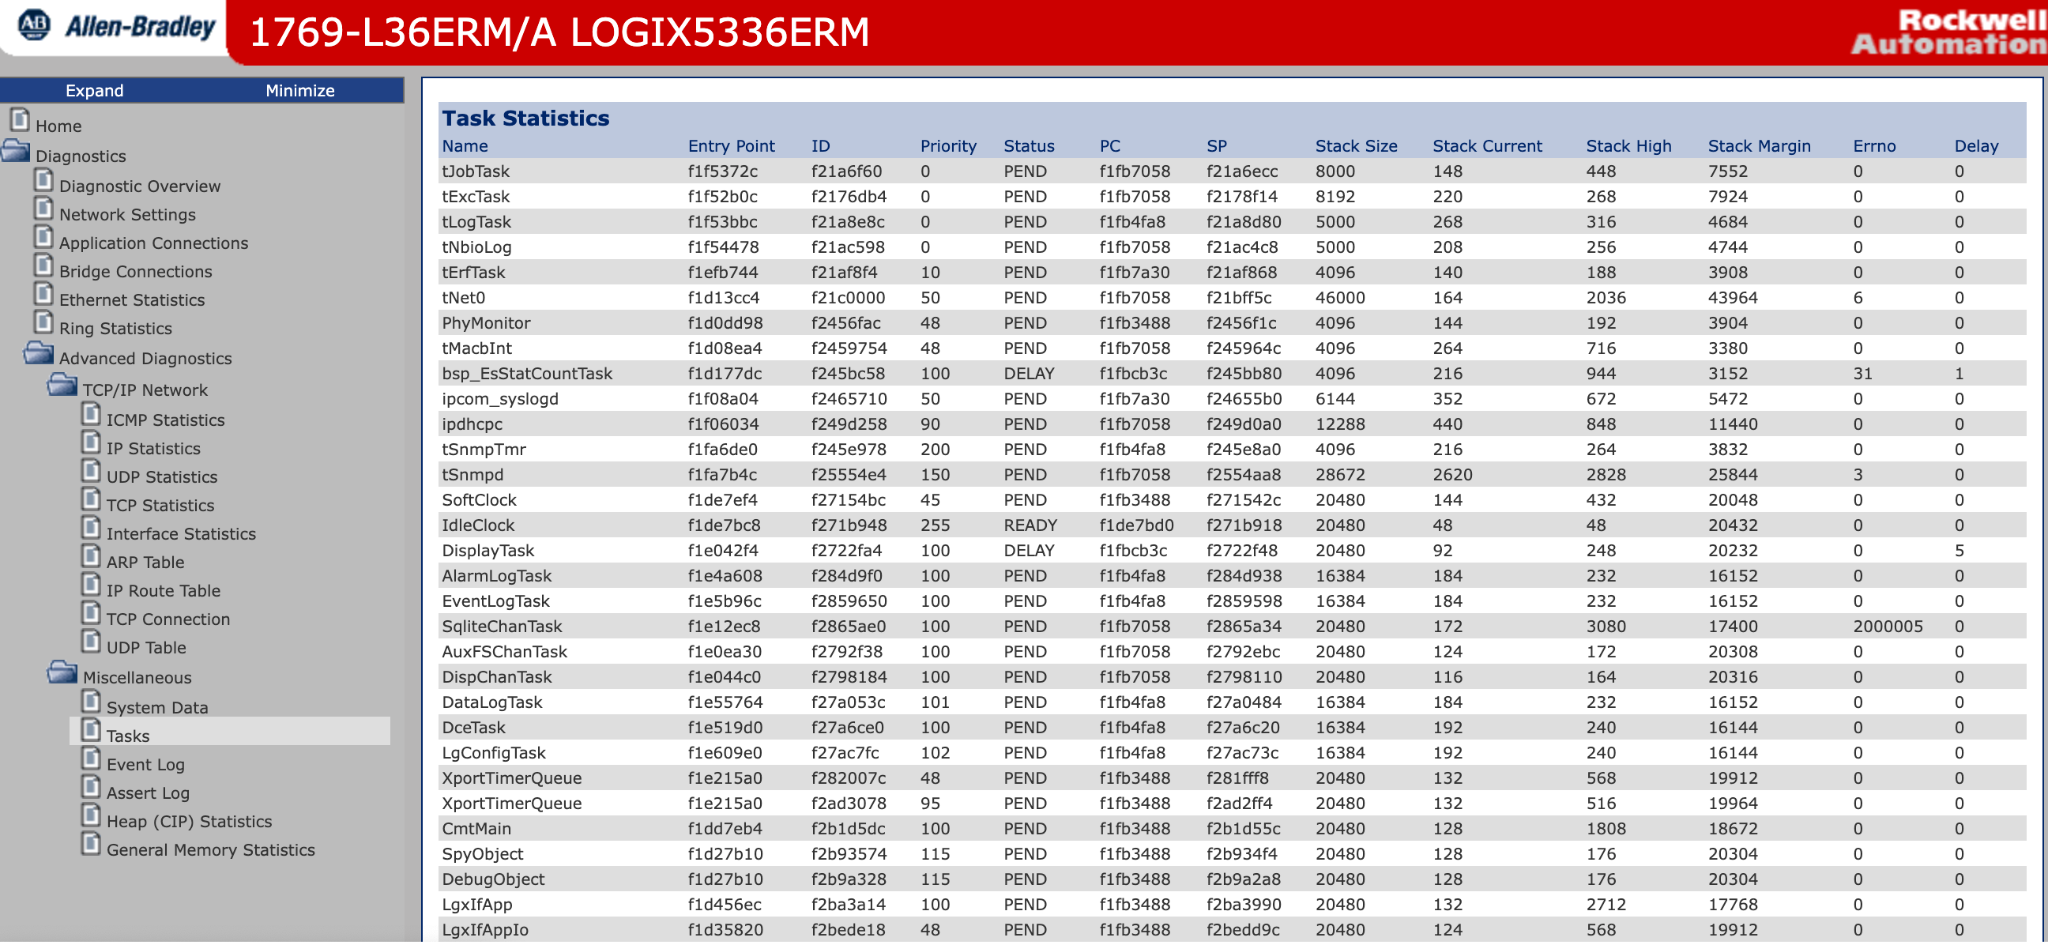
Figure 3: Web interface for Allen-Bradley CompactLogix controller.

‍

Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.

Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.

The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.

The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.

Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.

The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.

Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.

Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.

Darktrace helps security teams gain visibility across IT and OT and respond to risks: https://www.darktrace.com/products/operational-technology.

Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.

References

1.        https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

‍

Continue reading
About the author
Tara Gould
Malware Research Lead

Blog

/

Network

/

October 20, 2026

Why Kubernetes Security Needs A Behavioral Approach

Default blog imageDefault blog image

Kubernetes has become a foundational technology for modern cloud-native infrastructure. It can orchestrate everything from customer-facing applications to data pipelines and, increasingly, AI workloads. This is due to the highly scalable nature of Kubernetes, making it cost efficient and reliable.

Gartner projects that by 2028, 95% of new AI deployments will run on Kubernetes, up from less than 30% today1. However, the same qualities that make Kubernetes powerful also make it uniquely challenging to secure, leaving many organizations with limited visibility into their clusters. This lack of visibility increases risk - it’s difficult to secure what you can’t see.

However, this risk is often looked at as purely a posture management challenge. While Cloud Security Posture Management (CSPM) solutions can tell you how a cluster should be configured, they don’t tell you what it is doing in real time. This requires runtime behavioral monitoring of clusters to detect active threats.

Yet existing approaches to securing Kubernetes by most Cloud Detection and Response (CDR) and Network Detection and Response (NDR) vendors often have limited coverage or require a third-party integration to forward traffic and metadata. This means that capabilities can be limited and detections can lack the context of the wider environment, which slows down triage, investigation and response.

Why Kubernetes is hard to secure

Traditional security tooling was built for persistent, long-term infrastructure such as servers and virtual machines with fixed identities that last months or years. Some elements of Kubernetes environments can have a much shorter lifespan, breaking many assumptions those tools rely on:

  1. Increased complexity
    1. Kubernetes environments can be complex in comparison to traditional infrastructure, with many different elements to consider such as nodes, clusters, containers, pods and the workloads themselves.
  2. Ephemeral by design
    1. Kubernetes pods can spin up and terminate in seconds. A container that was compromised may no longer exist by the time a deeper investigation is required, leaving no artifact to analyze. This poses a unique challenge for security operations.
  3. Weaker workload boundaries
    1. Kubernetes containers use lightweight, shared-kernel isolation rather than separate virtual machines, improving efficiency but reducing separation between workloads and the host. As a result, a compromised container may have a greater potential impact on the node and neighboring workloads than a compromised virtual machine (VM).2
    2. Recent vulnerabilities have shown that threat actors can escape a container and gain access to the underlying host.3, 4
  4. Everything is API-driven
    1. Dozens or hundreds of microservices communicate over internal APIs, and the Kubernetes control plane itself is an API. This creates a large and dynamic attack surface, making it difficult to distinguish legitimate activity from malicious behavior.
    2. Without identity-aware runtime visibility, threat actors can move laterally between pods and exploit misconfigured role-based access controls (RBAC) with little chance of detection.

Rising to the challenge of securing Kubernetes

With the release of Darktrace 7.2, Darktrace / HYBRID NETWORK can extend behavioral security into Kubernetes, delivering visibility, detection and response capabilities across runtime activity. Darktrace addresses the challenges of securing Kubernetes environments in several ways.

Behavioral detection, not static rules

Many Kubernetes runtime tools rely on predefined rules and signatures - a fixed list of “bad” behaviors to match against. That approach struggles with novel attacks and generates noise at scale. Darktrace takes a different approach: our Adaptive AI builds a Unique Behavioral Profile for each organization from the ground up, learning the normal behavior of every workload, node and identity in your cluster. It then uses this understanding to detect meaningful deviations from expected behavior, which serves as the basis for surfacing suspicious and malicious activity.  

A pod reaching out to an unfamiliar destination, an unexpected executable launching inside a workload, or an identity performing an action it has never performed, all surface as anomalies without anyone having to write a rule in advance.

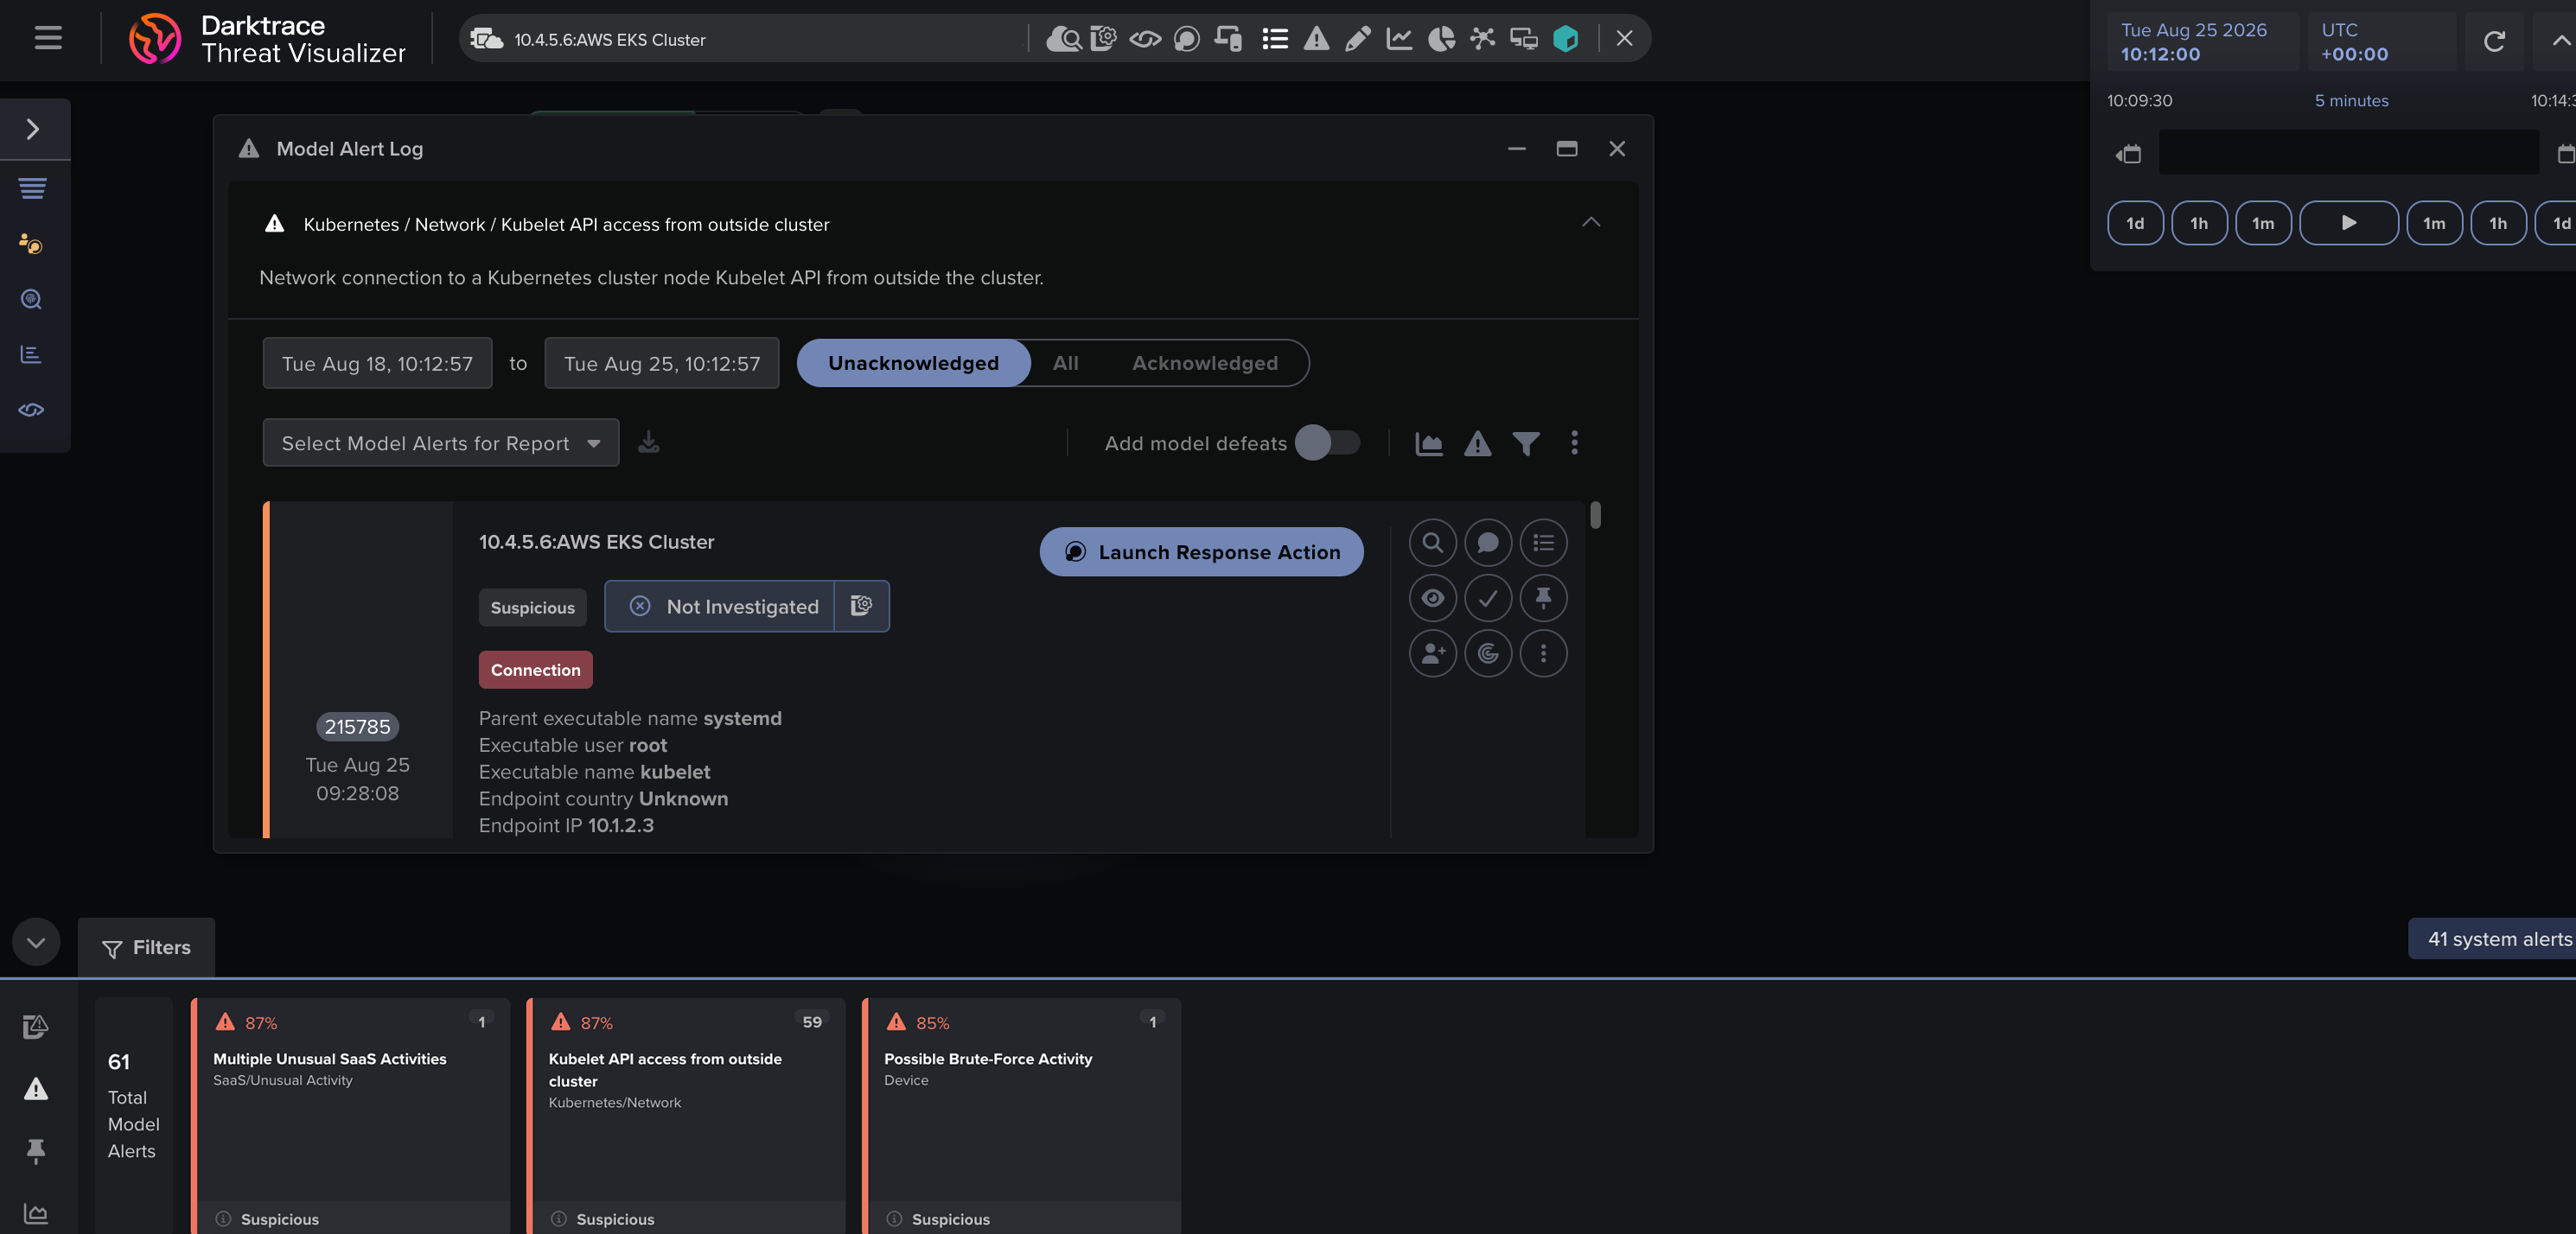
Darktrace surfaces unexpected Kubernetes activity that does not align with an organization’s Unique Behavioral Profile

‍

Visibility across the network, the process, and the control plane

Darktrace monitors Kubernetes at three levels that together provide comprehensive runtime visibility:

  1. Network-layer
    1. Traffic between pods, across nodes and out to the internet. This helps to detect lateral movement and unusual connectivity, whether internal or external.
  2. Process-layer
    1. What is executing inside your containers. If a process reads a sensitive credential file or spawns an unexpected shell inside a production pod, Darktrace can identify that activity and use it as context for further detections.
  3. Control plane
    1. Activity against the Kubernetes API itself: someone executes a command in a running pod, RBAC changes, or unusual administrative actions. Many high-impact security events involve the control plane, an area that is often less visible to solutions that only analyze or scan network-layer telemetry.

Misconfiguration and vulnerability awareness

Runtime detection is strongest when combined with posture and exposure management. Darktrace surfaces risky pod configurations, such as privileged containers, host networking, and over-permissive service accounts as workloads are deployed, and links CVEs from images to the workloads running them. Security teams can go beyond simply knowing that a vulnerability exists and see exactly where it is in the cluster. When combined with behavior-based detections, this provides invaluable context that can help prioritize incidents and proactively identify areas that need further attention. For example, anomalous workload behavior on its own might not be very interesting to a security team at first, but if that same workload is known to host sensitive data, is known to have critical vulnerabilities associated with it, or is publicly accessible, then this narrative becomes much more suspicious and demanding of their attention.

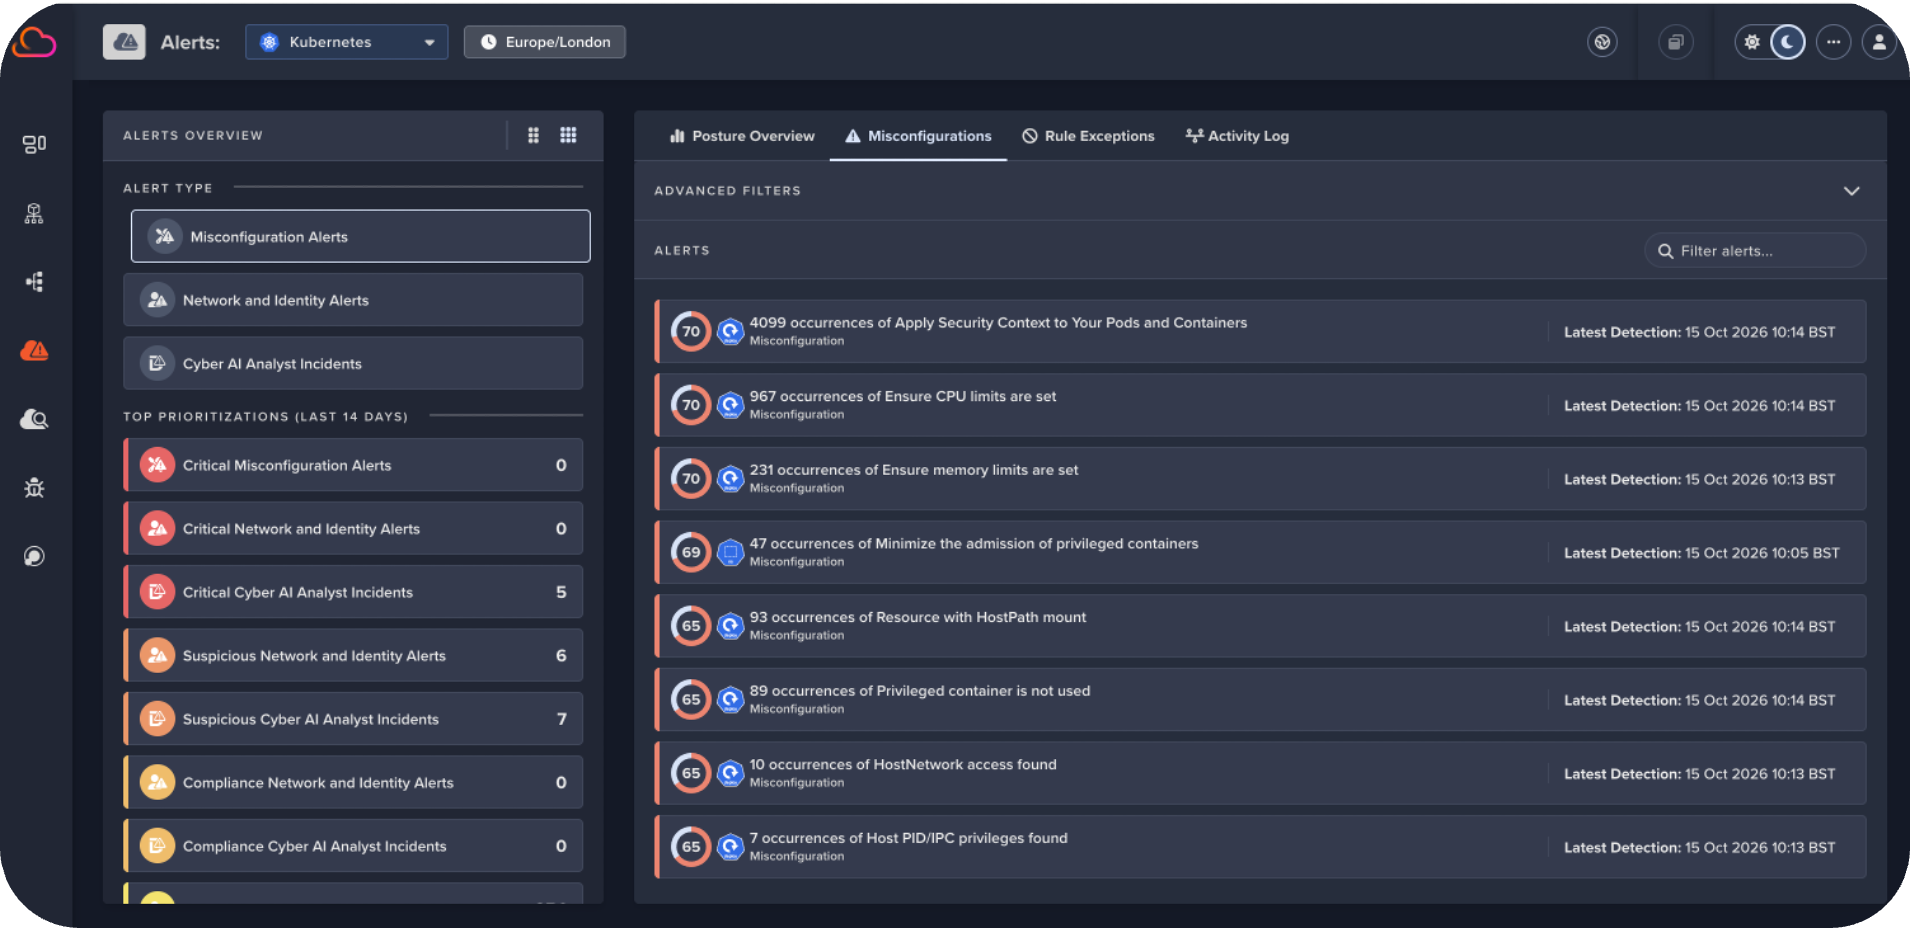
Darktrace highlights Kubernetes misconfigurations such as privileged containers, host networking, and missing security controls, helping teams prioritize runtime alerts with valuable exposure and risk context

‍

Response, tailored to Kubernetes

Detection is most effective when paired with response. Darktrace can take precise actions on Kubernetes workloads, including blocking a malicious connection at the pod level, helping to safely contain threats while security teams investigate. Response actions can be taken fully autonomously or via a human-in-the-loop process, which is completely configurable depending on the desired level of autonomy and scope. Darktrace is expanding the number of Kubernetes-native response actions to give customers even more flexibility when containing threats.

Forensics that survive the workload

Because containers are so short-lived, evidence disappears fast and this can make it very difficult to answer questions related to the initial detections. Darktrace solves this with Forensic Acquisition & Investigation capabilities that extend to Kubernetes containers, allowing investigations to be triggered manually by an analyst, or automatically from an alert, preserving evidence before the workload is gone.

For incident responders, this addresses a key challenge in container security: being able to answer “what actually happened?” after an ephemeral workload has vanished.

One platform, not another silo

Kubernetes doesn't exist in isolation, and neither should its security. Darktrace correlates cluster activity with the surrounding cloud environment, including AWS, Azure and GCP identities, network activity and cloud assets, allowing analysts to pivot between a Kubernetes workload and its wider context. A single anomalous action can be traced from the control plane to the pod, and from the pod to the cloud identity behind it, all within a single investigation workflow. This can also include alerts from other areas of hybrid infrastructure or third-party sources where relevant, adding more context to investigations and speeding up workflows for human analysts.

Built to deploy easily

Operational complexity can be a barrier to security adoption. Darktrace / HYBRID NETWORK for Kubernetes installs with a single command, and for teams that manage their infrastructure as code, it supports raw manifests so the deployment can live in a Git repository and be managed through existing GitOps workflows. The same deployment approach works across Kubernetes environments in AWS, Azure, Google Cloud, and on-premises infrastructure. Early adopters of Darktrace’s Kubernetes capabilities have highlighted the simplicity of deployment and time to value.

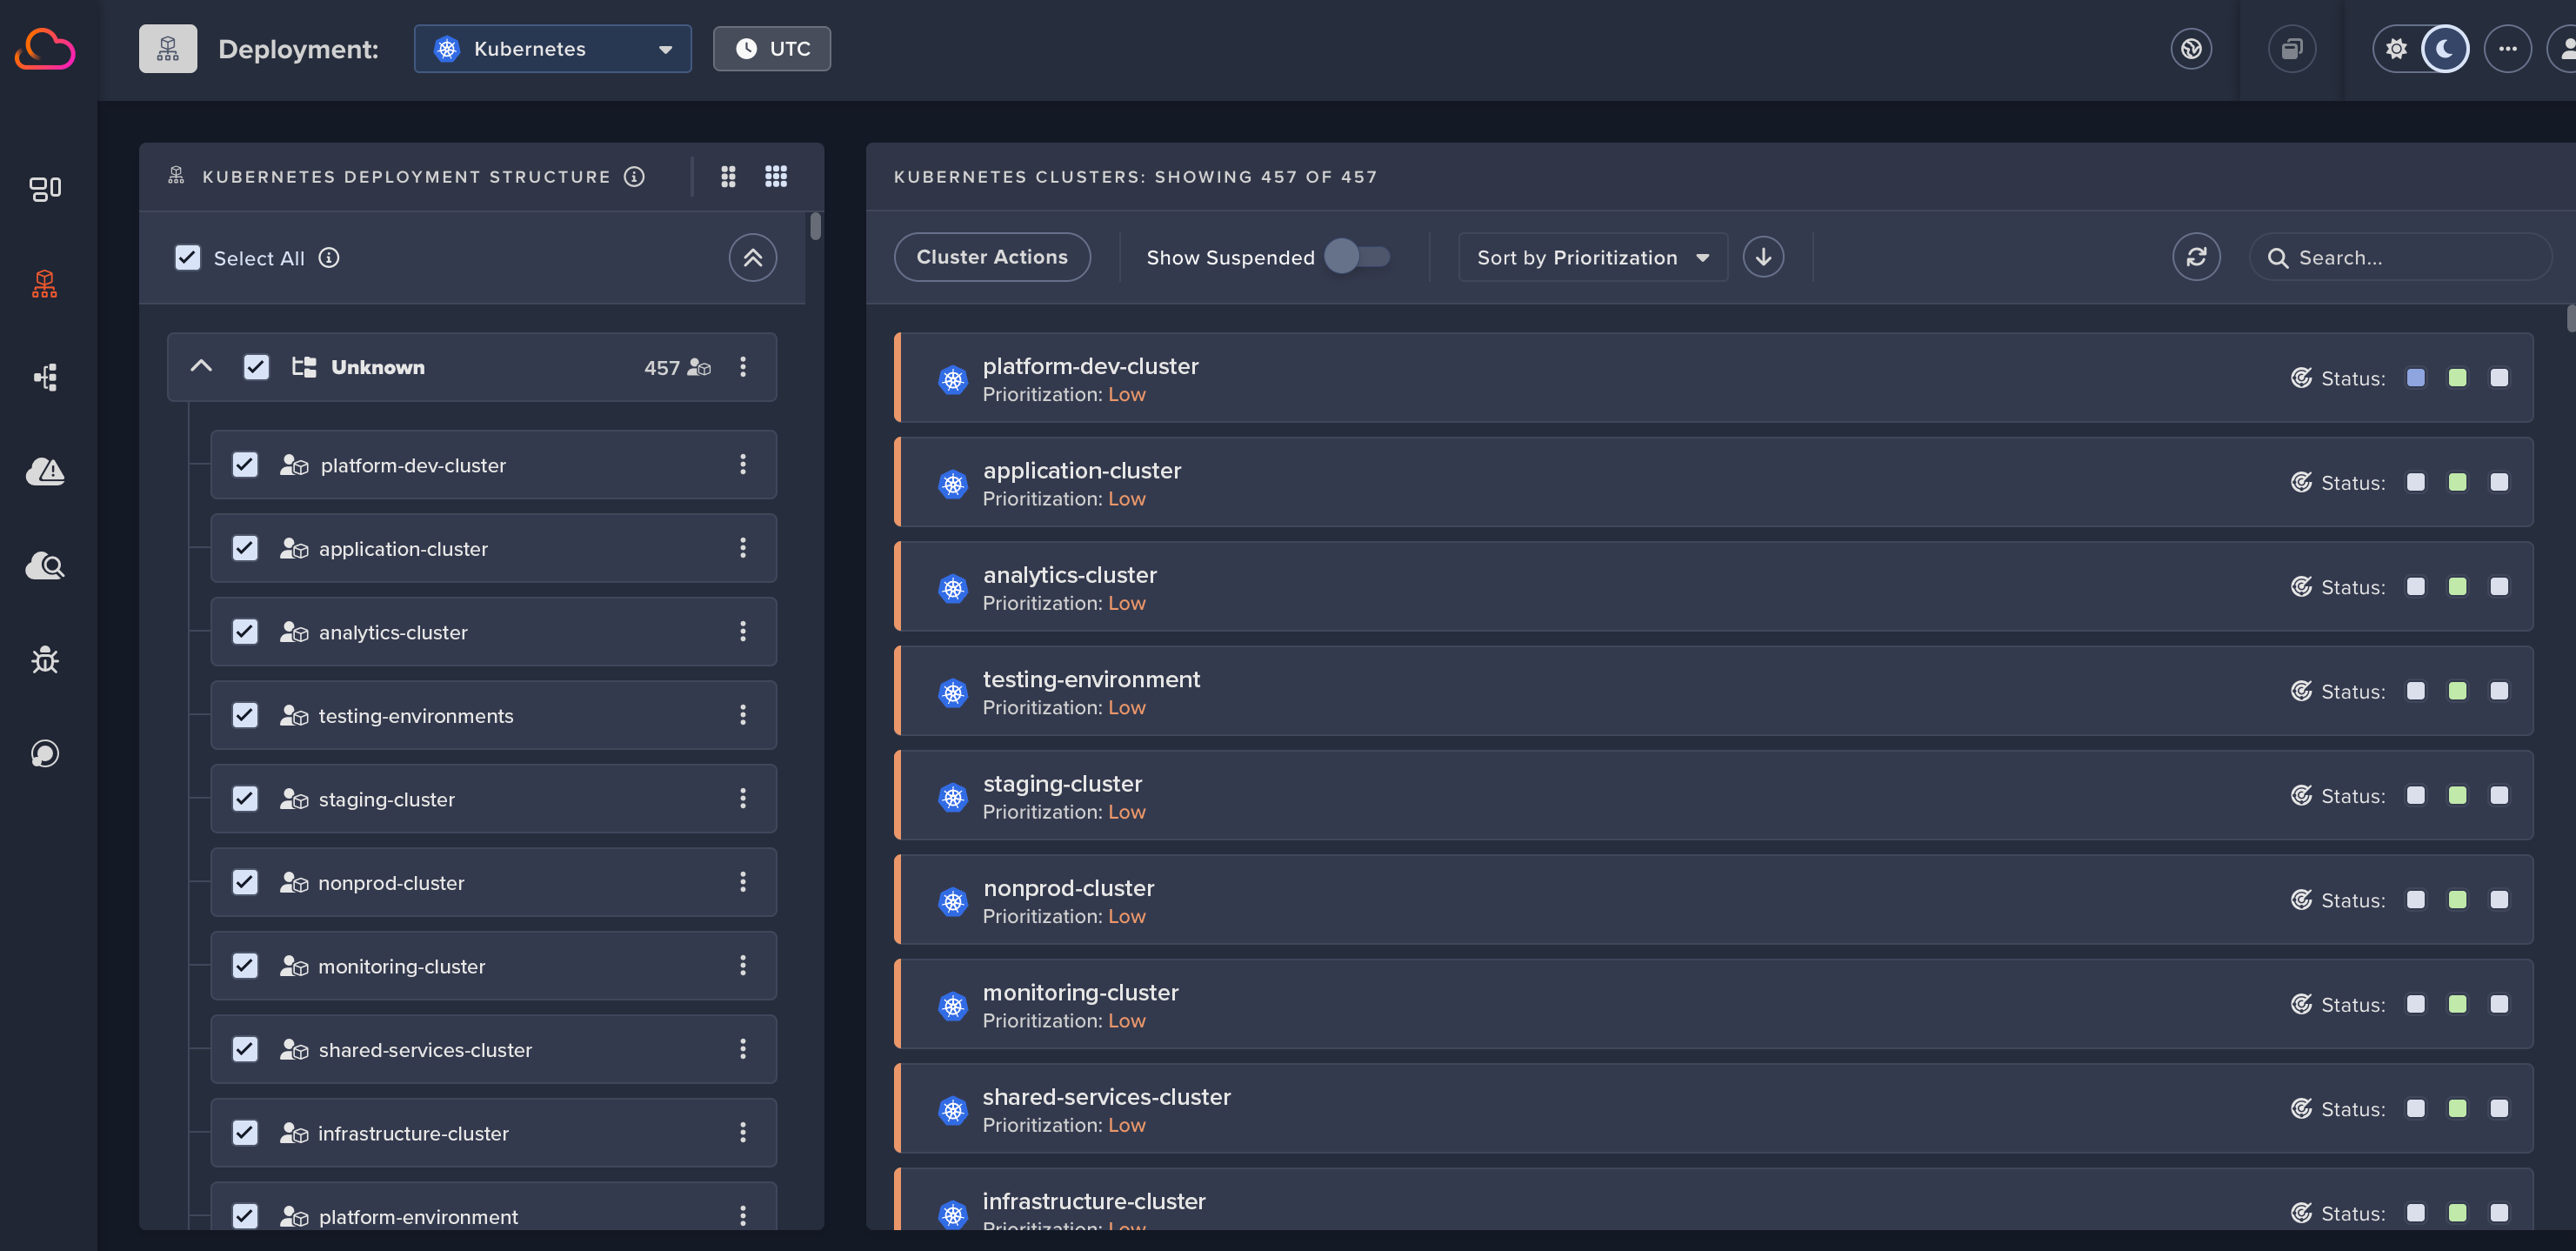
Darktrace can deploy across your Kubernetes environment and wider hybrid infrastructure, while also providing visibility into Kubernetes deployment structure and status

Next steps

Kubernetes environments are dynamic, ephemeral and API-driven in ways that challenge traditional security tooling. With Kubernetes usage increasing due to widespread AI adoption, it is essential to secure Kubernetes environments as part of securing what AI can do. Darktrace / HYBRID NETWORK addresses these challenges by learning normal behavior in Kubernetes environments across network, process and control-plane layers, identifying meaningful threats and enabling targeted response. Combined with the context of wider hybrid infrastructure and forensic investigation capabilities, Darktrace provides visibility into both emerging threats and active incidents.

To see how Darktrace can help secure your Kubernetes environment and your wider hybrid infrastructure, get in touch to arrange your free trial. Existing customers can contact their Darktrace Account Team for more information about deployment options and licensing.

‍

Sources

[1] Gartner, Container Management research, 2025: "By 2028, 95% of new AI deployments will use Kubernetes, up from less than 30% today."  https://www.gartner.com/en/documents/7913109. (quote reproduced under Gartner reprint at https://www.kubermatic.com/magic-quadrant-and-critical-capabilities-for-container-management/)

[2] Palo Alto Networks (Unit 42) – Container Breakouts: Escape Techniques in Cloud Environments. https://unit42.paloaltonetworks.com/container-escape-techniques/

[3] runC container-escape vulnerabilities (CVE-2025-31133, CVE-2025-52565, CVE-2025-52881), disclosed by a SUSE researcher on November 5, 2025. https://www.securityweek.com/runc-vulnerabilities-can-be-exploited-to-escape-containers/

[4] NVIDIAScape (CVE-2025-23266), CVSS 9.0. https://nvidia.custhelp.com/app/answers/detail/a_id/5659

[related-resource]

‍

Continue reading
About the author
Elise Longhurst
Senior Product Executive
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ