ブログ
/
AI
/
August 6, 2026

信頼が新たなアタックサーフェスである理由:ダークトレースの2026年度中間脅威アップデート

ダークトレースが実施した2026年度前半の脅威分析では、攻撃者はセキュリティコントロールを回避するのではなく、信頼を利用する傾向がますます強まっていることが明らかになりました。アイデンティティ侵害、サプライチェーン攻撃、SaaSの悪用、AIを利用した作戦、および国家と連携したさまざまな活動は、信頼されるユーザー、サービス、およびインフラが重要な攻撃経路となっていることを示しています。これは防御者にとって、コンテキストとビヘイビア分析がセキュリティを維持するための根本的な基盤であることを意味しています。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence
Written by
Emma Foulger
Global Threat Research Operations Lead
Default blog image
06
Aug 2026

2026年初頭、ダークトレースのアナリストによって専用に設計されたReact2Shellハニーポットは、その展開から2時間未満で侵害を受けました。この1つのデータをとって見ても2026年前半の脅威ランドスケープのペースを表していると言うことができますが、スピードは1つの側面に過ぎません。

過去6か月間の変化は、従来のマルウェアや脆弱性を中心とした攻撃から、信頼されるアイデンティティ、プラットフォーム、およびインフラの悪用への移行を示しています。多くの組織が広範囲にAIを導入するのに伴い、アイデンティティ、SaaSプラットフォーム、クラウドに対する権限、自動化フレームワーク、および非人間アイデンティティが、攻撃者に好まれる攻撃経路となっています。

攻撃者は、外部から侵入するよりも、防御者やユーザーが信頼するよう条件づけられている関係、サービス、認証済みチャネル内で活動する傾向が高まっています。

2025年と比較して何が変わったか?

2025年には、アイデンティティが新たな境界となり、攻撃者はますます従来のエクスプロイト手法を使うよりも信頼されるアカウント、SaaSプラットフォーム、そしてAIによって可能になった新手の手法を使うようになりました。2026年前半は、この進化の次の段階にあると言えます。アイデンティの悪用は依然として中心的ですが、信頼の問題は今やアカウントをはるかに超えてEメール認証、クラウドに対する権限、ソフトウェアサプライチェーン、AIゲートウェイ、リモート管理ツール、そして非人間アイデンティティにも及んでいます。

Theme 2025 (Mid-Year / Annual) H1 2026
Identity Credentials remained the weak link; identity emerged as the new perimeter. Identity remains the entry point, but trust has become the new attack surface.
Cloud & SaaS SaaS-targeted ransomware continued to rise. Cloud and SaaS became the attacker's preferred operating environment.
AI Large Language Models (LLMs) were suspected of influencing phishing shifts. LLM-generated malware, compromised AI proxies, and the abuse of AI identities emerged.
Attack Surface Scale & Speed Exponential growth of Common Vulnerabilities and Exposures (CVEs), with public proof-of-concepts appearing faster. Cloud and AI adoption expanded the attack surface, while AI accelerated exploitation. One honeypot was compromised in under two hours.
Supply Chain Legitimate services were increasingly abused. Trusted maintainers and CI/CD workflows were weaponized.

アイデンティティとEメール:危険にさらされる信頼のシグナル

Eメールは信頼されるアイデンティティへの最も確実なルートであり、攻撃者はノイズを作り出すことよりも品質の向上に投資していることをデータが示しています。2026年前半において、フィッシングEメールの67%がDMARC認証を通過していました。ほとんどのフィッシングの試みに対して、阻止するには認証だけではもはや不十分なのです。フィッシングEメールの25.8%でVIPユーザーが標的となっており、22025年と同様に25%を上回る値ですが、期間全体を通じて上昇傾向にあります。重要な点は、フィッシングの巧妙さが高まり続けていることです:フィッシングEメールの37%が大量のテキストを含んでおり、2025年前半の32%から増加しています。また、39%は新手のソーシャルエンジニアリングテクニックを特徴としており、攻撃者が特定の標的にあわせてさらなるカスタマイズを行っていることを示唆しています。

ダークトレースの顧客に最も幅広く影響を与えている脅威もアイデンティティに焦点を当てたものであり、専用のStealCおよびAMOSインフォスティーラーを使った攻撃がこの半年間に多く見られています。これらのマルウェアの蔓延も、根本的にはアイデンティティの問題です。インフォスティーラーによって収集された認証情報がしばしば最初のアクセスベクトルとして使用され、攻撃チェーンの後の段階で格段に影響の大きい侵害につながります。また、マルウェアの投下には技術的弱点の悪用をほとんど必要としない点が重要です。ユーザー自身の手で悪意あるコードを実行させるClickFixソーシャルエンジニアリング手法は、依然としてよく見られます。最近観測されたある攻撃キャンペーンは17か国のダークトレース顧客で確認され、最も影響を受けたのは米国でした。この侵害はソフトウェアの欠陥から始まったものではなく、信頼されるユーザーが信頼されるアクションを実行したことが端緒となりました。

サプライチェーン:信頼が大規模に武器化される

3月と4月には共通の教訓が確認されました。それは信頼がサプライチェーン脆弱性となったということです。Axiosの侵害では幅広く使用されているメンテナーへの信頼が悪用され、Trivyキャンペーンは信頼されるCI/CDインフラ、リリースアーティファクト、およびコンテナイメージを利用して、正当な開発ワークフローに悪意あるコードを押し込みました。

これを最もはっきりと示した事例は、2月から3月にかけて観測されたキャンペーンです。多数のデバイスがHola VPNを使用している間に悪意のあるペイロードをダウンロードし、その後、Holaの配信パイプラインの侵害に関連していることが判明しました。ダークトレースの脅威調査チームは、公開アドバイザリがリリースされる前に、複数の顧客において繰り返し発生している異常な動作から、この侵害に関連する活動を特定しました。

最近では、攻撃者が正当なブロックチェーンインフラを悪用して、AMOSやPhexia等のインフォスティーラーを投下しているケースが見られます。セキュリティリソースが限られているユーザーによく使用されている一般的なVPN等のツールは、正当なC2インフラと組み合わせることで、攻撃者がはるかに広範な被害者層に到達することを可能にする一方、防御側は関連するエンドポイントを単純にブロックすることはできないため、やっかいな問題になります。

防御者にとっての課題は、もはや悪意のあるインフラを特定することではなく、信頼されるインフラが悪意のある動作を始めたときにそれを認識できるかどうかということです。

クラウドとSaaS:標的から作戦領域へ

5月から6月には、デバイス登録、クラウドデータ窃取、SaaS悪用、RDPの拡大、リモート管理ツール関連の活動が見られ、攻撃者がクラウドやSaaSを単なる標的としてではなく、むしろ好ましい作戦環境としてますます認識していることが示唆されました。 

ダークトレース顧客でのある事例では、1つの侵害されたSaaSアカウントがEメール、SaaS、ネットワークレイヤーにわたる活動を引き起こし、これには受信トレイルールの変更、フィッシングの拡散、疑わしいインフラへの接続が含まれていました。これらの兆候のいずれも単独では決定的とは言えませんでしたが、総合すると明らかに侵入を示していました。これらの環境において、攻撃者はますます信頼管理をを回避する必要がなくなっています。信頼は、侵害されたアイデンティティ、委任されたアクセス権、および正当な管理ツールを通じて引き継ぐことができるからです。これは、2025年に見られたSaaSを標的としたランサムウェアの傾向の自然な進化であると言えます。ますます多くのケースにおいて、ビジネスが運営されるのと同じプラットフォームが、敵対者が作戦を展開するプラットフォームとなっています。

AI:攻撃の加速装置でありアタックサーフェス、そして信頼される、しかしリスクの高いアクター

信頼がアタックサーフェスなら、AIはそれが最も急激に拡大している領域であると言えます。ダークトレースの顧客基盤全体において、2026年前半にAIサービスへの接続は平均13%増加し、接続数は1600万回以上、標準的な組織は7つの異なるAIプロバイダーとやり取りするようになっています。そしてAIはもはや企業のごく一部ではありません。日々の業務に組み込まれています。この変化が3つの問題を生み出しましたが、これらはすべて2026年前半にダークトレースによって観測されています。

1. 攻撃倍増装置としてのAI

ダークトレースは、AIによって生成されたReact2Shellを悪用するマルウェアを特定しました。これは攻撃者がLLMを使用して有効なエクスプロイトコードを生成し大規模に展開したものです。脅威ランドスケープ全体で見ても同様の活動が増えており、効果的な攻撃作戦への参入障壁が崩れつつあることを示唆しています。最近のJadePuffer事例にも見られるように、エージェント型脅威アクターがインターネットに接続されたサーバーの脆弱性をエクスプロイトし、その後完全に自動化されたランサムウェア攻撃が開始されており、AIは脆弱性の公開から実際のエクスプロイトまでの過程を加速させています[1]。

2. アタックサーフェスとしてのAI

今やAIレイヤー自体も、調べてみる価値があります。あるオートメーション技術メーカーにおいて、侵害されたLLMプロキシが他のAIサービスへの踏み台として利用され、それが失敗すると攻撃者は暗号通貨マイニングに切り替えたという事例がありました。DarktraceのCyber AI Analystはこの侵入インシデントを明らかにし、Managed Threat Detectionサービスにより顧客への通知が行われたことにより、事態がそれ以上進行する前に封じ込めることができました。実務者にとっての教訓は明確です:AIゲートウェイ、プロキシ、モデルエンドポイントは、本番環境のクラウドワークロードと同様に扱うべきです。なぜなら、攻撃者は既にそうしているからです。

3. 信頼される、ただしリスクもあるアクターとしてのAI

Darktrace/ SECURE AIの観測結果からわかることは、最も一般的な現実世界のリスクはさらに判別が難しいということです。従業員が、個人識別情報(PII)、税務記録、身分証明書、会社の財務データ、人事記録、個人の医療データをLLMのプロンプトに入力することや、シャドーAIの蔓延、そしてモバイルデバイスからのAI使用の増加が挙げられます。28日間で約28,000人のユーザーから送信された約280,000件のプロンプトのうち、Darktraceはこれらのプロンプトの約1%(2,945件)に機密性の高いデータが含まれていることを特定しました。*

‍*プロンプトデータはユーザーのプライバシーを保護するために、集積および匿名化された形で分析されました。

防御者にとって、課題はコンテキストです。つまり、正当なビジネス利用が重大なリスクに変わるタイミングを、プライバシーやユーザーの信頼を損なうことなく見極めることです。組織がAIシステムをますます信頼し、AIがマシンスピードで機密情報にアクセス、処理、共有するようになるなかで、アイデンティティ、アプリケーション、クラウドインフラと同様に、AIも保護および監視されなければなりません。

スピードと地政学:迅速な作戦、長期的な目標

2026年前半に行われたいくつかの調査では、攻撃者が新たに公開された脆弱性をいかに迅速に実用化し、パッチ適用サイクルが完了する前にOAST(Out-of-Band Application Security Testing)インフラおよび信頼されたクラウドサービスを通じてエクスプロイト検証を行っているかが明らかになりました。React2Shellは2時間で侵害され、BeyondTrustのエクスプロイトも1日未満で発生しました。このような状況の中で、国家を背後に持つ脅威アクターは、引き続き正当なサービス、クラウドインフラ、および信頼関係を通じた、長期的なアクセス、情報収集、および事前配置に重点を置いています。中国、ロシア、イラン、北朝鮮(DPRK)を背後に持つ作戦は共通の特徴を持っています。それは即座に混乱を起こすことよりも、永続化と戦略的な配置を優先するということです。

中国:ダークトレースは、中国系アクターが信頼されるサービス、DLLサイドローディング、およびモジュール型の侵入チェーンを通じた長期的なアクセスの獲得を優先している状況を確認しています。これはCrimson Echoレポートでも解説され、Twill Typhoonの手法に関連するアクティビティと一致しています。

イラン:ダークトレースによるZionSiphonの調査は、イランに関連するアクターのOT環境への関心を浮き彫りにし、諜報目的とインフラ破壊能力を融合させている実態を明らかにしています。

ロシア:ダークトレースによる調査、および業界全体のさまざまな報告は、ロシアがウクライナ関連の支援に関する長期的な情報収集のために、信頼関係とサプライチェーンを標的としていることを明らかにしています[2]。

北朝鮮:ダークトレースは、脆弱性の迅速な武器化と永続的アクセス技術を組み合わせた北朝鮮関連の活動を観測ししています。これにはAxiosのサプライチェーン侵害、React2Shellエクスプロイト、ステルス性のmacOS侵入が含まれています。

 目的は脅威アクターによって異なっていましたが、手法は非常に一貫していました。信頼されるサービス、正当なインフラ、そして永続的アクセスは、即時の混乱よりも価値が高いことが示されています。

防御者のシフト

アイデンティティの侵害、サプライチェーン攻撃、SaaSの悪用、AIインフラの標的化、国家が支援する作戦、いずれのケースにおいても、攻撃者は防御のコントロールを突破するのではなく、信頼されたシステムを通じて行動することで成功を収めることが増えています。信頼されるユーザー、信頼されるソフトウェア、信頼されるインフラチャ、そしてますます信頼されるAIシステムは、すべて有効な攻撃経路となりました。 

防御者にとっての課題はもはや、単にあるアクションが許可されるかどうかを判断することではなく、そのアクションがより広いコンテキストの中で正当かどうかを見極めることです。認証、評判、出自は依然として重要ですが、それだけではもはや十分とは言えません。攻撃者がますます信頼されるシステム内で活動するようになる中で、最も強力なシグナルは多くの場合動作の逸脱です。つまり、信頼されているアクティビティが期待される振る舞いと一致しなくなった時にそれを識別することです。

本稿の執筆にはNathaniel Jones(SVP, Global Threat Intelligence)、Emma Foulger(Global Threat Research Operations Lead)、Justin Torres (Senior Cyber Analyst) Daniel Levy(Threat Hunting Data Scientist)が協力しました。

‍
編集:Ryan Traill(Content Manager)

‍

付録1:脅威調査手法

ダークトレースの脅威調査チームは、顧客の運用環境に対する詳細な調査を行ってアクティブな脅威を識別し、主要な侵害インジケーター(IoC)を特定し、関連する脅威インテリジェンスを提供しています。この調査はダークトレースの異常ベース検知に基づいたもので、脅威調査チームによる徹底した分析およびコンテキスト化が行われています。検知された脅威は関連する顧客のセキュリティチームに直ちに報告されます。顧客がダークトレースの自律遮断テクノロジーを使用している場合、これらの脅威は速やかに緩和され、エスカレーションが阻止されます。

 2026年1月1日から6月30日までの期間、ダークトレースは顧客ベースにおいて多種多様なサイバー脅威を調査しました。その多くは同様のTTPおよびIoCが短い期間内に一定の数の顧客に影響を及ぼした、複数の顧客を標的とした攻撃作戦的活動であったことが判明しています。 

Eメールに関連する統計は、2026年1月1日から6月30日までの間に、すべてのクラウドホスト型顧客環境におけるDarktrace / EMAILの集約されたデータから導出されています。特異な観測値を除外するために、集約を行う前に標準的なデータ品質フィルタリングが適用されています。地域別の統計は、このデータセットの関連サブセットに基づいています。 

付録2:キャンペーン - 地域およびセクター別の傾向

過去6か月間の脅威ランドスケープは上記の大まかなテーマにより定義されていますが、ダークトレースの顧客基盤全体でのキャンペーンクラスタリングにより、それらがセクター、地域、産業ごとにどのように異なっているかが明らかになりました。 

ダークトレースの脅威調査チームは、顧客ベースに影響を与えるさまざまな脅威を調査しています。この調査を通じて、共通のTTPやインフラが観察され、短期間で多くの顧客に影響を与える、攻撃キャンペーンのような活動のクラスターが特定されました。 

セクターおよび産業は、一貫した分類を確保するために標準産業分類(SIC)システムを使用して分類されています。本レポートのセクターおよび地域別の考察は、より広範な世界的な傾向を反映している一方で、ダークトレースの顧客基盤の分布にも影響を受けています。例えば、金融、製造、教育分野はダークトレースの顧客の中で多く、これらのセクターで観測される事例数が多くなる可能性があります。これは必ずしも特定のセクターにおけるリスクが高いことを示すものではなく、顧客の分布を反映しています。同様に、地域の傾向はダークトレースの顧客の地理的分布によって影響を受ける可能性があります。

2026年前半にダークトレースの脅威調査チームによって特定されたキャンペーンクラスターの分析では、明確な地域別の傾向が明らかになりました:

  • ヨーロッパ、中東、アフリカ(EMEA)がすべてのキャンペーンクラスター事例の60%を占めており支配的でした。
  • アメリカ大陸(AMS)は、その次に影響が大きかった地域でありキャンペーンクラスター事例の30%を占めていました。
  • アジア太平洋および日本(APJ)地域はキャンペーンクラスターの影響をあまり受けていませんでした。これは脅威アクターがこの地域の優先度を低くし、代わりに他の地域に注力した可能性を示しています。

産業セクターの標的化も地域によって大きく異なりました:

  • EMEA地域では、情報通信分野が大きく影響を受け、全体の25%を占めました。
  • 対照的に、AMSでは標的はより均等に分布しており、教育、行政機関および防衛、金融および保険の各セクターがいずれもAMS地域の事例の20%以上を占めていました。
  • APJ地域ではキャンペーン活動はより均等に分散しており、特定のセクターが支配的な標的として浮上することはありませんでした。

いくつかの国はそれぞれの地域内でも際立った特徴がありました:

  • 米国はAMS内のすべてのキャンペーンクラスターの60%を占めていました。
  • 日本はAPJ全体のキャンペーン事例の40%を占めました。
  • EMEA地域では、英国とジンバブエがそれぞれ特定された事例の23%を占めており、両国ともさまざまなキャンペーンのタイプに影響を受けています。

‍

Inside the SOCおよび2026年度脅威調査の月次傾向:アクセスからインパクトまで

Month Dominant Themes
January Voice phishing, VPS infrastructure, WebSocket C2, RMM abuse, ransomware, infostealers (StealC), and trojanized installers (7-Zip).
February Voice phishing, VPN intrusion, edge infrastructure compromise (BeyondTrust), and RMM abuse.
March Sustained supply chain compromise (Hola VPN, Axios, Trivy), malicious browser extensions, phishing, and discovery tools.
April Account creation abuse, payload delivery, VPN credential abuse, Fortinet exploitation, and botnet activity.
May PowerShell, EtherHiding, data exfiltration, VPN access, business email compromise (BEC), ClickFix, and infostealers (AMOS).
June RDP abuse, device registration, RMM usage, voice phishing, cloud data theft, botnet activity, blockchain abuse, ClickFix, and infostealers (AMOS).

付録3:参考文献

外部

[1] https://www.darkreading.com/cyberattacks-data-breaches/jadepuffer-first-complete-llm-driven-ransomware-attack

[2] https://www.trendmicro.com/en_us/research/26/c/pawn-storm-targets-govt-infra.html

ダークトレースのリソース

1.        https://www.darktrace.com/blog/ai-llm-generated-malware-used-to-exploit-react2shell

2.        https://www.darktrace.com/blog/2025-cyber-threat-landscape-darktraces-mid-year-review

3.        https://www.darktrace.com/resources/annual-threat-report-2026

4.        https://www.darktrace.com/blog/when-trust-becomes-the-attack-surface-supply-chain-attacks-in-an-era-of-automation-and-implicit-trust

5.        https://www.darktrace.com/blog/hola-vpn-abuse-from-proxy-traffic-to-malware-and-cryptomining

6.        https://www.darktrace.com/blog/security-after-signatures-operating-in-a-world-of-pre-cve-disclosure-exploitation-collapsed-trust-boundaries-and-autonomous-systems

7.        https://www.darktrace.com/blog/when-ai-infrastructure-becomes-part-of-the-attack-surface

8.        https://www.darktrace.com/blog/cve-2026-1731-how-darktrace-sees-the-beyondtrust-exploitation-wave-unfolding

9.        https://www.darktrace.com/resource/understanding-chinese-nexus-cyber-tradecraft

10.   https://www.darktrace.com/blog/chinese-apt-campaign-targets-entities-with-updated-fdmtp-backdoor

11.  https://www.darktrace.com/blog/inside-zionsiphon-darktraces-analysis-of-ot-malware-targeting-israeli-water-systems

12.  https://www.darktrace.com/resources/the-state-of-cybersecurity-in-the-finance-sector

13.  https://www.darktrace.com/blog/from-click-to-command-behavioral-detection-of-applescript-led-macos-intrusions

14.  https://www.darktrace.com/blog/the-state-of-cybersecurity-in-the-finance-sector-six-trends-to-watch

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence
Written by
Emma Foulger
Global Threat Research Operations Lead

More in this series

No items found.

Blog

/

AI

/

October 5, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

October 5, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

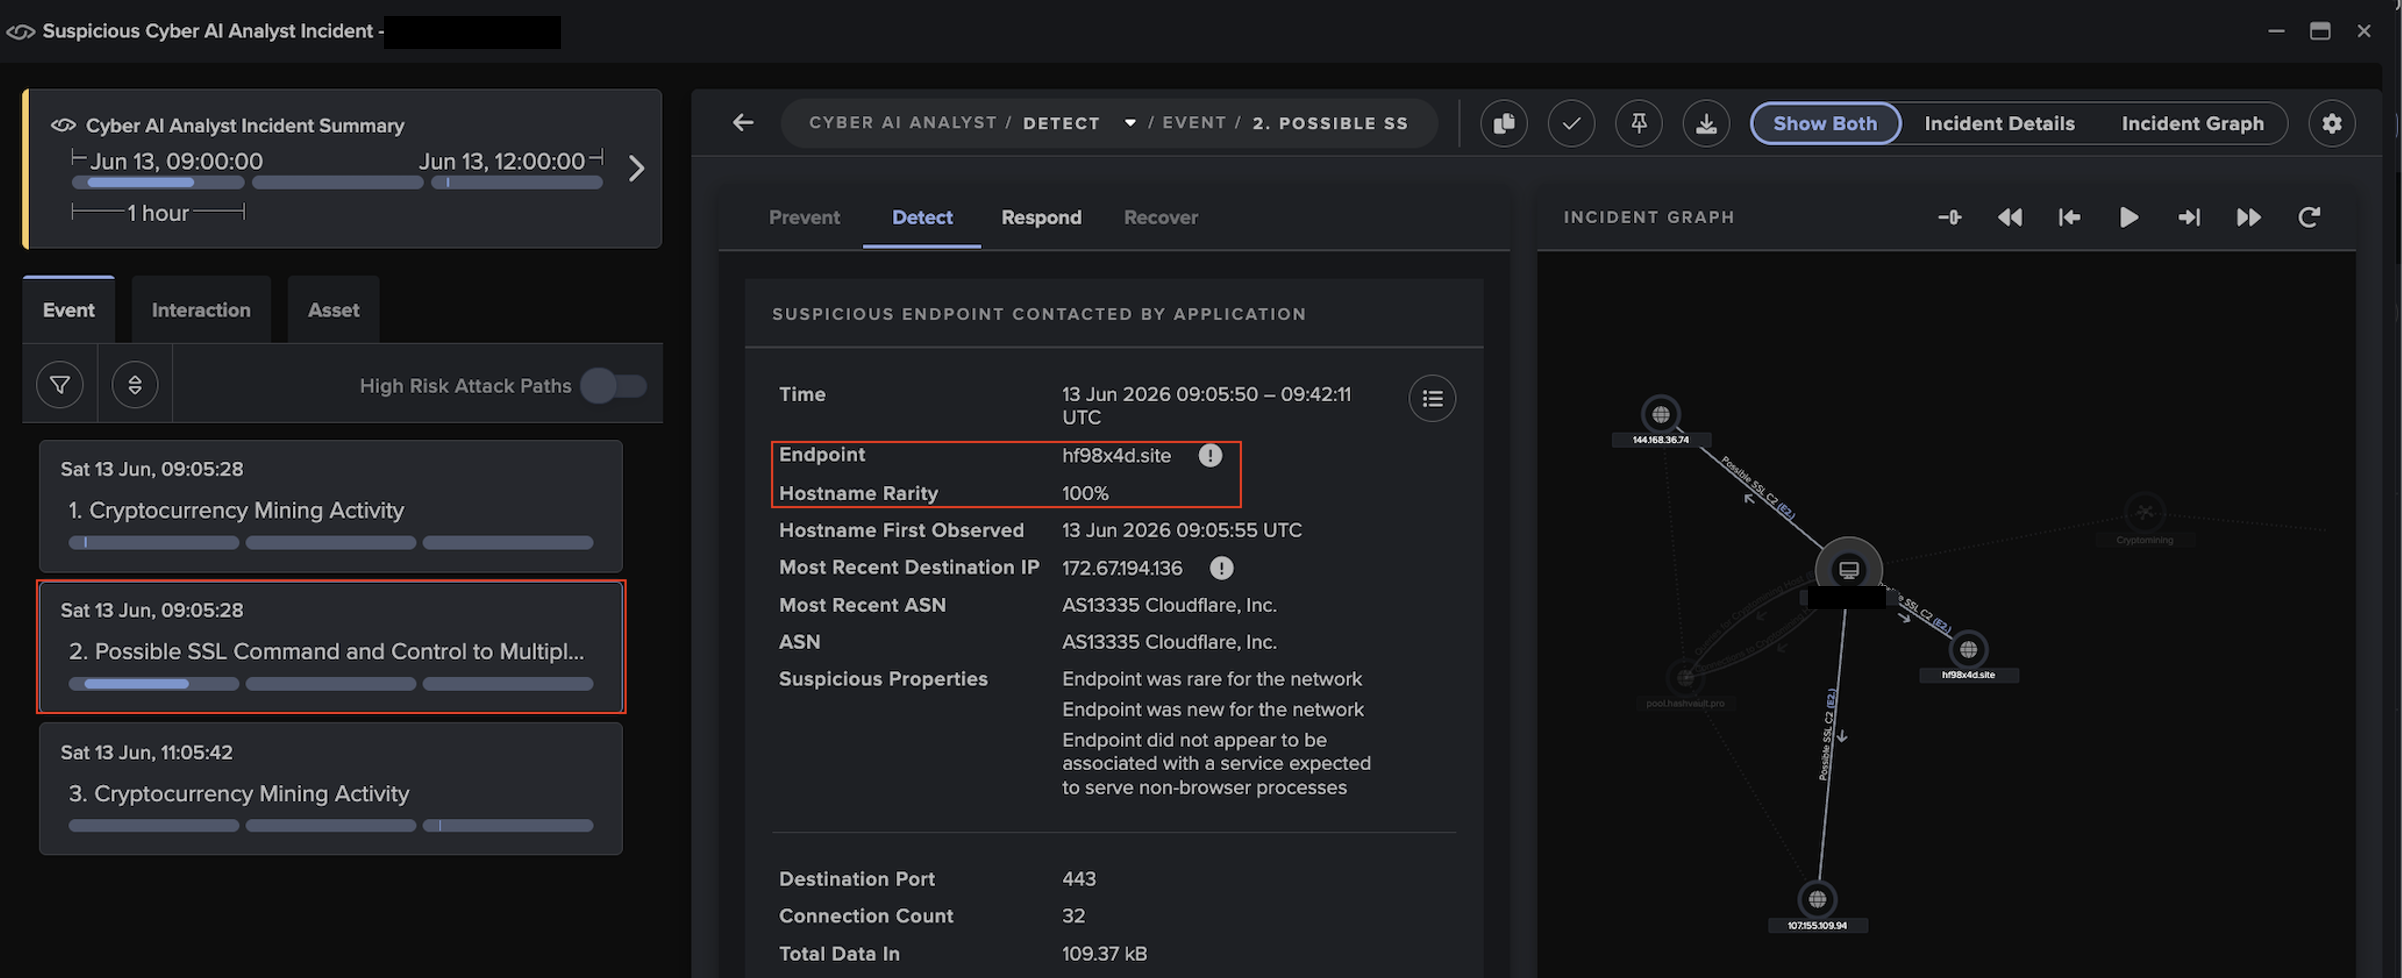
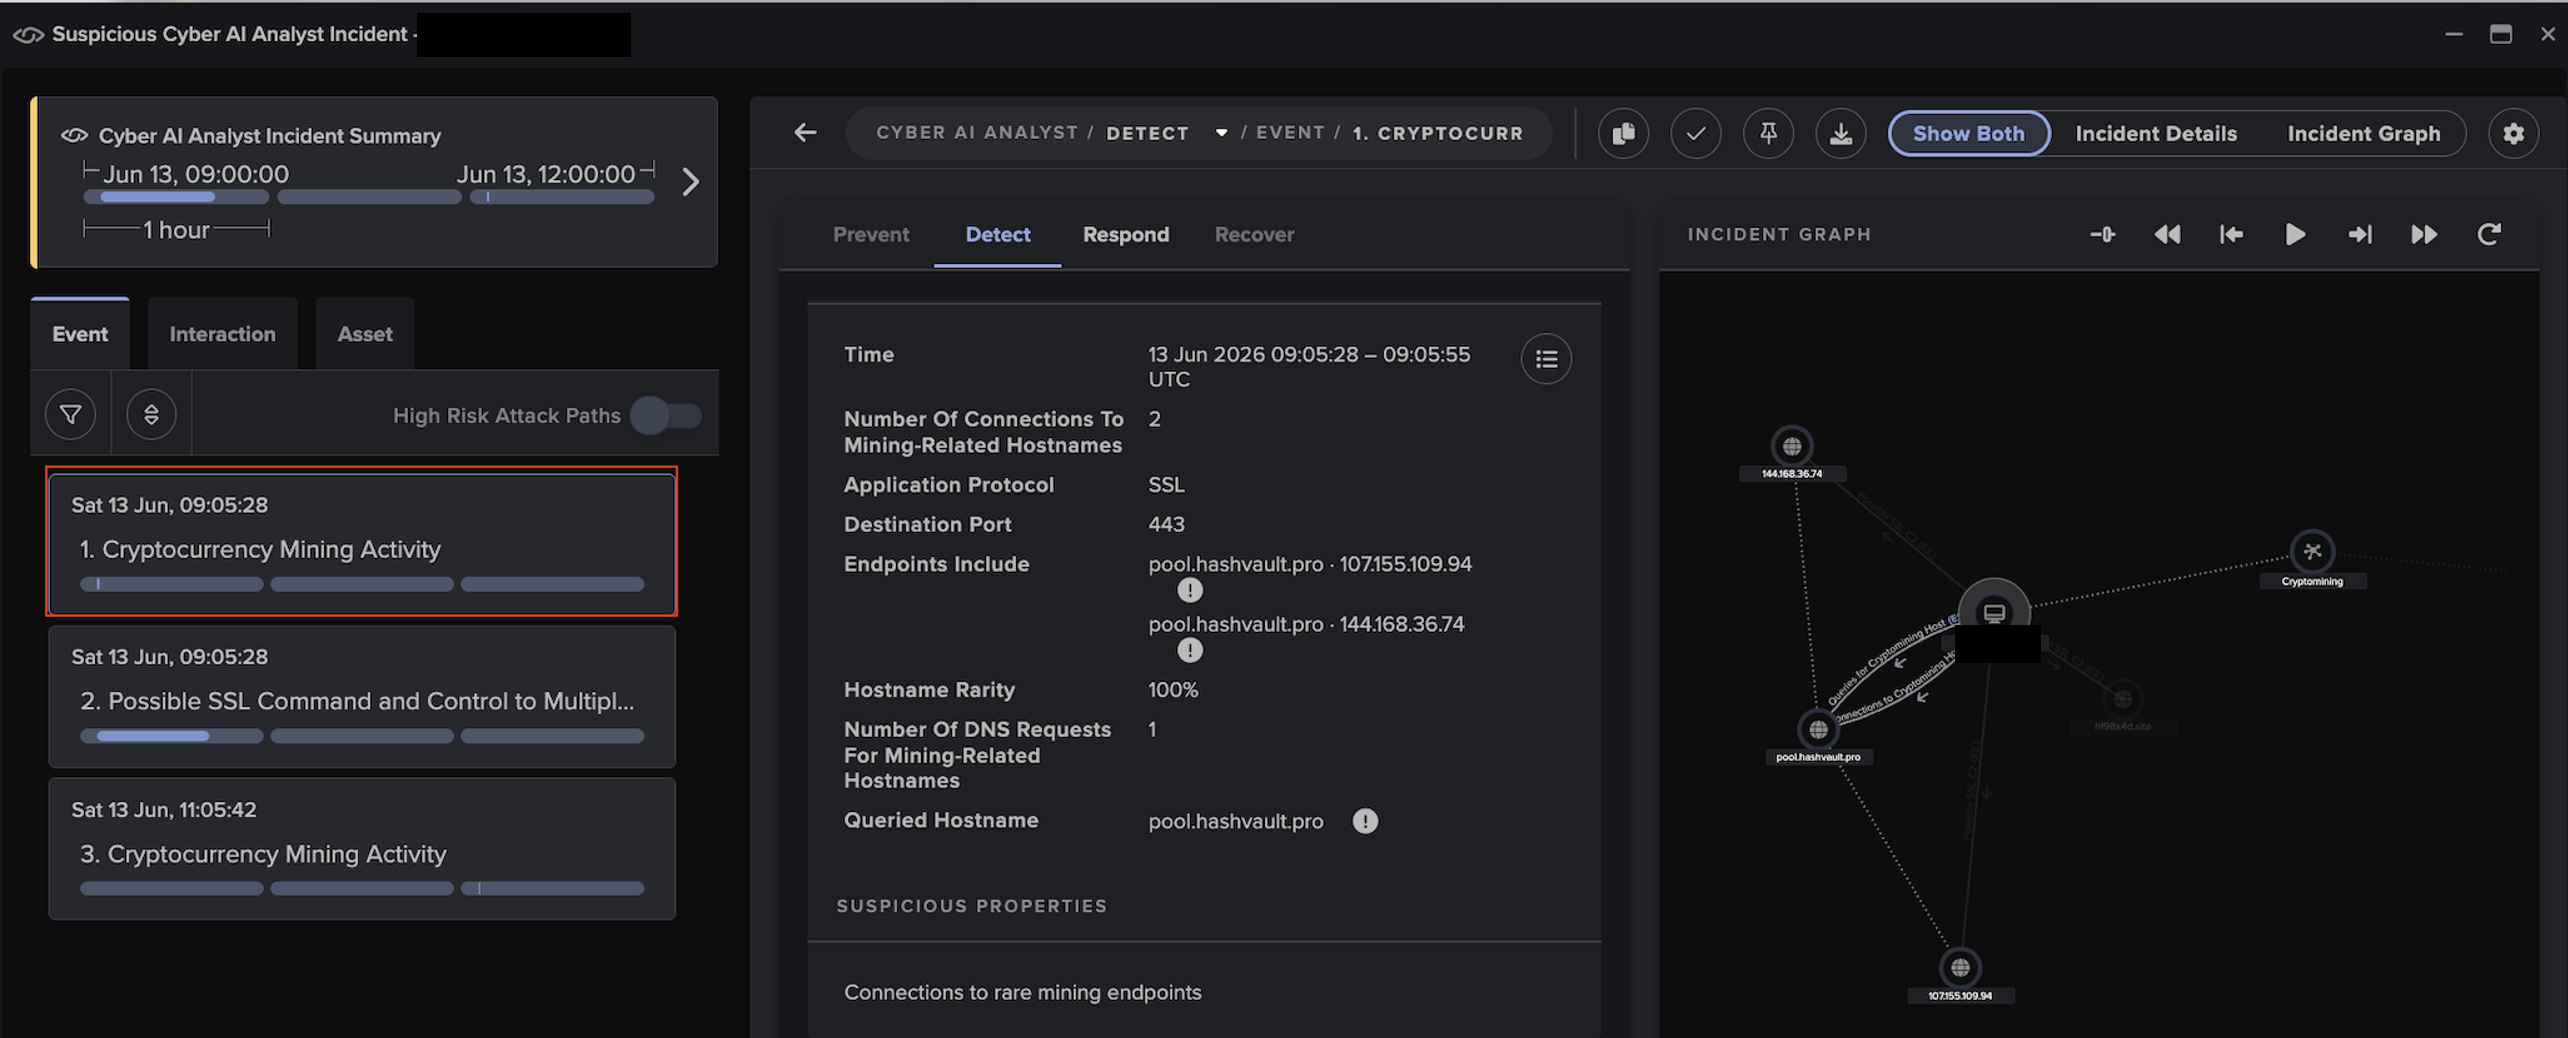
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

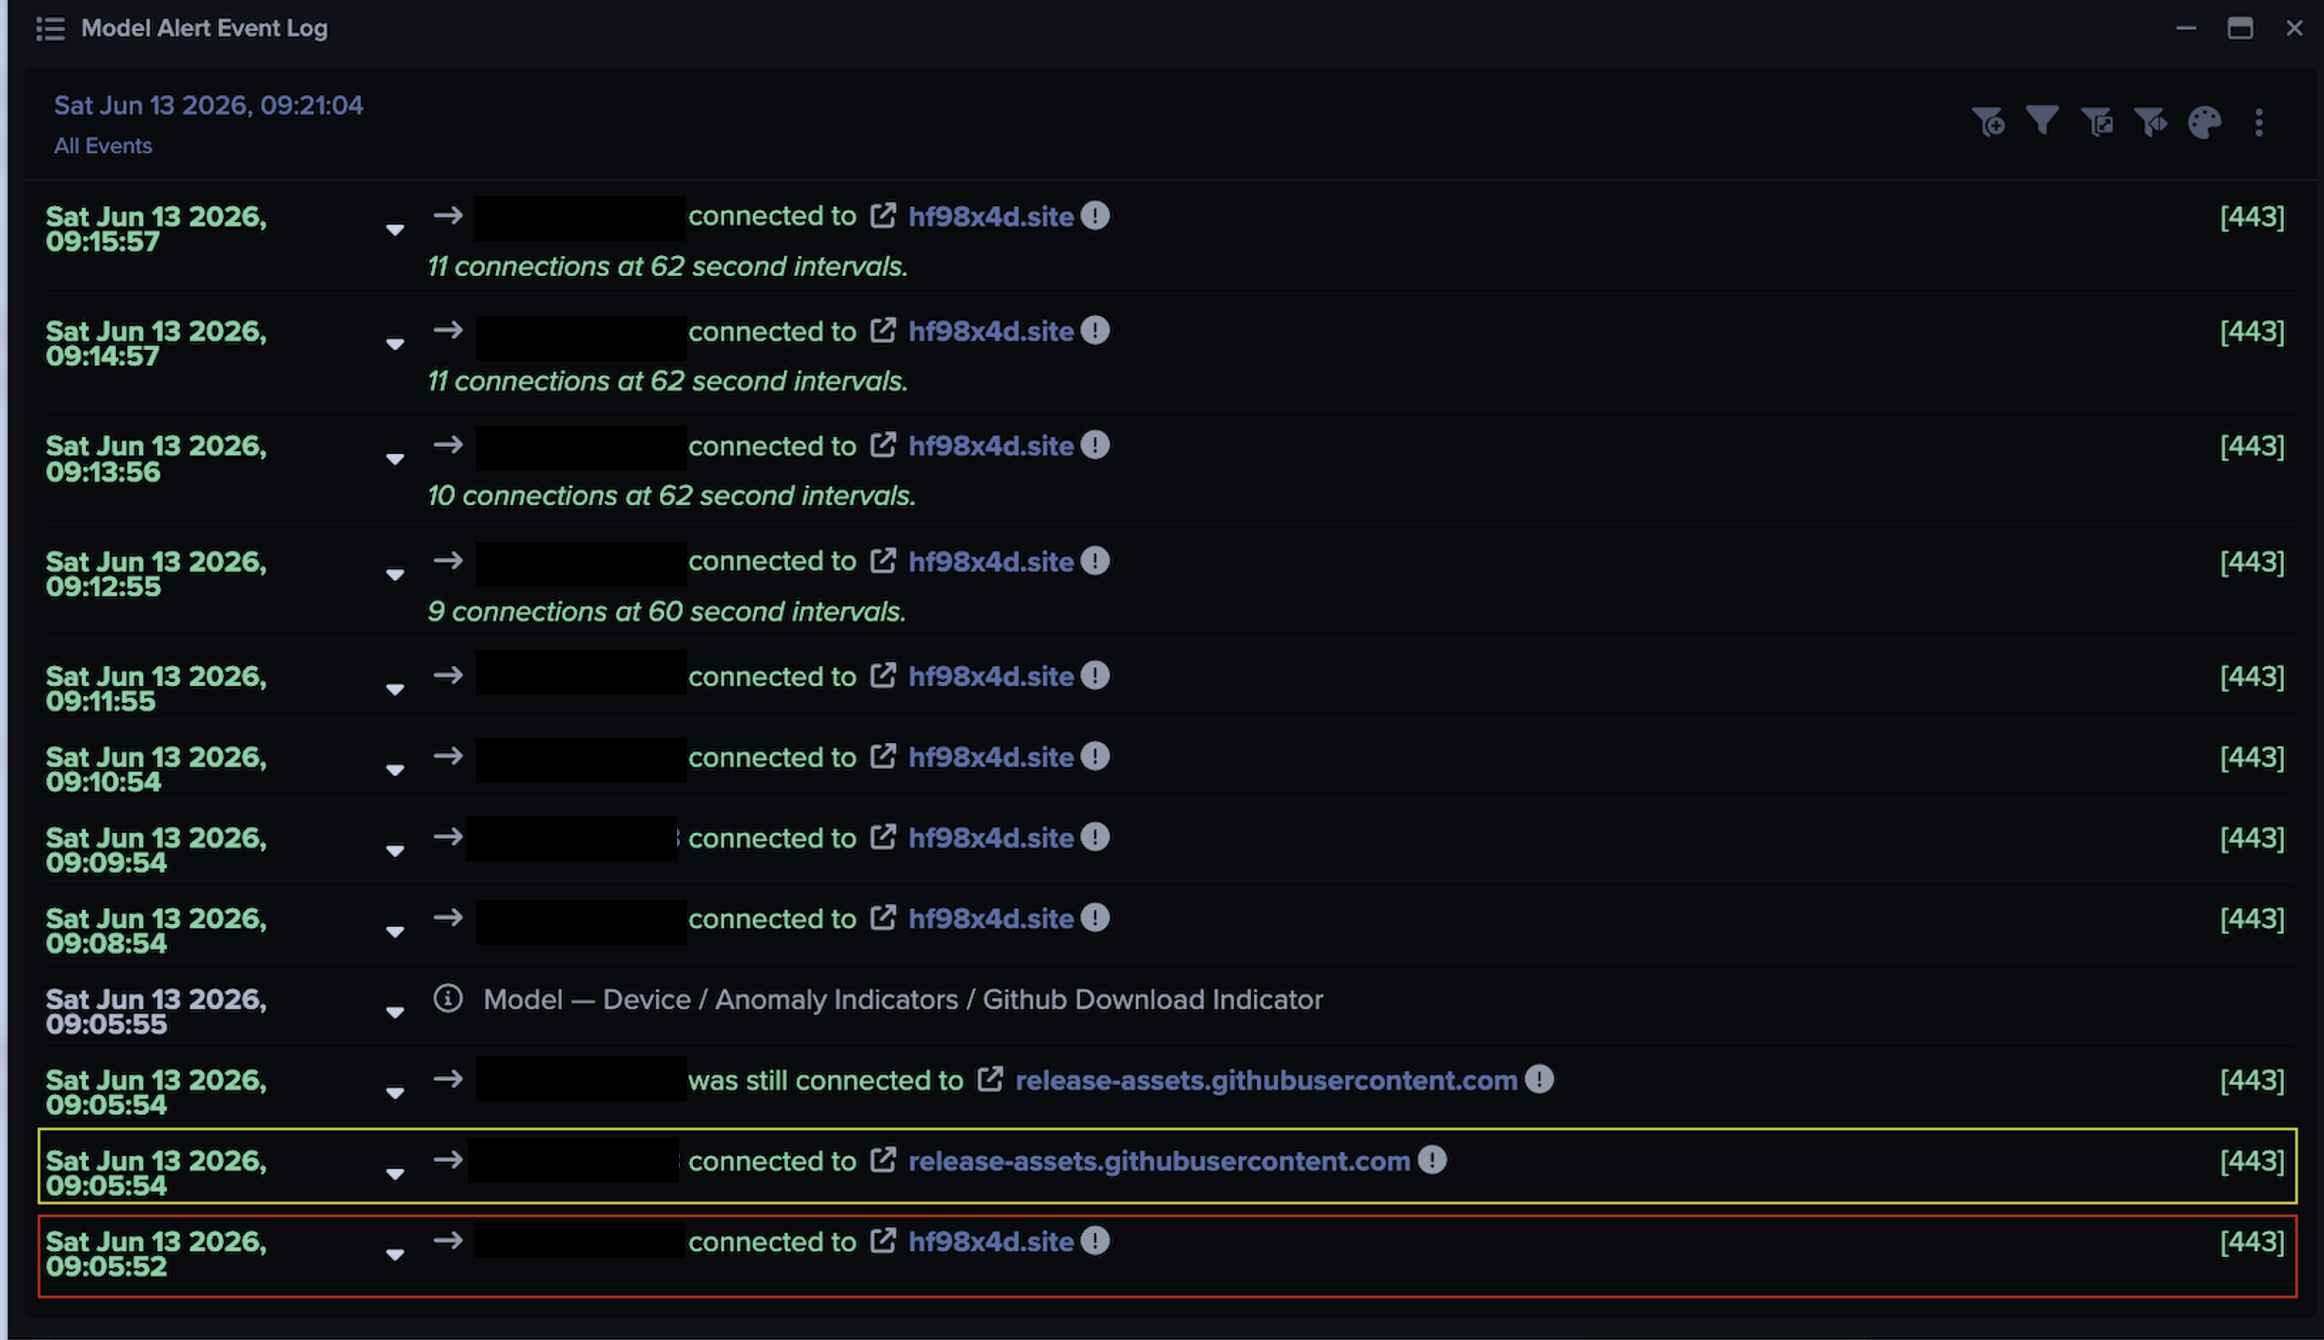
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ