ブログ
/
OT
/
March 20, 2026

ダークトレース、2026年度Gartner® CPS Protection Platforms部門のMagic Quadrant™ において唯一のVisionaryの評価を受ける

ダークトレースはDarktrace / OTにおいて2026年度Gartner® CPS Protection Platforms部門のMagic Quadrant™ において唯一のVisionaryの評価を受けたことを喜んでお知らせいたします。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Pallavi Singh
Senior Product Marketing Manager
Default blog image
20
Mar 2026

Gartner® Magic Quadrant™ for CPS Protection Platformsは、この急激に変化する市場を形成するベンダーについての独立した見解を提供するものであり、各プロバイダーがますます接続の進むOT(Operational Technology)およびサイバーフィジカル環境に関連するサイバーセキュリティリスクの解決をどのように支援しているかを評価するものです。セキュリティおよびリスク管理のリーダー達はこの調査結果を使用してベンダーの位置づけを理解し、CPS(Cyber Physical System)セキュリティ戦略の最新化に向けた判断の参考にしています。CPSセキュリティプラットフォームを評価されている組織の方はレポート全体をレビューし、この市場についての包括的な視点を得られることをお勧めします。

ダークトレースが2回連続して唯一のVisionaryに位置付けられたことは、CPSセキュリティに対する当社のイノベーション、製品展開および長期戦略の強みを裏付けていると捉えています。

Darktrace / OTは現代の産業環境の防御、そしてIT、OT、およびIoTが統合された環境の保護の現実に対処するために構築されており、自己学習型AIを適用して既知、未知、および新手の脅威を検知し、調査を加速するとともに運用上の影響に基づいてリスクの優先付けを行います。この独自のアプローチが重要インフラを担う複雑な組織が必要とする柔軟な展開モデルを支えています。
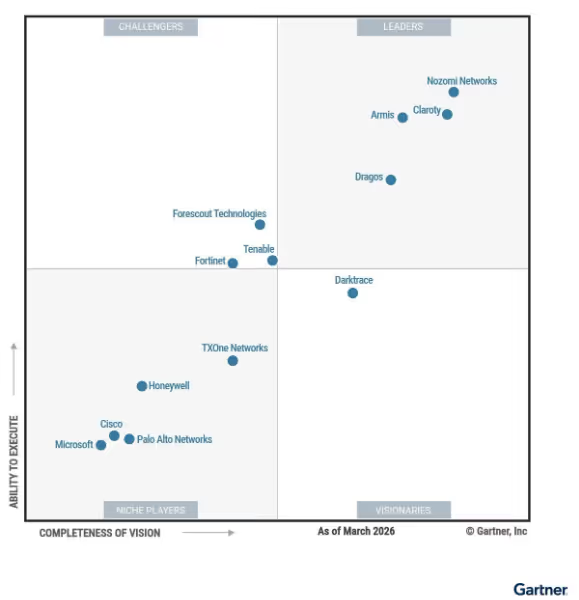
gartner 2026 CPS magic quadrant

CPSセキュリティでDarktrace/ OTが傑出している理由

産業用環境と企業インフラの統合が引き続き進むなかで、セキュリティリーダーは従来のセキュリティアプローチではアップタイム、安全性、規制要件への対応が難しいシステムのサイバーリスクの削減を求められています。セキュリティチームは環境内でどのようにリスクが発生するかを理解し、より迅速かつ明確性を持って脅威を調査し、運用への影響に基づいて対処を優先付けなければなりません。

Darktrace / OTはその課題のために設計されています。クロスドメインの可視性、検知、調査を、自己学習型AI、CVEを超えた専用のリスク管理、そしてセキュリティの成果とオペレーションのレジリエンスを両立させる、OTのためのワークフローを組み合わせたソリューションです。

統合されたCPS環境全体に一元的な可視性

重要インフラは従来のOTネットワークを超えて拡大し、エンジニアリングワークステーション、HMI、リモートアクセス、企業システム、クラウドにリンクされたアーキテクチャも含まれるようになっており、セキュリティチームはアセット間の関係、依存関係がどこに存在しているか、そして複数のドメインにわたり露出がどのように生じるかを理解する必要があります。

Darktrace / OTはOT、IT、IoT、IoMTにわたる一元的な可視性を提供し、コネクテッド環境内のサイバーリスクに対する理解を助けます。Operational Overview,、OTワークフロー、プロトコルに対する深いレベルの検査等の機能を通じてテレメトリーを組み合わせることにより、Darktraceはエンジニアとセキュリティチームが共通のコンテキストを使用し、防御する環境についてのよりOTに即した理解に基づいて作業することを可能にします。

自己学習型AIにより強化された脅威検知、調査、対応

シグネチャは既知の脅威に対しては依然として価値を提供しますが、内部関係者による不正使用、ゼロデイエクスプロイト、および標的を絞った作戦のためにカスタム構築されたマルウェアには対応できません。Darktrace / OTは自己学習型AIを使用して、既知のマルウェアよりも異常な通信、正当なアクセスの誤用、または疑わしいデバイスの挙動を通じて脅威が現れることが多い産業用環境全体において、正常な行動からの微妙な逸脱を検出します。インシデント調査を強化するために、DarktraceのCyber AI Analystは自動的にアクティビティを相関付け、コンテキストに基づくサマリーを生成して人手によるトリアージ作業を削減し、チームはアラートの発生からインシデントの理解へ、より迅速に進むことができます。  

Darktrace / OTは、NEXTfor OTを通じた拡張テレメトリーにより調査と対応をさらに強化し、エンジニアリングワークステーションやHMIなどの運用エンドポイントへの可視性を拡大して、より深い根本原因分析をサポートします。自己学習型AIを活用することで、Darktraceは異常なアクティビティをピンポイントで封じ込めつつ産業プロセスの正常な稼働を維持する、自律遮断も可能にしています。対応アクションはデバイス、デバイス種別、またはネットワークセグメントごとにカスタマイズでき、完全に自律的なアクションの実行や、人間の確認を含むワークフローなどのオプションを選択可能です。これにより、セキュリティチームはオペレーションの中断を削減すると同時に、対応の判断に対するコントロールを維持できます。

オペレーションへの影響に基づく、コンテキストを考慮した優先付け

セキュリティチームが受け身の防御からセキュリティ体制についての積極的な思考へシフトするには適切なツールが必要です。しかしほとんどのOTチームは産業用システムを理解していないIT中心型のツールに縛られ、静的なCVEリストに常に圧倒されています。そしてこれらのツールはOT専用のプロトコルへの理解が欠けています。  

Darktrace / OTはオペレーションのコンテキストに基づいてサイバーリスクを優先付けることにより、静的な脆弱性リストを超えた防御を可能にします。アセットの重要性、ネットワークの関係、エクスプロイト可能性についてのインテリジェンス、動作のテレメトリー、攻撃経路分析を取り込むことにより、Darktrace / OTはどの露出がオペレーションに現実的に影響を与える可能性があるかを理解するのに役立ちます。CVE深刻度、KEVデータ、MITREテクニック、ビジネスへの影響を相関付けることにより、Darktraceはオペレーションのレジリエンス、ガバナンス、そしてIEC-62443等のコンプライアンスの取り組みを支持する、より焦点を絞った修正の判断を可能にします。

現実の環境と企業システムとの整合性を考えた設計

Darktrace / OTは、産業用環境の現実、つまり、オンプレミス、ハイブリッド、分散、エアギャップを含むさまざまな、オペレーションに重要な影響を与えるネットワークへの柔軟な展開が欠かせない産業用環境のために設計されています。Darktrace / OTはSIEM、SOAR、CMDB、ファイアウォール、およびガバナンスツールを含むエンタープライズセキュリティエコシステムとも統合が可能で、幅広いセキュリティワークフローをサポートしています。これにより産業用環境の制約も尊重しつつOTセキュリティをエンタープライズプログラムと整合させ、セキュリティチームとエンジニアリングチーム間のコラボレーションを促進することができます。

お客様の評価とプラットフォームの認知  

過去12か月間に、Darktrace / OTはGartner Peer Insights*において4.8/5の評価(37 Reviewsに基づく)を受け、このことは重要インフラおよび産業用環境におけるお客様のこのプラットフォームに対する強い支持を裏付けているものと確信しています。

この評価に加え、ダークトレースは Network Detection and Response (NDR) およびEmail Security Platforms,部門でのLeaderの評価を含むGartner Magic Quadrantsの複数の部門において評価を受けており、このことはダークトレースの ActiveAI Security Platformの幅広さを表しています。
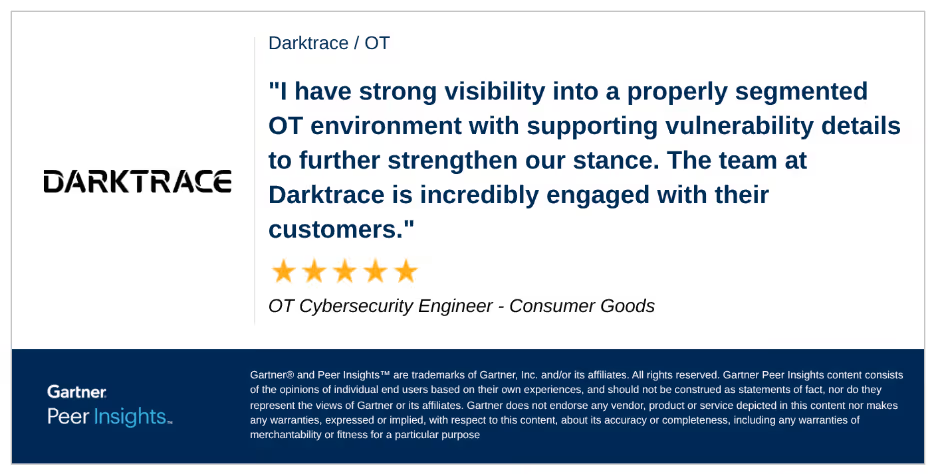
Darktrace / OT customer review

CPSセキュリティの未来を拓く

ダークトレースが2年連続して唯一のVisionaryに位置付けられたことは、当社の明確な方向性を反映していると考えます:つまりCPSセキュリティプラットフォームはお客様が可視性を調査につなげ、調査を優先付けにつなげ、優先付けを実際の運用上の成果につなげるのを支援する必要があるということです。

このことは引き続き Darktrace / OT の目標です。

産業用環境がより接続され、より複雑化し、よりビジネスにとって決定的なものとなるなかで、ダークトレースはこれからもお客様が不確実性を解消し、レジリエンスを強化し、稼働を維持しつづけるシステムを保護するのに役立つ機能に投資を続けます。

Gartner, Magic Quadrant for CPS Protection Platforms, Katell Thielemann,Ruggero Contu, Wam Voster, Sumit Rajput, 3 March 2026

Gartner®, Peer Insights™, Darktrace in CPS Protection Platforms, as of March 26, 2026

https://www.gartner.com/reviews/product/darktraceot

Gartner免責事項

GARTNER, MAGIC QUADRANTおよびPEER INSIGHTSは、Gartner Inc.または関連会社の米国およびその他の国における登録商標およびサービスマークであり、同社の許可に基づいて使用しています。All rights reserved.

Gartnerは、Gartnerリサーチの発行物に掲載された特定のベンダー、製品またはサービスを推奨するものではありません。また、最高のレーティング又はその他の評価を得たベンダーのみを選択するようにテクノロジーユーザーに助言するものではありません。Gartnerリサーチの発行物は、Gartnerリサーチの見解を表したものであり、事実を表現したものではありません。Gartnerは、明示または黙示を問わず、本リサーチの商品性や特定目的への適合性を含め、一切の責任を負うものではありません。

Gartner Peer Insightsのコンテンツは、個々のエンドユーザー自身の経験による主観的な意見が集約されたものであり、Gartnerまたはその関連会社の見解を表すものではありません。Gartnerは、Gartner Peer Insightsに掲載された特定のベンダー、製品またはサービスを推奨するものではありません。Gartnerは、商品性または特定目的への適合性の保証を含む、その正確性または完全性について、本コンテンツの内容に関する一切の責任を、明示または黙示を問わず負うものではありません。

この図表は、Gartner, Inc.がリサーチの一部として公開したものであり、文書全体のコンテクストにおいて評価されるべきものです。オリジナルのGartnerドキュメントは、リクエストによりDarktraceからご提供することが可能です。

‍

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Pallavi Singh
Senior Product Marketing Manager

More in this series

No items found.

Blog

/

AI

/

October 5, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

October 5, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

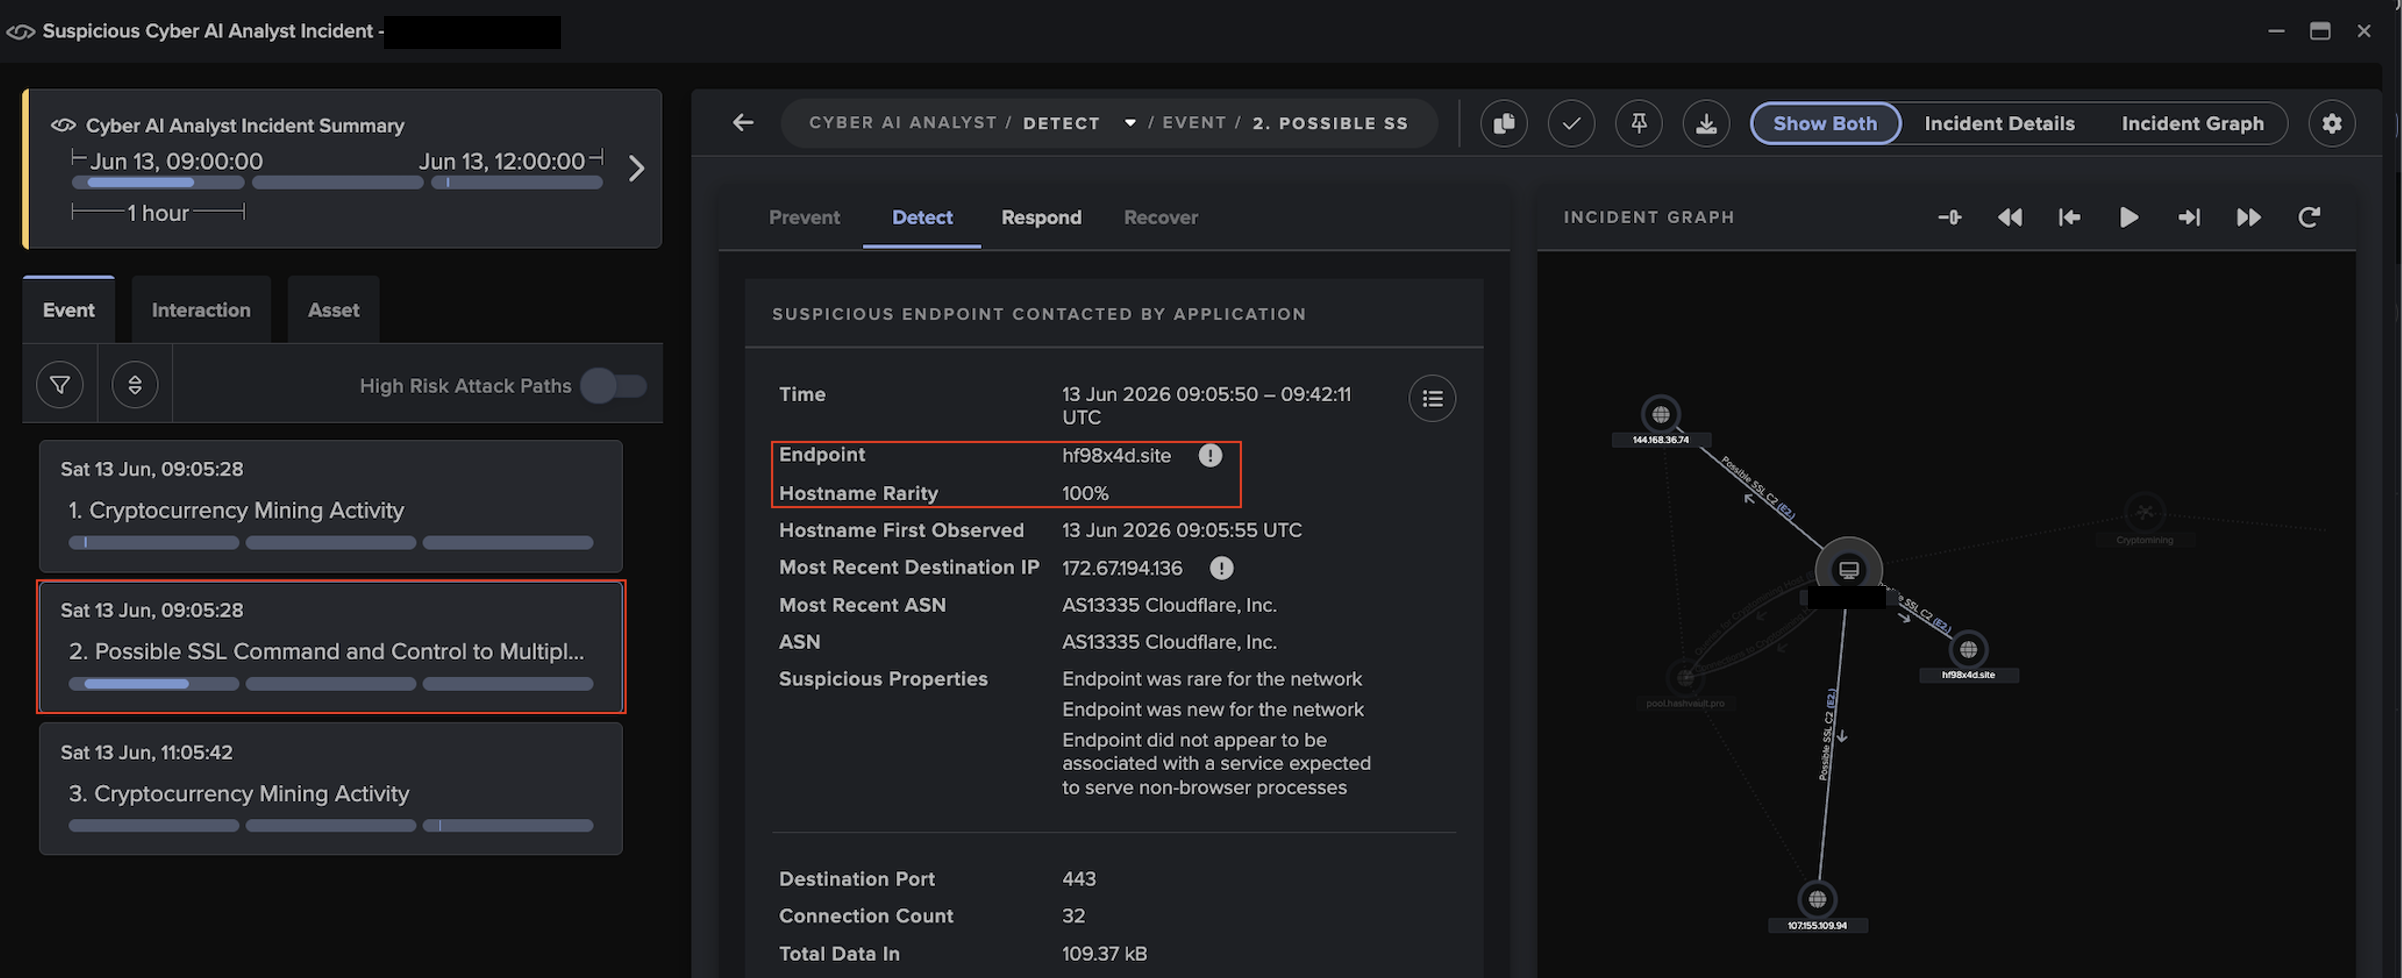
Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

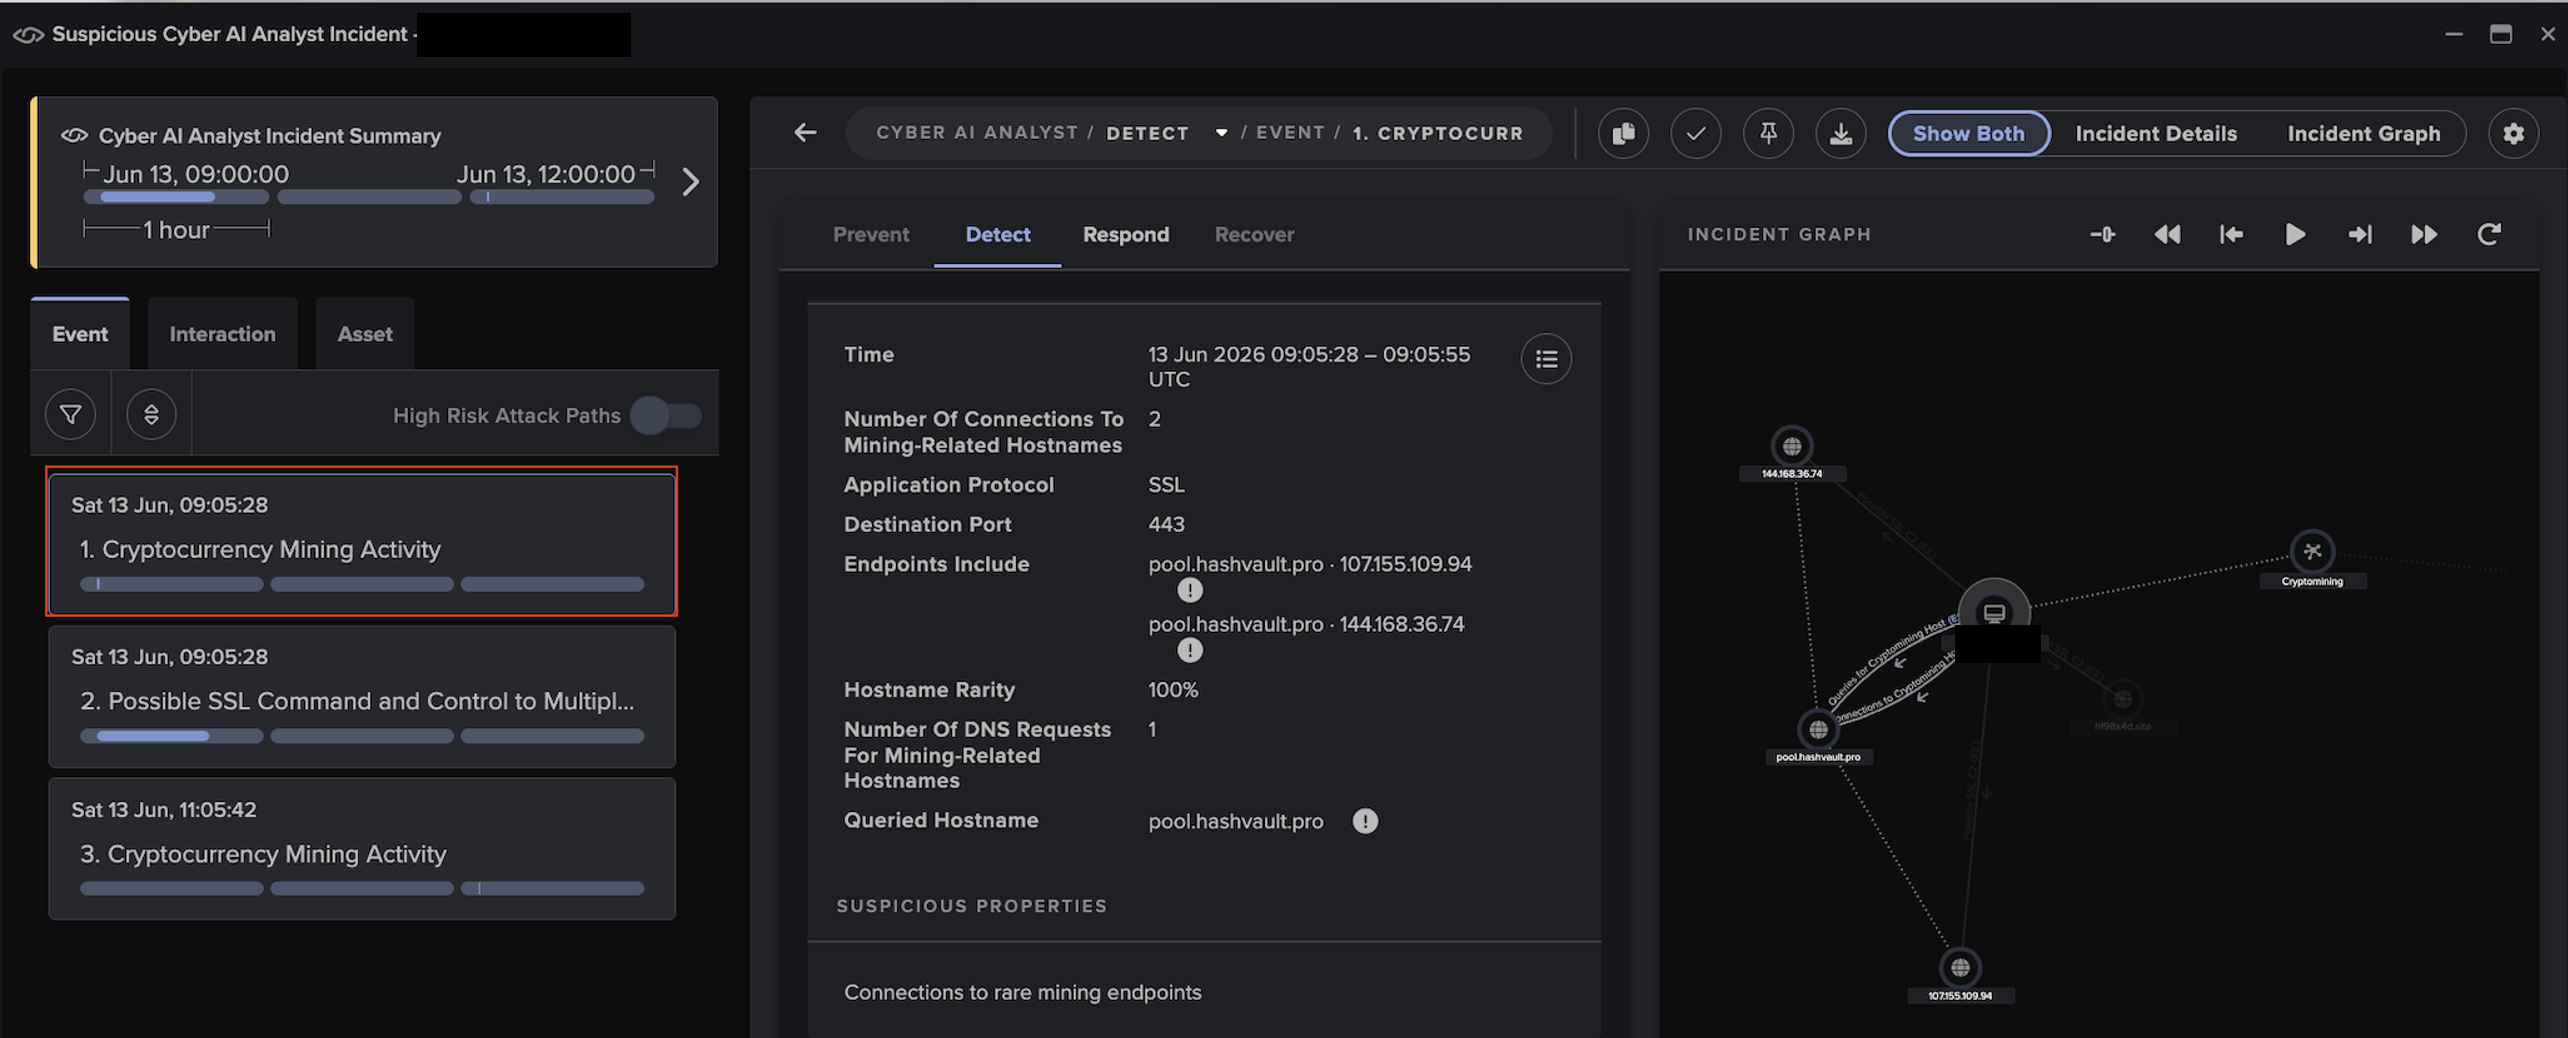
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

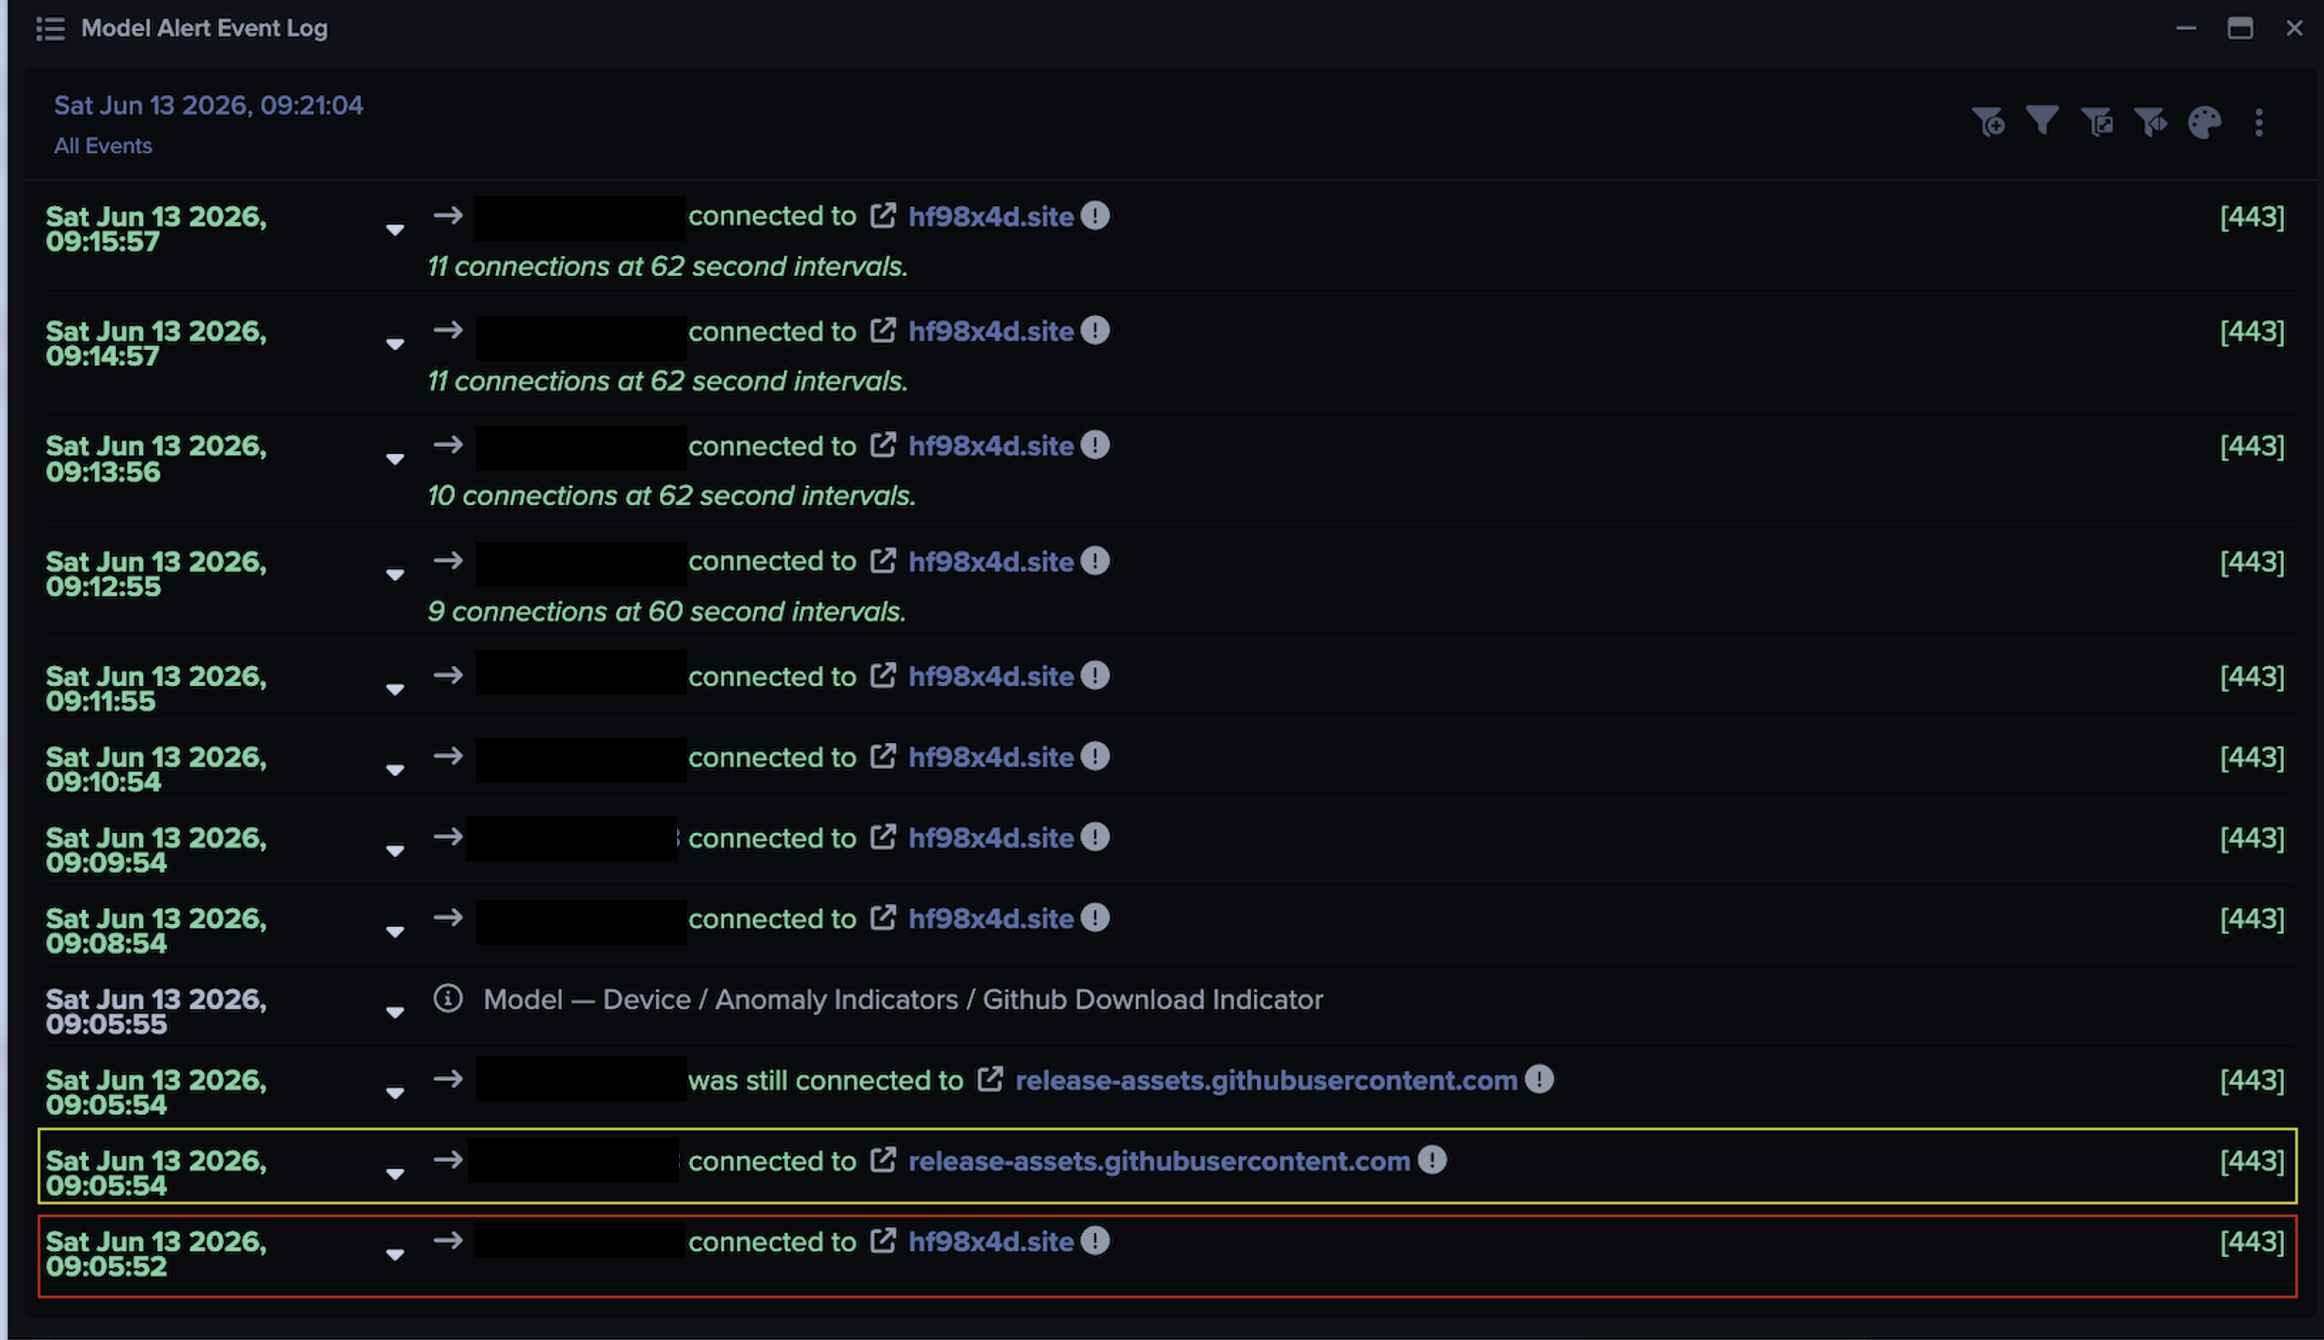
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ