Blog
/
/
June 15, 2026

Forensics or Fauxrensics: Five Core Capabilities for Cloud Forensics and Incident Response

This blog covers the five core capabilities that security teams should consider when evaluating a cloud forensics and incident response solution.
No items found.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
No items found.
people working and walking in officeDefault blog image
15
Jun 2026

The speed and scale at which new cloud resources can be spun up has resulted in uncontrolled deployments, misconfigurations, and security risks. It has had security teams racing to secure their business’ rapid migration from traditional on-premises environments to the cloud.

While many organizations have successfully extended their prevention and detection capabilities to the cloud, they are now experiencing another major gap: forensics and incident response.

Once something bad has been identified, understanding its true scope and impact is nearly impossible at times. The proliferation of cloud resources across a multitude of cloud providers, and the addition of container and serverless capabilities all add to the complexities. It’s clear that organizations need a better way to manage cloud incident response.

Security teams are looking to move past their homegrown solutions and open-source tools to incorporate real cloud forensics capabilities. However, with the increased buzz around cloud forensics, it can be challenging to decipher what is real cloud forensics, and what is “fauxrensics.”

This blog covers the five core capabilities that security teams should consider when evaluating a cloud forensics and incident response solution.

[related-resource]

1. Why is deep forensic data important in cloud incident response?

There have been many conversations among the security community about whether cloud forensics is just log analysis. The reality, however, is that cloud forensics necessitates access to a robust dataset that extends far beyond traditional log data sources.

While logs provide valuable insights, a forensics investigation demands a deeper understanding derived from multiple data sources, including disk, network, and memory, within the cloud infrastructure. Full disk analysis complements log analysis, offering crucial context for identifying the root cause and scope of an incident.

For instance, when investigating an incident involving a Kubernetes cluster running on an EC2 instance, access to bash history can provide insights into the commands executed by attackers on the affected instance, which would not be available through cloud logs alone.

Having all of the evidence in one place is also a capability that can significantly streamline investigations, unifying your evidence be it disk images, memory captures or cloud logs, into a single timeline allowing security teams to reconstruct an attacks origin, path and impact far more easily. Multi–cloud environments also require platforms that can support aggregating data from many providers and services into one place. Doing this enables more holistic investigations and reduces security blind spots.

There is also the importance of collecting data from ephemeral resources in modern cloud and containerized environments. Critical evidence can be lost in seconds as resources are constantly spinning up and down, so having the ability to capture this data before its gone can be a huge advantage to security teams, rather than having to figure out what happened after the affected service is long gone.
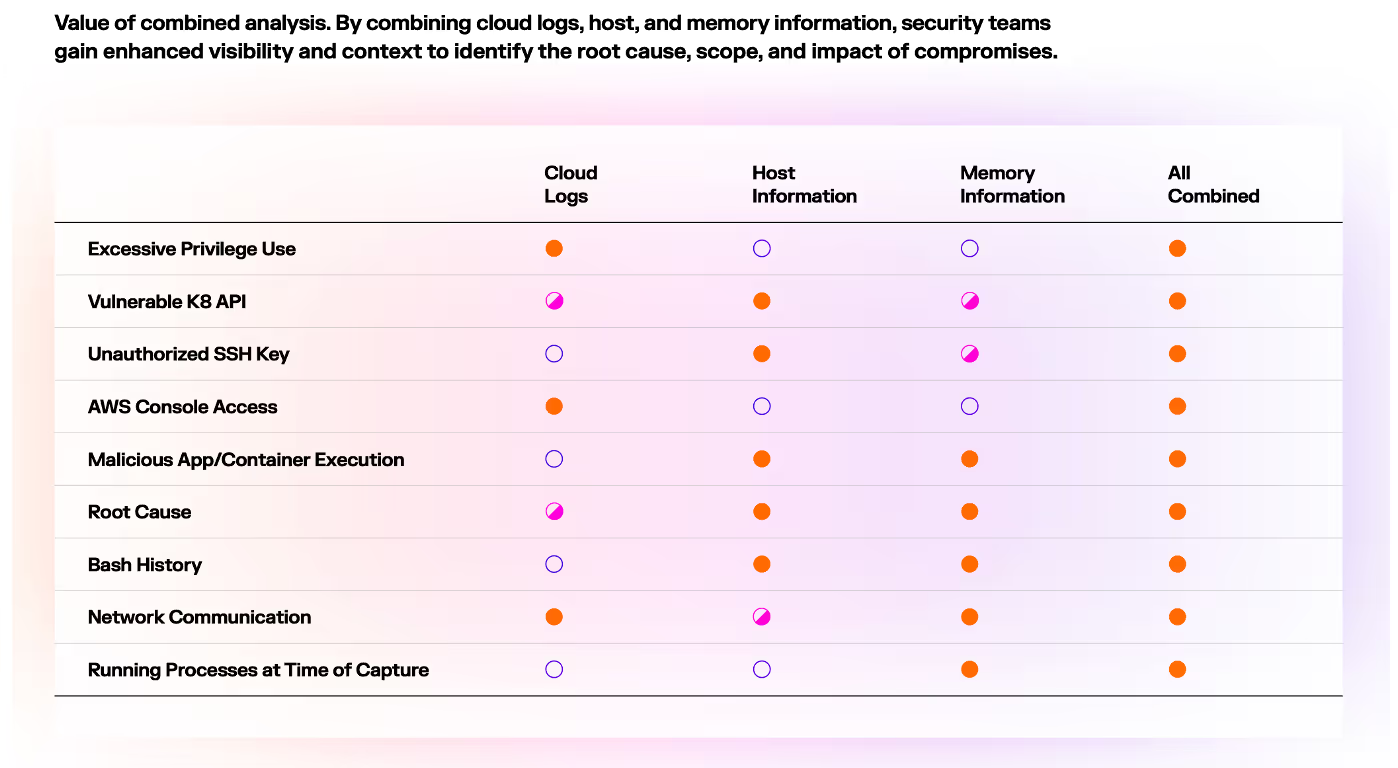
darktrace / cloud, cado, cloud logs, ost, and memory information. value of cloud combined analysis

2. Why is chain of custody important in cloudforensics?

Chain of custody is extremely critical in the context of legal proceedings and is an essential component of forensics and incident response. However, chain of custody in the cloud can be extremely complex with the number of people who have access and the rise of multi-cloud environments.

In the cloud, maintaining a reliable chain of custody becomes even more complex than it already is, due to having to account for multiple access points, service providers and third parties. Having automated evidence tracking is a must. It means that all actions are logged, from collection to storage to access. Automation also minimizes the chance of human error, reducing the risk of mistakes or gaps in evidence handling, especially in high pressure fast moving investigations.

The ability to preserve unaltered copies of forensic evidence in a secure manner is required to ensure integrity throughout an investigation. It is not just a technical concern, its a legal one, ensuring that your evidence handling is documented and time stamped allows it to stand up to court or regulatory review.

Real cloud forensics platforms should autonomously handle chain of custody in the background, recording and safeguarding evidence without human intervention.

3. How does automation improve cloud incidentresponse?

When malicious activity is detected, the speed at which security teams can determine root cause and scope is essential to reducing Mean Time to Response (MTTR).

Automated forensic data collection and system isolation ensures that evidence is collected and compromised resources are isolated at the first sign of malicious activity. This can often be before an attacker has had the change to move latterly or cover their tracks. This enables security teams to prevent potential damage and spread while a deeper-dive forensics investigation takes place. This method also ensures critical incident evidence residing in ephemeral environments is preserved in the event it is needed for an investigation. This evidence may only exist for minutes, leaving no time for a human analyst to capture it.

Cloud forensics and incident response platforms should offer the ability to natively integrate with incident detection and alerting systems and/or built-in product automation rules to trigger evidence capture and resource isolation.
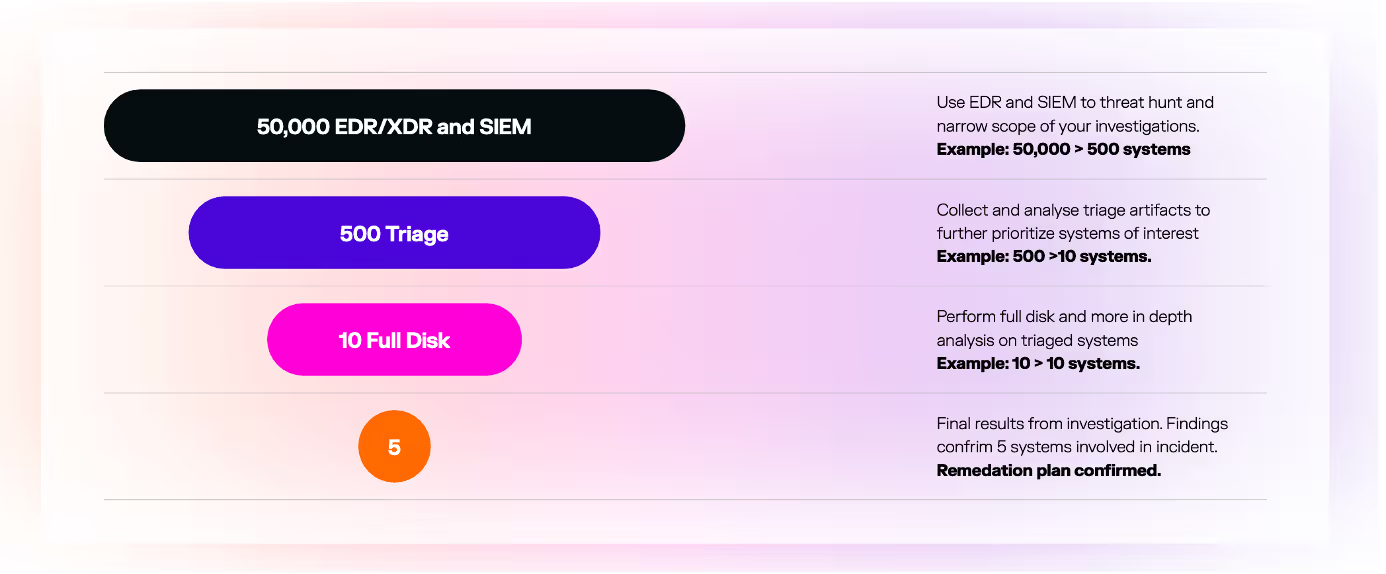
4. How do streamlined workflows improve cloudinvestigations?

Security teams shouldn’t require deep cloud or incident response knowledge to perform forensic investigations of cloud resources. They already have enough on their plates.

While traditional forensics tools and approaches have made investigation and response extremely tedious and complex, modern forensics platforms prioritize usability at their core, and leverage automation to drastically simplify the end-to-end incident response process, even when an incident spans multiple Cloud Service Providers (CSPs).

Useability is a core requirement for any modern forensics platform. Security teams should not need to have indepth knowledge of every system and resource in a given estate. Workflows, automation and guidance should make it possible for an analyst to investigate whatever resource they need to.

Unifying the workflow across multiple clouds can also save security teams a huge amount of time and resources. Investigations can often span multiple CSP’s. A good security platform should provide a single place to search, correlate and analyze evidence across all environments.

Offering features such as cross cloud support, data enrichment, a single timeline view, saved search, and faceted search can help advanced analysts achieve greater efficiency, and novice analysts are able to participate in more complex investigations.

5. Why is incident preparedness important in cloud security?

Incident response shouldn't just be reactive. Modern security teams need to regularly test their ability to acquire new evidence, triage assets and respond to threats across both new and existing resources, ensuring readiness even in the rapidly changing environments of the cloud.  Having the ability to continuously assess your incident response and forensics workflows enables you to rapidly improve your processes and identify and mitigate any gaps identified that could prevent the organization from being able to effectively respond to potential threats.

Real forensics platforms deliver features that enable security teams to prepare extensively and understand their shortcomings before they are in the heat of an incident. For example, cloud forensics platforms can provide the ability to:

  • Run readiness checks and see readiness trends over time
  • Identify and mitigate issues that could prevent rapid investigation and response
  • Ensure the correct logging, management agents, and other cloud-native tools are appropriately configured and operational
  • Ensure that data gathered during an investigation can be decrypted
  • Verify that permissions are aligned with best practices and are capable of supporting incident response efforts

How does Darktracesupport cloud forensics and response?

As cloudenvironments become increasingly dynamic and distributed, security teams needmore than alerts and visibility. Effective incident response depends on theability to rapidly collect evidence, preserve forensic artifacts, understandroot cause, and confidently determine the scope and impact of an incident.

Darktrace /Forensic Acquisition & Investigation helps organizations bring forensic rigor tomodern cloud environments by automating evidence acquisition and investigationacross cloud, containerized, serverless, SaaS, and on-premises resources. Byreducing reliance on manual collection processes and preserving evidence beforeit disappears, security teams can investigate incidents faster and with greaterconfidence.

Darktrace /Forensic Acquisition & Investigation enables organizations to move beyondfragmented investigations and adopt a more scalable approach to cloud forensicsand incident response. The result is faster access to critical evidence,improved investigation outcomes, and greater readiness when incidents occur.

[related-resource]

Need help evaluating cloud security solutions?

Discover five essential capabilities for effective cloud forensics and incident response and how AI-based security solutions can make a difference.

No items found.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
No items found.

More in this series

No items found.

Blog

/

/

November 3, 2026

From One Alert to a Wider Campaign: Uncovering Novel Threats Through Behavioral Analysis

Default blog imageDefault blog image

Key Findings

  • Darktrace’s Threat Research team is exploring a new method to identify malicious campaigns by correlating similar anomalous activity across its customer fleet.
  • The method uses unsupervised clustering to identify shared behavioral patterns across multiple customer deployments without relying on prior indicators of compromise (IoCs).
  • The approach identified shared infrastructure across dozens of customers, with activity linked to the likely POPA botnet.
  • A second cluster identified anomalous activity associated with Monero cryptocurrency mining.

‍

How does Darktrace conduct threat research?

The Darktrace Threat Research team aims to identify malicious campaign activity affecting multiple customers. By their nature, these campaigns will lead to shared behavioral patterns across multiple victims.

In this piece, we describe a method for identifying malicious campaign activity that uses this simple observation as a guiding principle. We begin by outlining a few key facts about the modern threat landscape and why behavioral detection is necessary to meet the challenges it presents. We then explore how fleet-wide behavioral detections can be leveraged using the principle above to systematically identify multi-deployment campaigns impacting the Darktrace customer fleet. Finally, we demonstrate that this research is not purely theoretical, using real examples of campaign activity detected through this novel approach.

Shifting to a behavioral-focused approach

The modern era of cyber-defense necessitates detection capabilities beyond traditional signature-based methods. Technologies such as antivirus signatures, hash-based malware identification, and IP blocklists have historically been successful in defending against known threats. However, they are easily circumvented by attackers and inherently limited in defending against the novel attack techniques that today's threat landscape is producing.

Recent breakthroughs in AI represent a transformational risk multiplier that cannot be ignored. AI systems do not merely execute existing attacks at machine speed; there are signs they can also synthesize novel tradecraft [1], increasing the likelihood that defenders will encounter attack patterns that have never previously been observed. Meanwhile vulnerability disclosures continue to accelerate. More than 48,000 CVEs were published in 2025, and published statistics to date indicate that 2026 is already on track to significantly exceed that figure [2]. While multiple factors may contribute to vulnerability discovery, AI is seen as a key factor in this rapid growth. Organizations should expect a growing proportion of malicious activity to fall outside the scope of detections that rely solely on prior knowledge of known threats.

By design, Darktrace’s behavioral and anomaly-focused detection capabilities are well-suited to this testing landscape. With a focus on detecting unknown and unexpected activity that deviates from the baseline of “normal” behavior, detection of CVE exploitation without prior knowledge of the vulnerability and before public disclosure, for example, is achievable [3][4].

Darktrace’s diverse customer base benefits from a further layer of protection: working with only deidentified alert metadata, our threat researchers hunt proactively across the fleet. Beyond the level of the individual customer, there is a second, larger vantage to be leveraged.

Darktrace data provides unique insight into the unexpected behavioral patterns that occur across its customer fleet. What can we see if we look at this fleet-wide telemetry and hunt for systematic behavioral campaigns that impact our customer base?

Correlating across the customer base

At the deployment level, Darktrace focuses on whether activity is unusual in the context of an organization's normal behavior, but as we zoom out and look at these alerts at the fleet level, the problem fundamentally changes . We are no longer seeking anomalies in largely normal data; we are seeking systematic patterns within data already known to be anomalous. An isolated behavior anomaly may be notable for a single customer; the same fingerprint across dozens is a signal of a structured campaign. Hunting for such campaigns and sharing our findings are key areas of focus for Darktrace’s Threat Research team.  In this spirit, Darktrace is  actively exploring a a new research approach that leverages deidentified alert metadata to increase campaign detection ability.

This approach is based on the premise that an expert human analyst presented with a set of alerts will identify likely related activity by assessing whether the metadata fields indicate a relationship. For example, two connections to a rare endpoint that exhibits naming structure that is likely from a single algorithm are a strong indicator, as is the use of an unusual port carrying a given protocol (e.g. port 6000 for SSL). Darktrace’s approach to campaign detection encodes this expert human judgement process through deterministic embedding functions that obtain reproducible vector representations of alert data. Unsupervised clustering is then applied to these vector representations to obtain groups of alerts that describe semantically similar alert data across multiple customers. These clusters therefore represent similar anomalous activity that has occurred across multiple customers. In other words, these clusters are candidates for malicious campaign activity.

‍

Figure 1: Layers of AI-based analysis provided through Darktrace products and cross-customer correlation.

‍

Case study 1 – unusual connections to shared underlying infrastructure

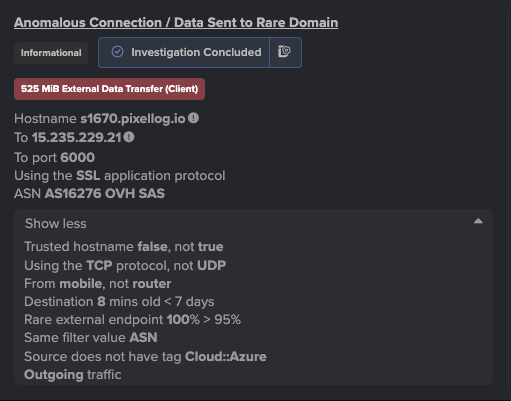
In one recent case, the clustering produced several tight groups of alerts spanning dozens of customers. Each group centered on a single domain whose subdomains were algorithmically generated (e.g. s01699, s1736, s91). Examined side by side, these clusters shared an unmistakable behavioral shape: each involved a domain with a clear naming pattern (e.g. s016841786.net-echo[.]com, s1670.pixellog[.]io, s217.pixellog[.]io) , with connections over SSL on the unusual port 6000 to servers hosted by non-mainstream providers (e.g. OVH, Hetzner, GTHost, Leaseweb), rather than generally expected content-delivery networks.

‍

Figure 2: An example model alert triggering on unusual outbound connections and data transfer to s1670.pixellog[.]io.

‍

Closer inspection revealed that the same subdomain label appeared under different domains (e.g. s1786.net-echo[.]com and s1786.pixellog[.]io). Following this lead, Darktrace’s threat researchers pivoted across the customer base and found numerous distinct subdomain labels reused under more than one registered domain. In several cases, the same label resolved to the same IP across different domains (e.g. s1704 under both pixellog[.]io and net-echo[.]com → 148.113.222[.]244; s01684 → 15.235.67[.]95), suggesting the use of ephemeral subdomain infrastructure in an attempt to avoid signature-based defense techniques.

This example demonstrates how multi-deployment data can uncover shared infrastructure that may be difficult to identify at the individual deployment level alone. In particular, the presented method facilitated this discovery by producing coherent, tight clusters of geometrically similar vector embeddings of malicious activity from large-scale fleet data, which could then be presented to a researcher for further investigation. This  activity highlighted across the Darktrace customer base was ultimately linked to likely POPA botnet activity through use of open-source intelligence (OSINT) [5].

Case Study 2 – anomalous user agent and txt URI

A second example shows the method surfacing a single, self-contained cluster. The clustering was not given any indicators to look for; instead, it grouped devices that shared an unusual combination of features. On inspection, that shared consisted of:

-      unusual user agent (tes)

-      specific request path (/md5_GIP.txt)

-      uncommon destination port (83)

-      hostname impersonating Google (matching regular expression ^www\.google\.com\.[a-zA-Z0-9]+\.fast-dns-host\.com$)

Treating these shared features as IoCs, Darktrace’s threat researchers then pivoted to an exploration across the customer base to investigate the full breadth of the campaign. This search identified further commonalities; additional domains which shared the same IP as the domain family highlighted in the cluster, as well as evidence of cryptocurrency mining on affected devices. Additional OSINT research also aligned with these findings, linking the discovered payloads and infrastructure to Monero cryptocurrency mining [6].

Conclusion

The method outlined in this blog is under active development, with ongoing technical refinement providing opportunities to further enhance its capabilities. While the capability continues to mature, this approach to threat hunting leverages the powerful vantage point of fleetwide telemetry across a diverse customer base to help protect Darktrace customers. This method allows campaigns that at the deployment level appear as isolated alerts to be seen at their true scale and spread. It enables proactive fleet-wide analysis without prior IoCs to identify campaigns impacting Darktrace customers.

This is possible because of what the method is built on: the atomic unit is the Darktrace alert, a signal that encodes years of cyber expertise, while the multi-deployment nature of the method allows organizations to indirectly benefit from findings from other networks through shared intelligence by Darktrace’s Threat Research team.

Credit to Daniel Levy (Threat Hunting Data Scientist), Paul Jennings (Principal Cyber Analyst), Emma Foulger (Global Head, Threat Operations)

Edited by Ryan Traill (Content Manager)

References

1. https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing

2. https://www.cvefind.com/en/cve-statistic-date.html

3. https://www.darktrace.com/blog/security-after-signatures-operating-in-a-world-of-pre-cve-disclosure-exploitation-collapsed-trust-boundaries-and-autonomous-systems

4. https://www.darktrace.com/blog/pre-cve-threat-detection-10-examples-identifying-malicious-activity-prior-to-public-disclosure-of-a-vulnerability

5. https://github.com/synthient/public-research/blob/main/2026/06/popa/Popa.md

6. https://www.deepwatch.com/blog/pirated-adobe-photoshop-2023-installers-lead-to-monero-cryptocurrency-mining/

Continue reading
About the author
Daniel Levy
Threat Hunting Data Scientist

Blog

/

AI

/

November 2, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

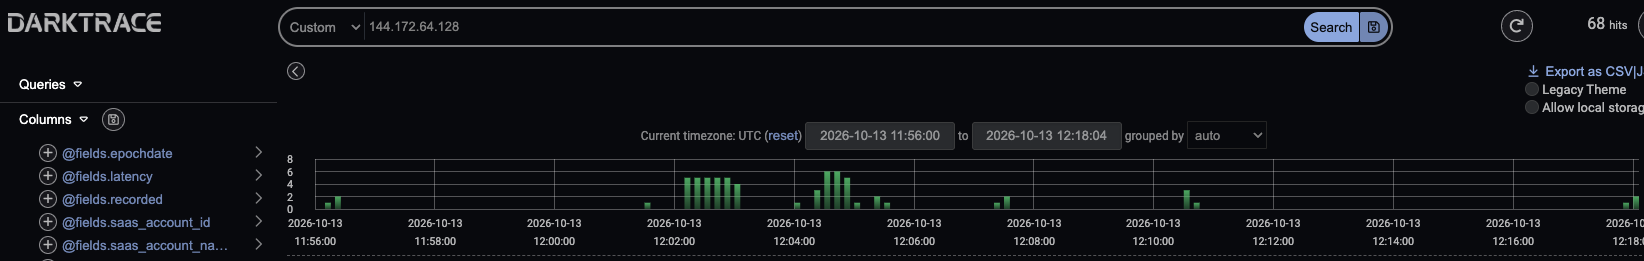
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence
Your data. Our AI.
Elevate your network security with Darktrace AI