
Blog
/
/
January 14, 2026

React2Shell Reflections: Cloud Insights, Finance Sector Impacts, and How Threat Actors Moved So Quickly

This blog breaks down how attackers rapidly weaponized the React2Shell vulnerability, with a particular focus on cloud‑native financial environments. Drawing on Darktrace’s honeypot research, it explores emerging threat actor tooling, exploitation timelines, and why behavioral‑anomaly‑led security is critical in today’s cloud landscape.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence
React2Shell Default blog image
14
Jan 2026

Introduction

Last month’s disclosure of CVE 2025-55812, known as React2Shell, provided a reminder of how quickly modern threat actors can operationalize newly disclosed vulnerabilities, particularly in cloud-hosted environments.

The vulnerability was discovered on December 3, 2025, with a patch made available on the same day. Within 30 hours of the patch, a publicly available proof-of-concept emerged that could be used to exploit any vulnerable server. This short timeline meant many systems remained unpatched when attackers began actively exploiting the vulnerability.  

Darktrace researchers rapidly deployed a new honeypot to monitor exploitation of CVE 2025-55812 in the wild.

Within two minutes of deployment, Darktrace observed opportunistic attackers exploiting this unauthenticated remote code execution flaw in React Server Components, leveraging a single crafted request to gain control of exposed Next.js servers. Exploitation quickly progressed from reconnaissance to scripted payload delivery, HTTP beaconing, and cryptomining, underscoring how automation and pre‑positioned infrastructure by threat actors now compress the window between disclosure and active exploitation to mere hours.

For cloud‑native organizations, particularly those in the financial sector, where Darktrace observed the greatest impact, React2Shell highlights the growing disconnect between patch availability and attacker timelines, increasing the likelihood that even short delays in remediation can result in real‑world compromise.

Cloud insights

In contrast to traditional enterprise networks built around layered controls, cloud architectures are often intentionally internet-accessible by default. When vulnerabilities emerge in common application frameworks such as React and Next.js, attackers face minimal friction.  No phishing campaign, no credential theft, and no lateral movement are required; only an exposed service and exploitable condition.

The activity Darktrace observed during the React2shell intrusions reflects techniques that are familiar yet highly effective in cloud-based attacks. Attackers quickly pivot from an exposed internet-facing application to abusing the underlying cloud infrastructure, using automated exploitation to deploy secondary payloads at scale and ultimately act on their objectives, whether monetizing access through cryptomining or to burying themselves deeper in the environment for sustained persistence.

Cloud Case Study

In one incident, opportunistic attackers rapidly exploited an internet-facing Azure virtual machine (VM) running a Next.js application, abusing the React/next.js vulnerability to gain remote command execution within hours of the service becoming exposed. The compromise resulted in the staged deployment of a Go-based remote access trojan (RAT), followed by a series of cryptomining payloads such as XMrig.

Initial Access

Initial access appears to have originated from abused virtual private network (VPN) infrastructure, with the source IP (146.70.192[.]180) later identified as being associated with Surfshark.
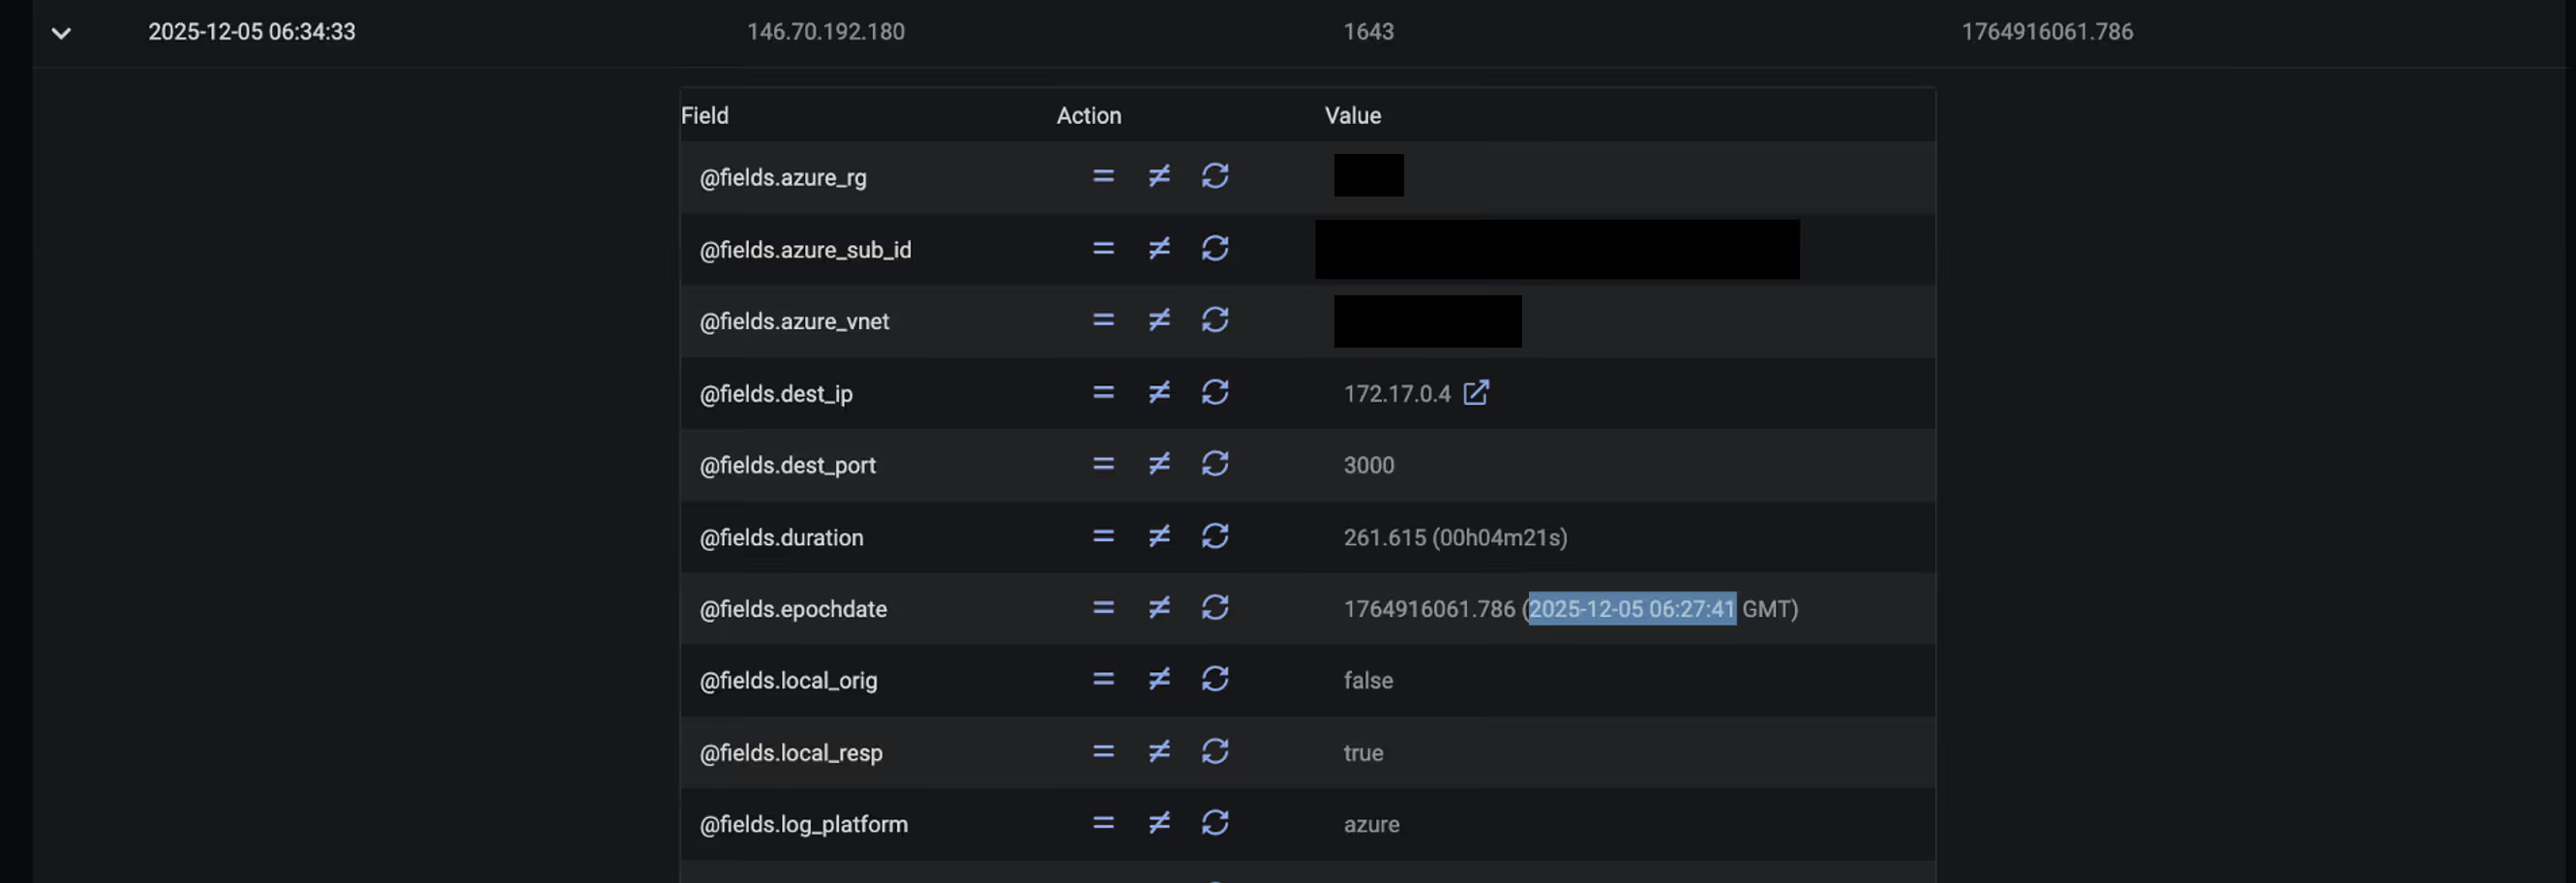
Figure 1: The IP address above is associated with VPN abuse leveraged for initial exploitation via Surfshark infrastructure.

The use of commercial VPN exit nodes reflects a wider trend of opportunistic attackers leveraging low‑cost infrastructure to gain rapid, anonymous access.

Parent process telemetry later confirmed execution originated from the Next.js server, strongly indicating application-layer compromise rather than SSH brute force, misused credentials, or management-plane abuse.

Payload execution

Shortly after successful exploitation, Darktrace identified a suspicious file and subsequent execution. One of the first payloads retrieved was a binary masquerading as “vim”, a naming convention commonly used to evade casual inspection in Linux environments. This directly ties the payload execution to the compromised Next.js application process, reinforcing the hypothesis of exploit-driven access.

Command-and-Control (C2)

Network flow logs revealed outbound connections back to the same external IP involved in the inbound activity. From a defensive perspective, this pattern is significant as web servers typically receive inbound requests, and any persistent outbound callbacks — especially to the same IP — indicate likely post-exploitation control. In this case, a C2 detection model alert was raised approximately 90 minutes after the first indicators, reflecting the time required for sufficient behavioral evidence to confirm beaconing rather than benign application traffic.

Cryptominers deployment and re-exploitation

Following successful command execution within the compromised Next.js workload, the attackers rapidly transitioned to monetization by deploying cryptomining payloads. Microsoft Defender observed a shell command designed to fetch and execute a binary named “x” via either curl or wget, ensuring successful delivery regardless of which tooling was availability on the Azure VM.

The binary was written to /home/wasiluser/dashboard/x and subsequently executed, with open-source intelligence (OSINT) enrichment strongly suggesting it was a cryptominer consistent with XMRig‑style tooling. Later the same day, additional activity revealed the host downloading a static XMRig binary directly from GitHub and placing it in a hidden cache directory (/home/wasiluser/.cache/.sys/).

The use of trusted infrastructure and legitimate open‑source tooling indicates an opportunistic approach focused on reliability and speed. The repeated deployment of cryptominers strongly suggests re‑exploitation of the same vulnerable web application rather than reliance on traditional persistence mechanisms. This behavior is characteristic of cloud‑focused attacks, where publicly exposed workloads can be repeatedly compromised at scale more easily.

Financial sector spotlight

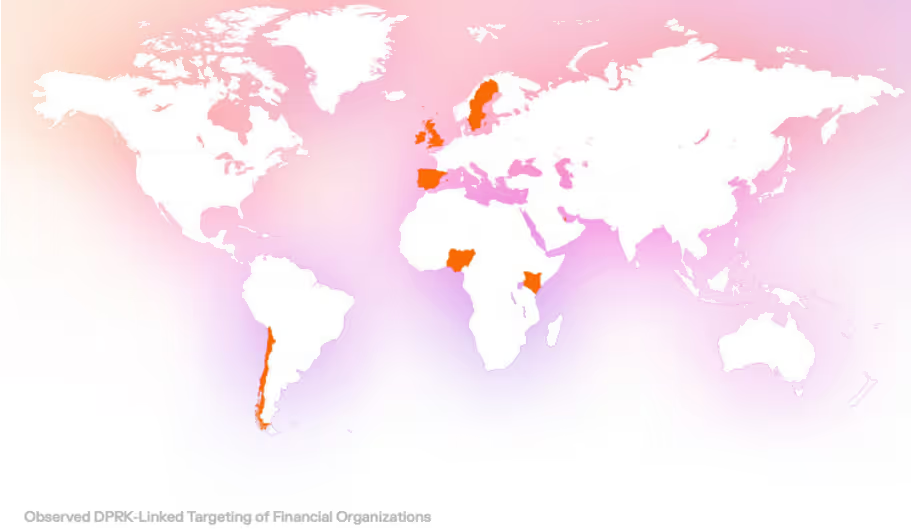
During the mass exploitation of React2Shell, Darktrace observed targeting by likely North Korean affiliated actors focused on financial organizations in the United Kingdom, Sweden, Spain, Portugal, Nigeria, Kenya, Qatar, and Chile.

The targeting of the financial sector is not unexpected, but the emergence of new Democratic People’s Republic of Korea (DPRK) tooling, including a Beavertail variant and EtherRat, a previously undocumented Linux implant, highlights the need for updated rules and signatures for organizations that rely on them.

EtherRAT uses Ethereum smart contracts for C2 resolution, polling every 500 milliseconds and employing five persistence mechanisms. It downloads its own Node.js runtime from nodejs[.]org and queries nine Ethereum RPC endpoints in parallel, selecting the majority response to determine its C2 URL. EtherRAT also overlaps with the Contagious Interview campaign, which has targeted blockchain developers since early 2025.
Read more finance‑sector insights in Darktrace’s white paper, The State of Cyber Security in the Finance Sector.

Threat actor behavior and speed

Darktrace’s honeypot was exploited just two minutes after coming online, demonstrating how automated scanning, pre-positioned infrastructure and staging, and C2 infrastructure traced back to “bulletproof” hosting reflects a mature, well‑resourced operational chain.

For financial organizations, particularly those operating cloud‑native platforms, digital asset services, or internet‑facing APIs, this activity demonstrates how rapidly geopolitical threat actors can weaponize newly disclosed vulnerabilities, turning short patching delays into strategic opportunities for long‑term access and financial gain. This underscores the need for a behavioral-anomaly-led security posture.

Credit to Nathaniel Jones (VP, Security & AI Strategy, Field CISO) and Mark Turner (Specialist Security Researcher)

Edited by Ryan Traill (Analyst Content Lead)

Appendices

Indicators of Compromise (IoCs)

146.70.192[.]180 – IP Address – Endpoint Associated with Surfshark

References

https://www.darktrace.com/resources/the-state-of-cybersecurity-in-the-finance-sector

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence

More in this series

No items found.

Blog

/

/

September 4, 2026

Darktrace Advances Incident Investigation and AI-Agent Security with OpenAI Daybreak Models

Default blog imageDefault blog image

Earlier this year, Darktrace joined OpenAI’s Daybreak Defense Network to explore how their cyber capabilities can be integrated within Darktrace products and services to transform how security teams move from signal to action.

At the heart of this work is Darktrace's behavioral understanding of customer environments and identification of complex security incidents, combined with OpenAI models that can add context to help explain why an incident matters and its potential impact on the business. By bringing these capabilities into defensive workflows security teams already use, the goal is to give defenders not just greater visibility, but the context and guidance they need to act with confidence.

Since joining the program, we've been working with OpenAI to explore how these capabilities can address specific security challenges for defenders.

The problem we're solving

Attackers continue to change how they operate, including by using AI to increase the speed and scale of some techniques. Security teams are already managing a large volume of alerts, and the question isn't just what's happening, but how it could affect the organization. Even when an incident is fully investigated and correlated, technical severity alone doesn't tell a security team how much it actually matters to the business. That same challenge extends to internal AI adoption. As organizations adopt more AI systems and agents, security teams need visibility into their behavior, access and activity, along with the broader business context needed to identify and investigate potential risk.

Darktrace's Adaptive AI™ builds a detailed, organization-specific picture of what's normal for each environment, and uses that picture to investigate threats and identify complex security activity across domains. OpenAI's models can build on Darktrace's correlated, technically prioritized incidents by adding context that can help defenders understand what may be at stake.

What we're building

Our work is focused on two areas: supporting security investigation and response, and helping defenders identify risky behavior across enterprise AI systems and agents.

The first aligns Darktrace's behavioral understanding with OpenAI models to support  security investigation and prioritization. Darktrace's Adaptive AI continuously learns the unique patterns of normal behavior within each customer it protects, creating a deep, organization-specific understanding of its digital estate. When unusual activity emerges, OpenAI's models can draw on that context to help analysts investigate the incident, understand its significance and assess potential business consequences — reducing the need to manually assemble context from fragmented signals.

Second, we are exploring how these capabilities can support AI-agent and runtime security through Darktrace / SECURE AI™. OpenAI’s Daybreak models can build on the detections and visibility Darktrace / SECURE AI provides, connecting signals across a customer's environment and help defenders identify potentially risky behavior involving AI systems and agents. Activity that might appear isolated can instead be connected with related signals, helping defenders investigate the broader context and determine appropriate remediation.

Darktrace brings deep cybersecurity expertise, an evolving understanding of each customer's environment, and AI-driven identification of threats across the digital estate. Through the Daybreak Defense Network, Darktrace is exploring how OpenAI models can augment those capabilities in defensive security workflows — supporting incident investigation and response and improving visibility into AI-agent and runtime risk.

These capabilities are still in development, and we're excited to continue building on this work.

To learn more about how Darktrace continues to innovate to meet today's most pressing security challenges, register for our upcoming launch broadcast here.

Continue reading
About the author

Blog

/

OT

/

September 4, 2026

Botnet Behind the Camera: Mirai Katana Activity on a Video Recording Device

Default blog imageDefault blog image

Key takeaways

  • Darktrace identified a camera device infected with the Mirai/Katana botnet in a sports-sector customer environment, showing how exposed IoT devices can become active participants in wider attack chains.
  • The compromise involved suspicious Wget behavior, file downloads from rare external IPs, unusual incoming HTTP connections to video recorder management interfaces, and large outbound data transfers to infrastructure associated with botnet activity.
  • The incident highlights the importance of extending visibility and response beyond traditional endpoints, as unmanaged or overlooked connected devices can be exploited for command-and-control, malware delivery, and data exfiltration.

Mirai and the Katana variant

Mirai is a botnet that first emerged in August 2016 and is well known for launching large-scale distributed-denial-of-service (DDoS) attacks, typically targeting exposed Internet of Things (IoT) devices. It identifies vulnerable IoT devices ,often by abusing default credentials or exposed services, and recruiting them into a remotely controlled botnet that can be used in DDoS campaigns [1].

Katana, one of the many variants that arose after Mirai’s source code was released publicly, was first observed in late 2020 and has been seen using more advanced capabilities, including custom command-and-control (C2), persistence mechanisms, and DDoS functionality [2].

In March 2026, research from the Nokia Deepfield Emergency Response Team (ERT) identified Katana as a Mirai-derived DDoS botnet targeting Android-based TV set-top boxes through exposed Android Debug Bridge (ADB) access.  Observed capabilities included custom C2, runtime domain rotation, multiple DDoS methods, and an on-device compiled kernel rootkit used for persistence and stealth [3].

Darktrace’s detection of Mirai Botnet activity on a camera device

In early 2026, Darktrace identified a Network/Digital Video Recorder (NVR/DVR) on the network of a sports-sector customer that had been infected with the Mirai Katana botnet and subsequently used to exfiltrate data from the customer’s environment. Seemingly related follow-up activity was observed on the same device several months later.

In both instances, the Darktrace Security Operations Centre (SOC) alerted the customer as part of the Managed Threat Detection (MTD) service. However, as Darktrace’s Autonomous Response capability was not fully enabled on the affected device, Darktrace was unable to proactively block the suspicious activity or prevent the compromise from continuing and recurring.

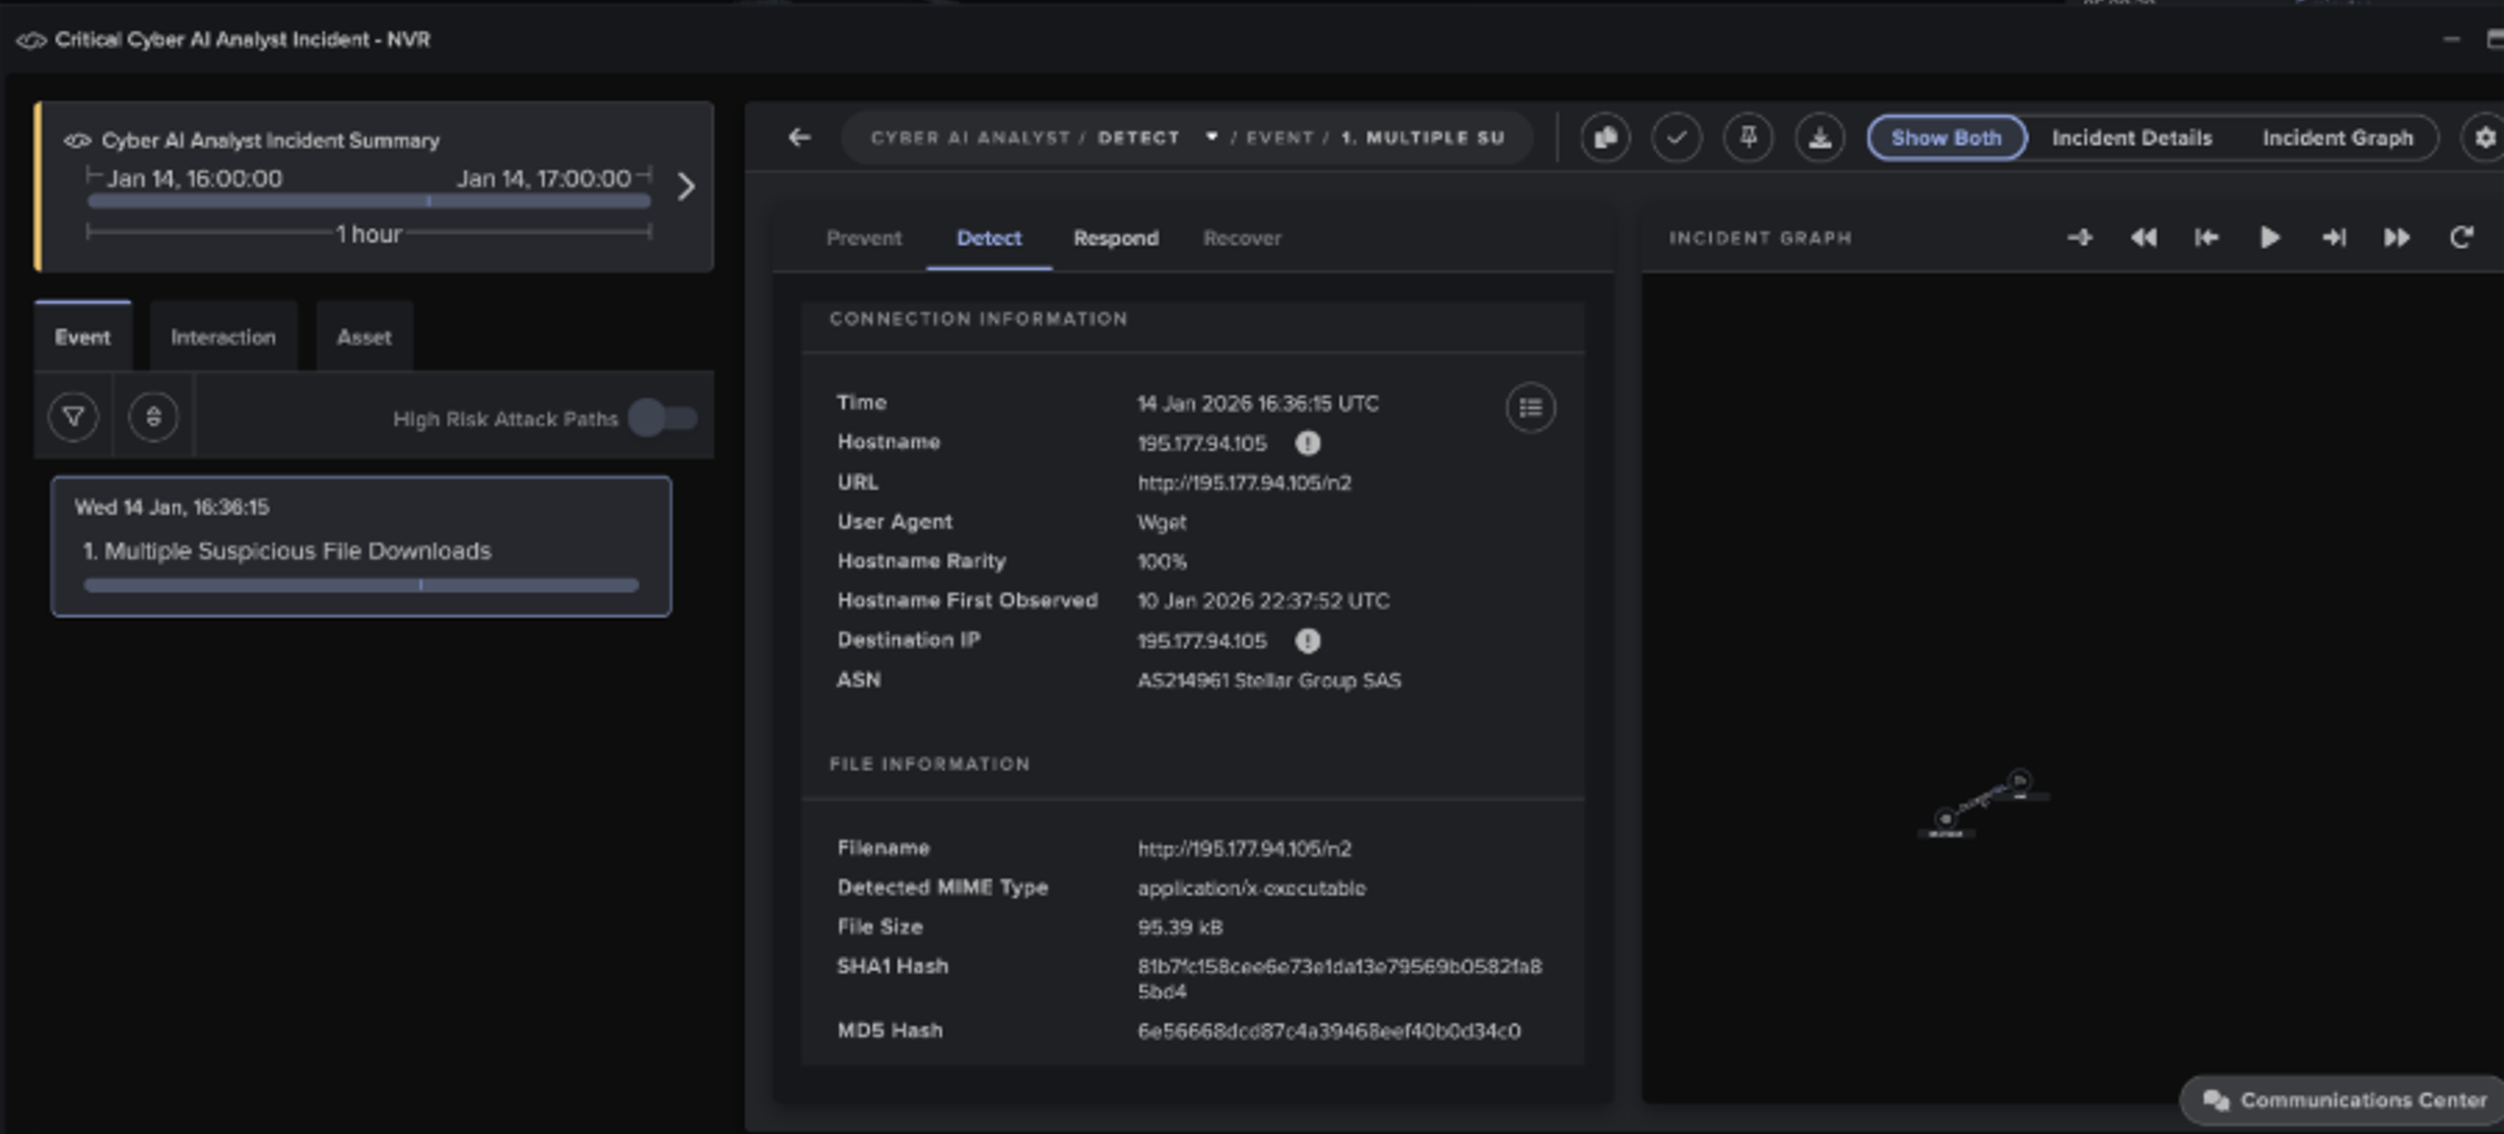
The initial compromise appears to have occurred when the affected device was seen using Wget to download Linux-based Executable and Linkable Format (ELF) files from a rare external IP, 195.177.94[.]105, which had not previously been observed in the customer’s network. Further analysis downloaded file hashes identified files related to the Mirai botnet.

Figure 1: Darktrace’s Real-Time AI Analyst investigation into the unusual outbound connection where the ELF files were downloaded.

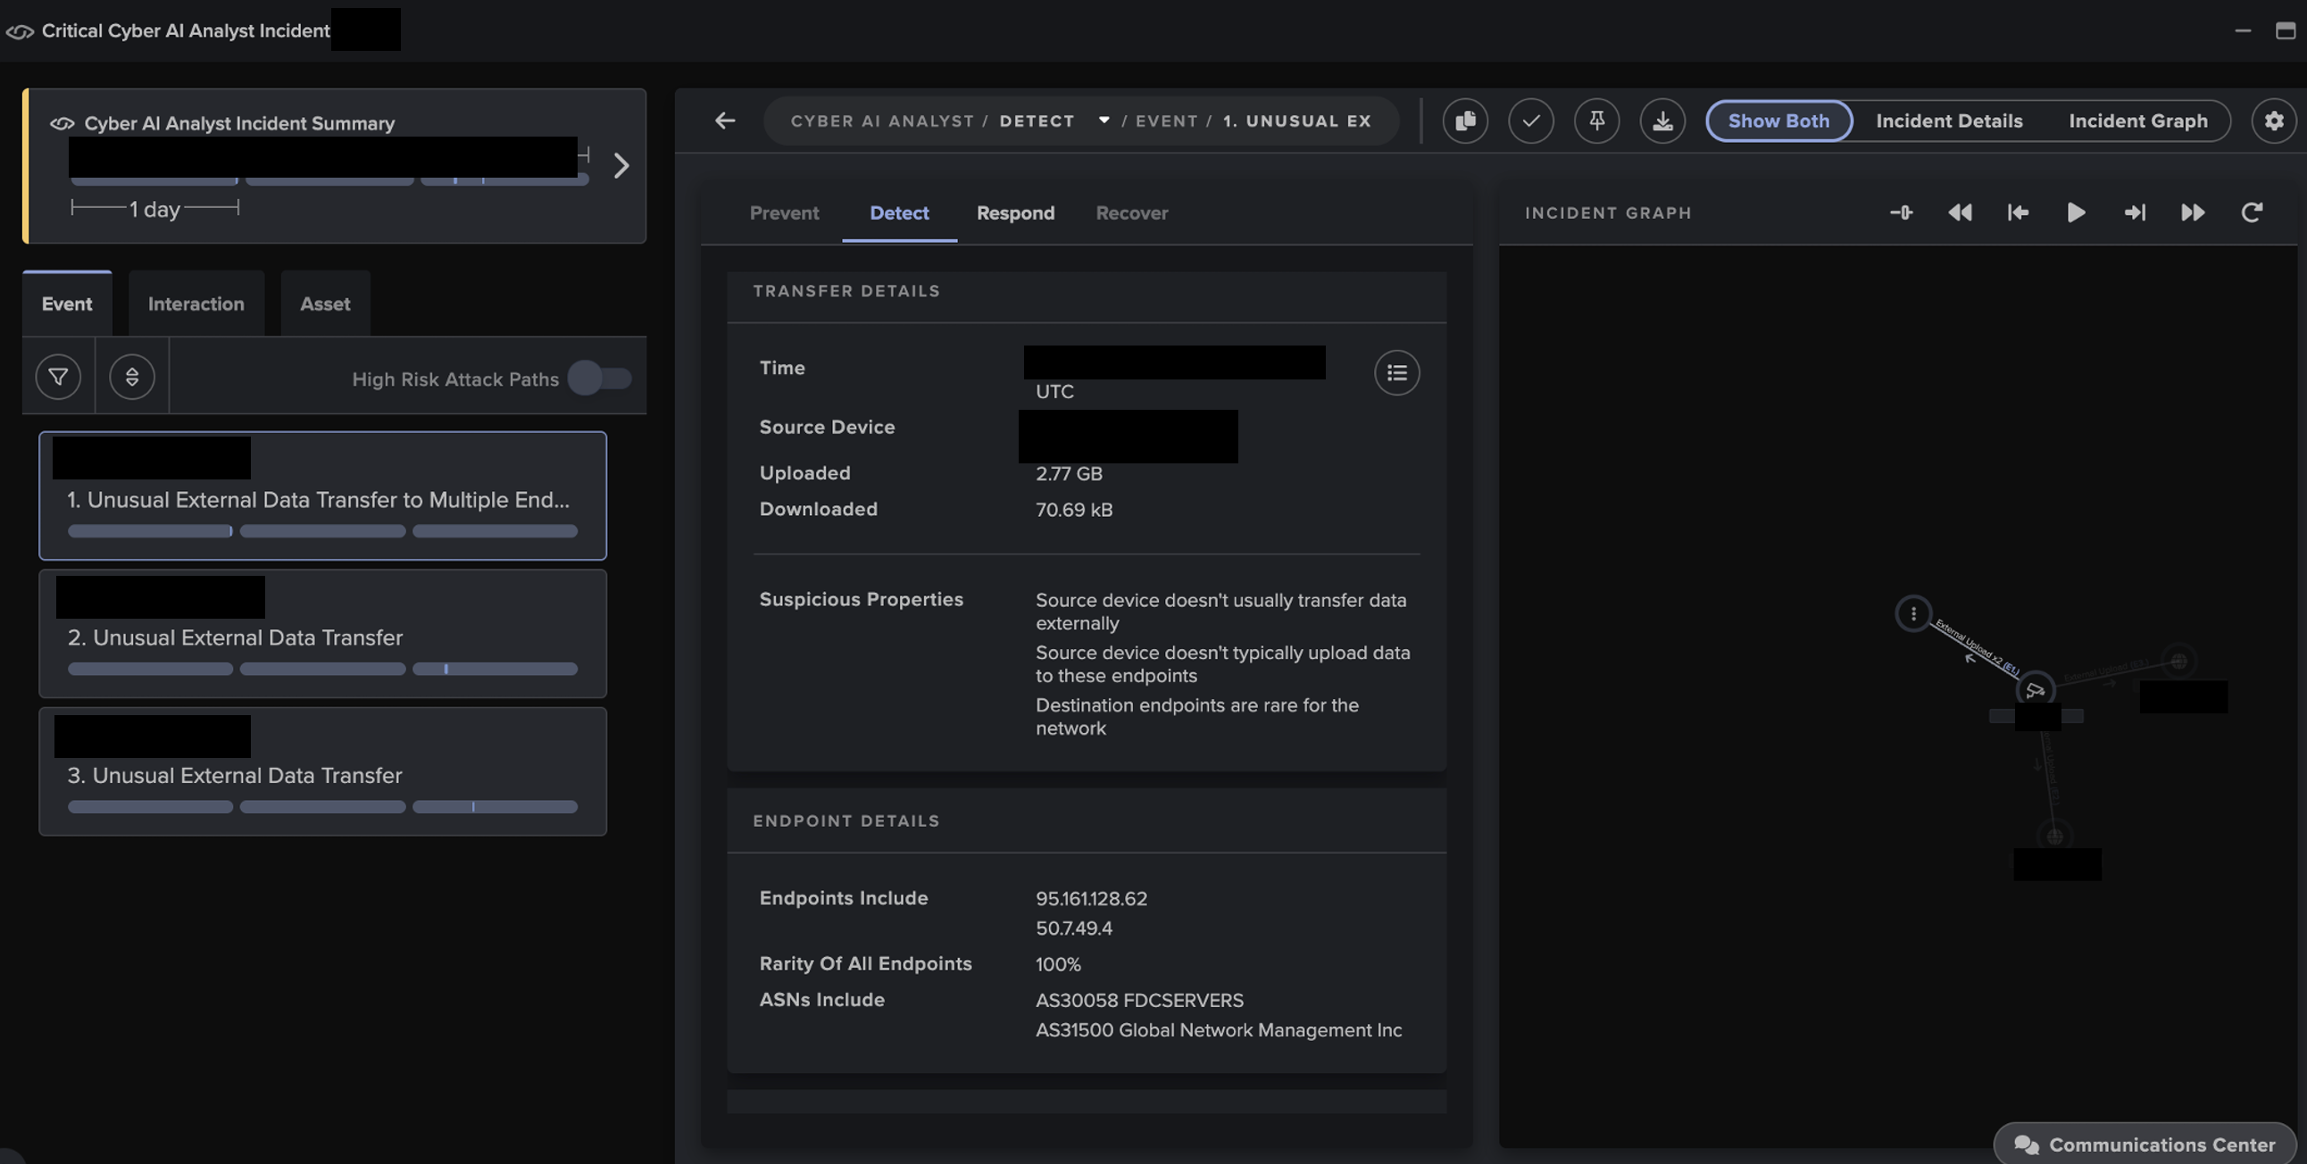
Within a few hours, Darktrace detected the device uploading close to 3GB of data to another external IP, 50.7.49[.]4:3017 (ASN AS30058 FDCSERVERS), suggesting that the activity was likely routed via a virtual private server (VPS) hosted by FDC Servers [2]. Attackers often abuse VPS infrastructure from legitimate cloud providers to blend in with legitimate traffic and evade IP reputation and geolocation-based detections.

Figure 2:  Darktrace’s detection of the unusual data upload activity by the affected camera device.

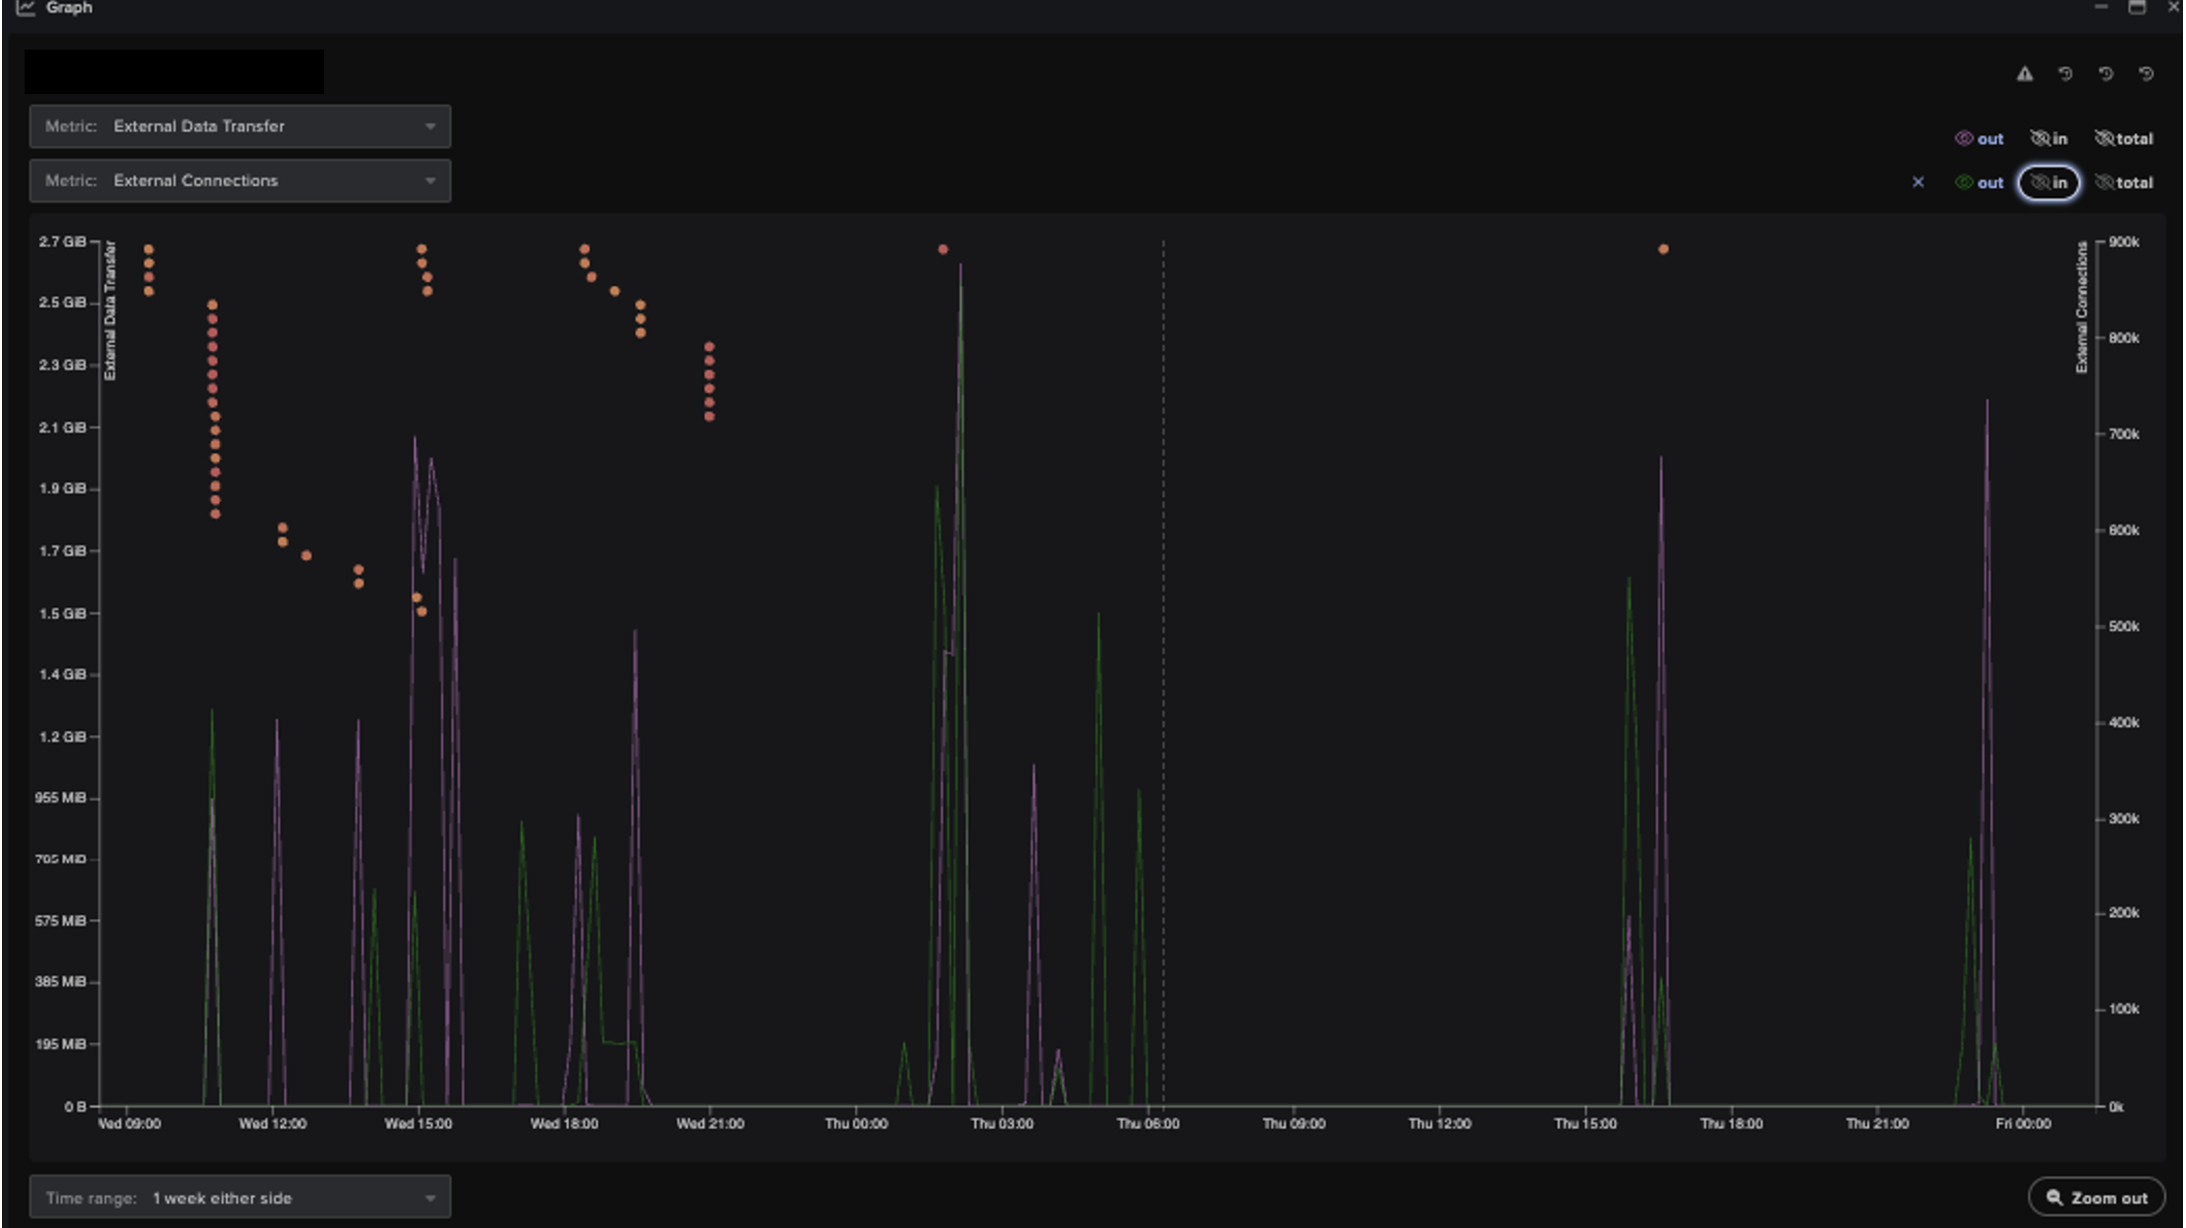
Darktrace continued to observe similar data transfers to multiple rare endpoints  including 171.225.223[.]53, 95.161.128[.]62, 61.7.209[.]88, 95.161.128[.]62, which have been linked to Mirai by open-source intelligence (OSINT).

Figure 3: Darktrace’s detection of spikes in unusual external data transfer activity from the camera device.

Exploitation continued

Several months later, Darktrace identified the same exfiltration pattern on the device again, this time with stronger indications of associations with Mirai Katana botnet infection.

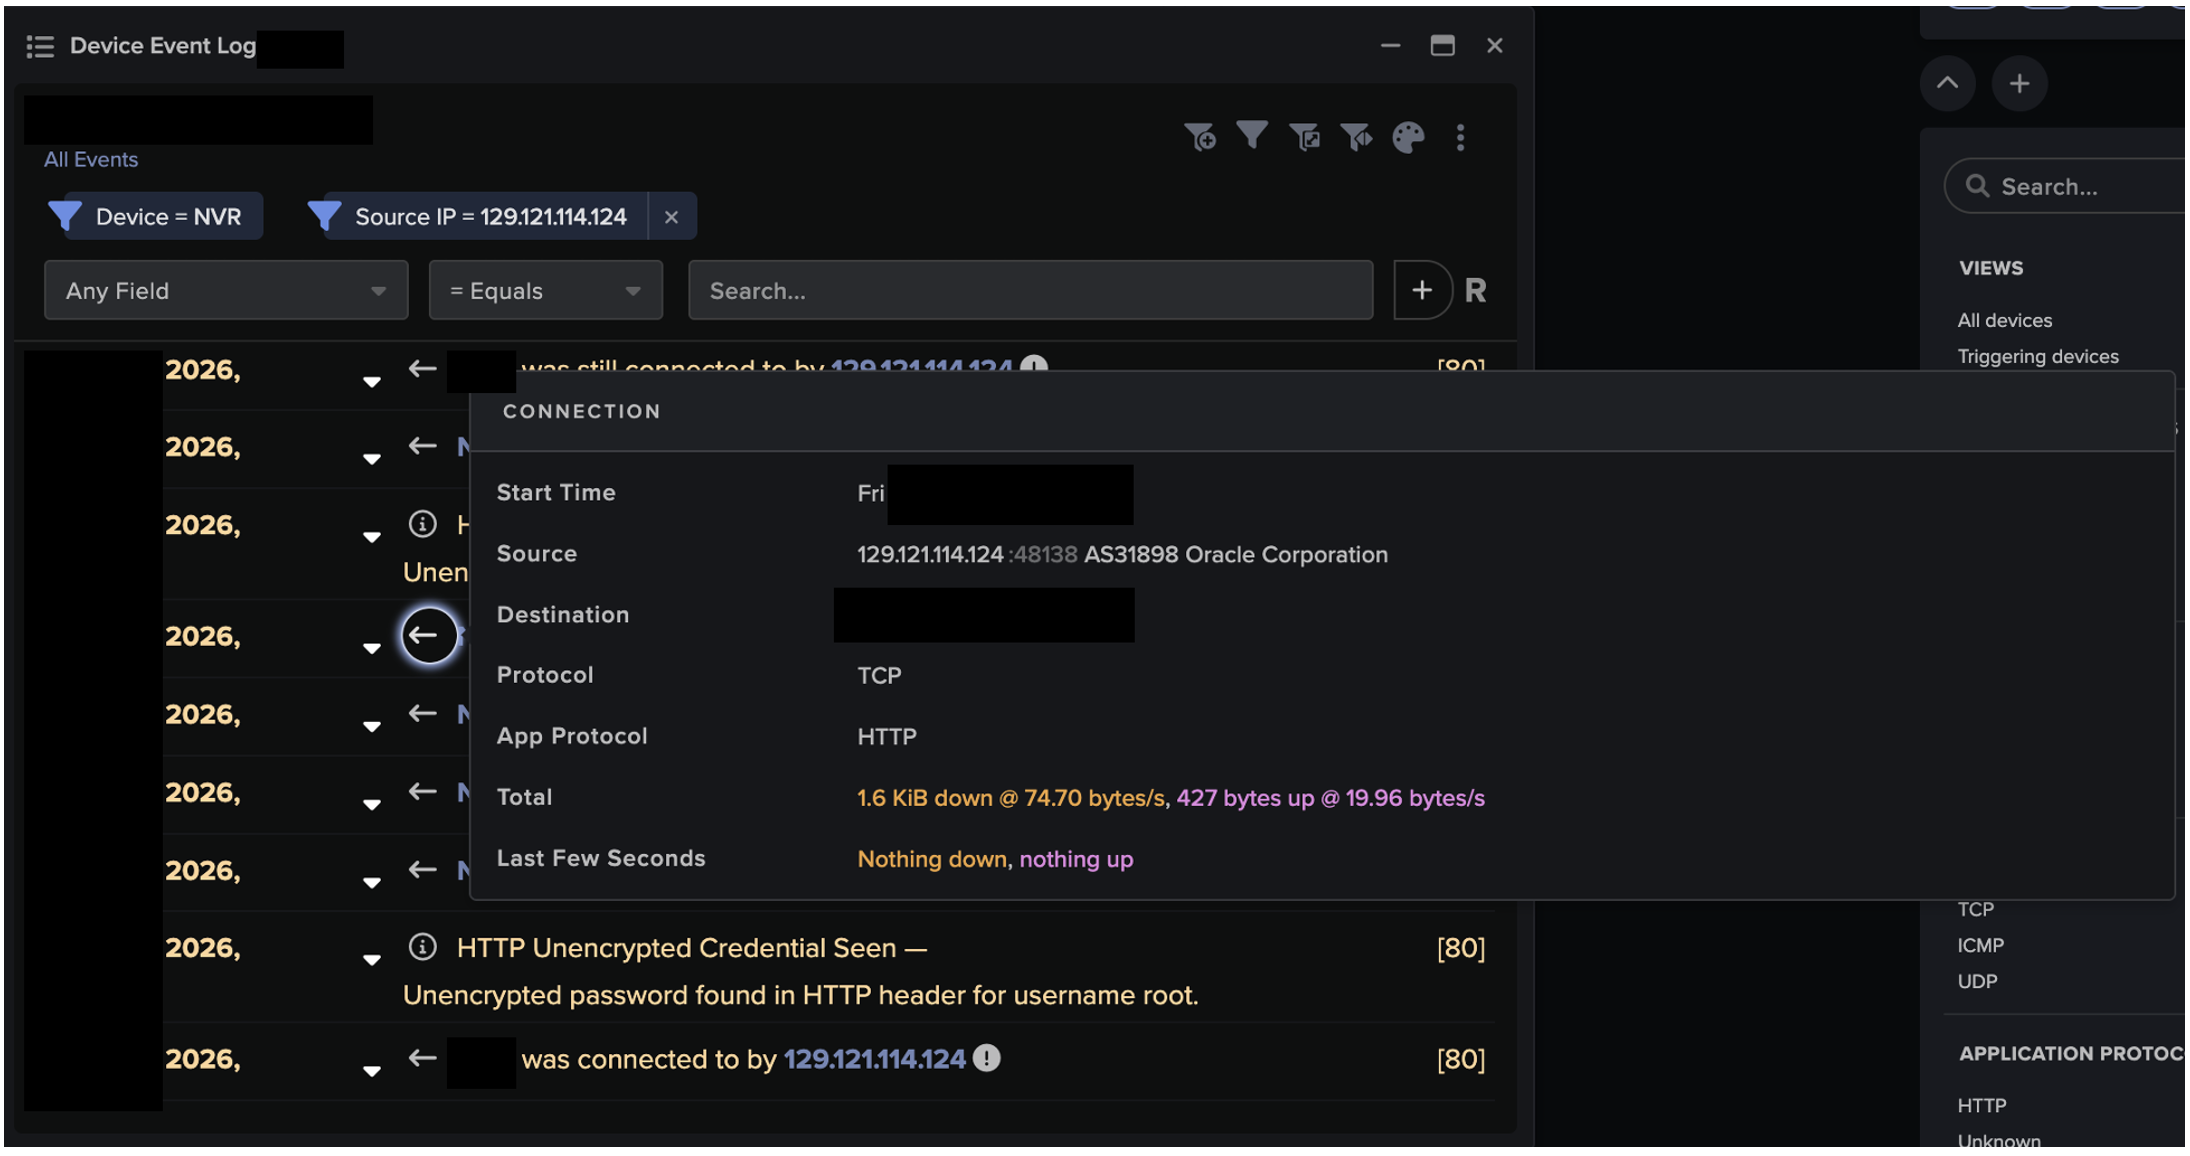
The device received incoming HTTP connections from 129.121.114[.]124, an external IP known to be associated with the Katana botnet IP [3]. The connections targeted the ‘/dvr/cmd’ path using the root username and user agent Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/42.0.2311.135 Safari/537.36 Edge/12.246.

The ‘/dvr/cmd’ path appears to be associated with the affected device’s web management functionality. This API endpoint has historically been targeted by Mirai and other IoT botnets through the exploitation of critical command injection vulnerabilities and automated botnet exploitation [4].

Figure 4: Darktrace’s  detection of HTTP connectivity from the external IP associated with Mirai Katana Botnet.

A few days later, Darktrace observed the Wget utility being used to download ELF files, including “/lil”,  from the IP 129.121.114[.]124. OSINT reporting has since associated this IP address with the Mirai Katana botnet. Notably, the IP observed earlier in the year, 195.177.94[.]105, had also hosted a file named “lil”, indicating a link between the observed activity.

Over the following days, the device received a sudden spike in connections from multiple rare external endpoints, suggesting a possible successful brute force attack. Darktrace also observed the device exfiltrating just under 4GB of data to another Mirai-associated IP address,  66.92.198[.]194, over ports 3344, 954922, and 80. Finally, the device was seen uploading data to the Mirai botnet IP 5.175.249[.]53 over port138 and exhibited an increase in UDP connections to 34.18.28[.]10 over port 9068.

Following both file download events, Darktrace identified spikes in external data transfers and connection attempts to rare destinations. While Darktrace’s Threat Research team could not confirm with high confidence that this to activity was directly associated with Mirai, it may indicate that Mirai Katana includes data exfiltration functionality.

Darktrace’s threat researchers also identified an internet-facing NTP server belonging to a separate customer receiving incoming connection attempts from the same initially observed IP, 195.177.94[.]105,over the port 123. This suggests that Mirai Katana may not exclusively target IoT devices.

Conclusion

This case demonstrates how threat actors can exploit overlooked IoT and OT devices to support broader malicious objectives. Here, a camera device infected with a botnet was used to exfiltrate data from the customer's environment, showing how peripheral assets can become active participants in an attack chain.

This case also reinforces a challenge many organizations face today: extending security visibility beyond traditional endpoints and servers. Cameras, sensors, and other connected devices often operate with limited monitoring and may fall outside established security processes, despite maintaining network connectivity and access to potentially sensitive environments. This is particularly relevant in the sports sector, where growing reliance on connected cameras, smart stadium technologies, and other IoT devices continues to expand the attack surface, as highlighted in Darktrace's Sports Sector Threat Report.

As botnets like Kata and Mirai continue to evolve, defenders need visibility across unmanaged IoT and edge devices, as well as security solutions that can recognize subtle deviations in device behavior that may indicate an emerging compromise.

Credit to Parvatha Ananthakannan (Cyber Analyst), Signe Zaharka (Principal Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

·      Anomalous File / EXE from Rare External Location

·      Anomalous File / Multiple EXE from Rare External Locations

·      Device / Initial Attack Chain Activity

·      Unusual Activity / Unusual External Data to New Endpoint

·      Anomalous Connection / Data Sent to Rare Domain

·      Unusual Activity / Enhanced Unusual External Data Transfer

·      Anomalous Connection / Uncommon 1 GiB Outbound

·      Device / Significant UDP Increase

·      Anomalous Connection / Low and Slow Exfiltration to IP

·      Compromise / Large Number of Suspicious Failed Connections

·      Compromise / Large Number of Suspicious Successful Connections

·      Unusual Activity / Unusual External Activity

·      Compliance / SSH to Rare External Destination

·      Unusual Activity / Unusual DNS

·      Device / External Network Scan

·      Device / Suspicious DNS Activity

·      Device / Large Number of Model Alerts

List of Indicators of Compromise (IoCs)

Indicator of Compromise Type Description
195.177.94[.]105 IP C2 endpoint
50.7.49[.]4:30171 IP Possible C2 endpoint
129.121.114[.]124 IP C2 endpoint
hxxp://195.177.94[.]105/n3 URL Likely C2 endpoint
hxxp://195.177.94[.]105/n2 URL Likely C2 endpoint
hxxp://129.121.114[.]124/lil URL Likely C2 endpoint
hxxp://129.121.114[.]124/HHn URL Possible C2 endpoint
hxxp://129.121.114[.]124/JFc URL Possible C2 endpoint
hxxp://129.121.114[.]124/jum URL Likely C2 endpoint
hxxp://129.121.114[.]124/OaSf URL Likely C2 endpoint
hxxp://129.121.114[.]124/OPWg URL Possible C2 endpoint
hxxp://129.121.114[.]124/vHwK URL Possible C2 endpoint
hxxp://129.121.114[.]124/VLv URL Possible C2 endpoint
hxxp://129.121.114[.]124/WbJ URL Possible C2 endpoint
hxxp://129.121.114[.]124/zkR URL Possible C2 endpoint
Ab17883ae4c3bc6afa18c439166eeeb4b03186e3093d984e3a95f573e0fcb7d8 SHA-256 Mirai payload
3d587e809dac49d34a3f717e072fd0aebe5e71db63333e45c81577d6b4266f87 SHA-256 Mirai payload
Bf6e81733a7e209d3dce80d15bf3c5d300752d961fae6b45d90c9bbe7f8c89a2 SHA-256 Possible payload
f25488303813ab1ec0eaa71562938601aac185e8aaf93adb84522557f7cf4dd6 SHA-256 Possible payload
0cb4ff6b71f4423184bfa35c34e9090297637208b0e30205d4b224e56abde2ef SHA-256 Possible payload
19c24cbeaf06b2e7697083f33a85521a9315105c784691bde7420fde4cc69410 SHA-256 Likely Mirai payload
1e74f734fff8df91f4f7172d0de10c421eca78aeb800e8a48e16bc5dbde5d20e SHA-256 Possible payload
6e71f7763d1f29d5712106ebb122e281c32787540aa2342b0fe5351d585d18d7 SHA-256 Possible payload
71f4ff7cdb6d6a7d2673c543c5d2535093afbd707b20a5b9ddf735466c1105c1 SHA-256 Possible payload
76db7ee73ebf15e48a3cb24a074d92248671ef2c6ed3bc3e708377341fb7674d SHA-256 Possible payload
da87a65f7beb438e61f0b61964fed8aa305a380f569042f84c55eca8fa7929b8 SHA-256 Possible payload
e15809eb6ba66477175270d62cfa53e4bf278595f69938708c81c4bc457930fe SHA-256 Mirai payload

MITRE ATT&CK Mapping

Tactic Technique ID Technique / Sub-technique
Initial Access T1659 Content Injection
T1189 Drive-by Compromise
Exfiltration T1041 Exfiltration Over C2 Channel
T1048.003 Exfiltration Over Unencrypted Non-C2 Protocol
Command and Control T1105 Ingress Tool Transfer
T1095 Non-Application Layer Protocol
T1571 Non-Standard Port
Reconnaissance T1595.001 Scanning IP Blocks
Continue reading
About the author
Parvatha Ananthakannan
Cyber Analyst
Your data. Our AI.
Elevate your network security with Darktrace AI