Blog
/
OT
/
May 20, 2025

Adapting to new USCG cybersecurity mandates: Darktrace for ports and maritime systems

Darktrace uses AI-led OT, IoT, and IT Network Security to help secure maritime transportation systems. This blog describes some of the new mandated requirements by the USCG and demonstrates Darktrace’s security capabilities.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Daniel Simonds
Director of Operational Technology
Cargo ships at a portDefault blog image
20
May 2025

What is the Marine Transportation System (MTS)?

Marine Transportation Systems (MTS) play a substantial roll in U.S. commerce, military readiness, and economic security. Defined as a critical national infrastructure, the MTS encompasses all aspects of maritime transportation from ships and ports to the inland waterways and the rail and roadways that connect them.

MTS interconnected systems include:

  • Waterways: Coastal and inland rivers, shipping channels, and harbors
  • Ports: Terminals, piers, and facilities where cargo and passengers are transferred
  • Vessels: Commercial ships, barges, ferries, and support craft
  • Intermodal Connections: Railroads, highways, and logistics hubs that tie maritime transport into national and global supply chains

The Coast Guard plays a central role in ensuring the safety, security, and efficiency of the MTS, handling over $5.4 trillion in annual economic activity. As digital systems increasingly support operations across the MTS, from crane control to cargo tracking, cybersecurity has become essential to protecting this lifeline of U.S. trade and infrastructure.

Maritime Transportation Systems also enable international trade, making them prime targets for cyber threats from ransomware gangs to nation-state actors.

To defend against growing threats, the United States Coast Guard (USCG) has moved from encouraging cybersecurity best practices to enforcing them, culminating in a new mandate that goes into effect on July 16, 2025. These regulations aim to secure the digital backbone of the maritime industry.

Why maritime ports are at risk

Modern ports are a blend of legacy and modern OT, IoT, and IT digitally connected technologies that enable crane operations, container tracking, terminal storage, logistics, and remote maintenance.

Many of these systems were never designed with cybersecurity in mind, making them vulnerable to lateral movement and disruptive ransomware attack spillover.

The convergence of business IT networks and operational infrastructure further expands the attack surface, especially with the rise of cloud adoption and unmanaged IoT and IIoT devices.

Cyber incidents in recent years have demonstrated how ransomware or malicious activity can halt crane operations, disrupt logistics, and compromise safety at scale threatening not only port operations, but national security and economic stability.

Relevant cyber-attacks on maritime ports

Maersk & Port of Los Angeles (2017 – NotPetya):
A ransomware attack crippled A.P. Moller-Maersk, the world’s largest shipping company. Operations at 17 ports, including the Port of Los Angeles, were halted due to system outages, causing weeks of logistical chaos.

Port of San Diego (2018 – Ransomware Attack):
A ransomware attack targeted the Port of San Diego, disrupting internal IT systems including public records, business services, and dockside cargo operations. While marine traffic was unaffected, commercial activity slowed significantly during recovery.

Port of Houston (2021 – Nation-State Intrusion):
A suspected nation-state actor exploited a known vulnerability in a Port of Houston web application to gain access to its network. While the attack was reportedly thwarted, it triggered a federal investigation and highlighted the vulnerability of maritime systems.

Jawaharlal Nehru Port Trust, India (2022 – Ransomware Incident):
India’s largest container port experienced disruptions due to a ransomware attack affecting operations and logistics systems. Container handling and cargo movement slowed as IT systems were taken offline during recovery efforts.

A regulatory shift: From guidance to enforcement

Since the Maritime Transportation Security Act (MTSA) of 2002, ports have been required to develop and maintain security plans. Cybersecurity formally entered the regulatory fold in 2020 with revisions to 33 CFR Part 105 and 106, requiring port authorities to assess and address computer system vulnerabilities.

In January 2025, the USCG finalized new rules to enforce cybersecurity practices across the MTS. Key elements include (but are not limited to):

  • A dedicated cyber incident response plan (PR.IP-9)
  • Routine cybersecurity risk assessments and exercises (ID.RA)
  • Designation of a cybersecurity officer and regular workforce training (section 3.1)
  • Controls for access management, segmentation, logging, and encryption (PR.AC-1:7)
  • Supply chain risk management (ID.SC)
  • Incident reporting to the National Response Center

Port operators are encouraged to align their programs with the NIST Cybersecurity Framework (CSF 2.0) and NIST SP 800-82r3, which provide comprehensive guidance for IT and OT security in industrial environments.

How Darktrace can support maritime & ports

Unified IT + OT + Cloud coverage

Maritime ports operate in hybrid environments spanning business IT systems (finance, HR, ERP), industrial OT (cranes, gates, pumps, sensors), and an increasing array of cloud and SaaS platforms.

Darktrace is the only vendor that provides native visibility and threat detection across OT/IoT, IT, cloud, and SaaS environments — all in a single platform. This means:

  • Cranes and other physical process control networks are monitored in the same dashboard as Active Directory and Office 365.
  • Threats that start in the cloud (e.g., phishing, SaaS token theft) and pivot or attempt to pivot into OT are caught early — eliminating blind spots that siloed tools miss.

This unification is critical to meeting USCG requirements for network-wide monitoring, risk identification, and incident response.

AI that understands your environment. Not just known threats

Darktrace’s AI doesn’t rely on rules or signatures. Instead, it uses Self-Learning AI TM that builds a unique “pattern of life” for every device, protocol, user, and network segment, whether it’s a crane router or PLC, SCADA server, Workstation, or Linux file server.

  • No predefined baselines or manual training
  • Real-time anomaly detection for zero-days, ransomware, and supply chain compromise
  • Continuous adaptation to new devices, configurations, and operations

This approach is critical in diverse distributed OT environments where change and anomalous activity on the network are more frequent. It also dramatically reduces the time and expertise needed to classify and inventory assets, even for unknown or custom-built systems.

Supporting incident response requirements

A key USCG requirement is that cybersecurity plans must support effective incident response.

Key expectations include:

  • ‍Defined response roles and procedures: Personnel must know what to do and when (RS.CO-1).
  • ‍Timely reporting: Incidents must be reported and categorized according to established criteria (RS.CO-2, RS.AN-4).‍
  • Effective communication: Information must be shared internally and externally, including voluntary collaboration with law enforcement and industry peers (RS.CO-3 through RS.CO-5).‍
  • Thorough analysis: Alerts must be investigated, impacts understood, and forensic evidence gathered to support decision-making and recovery (RS.AN-1 through RS.AN-5).‍
  • Swift mitigation: Incidents must be contained and resolved efficiently, with newly discovered vulnerabilities addressed or documented (RS.MI-1 through RS.MI-3).‍
  • Ongoing improvement: Organizations must refine their response plans using lessons learned from past incidents (RS.IM-1 and RS.IM-2).

That means detections need to be clear, accurate, and actionable.

Darktrace cuts through the noise using AI that prioritizes only high-confidence incidents and provides natural-language narratives and investigative reports that explain:

  • What’s happening, where it’s happening, when it’s happening
  • Why it’s unusual
  • How to respond

Result: Port security teams often lean and multi-tasked can meet USCG response-time expectations and reporting needs without needing to scale headcount or triage hundreds of alerts.

Built-for-edge deployment

Maritime environments are constrained. Many traditional SaaS deployment types often are unsuitable for tugboats, cranes, or air-gapped terminal systems.

Darktrace builds and maintains its own ruggedized, purpose-built appliances and unique virtual deployment options that:

  • Deploy directly into crane networks or terminal enclosures
  • Require no configuration or tuning, drop-in ready
  • Support secure over-the-air updates and fleet management
  • Operate without cloud dependency, supporting isolated and air-gapped systems

Use case: Multiple ports have been able to deploy Darktrace directly into the crane’s switch enclosure, securing lateral movement paths without interfering with the crane control software itself.

Segmentation enforcement & real-time threat containment

Darktrace visualizes real-time connectivity and attack pathways across IT, OT, and IoT it and integrates with firewalls (e.g., Fortinet, Cisco, Palo Alto) to enforce segmentation using AI insights alongside Darktrace’s own native autonomous and human confirmed response capabilities.

Benefits of autonomous and human confirmed response:

  • Auto-isolate rogue devices before the threat can escalate
  • Quarantine a suspicious connectivity with confidence operations won’t be halted
  • Autonomously buy time for human responders during off-hours or holidays
  • This ensures segmentation isn't just documented but that in the case of its failure or exploitation responses are performed as a compensating control

No reliance on 3rd parties or external connectivity

Darktrace’s supply chain integrity is a core part of its value to critical infrastructure customers. Unlike solutions that rely on indirect data collection or third-party appliances, Darktrace:

  • Uses in-house engineered sensors and appliances
  • Does not require transmission of data to or from the cloud

This ensures confidence in both your cyber visibility and the security of the tools you deploy.

See examples here of how Darktrace stopped supply chain attacks:

Readiness for USCG and Beyond

With a self-learning system that adapts to each unique port environment, Darktrace helps maritime operators not just comply but build lasting cyber resilience in a high-threat landscape.

Cybersecurity is no longer optional for U.S. ports its operationally and nationally critical. Darktrace delivers the intelligence, automation, and precision needed to meet USCG requirements and protect the digital lifeblood of the modern port.

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Daniel Simonds
Director of Operational Technology

More in this series

No items found.

Blog

/

AI

/

November 2, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

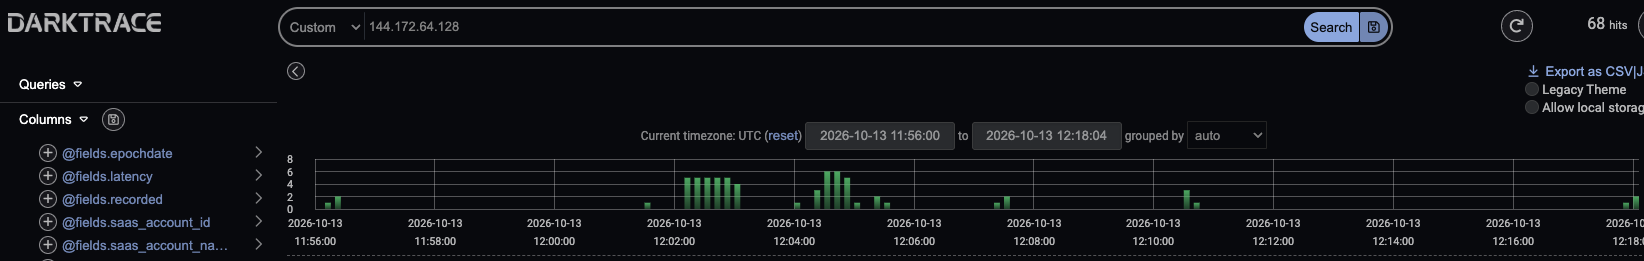
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence

Blog

/

OT

/

November 2, 2026

Beyond the Fridge: Exposed Industrial Control Systems

Default blog imageDefault blog image

Introduction

In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.

The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.

The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].

Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.

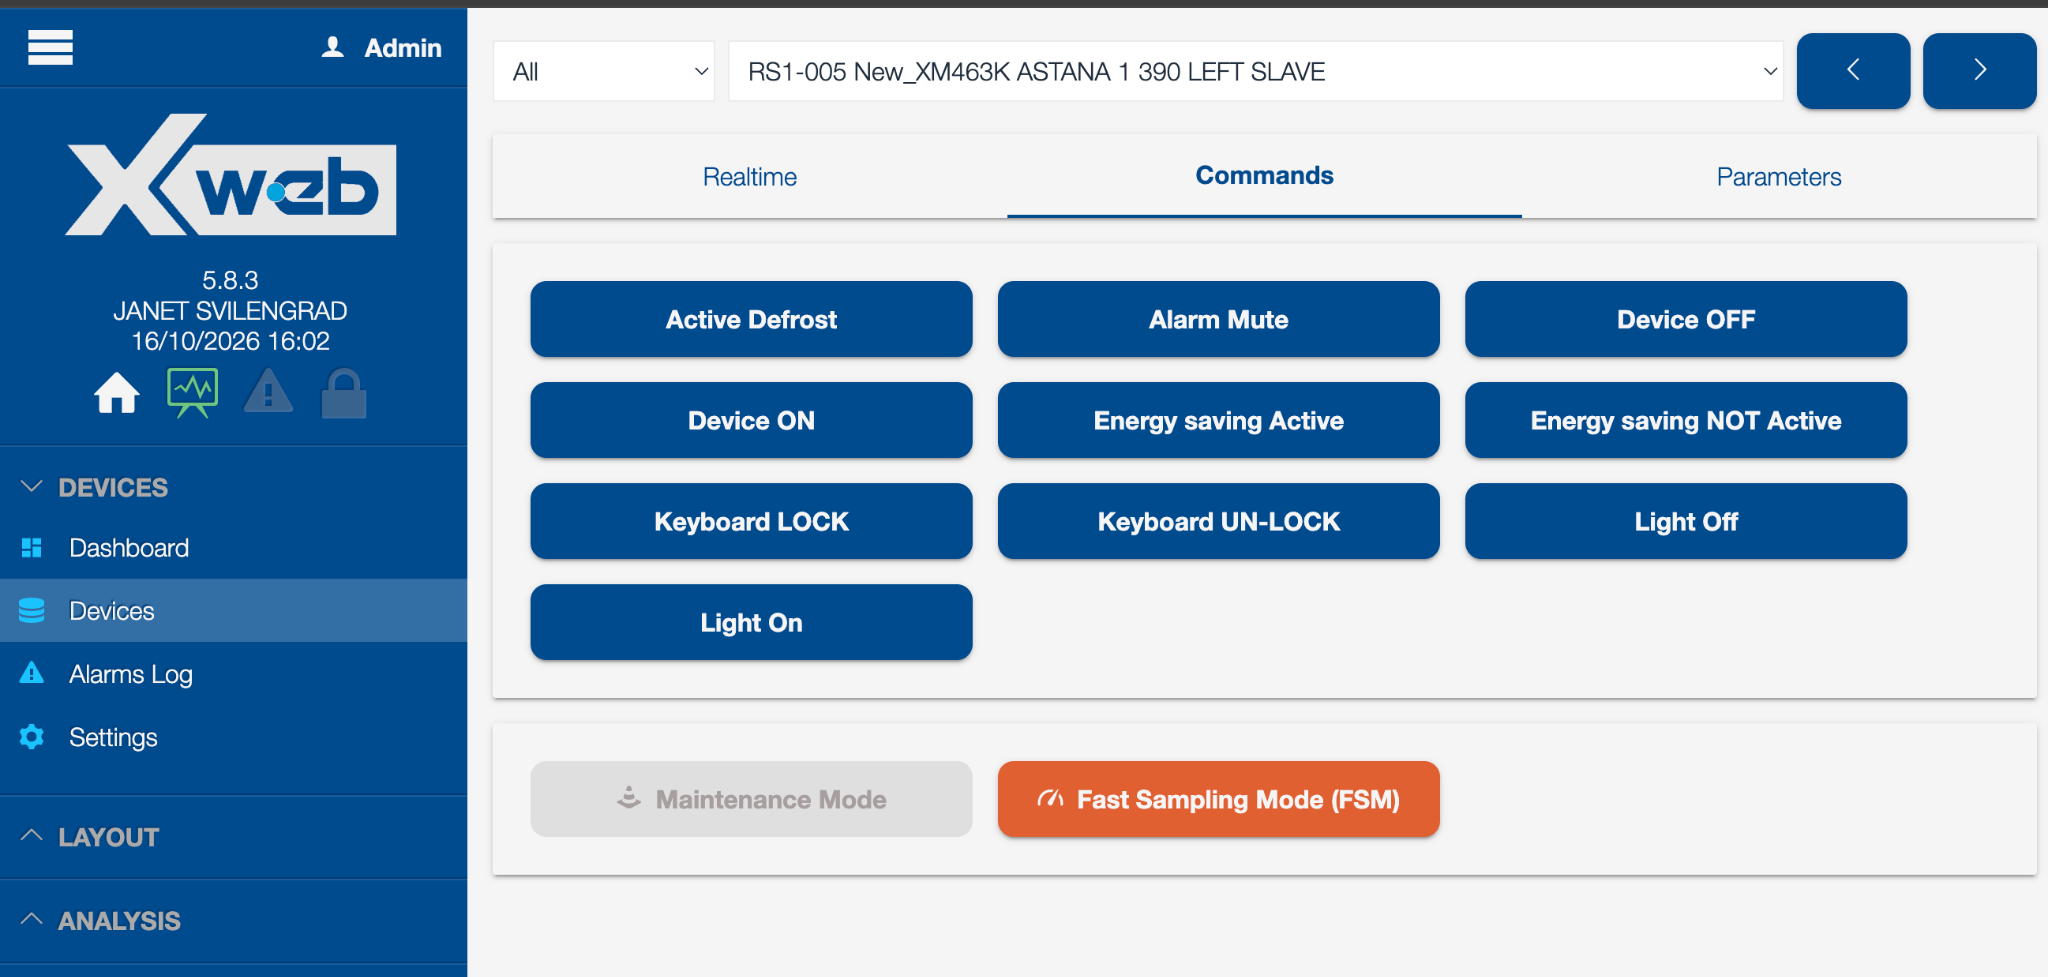
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.

‍

Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.

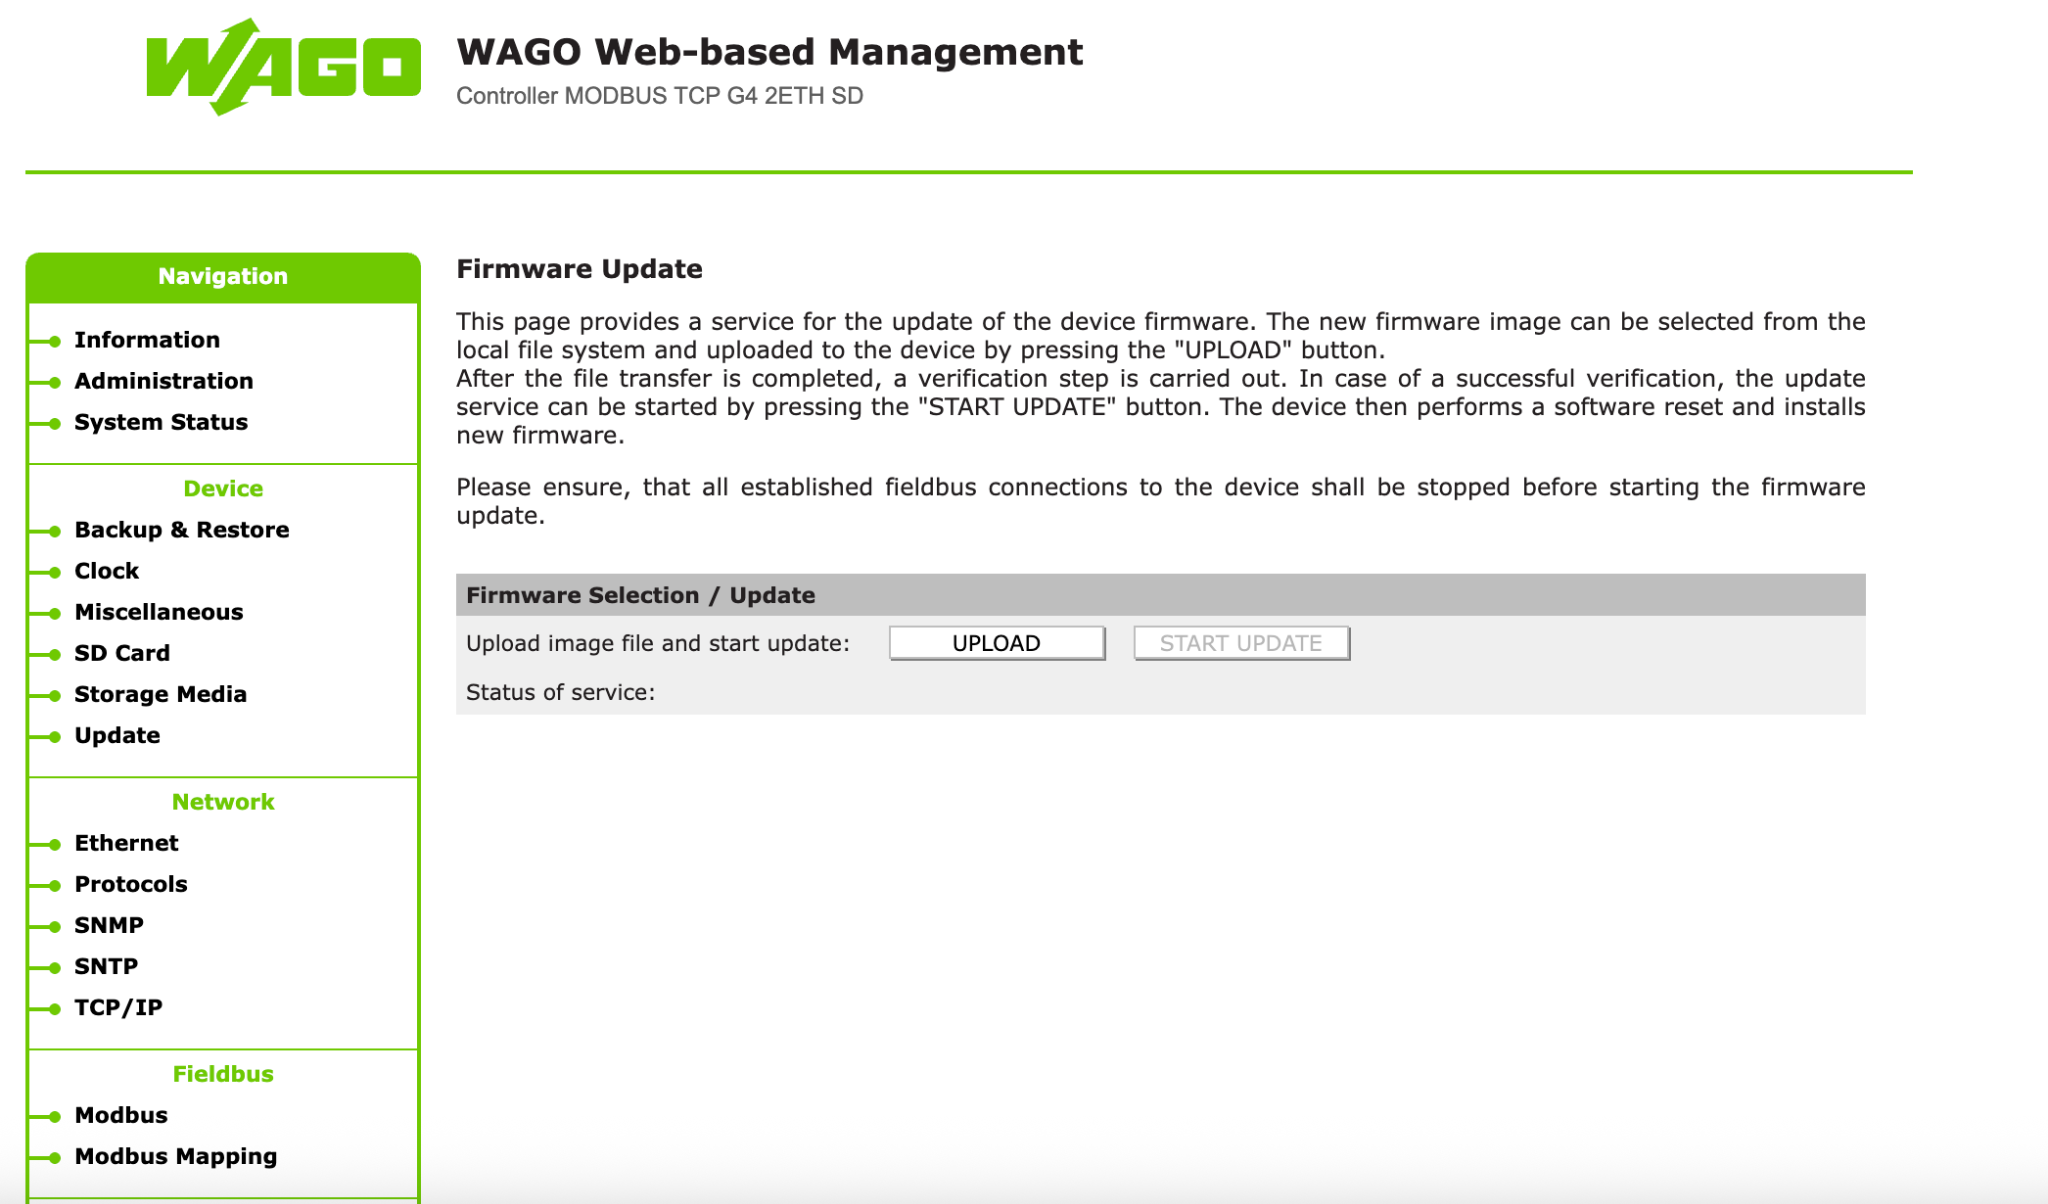
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.

‍

Figure 2: WAGO Management interface.

‍

The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.

‍

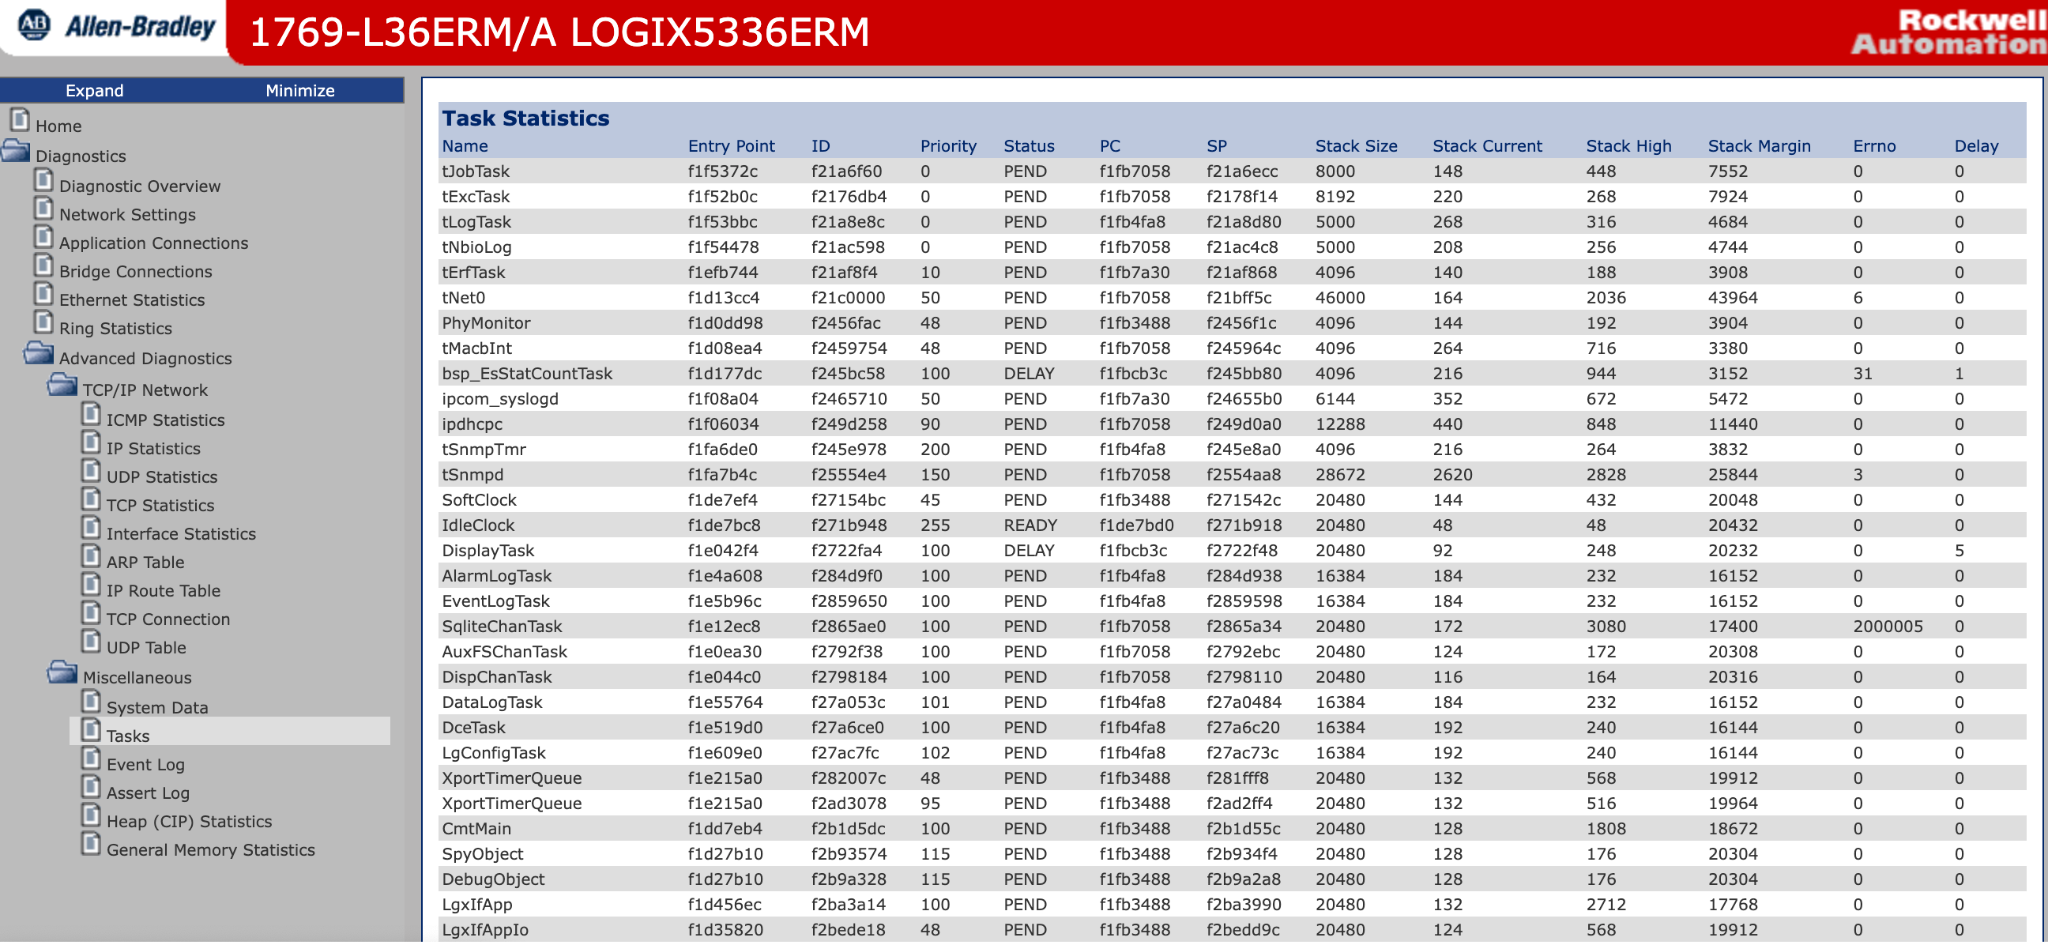
Figure 3: Web interface for Allen-Bradley CompactLogix controller.

‍

Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.

Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.

The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.

The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.

Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.

The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.

Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.

Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.

Darktrace helps security teams gain visibility across IT and OT and respond to risks: https://www.darktrace.com/products/operational-technology.

Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.

References

1.        https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

‍

Continue reading
About the author
Tara Gould
Malware Research Lead
Your data. Our AI.
Elevate your network security with Darktrace AI