
Blog
/
AI
/
June 10, 2026

So sichern Sie KI im Unternehmen: Praktisches Framework für Modelle, Daten und Agenten

Die KI entwickelt sich schneller, als die Regulierung damit Schritt halten kann, wodurch die Angriffsflächen zunehmen und bisher unbekannte Risiken entstehen. Von Daten und Modellen bis hin zu KI-Agenten und Integrationen: Sicherheit beginnt damit, zu wissen, was geschützt werden muss. Erfahren Sie, wie Sie KI-bedingte Risiken erkennen, damit Sie Governance-Rahmenwerke und Kontrollmechanismen etablieren können, die Innovation gewährleisten, ohne das Unternehmen neuen Angriffsflächen auszusetzen. 
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brittany Woodsmall
Senior Product Marketing Manager, AI
Written by
Simon Fellows
Senior Vice President, Product Strategy
How to secure AI in the enterprise: A practical framework for models, data, and agents Default blog image
10
Jun 2026

Wichtigste Erkenntnisse

  • Die KI-Sicherheit in Unternehmen geht über den Schutz von KI-Modellen hinaus und umfasst auch die Absicherung von KI-Agenten, Unternehmensdaten, Identitäten, APIs und Integrationen von Drittanbietern. Unternehmen benötigen einen Überblick darüber, wo KI eingesetzt wird, auf welche Daten sie zugreifen kann und wie sie sich verhält, um KI-Risiken effektiv zu bewältigen.
  • Ein wirksames Sicherheitsframework für KI vereint Governance, Identitäts- und Zugriffsmanagement, Datenschutz, Laufzeitüberwachung und die Sicherheit der Software-Lieferkette. Keine einzelne Kontrollmaßnahme oder KI-Schutzvorkehrung reicht allein aus, um KI in Unternehmen zu schützen.
  • KI-Einführung und KI-Sicherheit müssen sich gemeinsam weiterentwickeln. Die Einbettung von Sicherheitskontrollen über den gesamten KI-Lebenszyklus hinweg ermöglicht es Unternehmen, Cyberrisiken zu reduzieren, die regulatorische Compliance zu unterstützen und KI-Initiativen mit größerer Zuversicht auszuweiten.

Warum hat die KI-Sicherheit in Unternehmen jetzt Priorität?

Die Absicherung von Unternehmens-KI hat mittlerweile Priorität, da die Einführung schneller voranschreitet als Governance, Verantwortlichkeiten und technische Kontrollen. Generative KI-Tools, eingebettete KI-Funktionen und autonome Agenten können auf sensible Daten zugreifen, Entscheidungen treffen und sich mit externen Systemen verbinden – wodurch Risiken entstehen, die Sicherheit, Datenschutz, Compliance und den laufenden Betrieb betreffen. Für viele Unternehmen besteht die erste Herausforderung nicht darin, ob KI abgesichert werden sollte, sondern was die „Absicherung von KI“ in der Praxis eigentlich bedeutet. Geht es um den Schutz von Modellen? Um Daten-Governance? Um die Überwachung der Ergebnisse? Oder um die Steuerung, wie sich KI-Agenten nach ihrer Bereitstellung verhalten?  

Während die Nachfrage nach der Einführung wächst, bleibt die Absicherung der KI-Nutzung in Unternehmen für viele noch ein abstraktes Konzept, und die Operationalisierung ihrer Nutzung geht weit über bloße Transparenz hinaus. Fachleute müssen außerdem berücksichtigen, wie KI im gesamten Unternehmen beschafft, entwickelt, bereitgestellt, genutzt und gesteuert wird.

Das Ziel für Sicherheitsteams: ein klares, lebenszyklusorientiertes Framework für KI-Sicherheit. Dieser Blogbeitrag zeigt die Vielfalt der KI-Anwendungsfälle auf, die bei der Entwicklung dieses Frameworks berücksichtigt werden sollten, und erläutert, wie sich dieses Gespräch für nichttechnische Zielgruppen gestalten lässt.  

Was bedeutet es, KI im Unternehmen abzusichern?

Die Absicherung von KI bedeutet, Transparenz und Kontrolle darüber zu gewährleisten, wo KI eingesetzt wird, auf welche Daten sie zugreift, wie sich Modelle und Agenten verhalten und ob ihre Aktionen der geschäftlichen Zielsetzung entsprechen. Sie erstreckt sich über Anwendungen, Identitäten, Infrastruktur, Daten, Entwicklungs-Workflows und Drittanbieter hinweg, sodass die Verantwortung nicht allein bei einer Sicherheitsfunktion liegen kann.

Die Absicherung von KI wird oft als Erweiterung bestehender Sicherheitsdisziplinen dargestellt. In der Praxis kann diese Annahme zu Verwirrung führen.

Sicherheitsfunktionen basieren auf relativ stabilen Grenzen. Bei der Anwendungssicherheit stehen Code und Logik im Mittelpunkt. Cloud-Sicherheit regelt Infrastruktur und Identität. Datensicherheit schützt sensible Informationen im Ruhezustand und bei der Übertragung. Identitätssicherheit steuert, wer auf Systeme und Dienste zugreifen kann. Jede Funktion verfügt über eine klare Zuständigkeit, etablierte Werkzeuge und gut bekannte Fehlerquellen.

KI lässt sich keiner dieser Kategorien eindeutig zuordnen. Ein KI-System ist gleichzeitig:

  • Eine Anwendung, die Logik ausführt
  • Ein Datenverarbeiter, der sensible Informationen einliest und generiert
  • Eine Entscheidungsebene, die Handlungen beeinflusst oder automatisiert
  • Ein dynamisches System, das sein Verhalten im Laufe der Zeit ändert

Daher erstrecken sich die durch KI entstehenden Sicherheitsrisiken gleichzeitig über mehrere Bereiche hinweg. Eine einzelne KI-Interaktion kann innerhalb desselben Workflows Identitätsmissbrauch, die Offenlegung von Daten, den Missbrauch von Anwendungslogik und Risiken in der Lieferkette umfassen. Hier beginnen die traditionellen Grenzen zwischen Sicherheitsfunktionen zu verschwimmen.

So ist beispielsweise eine von einem autorisierten Nutzer übermittelte bösartige Eingabeaufforderung keine klassische Kompromittierung einer Identität, kann jedoch Datenlecks oder unbefugte Aktionen auslösen. Der Aufruf eines externen Dienstes durch einen KI-Agenten kann wie legitimes Anwendungsverhalten wirken, obwohl dabei Anforderungen an die Datenhoheit oder Compliance verletzt werden. Von KI generierter Code kann die üblichen Entwicklungsprüfungen bestehen und dennoch subtile Schwachstellen oder kompromittierte Abhängigkeiten einführen.

In keinem der Fälle ist ein einzelnes Sicherheitsteam allein für das Risiko „verantwortlich“.

Aus diesem Grund lässt sich die Sicherheit von KI nicht allein auf Modellsicherheit, Governance-Richtlinien oder Perimeterkontrollen reduzieren. Sie erfordert einen gemeinsamen Sicherheitsansatz, der Entwicklung, Betrieb, Datenverarbeitung und Benutzerinteraktion umfasst. Bei der Sicherheit von KI geht es nicht nur darum, zu verstehen, ob der Zugriff auf Systeme sicher erfolgt, sondern auch, ob diese Systeme so genutzt, trainiert und eingesetzt werden, dass sie mit den geschäftlichen Zielen und der Risikotoleranz im Einklang stehen.

Im Kern geht es bei der Sicherheit von KI darum, Klarheit in Umgebungen wiederherzustellen, in denen die Verantwortlichkeiten schnell unklar werden können. Es geht darum zu wissen, wo KI vorhanden ist, wie sie sich verhält, was sie tun darf und wie sich ihre Entscheidungen auf das gesamte Unternehmen auswirken. Ohne diese Klarheit wird KI zu einem Kraftmultiplikator sowohl für die Produktivität als auch für das Risiko.

Was sollte ein KI-Sicherheitsframework für Unternehmen abdecken?

Ein Sicherheitsframework für KI in Unternehmen sollte Missbrauch und emergentes Verhalten, die Laufzeitüberwachung, Entwicklung und Infrastruktur, Schatten-KI und Lieferketten von Drittanbietern sowie die organisatorische Bereitschaft berücksichtigen. Zusammen decken diese Bereiche ab, wie KI während ihres gesamten Lebenszyklus beschafft, entwickelt, bereitgestellt, abgerufen, überwacht und gesteuert wird.

Es gibt fünf zentrale Bereiche für die Absicherung von KI im Unternehmen:

  • Schutz vor Missbrauch und unerwarteten KI-Verhaltensweisen
  • Überwachung und Steuerung von KI im Betrieb
  • Schutz der KI-Entwicklung und -Infrastruktur
  • Sicherung der KI-Lieferkette
  • Stärkung der Einsatzbereitschaft und Aufsicht

Gemeinsam bieten diese Kategorien einen strukturierten Bezugsrahmen, um zu verstehen, wie sich KI-Risiken äußern und worauf Sicherheitsteams ihre Anstrengungen konzentrieren sollten.

1. Schutz vor Missbrauch und neu auftretenden Verhaltensweisen von KI

Generative-KI-Systeme und Agenten können auf eine Weise manipuliert werden, die herkömmliche Kontrollen umgeht. Selbst wenn der Zugriff autorisiert ist, kann KI durch sorgfältig formulierte Prompts und Interaktionen missbraucht, zweckentfremdet oder beeinflusst werden.

Zu den wichtigsten Risiken zählen:

  • Bösartige Prompt-Injection, die darauf ausgelegt ist, unerwünschte Handlungen zu erzwingen
  • Unbefugte oder unbeabsichtigte Anwendungsfälle, die Schutzmaßnahmen umgehen
  • Offenlegung sensibler Daten durch Prompt-Historien
  • Halluzinierte oder böswillige Ausgaben, die das Verhalten von Menschen beeinflussen

Anders als herkömmliche Anwendungen können KI-Systeme schädliche Ergebnisse hervorbringen, ohne explizit kompromittiert worden zu sein. Die Absicherung dieser Ebene erfordert die Überwachung der Absicht, nicht nur des Zugriffs. Sicherheitsteams benötigen Einblick darin, wie KI-Systeme mit Eingaben versorgt werden, wie die Ergebnisse genutzt werden und ob die Nutzung mit den genehmigten Geschäftszwecken übereinstimmt.

2. Überwachung und Steuerung von KI im Betrieb

Nach ihrer Bereitstellung arbeiten KI-Agenten mit maschineller Geschwindigkeit und in maschinellem Umfang. Sie können Maßnahmen einleiten, Daten austauschen und mit anderen Systemen interagieren, ohne dass dabei nennenswerte menschliche Aufsicht erforderlich ist. Daher ist die Transparenz während der Laufzeit von entscheidender Bedeutung.

Zu den operativen KI-Risiken gehören:

  • Agenten, die Berechtigungen auf unbeabsichtigte Weise nutzen
  • Unkontrollierte ausgehende Verbindungen zu externen Diensten oder Agenten
  • Verlust der forensischen Transparenz über kurzlebige KI-Komponenten
  • Nicht konforme Datenübertragung über Rechtsraumgrenzen hinweg

Die Absicherung von KI im laufenden Betrieb erfordert die Echtzeitüberwachung des Agentenverhaltens, zentrale Kontrollpunkte wie KI-Gateways sowie die Möglichkeit, den Zustand des Agenten für Untersuchungen zu erfassen. Ohne diese Funktionen fehlt Sicherheitsteams möglicherweise der Einblick darin, wie sich KI-Systeme im laufenden Betrieb verhalten, insbesondere in Cloud-nativen oder regulierten Umgebungen.

3. Schutz der KI-Entwicklung und -Infrastruktur

Viele KI-Risiken entstehen lange vor der Bereitstellung. Entwicklungspipelines, Infrastrukturkonfigurationen und Architekturentscheidungen beeinflussen die Sicherheitslage von KI-Systemen.

Zu den häufigen Risiken zählen:

  • Fehlkonfigurierte Berechtigungen und Schutzmechanismen
  • Unsichere oder übermäßig komplexe Agentenarchitekturen
  • Infrastructure-as-Code bringt unbemerkte Fehlkonfigurationen mit sich
  • Schwachstellen in KI-generiertem Code und Abhängigkeiten

KI-generierter Code bringt eine neue Risikodimension mit sich, da halluzinierte Pakete oder unsichere Logik möglicherweise schwerer zu erkennen und zu debuggen sind als von Menschen geschriebener Code. Die Absicherung der KI-Entwicklung bedeutet, Sicherheitskontrollen frühzeitig anzuwenden, darunter statische Analysen, Architekturprüfungen und die kontinuierliche Überwachung der Konfiguration während des gesamten Entwicklungsprozesses.

4. Sicherung der KI-Lieferkette

KI-Lieferketten sind oft undurchsichtig. Modelle, Datensätze, Abhängigkeiten und Dienste können von Drittanbietern stammen, die unterschiedlich transparent sind und unterschiedlich belastbare Zusicherungen bieten.

Zu den wichtigsten Risiken in der Lieferkette zählen:

  • Schatten-KI-Tools, die außerhalb genehmigter Kontrollmechanismen eingesetzt werden
  • Externe KI-Agenten mit internem Zugriff
  • Anbieter, die KI auf Unternehmensdaten anwenden, ohne dies offenzulegen
  • Kompromittierte Modelle, Trainingsdaten oder Abhängigkeiten

Um die KI-Lieferkette zu sichern, muss ermittelt werden, wo KI zum Einsatz kommt, die Herkunft und Lizenzierung von Modellen und Daten überprüft werden und bewertet werden, wie Lieferanten Unternehmensdaten verarbeiten und schützen. Ohne diesen Überblick riskieren Unternehmen Datenabflüsse, regulatorische Risiken und eine nachgelagerte Kompromittierung durch vertrauenswürdige Integrationen.

5. Stärkung der Einsatzbereitschaft und Aufsicht

Selbst bei robusten technischen Kontrollmaßnahmen versagt die KI-Sicherheit ohne Governance, Tests und geschulte Teams. KI führt zu neuen Vorfallszenarien, auf deren Bewältigung viele Sicherheitsteams noch nicht vorbereitet sind.

Zu den Risiken bei der Aufsicht zählen:

  • Mangel an aussagekräftiger Berichterstattung zu KI-Risiken
  • Ungetestete KI-Systeme im Produktivbetrieb
  • Nicht für KI-spezifische Bedrohungen geschulte Sicherheitsteams

Unternehmen benötigen KI-orientierte Berichterstattung, Red- und Purple-Team-Übungen, die KI-Systeme einbeziehen, sowie fortlaufende Schulungen, um ihre Einsatzbereitschaft zu stärken. Diese Fähigkeiten stellen sicher, dass KI-Risiken verstanden, getestet und kontinuierlich adressiert werden, anstatt erst bei einem Live-Vorfall zutage zu treten.

Ein neues Verständnis von KI-Sicherheit für die Unternehmensleitung

KI-Sicherheit ist nicht nur ein technisches Thema. Es geht um Vertrauen, Verantwortlichkeit und Resilienz. Vorstände wollen die Gewissheit, dass KI-gestützte Entscheidungen zuverlässig, nachvollziehbar und vor Manipulationen geschützt sind.

Wirksame Kommunikation mit der Führungsebene konzentriert sich auf:

  • Vertrauen: Vertrauen in Datenintegrität, Modellverhalten und Ergebnisse
  • Rechenschaftspflicht: klare Zuständigkeiten über Teams und Lieferanten hinweg
  • Resilienz: die Fähigkeit, auch bei Angriffen oder unter regulatorischen Vorgaben den Betrieb aufrechtzuerhalten, Audits durchzuführen und sich anzupassen

Die Ausrichtung von Maßnahmen zur KI-Sicherheit an anerkannten Rahmenwerken wie ISO/IEC 42001 und dem NIST AI Risk Management Framework zeugt von Reife und bringt die KI-Sicherheit mit umfassenderen Governance-Zielen in Einklang.

Fazit: Die Absicherung von KI ist eine Herausforderung über den gesamten Lebenszyklus hinweg

Dieselben Eigenschaften, die KI so transformativ machen, erschweren auch ihre Absicherung. KI-Systeme verwischen traditionelle Grenzen zwischen Software, Nutzern und Entscheidungsfindung und vergrößern die Angriffsfläche auf subtile, aber bedeutsame Weise.

Um KI sicher zu machen, muss wieder Klarheit geschaffen werden. Es muss bekannt sein, wo KI zum Einsatz kommt, wie sie sich verhält, wer sie steuert und wie sie reguliert wird. Ein rahmenbasierter Ansatz ermöglicht es Unternehmen, mit KI innovativ zu sein und gleichzeitig Vertrauen, Verantwortlichkeit und Kontrolle zu wahren.

Der Weg zu sicherer KI ist noch nicht zu Ende, beginnt jedoch damit, die Risiken über den gesamten KI-Lebenszyklus hinweg zu verstehen und Sicherheitspraktiken zu etablieren, die sich gemeinsam mit der Technologie weiterentwickeln.

Darktrace / SECURE AI unterstützt diesen Lebenszyklusansatz, indem es unternehmensweite Transparenz, Verhaltensüberwachung und Echtzeitkontrolle vereint und Sicherheitsteams dabei hilft, riskante Aktivitäten zu erkennen und KI sicherer einzuführen.

[related-resource]

Laden Sie das vollständige Framework herunter

Erfahren Sie, wie Sie KI-gestützte Risiken erkennen, um Governance-Frameworks und Kontrollen in Ihrem Unternehmen zu etablieren.

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brittany Woodsmall
Senior Product Marketing Manager, AI
Written by
Simon Fellows
Senior Vice President, Product Strategy

More in this series

No items found.

Blog

/

/

November 9, 2026

From One Alert to a Wider Campaign: Uncovering Novel Threats Through Behavioral Analysis

Default blog imageDefault blog image

Key Findings

  • Darktrace’s Threat Research team is exploring a new method to identify malicious campaigns by correlating similar anomalous activity across its customer fleet.
  • The method uses unsupervised clustering to identify shared behavioral patterns across multiple customer deployments without relying on prior indicators of compromise (IoCs).
  • The approach identified shared infrastructure across dozens of customers, with activity linked to the likely POPA botnet.
  • A second cluster identified anomalous activity associated with Monero cryptocurrency mining.

‍

How does Darktrace conduct threat research?

The Darktrace Threat Research team aims to identify malicious campaign activity affecting multiple customers. By their nature, these campaigns will lead to shared behavioral patterns across multiple victims.

In this piece, we describe a method for identifying malicious campaign activity that uses this simple observation as a guiding principle. We begin by outlining a few key facts about the modern threat landscape and why behavioral detection is necessary to meet the challenges it presents. We then explore how fleet-wide behavioral detections can be leveraged using the principle above to systematically identify multi-deployment campaigns impacting the Darktrace customer fleet. Finally, we demonstrate that this research is not purely theoretical, using real examples of campaign activity detected through this novel approach.

Shifting to a behavioral-focused approach

The modern era of cyber-defense necessitates detection capabilities beyond traditional signature-based methods. Technologies such as antivirus signatures, hash-based malware identification, and IP blocklists have historically been successful in defending against known threats. However, they are easily circumvented by attackers and inherently limited in defending against the novel attack techniques that today's threat landscape is producing.

Recent breakthroughs in AI represent a transformational risk multiplier that cannot be ignored. AI systems do not merely execute existing attacks at machine speed; there are signs they can also synthesize novel tradecraft [1], increasing the likelihood that defenders will encounter attack patterns that have never previously been observed. Meanwhile vulnerability disclosures continue to accelerate. More than 48,000 CVEs were published in 2025, and published statistics to date indicate that 2026 is already on track to significantly exceed that figure [2]. While multiple factors may contribute to vulnerability discovery, AI is seen as a key factor in this rapid growth. Organizations should expect a growing proportion of malicious activity to fall outside the scope of detections that rely solely on prior knowledge of known threats.

By design, Darktrace’s behavioral and anomaly-focused detection capabilities are well-suited to this testing landscape. With a focus on detecting unknown and unexpected activity that deviates from the baseline of “normal” behavior, detection of CVE exploitation without prior knowledge of the vulnerability and before public disclosure, for example, is achievable [3][4].

Darktrace’s diverse customer base benefits from a further layer of protection: working with only deidentified alert metadata, our threat researchers hunt proactively across the fleet. Beyond the level of the individual customer, there is a second, larger vantage to be leveraged.

Darktrace data provides unique insight into the unexpected behavioral patterns that occur across its customer fleet. What can we see if we look at this fleet-wide telemetry and hunt for systematic behavioral campaigns that impact our customer base?

Correlating across the customer base

At the deployment level, Darktrace focuses on whether activity is unusual in the context of an organization's normal behavior, but as we zoom out and look at these alerts at the fleet level, the problem fundamentally changes . We are no longer seeking anomalies in largely normal data; we are seeking systematic patterns within data already known to be anomalous. An isolated behavior anomaly may be notable for a single customer; the same fingerprint across dozens is a signal of a structured campaign. Hunting for such campaigns and sharing our findings are key areas of focus for Darktrace’s Threat Research team.  In this spirit, Darktrace is  actively exploring a a new research approach that leverages deidentified alert metadata to increase campaign detection ability.

This approach is based on the premise that an expert human analyst presented with a set of alerts will identify likely related activity by assessing whether the metadata fields indicate a relationship. For example, two connections to a rare endpoint that exhibits naming structure that is likely from a single algorithm are a strong indicator, as is the use of an unusual port carrying a given protocol (e.g. port 6000 for SSL). Darktrace’s approach to campaign detection encodes this expert human judgement process through deterministic embedding functions that obtain reproducible vector representations of alert data. Unsupervised clustering is then applied to these vector representations to obtain groups of alerts that describe semantically similar alert data across multiple customers. These clusters therefore represent similar anomalous activity that has occurred across multiple customers. In other words, these clusters are candidates for malicious campaign activity.

‍

Figure 1: Layers of AI-based analysis provided through Darktrace products and cross-customer correlation.

‍

Case study 1 – unusual connections to shared underlying infrastructure

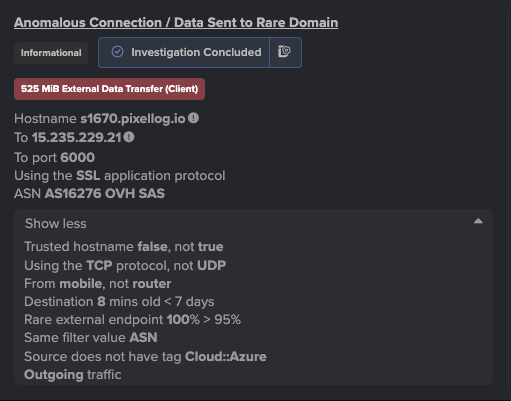
In one recent case, the clustering produced several tight groups of alerts spanning dozens of customers. Each group centered on a single domain whose subdomains were algorithmically generated (e.g. s01699, s1736, s91). Examined side by side, these clusters shared an unmistakable behavioral shape: each involved a domain with a clear naming pattern (e.g. s016841786.net-echo[.]com, s1670.pixellog[.]io, s217.pixellog[.]io) , with connections over SSL on the unusual port 6000 to servers hosted by non-mainstream providers (e.g. OVH, Hetzner, GTHost, Leaseweb), rather than generally expected content-delivery networks.

‍

Figure 2: An example model alert triggering on unusual outbound connections and data transfer to s1670.pixellog[.]io.

‍

Closer inspection revealed that the same subdomain label appeared under different domains (e.g. s1786.net-echo[.]com and s1786.pixellog[.]io). Following this lead, Darktrace’s threat researchers pivoted across the customer base and found numerous distinct subdomain labels reused under more than one registered domain. In several cases, the same label resolved to the same IP across different domains (e.g. s1704 under both pixellog[.]io and net-echo[.]com → 148.113.222[.]244; s01684 → 15.235.67[.]95), suggesting the use of ephemeral subdomain infrastructure in an attempt to avoid signature-based defense techniques.

This example demonstrates how multi-deployment data can uncover shared infrastructure that may be difficult to identify at the individual deployment level alone. In particular, the presented method facilitated this discovery by producing coherent, tight clusters of geometrically similar vector embeddings of malicious activity from large-scale fleet data, which could then be presented to a researcher for further investigation. This  activity highlighted across the Darktrace customer base was ultimately linked to likely POPA botnet activity through use of open-source intelligence (OSINT) [5].

Case Study 2 – anomalous user agent and txt URI

A second example shows the method surfacing a single, self-contained cluster. The clustering was not given any indicators to look for; instead, it grouped devices that shared an unusual combination of features. On inspection, that shared consisted of:

-      unusual user agent (tes)

-      specific request path (/md5_GIP.txt)

-      uncommon destination port (83)

-      hostname impersonating Google (matching regular expression ^www\.google\.com\.[a-zA-Z0-9]+\.fast-dns-host\.com$)

Treating these shared features as IoCs, Darktrace’s threat researchers then pivoted to an exploration across the customer base to investigate the full breadth of the campaign. This search identified further commonalities; additional domains which shared the same IP as the domain family highlighted in the cluster, as well as evidence of cryptocurrency mining on affected devices. Additional OSINT research also aligned with these findings, linking the discovered payloads and infrastructure to Monero cryptocurrency mining [6].

Conclusion

The method outlined in this blog is under active development, with ongoing technical refinement providing opportunities to further enhance its capabilities. While the capability continues to mature, this approach to threat hunting leverages the powerful vantage point of fleetwide telemetry across a diverse customer base to help protect Darktrace customers. This method allows campaigns that at the deployment level appear as isolated alerts to be seen at their true scale and spread. It enables proactive fleet-wide analysis without prior IoCs to identify campaigns impacting Darktrace customers.

This is possible because of what the method is built on: the atomic unit is the Darktrace alert, a signal that encodes years of cyber expertise, while the multi-deployment nature of the method allows organizations to indirectly benefit from findings from other networks through shared intelligence by Darktrace’s Threat Research team.

Credit to Daniel Levy (Threat Hunting Data Scientist), Paul Jennings (Principal Cyber Analyst), Emma Foulger (Global Head, Threat Operations)

Edited by Ryan Traill (Content Manager)

References

1. https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing

2. https://www.cvefind.com/en/cve-statistic-date.html

3. https://www.darktrace.com/blog/security-after-signatures-operating-in-a-world-of-pre-cve-disclosure-exploitation-collapsed-trust-boundaries-and-autonomous-systems

4. https://www.darktrace.com/blog/pre-cve-threat-detection-10-examples-identifying-malicious-activity-prior-to-public-disclosure-of-a-vulnerability

5. https://github.com/synthient/public-research/blob/main/2026/06/popa/Popa.md

6. https://www.deepwatch.com/blog/pirated-adobe-photoshop-2023-installers-lead-to-monero-cryptocurrency-mining/

Continue reading
About the author
Daniel Levy
Threat Hunting Data Scientist

Blog

/

AI

/

November 2, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

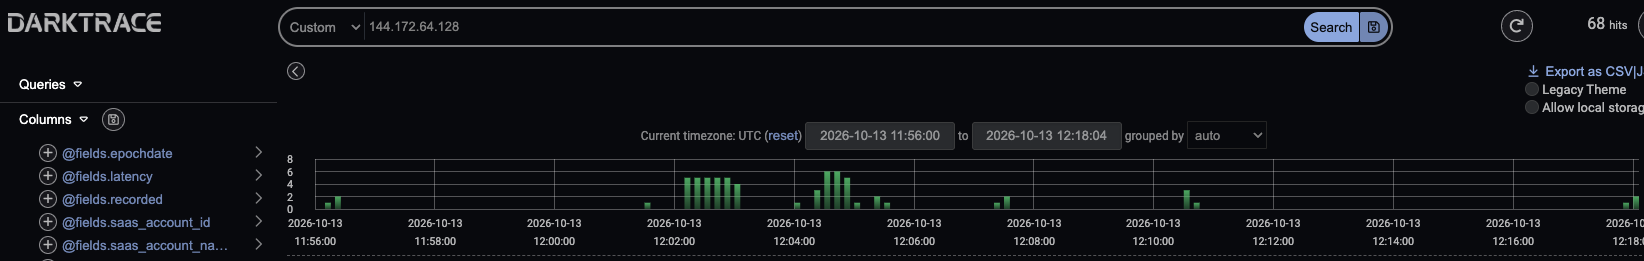
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence
Your data. Our AI.
Elevate your network security with Darktrace AI