Blog
/
Network
/
August 14, 2025

From Exploit to Escalation: Tracking and Containing a Real-World Fortinet SSL-VPN Attack

This blog outlines a real-world attack where threat actors exploited Fortinet SSL-VPN vulnerabilities to infiltrate a network. It highlights how Darktrace identified threat and took immediate actions to contain it, demonstrating the importance of proactive detection and rapid intervention in minimizing risk and disruption.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Priya Thapa
Cyber Analyst
Fortinet SSL-VPN AttackDefault blog image
14
Aug 2025

Threat actors exploiting Fortinet CVEs

Over the years, Fortinet has issued multiple alerts about a wave of sophisticated attacks targeting vulnerabilities in its SSL-VPN infrastructure. Despite the release of patches to address these vulnerabilities, threat actors have continued to exploit a trio of Common Vulnerabilities and Exposures (CVEs) disclosed between 2022 and 2024 to gain unauthorized access to FortiGate devices.

Which vulnerabilities are exploited?

The vulnerabilities—CVE-2022-42475, CVE-2023-27997, and CVE-2024-21762—affect Fortinet’s SSL-VPN services and have been actively exploited by threat actors to establish initial access into target networks.

The vulnerabilities affect core components of FortiOS, allowing attackers to execute remote code on affected systems.

CVE-2022-42475‍

Type: Heap-Based Buffer Overflow in FortiOS SSL-VPN‍

Impact: Remote Code Execution (Actively Exploited)

This earlier vulnerability also targets the SSL-VPN interface and has been actively exploited in the wild. It allows attackers to execute arbitrary code remotely by overflowing a buffer in memory, often used to deploy malware or establish persistent backdoors [6].

CVE-2023-27997

Type: Heap-Based Buffer Overflow in FortiOS and FortiProxy‍

Impact: Remote Code Execution

This flaw exists in the SSL-VPN component of both FortiOS and FortiProxy. By exploiting a buffer overflow in the heap memory, attackers can execute malicious code remotely. This vulnerability is particularly dangerous because it can be triggered without authentication, making it ideal for an initial compromise [5].

CVE-2024-21762

Type: Out-of-Bounds Write in sslvpnd

Impact: Remote Code Execution

This vulnerability affects the SSL-VPN daemon (sslvpnd) in FortiOS. It allows unauthenticated remote attackers to send specially crafted HTTP requests that write data outside of allocated memory bounds. This can lead to arbitrary code execution, giving attackers full control over a device [4].

In short, these flaws enable remote attackers to execute arbitrary code without authentication by exploiting memory corruption issues such as buffer overflows and out-of-bounds writes. Once inside, threat actors use symbolic link (symlink) in order to maintain persistence on target devices across patches and firmware updates. This persistence then enables them to bypass security controls and manipulate firewall configurations, effectively turning patched systems into long-term footholds for deeper network compromise [1][2][3].

Darktrace’s Coverage

Darktrace detected a series of suspicious activities originating from a compromised Fortinet VPN device, including anomalous HTTP traffic, internal network scanning, and SMB reconnaissance, all indicative of post-exploitation behavior. Following initial detection by Darktrace’s real-time models, its Autonomous Response capability swiftly acted on the malicious activity, blocking suspicious connections and containing the threat before further compromise could occur.

Further investigation by Darktrace’s Threat Research team uncovered a stealthy and persistent attack that leveraged known Fortinet SSL-VPN vulnerabilities to facilitate lateral movement and privilege escalation within the network.

Phase 1: Initial Compromise – Fortinet VPN Exploitation

The attack on a Darktrace customer likely began on April 11 with the exploitation of a Fortinet VPN device running an outdated version of FortiOS. Darktrace observed a high volume of HTTP traffic originating from this device, specifically targeting internal systems. Notably, many of these requests were directed at the /cgi-bin/ directory,  a common target for attackers attempting to exploit web interfaces to run unauthorized scripts or commands. This pattern strongly indicated remote code execution attempts via the SSL-VPN interface [7].

Once access was gained, the threat actor likely modified existing firewall rules, a tactic often used to disable security controls or create hidden backdoors for future access. While Darktrace does not have direct visibility into firewall configuration changes, the surrounding activity and post-exploitation behavior indicated that such modifications were made to support long-term persistence within the network.
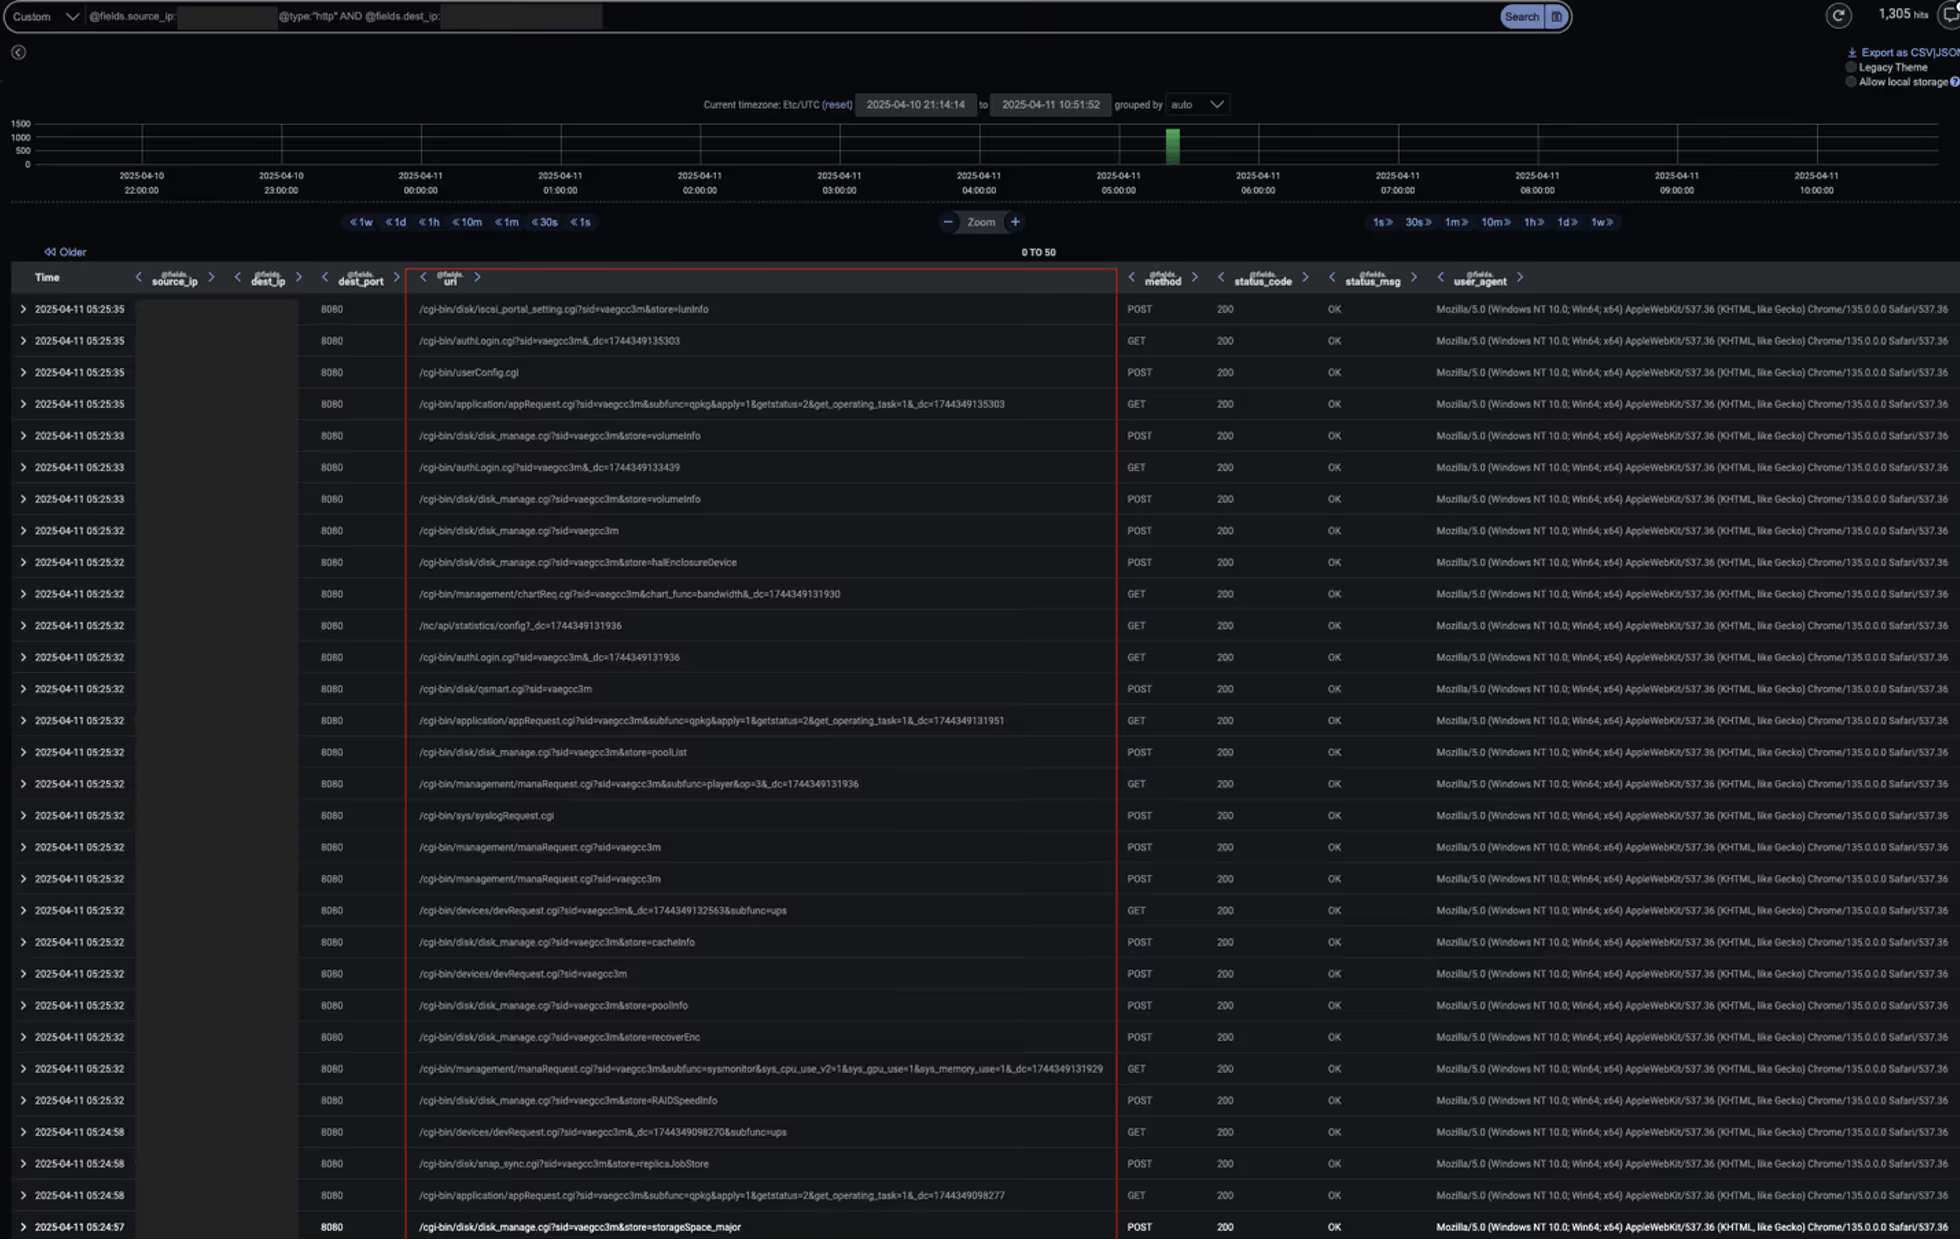
HTTP activity from the compromised Fortinet device, including repeated requests to /cgi-bin/ over port 8080.
Figure 1: HTTP activity from the compromised Fortinet device, including repeated requests to /cgi-bin/ over port 8080

Phase 2: Establishing Persistence & Lateral Movement

Shortly after the initial compromise of the Fortinet VPN device, the threat actor began to expand their foothold within the internal network. Darktrace detected initial signs of network scanning from this device, including the use of Nmap to probe the internal environment, likely in an attempt to identify accessible services and vulnerable systems.
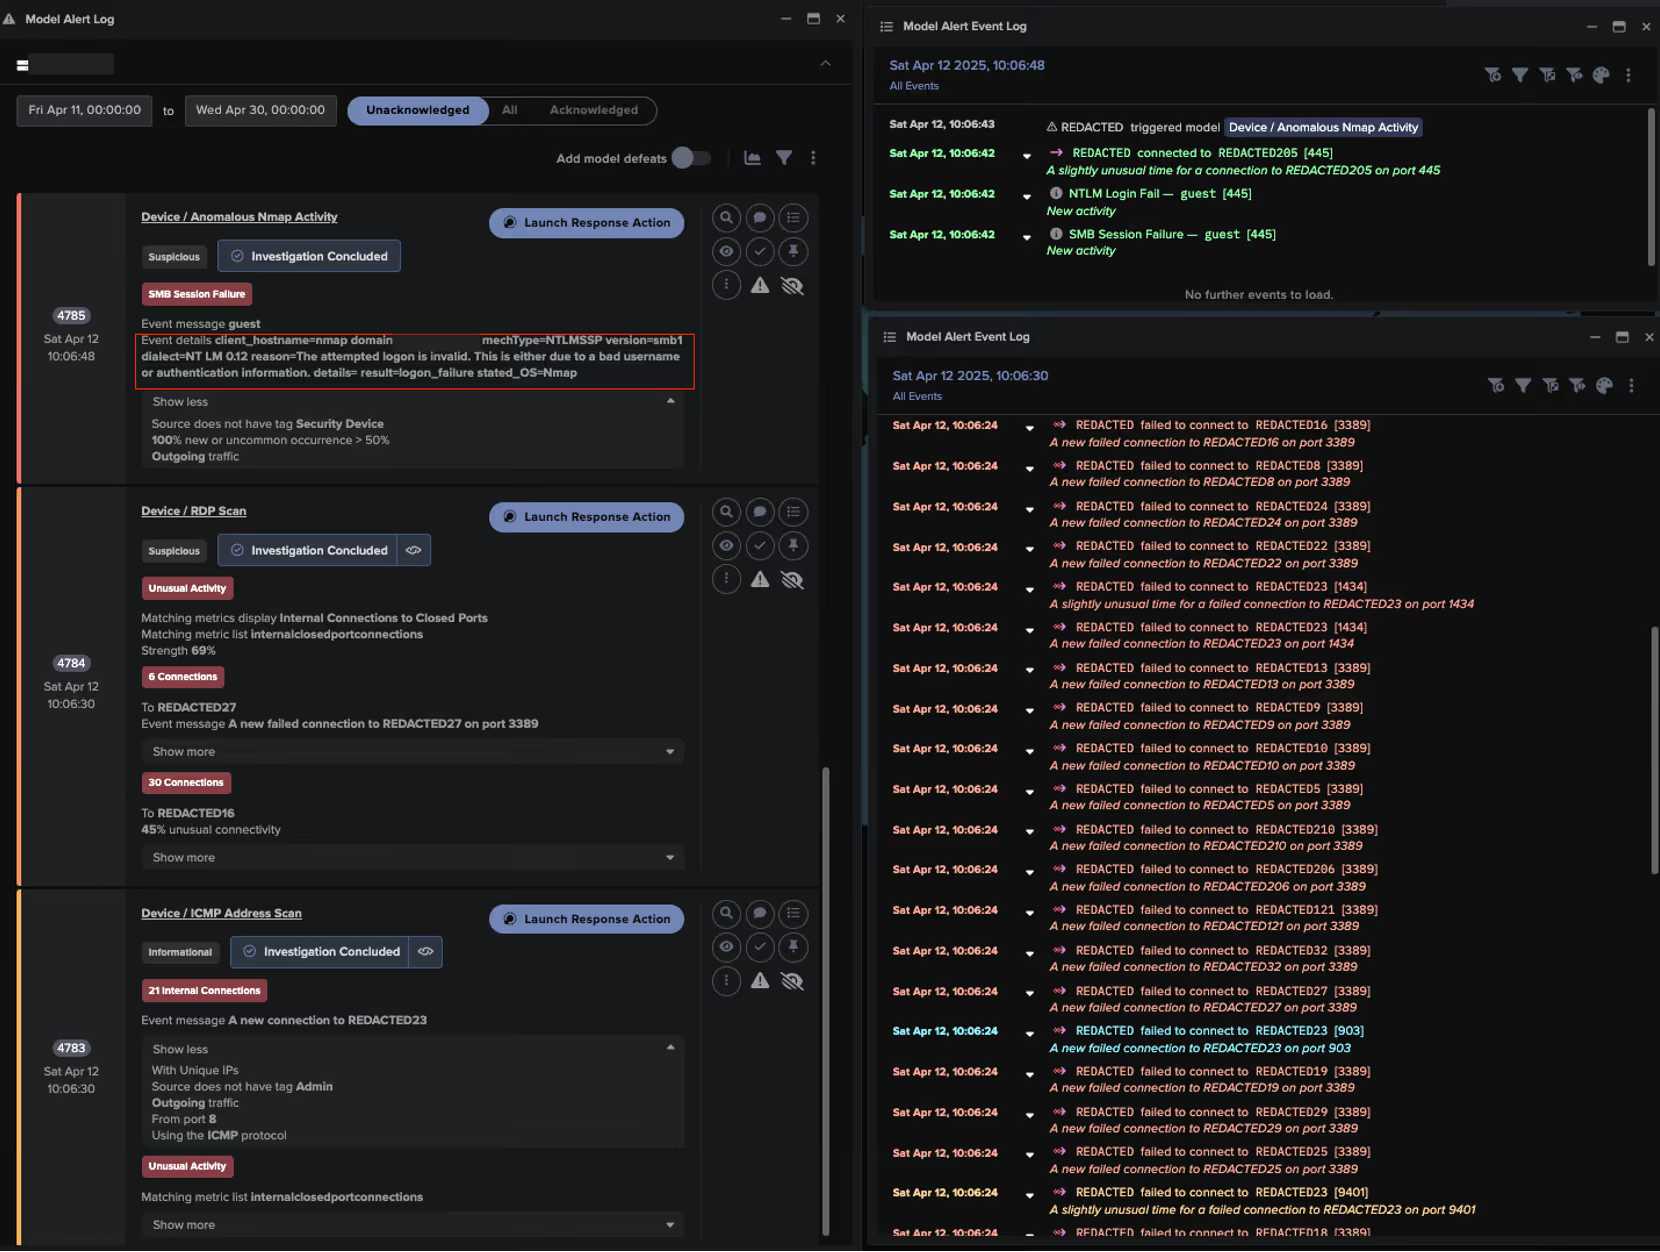
Darktrace’s detection of unusual network scanning activities on the affected device.
Figure 2: Darktrace’s detection of unusual network scanning activities on the affected device.

Around the same time, Darktrace began detecting anomalous activity on a second device, specifically an internal firewall interface device. This suggested that the attacker had established a secondary foothold and was leveraging it to conduct deeper reconnaissance and move laterally through the network.

In an effort to maintain persistence within the network, the attackers likely deployed symbolic links in the SSL-VPN language file directory on the Fortinet device. While Darktrace did not directly observe symbolic link abuse, Fortinet has identified this as a known persistence technique in similar attacks [2][3]. Based on the observed post-exploitation behavior and likely firewall modifications, it is plausible that such methods were used here.

Phase 3: Internal Reconnaissance & Credential Abuse

With lateral movement initiated from the internal firewall interface device, the threat actor proceeded to escalate their efforts to map the internal network and identify opportunities for privilege escalation.

Darktrace observed a successful NTLM authentication from the internal firewall interface to the domain controller over the outdated protocol SMBv1, using the account ‘anonymous’. This was immediately followed by a failed NTLM session connection using the hostname ‘nmap’, further indicating the use of Nmap for enumeration and brute-force attempts. Additional credential probes were also identified around the same time, including attempts using the credential ‘guest’.
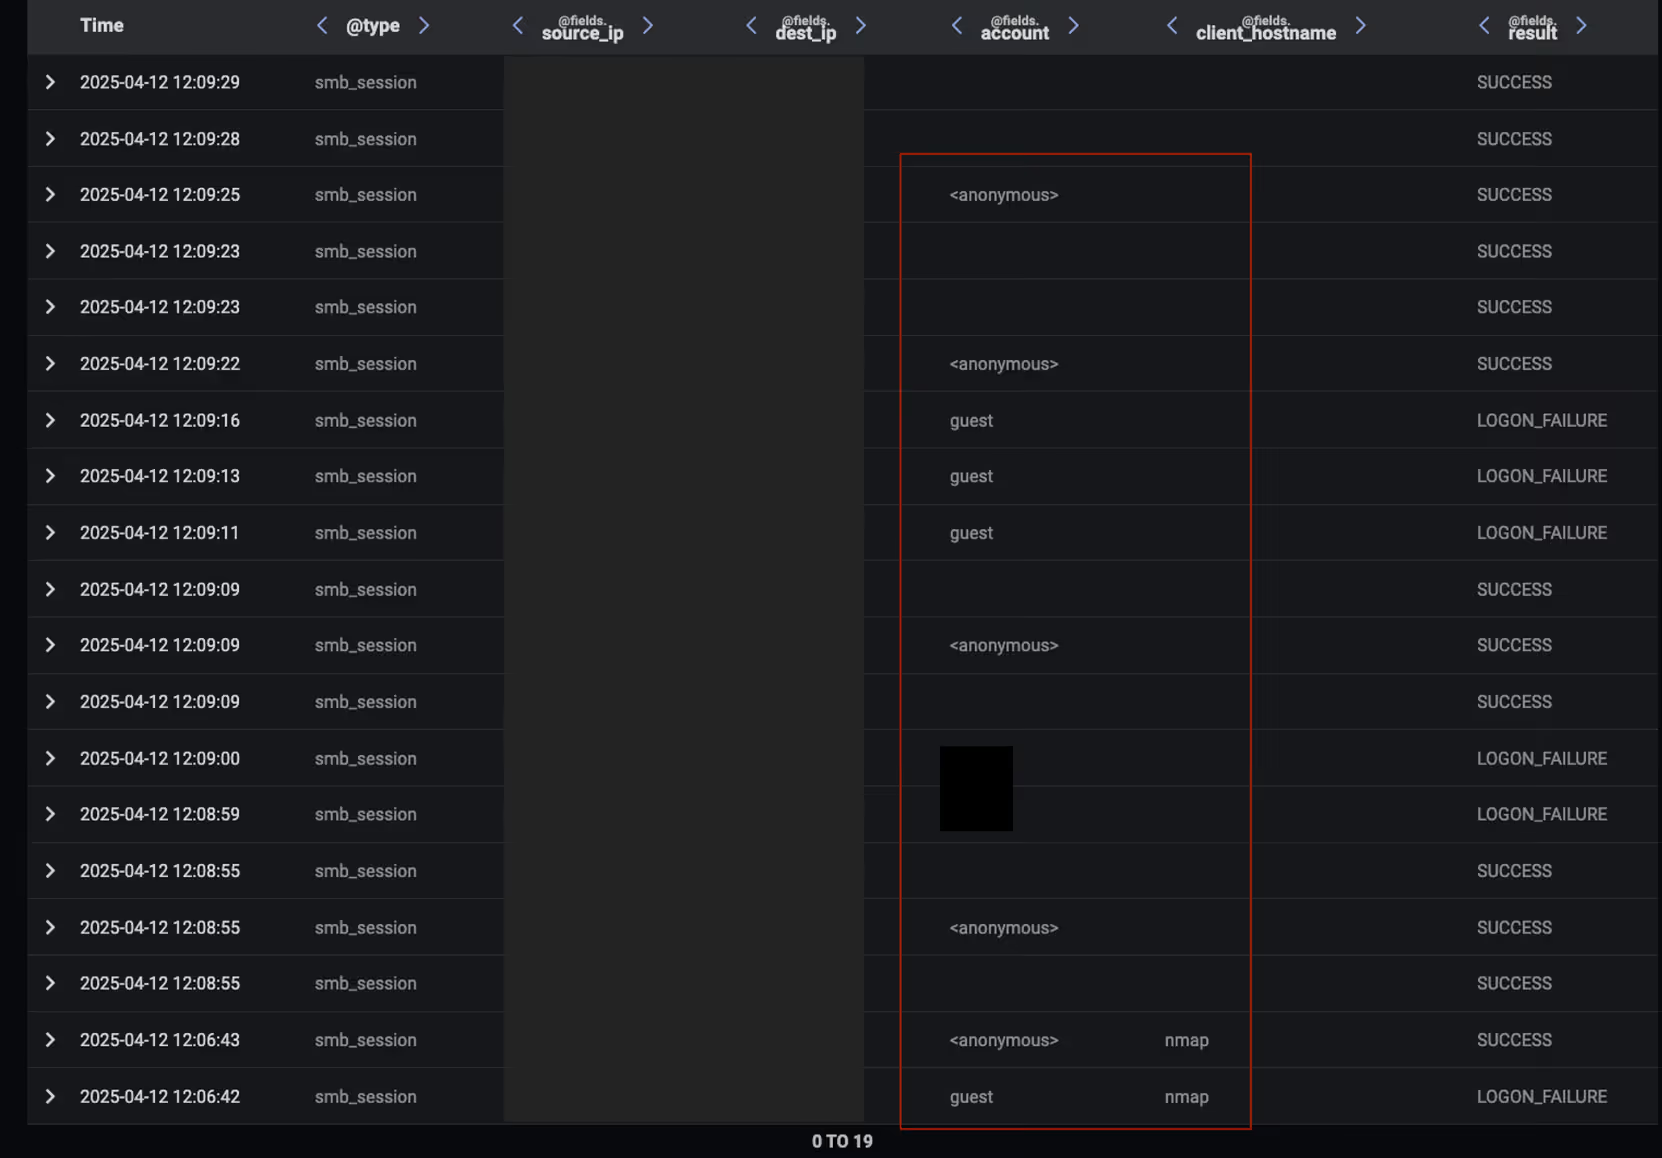
Darktrace detection of a series of login attempts using various credentials, with a mix of successful and unsuccessful attempts.
Figure 3: Darktrace detection of a series of login attempts using various credentials, with a mix of successful and unsuccessful attempts.

The attacker then initiated DCE_RPC service enumeration, with over 300 requests to the Endpoint Mapper endpoint on the domain controller. This technique is commonly used to discover available services and their bindings, often as a precursor to privilege escalation or remote service manipulation.

Over the next few minutes, Darktrace detected more than 1,700 outbound connections from the internal firewall interface device to one of the customer’s subnets. These targeted common services such as FTP (port 21), SSH (22), Telnet (23), HTTP (80), and HTTPS (443). The threat actor also probed administrative and directory services, including ports 135, 137, 389, and 445, as well as remote access via RDP on port 3389.

Further signs of privilege escalation attempts were observed with the detection of over 300 Netlogon requests to the domain controller. Just over half of these connections were successful, indicating possible brute-force authentication attempts, credential testing, or the use of default or harvested credentials.

Netlogon and DCE-RPC activity from the affected device, showing repeated service bindings to epmapper and Netlogon, followed by successful and failed NetrServerAuthenticate3 attempts.
Figure 4: Netlogon and DCE-RPC activity from the affected device, showing repeated service bindings to epmapper and Netlogon, followed by successful and failed NetrServerAuthenticate3 attempts.

Phase 4: Privilege Escalation & Remote Access

A few minutes later, the attacker initiated an RDP session from the internal firewall interface device to an internal server. The session lasted over three hours, during which more than 1.5MB of data was uploaded and over 5MB was downloaded.

Notably, no RDP cookie was observed during this session, suggesting manual access, tool-less exploitation, or a deliberate attempt to evade detection. While RDP cookie entries were present on other occasions, none were linked to this specific session—reinforcing the likelihood of stealthy remote access.

Additionally, multiple entries during and after this session show SSL certificate validation failures on port 3389, indicating that the RDP connection may have been established using self-signed or invalid certificates, a common tactic in unauthorized or suspicious remote access scenarios.

Darktrace’s detection of an RDP session from the firewall interface device to the server, lasting over 3 hours.
Figure 5: Darktrace’s detection of an RDP session from the firewall interface device to the server, lasting over 3 hours.

Darktrace Autonomous Response

Throughout the course of this attack, Darktrace’s Autonomous Response capability was active on the customer’s network. This enabled Darktrace to autonomously intervene by blocking specific connections and ports associated with the suspicious activity, while also enforcing a pre-established “pattern of life” on affected devices to ensure they were able to continue their expected business activities while preventing any deviations from it. These actions were crucial in containing the threat and prevent further lateral movement from the compromised device.

Darktrace’s Autonomous Response targeted specific connections and restricted affected devices to their expected patterns of life.
Figure 6: Darktrace’s Autonomous Response targeted specific connections and restricted affected devices to their expected patterns of life.

Conclusion

This incident highlights the importance of important staying on top of patching and closely monitoring VPN infrastructure, especially for internet-facing systems like Fortinet devices. Despite available patches, attackers were still able to exploit known vulnerabilities to gain access, move laterally and maintain persistence within the customer’s network.

Attackers here demonstrated a high level of stealth and persistence. Not only did they gain access to the network and carry out network scans and lateral movement, but they also used techniques such as symbolic link abuse, credential probing, and RDP sessions without cookies to avoid detection.  Darktrace’s detection of the post-exploitation activity, combined with the swift action of its Autonomous Response technology, successfully blocked malicious connections and contained the attack before it could escalate

Credit to Priya Thapa (Cyber Analyst), Vivek Rajan (Cyber Analyst), and Ryan Traill (Analyst Content Lead)

Appendices

Real-time Detection Model Alerts

·      Device / Suspicious SMB Scanning Activity

·      Device / Anomalous Nmap Activity

·      Device / Network Scan

·      Device / RDP Scan

·      Device / ICMP Address Scan

Autonomous Response Model Alerts:  

·      Antigena / Network / Insider Threat / Antigena Network Scan Block

·       Antigena / Network / Significant Anomaly / Antigena Significant Anomaly from Client Block

MITRE ATT&CK Mapping

Initial Access – External Remote Services – T1133

Initial Access – Valid Accounts – T1078

Execution – Exploitation for Client Execution – T1203

Persistence – Account Manipulation – T1098

Persistence – Application Layer Protocol – T1071.001

Privilege Escalation – Exploitation for Privilege Escalation – T1068

Privilege Escalation – Valid Accounts – T1078

Defense Evasion – Masquerading – T1036

Credential Access – Brute Force – T1110

Discovery – Network Service Scanning – T1046

Discovery – Remote System Discovery – T1018

Lateral Movement – Remote Services – T1021

Lateral Movement – Software Deployment Tools – T1072

Collection – Data from Local System – T1005

Collection – Data Staging – T1074

Exfiltration – Exfiltration Over Alternative Protocol – T1048

References

[1]  https://www.tenable.com/blog/cve-2024-21762-critical-fortinet-fortios-out-of-bound-write-ssl-vpn-vulnerability

[2] https://thehackernews.com/2025/04/fortinet-warns-attackers-retain.html

[3] https://www.cisa.gov/news-events/alerts/2025/04/11/fortinet-releases-advisory-new-post-exploitation-technique-known-vulnerabilities

[4] https://www.fortiguard.com/psirt/FG-IR-24-015

[5] https://www.tenable.com/blog/cve-2023-27997-heap-based-buffer-overflow-in-fortinet-fortios-and-fortiproxy-ssl-vpn-xortigate

[6]  https://www.tenable.com/blog/cve-2022-42475-fortinet-patches-zero-day-in-fortios-ssl-vpns

[7] https://www.fortiguard.com/encyclopedia/ips/12475

The content provided in this blog is published by Darktrace for general informational purposes only and reflects our understanding of cybersecurity topics, trends, incidents, and developments at the time of publication. While we strive to ensure accuracy and relevance, the information is provided “as is” without any representations or warranties, express or implied. Darktrace makes no guarantees regarding the completeness, accuracy, reliability, or timeliness of any information presented and expressly disclaims all warranties.

Nothing in this blog constitutes legal, technical, or professional advice, and readers should consult qualified professionals before acting on any information contained herein. Any references to third-party organizations, technologies, threat actors, or incidents are for informational purposes only and do not imply affiliation, endorsement, or recommendation.

Darktrace, its affiliates, employees, or agents shall not be held liable for any loss, damage, or harm arising from the use of or reliance on the information in this blog.

The cybersecurity landscape evolves rapidly, and blog content may become outdated or superseded. We reserve the right to update, modify, or remove any content without notice.

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Priya Thapa
Cyber Analyst

More in this series

No items found.

Blog

/

/

October 5, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

October 5, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

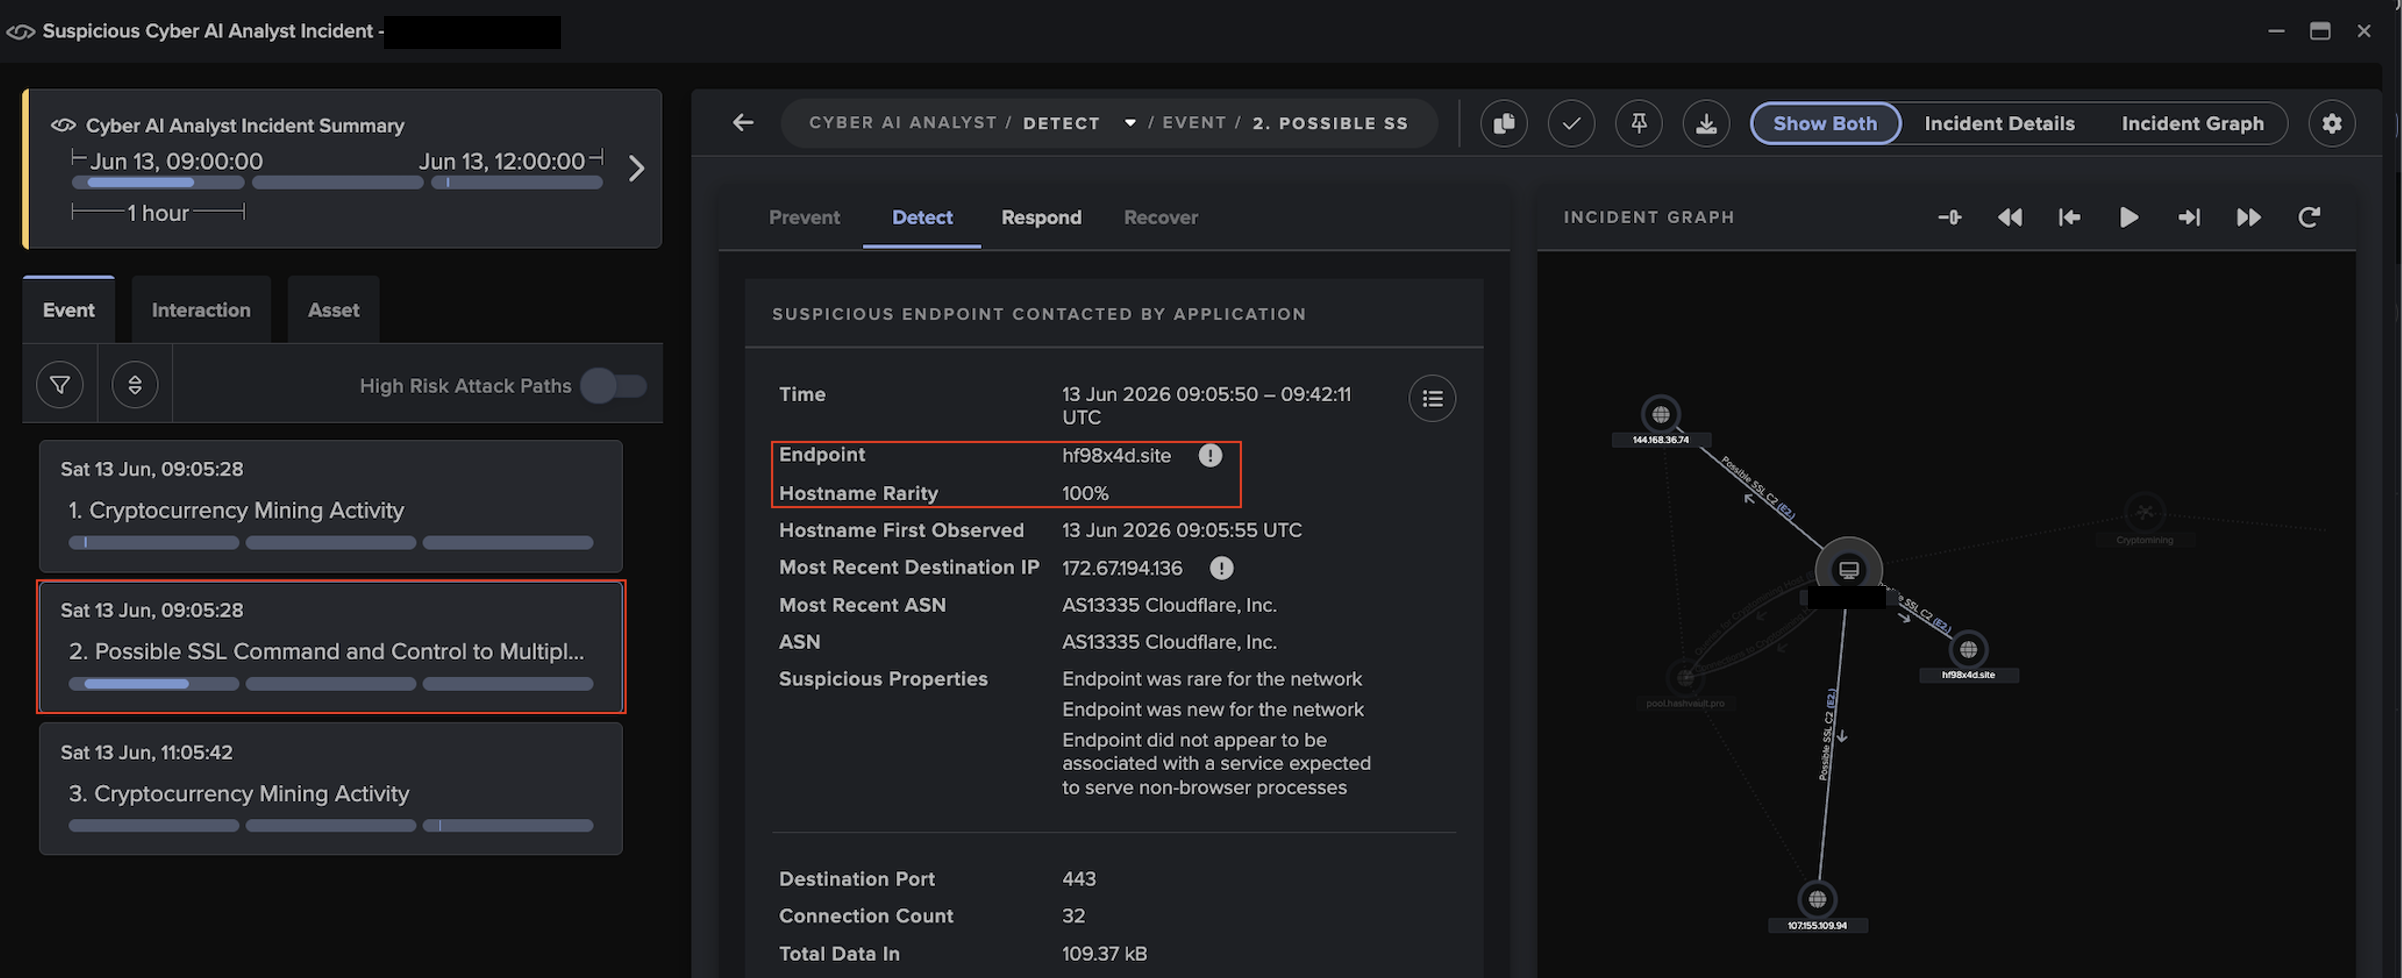
Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

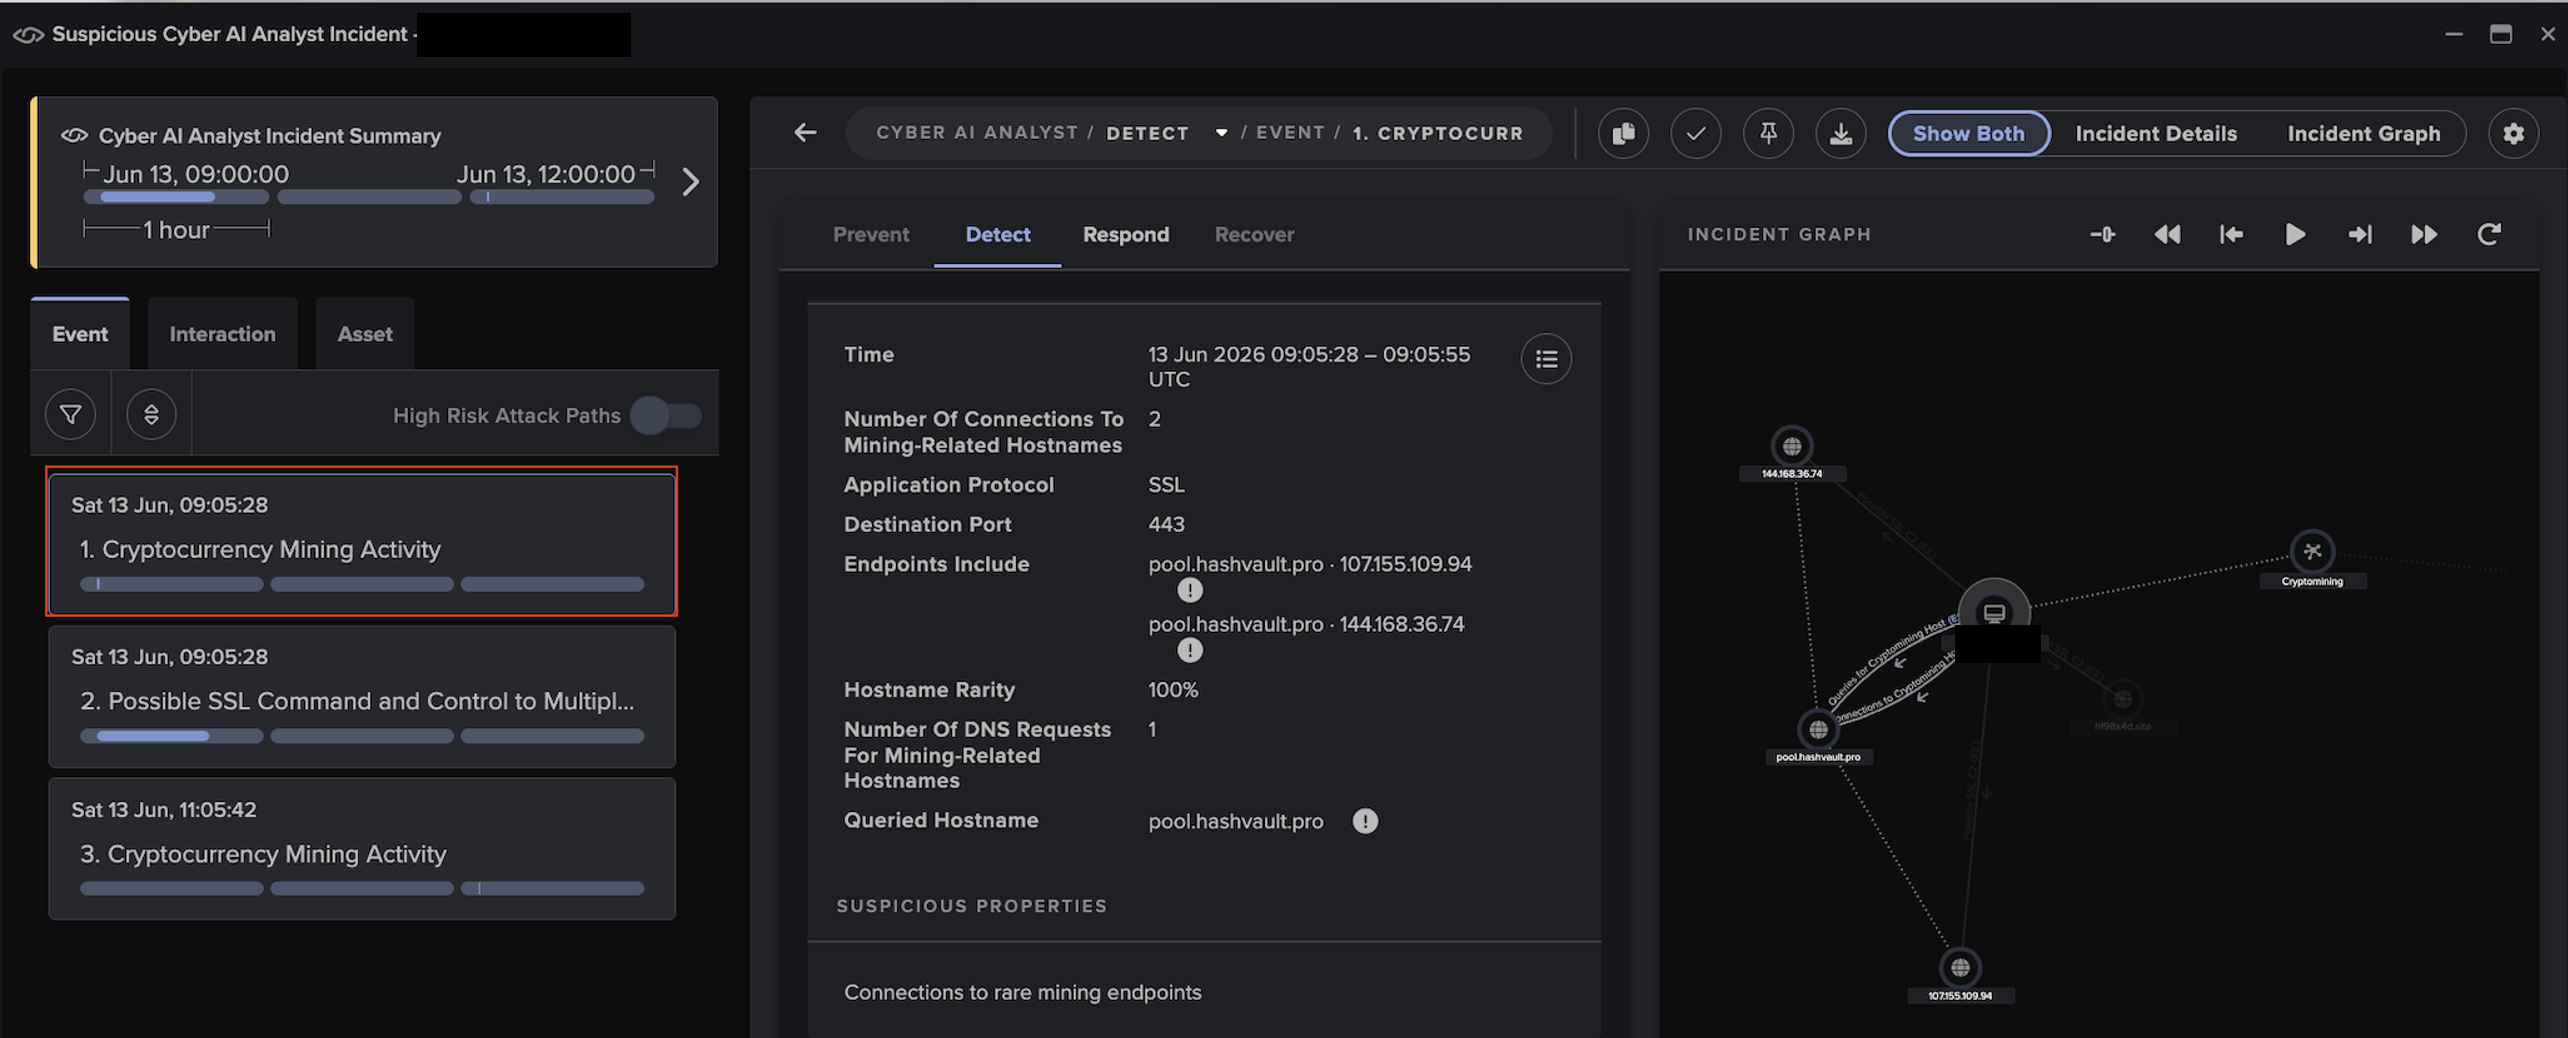
Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

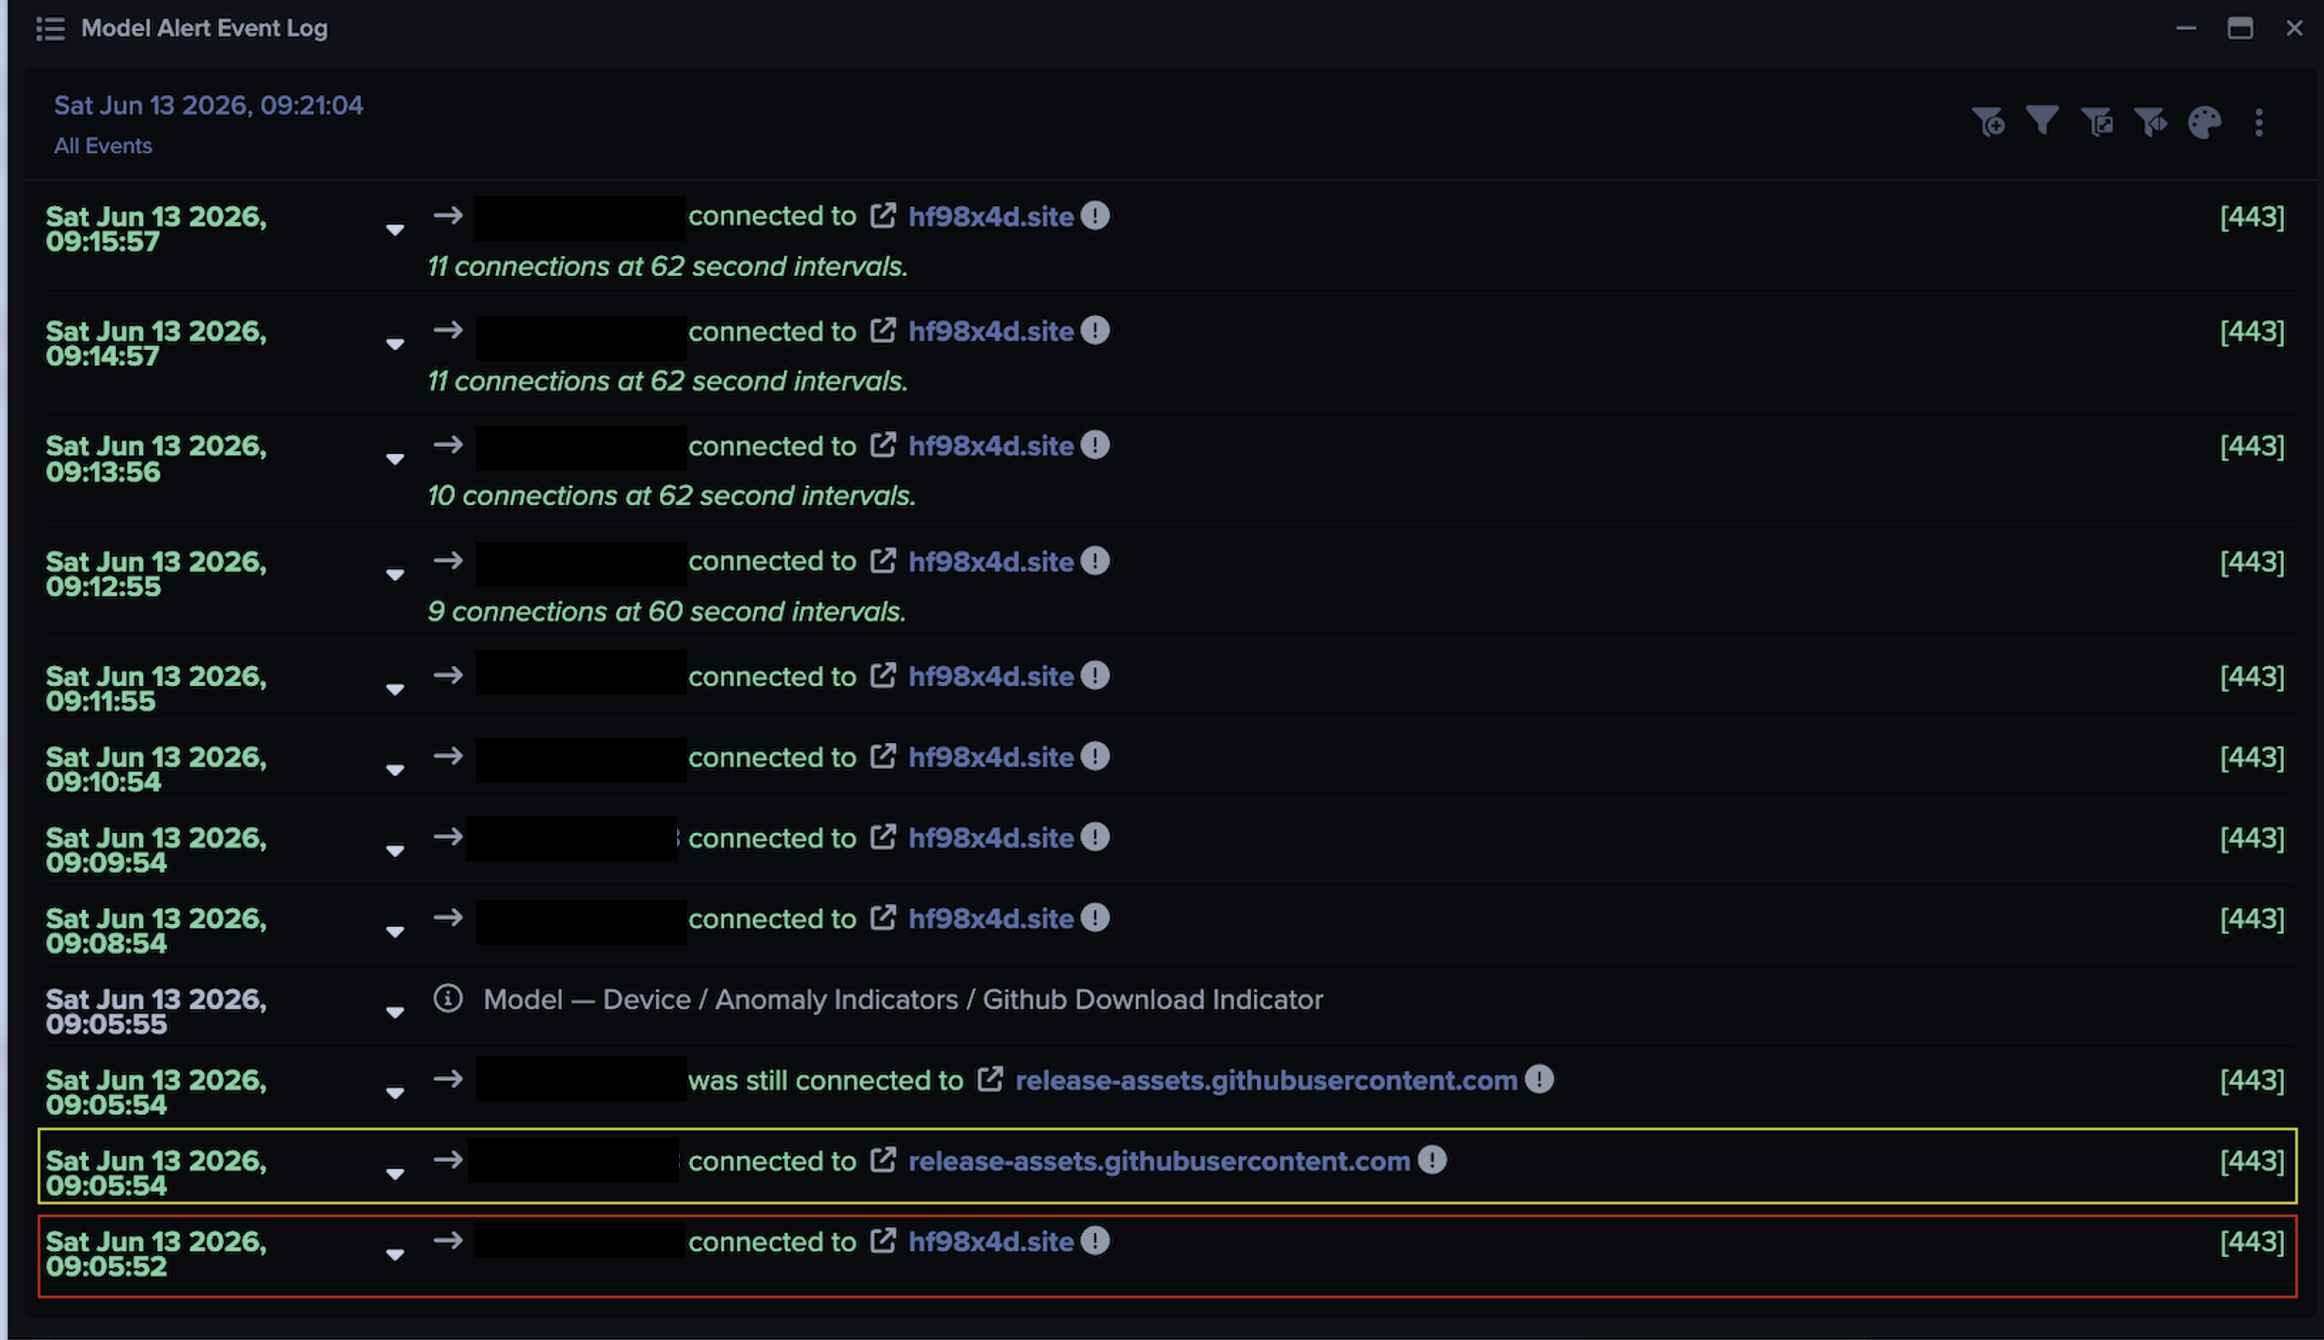
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
Your data. Our AI.
Elevate your network security with Darktrace AI