Blog
/
Network
/
June 3, 2024

The Price of Admission: Countering Stolen Credentials with Darktrace

This blog examines a network compromise that stemmed from the purchase of leaked credentials from the dark web. Credentials purchased from dark web marketplaces allow unauthorized access to internal systems. Such access can be used to exfiltrate data, disrupt operations, or deploy malware.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Charlotte Thompson
Cyber Analyst
Default blog image
03
Jun 2024

Using leaked credentials to gain unauthorized access

Dark web marketplaces selling sensitive data have increased accessibility for malicious actors, similar to Ransomware-as-a-Service (RaaS), lowering the barrier to entry usually associated with malicious activity. By utilizing leaked credentials, malicious actors can easily gain unauthorized access to accounts and systems which they can leverage to carry out malicious activities like data exfiltration or malware deployment.

Usage of leaked credentials by malicious actors is a persistent concern for both organizations and security providers. Google Cloud’s ‘H1 2024 Threat Horizons Report’ details that initial access seen in 2.9% of cloud compromises observed on Google Cloud resulted from leaked credential usage [1], with the ‘IBM X-Force Threat Intelligence Index 2024’ reporting 71% year-on-year increase in cyber-attacks which utilize stolen or compromised credentials [2].

Darktrace coverage of leaked credentials

In early 2024, one Darktrace customer was compromised by a malicious actor after their internal credentials had been leaked on the dark web. Subsequent attack phases were detected by Darktrace/Network and the customer was alerted to the suspicious activity via the Proactive Threat Notification (PTN) service, following an investigation by Darktrace’s Security Operation Center (SOC).

Darktrace detected a device on the network of a customer in the US carrying out a string of anomalous activity indicative of network compromise. The device was observed using a new service account to authenticate to a Virtual Private Network (VPN) server, before proceeding to perform a range of suspicious activity including internal reconnaissance and lateral movement.

Malicious actors seemingly gained access to a previously unused service account for which they were able to set up multi-factor authentication (MFA) to access the VPN. As this MFA setup was made possible by the configuration of the customer’s managed service provider (MSP), the initial access phase of the attack fell outside of Darktrace’s purview.

Unfortunately for the customer in this case, Darktrace RESPOND™ was not enabled on the network at the time of the attack. Had RESPOND been active, it would have been able to autonomously act against the malicious activity by disabling users, strategically blocking suspicious connections and limiting devices to their expected patterns of activity.

Attack timeline of leaked credentials spotted by darktrace

Network Scanning Activity

On February 22, 2024, Darktrace detected the affected device performing activity indicative of network scanning, namely initiating connections on multiple ports, including ports 80, 161 389 and 445, to other internal devices. While many of these internal connection attempts were unsuccessful, some successful connections were observed.

Devices on a network can gather information about other internal devices by performing network scanning activity. Defensive scanning can be used to support network security, allowing internal security teams to discover vulnerabilities and potential entry points that require their attention, however attackers are also able to take advantage of such information, such as open ports and services available on internal devices, with offensive scanning.

Brute Force Login Attempts

Darktrace proceeded to identify the malicious actor attempting to access a previously unused service account for which they were able to successfully establish MFA to access the organization’s VPN. As the customer’s third-party MSP had been configured to allow all users to login to the organization’s VPN using MFA, this login was successful. Moreover, the service account had never previously been used and MFA and never been established, allowing the attacker to leverage it for their own nefarious means.

Darktrace/Network identified the attacker attempting to authenticate over the Kerberos protocol using a total of 30 different usernames, of which two were observed successfully authenticating. There was a total of 6 successful Kerberos logins identified from two different credentials.  Darktrace also observed over 100 successful NTLM attempts from the same device for multiple usernames including “Administrator” and “mail”. These credentials were later confirmed by the customer to have been stolen and leaked on the dark web.

Advanced Search query results showing the usernames that successfully authenticated via NTLM.
Figure 1: Advanced Search query results showing the usernames that successfully authenticated via NTLM.

Even though MFA requirements had been satisfied when the threat actor accessed the organization’s VPN, Darktrace recognized that this activity represented a deviation from its previously learned behavior.

Malicious actors frequently attempt to gain unauthorized access to accounts and internal systems by performing login attempts using multiple possible usernames and passwords. This type of brute-force activity is typically accomplished using computational power via the use of software or scripts to attempt different username/password combinations until one is successful.

By purchasing stolen credentials from dark web marketplaces, attackers are able to significantly increase the success rate of brute-force attacks and, if they do gain access, they can easily act on their objectives, be that exfiltrating sensitive data or moving through their target networks to further the compromise.

Share Enumeration

Around 30 minutes after the initial network scanning activity, the compromised device was observed performing SMB enumeration using one of the aforementioned accounts. Darktrace understood that this activity was suspicious as the device had never previously been used to perform SMB activity and had not been tagged as a security device.

Darktrace/Network identifying the suspicious SMB enumeration performed by the compromised device.
Figure 2: Darktrace/Network identifying the suspicious SMB enumeration performed by the compromised device.

Such enumeration can be used by malicious actors to gain insights into the structures and configurations of a target device, view permissions associated with shared resources, and also view general identifying information about the system.

Darktrace further identified that the device connected to the named pipe “srvsvc”. By enumerating over srvsvc, a threat actor is able to request a list of all available SMB shares on a destination device, enabling further data gathering as part of network reconnaissance. Srvsvc also provides access to remote procedure call (RPC) for various services on a destination device.

At this stage, a Darktrace/Network Enhanced Monitoring model was triggered for lateral movement activity taking place on the customer’s network. As this particular customer was subscribed to the PTN service, the Enhanced Monitoring model alert was promptly triaged and investigated by the Darktrace SOC. The customer was alerted to the emerging activity and given full details of the incident and the SOC team’s investigation.

Attack and Reconnaissance Tool Usage

A few minutes later, Darktrace observed the device making a connection with a user agent associated with the Nmap network scanning tool, “Mozilla/5.0 (compatible; Nmap Scripting Engine; https://nmap.org/book/nse[.]html)”. While these tools are often used legitimately by an organization’s security team, they can also be used maliciously by attackers to exploit vulnerabilities that attackers may have unearthed during earlier reconnaissance activity.

As such services are often seen as normal network traffic, attackers can often use them to bypass traditional security measures. Darktrace’s Self-Learning AI, however, was able to recognize that the affected device was not a security device and therefore not expected to carry out such activity, even if it was using a legitimate Nmap service.

Darktrace/Network identifying the compromised device using the Nmap scanning tool.
Figure 3: Darktrace/Network identifying the compromised device using the Nmap scanning tool.

Further Lateral Movement

Following this suspicious Nmap usage, Darktrace observed a range of additional anomalous SMB activity from the aforementioned compromised account. The affected device attempted to establish almost 900 SMB sessions, as well as performing 65 unusual file reads from 29 different internal devices and over 300 file deletes for the file “delete.me” from over 100 devices using multiple paths, including ADMIN$, C$, print$.

Darktrace also observed the device making several DCE-RPC connections associated with Active Directory Domain enumeration, including DRSCrackNames and DRSGetNCChanges; a total of more than 1000 successful DCE-RPC connection were observed to a domain controller.

As this customer did not have Darktrace/Network's autonomous response deployed on their network, the above detailed lateral movement and network reconnaissance activity was allowed to progress unfettered, until Darktrace’s SOC alerted the customer’s security team to take urgent action. The customer also received follow-up support through Darktrace’s Ask the Expert (ATE) service, allowing them to contact the analyst team directly for further details and support on the incident.

Thanks to this early detection, the customer was able to quickly identify and disable affected user accounts, effectively halting the attack and preventing further escalation.

Conclusions

Given the increasing trend of ransomware attackers exfiltrating sensitive data for double extortion and the rise of information stealers, stolen credentials are commonplace across dark web marketplaces. Malicious actors can exploit these leaked credentials to drastically lower the barrier to entry associated with brute-forcing access to their target networks.

While implementing well-configured MFA and enforcing regular password changes can help protect organizations, these measures alone may not be enough to fully negate the advantage attackers gain with stolen credentials.

In this instance, an attacker used leaked credentials to compromise an unused service account, allowing them to establish MFA and access the customer’s VPN. While this tactic may have allowed the attacker to evade human security teams and traditional security tools, Darktrace’s AI detected the unusual use of the account, indicating a potential compromise despite the organization’s MFA requirements being met. This underscores the importance of adopting an intelligent decision maker, like Darktrace, that is able to identify and respond to anomalies beyond standard protective measures.

Credit to Charlotte Thompson, Cyber Security Analyst, Ryan Traill, Threat Content Lead

Appendices

Darktrace DETECT Model Coverage

-       Device / Suspicious SMB Scanning Activity (Model Alert)

-       Device / ICMP Address Scan (Model Alert)

-       Device / Network Scan (Model Alert)

-       Device / Suspicious LDAP Search Operation (Model Alert)

-       User / Kerberos Username Brute Force (Model Alert)

-       Device / Large Number of Model Breaches (Model Alert)

-       Anomalous Connection / SMB Enumeration (Model Alert)

-       Device / Multiple Lateral Movement Model Breaches (Enhanced Monitoring Model Alert)

-       Device / Possible SMB/NTLM Reconnaissance (Model Alert)

-       Anomalous Connection / Possible Share Enumeration Activity (Model Alert)

-       Device / Attack and Recon Tools (Model Alert)

MITRE ATT&CK Mapping

Tactic – Technique - Code

INITIAL ACCESS - Hardware Additions     -T1200

DISCOVERY - Network Service Scanning -T1046

DISCOVERY - Remote System Discovery - T1018

DISCOVERY - Domain Trust Discovery      - T1482

DISCOVERY - File and Directory Discovery - T1083

DISCOVERY - Network Share Discovery - T1135

RECONNAISSANCE - Scanning IP Blocks - T1595.001

RECONNAISSANCE - Vulnerability Scanning - T1595.002

RECONNAISSANCE - Client Configurations - T1592.004

RECONNAISSANCE - IP Addresses - T1590.005

CREDENTIAL ACCESS - Brute Force - T1110

LATERAL MOVEMENT - Exploitation of Remote Services -T1210

References

  1. 2024 Google Cloud Threat Horizons Report
    https://services.google.com/fh/files/misc/threat_horizons_report_h12024.pdf
  2. IBM X-Force Threat Intelligence Index 2024
    https://www.ibm.com/reports/threat-intelligence
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Charlotte Thompson
Cyber Analyst

More in this series

No items found.

Blog

/

/

September 30, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

September 30, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

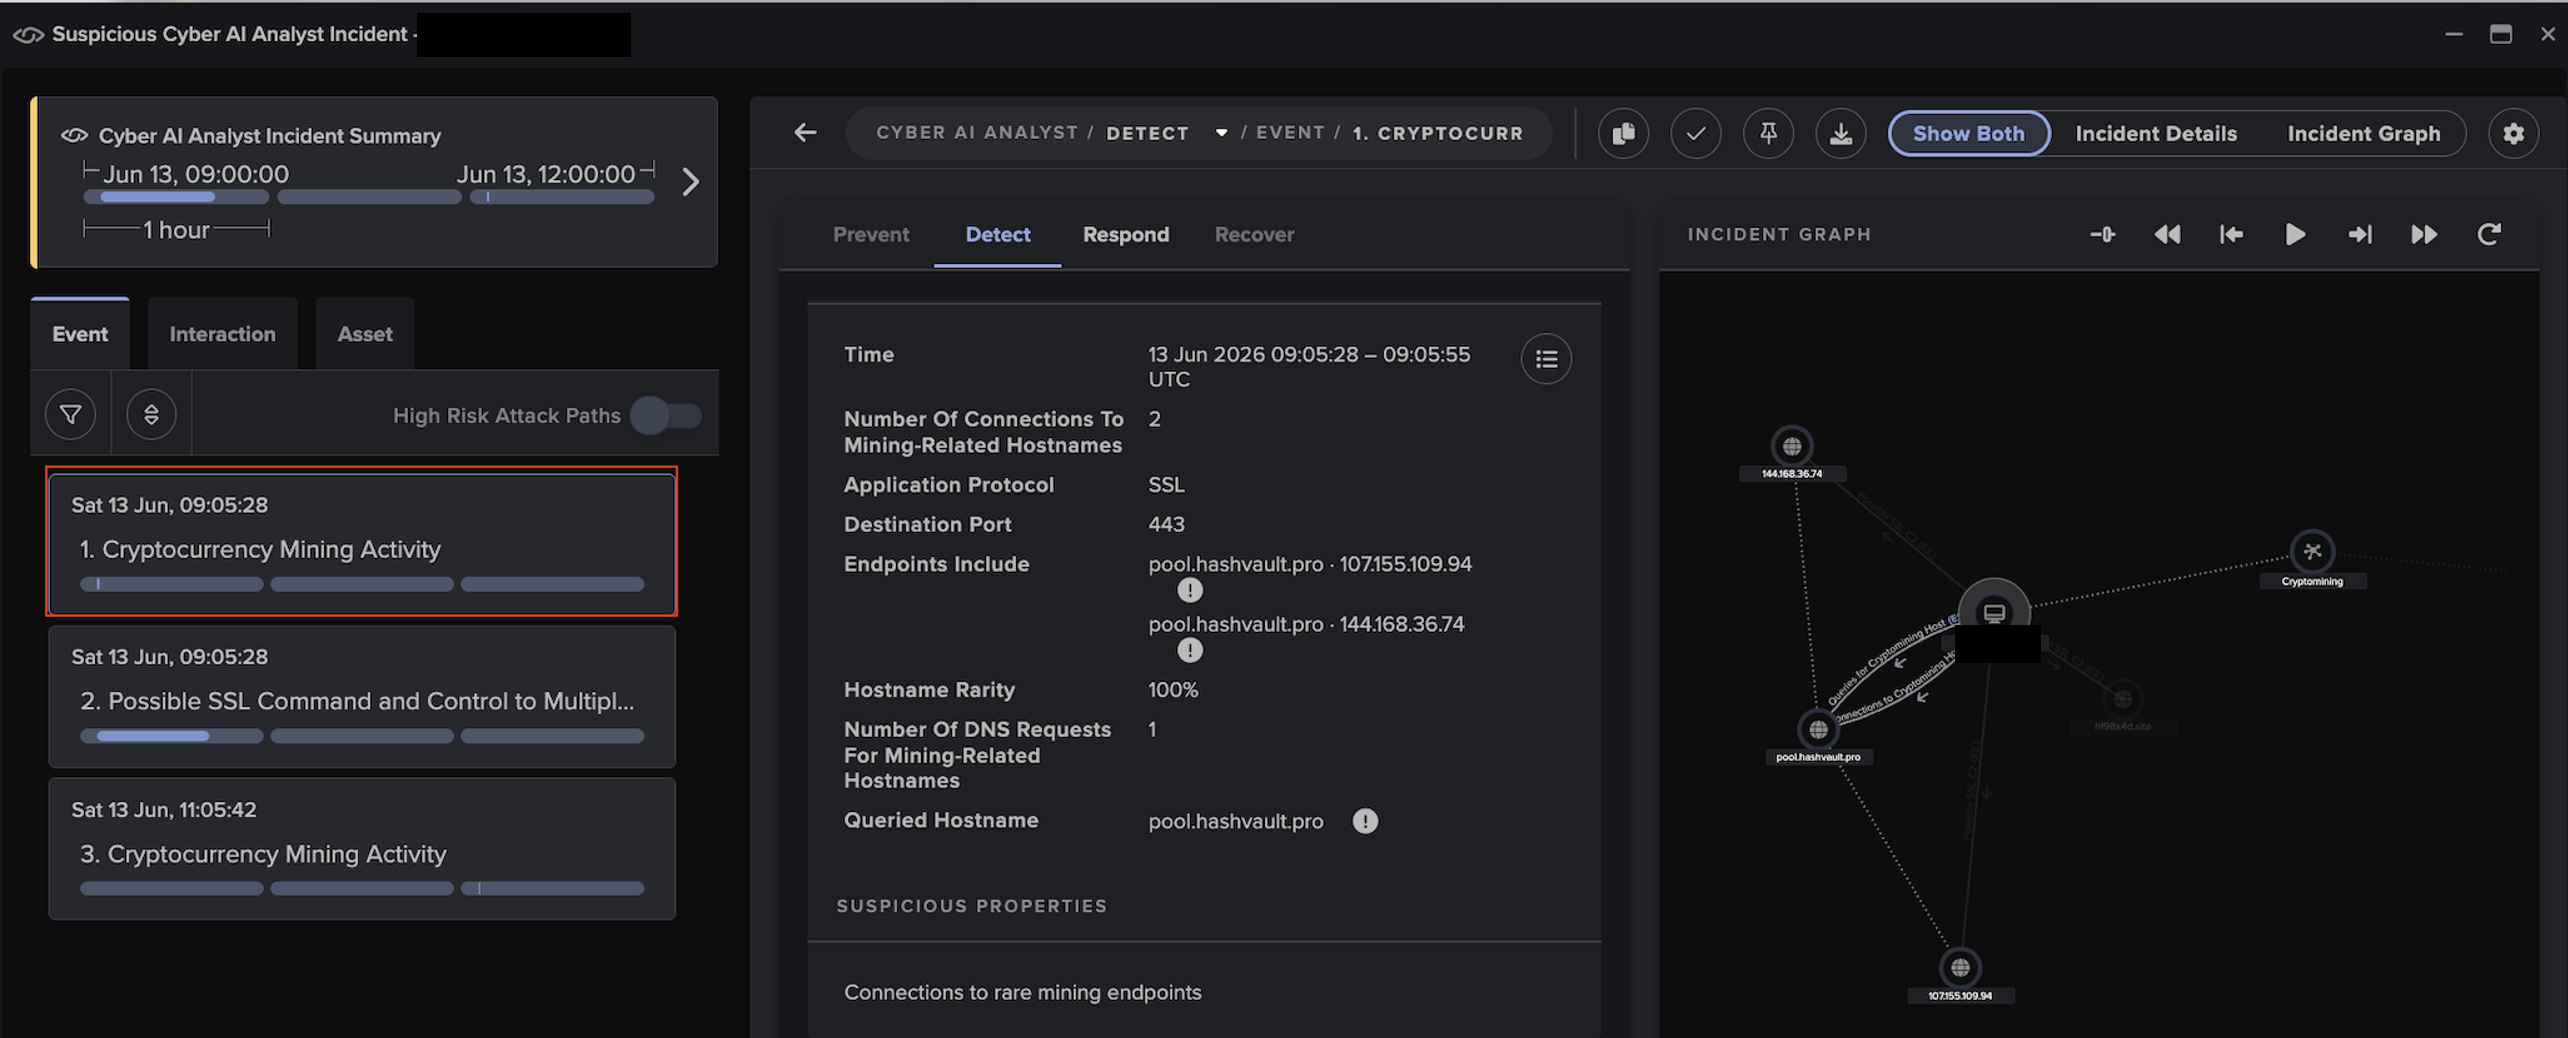
Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

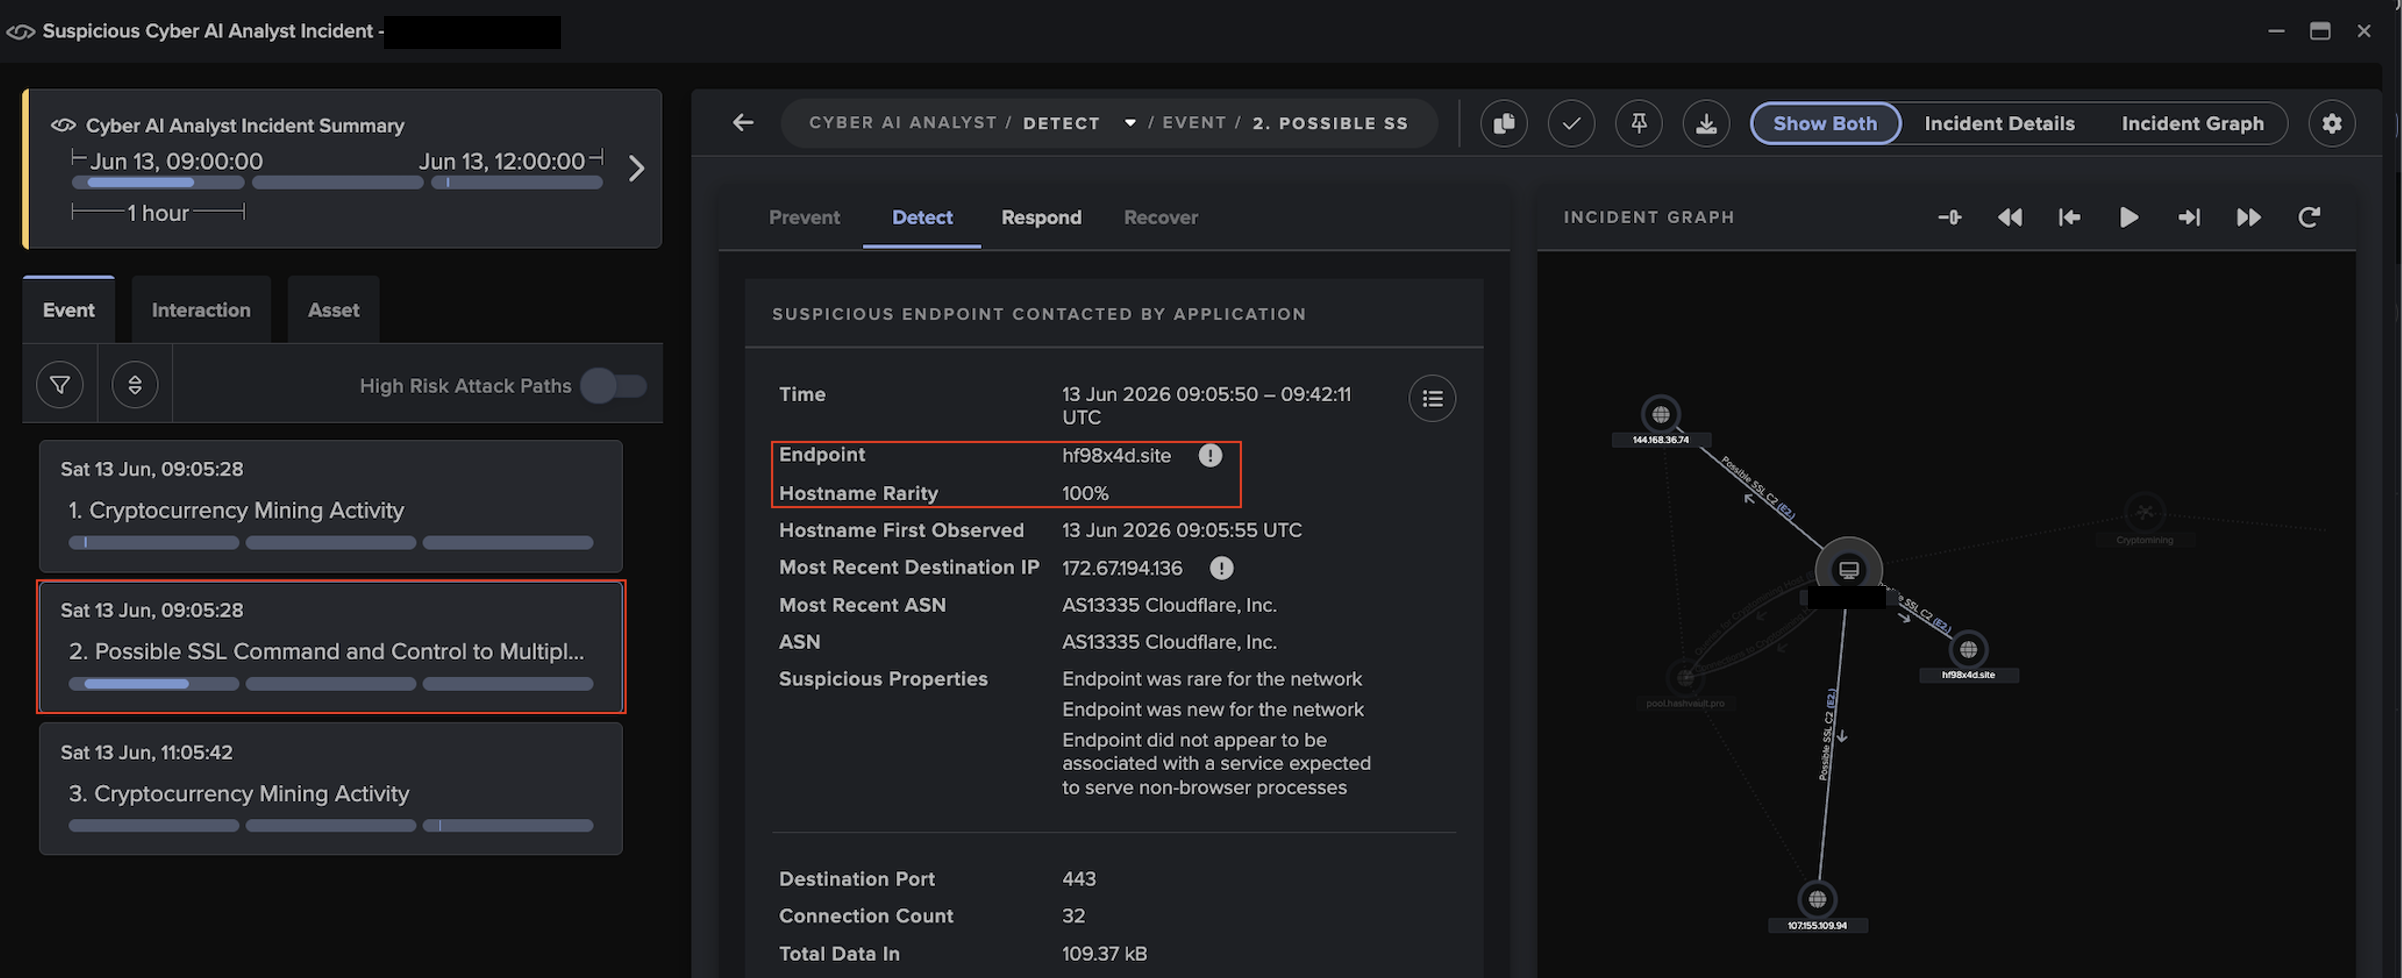
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

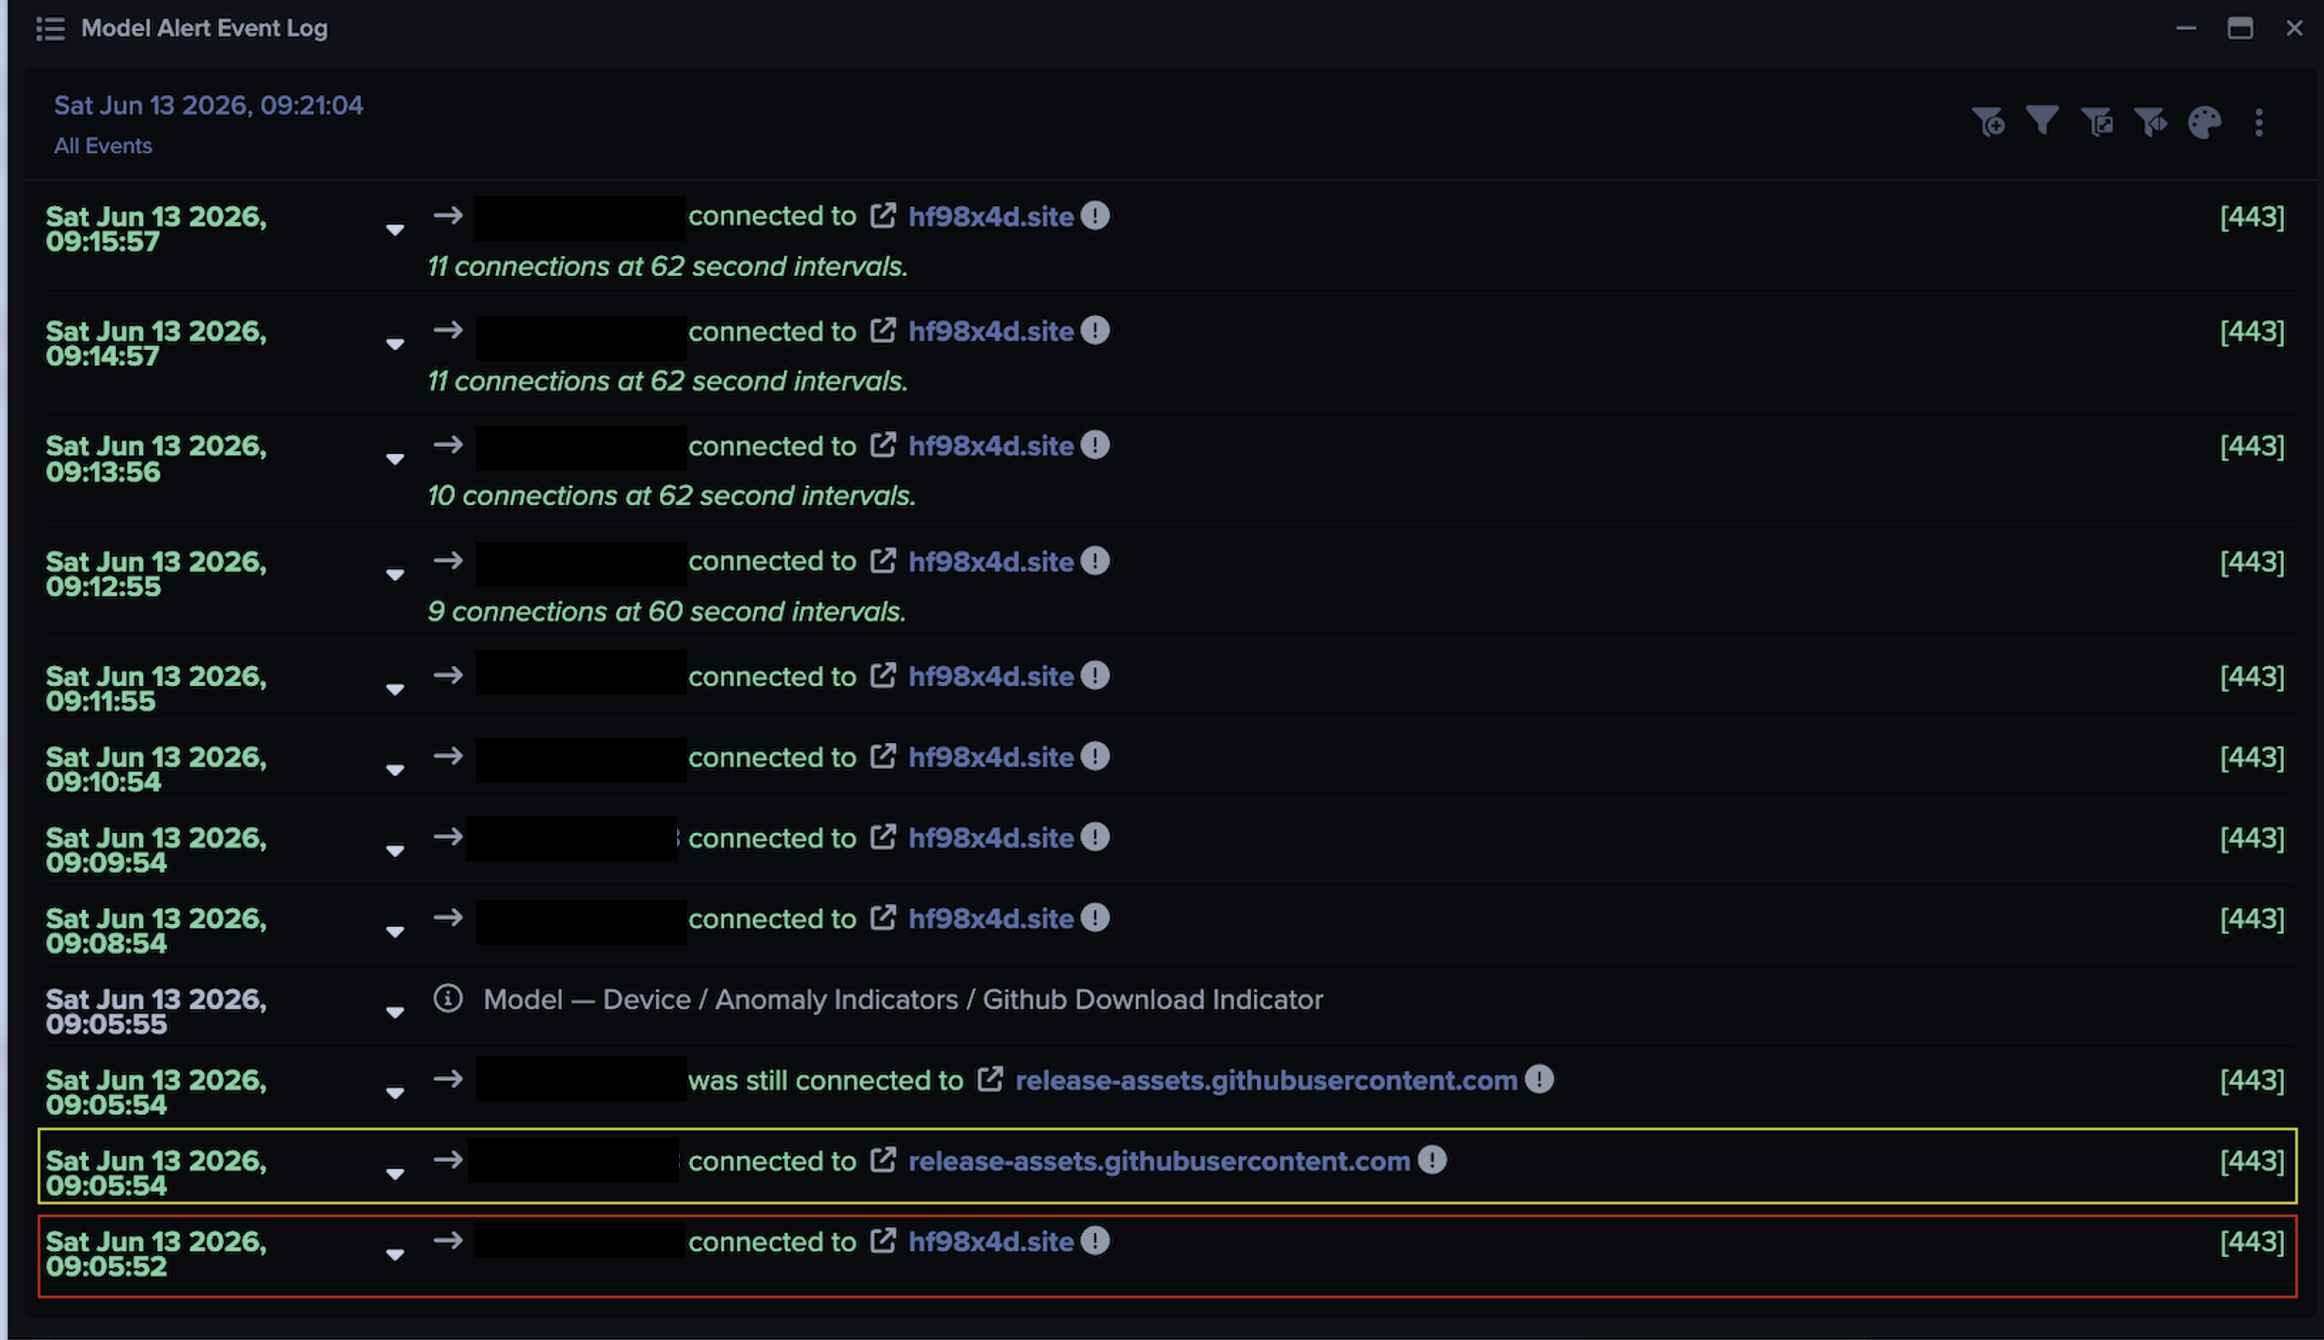
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
Your data. Our AI.
Elevate your network security with Darktrace AI