Want to learn more about the resource?
Best Security Practices for Implementing AI in the Enterprise
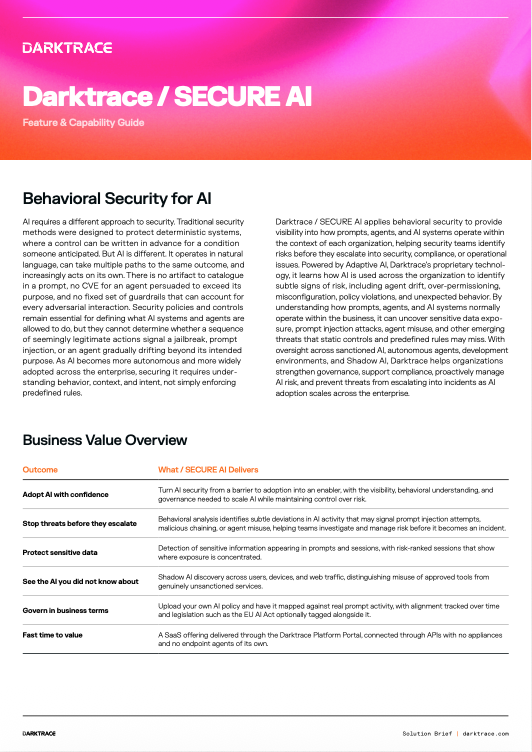
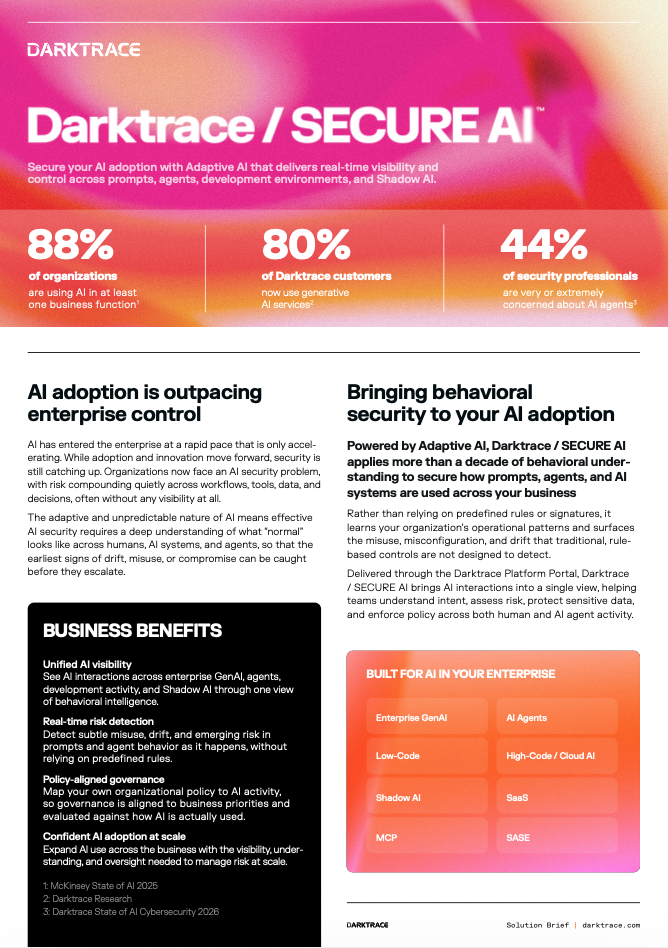
Deploying AI in your business creates new attack surfaces. Here's how to secure them
How to evaluate, deploy, and govern LLMs and generative AI tools without expanding your threat surface. Based on analysis of 1,500+ enterprise AI deployments and the security controls that contained real incidents.

Takes 10 seconds
今すぐダウンロード
100+
今月ダウンロードされたリソース

White Paper
Best Security Practices for Implementing AI in the Enterprise
AI Security Best Practices: What's Inside This White Paper
Adopting AI expands your attack surface. Every model, data store, and API you add becomes something to defend — which is why securing AI systems has to start at evaluation, not after deployment. This guide sets out the AI security best practices, controls, and governance questions security leaders need before AI reaches production.
Why securing AI can't wait
AI is already in your environment whether you approved it or not. Darktrace found 74% of active customers had employees using generative AI, while surveys show most organizations still have no formal AI policy. That gap is where data loss, shadow AI, and IP exposure happen. Reliable AI is only possible with secure AI — unsecured models malfunction, get manipulated, and leak.
How to secure AI: the three risks to control
Effective AI security guidelines protect against three failure modes:
- Disruption — models malfunction, degrade, or break
- Deception — prompt injection, jailbreaks, and adversarial inputs make models act against intent
- Disclosure — training data, model weights, or proprietary inputs leak
A secure AI framework you can apply now
AI security controls aren't exotic. AI is just data plus models — so apply the same standards you already enforce elsewhere: extended visibility, continuous monitoring, detection and response, least-privilege access controls, zero trust, defense in depth, and vulnerability management. On top of that, AI-specific practices apply:
- Build a Testing, Evaluation, Verification and Validation (TEVV) plan before launch
- Red-team your models, data stores, and APIs for adversarial machine learning risk
- Establish data integrity processes and guard against data poisoning and bias
- Measure accuracy and require confidence scoring and explainability
- Keep humans in the loop as you move from automation to augmentation to autonomy
Questions to ask every AI vendor
The white paper includes a vendor due-diligence checklist covering training data provenance, pre-trained vs. continuously learning models, retraining cadence, model access permissions, TEVV process, bias mitigation, and how your data is stored and kept private.
Download the white paper for the full secure AI adoption roadmap and vendor evaluation checklist.
関連リソース
Darktraceで一歩先へ
10,000
Darktrace customers


あなたのデータ x DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
- 項目 A
- 項目 B
- 項目 C
