Blog
/
Network
/
May 23, 2025

Defending the Frontlines: Proactive Cybersecurity in Local Government

To quickly identify and respond to threats before damage occurs, this local government relies on Darktrace to improve network visibility, stop insider threats, protect its email systems, and accelerate incident investigations.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
The Darktrace Community
Default blog image
23
May 2025

Serving a population of over 165,000 citizens, this county government delivers essential services that enhance the quality of life for all of its residents in Florida, United States. From public safety and works to law enforcement, economic development, health, and community services, the county’s cybersecurity strategy plays a foundational role in protecting its citizens.

From flying blind to seeing the bigger picture

Safeguarding data from multiple systems, service providers, and citizens is a key aspect of the County’s Systems Management remit. Protecting sensitive information while enabling smooth engagement with multiple external partners poses a unique challenge; the types of data and potential threats are continuously evolving, but resources – both human and financial – remain consistently tight.

When the Chief Information Officer took on his role in 2024, building out a responsive defense-in-depth strategy was central to achieving these goals. However, with limited resources and complex needs, his small security team was struggling with high alert volumes, inefficient tools, and time-consuming investigations that frequently led nowhere.

Meanwhile, issues like insider threats, Denial of Service (DoS), and phishing attacks were growing; the inefficiencies were creating serious security vulnerabilities. As the CIO put it, he was flying blind. With so much data coming in, security analysts were in danger of missing the bigger picture.

“We would just see a single portion of data that could send us down a rabbit hole, thinking something’s going on – only to find out after spending days, weeks, or even months that it was nothing. If you’re only seeing one piece of the issue, it’s really difficult to identify whether something is a legitimate threat or a false positive.”

Local government’s unique cybersecurity challenges

According to the CIO, even with a bigger team, aligning and comparing all the data into a comprehensive, bigger picture would be a major challenge. “The thing about local government specifically is that it’s a complex security environment. We bring together a lot of different individuals and organizations, from construction workers to people who bring projects into our community to better the County. What we work with varies from day to day.”

The challenge wasn’t just about identifying threats, but also about doing so quickly enough to respond before damage was done. The CIO said this was particularly concerning when dealing with sophisticated threats: “We’re dealing with nation-state attackers nowadays, as opposed to ‘script kiddies.’ There’s no time to lose. We’ve got to have cybersecurity that can respond as quickly as they can attack.”

To achieve this, among the most critical challenges the CIO and his team needed to address were:

  • Contextual awareness and visibility across the network: The County team lacked the granular visibility needed to identify potentially harmful behaviors. The IT team needed a tool that uncovered hidden activities and provided actionable insights, with minimal manual intervention.
  • Augmenting human expertise and improving response times: Hiring additional analysts to monitor the environment is prohibitively expensive for many local governments. The IT team needed a cybersecurity solution that could augment existing skills while automating day-to-day tasks. More effective resource allocation would drive improved response times.
  • Preventing email-based threats: Phishing and malicious email links present a persistent threat. The County team needed a way to flag, identify, and hold suspicious messages automatically and efficiently. Given the team’s public service remit, contextual awareness is crucial to ensuring that no legitimate communications are accidentally blocked. Accuracy is extremely important.
  • Securing access and managing insider threats: Having already managed insider threats posed by former staff members, the IT team wanted to adopt a more proactive, deterrent-based approach towards employee IT resource use, preventing incidents before they could occur.

Proactive cybersecurity

Recognizing these challenges, the CIO and County sought AI-driven solutions capable of acting autonomously to support a lean IT team and give the big picture view needed, without getting lost in false positive alerts.

Ease of deployment was another key requirement: the CIO wanted to quickly establish a security baseline for County that would not require extensive pre-planning or disrupt existing systems. Having worked with Darktrace in previous roles, he knew the solution had the capacity to make the critical connections he was looking for, while delivering fast response times and reducing the burden on security teams.

When every second counts, we want to be as close to the same resources as our attackers are utilizing. We have got to have something that can respond as quickly as they can attack. For the County, that’s Darktrace.” – CIO, County Systems Management Department.

Closing network visibility gaps with Darktrace / NETWORK

The County chose Darktrace / NETWORK for unparalleled visibility into the County’s network. With the solution in place, the CIO and his team were able to identify and address previously hidden activities, uncovering insider threats in unexpected places. For example, one team member had installed an unauthorized anonymizer plug-in on their browser, posing a potentially serious security risk via traffic being sent out to the internet. “Darktrace immediately alerted on it,” said CIO. “We were able to deal with the threat proactively and quickly.”

Darktrace / NETWORK continuously monitored and updated its understanding of the County environment, intelligently establishing the different behaviors and network activity. The end result was a level of context awareness that enabled the team to focus on the alerts that mattered most, saving time and effort.

“Darktrace brings all the data we need together, into one picture. We’re able to see what’s going on at a glance, as opposed to spending time trying to identify real threats from false positives,” said the CIO. The ability to automate actions freed the team up to focus on more complex tasks, with 66% of network response actions being applied autonomously, taking the right action at the right time to stop the earliest signs of threatening activity. This reduced pressure on the County’s team members, while buying valuable containment time to perform deeper investigations.

The agentless deployment advantage

For the CIO, one of the major benefits of Darktrace / NETWORK is that it’s agentless. “Agents alert attackers to the presence of security in your environment, it helps them to understand that there’s something else they need to bring down your defenses,” he said. Using Darktrace to mirror network traffic, the County can maintain full visibility across all network entities without alerting attackers and respond to threatening activity at machine speed. “It allows me to sleep better at night, knowing that this tool can effectively unplug the network cable from that device and bring it offline,” said CIO.

Streamlining investigations with Darktrace Cyber AI Analyst

For lean security teams, contextual awareness is crucial in reducing the burden of alert fatigue. Using Cyber AI Analyst, the County team is able to take the pressure off, automatically investigating every relevant event, and reducing thousands of individual alerts to only a small number of incidents that require manual review.

For the County team, the benefits are clear: 520 investigation hours saved in one month, with an average of just 11 minutes investigation time per incident. For the CIO, Darktrace goes beyond reducing workloads, it actually drives security: “It identifies threats almost instantly, bringing together logs and behaviors into a single, clear view.”

The efficiency gain has been so significant that the CIO believes Darktrace augments capabilities beyond the size of a team of analysts. “You could have three analysts working around the clock, but it’s hard to bring all those logs and behaviors together in one place and communicate everything in a coordinated way. Nothing does that as quickly as Darktrace can.”

Catching the threats from within: Defense in depth with Darktrace / IDENTITY

One of the key benefits of Darktrace for the County was its breadth of capability and responsiveness. “We’re looking at everything from multi-factor authentication, insider threats, distributed denial of service attacks,” said the CIO. “I’ve worked with other products in the past, but I’ve never found a tool as good as Darktrace.”

Further insider threats uncovered by Darktrace / IDENTITY included insecure access practices. Some users had logins and passwords on shared network resources or in plain-text files. Darktrace alerted the security team and the threats were mitigated before serious damage was done.

Darktrace / IDENTITY gives organizations advanced visibility of application user behavior from unusual authentication, password sprays, account takeover, resource theft, and admin abuse. Security teams can take targeted actions including the forced log-off of a user or temporary disabling of an account to give the team time to verify legitimacy.

First line of defense against the number one attack vector: Enhancing email security with Darktrace / EMAIL

Email-based threats, such as phishing, are among the most common attack vectors in modern cybersecurity, and a key vector for ransomware attacks. Post implementation performance was so strong that the organization now plans to retire other tools, cutting costs without compromising on security.

“Darktrace / EMAIL was one of the first tools that I implemented when I started here,” said CIO. “I really recognize the value of it in our environment.” In addition to detecting and flagging potentially malicious email, the CIO said an unexpected benefit has been the reinforcement of more security-aware behaviors among end users. “People are checking their junk folders now, alerting us and checking to see if something is legitimate or not.”

The CIO said that, unlike traditional email security tools that basically perform only one function, Darktrace has multiple additional capabilities that deliver extra layers of protection compared to one-dimensional alternatives. For example, AI-employee feedback loops leverage insights gained from individual users to not only improve detection rates, but also provide end users with contextual security awareness training, to enhance greater understanding of the risks.

Straightforward integration, ease of use

The County wanted a powerful, responsive solution – without demanding pre-installation or integration needs, and with maximum ease of use. “The integration is relatively painless,” said the CIO. “That’s another real benefit, you can bring Darktrace into your environment and have it up and running faster than you could ever hire additional analysts to look at the same data.”

The team found that, compared to competing products, where there was extensive setup, overhead, and resources, “Darktrace is almost plug-and-play.” According to the CIO, the solution started ingesting information and providing notifications immediately: “You can turn on defense or response mechanisms at a granular level, for email or network – or both at the same time.”

The County sees Darktrace as an integral part of its cybersecurity strategy into the future. “Having worked with Darktrace in the past, it was an easy decision for me to agree to a multi-year partnership,” said the CIO “As we continue to build out our defense-in-depth strategy, the ability to use Darktrace to manage other data sources and identify new, additional behavior will be crucial to our proactive, risk-based approach.”

Darktrace has the capacity to meet the organization’s need for exceptional responsiveness, without burning out teams. “If you’re not overburdening the teams that you do have with significant workloads, they have a lot more agility to deal with things on the fly,” said the CIO.

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
The Darktrace Community

More in this series

No items found.

Blog

/

AI

/

November 2, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

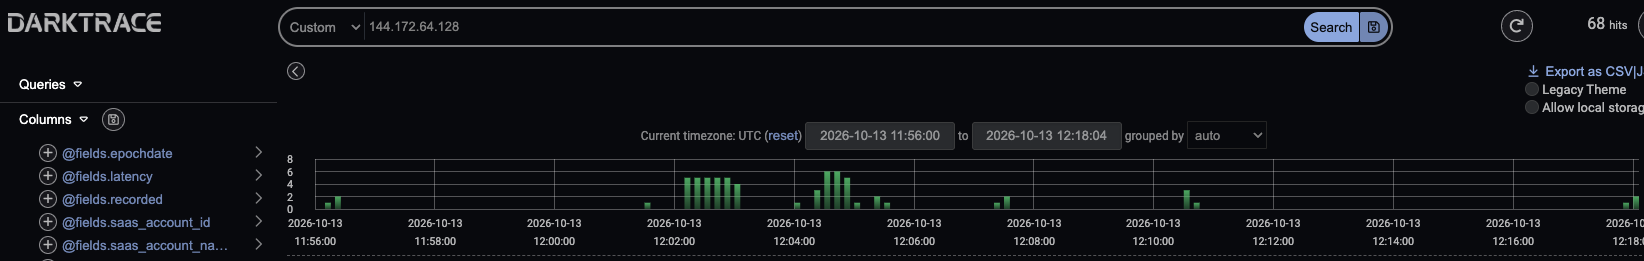
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence

Blog

/

OT

/

November 2, 2026

Beyond the Fridge: Exposed Industrial Control Systems

Default blog imageDefault blog image

Introduction

In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.

The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.

The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].

Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.

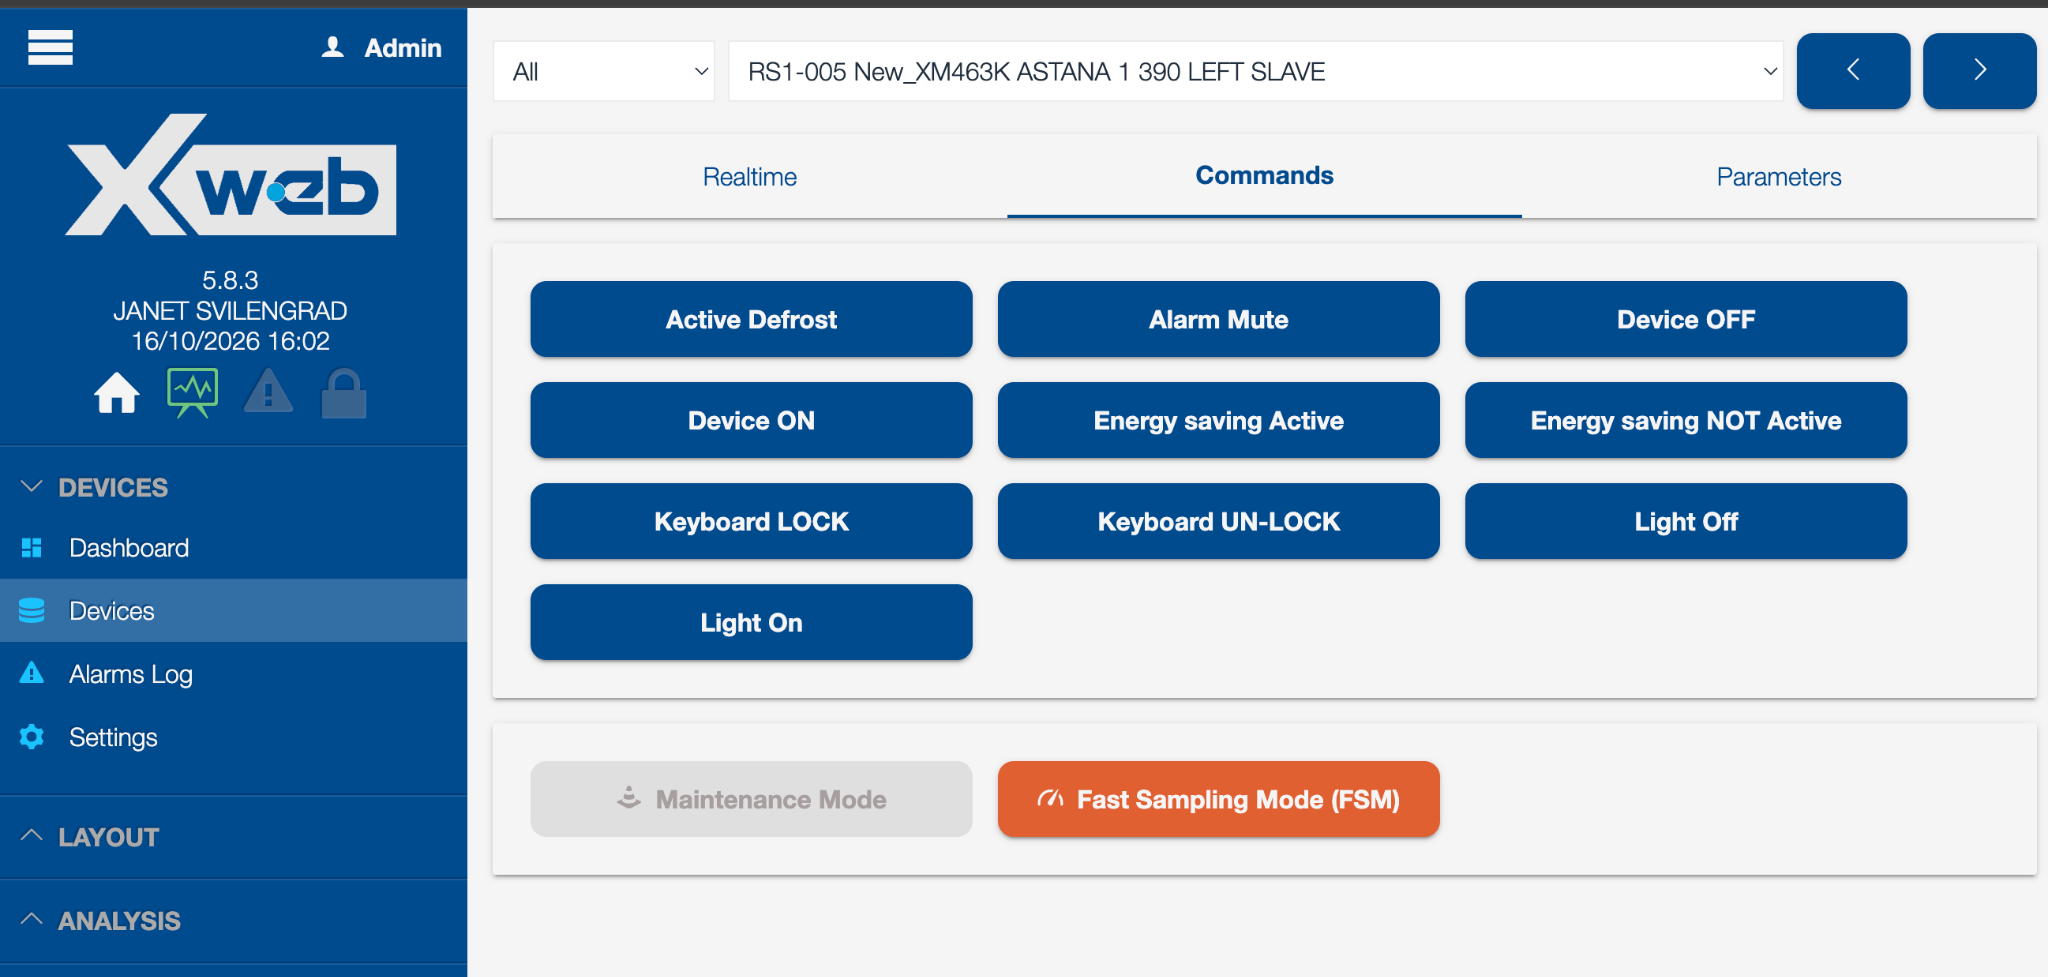
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.

‍

Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.

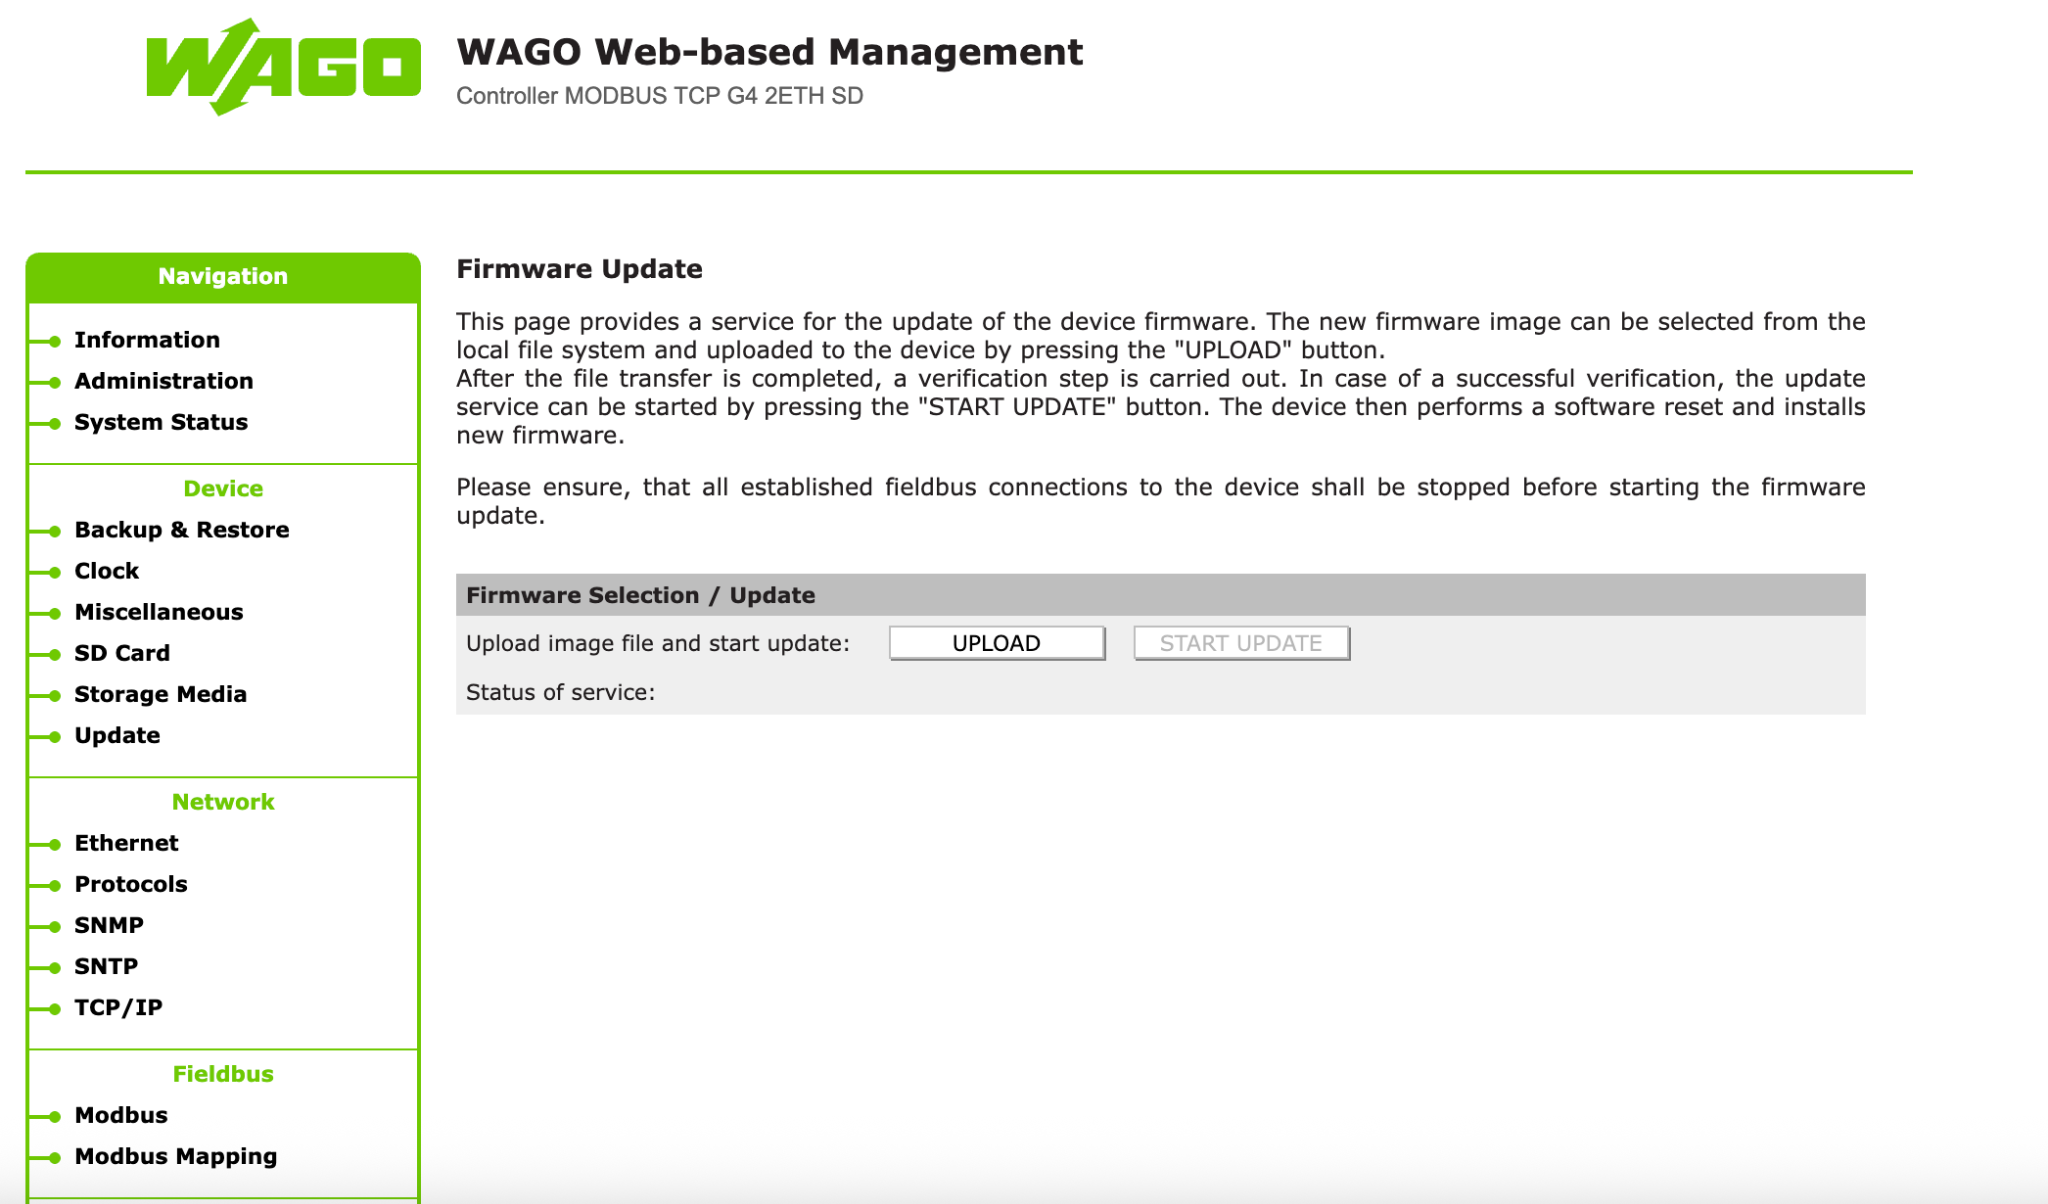
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.

‍

Figure 2: WAGO Management interface.

‍

The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.

‍

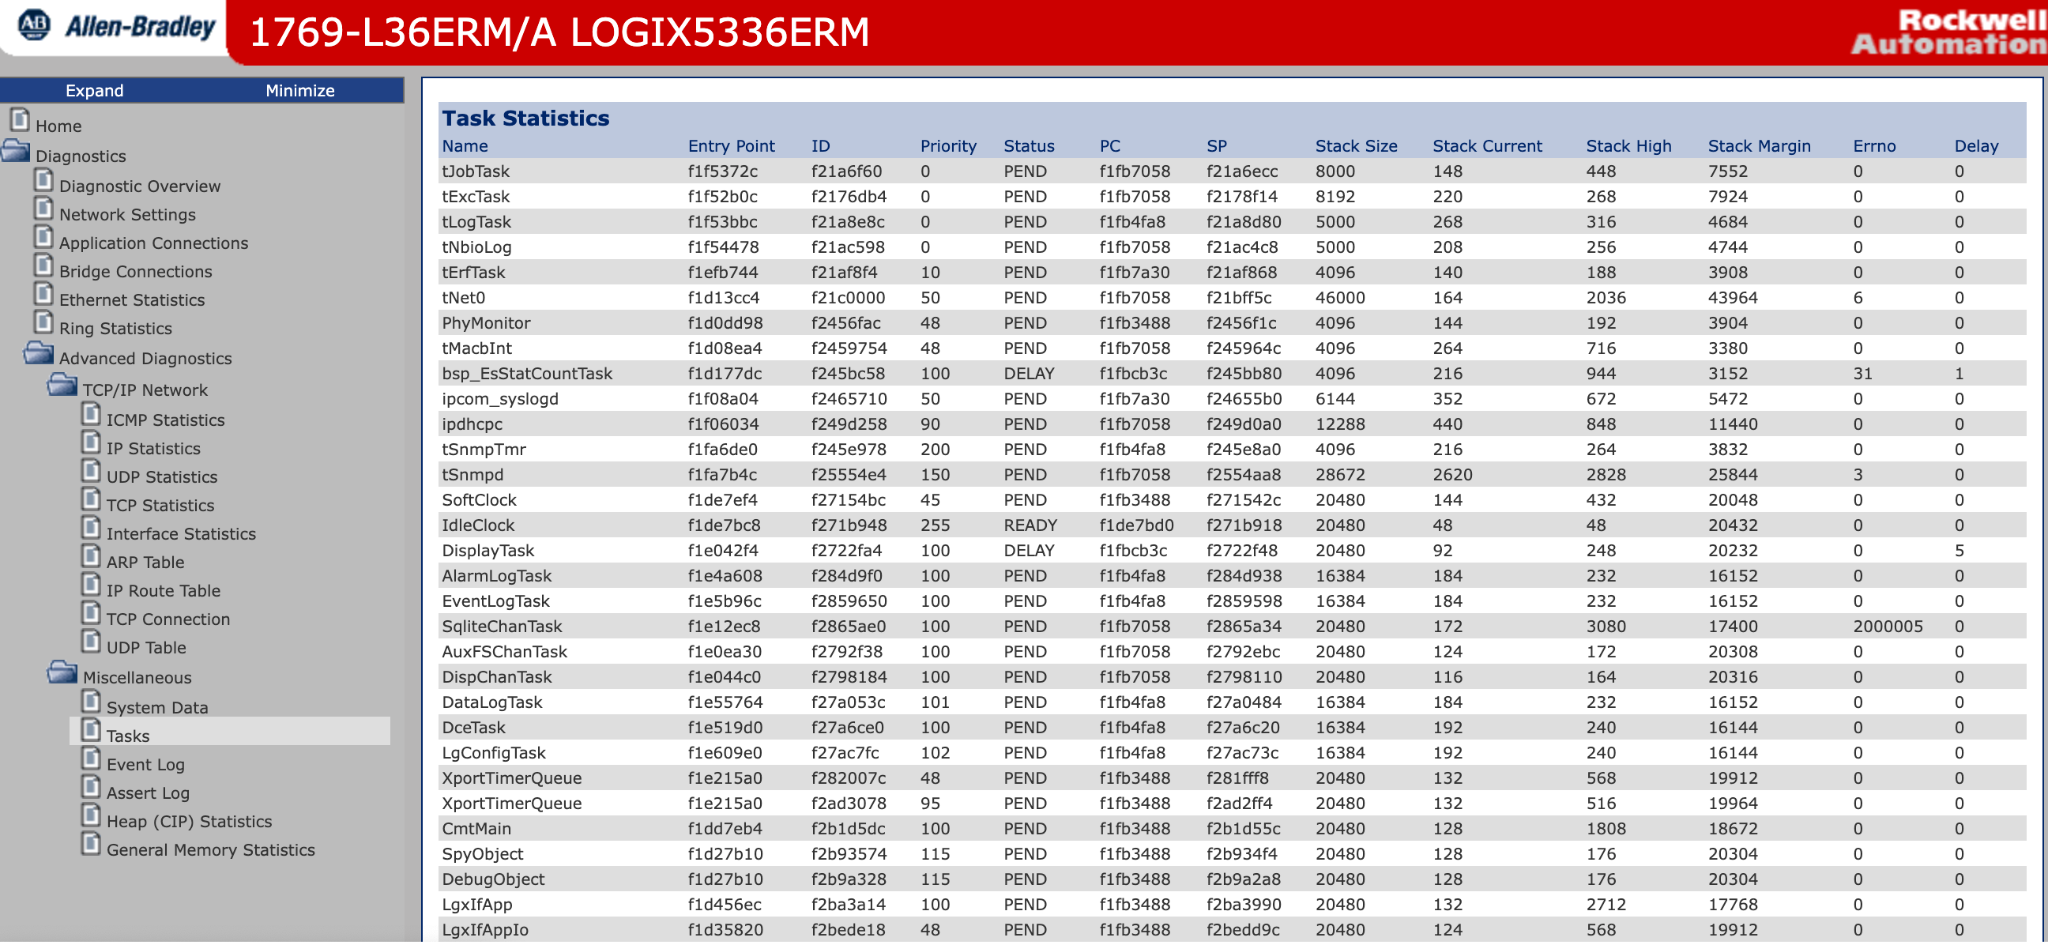
Figure 3: Web interface for Allen-Bradley CompactLogix controller.

‍

Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.

Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.

The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.

The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.

Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.

The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.

Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.

Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.

Darktrace helps security teams gain visibility across IT and OT and respond to risks: https://www.darktrace.com/products/operational-technology.

Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.

References

1.        https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

‍

Continue reading
About the author
Tara Gould
Malware Research Lead
Your data. Our AI.
Elevate your network security with Darktrace AI