ブログ
/
AI
/
August 4, 2021

Detecting a Cobalt Strike Attack With Darktrace AI

See how Darktrace AI was able to detect Cobalt Strike attacks by identifying anomalous connections and performing automated network reconnaissance.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brianna Luong (Leddy)
Sr. Technical Alliances Manager
Default blog image
04
Aug 2021

Since its release in 2012, Cobalt Strike has become a popular platform for red teams and ethical hackers. Robust and reliable software combined with innovative features such as DNS tunnelling, lateral movement tools for privilege escalation, and PowerShell support, have made it a desirable option for organizations wanting to test their own cyber defenses. As the framework was previously only available with a commercial license, it gave security teams a distinct advantage over threat actors when preparing for attacks.

That all changed in late 2020, when a GitHub repository appeared hosting a decompiled version of the framework. Users claimed that the leaked platform did indeed function similarly, if not identically, to the commercial version, and even included a commented-out licensing check. This suddenly made the software readily available, and highly appealing for cyber-criminals: rather than requiring a paper trail and licensing, its source code was freely available for customization and use in offensive campaigns.

With sophisticated capabilities of subtle command and control (C2), privilege escalation, and lateral movement, the tools have become a favorite for ransomware gangs. Even prior to the reporting of the leaked version, 66% of ransomware attacks were found to use Cobalt Strike.

Overview of a Cobalt Strike attack

Cobalt Strike has distinctive TTPs (tools, techniques and procedures) and evasive features for each stage of the attack.

Figure 1: Cyber kill chain with Cobalt Strike

Initial compromise can be achieved with a native module for modifying emails. This includes the insertion of malicious links into existing emails or the creation of convincing spear phishing emails.

The initial payload is intentionally lightweight and can be delivered from cheaply hosted infrastructure. The smaller file size is easier to obfuscate and can be implemented in several ways, including injection into libraries or trusted processes, or creating a series of persistence mechanisms (such as turning off anti-virus prior to downloading the full payload). As such, it is remarkably difficult to detect with blocking rules or signatures.

Network reconnaissance can be done through a variety of subtle methods, using commonly used protocols such as DNS and DCE-RPC to interrogate the network. These services are frequently used in legitimate operations, so it is challenging to apply sufficiently strict controls to prevent this stage of the attack.

Lateral movement and privilege escalation are easily accessible with pre-packaged versions of common attack tools such as Mimikatz. They can interrogate an Active Directory (AD) or steal credentials, while also using SMB pipes for peer-to-peer C2. There is little space for perimeter-based security controls to monitor and restrict these abuses, even if sufficiently granular controls could be imposed.

Payload execution is a straightforward matter as Cobalt Strike beacon allows the delivery of effectively arbitrary payloads, including portability for ransomware. As the previous evasive steps can afford the attacker privileged credentials, the deployment of such payloads could look like non-threatening administrative behavior.

AI detections

Initial compromise

Cobalt Strike has utilities for creating spear phishing documents. As email remains a prolific source of perimeter breaches, threat actors will frequently implant the tool through phishes.

One such example was detected by Darktrace’s AI at Canadian manufacturer in June 2021. The compromise started when an end user appeared to open a phishing document, evidenced by connections to Adobe and VeriSign shortly prior to an HTTP connection to a rare external IP address.

A packet capture of the anomalous connection revealed the creation of an object using a base64 encoded string – a common obfuscation technique. If the customer had been using Darktrace/Email, the threat would have been nullified before it hit the mailbox.

Shortly after the HTTP connection, Darktrace identified unusual use of SSL, which appears to have been leveraged to upgrade to HTTPS using self-signed certificates. The endpoint served an executable, which was later confirmed as a Cobalt Strike beacon based on open-source intelligence (OSINT). Such beacons are supported by the framework, with a variety of common C2 protocols available to the attacker.

Figure 2: Event log for ‘Patient Zero’ of a Sodinokibi infection

Darktrace’s detection was based on the anomalous nature of the connection (suspicious violations of standard SSL protocols) and not a pre-defined rule. The initial compromise was detected in a matter of minutes.

Network reconnaissance

In another example at a Swiss telecommunications company in April 2021, Darktrace alerted the security team that a device – normally used for data collection – was engaging in suspicious lateral movement activity.

The host was abusing privileged credentials to perform AD reconnaissance and SMB enumeration. The alert then prompted a broader investigation, revealing that multiple devices, including domain controllers, were compromised with IoCs related to Cobalt Strike.

Thanks to Darktrace’s deep understanding of the business and recognition that this behavior was anomalous, the security team were able to remediate the infection before file encryption or large data exfiltration had occurred.

Privilege escalation and ransomware deployment

In a ransomware attack against a South African insurance company in May 2021, where a phishing email resulted in the deployment of ransomware, Darktrace first identified the creation of new administrative credentials. The devices which used the credentials were then seen making anomalous connections to various C2 endpoints associated with Cobalt Strike beacons.

Darktrace enabled the rapid identification of compromised hosts, which in turn allowed for a faster remediation and mitigated fears of a resurgent infection.

Cyber AI Analyst performed a machine-speed investigation of the activity, and automatically produced a report highlighting unusual connections on TCP port 4444 as well as other mail related ports. Port 4444 is the default port for Metasploit, another hacking platform which is often seen in conjunction with Cobalt Strike beacon. It then presented the human analysts with a full list of compromised hosts.

Figure 3: Cyber AI Analyst summary of an affected host using non-standard ports for C2 and subsequently scanning the network

Cobalt Strike malware

As it appears that a cheaply accessible analog of Cobalt Strike has been leaked, detection of the framework is critical to defend against active attackers. Signatures and rule-based restrictions prove ineffective in this regard, as the framework was designed specifically to evade such tools.

Darktrace offers the capability to detect malicious activity in its earliest stages, to triage at the speed of AI, and to autonomously block the proliferation of active threats.

Thanks to Darktrace analyst Roberto Romeu for his insights on the above threat find.

Learn how Darktrace caught APT41 leveraging Cobalt Strike

‍

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brianna Luong (Leddy)
Sr. Technical Alliances Manager

More in this series

No items found.

Blog

/

AI

/

November 18, 2026

Agentic attacks in the wild: Inside three ARTEX investigations

Default blog imageDefault blog image

Key insights

·       Darktrace observed activity in several customer environments involving infrastructure and behaviors associated with reported ARTEX-enabled campaigns, including activity linked to China-nexus espionage and financially motivated attacks.

·       In the higher-confidence cases, known infrastructure appeared alongside beaconing, unusual TLS, reconnaissance, tunneling, script retrieval, SMB activity and external data transfer. One Azure case had no observed network command and control at all, only key listing and application identity activity.

·       ARTEX is now used by actors with different objectives. Identifying the framework can help locate relevant activity, while the behavior around the affected system provides the stronger evidence for understanding compromise and attribution.

‍

Introduction

Attackers have moved beyond using AI for phishing and are running agentic frameworks; open-source tools like ARTEX, CAIRN, PentAGI and Hexstrike that let AI agents scan, exploit and move through an environment with little human input [1]. ARTEX has moved quickly from an offensive security project into live intrusion activity. Since at least August 2026, the framework has been associated with espionage, financially motivated attacks and opportunistic campaigns across government, financial services, technology, defense, telecommunications and other sectors. The FBI has documented ARTEX activity spanning reconnaissance, exploitation, credential abuse, lateral movement, collection, command and control, and exfiltration [2].

Darktrace has observed activity in customer environments that overlaps with infrastructure, tooling and behaviors reported in several of these campaigns. The cases below highlight how those intrusions appeared on the network, including the activity visible before an analyst can determine which actor or framework may be responsible.

ARTEX as part of the attacker workflow

ARTEX is an open-source, multi-agent offensive security platform that converts high-level objectives into actions carried out by specialized agents [2]. Operators have used it to automate activity across the attack lifecycle, including scanning, exploitation, credential activity and post-compromise operations. Some reported intrusions moved from initial targeting to privileged access in under three hours [2].

The framework is now associated with actors pursuing different objectives and using different post-exploitation tooling. The original public repository was removed in October 2026, but archived copies and localized versions remain available. For defenders, ARTEX is more useful as context for an investigation than as an attribution shortcut.

Darktrace observations show the same point at network level. Infrastructure linked to reported ARTEX campaigns appeared alongside beaconing, tunneling, unusual TLS, reconnaissance, file retrieval and lateral activity.

Case 1: Espionage-linked activity

Darktrace observed activity associated with BLOODALCHEMY command-and-control (C2) infrastructure in two customer environments. In one environment, five devices communicated with nginxmysql[.]com and 45.153.126[.]223 between October 23 and November 2. Both indicators had previously been linked to China-nexus espionage activity involving ARTEX [4].

The connections were accompanied by suspicious beaconing, repeated successful connections and unusual self-signed TLS. One system began making suspicious TLS connections to nginxmysql[.]com on October 23. Beaconing followed on October 24, and SMB scanning appeared later in the sequence. Other affected systems subsequently communicated with previously unseen external endpoints.

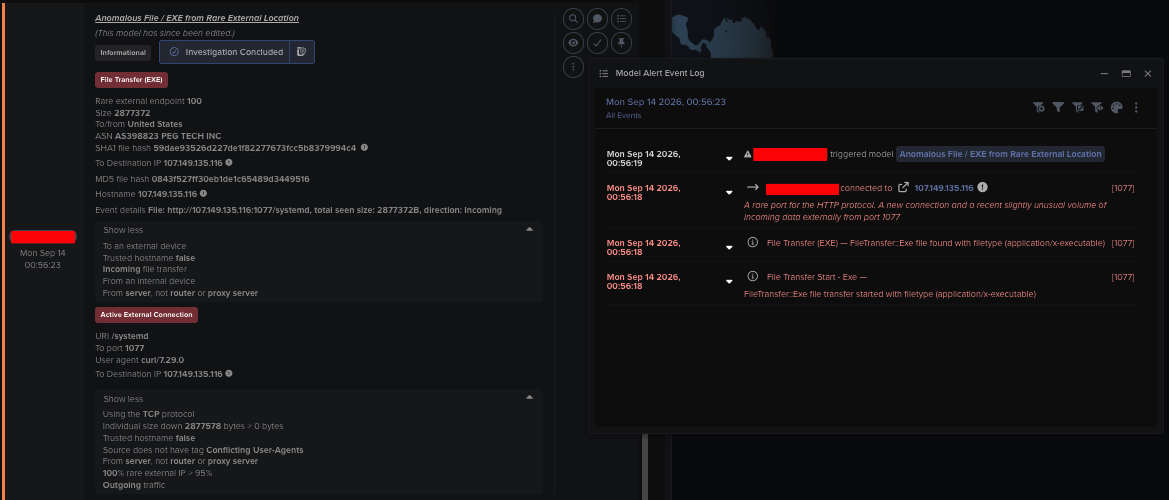
Prior to the observed C2, Darktrace detected curl requests retrieving executable and script content including /systemd, /wazuh, linux_amd64, u.sh and q.sh. Related telemetry included DRSGetNCChanges activity consistent with DCSync, LDAP enumeration, DNS zone transfers, network scanning, certificate downloads and SMB writes involving start.bat.

‍

Figure 1: Darktrace investigation showing suspicious network activity associated with infrastructure linked to reported ARTEX activity.

‍

Figure 2: Darktrace detection showing anomalous self-signed TLS activity during the espionage-linked investigation.

‍

BLOODALCHEMY has been reported in more than one China-nexus cluster [5]. SoftEther infrastructure observed in one environment provided another point of correlation with reported VAPOR PANDA tradecraft. The moderate-confidence assessment tying this to a Chinese nexus threat actor is based on infrastructure, victim context, tradecraft behavior that followed the initial connection, and public reporting.

Case 2: Financial-sector activity

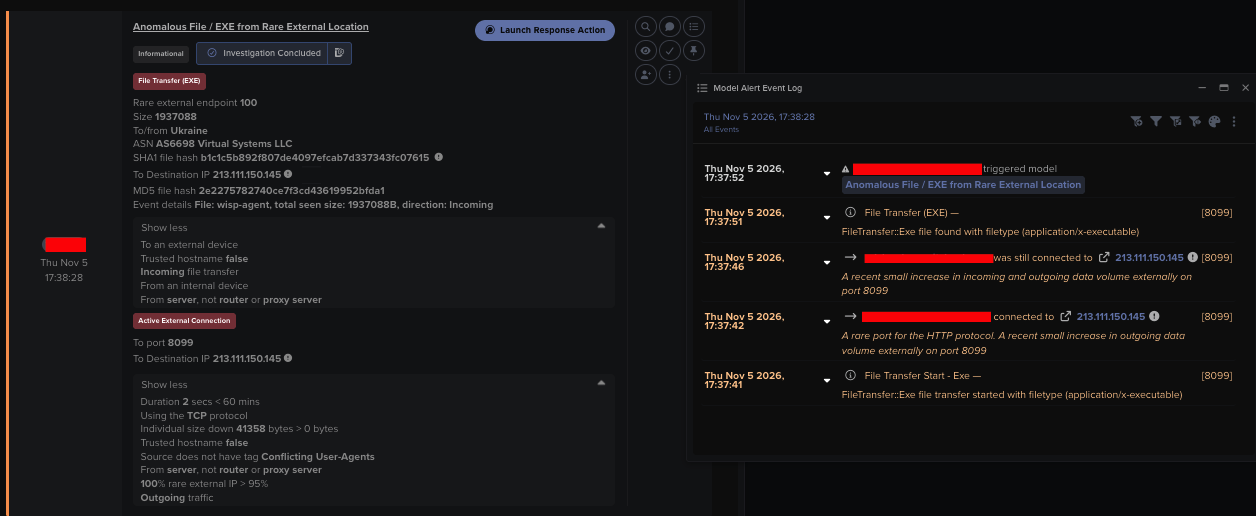
In early November, Darktrace observed activity in two financial-sector environments that overlap with reported ARTEX infrastructure. On November 5, a server connected to 213.111.150[.]145:8099 and downloaded wisp-agent, associated with WISP C2 activity.

In a second environment, a device attempted connections to 85.11.167[.]52 on November 1 and 2. The connections occurred alongside beaconing to new and rare destinations, anomalous TLS, possible tunneling and unusual package downloads.

The device also communicated with temp[.]sh, ssh.localhost[.]run, localhost[.]run, termbin[.]com, pastebin[.]com and GitHub-hosted release infrastructure. The sequence showed potential tooling retrieval, C2, tunneling and use of external services capable of staging or moving data.

Figure 3: Darktrace investigation showing connections to new and rare external destinations during the financial-sector activity.

‍

Case 3: Credential collection in Azure

On October 20, Darktrace observed a sweep of credential collection in a customer’s Azure environment that is consistent with ARTEX use. The intrusion began with connections to the virtual network from 43.98.196[.]73 (Alibaba Cloud). Open-source scanning data associates the address with ARTEX.

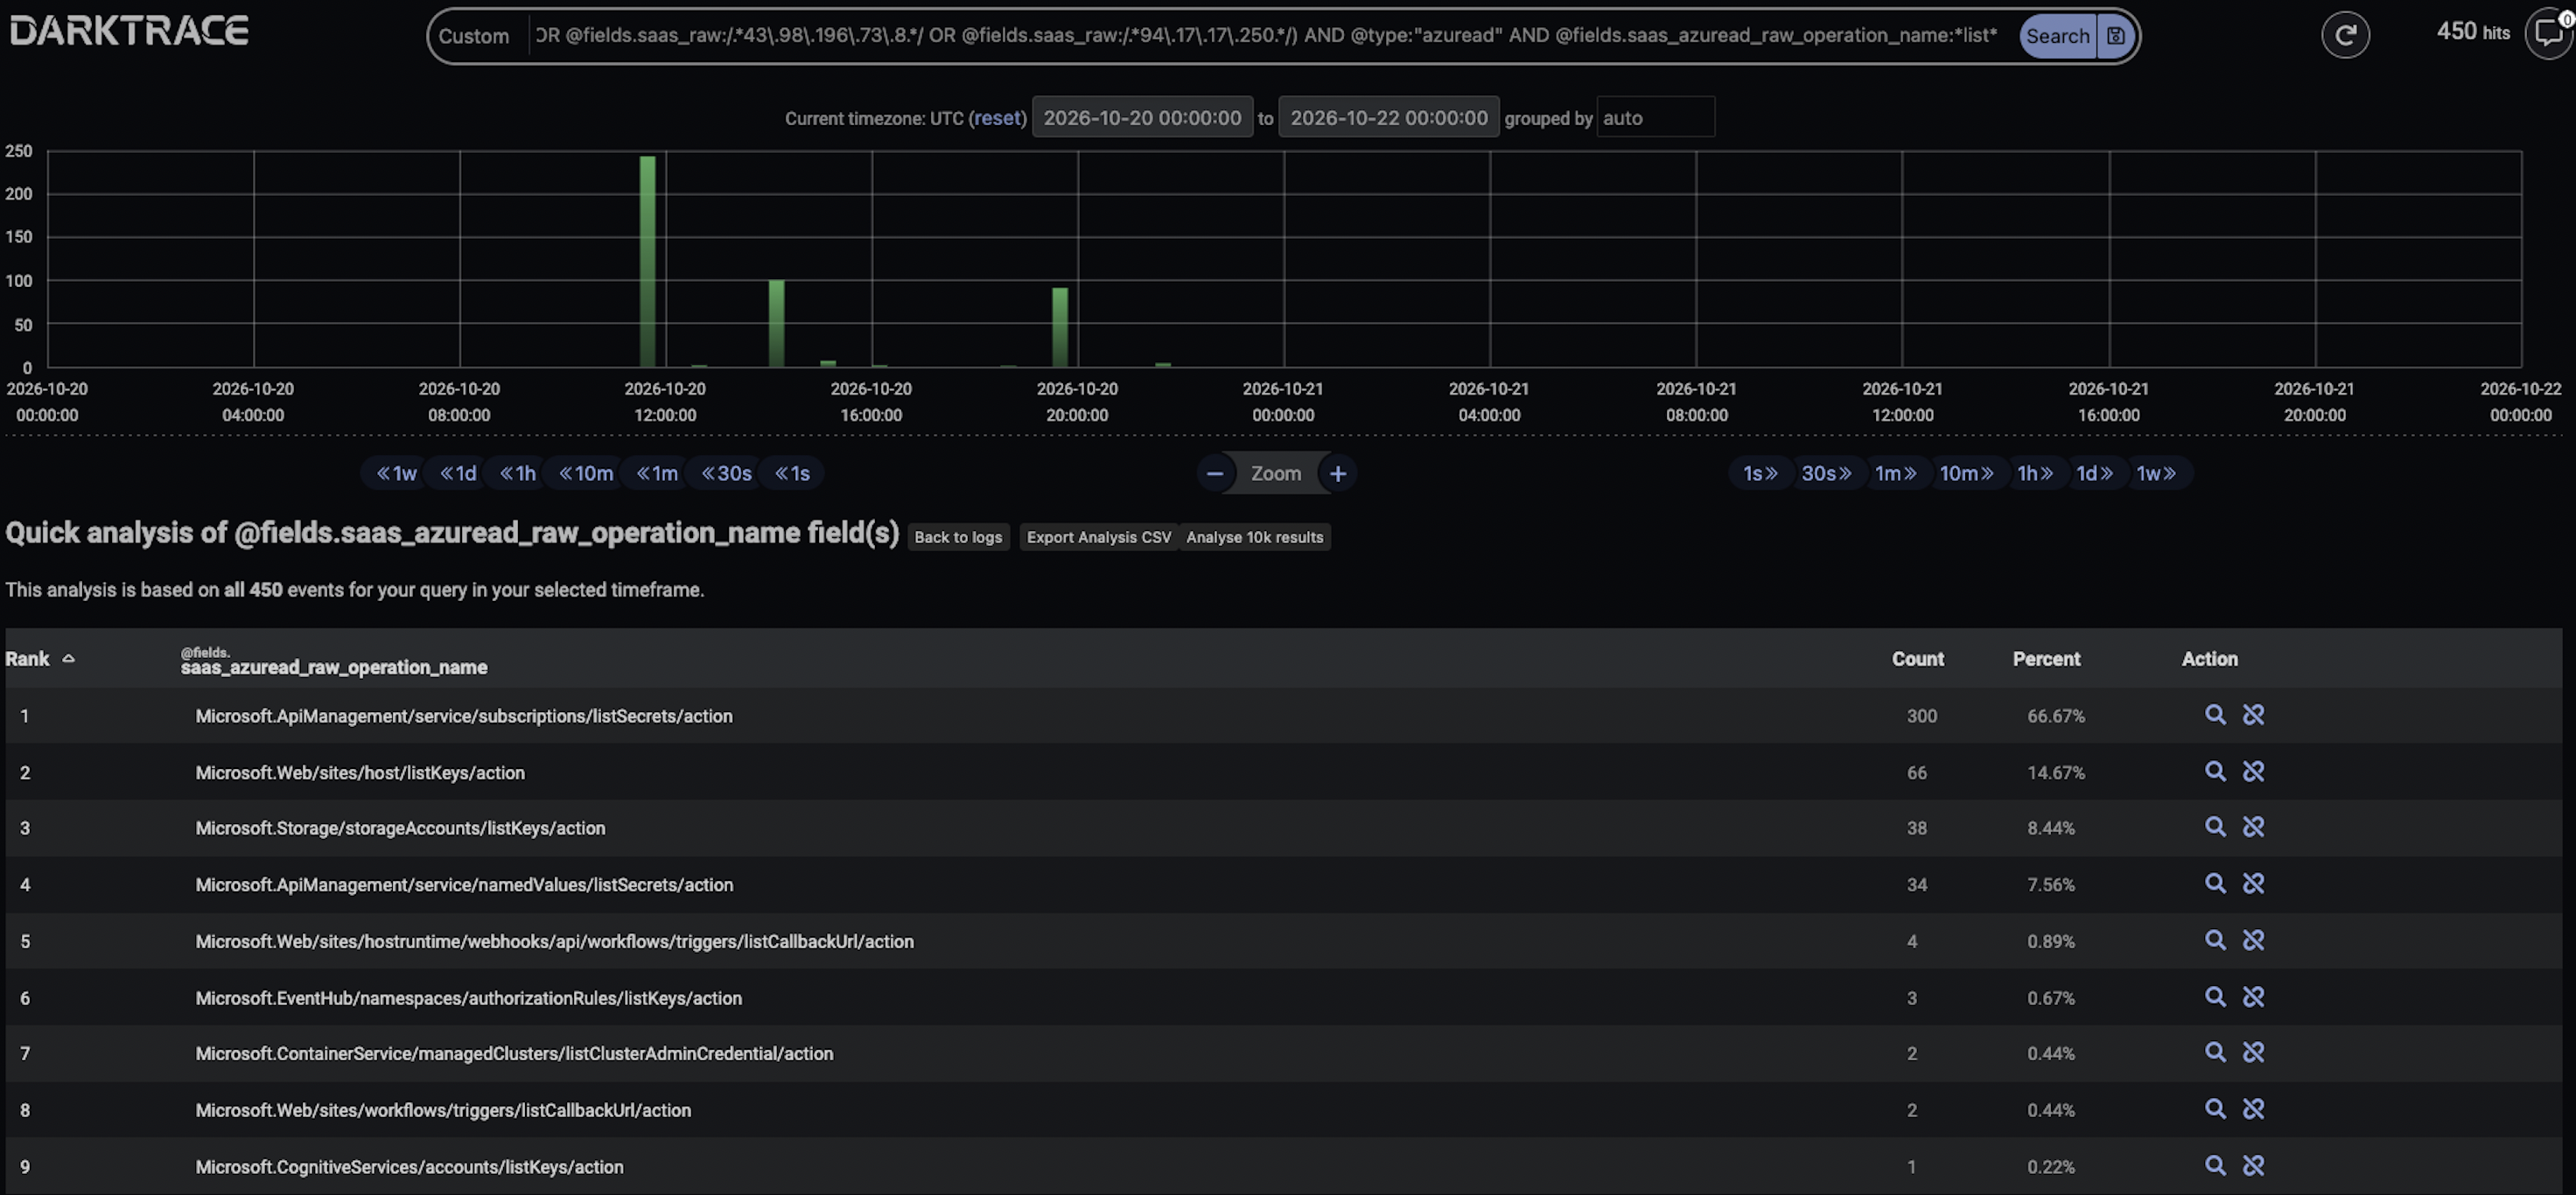
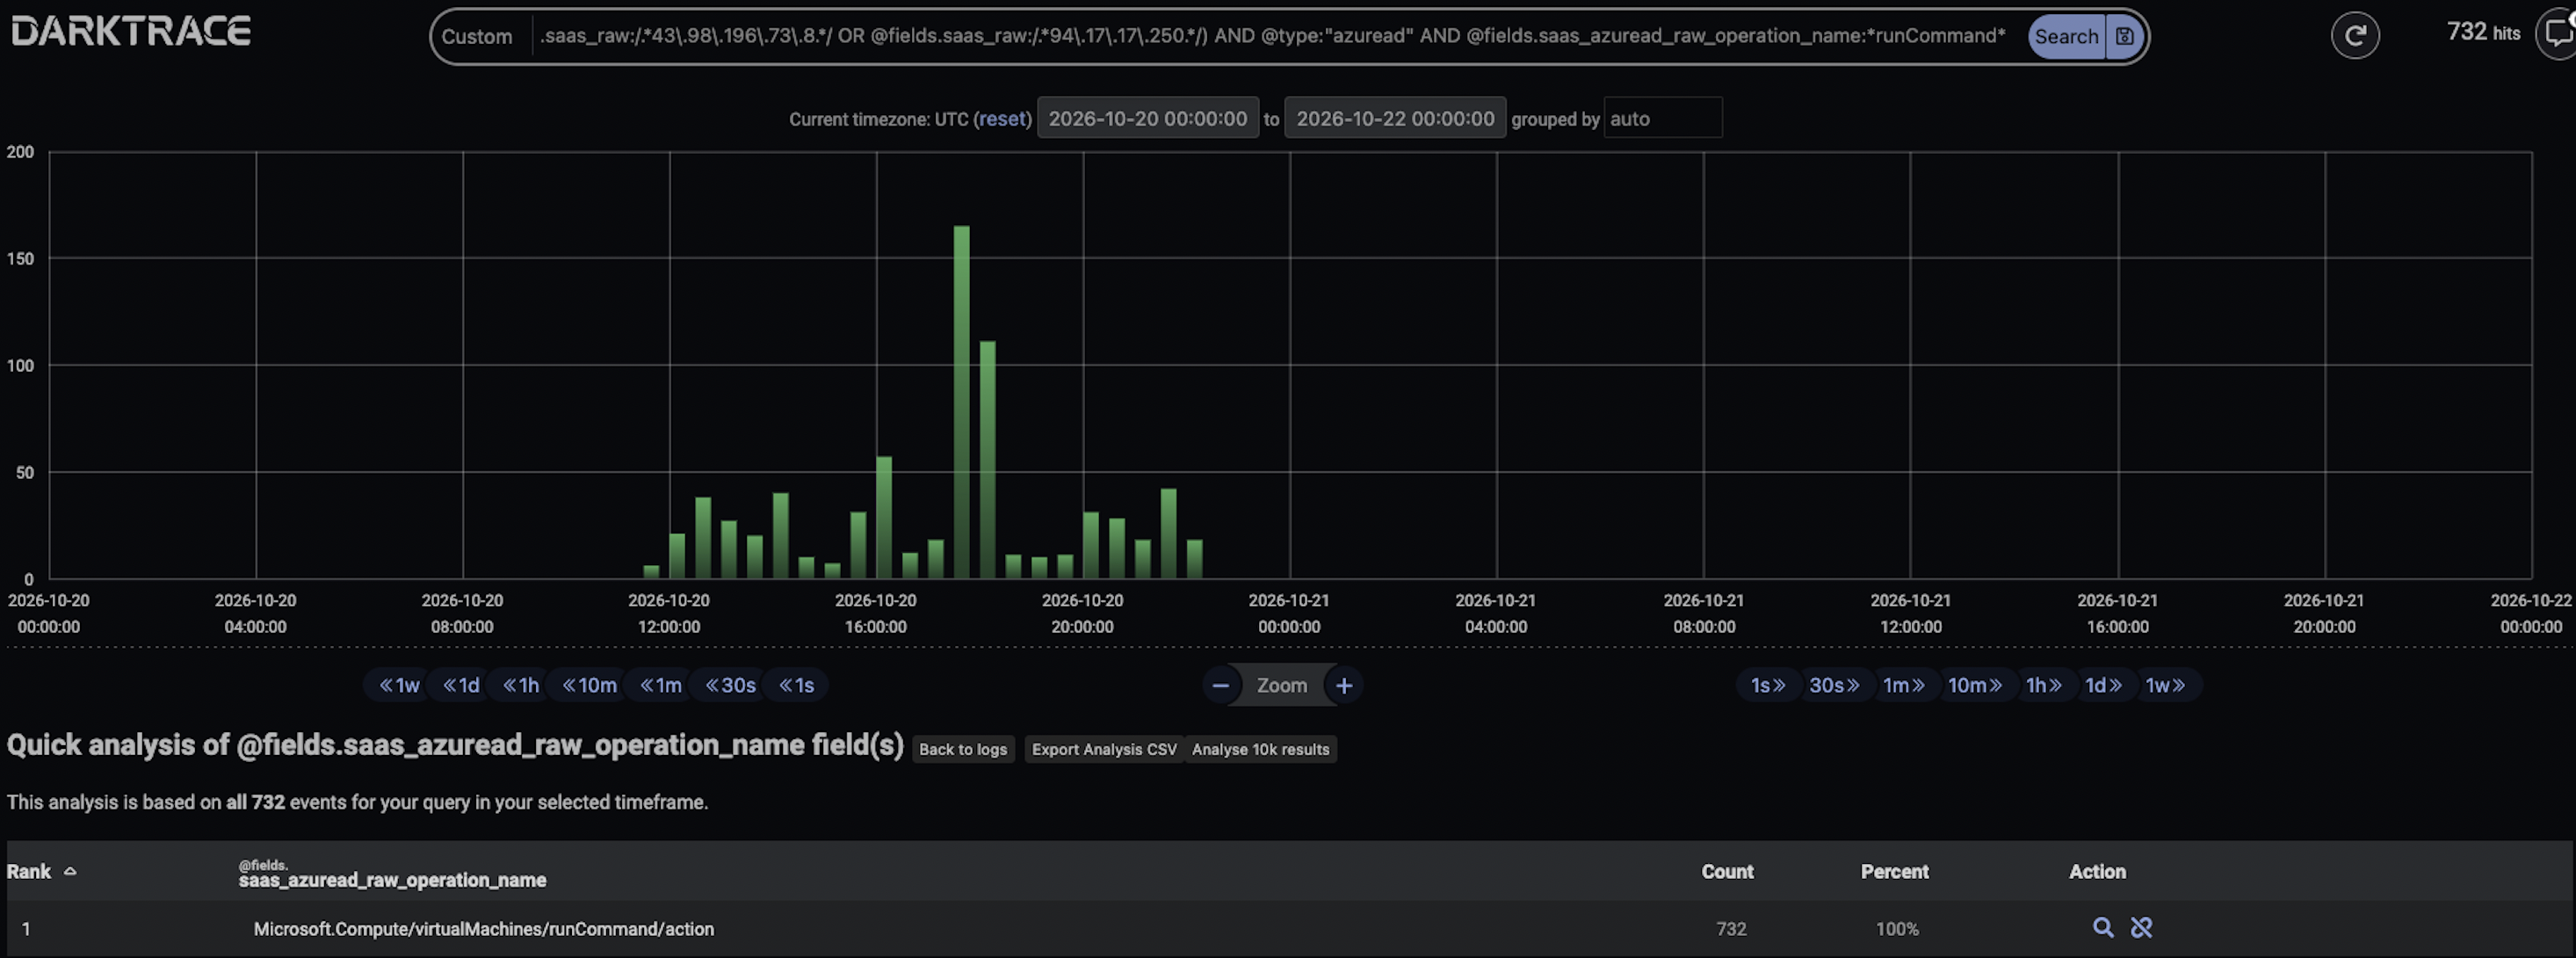
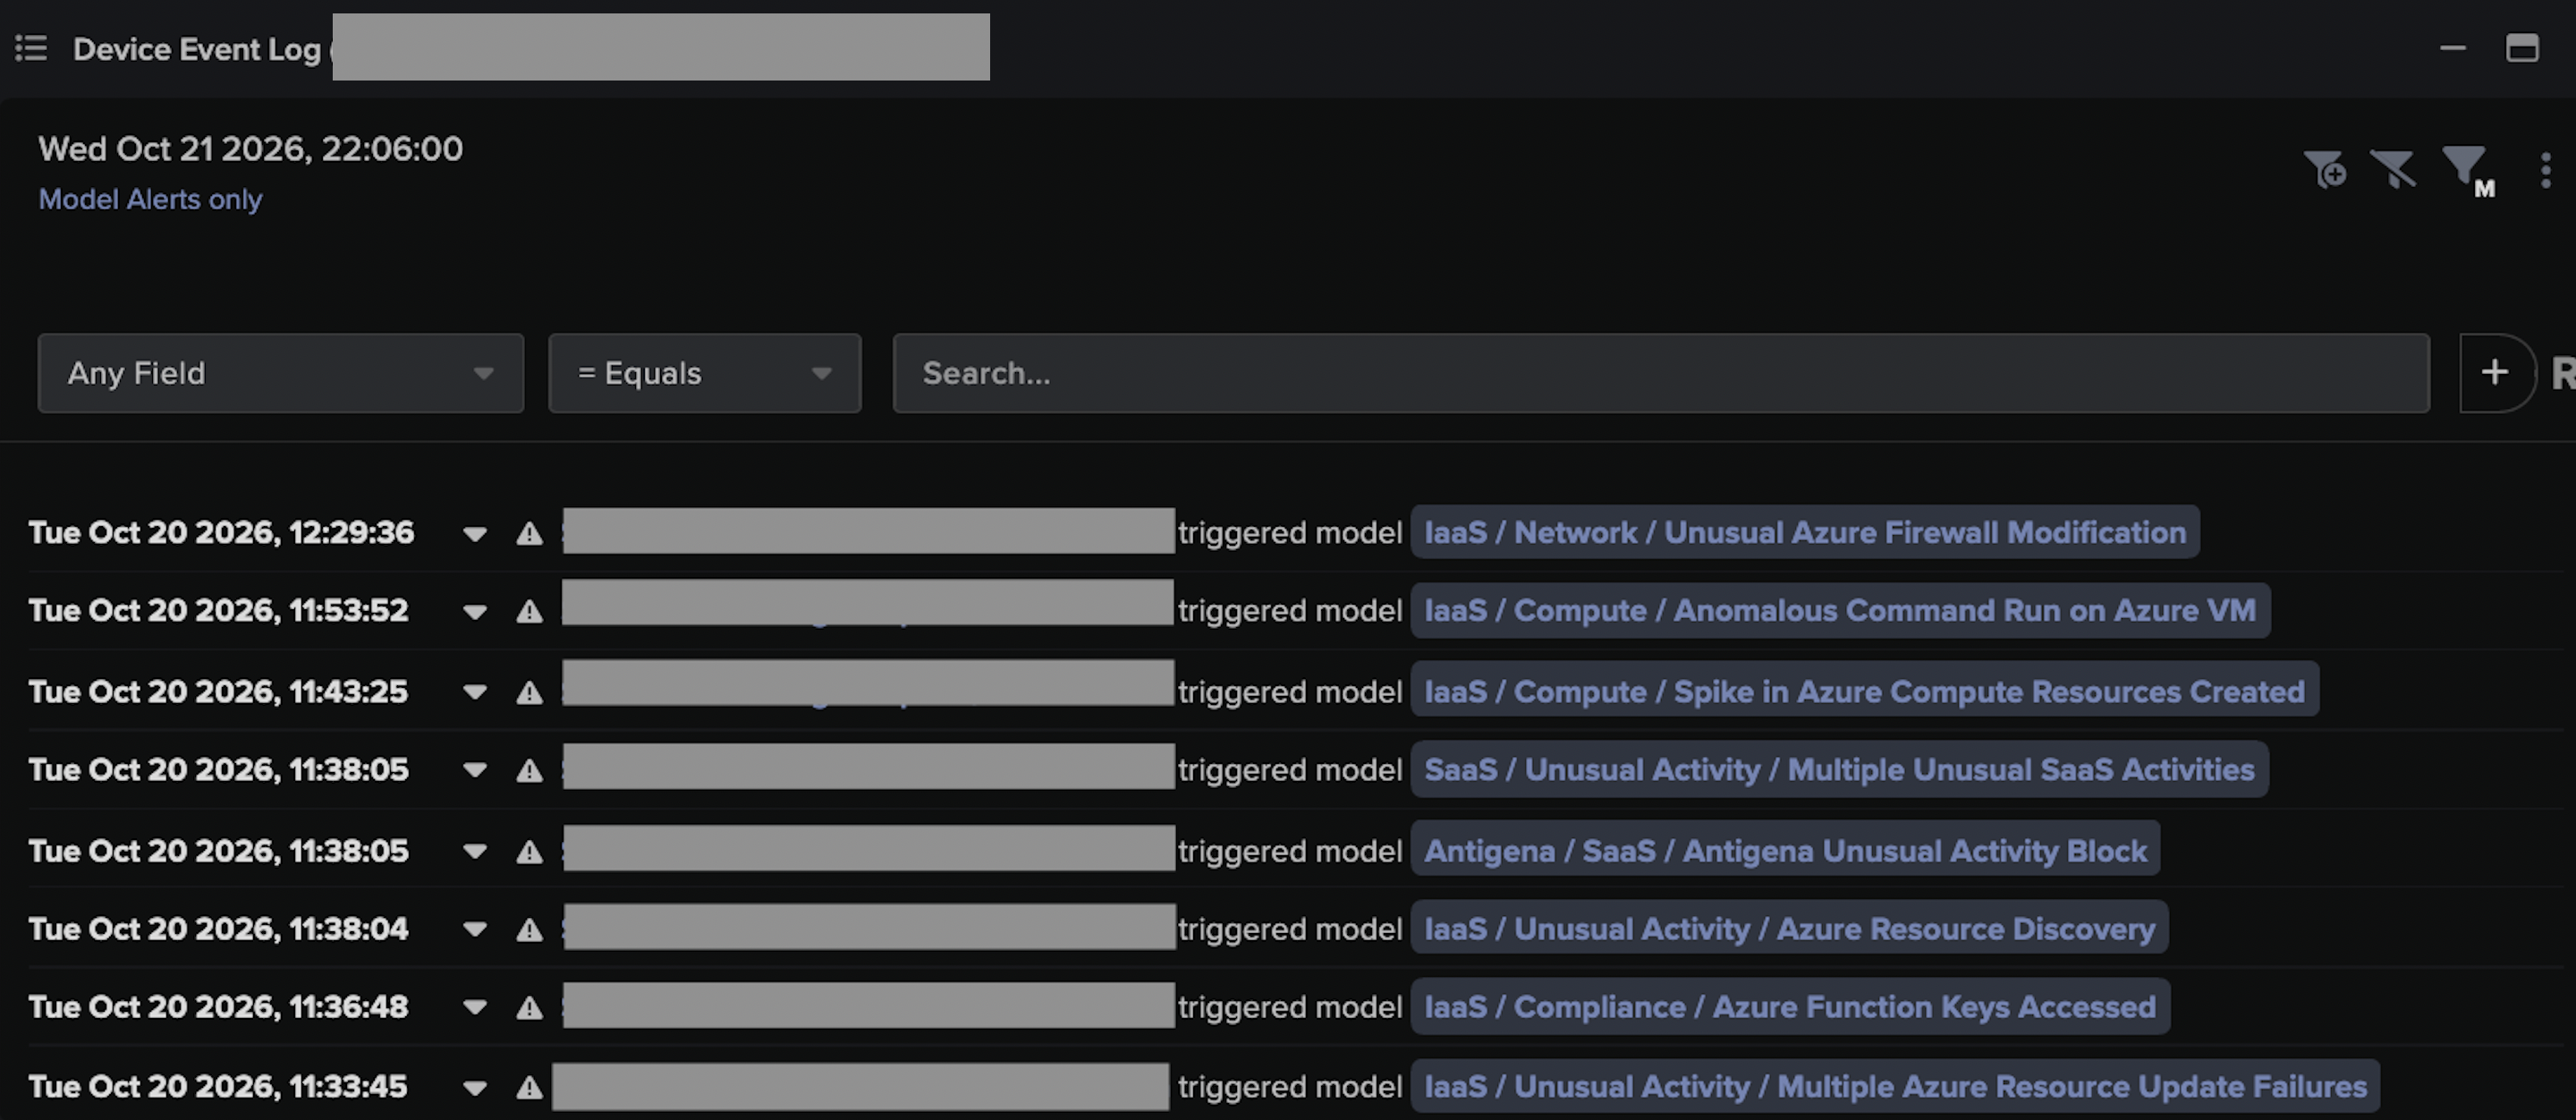
A compromised user identity made requests to the Azure Resource Manager API, though how it was compromised is unknown. The requests listed keys and secrets across API Management, web and function apps, Cognitive Services, Event Hubs, storage accounts and a managed Kubernetes cluster. With those credentials the attacker compromised multiple application identities. The attacker then used the application identities and the user identity to retrieve more credentials, change firewall and security rules and run scripts on virtual machines. Microsoft Defender alerts showed attempted execution of scripts related to Mimikatz and Impacket.

In a cloud environment, such privileged and enumerative operations are potentially indistinguishable from legitimate administrative actions. Consequently, the sequence and context of such operations signified more than any specific API call. There was no C2 traffic to match, and listing keys and using application identities are also what administrators and automation do. A compromised user, credential retrieval across several Azure services, new application identities, more credential collection and changes to security controls only made sense together, and by then access was spreading through the cloud environment.

‍

Figure 4: Darktrace Advanced Search showing Azure AD operation names associated with the activity.

‍

Figure 5: Darktrace Advanced Search showing the Azure Resource Manager action used to execute scripts.
Figure 6: Darktrace Device Event log window showing the triggered models related to the suspicious Azure activity.

‍

Shared tooling weakens attribution signals

The three cases looked different on the network: BLOODALCHEMY infrastructure and espionage-consistent tradecraft, WISP infrastructure in financial-sector systems, and Azure identity and control-plane activity with no C2 at all.

Shared tooling has complicated attribution for years, and ARTEX adds to it because the framework carries out more of the attack, so reconnaissance, exploitation attempts and some post-compromise activity can look the same whoever set the objective. Attribution still needs infrastructure, malware, victimology, timing and the sequence of behavior inside the environment, and an ARTEX link is one input to that. Moreover, the behavior and the agent will still be shaped by the biases, preferences, and tradecraft of its operators.

At its core, ARTEX’s planner and worker agents identify and record facts, while exploring intents. However, the way the Large Language Model (LLM) chooses its next steps toward an objective is shaped fundamentally by the skills and tools available in its context. This includes its starting context, as well as various possible Model Context Protocol (MCP) plugins and user-injected context (e.g. user input mid-operation). Operators still have preferred tradecraft, and this preference shapes the pathways the harness will provide to the LLM in context prompts. Even on the same platform, customization based on operator preferences and goals will remain a key facet of campaign and actor identification.

Detection and response

Across the Darktrace cases, the stronger signals came from behavior after the connection: beaconing, abnormal TLS, reconnaissance, unusual authentication, tunneling, script retrieval, SMB activity and outbound transfer. Automated activity also produced compressed bursts of requests, sequential enumeration and repeated attempts with small changes.

With agentic tools reaching privileged access in under three hours, analysts may have only a short window to connect scanning or authentication activity to credential changes, new administrative access, tooling retrieval or lateral movement. Keeping network, identity and cloud telemetry together shows what happened before and after the first match, and whether a connection was noise or an intrusion moving toward privileged access.

ARTEX won’t be the last of these frameworks. The next ones will come with new capabilities and defaults, but an intrusion still must interact with the target environment, and that shows up in how systems, identities and applications behave even after the indicator has aged out. The harder intrusions to catch will have no infrastructure to match, just ordinary API calls and legitimate identities. Detecting those depends on knowing what normal looks like for each identity and device.

‍

Credit to Nathaniel Jones (SVP, Global Threat Intelligence), Eugene Chua (Principal Analyst), Sam Lister (Senior Security Researcher), Adam Potter (Associate Principal Cyber Analyst)

Appendices

Darktrace model detections

·       Anomalous Connection / Multiple HTTP POSTs to Rare Hostname

·       Anomalous Connection / Rare External SSL Self-Signed

·       Anomalous Connection / Suspicious Self-Signed SSL

·       Compromise / Large Number of Suspicious Successful Connections

·       Compromise / Suspicious Beaconing Behaviour

·       Compromise / Agent Beacon to New Endpoint

·       Compromise / Beacon to Young Endpoint

·       Compromise / SSL Beaconing to Rare Destination

·       Compromise / Suspicious TLS Beaconing To Rare External

·       Compromise / Possible Tunnelling to Bin Services

·       Device / Anomalous Github Download

·       Device / Anomalous Package Download

·       Device / Initial Attack Chain Activity

Indicators of compromise (IoCs)

nginxmysql[.]com

45.153.126[.]223

213.111.150[.]145

wisp-agent

85.11.167[.]52

43.98.196[.]73

192.121.47[.]20

www[.]ddduuuppp[.]com

89.46.234[.]50

sqlserver-sqlite[.]com

199.19.95[.]66

graphics-hook-filter64.dll

graphics-hook_config.bin

References

1.      Google. GTIG AI Threat Tracker - https://cloud.google.com/blog/topics/threat-intelligence/agentic-threat-activity-crosses-a-significant-threshold

2.      Federal Bureau of Investigation, Threat Overview of ARTEX Autonomous Penetration Testing Framework, FLASH-20261113-001, 13 November 2026: https://www.ic3.gov/CSA/2026/261113.pdf

3.      Microsoft Security Blog, Storm-0940 Uses ARTEX Agentic AI in ConnectWise Supply Chain Compromise: https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

4.      CrowdStrike, VAPOR PANDA Uses ARTEX to Scale Global Campaign: https://www.crowdstrike.com/en-us/blog/vapor-panda-uses-artex-to-scale-global-campaign/

5.      Bitdefender, SilkParasite: Tracking a China-Nexus APT Across Central Asia: https://www.bitdefender.com/en-us/blog/businessinsights/silkparasite-tracking-china-nexus-apt-across-central-asia

‍

‍

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence

Blog

/

AI

/

November 18, 2026

Darktrace qualifies for NATO’s Cybersecurity Dynamic Marketplace

Default blog imageDefault blog image

Darktrace has been selected to join NATO’s Cybersecurity Dynamic Marketplace (CSDM), an initiative designed to give NATO faster, more flexible access to cybersecurity technology and services in support of its missions.  

Established by the NATO Communications and Information Agency (NCIA), the marketplace brings together qualified suppliers whose technical capabilities have been reviewed, helping NATO match specialist expertise to project needs and respond more quickly to changing operational priorities.

Qualified across all eight cybersecurity categories

The program’s first phase, known as Lot 1, covers eight cybersecurity categories. Suppliers can qualify in individual categories; Darktrace has qualified to compete for future work across all eight:

  • Identity, Credential and Access Management
  • Endpoint Protection and Platforms
  • Network and Perimeter Security
  • Cloud Security
  • Threat Detection and Analytics Platforms
  • Vulnerability and Exposure Management
  • Digital Forensics and Evidence Platforms
  • Professional Services

Darktrace’s qualification across all eight categories reflects the breadth of our technology and services.

Supporting government and defense organizations

Nation-state attacks, compromised suppliers, the rapid exploitation of security weaknesses and attackers’ growing use of AI are increasing pressure on public-sector organizations. At the same time, agencies are adopting cloud services, connecting the technology that runs physical operations, and introducing automation and AI. Security teams must manage these changes while keeping essential operations running and sensitive information secure.

Protecting these environments requires an understanding of how people, AI and connected systems interact, and the ability to recognize when their activity creates risk. Threats can span several systems, making it essential for security teams to connect related activity and respond quickly.

The Darktrace Behavioral Defense Platform™ supports this approach through unified visibility, continuous behavioral monitoring and autonomous response across AI, people and infrastructure.

At its core, Darktrace’s Adaptive AI™ continuously learns how each organization behaves, building a unique understanding of its people, AI agents and connected systems. This enables the platform to help identify activity that does not belong, connect related behavior across the organization, and investigate and respond to threats autonomously in real time, helping prevent disruption to essential operations.

Our selection builds on work to meet government security requirements internationally. Darktrace recently completed an independent assessment under Australia’s InfoSec Registered Assessors Program (IRAP) for Darktrace / NETWORK™ and Darktrace / OT™ against the Australian Government’s Information Security Manual PROTECTED-level controls. In the United States, Darktrace Federal continues to deliver the Darktrace technology to Department of War, Department of State, and Federal civilian organizations via its on-premises and FedRAMP CLASS D (High) Authorization platforms.

Together, these achievements demonstrate Darktrace’s ability to meet rigorous public-sector security requirements and reinforce its position as a trusted provider of mission-critical cybersecurity technology for government environments.

Meet us at NATO Edge 2026

Darktrace representatives will attend NATO Edge 2026, NCIA’s flagship technology event, in İzmir, Türkiye, from 17 to 19 November. We look forward to meeting government, military, and industry partners to discuss their cybersecurity priorities and how we can support them.

To learn more about the Darktrace Behavioral Defense Platform, visit the platform hub.

Continue reading
About the author
The Darktrace Community
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ