
ブログ
/
/
February 11, 2021

Detecting IoT Threats in Control Systems

Discover how Darktrace uncovers pre-existing threats in Industrial IoT systems. Learn about advanced detection techniques in industrial control systems.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
David Masson
VP, Field CISO
Default blog image
11
Feb 2021

Industrial IoT (IIoT) devices are a pressing concern for security teams. Companies invest large sums of money to keep cyber-criminals out of industrial systems, but what happens when the hacker is already inside? Gateways and legacy security tools generally sit at the border of an organization and are designed to stop external threats, but are less effective once the threat is already inside. During this period, cyber-criminals carry out further reconnaissance, tamper with PLC settings, and subtly disrupt the production process.

Darktrace recently detected a series of pre-existing infections in Industrial IoT (IIoT) devices at a manufacturing firm in the EMEA region. The organization already had Darktrace in place in one area of the environment, but after seeing how the AI could successfully detect zero-day vulnerabilities and threats, they expanded the deployment, allowing Darktrace to actively monitor and defend interactions among its 5,000 devices, and dramatically improving visibility.

An unknown emerging threat was identified by Darktrace’s Industrial Immune System on multiple machines within hours of Darktrace being active in the environment. By casting light on this previously unknown threat, Darktrace enabled the customer to perform full incident response and threat investigation, before the attacker was able to cause any serious damage to the company.

Though it is unclear how long the devices had been infected, it is likely to have been first introduced manually via an infected USB. The affected endpoints were being used as part of a continuous production process and could not be installed with endpoint protection.

The Industrial Immune System, however, easily detects infections across the digital estate, regardless of the type of environment or technology. Darktrace AI does not rely on signature-based methods but instead continuously updates its understanding of what constitutes ‘normal’ in an industrial environment. This self-learning approach allows the AI to contain zero-days that have never been seen before in the wild, as well as detecting the new appearance of pre-existing attacks.

Industrial IoT attacked

Only a few hours after Darktrace AI had begun defending the wider connections and interactions across the manufacturing firm, the Industrial Immune System detected a highly unusual network scan. A timeline of events, from first scan to full incident response results and conclusions, is shown below:

Figure 1: Timeline of incident response across 28 hours

Darktrace’s AI recognized that the device was exploiting an SMBv1 protocol in order to attempt lateral movement. In addition to anonymous SMBv1 authentication, Darktrace detected the device abusing default vendor credentials for device enumeration.

The device made a large number of unusual connections, including connections to internal endpoints which the company had previously been unaware of. As these occurred, the Threat Visualizer, Darktrace’s user interface, provided a graphical visualization of the incident, illuminating the unusual activity’s spread from the infected device across the infrastructure in question.
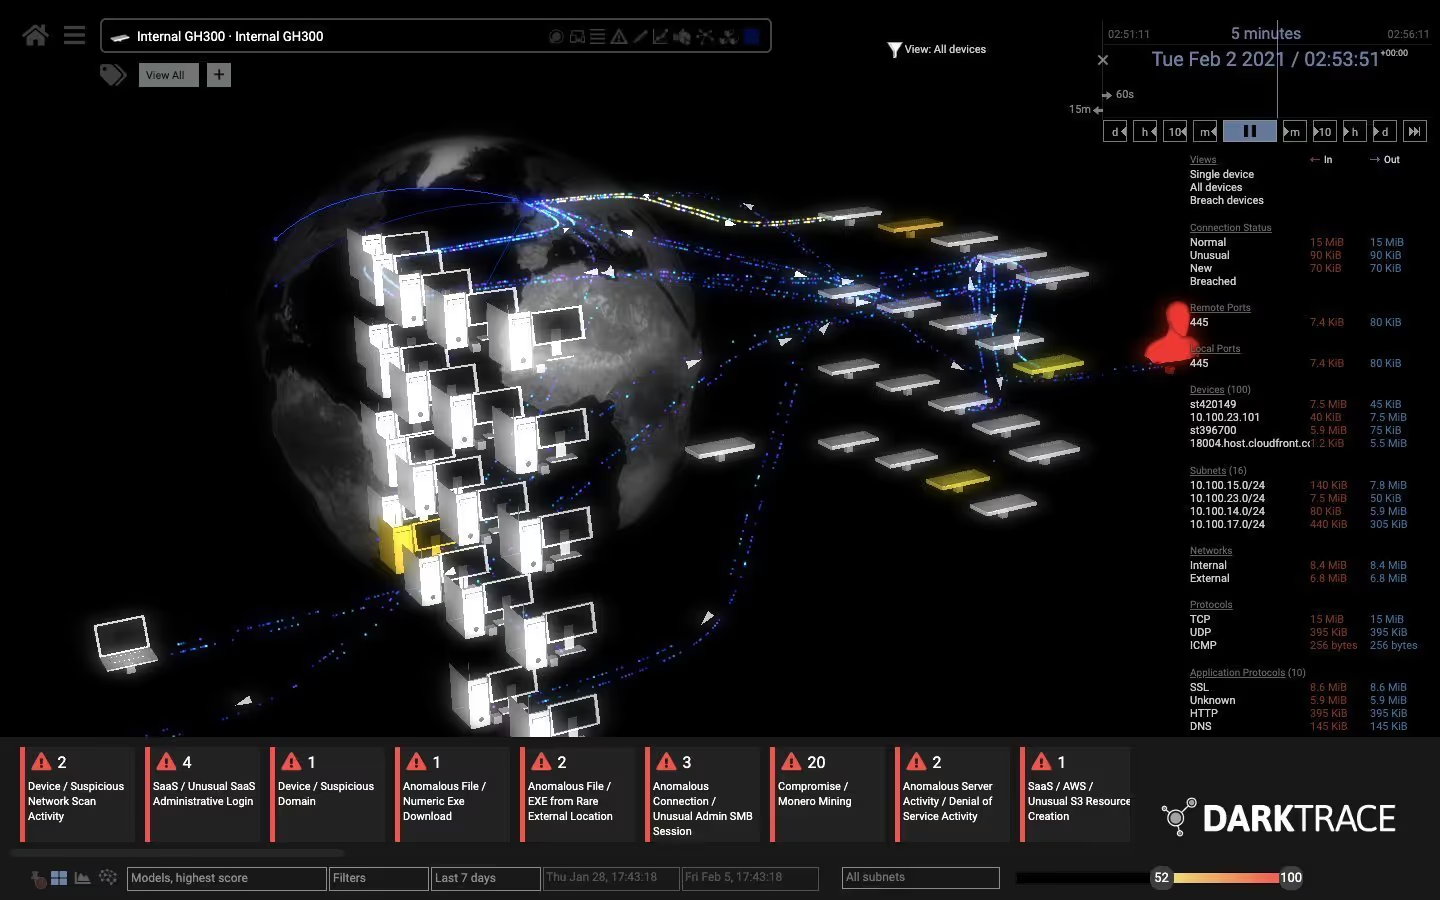
Figure 2: The Darktrace Threat Visualizer

Darktrace’s Immune System identified that the infected Industrial IoT device was making an unusually large number of internal connections, suggesting an effort to perform reconnaissance.

Darktrace’s Cyber AI Analyst launched an immediate investigation into the alert, surfacing an incident summary at machine speed with all the information the security team needed to act.
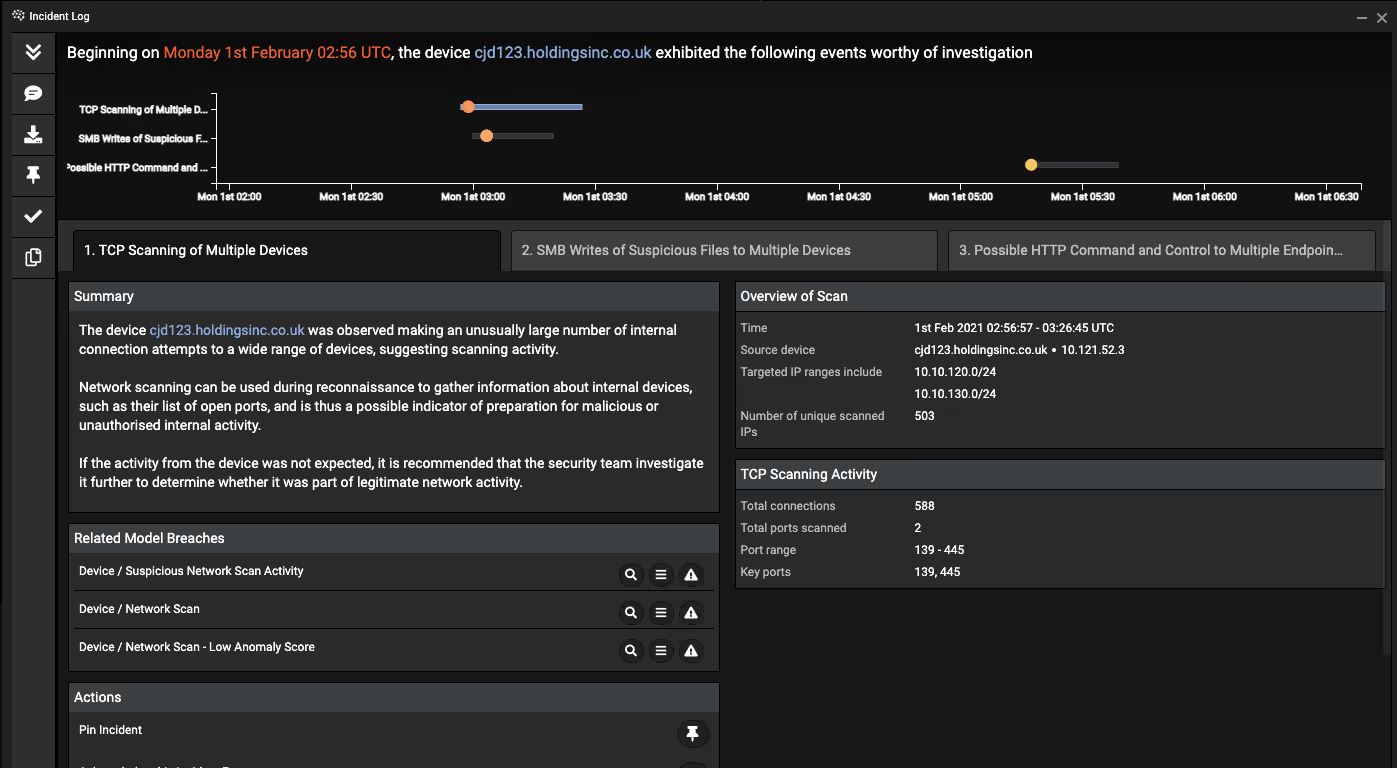
Figure 3: An example of an AI Analyst Report on a network scan

The Cyber AI Analyst further identified two other devices behaving in a similar way, and these were removed from the network by the customer in response. When investigated by the security team, these devices were shown to be infected with the Yalove and Renocide worms, and the Autoit trojan-dropper. Open source intelligence suggests these infections are often spread via removable media such as USB drives.

Using Darktrace’s Advanced Search function, the customer was able to investigate related model breaches to build a list of similar indicators of compromise (IoCs), including failed external connections to www.whatismyip[.]com and DYNDNS IP addresses on HTTP port 80.

Recurring infections: How to deal with a persistent attack

In total, Darktrace was used to identify 13 infected production devices. The customer contacted the equipment owner, whose response confirmed that they had seen similar attacks on other networks in the past, including recurring infections.

Recurring infections imply one of two things: either, that the malware has a persistence mechanism, where it uses a range of techniques to remain undetected on the exploited machine and achieve persistent access to the system. Alternatively, a recurring infection could mean that the IoT manufacturer was not able to find all infected devices when they were first alerted to the compromise, and thus did not shut down the attack in its entirety.

As the infected machines are owned by a third party, they could not be immediately remediated. Darktrace AI, however, contained this threat with minimal business disruption. The customer was able to leave the infected devices active, which were still needed for production, confident that Darktrace would alert them if the infection spread or changed in behavior.

Industrial IoT: Shining a light on pre-existing threats

The mass adoption of Industrial IoT devices has made industrial environments more complex and more vulnerable than ever. This blog demonstrates the prevalent threat that attackers are already on the inside, and the importance for security teams to expand visibility over their full industrial system. In this case, the customer was able to use Darktrace’s AI to illuminate a previous blind spot and contain a persistent attack, while minimizing disruption to operations. Crucially, this ‘unknown known’ threat was detected without any prior knowledge of the devices, their supplier, or patch history, and without using malware signatures or IoCs.

The customer was made aware of the infection via the Darktrace SOC service. Yet the same outcome could have been obtained with other workflows provided by Darktrace, such as email alerting, notifications through the Darktrace mobile app, seamlessly integrating Darktrace with a SIEM solution, or alerting via an internal SOC.

Cyber AI Analyst enabled the customer to perform immediate incident response. While waiting for a reinstallation date with the equipment owner, the customer could keep the production devices online, knowing Darktrace would be monitoring the outstanding risk. In an industrial setting, trade-offs like this are often necessary to sustain production. Darktrace helps organizations maintain the vigilance they need to do this securely, and when remediation does become possible, Darktrace can be used to reliably locate the full extent of the infection.

Thanks to Darktrace analyst Oakley Cox for his insights on the above threat find.

Find out more about the Industrial Immune System

Darktrace model detections:

  • Device / Suspicious Network Scan Activity [Enhanced Monitoring]
  • Device / ICMP Address Scan
  • ICS / Anomalous IT to ICS Connection
  • Anomalous Connection / SMB Enumeration
  • Device / Network Scan

‍

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
David Masson
VP, Field CISO

More in this series

No items found.

Blog

/

AI

/

October 26, 2026

PHP脆弱性、ARTEX、そしてサイバー攻撃におけるAIの役割拡大

Default blog imageDefault blog image

BCVE-2026-109618およびCVE-2026-109619の公開により、PHPを運用している組織は緊急対応を余儀なくされました。どちらの脆弱性も許可のないリモートコード実行を可能にするものであり、対象はPHPが組み込まれ、サードパーティベンダーにアップデートを依存する製品およびアプライアンスも含まれていました[1]。

初期のガイダンスではインターネットに接続されたシステムにパッチを適用し、予期しないコマンド実行やWebroot変更、PHPサーバーからのアウトバウンド接続など、エクスプロイトの成功に関連した振る舞いを監視することに重点が置かれました。

Darktraceは監視中の環境においてスキャニングが広範に発生していることを観測し、これにはPHP脆弱性を標的としたアクティビティに関連すると報告されている数百の個別のIPアドレスが関係していました。スキャニングの量はエクスプロイトの成功を示す証拠の数を著しく上回るものでした。アナリストにとってはこの違いが重要です。スキャニングは露出したインフラへの関心を表すものです。侵害を確認するには、標的とされたシステム上でこれに続く振る舞い、たとえばコマンド実行、ファイル変更、予期しないアウトバウンド接続などの証拠が必要です。

PHPは例外的なケースではありません。その後、Imperva社が脆弱なNode.jsビルドに対するリモートコード実行を悪意あるBrotliデータを通じて実証し、圧縮HTTPレスポンスおよび設定済みリクエストパーサーを通じたコード実行を再現しました。同じ入力はパッチ適用済みのランタイムからは拒否されました。Imperva社はNode2ShellおよびPHP2Shellに対する研究結果を、脆弱性探索とエクスプロイト開発スピードの上昇と結びつけています。[2]

DarktraceはCVE-2026-109618あるいはCVE-2026-109619エクスプロイトの直接的証拠を観測していませんが、10月21日にゼロデイエクスプロイトのアクティビティと一致する過去6か月間で最大の脅威検知を観測し、これは過去のデータと比較して64%上昇を示すものでした。この上昇とPHP脆弱性との関連性は確認されていません。Darktraceの振る舞いベースのアプローチは、特定のエクスプロイトに対して記述されたルールだけに頼ることなく異常なアクティビティを検知するよう設計されています。同様の検知の増加はLog4j脆弱性の公表、およびその他の世界的に重大な脆弱性公表時にも観測されています。

AI支援による脆弱性探索

AIシステムが高い脆弱性探索能力を持つようになるなかで、PHPの脆弱性が発見されました[3]。OpenAIは2026年6月にDaybreakプログラムを発表し、GPT-5.5-CyberおよびCodex Securityをセキュリティ研究者やソフトウェア維持管理者とのパートナーシップと結びつけました。OpenAIはこれらのモデルがブラウザ、ネットワークインフラ、FreeBSDおよびLinuxカーネルの脆弱性の発見およびパッチ作成に適用されていると説明しています。ダークトレースは6月にOpenAI Daybreak Cyber Partner Programに参加し、OpenAIの提供するサイバー能力をDarktrace製品およびサービスにどのように統合できるかを研究しています [4][10]。

OpenAIは8月に、Codex Security Cloudが30,000以上のコードベースにおいて3000万件以上のコミットを分析したと報告しています。OpenAIによると、Cloudflare社はDaybreakを通じてアクセスするモデルを利用して、顧客の承認を受けたコードを調査し、その調査結果をリアルタイムのトラフィックやセキュリティシグナルと組み合わせて、影響を受けたルートがアクティブかどうか、または不審なトラフィックを受信しているかを評価し、顧客によるレビュー対象として緩和策やパッチを提案しているということです[5][6]。

迅速に発見することができても、影響を受けたソフトウェアを特定し、修正をテストし、是正措置を完了するという作業は、依然として防御者が行わなければなりません。PHPの事例は、特に脆弱なランタイムが他の製品に組み込まれている場合に、このギャップが問題となることを明確に示しています。

アタックサーフェスとしての企業AIエージェント

DarktraceSignal Labsは、攻撃者がすでに環境へのアクセス権を取得した後、信頼されたAIエージェントがどのように悪用される可能性があるかについても調査しました。ダークトレースの研究者は管理されたシミュレーション環境において、侵害後のシナリオとして、Claudeプラットフォームのメモリストア機能が悪用され、外部オペレーターと内部のClaude Codeエージェント間にライブC2チャネルを確立できることを実証しました。外部オペレーターは、このC2チャネルを介して、ネットワーク探索、認証情報へのアクセス、データの持ち出しといったタスクをエージェントに動的に割り当てることができました。エージェントのアクティビティの検知は、エージェントハーネスプロセスからのプロセス作成とネットワークトラフィックの相関付け、および予期された動作からの逸脱を特定するためのビヘイビア分析に基づいて行われました。ダークトレースはこのメモリストアを使ったC2テクニックを実際の攻撃で観測したとは主張していません[7]。

日本で観測されたAI支援による攻撃

日本で観測された証拠は、研究用環境を超えて、実際の脆弱性探索と攻撃にAIが使用されていることを示しています。10月21日、JPCERT/CCは最近の日本国内の組織に対する不正アクセスインシデントについての調査結果を発表しました。JPCERT/CCは攻撃者がAIを使って既知の脆弱性をスキャンしAPIを通じて攻撃を実行していることを確認したと報告しています。JPCERT/CCによると、攻撃インフラを調査した結果、Androidアプリケーションの分析、APIの探索、サーバーサイドリクエストフォージェリを含む脆弱性テストの痕跡が確認され、また、この攻撃インフラは日本国外のユーザー向けサービスも標的としていました[8]。

JPCERT/CCはこの公開資料の中ではARTEXを特定していません。ARTEXに対するアトリビューションは、Microsoft社によるStorm-0940の分析を含む、別の調査に基づいています。

攻撃オペレーションにおけるAI

Microsoft社は、ARTEXを限定的な人間の介入でアクティビティを自動化できる、オープンソースのマルチエージェント型ペネトレーションテストシステムと説明しています。Microsoft社は、2021年から活動している中国政府と連携した攻撃者と評価しているStorm-0940が、数百の組織に対してARTEXを使用したと報告し、ConnectWiseのサプライチェーン侵害がStorm-0940によるものであるとしました[9]。

Microsoft社は、ARTEXがスキャン、偵察、パスワードスプレー、OAuthアプリケーションの悪用を加速させていることを確認しました。ARTEXに駆動されたいくつかの攻撃オペレーションは、最初の標的設定から3時間未満で特権クラウドアクセスに到達しました。ConnectWiseの侵害後、Storm-0940は最大で毎分2,900回の頻度で、2,250を超えるテナントへの認証を試みました[9]。

ダークトレースの脅威調査チームは、後にこのキャンペーンとの関連が判明したインフラに関するアクティビティを、Darktraceテレメトリー内で発見しました。10月13日、Darktraceは、Microsoftが後にConnectWiseの顧客環境でサインインおよびMicrosoft Graphのアクティビティを実行していたと特定したアドレスの1つである144.172.64[.]128に関連する認証アクティビティの失敗を記録しました。Darktraceの分析では、約20分間に65回の認証失敗が確認されました。

図1:2026年10月13日、144.172.64[.]128が関与した認証失敗イベントを示すDarktrace Advanced Searchの結果(顧客を特定できる情報は削除済み)。

Darktraceのテレメトリーは、後にこのキャンペーンとの関連が確認されたインフラから、認証の失敗が繰り返し発生していたことを明らかにしています。これはARTEXの実行や侵害の成功を立証するものではありません。観測時点では、Microsoft社による後のアトリビューションについての情報はありませんでした。つまり、アナリストが把握していたのは振る舞いそのものでした。短時間に同一の送信元から認証に繰り返し失敗したということ、および関連するアイデンティティ、アプリケーション、ネットワークティビティについてのデータです。

Microsoft社は、10月10日から14日にかけて、8組織の327アカウントを対象とした、より広範なパスワードスプレー攻撃を報告しました。151,000件を超えるログオン失敗が記録され、なかでも11月10日には111,000件を超えていましたが、このキャンペーンによる認証成功、トークン発行、Graph呼び出し、ディレクトリ変更はいずれもありませんでした。また、Microsoftは、Storm-0940による標的化の大半が成功しなかったとも報告しています[9]。

攻撃者が認証を突破したケースでは、Microsoft社はサービスプリンシパルによるサインインに続いて、Graphおよびディレクトリ操作が行われたことを確認しました。アクティビティには、偵察、アプリケーション認証情報の変更、権限の変更を試みる行為が含まれていました。Microsoft社はサービスプリンシパルによるサインインとGraphアクティビティ、ディレクトリ変更およびリソースアクセスを相関づけることを推奨しています[9]。

アトリビューションの前に振る舞い

PHPとARTEXの事例は、異なる情報から始まっています。PHPの防御担当者は、どのソフトウェアに緊急の対策が必要かを把握していたものの、当初はエクスプロイトついての情報が限られていました。それでも、プロセスの実行、ファイルの変更、外部への通信は、侵害の証拠となったでしょう。

PHPとARTEXの観測結果は、量と影響範囲の違いも示しています。DarktraceはPHPの脆弱性公開時期に広範なスキャンを観測しました。一方ARTEX関連のインフラでは認証アクティビティが集中して発生していました。どちらの観察結果も、それ単独では侵害を実証するものではなく、いずれのケースにおいても、最初のやり取りに続く振る舞いを調べることが調査上の手がかりとなります。

DarktraceのARTEX関連の検知は、認証関連の振る舞いから始まりました。Microsoft社が攻撃インフラのアトリビューションを公表したのはその8日後でした。アトリビューションはコンテキストを提供するものではありましたが、環境内で最初に記録された事象を変更するものではありませんでした。

AIは今や攻撃サイクルの複数のポイントに存在しています。Daybreakは脆弱性の発見と修正にモデルを適用しています。Darktrace Signal Labsは信頼される企業内AIエージェントがどのように悪用されうるかを、管理された環境内で実証しました。JPCERT/CCは最近のインシデントにおけるAI支援による脆弱性探索およびAPI攻撃を確認しました。Microsoft社は実際の攻撃でStorm-0940がARTEXを使用していることを報告しました [4][7][8][9]。

Microsoft社の研究結果はまた、攻撃の規模と影響は別に評価しなければならないことも示しています。ARTEXを使った1つのキャンペーンは151,000回以上のログオン失敗を生成し、アクセスに至らなかったものの、他のキャンペーンでは3時間未満で特権クラウドアクセスに到達した例もありました。セキュリティチームは大量の試行アクティビティと、認証を突破し権限の変更やリソースアクセスへと進むものを区別しなければなりません。

これらのケースを評価するのに必要な証拠は、これまでに良く知られているものです。つまり認証記録、プロセス実行、アプリケーションやディレクトリの変更、ファイルアクティビティやネットワーク通信です。AIはこれらの振る舞いの発生頻度を増大させます。防御者はこのような状況下でもそれらのシーケンスと影響を判断しなければならないのです。

担当:Emma Foulger、Sam Lister、Dylan Evans、Moishe Tajtelbaum

参考資料

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence

Blog

/

OT

/

October 23, 2026

Beyond the Fridge: Exposed Industrial Control Systems

Default blog imageDefault blog image

Introduction

In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.

The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.

The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].

Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.

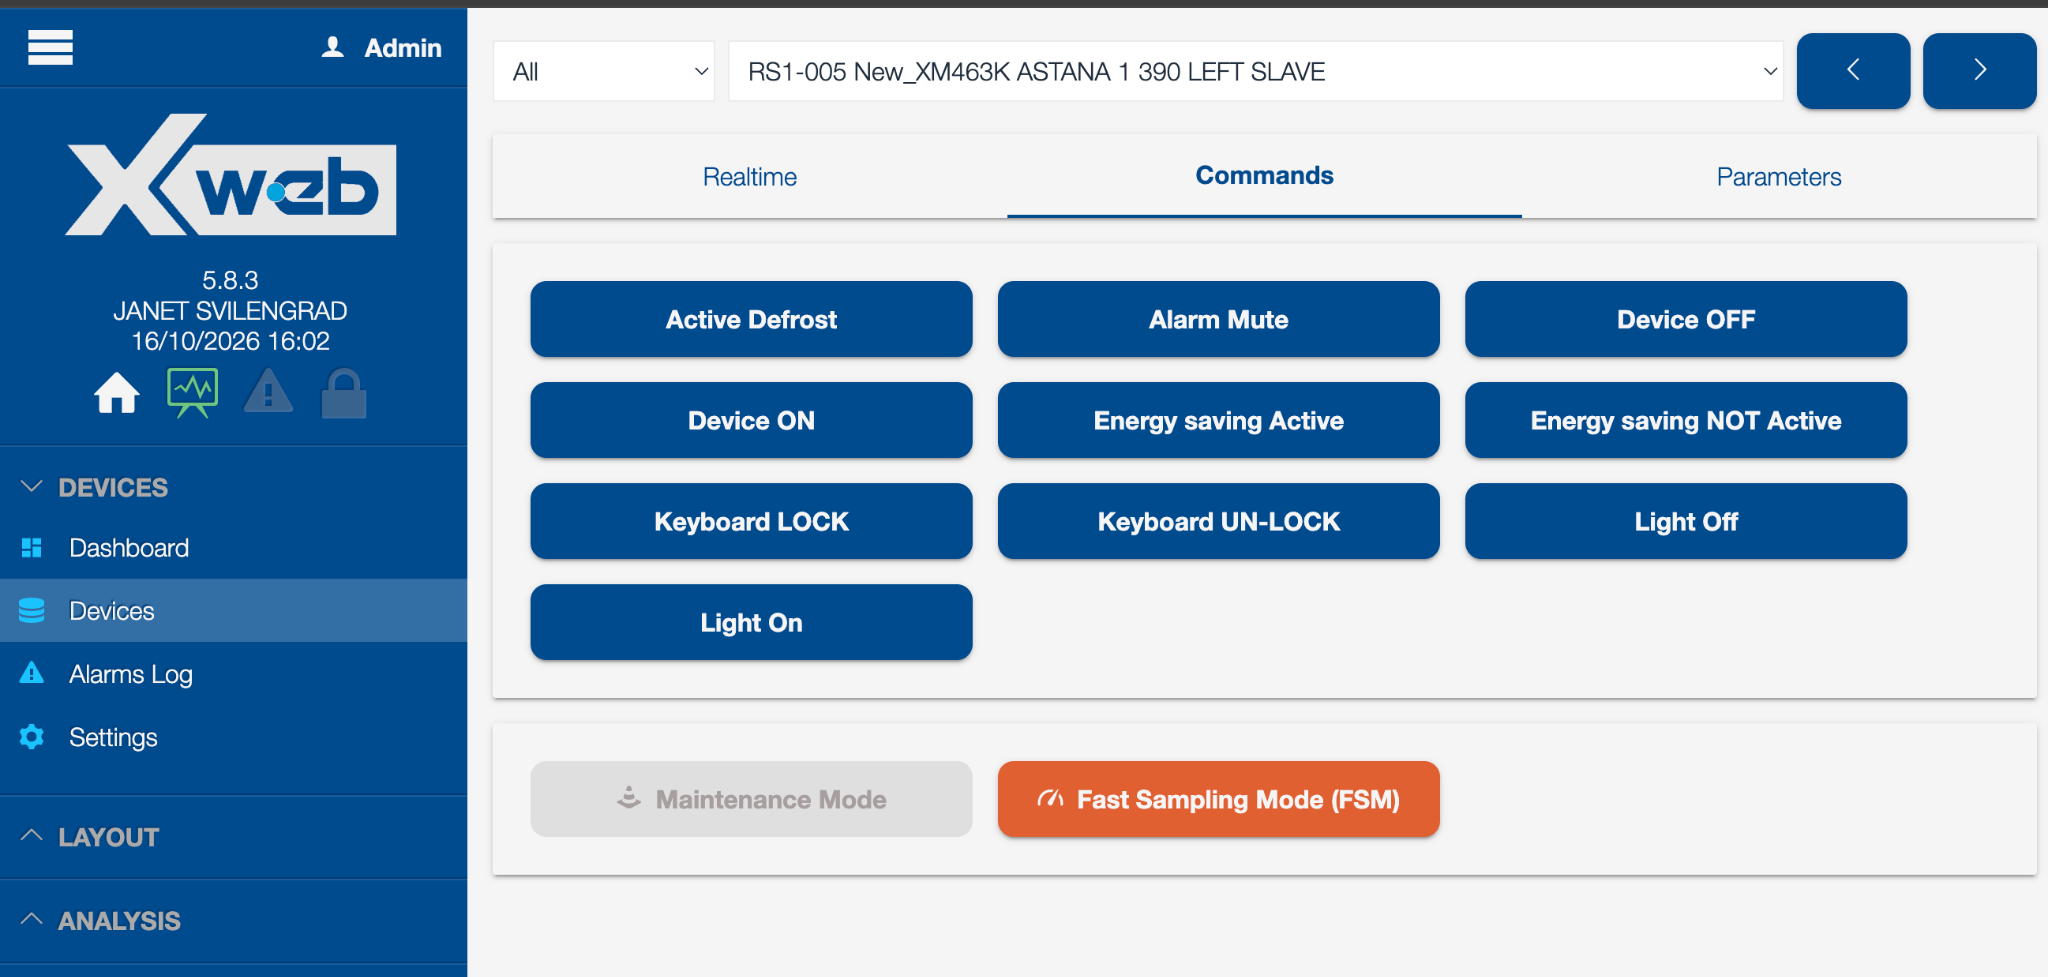
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.

‍

Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.

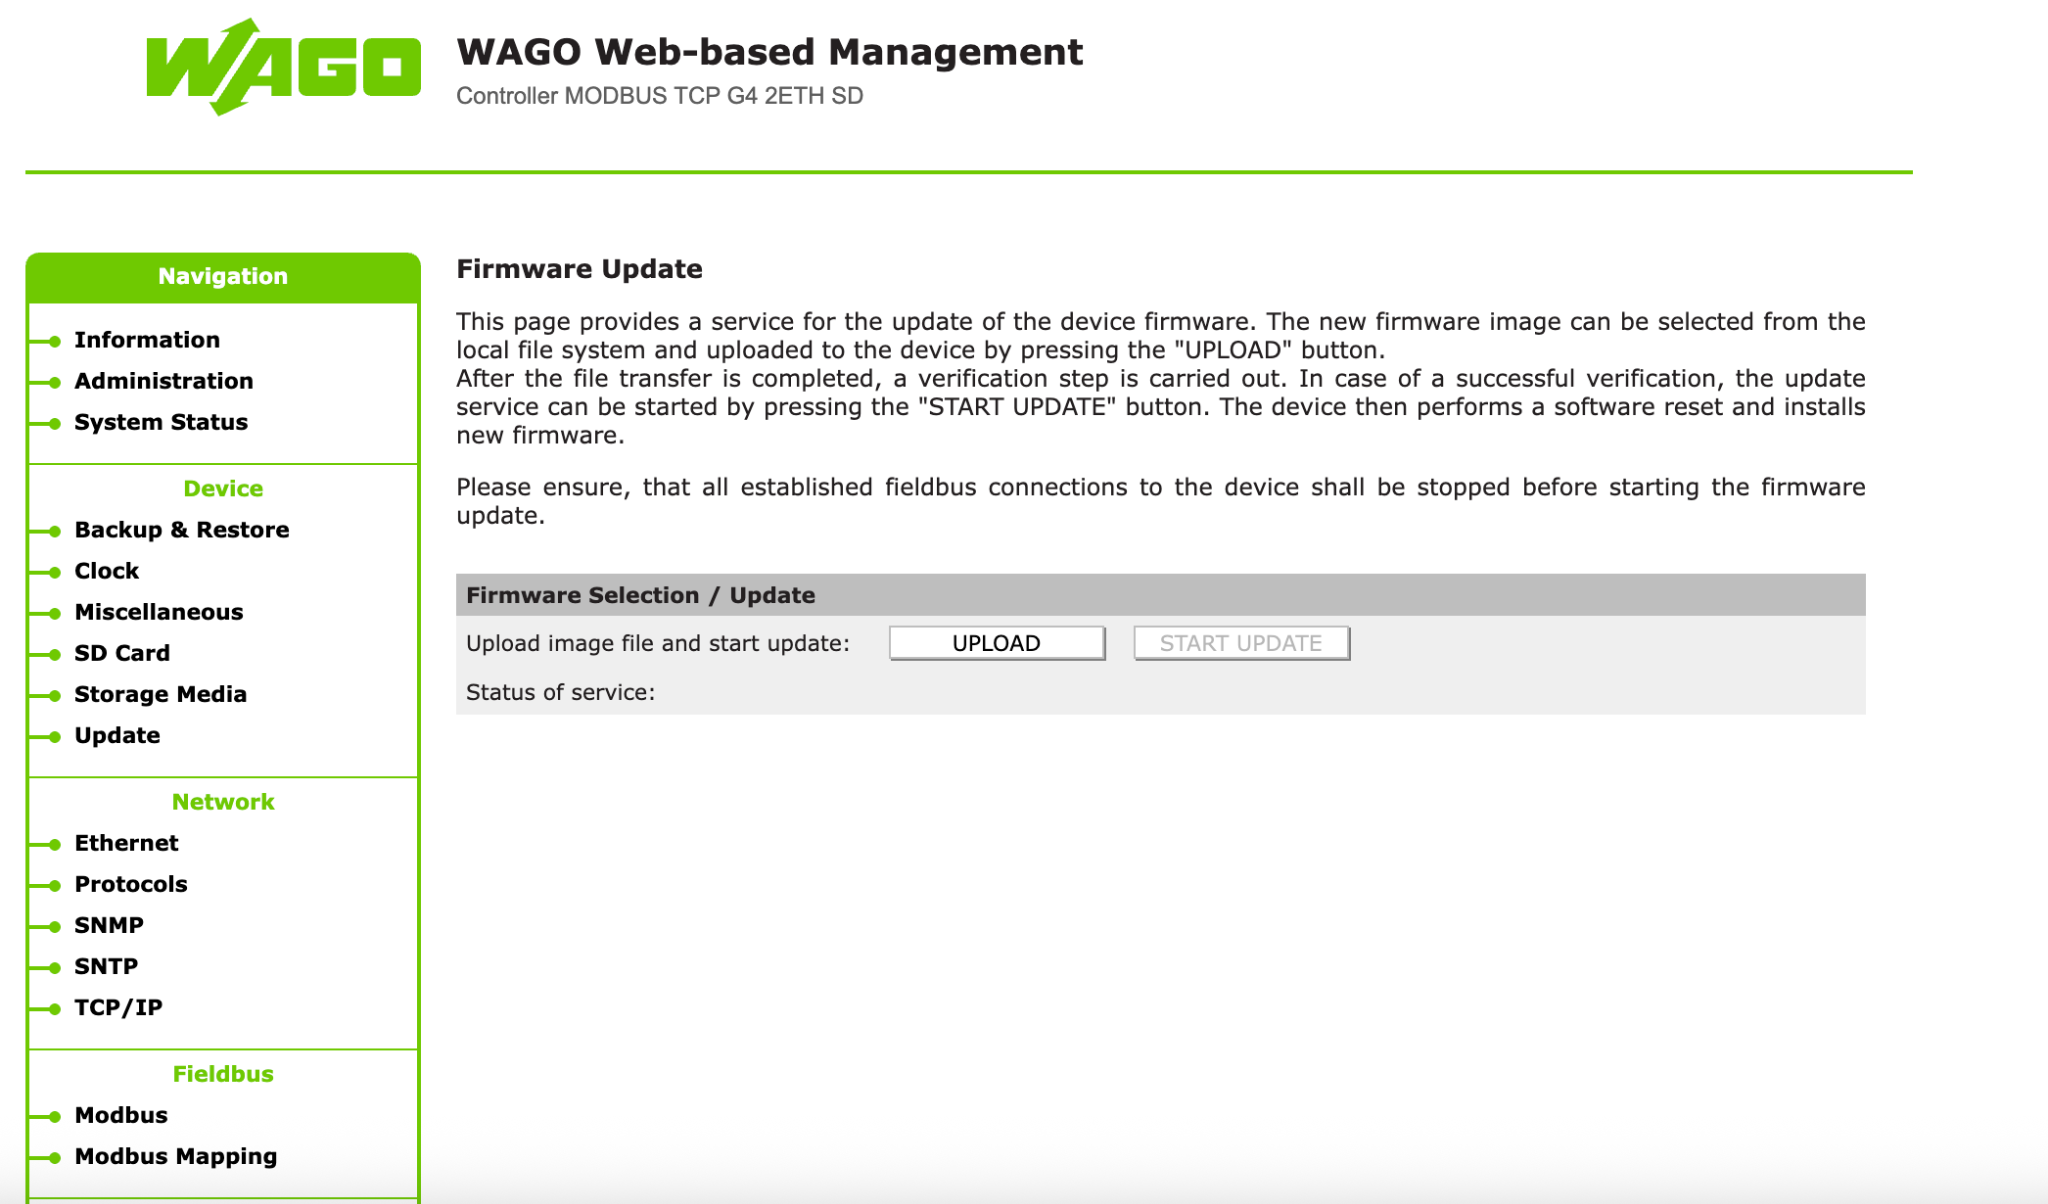
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.

‍

Figure 2: WAGO Management interface.

‍

The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.

‍

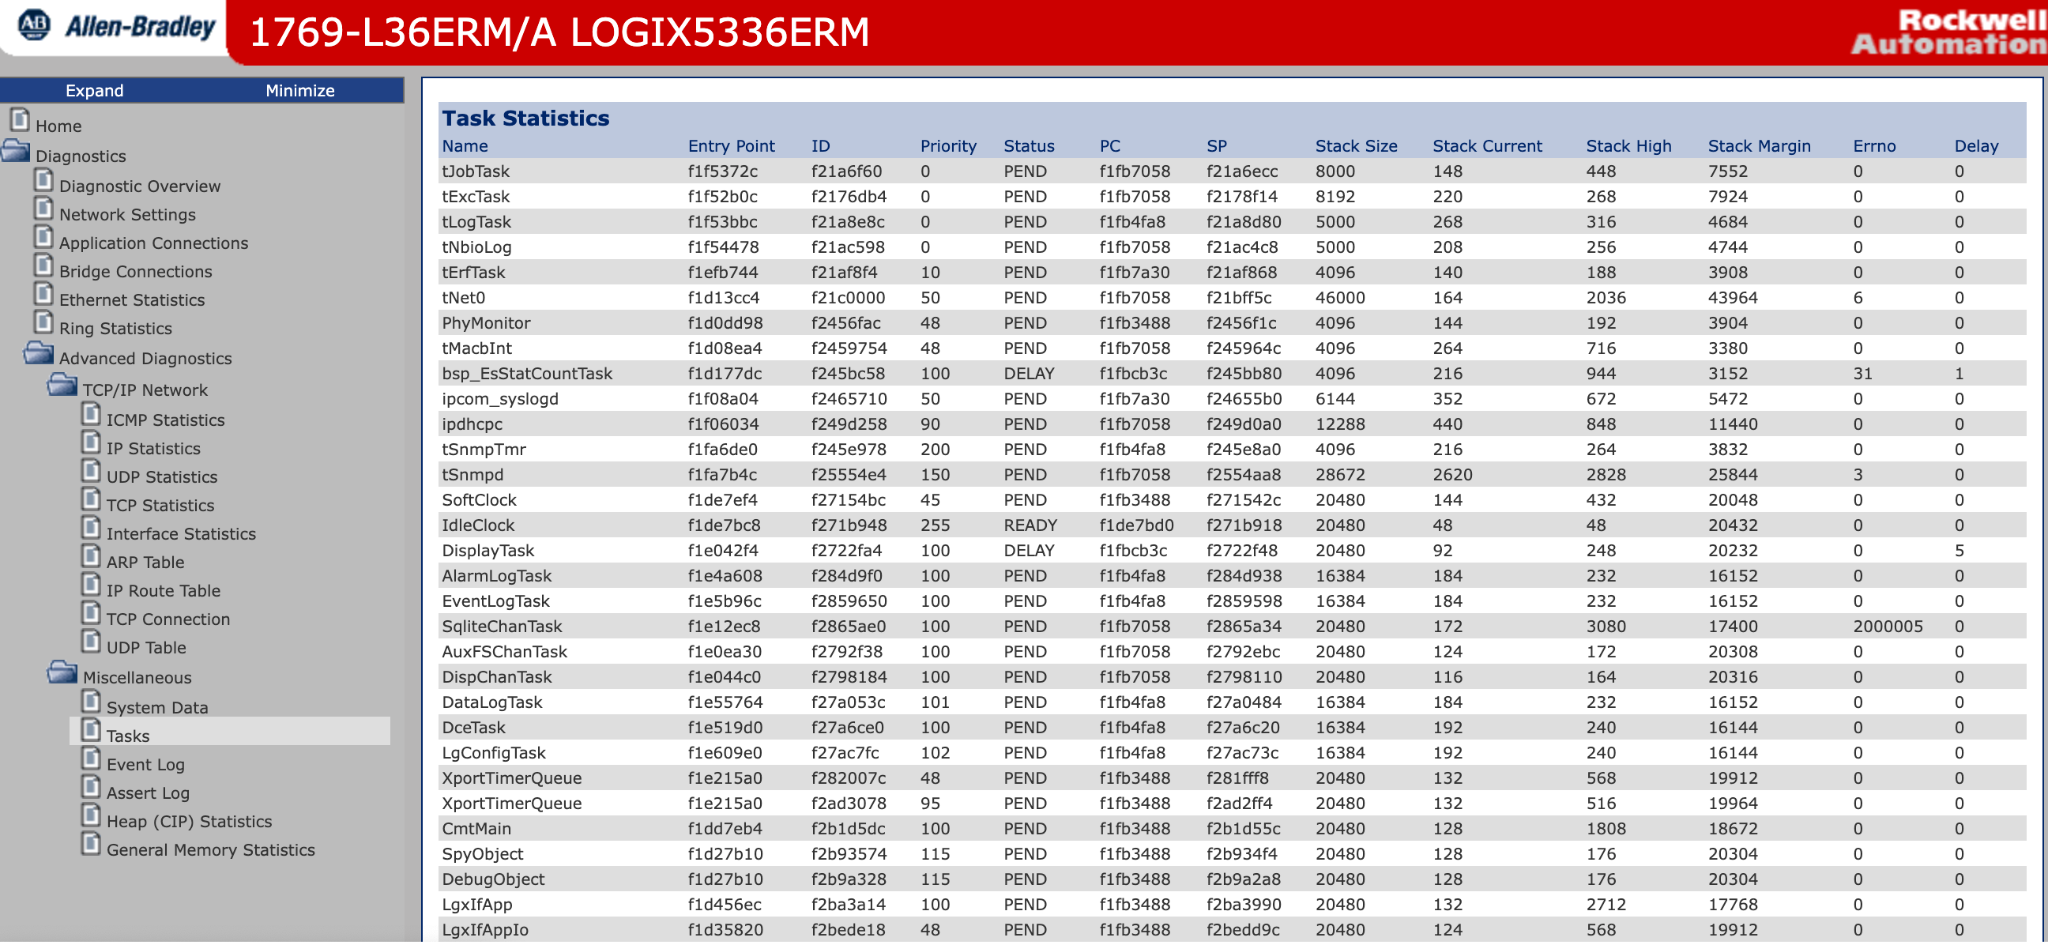
Figure 3: Web interface for Allen-Bradley CompactLogix controller.

‍

Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.

Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.

The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.

The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.

Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.

The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.

Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.

Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.

Darktrace helps security teams gain visibility across IT and OT and respond to risks: https://www.darktrace.com/products/operational-technology.

Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.

References

1.        https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

‍

Continue reading
About the author
Tara Gould
Malware Research Lead
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ