Darktrace continues to innovate with Microsoft in the shared mission to deliver proactive cyber protection tailored to every organization. Joint customers benefit from two distinct, complementary security approaches – combining large scale threat intelligence with enterprise-native security insights – to address the full range of email threats.
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Francesca Bowen
Global VP, Strategic Alliances
Share
27
Jun 2024
Darktrace has been named as Microsoft UK Partner of the Year for 2024! The Microsoft Partner Awards recognize winners for their commitment to customers, impact of solutions, and exemplary use of Microsoft technologies.
Whilst the award was granted based on our innovations combining Darktrace/Email and Microsoft Defender for Office 365, our shared values go beyond technology. Darktrace stood out for the integration of our products to deliver exceptional security value to customers, as well as our investment in partnerships, marketplace and go to market. Microsoft was also impressed with our strong commitment to diversity and inclusion and our broader contribution to both the UK economy and the UK tech sector.
Microsoft Defender for Office 365 + Darktrace/Email leave attackers nowhere to hide
The email threat landscape is constantly evolving. Attacks are becoming more sophisticated, more targeted and increasing in multi-stage payload attacks. Across the Darktrace customer base in 2023 alone, we have seen a 135% increase in ‘novel social engineering attacks’, corresponding with the rise of ChatGPT, 45% of phishing emails were identified as spear phishing attempts and a 59% increase in multi-stage payload attacks.
Legacy defenses were built to address a high volume of unsophisticated attacks, but generative AI has shifted the threats towards lower quantity yet very sophisticated, high impact targeted attacks. Microsoft Defender for Office 365’s rapid innovation has outpaced the Secure Email Gateway’s rule and signature based historical data approach. Customers no longer need email gateways which duplicate workflows and add expense native to their Defender for O365 solution.
Point email solutions overlap with Microsoft in 3 key areas: detection approach, workflows, capabilities
Detection - Microsoft receives trillions threat signals daily, giving customers the broadest scope of the attack landscape. Darktrace combined with Microsoft unites business and attack centric approaches
Workflows – any Microsoft configurations are reflected automatically in Darktrace/Email. Users can keep daily workflow in Microsoft, while a traditional SEG requires duplicated workflows
Capabilities – Microsoft handles foundational elements like archiving/encryption/signature matching while Darktrace handles advanced threat security
Darktrace/Email is built to elevate, not duplicate, Microsoft email security – removing the burden of operating legacy point solutions and blocking 25% more threats. Robust account takeover protections to stop the 38% of sophisticated threats other tools miss. Customers can seamlessly correlate activity and insights across Microsoft email, DMARC and Teams to stop threats on average 13 days earlier.
Azure Marketplace
Microsoft Azure customers can access Darktrace in the Azure Marketplace to take advantage of the scalability, reliability, and agility of Azure to drive rapid IT operations and security integrations across the enterprise. Customers can leverage their Microsoft Azure Consumption Commitments (MACC), making procurement simple. As UK Partner of the Year winner, customers know they have a trusted partner with Darktrace and a proven solution to work seamlessly with Azure.
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Darktrace / EMAIL Expands Behavioral Defense Across Email and Collaboration Workflows
New capabilities help employees understand suspicious content, give administrators more control over sensitive data, and show security teams where risky workflows sit across the organization.
AIは今や攻撃サイクルの複数のポイントに存在しています。Daybreakは脆弱性の発見と修正にモデルを適用しています。Darktrace Signal Labsは信頼される企業内AIエージェントがどのように悪用されうるかを、管理された環境内で実証しました。JPCERT/CCは最近のインシデントにおけるAI支援による脆弱性探索およびAPI攻撃を確認しました。Microsoft社は実際の攻撃でStorm-0940がARTEXを使用していることを報告しました [4][7][8][9]。
[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/
[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/
[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak
[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/
[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.
[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html
[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/
[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations
Beyond the Fridge: Exposed Industrial Control Systems
Introduction
In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.
The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.
The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].
Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.
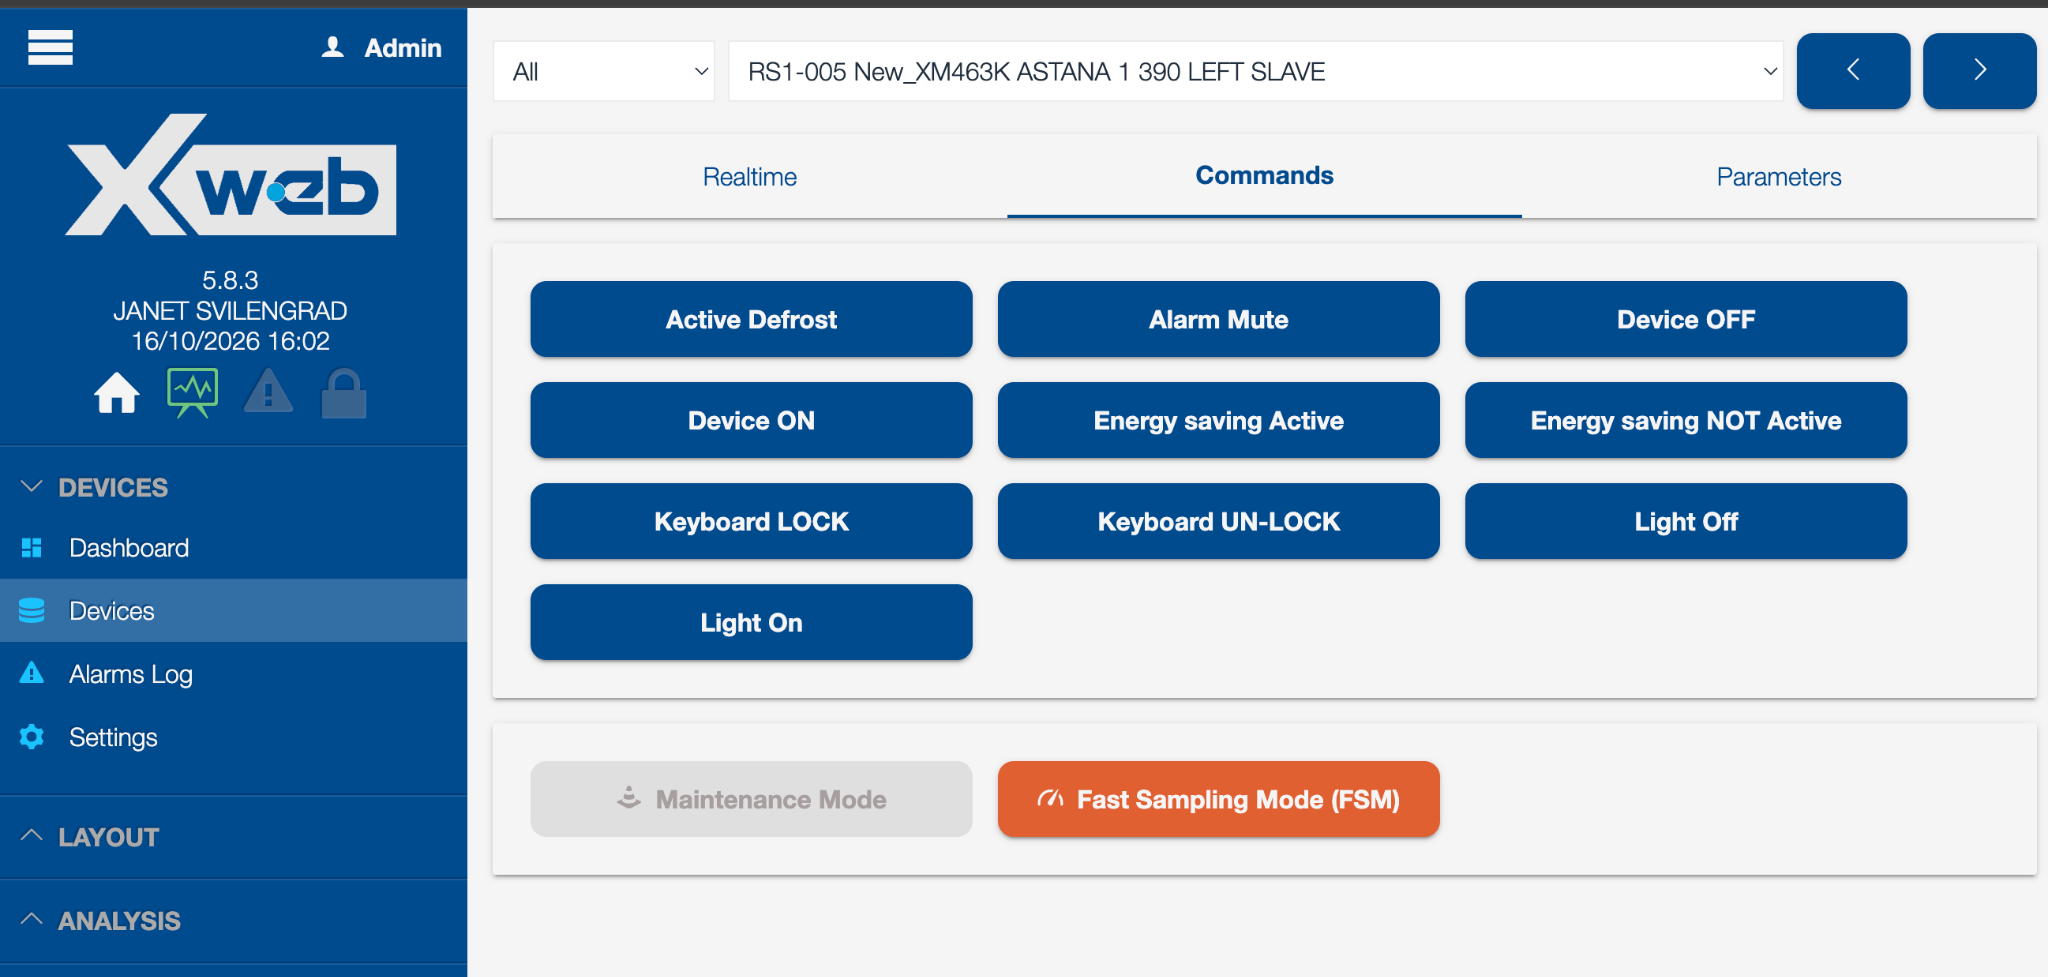
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.
Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.
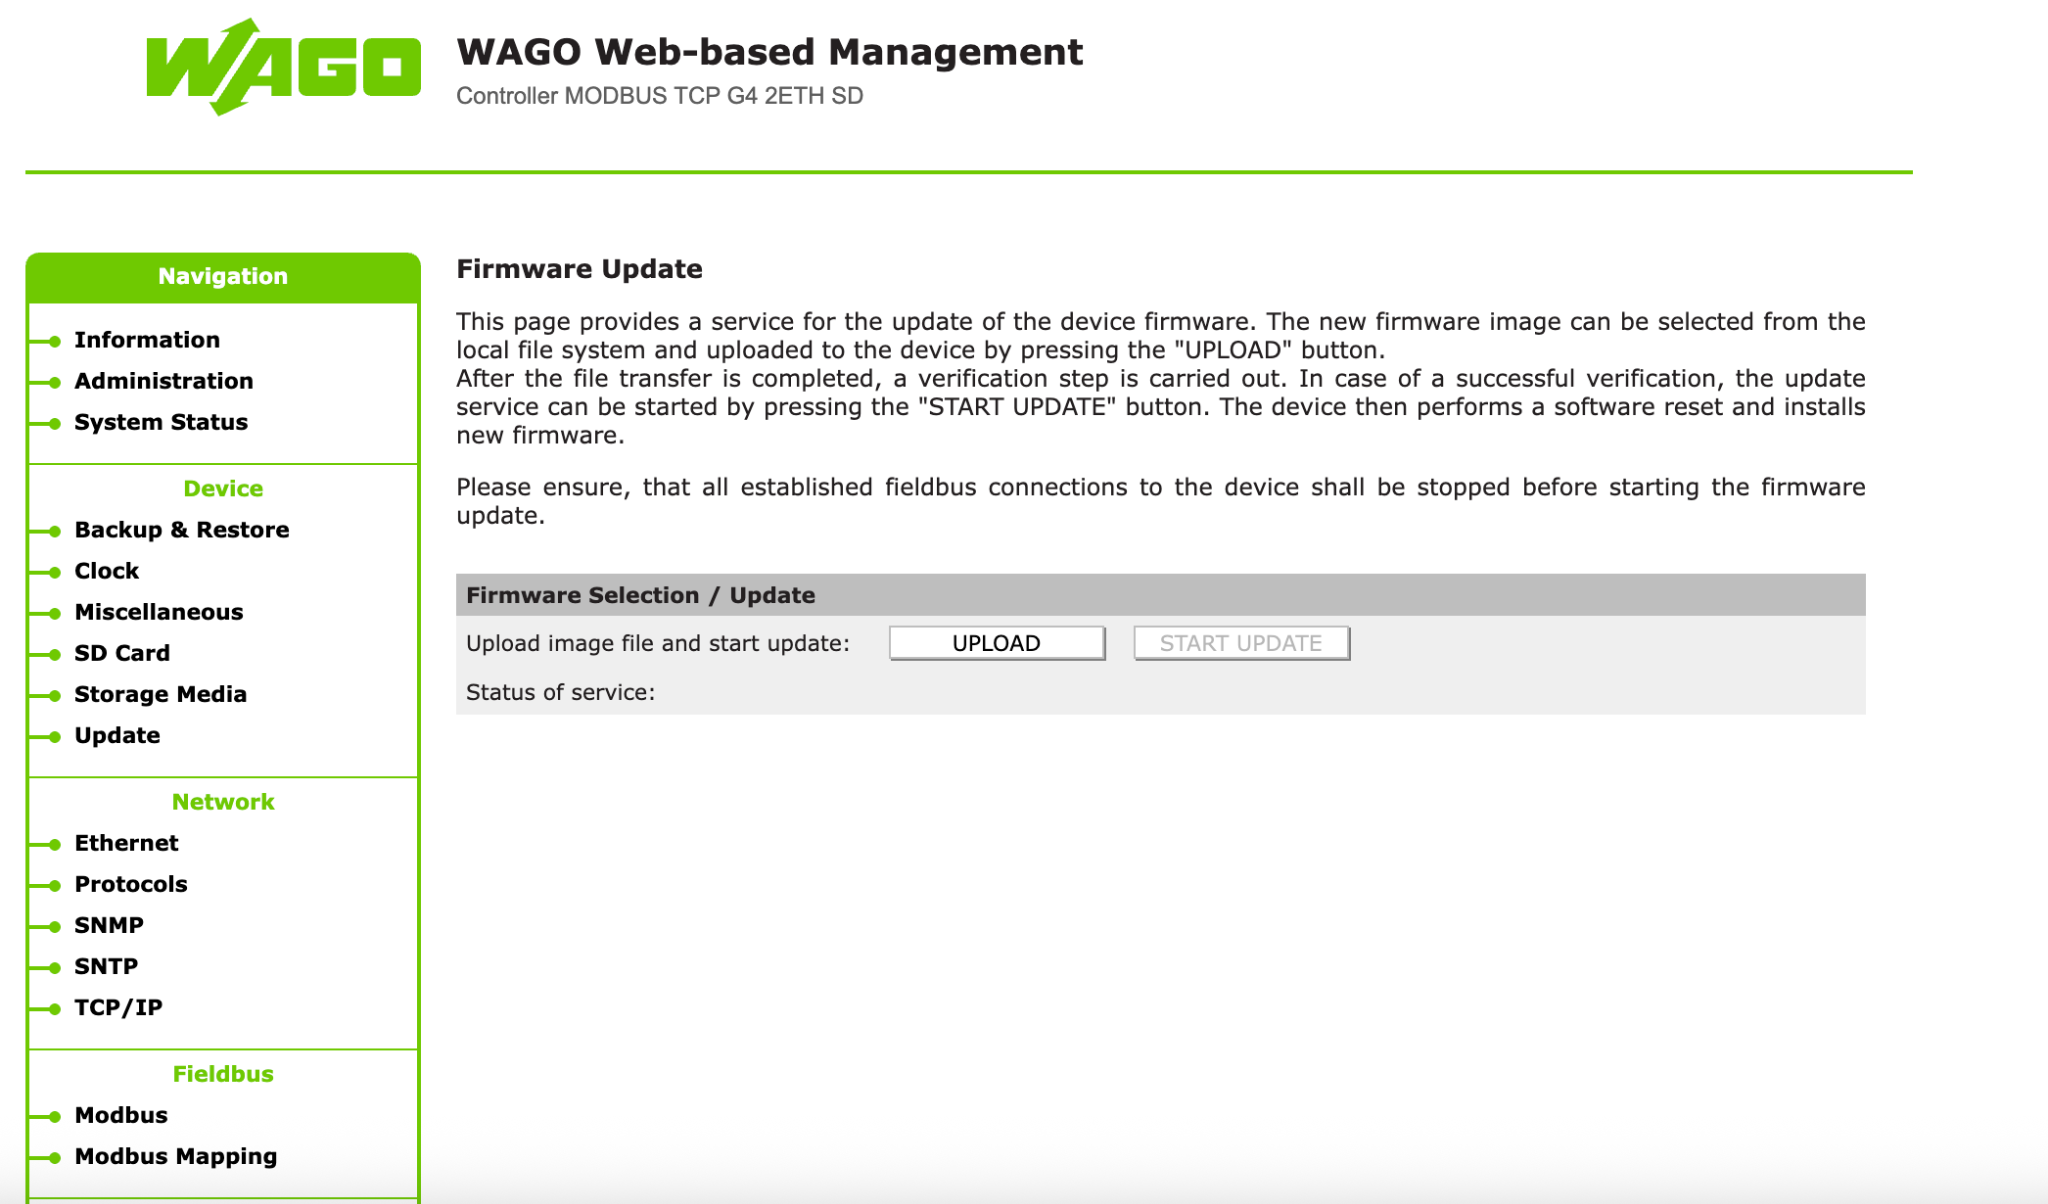
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.
Figure 2: WAGO Management interface.
The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.
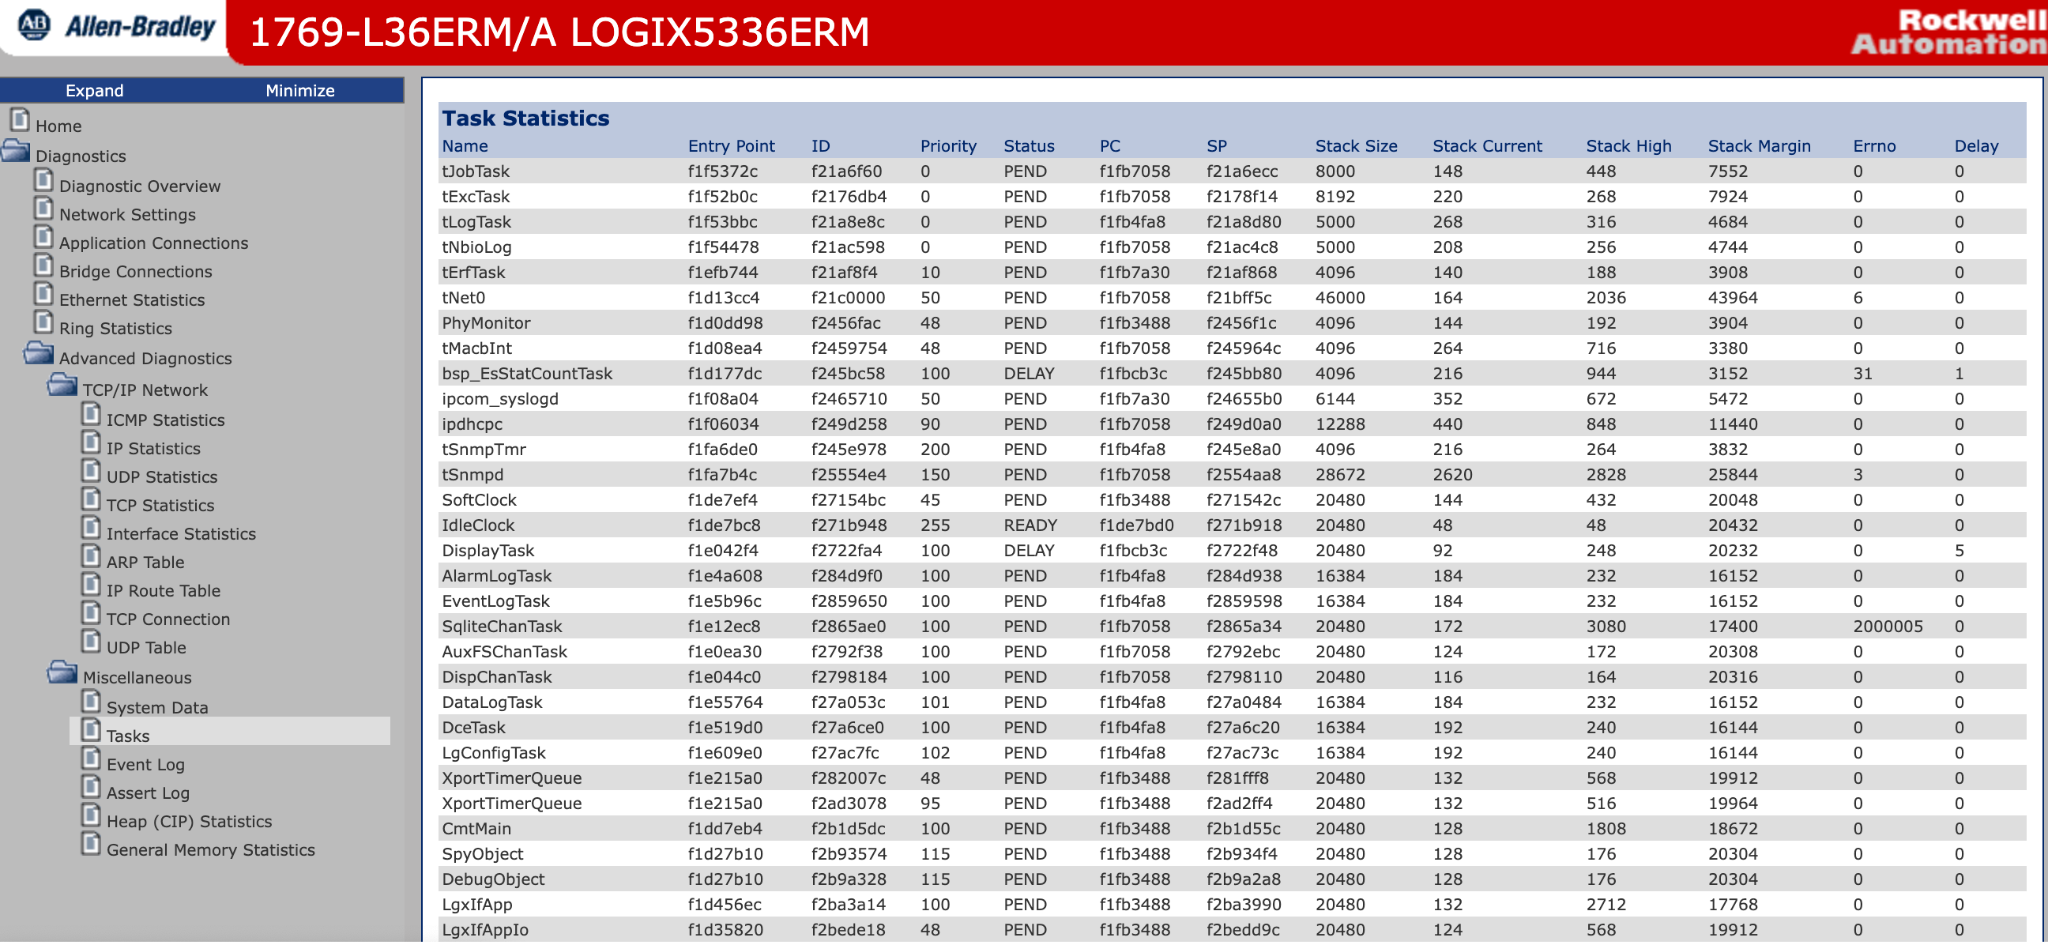
Figure 3: Web interface for Allen-Bradley CompactLogix controller.
Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.
Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.
The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.
The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.
Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.
The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.
Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.
Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.
Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.