
This week at Ignite, Microsoft announced that Microsoft Perception is generally available. It is a significant milestone for the industry, and one we welcome as a Microsoft partner. Microsoft is putting an architectural bet at the center of its security strategy: AI has changed the speed of cyber, and defense must change with it.
At Darktrace, we’ve long held the same view, so it’s encouraging to see a partner of Microsoft’s scale articulate it so clearly and bring it to market.
Security gets a team of agents
Perception is Microsoft’s agentic security system. It orchestrates red, blue, and green team agents through playbooks in a closed loop: red agents simulate attacks, blue agents detect, triage and investigate, and green agents fix and remediate. Rather than adding another assistant to the SOC, it creates coordinated teams of agents that share context. Security teams set the guardrails and approve high-impact actions.
Microsoft frames this as a three-layer cyber stack: signals, sensors and actuators; a context layer; and agents, harness and models on top. Together with partner sources, the foundation produces more than 165 trillion signals per day.
The announcement also makes a second point that matters just as much. Microsoft is treating AI agents themselves as a new insider-risk category. In its words, “Agents are the new insiders.” They work at machine speed, around the clock, with broad access to data, apps, tools and other agents, and like any insider they can make mistakes, be manipulated or be compromised. New capabilities such as Dynamic Agent Risk (now in preview) and dynamic Conditional Access controls are designed to assess and contain that risk as it changes.
Four truths about security in the agentic era
The announcement is built on four ideas, and together they describe the new reality security teams are defending:
- Static security can’t keep up. Microsoft validates what many security practitioners have observed; the window between a vulnerability’s discovery and its exploitation is collapsing from months to minutes. Manual triage can’t answer that pace. Autonomous detection and response is now a requirement, not simply a “nice to have”.
- Agents must be treated as insiders. The question for security teams is no longer only “who is this user?” but “what is this agent actually doing?” Identity tells you who an agent is. Policy tells you what it is allowed to do. Neither tells you whether its behavior is normal.
- Security is moving from signatures to behavior and context. Dynamic Agent Risk looks across identity, data, endpoint, cloud and network signals and asks whether an agent’s actions are drifting from the intent of its task. That is behavioral thinking, and it is philosophically close to the Adaptive AI approach Darktrace has pioneered.
- Machine-speed attacks demand machine-speed response. Humans set the objectives and guardrails. Autonomous systems do the work inside them, both detecting and acting. Microsoft’s design has agents investigate, recommend and, within approved boundaries, act, with security teams setting the limits. At this pace, the gap between knowing something is wrong and doing something about it has to close to seconds.
The opportunity: where control plane meets behavioral context
Perception is an extraordinary control plane for agentic security. The question for security leaders is how to make it even more effective in the environments they actually run.
Real enterprises are heterogeneous. They run AWS and Google Cloud alongside Azure, and OT, IoT and third-party identity alongside Entra. Increasingly they also run AI agents and MCP-connected systems that no single vendor’s telemetry fully covers. Microsoft’s architecture recognizes this, with more than 500 connectors into the wider ecosystem.
That is where Darktrace’s role is distinct. The challenge isn’t signal volume, where Microsoft’s scale is unmatched. It’s deeply understanding what is normal for a specific organization, across every system, identity and agent in it. Together, we deliver two complementary layers:
- Microsoft brings global intelligence and orchestration. It tells you what is known, what it means and what to do about it.
- Darktrace brings organization-specific behavioral context. It tells you what is unusual here, right now, across the organizations AI, people and infrastructure, even if it has never been seen before.
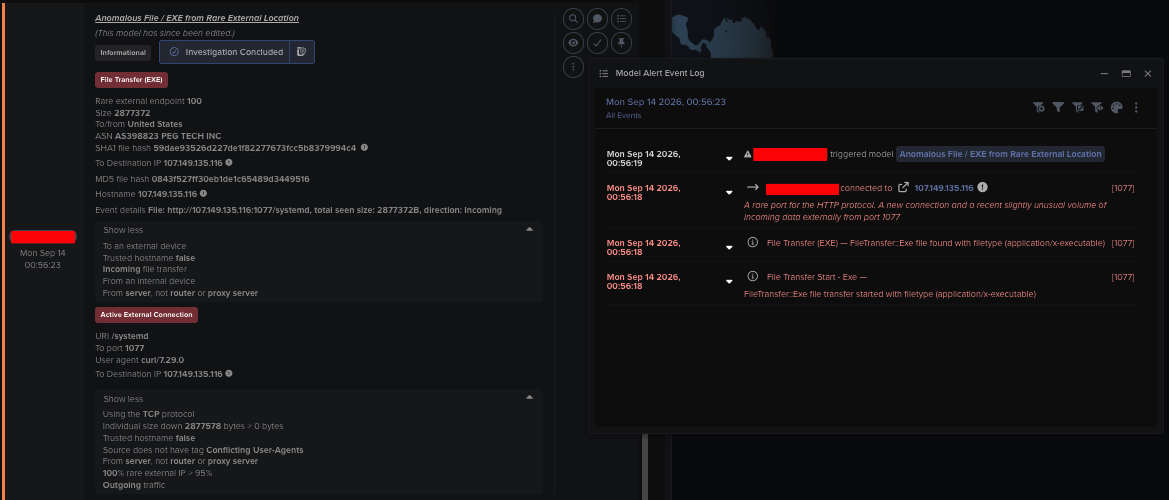
The difference shows up in the numbers. A large enterprise generates billions of signals. Darktrace turns them into thousands of incidents, narrows those to hundreds of AI-led investigations, and surfaces as few as 20 that merit a human’s attention. For an agentic SOC, that kind of evaluated, prioritized input makes agents faster, not busier.
As enterprises deploy more agents, the hard problem becomes behavior that is technically permitted but unusual, manipulated or inconsistent with the agent’s purpose. Consider an agent that normally reads Salesforce records during US business hours and suddenly starts enumerating SharePoint and opening unusual outbound connections. Each step may use valid access and approved tools, so identity and policy checks can all pass. Spotting it requires knowing the behavior is abnormal for this agent, in this environment, right now.
That is why one principle in Microsoft’s AI Transparency Initiative matters so much: organizations should be able to see what their AI accesses and does, and independently verify those actions.
- Identity and permissions answer “should this agent be allowed to do this?”
- Behavioral defense answers “even though it is allowed, is what it’s doing normal?”
Deterministic controls around non-deterministic AI are the right foundation, and continuously learned baselines are how organizations can verify those controls are working.
What to look for in an agentic SOC architecture
As organizations adopt platforms like Perception, we’d encourage them to look for three capabilities:
- Behavioral context in the control plane. Agents work best with high-confidence signals rather than thousands of raw alerts: here is the behavior that materially deviates from this organization’s learned normal.
- Behavioral reasoning on demand. During an investigation, agents should be able to ask what changed around a given identity, device or agent in the last 24 hours, and get a clear answer.
- Autonomous, coordinated response across the stack. Response should be as fast as the threat without being reckless: acting immediately when confidence is high, constraining or reversing actions when it isn’t, and keeping a human in the loop when it matters. Within policy and human-approval guardrails, it should target the abnormal behavior rather than the whole business process and span identity, endpoint and the wider environment.
These are the areas where we’re focused, and where we look forward to working with Microsoft and the broader ecosystem.
Response is where speed is won or lost
In the AI era, detection and investigation only matter if action follows quickly. Perception brings agentic orchestration to that problem, with security teams setting the guardrails and approving high-impact steps. Autonomous response from Darktrace takes a complementary approach: it responds on behavioral deviation, in a way that is proportionate and targeted. It can interrupt activity that is abnormal for that specific device, identity or agent while leaving normal business activity running.
The two approaches fit together naturally. Behavioral signals can tell an orchestration layer that something has changed and how confident the system is. Orchestrated playbooks can then coordinate wider containment across identity, endpoint and cloud, within the policies customers define.
The bigger picture
The industry’s architecture is converging on identity, policy, telemetry, behavior, autonomous reasoning and machine-speed response. Microsoft is building formidable pieces of that picture, especially identity, policy, telemetry and orchestration.
Behavior is the layer Darktrace is built to provide: an independent intelligence that continuously learns how humans, machines and AI agents normally act, detects the moment reality departs from intent, and can respond to that deviation in a targeted, proportionate way that keeps normal business running. When attacks move at machine speed, understanding what is abnormal and acting on it quickly have to go together.
Perception brings together what Microsoft knows and orchestrates the response across its stack. Darktrace helps organizations understand what is normal for them and act on what isn’t. Customers building their agentic security strategy will need both.
Congratulations to our partners at Microsoft on this milestone. We look forward to helping customers secure the agentic era together.