ブログ
/
Cloud
/
January 13, 2026

クラウドセキュリティが本当に重要な場所はランタイム:検知、フォレンジック、リアルタイムアーキテクチャ認識の重要性

クラウドセキュリティはこれまで予防、ポスチャ管理、設定にかなりの重点が置かれてきました。しかし実際の攻撃はそこでは発生しません。 攻撃はランタイムにおいて、稼働中のワークロードやアイデンティティにわたって進行していきますが、そこでは可視性が限られており証拠が短時間で消滅します。 このブログではランタイムが保護すべき最もクリティカルなレイヤーである理由、動的なクラウドの挙動を攻撃者がどのように悪用しているか、なぜポスチャベースだけでは不十分かを紹介します。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Adam Stevens
Senior Director of Product
Default blog image
13
Jan 2026

はじめに:予防からランタイムへ重点をシフト

クラウドセキュリティは過去10年間予防に的を絞ってきました。コンフィギュレーションを厳格にし、脆弱性をスキャンし、CNAPP(Cloud Native Application Protection Platforms)を通じてベストプラクティスを適用することです。これらの機能も引き続き重要ではありますが、クラウド攻撃が発生するのはそこではありません。

攻撃はランタイムに発生します。それは動的かつ短命な、絶えず変化する実行レイヤーであり、そこではアプリケーションが実行され、権限が付与され、アイデンティティが機能し、ワークロード間の通信が発生します。また、ランタイムは防御者にとってこれまで可視性が最も限られ 、対応に使える時間が最も少ないレイヤーでもあります。

現在の脅威ランドスケープでは抜本的なシフトが求められています。今やクラウドリスクを軽減するには、ポスチャやCNAPPのみの静的なアプローチを超えて、さまざまなワークロードおよびアイデンティティにわたるリアルタイムのビヘイビア検知を行うとともに、フォレンジック用の証拠を自動的に保全する必要があります。防御者に必要なのは、組織のクラウド環境の「正常」についての継続的な、リアルタイムの理解と、膨大なデータストリームを処理して攻撃者による動作の発生を示す逸脱を見つけだすことのできるAIです。

ランタイム:攻撃が発生するレイヤー

ランタイムは動いているクラウドです — コンテナが開始/停止され、サーバーレス関数が呼び出され、IAMロールが割り当てられ、ワークロードが自動スケールし、数百のサービス間をデータが流れています。また、攻撃者が次を行うところでもあります:

  • 盗まれた認証情報を武器化
  • 権限を昇格
  • プログラムによるピボット
  • 悪意ある計算リソースのデプロイ
  • データを改ざんあるいは抜き出し

問題は複雑です:ランタイム証拠は短命だからです。コンテナは消滅し、重要なプロセスデータは数秒で消失します。人間のアナリストが調査を始めるころには、アラートを理解し対応するために必要なデータは、既になくなっていることがしばしばです。この揮発性によりランタイムは監視が最も困難なレイヤーでああるとともに、保護すべき最も重要なレイヤーでもあります。

Darktrace/ CLOUDがランタイム防御にもたらすもの

Darktrace / CLOUD はクラウド実行レイヤーのために開発されたツールです。攻撃の数時間後あるいは数日後ではなく、その進行と同時に検知、封じ込め、理解するのに必要な機能を統合しています。その価値を定義する要素は4つあります:

1. ビヘイビアベースの、リアルタイム検知

クラウドサービス、アイデンティティ、ワークロード、データフローに渡る通常のアクティビティを学習し、シグネチャが存在しなくても、実際の攻撃者の挙動を示す異常を見つけ出します。

2. フォレンジックレベルのアーチファクトを自動収集

Darktraceは脅威を検知したその瞬間に、揮発性のフォレンジック証拠をキャプチャします。エフェメラルリソースからのデータを含め、ディスク状態、メモリ、ログ、プロセスコンテキストを自動的に保全します。これにより、ワークロードが停止し証拠が消える前に何が起こったかについての真実を記録することができます。

3. AI主導の調査

Cyber AI Analystはクラウドの動作を、理解しやすいインシデントストーリーにまとめ、アイデンティティの挙動、ネットワークの流れ、クラウドワークロードの動作を相関付けます。アナリストは個別のダッシュボード間を移動したり、タイムラインを人手で再構築したりする必要がなくなります。

4. リアルタイムのアーキテクチャ認識

Darktraceはクラウド環境の動作状況を継続的にマッピングします。これにはサービス、アイデンティティ、接続、データの経路が含まれます。このリアルタイムの可視性により異常が明確に識別でき、調査が劇的に加速します。

これらの機能が統合され、ランタイム第一主義のセキュリティモデルが構築されています。

CNAPPだけでは不十分な理由:

CNAPPプラットフォームは、デプロイメント前のチェックから開発者ワークステーションまで、設定ミスの発見、問題のある権限の組み合わせ、脆弱なイメージ、リスクの高いインフラの選択などを特定するのに優れています。しかしCNAPPのカバーする範囲の広さは、その限界にもなります。CNAPPは体制を管理するものです。ランタイム防御は動作を問題にしています。

CNAPPは問題が起こる可能性を教えてくれますが、ランタイム検知は今現在どんな問題が起こっているかを知らせます。

短命な証拠を保全する、動作をドメイン間で相関付ける、あるいは実際のインシデント発生中に必要な精度とスピードをもって攻撃を封じこめるといったことは、CNAPPには不可能です。予防も不可欠ですが、予防だけでは、既にクラウド環境内で活動している攻撃者を阻止することはできないのです。

実際にAWSで発生したシナリオ:ランタイム監視が有効な理由‍

Darktrace / CLOUDが最近検知したあるインシデントは、クラウド侵害の進行の様子と、ランタイム可視性が必要絶対条件である理由を示す好例です。以下に紹介するすべてのステップは、動作をリアルタイムに監視している場合にのみ可能な検知を表しています。

1. 外部での認証情報の使用

検知: 通常とは異なる外部ソースの認証情報使用:攻撃者がこれまでに見られたことのない場所からクラウドアカウントにログインします。これはアカウント乗っ取りの最も早い兆候です。

2. AWS CLIピボット

検知: 通常とは異なるCLIアクティビティ:攻撃者はプログラムによるアクセスに切り替え、疑わしいホストからコマンドを発行することで自動化し、同時にステルス性も獲得します。

3. 認証情報の操作

検知: 稀なパスワードのリセット:新たなパスワードをリセット、割り当てることにより、永続性を確立し既存のセキュリティコントロールをすり抜けます。

4. クラウド偵察

検知: 大規模なリソースディスカバリ:攻撃者はバケット、ロール、サービスの列挙を行い、高価値なアセットを識別して次のステップの計画を立てます。

5. .権限昇格

検知: 異常なIAM更新:許可のないポリシー更新またはロール変更により、攻撃者に高いアクセス権限やバックドアを与えます。

6. 悪意ある計算リソースのデプロイ

検知: 通常と異なるEC2/Lambda/ECS 作成:攻撃者はマイニング、水平移動、またはさらなるツールのステージングのための計算リソースをデプロイします。

7. データアクセスまたは改ざん

検知: 通常と異なるS3変更:攻撃者はS3権限またはオブジェクトを変更します。多くの場合データ抜き出しまたは破壊の前段階です。

ポスチャスキャンではこれらのアクションの一部しか発見できず、しかも事後になります。
これらすべてのランタイム検知は、攻撃が進行している間のリアルタイムの動作監視によってしか可視化できません。

クラウドセキュリティの未来はランタイム第一主義

クラウド防御はもはや予防だけを中心にすることはできません。現代の攻撃は、高速に変化するワークロードやサービス、そして — きわめて重要な — アイデンティティが複雑に入り組んだ、ランタイムで進行します。リスクを軽減するには、悪意あるアクティビティが発生次第、短命な証拠が消失し攻撃者がアイデンティティレイヤーを移動する前に、それを検知、理解、封じ込める能力が必要です。

Darktrace / CLOUD はクラウドで最も揮発性かつ重大な結果を伴うランタイムに対し、動作、ワークロード、アイデンティティに対する一元的な可視性を通じて、完全に防御可能なコントロールポイントに変えることによりこのシフトを実現します。Darktrace / CLOUDは以下を提供します:

  • リアルタイムビヘイビア検知: ワークロードおよびアイデンティティのアクティビティ‍
  • 自律遮断: アクションによる迅速な封じ込め‍
  • 自動的なフォレンジックレベル証拠: イベントが起こった瞬間に保全‍
  • AI駆動の調査: 実際の攻撃者のパターンから弱いシグナルを識別‍
  • リアルタイムのクラウド環境インサイト: コンテキストと影響を即座に理解

クラウドセキュリティは問題が起こる可能性 に対する防御から現在 起こっていることに対する、ランタイムの、さまざまなアイデンティティに渡る、攻撃者と同じスピードでの防御へ進化する必要があります。防御者がアドバンテージを取り戻すための方法は、ランタイムとアイデンティティの可視性の統合です。

[related-resource]

Darktrace / CLOUDの機能について知る

ソリューション概要をお読みになり、Darktrace / CLOUD が多様なクラウド環境に対応するリアルタイムクラウド検知および対応により、クラウド脅威をランタイムで防御する仕組みをご確認ください。

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Adam Stevens
Senior Director of Product

More in this series

No items found.

Blog

/

AI

/

September 30, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

September 30, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

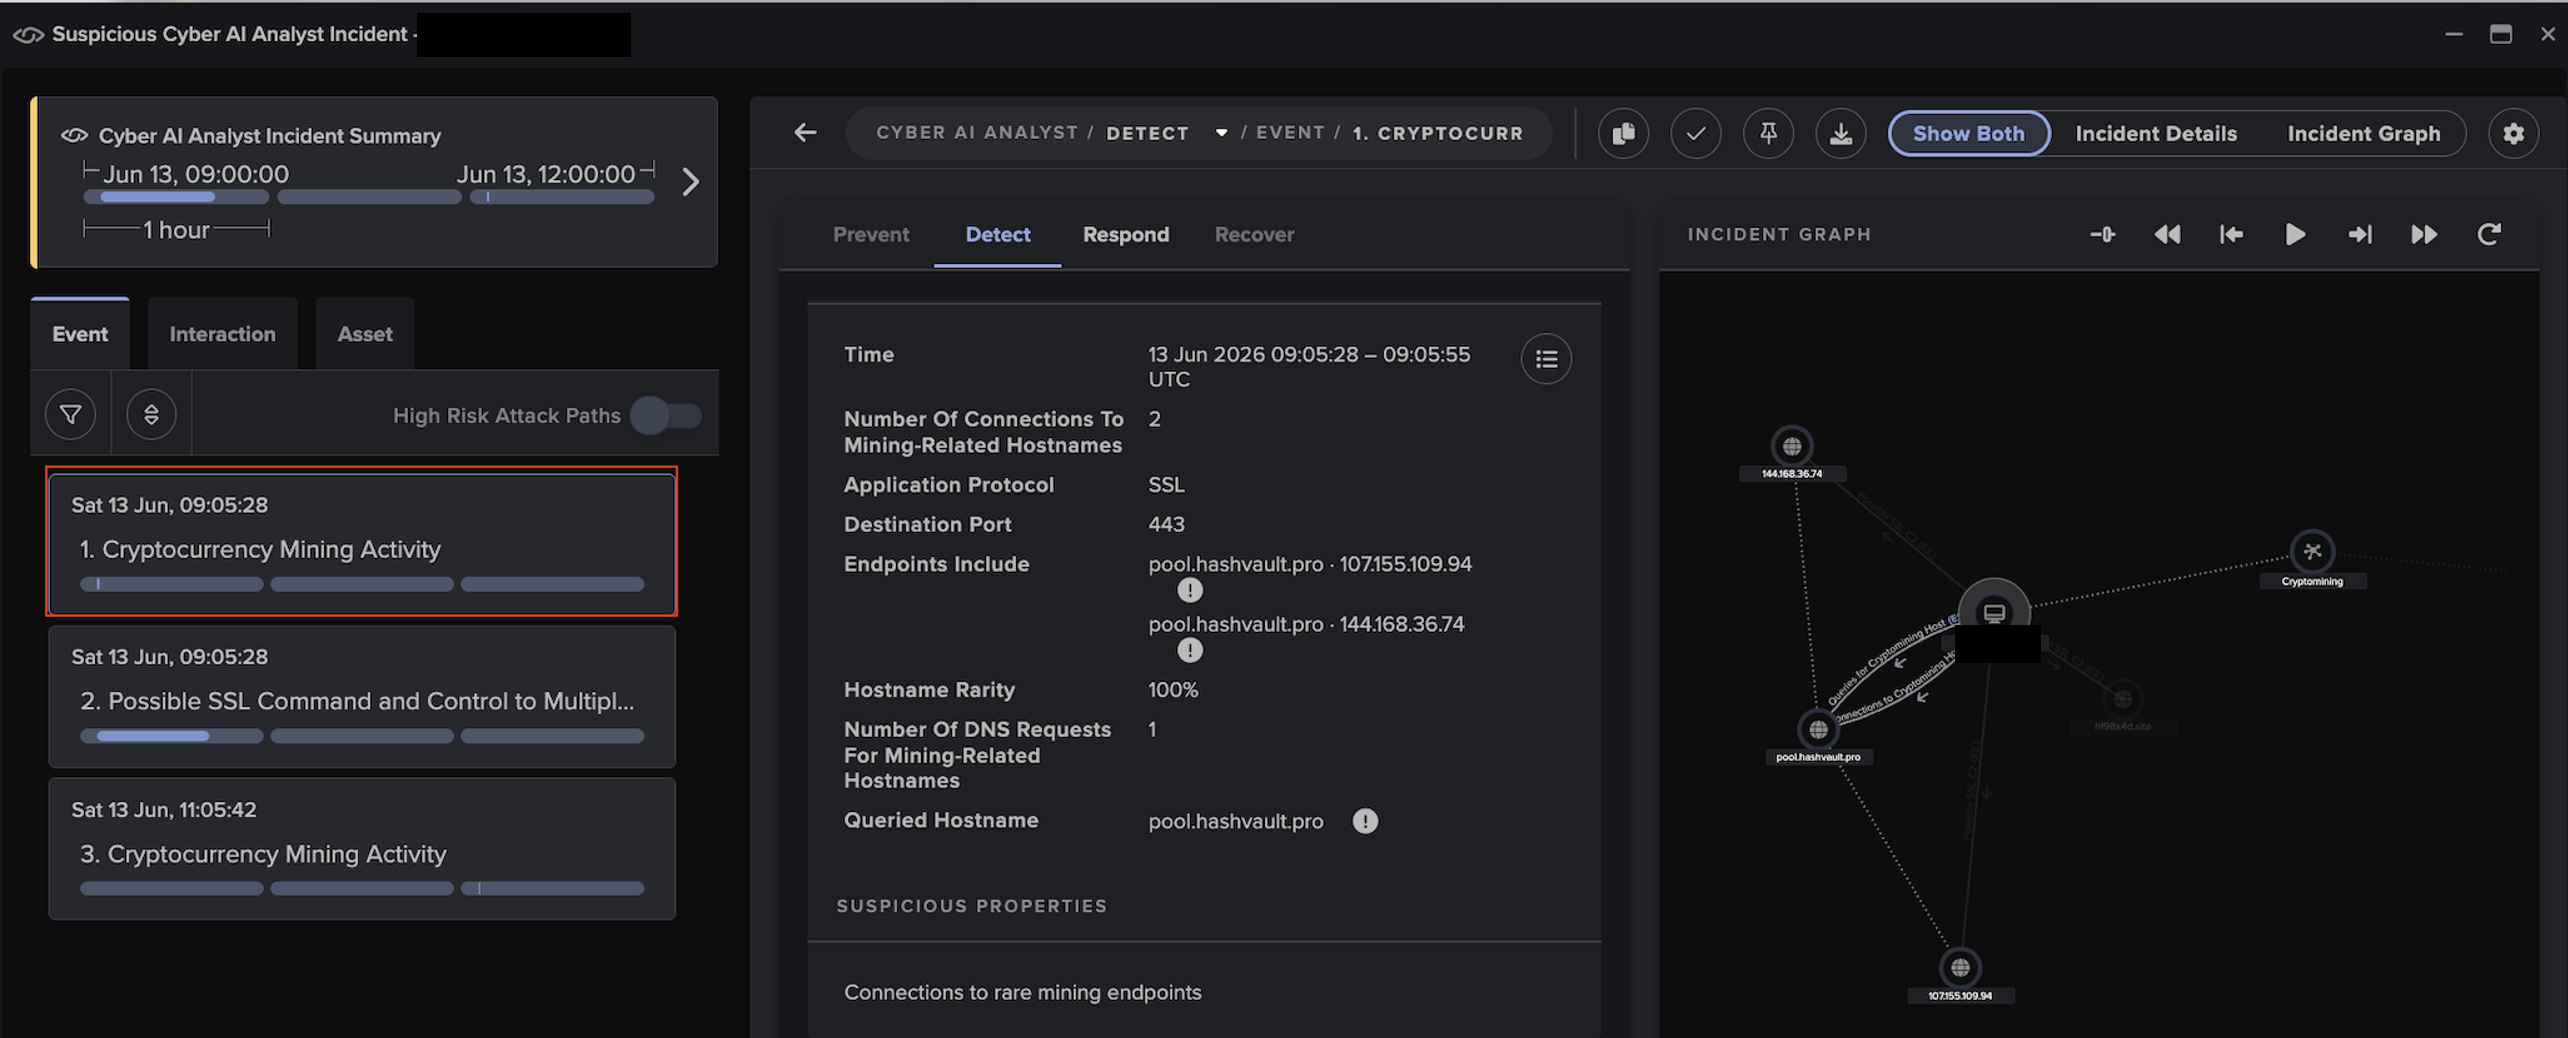
Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

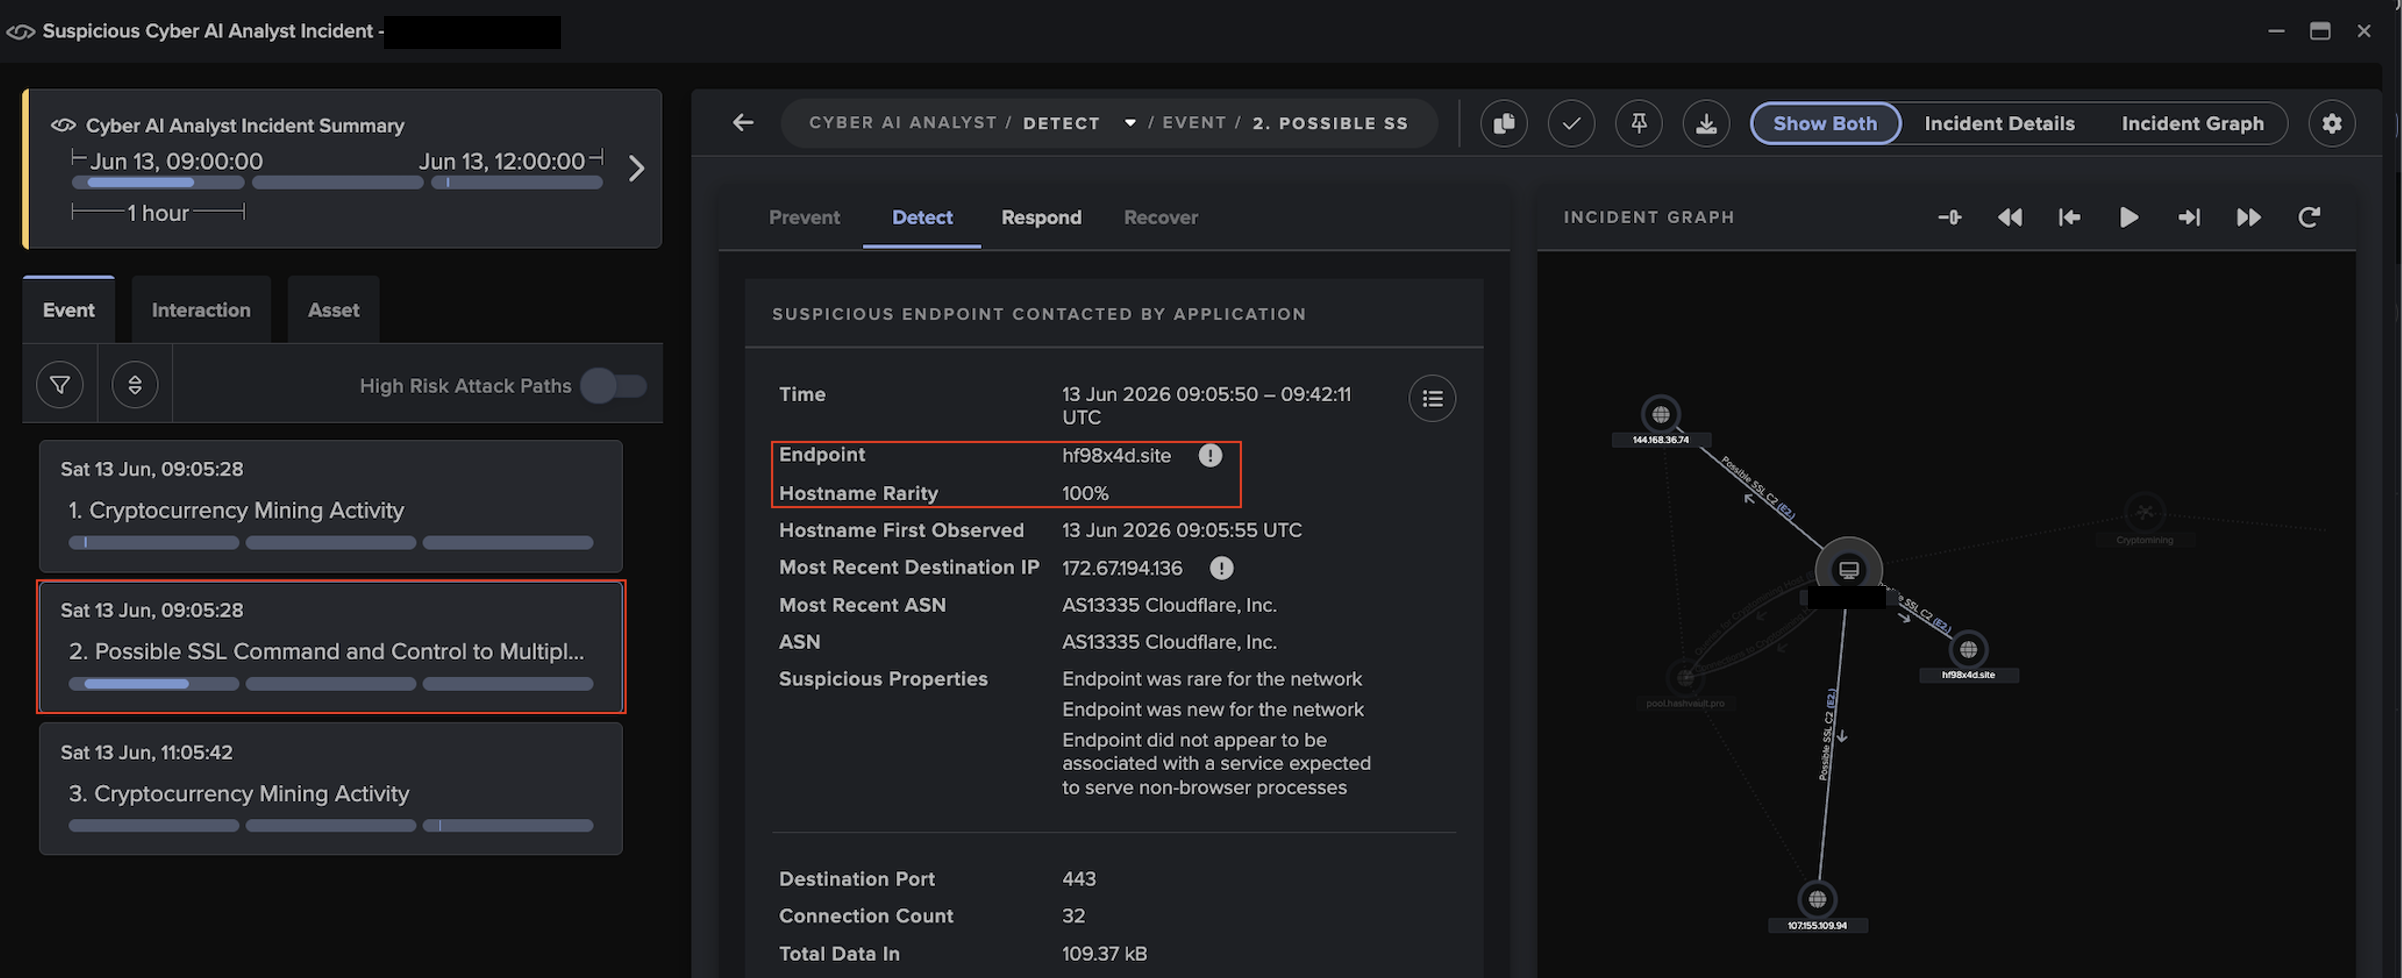
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

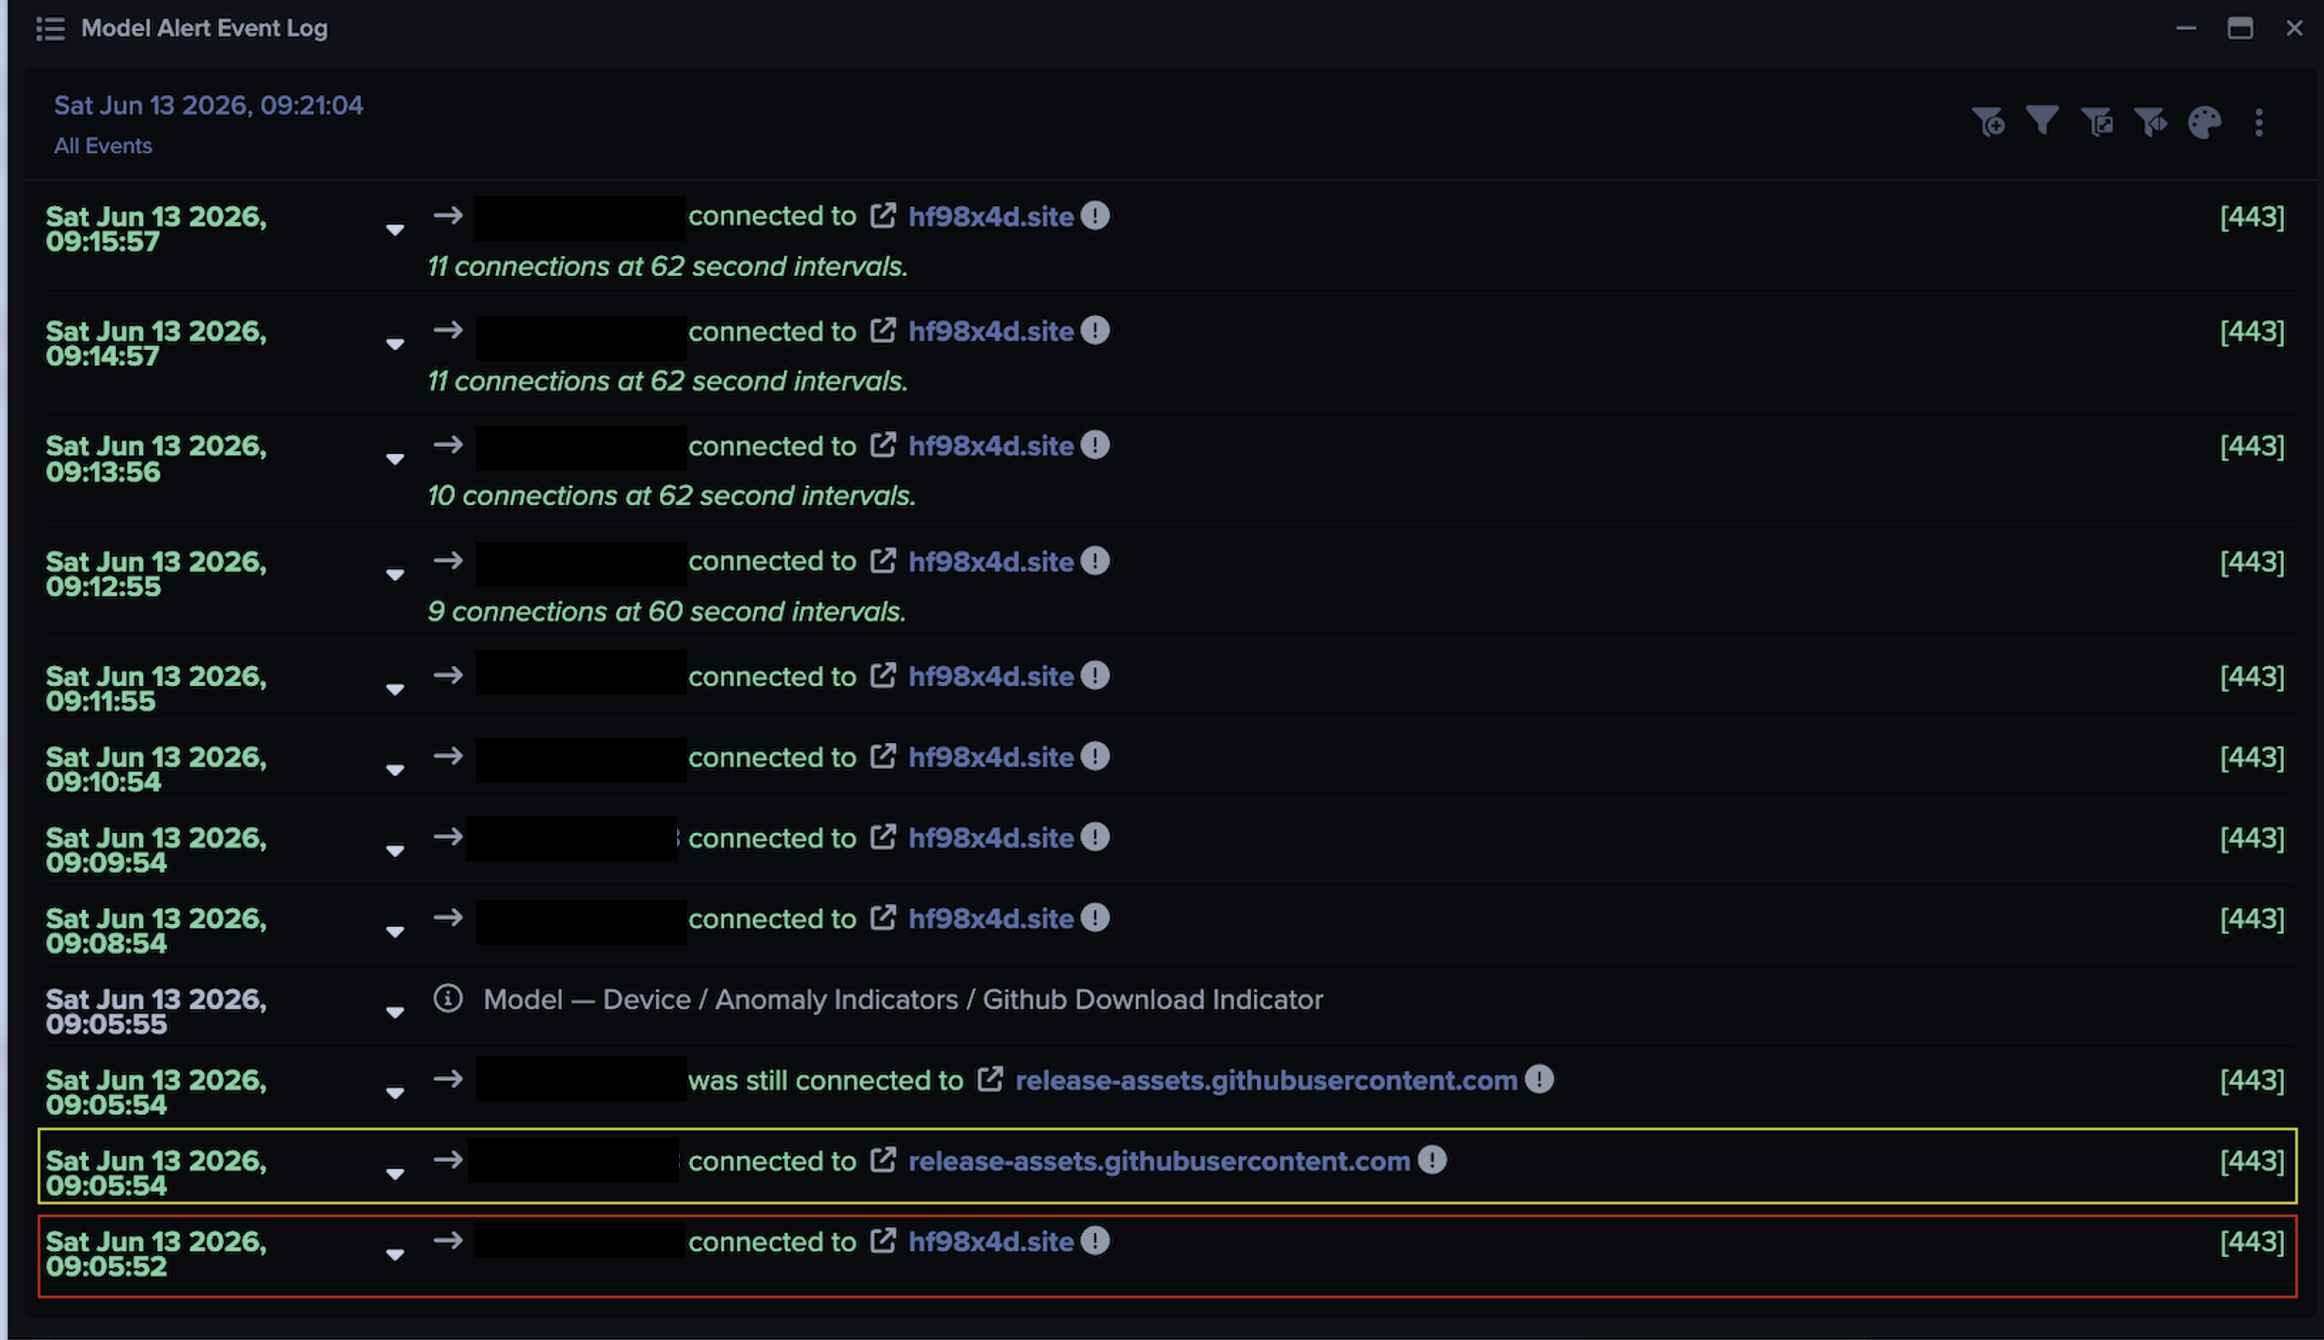
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ