
ブログ
/
Network
/
October 20, 2025

Salt Typhoon侵入事例に対するダークトレースの視点

中国に関係のあるサイバー諜報グループ、Salt TyphoonがDLLサイドローディングやゼロデイエクスプロイト等のステルス手法を使って世界的なインフラを狙っていることが確認されました。ダークトレースは最近Salt Typhoonの戦術と一致する初期の侵入アクティビティを検知しました。これは国家が支援する執拗な脅威に対する防御において従来のシグネチャベースの手法ではなく異常ベースの検知が重要であることを裏付けています。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence
Written by
Sam Lister
Specialist Security Researcher
Default blog image
20
Oct 2025

Salt Typhoonとは?‍

Salt Typhoonは、現在世界のインフラを狙っている最も執拗かつ巧妙なサイバー脅威の1つです。国家が支援する中国のアクターとされるこのAPT(Advanced Persistent Threat)グループは、主に米国の通信プロバイダー、エネルギーネットワーク、政府システムを標的とした、ー連のインパクトの大きいキャンペーンを実行しています。

少なくとも2019年から活動しており、Earth Estries、GhostEmperor、UNC2286としても記録されているこのグループは、エッジデバイスのエクスプロイトに高度な能力を示し、深い永続性を維持しつつ80か国以上において機密性の高いデータの抜き出しを行っています。公になっている被害の報告はほとんど米国の標的に集中していますが、Salt TyphoonのオペレーションはEMEA(ヨーロッパ、中東、アフリカ)地域にも拡大し、通信、政府機関、テクノロジー企業等が標的とされています。カスタムマルウェアの使用、およびインパクトの大きい脆弱性のエクスプロイト(例: Ivanti、Fortinet、Cisco等)は、インテリジェンス収集と地政学的影響を組み合わせたこのグループの戦略的性質を表しています [1]。

ゼロデイエクスプロイト、難読化テクニック、水平移動戦術を駆使することにより、Salt Typhoonは検知を回避し機密性の高い環境に長期間のアクセスを維持することのできる、恐るべき能力を実証しています。このグループのオペレーションにより合法的傍受システムが露出し、数百万のユーザーのメタデータが漏洩、必要不可欠なサービスの中断を招き、世界中で情報機関と民間パートナーの協調した対応が促されました。組織が自社の脅威モデルを評価するなかで、Salt Typhoonは国家が支援するサイバーオペレーションの進化と、積極的な防御戦略が緊急に必要であることをはっきりと思い出させる存在です。

Darktraceのカバレッジ

Darktraceはヨーロッパの通信企業において、DLLサイドローディングと正規のソフトウェアの悪用によるステルス性維持と実行を含む、Salt Typhoonのものとして知られているTTP(戦術、技法、手順)を確認しました。

初期アクセス

侵入は2025年7月、CVE-2025-5777のエクスプロイトから始まりました。これはCitrix NetScaler Gatewayアプライアンスに影響する脆弱性です。脅威アクターはここから、クライアントのMCS(Machine Creation Services)サービス内の Citrix VDA(Virtual Delivery Agent)ホストに移動しました。この侵入の初期のアクセス活動はSoftEther VPNサービスと関連するとみられるエンドポイントから発生しており、最初からインフラ難読化が行われていたことがわかります。

ツール

Darktraceはその後、この脅威アクターが複数のCitrix VDAホストに対し、高い確率でSNAPPYBEE(Deed RATとしても知られる) [2][3] であるとみられるバックドアを設置したことを検知しました。このバックドアはこれらの内部エンドポイントに対して、Norton Antivirus、Bkav Antivirus、IObit Malware Fighterなどのアンチウイルスソフトウェアの正規の実行形式ファイルと共にDLLとして仕掛けられました。このアクティビティのパターンは、攻撃者が正規のアンチウイルスソフトウェアを使ったDLLサイドローディングによりペイロードを実行しようとしたことを示しています。Salt Typhoonおよび類似のグループは過去にもこのテクニックを使用してきており[4][5]、これにより信頼されるソフトウェアの陰でペイロードを実行し従来型のセキュリティコントロールを回避することを可能にしています。

コマンド&コントロール(C2)

この脅威アクターが設置したバックドアはLightNode VPSエンドポイントをC2に使用し、HTTPと不明なTCPベースのプロトコルの両方を使って通信していました。このように二重のチャネルを使っていることは、Salt Typhoonが非標準プロトコルを多層的に使用して検知を回避することで知られていることと一致しています。バックドアに表示されたHTTP通信には、Internet Explorerの User-Agentヘッダーを持つPOSTリクエストや“/17ABE7F017ABE7F0” のようなTarget URIパターンが含まれていました。侵害されたエンドポイントが接続したC2ホストの1つはaar.gandhibludtric[.]com (38.54.63[.]75)であり、最近Salt Typhoonとの関連が確認されたドメインです[6]。

検知のタイムライン

Darktraceは侵入の初期段階に対して高確度の検知結果を生成しました。初期のツール使用とC2アクティビティは、Darktrace Cyber AI AnalystTMによる調査と、Darktraceのモデルの両方によって明確にカバーされていました。脅威アクターが高度であったにもかかわらず、侵入アクティビティはこれらの攻撃の初期段階から先へ進展する前に識別され、修正されました。Darktraceのタイムリーかつ高確度の検知が脅威の無害化に重要な役割を果たしたものと思われます。

Cyber AI Analystの知見

Darktrace Cyber AI Analyst は侵入の初期段階においてDarktraceが検知したモデルアラートを自律的に調査しました。この調査を通じ、Cyber AI Analystは初期のツール使用とC2イベントを突き止め、これらをつなぎ合わせて攻撃の進行を表す1つのインシデントにまとめました。
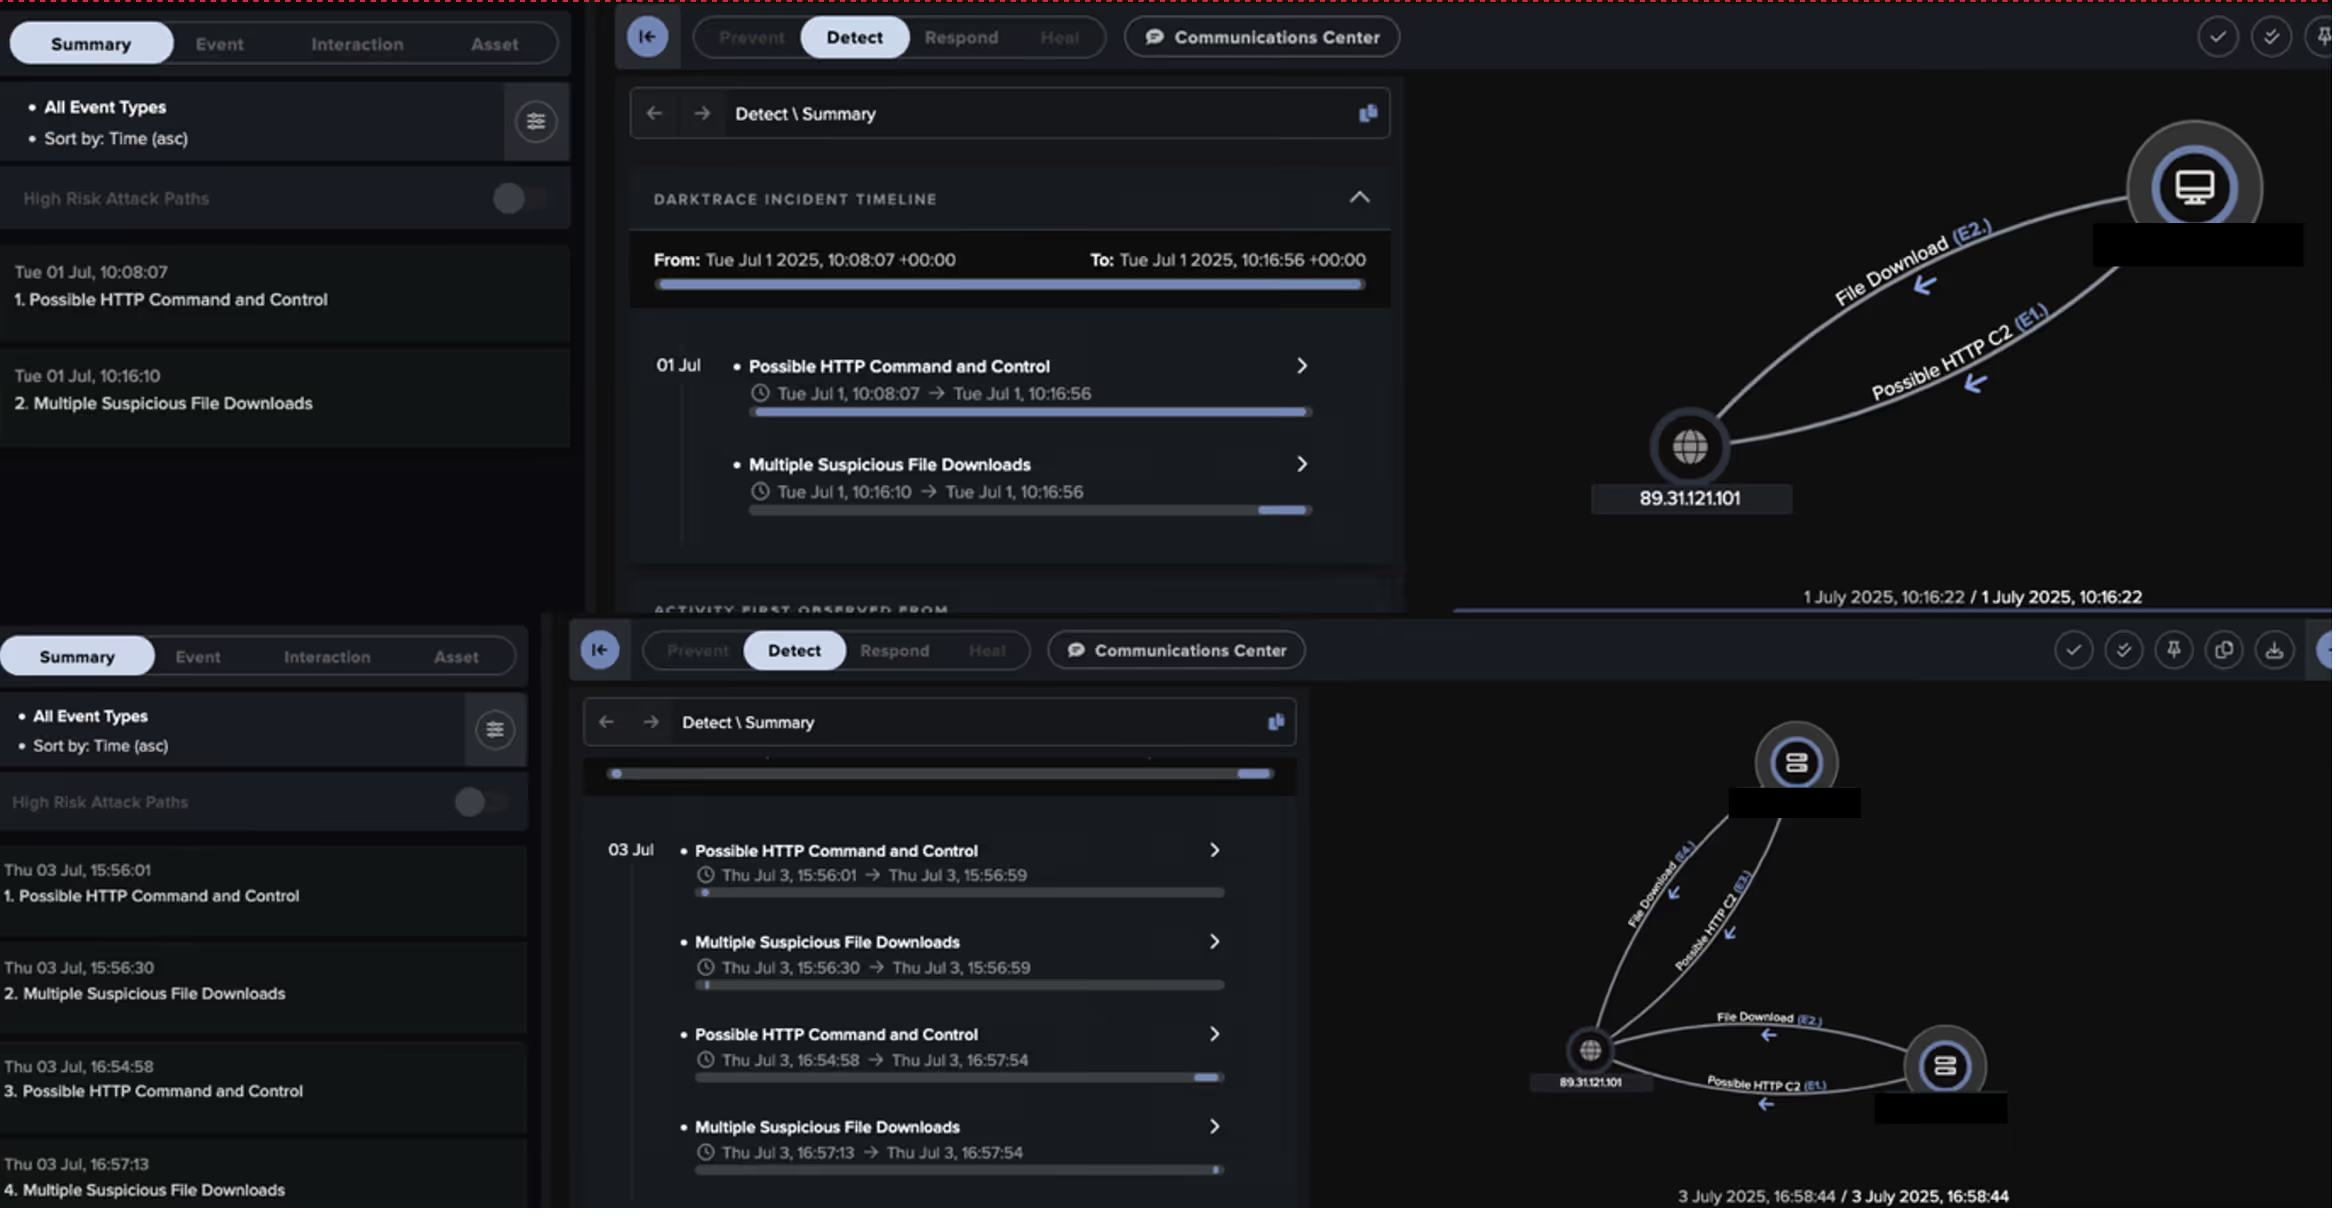
Cyber AI Analyst weaved together separate events from the intrusion into broader incidents summarizing the attacker’s progression.
図1: Cyber AI Analystは侵入アクティビティからの個別のイベントをつなぎ合わせて全体のインシデントを作成し、攻撃の進行状況を示しました。

まとめ

TTPやステージングパターン、インフラ、マルウェアの共通点に基づき、ダークトレースは一定の確信を持って観察されたアクティビティがSalt Typhoon/Earth Estries (ALA GhostEmperor/UNC2286)と一致していると評価しました。Salt Typhoonは引き続きそのステルス性、永続性、正規ツールの悪用によって防御者を悩ませています。攻撃者が通常のオペレーションに紛れ込もうとする傾向が高まるなかで、かすかな逸脱を識別し分散したシグナルを相関付けるには、動作の異常を検知することが不可欠となります。Salt Typhoonの特徴である変化する手法、そして信頼されるソフトウェアやインフラを別の目的に使用する能力により、従来の手法だけでは今後も検知が難しいことが確実です。この侵入インシデントは積極的な防御の重要性を示しており、そこではシグネチャの照合だけにとどまらない異常ベースの検知が、初期段階のアクティビティを明らかにする上で決定的な役割を果たします。

本稿の執筆には Nathaniel Jones (VP, Security & AI Strategy, FCISO)、Sam Lister(Specialist Security Researcher)、Emma Foulger(Global Threat Research Operations Lead)、Adam Potter(Senior Cyber Analystが協力しました。

編集:Ryan Traill(Analyst Content Lead)

付録

侵害インジケータ(IoC)

IoC-タイプ-説明 + 確度

89.31.121[.]101 – IP Address – Possible C2 server

hxxp://89.31.121[.]101:443/WINMM.dll - URI – Likely SNAPPYBEE download

b5367820cd32640a2d5e4c3a3c1ceedbbb715be2 - SHA1 – Likely SNAPPYBEE download

hxxp://89.31.121[.]101:443/NortonLog.txt - URI - Likely DLL side-loading activity

hxxp://89.31.121[.]101:443/123.txt - URI - Possible DLL side-loading activity

hxxp://89.31.121[.]101:443/123.tar - URI - Possible DLL side-loading activity

hxxp://89.31.121[.]101:443/pdc.exe - URI - Possible DLL side-loading activity

hxxp://89.31.121[.]101:443//Dialog.dat - URI - Possible DLL side-loading activity

hxxp://89.31.121[.]101:443/fltLib.dll - URI - Possible DLL side-loading activity

hxxp://89.31.121[.]101:443/DisplayDialog.exe - URI - Possible DLL side-loading activity

hxxp://89.31.121[.]101:443/DgApi.dll - URI - Likely DLL side-loading activity

hxxp://89.31.121[.]101:443/dbindex.dat - URI - Likely DLL side-loading activity

hxxp://89.31.121[.]101:443/1.txt - URI - Possible DLL side-loading activity

hxxp://89.31.121[.]101:443/imfsbDll.dll – Likely DLL side-loading activity

hxxp://89.31.121[.]101:443/imfsbSvc.exe - URI – Likely DLL side-loading activity

aar.gandhibludtric[.]com – Hostname – Likely C2 server

38.54.63[.]75 – IP – Likely C2 server

156.244.28[.]153 – IP – Possible C2 server

hxxp://156.244.28[.]153/17ABE7F017ABE7F0 - URI – Possible C2 activity

MITRE TTP

テクニック | 説明

T1190 | Exploit Public-Facing Application - Citrix NetScaler Gateway compromise

T1105 | Ingress Tool Transfer – Delivery of backdoor to internal hosts

T1665 | Hide Infrastructure – Use of SoftEther VPN for C2

T1574.001 | Hijack Execution Flow: DLL – Execution of backdoor through DLL side-loading

T1095 | Non-Application Layer Protocol – Unidentified application-layer protocol for C2 traffic

T1071.001| Web Protocols – HTTP-based C2 traffic

T1571| Non-Standard Port – Port 443 for unencrypted HTTP traffic

侵入時のDarktraceモデルアラート

Anomalous File::Internal::Script from Rare Internal Location

Anomalous File::EXE from Rare External Location

Anomalous File::Multiple EXE from Rare External Locations

Anomalous Connection::Possible Callback URL

Antigena::Network::External Threat::Antigena Suspicious File Block

Antigena::Network::Significant Anomaly::Antigena Significant Server Anomaly Block

Antigena::Network::Significant Anomaly::Antigena Controlled and Model Alert

Antigena::Network::Significant Anomaly::Antigena Alerts Over Time Block

Antigena::Network::External Threat::Antigena File then New Outbound Block  

参考文献

[1] https://www.cisa.gov/news-events/cybersecurity-advisories/aa25-239a

[2] https://www.trendmicro.com/en_gb/research/24/k/earth-estries.html

[3] https://www.trendmicro.com/content/dam/trendmicro/global/en/research/24/k/earth-estries/IOC_list-EarthEstries.txt

[4] https://www.trendmicro.com/en_gb/research/24/k/breaking-down-earth-estries-persistent-ttps-in-prolonged-cyber-o.html

[5] https://lab52.io/blog/deedrat-backdoor-enhanced-by-chinese-apts-with-advanced-capabilities/

[6] https://www.silentpush.com/blog/salt-typhoon-2025/

このブログで提供されるコンテンツはダークトレースが一般的な情報提供の目的でのみ公開するものであり、サイバーセキュリティに関するトピック、傾向、インシデント、出来事についての、公開の時点における当社の理解を反映したものです。当社は内容の正確性と重要性の担保に努めていますが、情報は明示的暗黙的を問わず、何らの表明あるいは保証も伴わわない「そのまま」の状態で提供されるものです。ダークトレースは本書に含まれる情報の完全性、正確性、信頼性、適時性について何らの責任も負わず、すべての保証を明示的に否認します。

本ブログに含まれるいかなる内容も法的、技術的、技術的助言を構成するものではなく、読者は本書に含まれる情報に基づいて行動する前に資格を持った専門家に相談されることをお勧めします。第三者の組織、技術、脅威アクター、インシデントに対する言及は情報目的のみであり、提携、承認、推奨を暗に意味するものではありません。

ダークトレース、その関連会社、従業員、あるいは代理人は、本ブログの情報の使用またはこれに対する信頼により生じた、いかなる損失、損害、危害についても責任を負いません。

サイバーセキュリティを取り巻く環境は急激に変化しており、ブログの内容は古くなるあるいは新しいものに代替される可能性があります。当社は任意のコンテンツを更新、変更、あるいは削除する権利を留保します。

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nathaniel Jones
SVP, Global Threat Intelligence
Written by
Sam Lister
Specialist Security Researcher

More in this series

No items found.

Blog

/

Network

/

November 17, 2026

GTA VI Cyber Threats: Fake downloads, ransomware and account hijacking

Default blog imageDefault blog image

Key findings

  • Darktrace detected GTA VI-themed suspicious activity across organizations in multiple sectors ahead of the game’s release, showing how malicious gaming content can reach corporate environments outside the gaming industry.
  • Twelve Darktrace customer environments connected to gta6demo[.]asia, a domain that public threat research has associated with a fake GTA VI demo used to distribute the Vidar infostealer. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.
  • Darktrace investigated ransomware activity at two European games companies. One incident involved DireWolf ransomware alongside reported data exfiltration. A separate Qilin incident included Active Directory reconnaissance, new administrative credentials, possible lateral movement and substantial cloud-storage transfers before ransomware deployment.
  • Another incident on a gaming organization involved a SaaS account hijack in which a compromised account authenticated from unusual IP addresses, created a new privileged account and subsequently sent a high volume of suspected malicious email. An administrative account later authenticated from rare endpoints.‍
  • Darktrace's new report highlights how threat actors continue to weaponize launch hype to breach corporate networks and target gaming infrastructure following the guilty plea of hacker Arion Kurtaj. These findings demonstrate that global enterprises remain actively exposed to franchise-related social engineering and exploitation attempts.

‍

GTA VI gives criminals an audience

Grand Theft Auto VI arrives on November 19 with the kind of attention few entertainment releases command [1]. Before launch, that interest is already being exploited by sites offering supposed demos and downloads.

During September and October 2026, Darktrace detected devices across multiple customer environments connecting to GTA VI-themed sites associated with suspicious activity. The organizations involved were spread across EMEA and the Americas and included Manufacturing, Finance, and Public administration and defense sectors.

Darktrace has also investigated multiple incidents affecting gaming organizations including ransomware and a SaaS account hijack. Those investigations show a separate side of the threat: attackers operating inside corporate infrastructure and accounts, sometimes well before the eventual impact becomes apparent.

Following a fake GTA VI download

On October 7, 2026, Darktrace detected a device making suspicious DNS requests for gta6-play[.]ru, an unofficial Russian-language GTA VI site that had also been flagged as likely malicious in open-source intelligence (OSINT).

‍

Figure 1: A screenshot of the suspicious endpoint gta6-play[.]ru .

‍

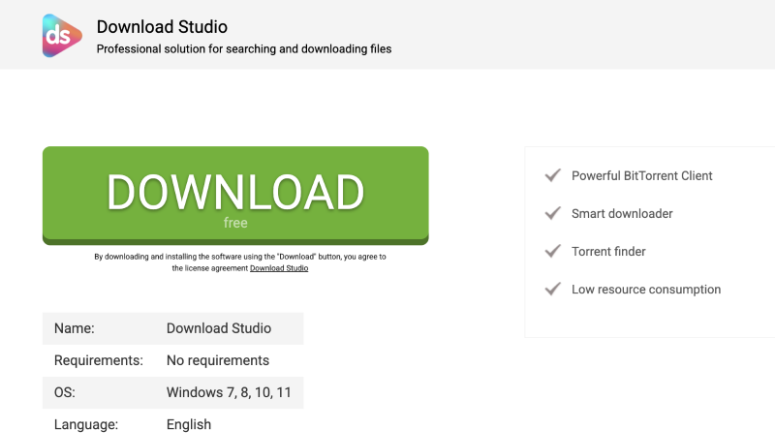
Figure 2: A screenshot of a “Download Studio” endpoint led to on gta6-play[.]ru.

‍

The site advertised a GTA VI download. The site led to a separate “Download Studio” page offering a Windows executable. Analysis found the file was packaged using InstallMate, a commercial installation framework, with an embedded .tsuarch section containing a compressed tiz3 archive.


Further examination identified functionality designed to inspect the environment in which the installer was running. This included checking registry entries for installed software and disk devices, enumerating network adapters, inspecting MAC addresses, and searching for running processes and window titles.


The installer also searched for processes associated with virtualization, debugging, and network analysis, including VMware and VirtualBox components, alongside debugging and monitoring utilities such as OllyDbg, WinDbg, Process Hacker, Process Monitor, Wireshark and Fiddler.

The presence of those checks did not prove that the executable was malicious. The installer contained functionality capable of extracting embedded files, but the investigation did not establish that it was being used to deploy a malicious payload. No definitive malicious payload or command-and-control infrastructure was identified. The software appeared to be InstallRex, which is classified by several security vendors as a potentially unwanted program.

That is still a useful finding; A user looking for GTA VI content could move from an unofficial gaming site to an executable that inspected the local environment, including checking for software commonly used by security researchers.

A second GTA VI lure appeared across twelve organizations

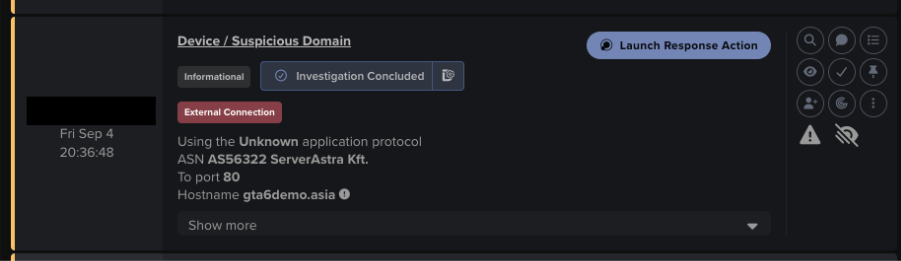
During September 2026, Darktrace alerted on HTTP connections to gta6demo[.]asia across twelve customer environments. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.

‍

Figure 3: An example model alert generated due to a suspicious connection to gta6demo[.]asia.

‍

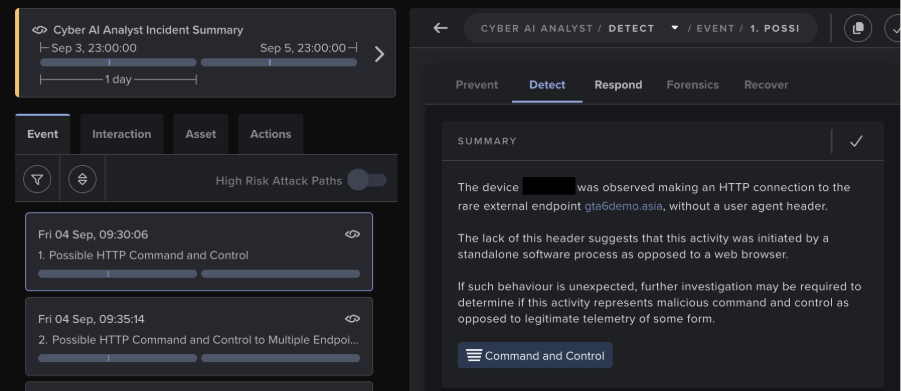
In a case affecting a UK-based customer, Darktrace’s Real-Time AI Analyst further investigated connections to gta6demo[.]asia and generated an incident due to the highly suspicious nature of the behavior.

‍

Figure 4: A Real-Time AI Analyst incident highlighting the suspicious activity for further investigation

‍

Public threat research has associated gta6demo[.]asia with a campaign advertising a fake GTA VI demo. Users clicking "Play Now" were reportedly directed towards an executable containing the Vidar infostealer [2].

There is a practical difference between this activity and an attack against a games company. The users encountering GTA VI-themed infrastructure can work anywhere. Darktrace saw the activity across several sectors outside Gaming, including Finance, Manufacturing, and Public administration and defense.

A major game release can therefore create security exposure well beyond its publisher. A search for a demo or unofficial download on a corporate device is enough to bring gaming-themed infrastructure into an enterprise environment.

Ransomware operators inside the gaming industry

The attacks Darktrace observed against Gaming companies themselves show different patterns.

In August 2026, Darktrace threat research identified possible malicious activity at a European game developer. Ransomware was ultimately deployed and data was exfiltrated, with the DireWolf ransomware group claiming responsibility.

Darktrace observed suspicious file downloads and beaconing from several devices to rare endpoints alongside Monero cryptocurrency mining, Active Directory and network reconnaissance, unusual administrative RDP connections, activity associated with data staging and HTTP-based exfiltration.

Much of the intrusion was therefore visible before ransomware appeared; the environment was already showing evidence of ingress tooling, external command-and-control communications (C2), reconnaissance, unusual administrative access and data movement.

A separate investigation in December 2025 provides a closer view of this pre-ransomware activity. A European games company was targeted by Qilin ransomware with Darktrace observing scanning and LDAP searches involving userAccountControl, which can expose information useful for identifying accounts and Service Principal Names within Active Directory.

New administrative credentials then appeared on a Domain Controller and the Domain Controller also generated scanning, anomalous RPC, SMB, and SSH activity, and NetShareEnum activity through srvsvc. Elsewhere in the environment, long Remote Desktop sessions and SMB enumeration appeared consistent with lateral movement.

Several devices also transferred data to cloud storage services including WebDrive and Amazon Web Services (AWS). In some cases, large downloads preceded subsequent uploads. Darktrace observed the transfer pattern, although the available telemetry does not establish that every transfer represented attacker-controlled exfiltration.

The activity preceding the Qilin deployment included Active Directory reconnaissance, privileged credential use, network and share enumeration, unusual remote access and significant data movement. Each appeared before ransomware became the defining feature of the incident.

SaaS hijacking shifts the attacker evidence

A separate investigation in May 2026 involved the hijacking of a SaaS account at a Gaming organization.

The compromised account authenticated from several IP addresses that were unusual for the organization. It then performed suspicious SaaS group administration, including creating a new privileged account. The account subsequently sent a high volume of emails assessed as likely malicious spam and potentially intended to compromise additional users.

The following day, an administrative SaaS account authenticated from rare endpoints, raising the possibility that further privileged access had been obtained.

The activity presented a different detection problem from the ransomware cases. Authentication from rare infrastructure, administrative changes, creation of a privileged account and subsequent email activity provided the strongest indications that a legitimate identity had been compromised.

For a Gaming company using hosted platforms for development, communication and business operations, a compromised account with the right permissions can provide considerable access without requiring the attacker to reproduce a conventional network intrusion.

Detecting the intrusion before impact

The ransomware investigations show why encryption should not be the first point at which an incident comes into focus. Darktrace observed LDAP and Active Directory-related reconnaissance, new privileged credentials, unusual Domain Controller activity, remote sessions, network enumeration and abnormal data movement before ransomware deployment.

The SaaS case produced different evidence: authentication from rare infrastructure, unexpected administrative changes and activity performed through a compromised account. GTA VI-themed activity required another approach again, following users through unofficial sites and redirects and examining the software offered for download.

GTA VI has put gaming back into the headlines ahead of its November release. The security activity around it is already visible beyond the games industry, while ransomware and account-compromise investigations show attackers operating inside gaming companies through very different routes.

For defenders, those routes leave evidence before the incident reaches its most damaging stage. The practical work is in recognizing those changes early enough to investigate them.

Credit to Gemma Stubberfield (Cyber Analyst), Ahmed Gardezi (Senior Cyber Analyst), Tara Gould (Malware Research Lead), Nathaniel Jones (SVP, Global Threat Intelligence)

References:

1.        https://www.rockstargames.com/VI

2.     https://www.malwarebytes.com/blog/threat-intel/2026/08/fake-gta-6-extended-look-and-demo-sites-deliver-an-infostealer

‍

‍

Continue reading
About the author
Gemma Stubberfield
Cyber Analyst

Blog

/

AI

/

November 17, 2026

How Microsoft and Darktrace Secure the AI-Powered Enterprise

Default blog imageDefault blog image

When legitimate activity creates business risk

AI is making information more accessible and enabling autonomous agents to act across enterprise systems. But legitimate access can still result in sensitive-data exposure, unintended actions, or activity that deviates from business expectations.

Microsoft's evolving security strategy recognizes this shift, emphasizing continuous risk assessment, stronger identity protection, and security that adapts as AI systems operate. For enterprises, the challenge is increasingly about recognizing when trusted activity introduces risk, even when existing controls are functioning as intended.

Where global intelligence meets deep business context

Microsoft brings global threat intelligence and comprehensive security capabilities, helping organizations protect identities, data, applications, and infrastructure. Its integrated approach connects security signals, governance, detection, and response across increasingly complex environments.

Darktrace complements these strengths with deep, organization-specific behavioral understanding. Powered by Adaptive AI, Darktrace continuously learns the patterns and relationships unique to each business, developing a Unique Behavioral Profile for each organization that helps distinguish meaningful threats from legitimate activity. By connecting identity, activity, context, and intent, it adds another dimension to security intelligence.

Together, Microsoft and Darktrace combine global intelligence with deeper knowledge of how each customer operates. Through supported integrations, this behavioral context enriches existing Microsoft security workflows, enabling more informed investigations and precise response.

This complementary approach extends across three interconnected areas of enterprise security- AI, People and Infrastructure. From understanding how AI and agents operate to protecting trusted communications and the infrastructure businesses depend on, Darktrace strengthens Microsoft's security capabilities with behavioral insight specific to each organization.

Understanding AI beyond permissions and policies

As AI moves into business-critical operations, security teams need to understand more than which applications and agents are approved. They need visibility into how AI is used, what information it accesses, and whether its actions remain aligned with business intent.

Microsoft provides extensive AI development, governance, and security capabilities. Darktrace / SECURE AI complements these with behavioral analysis across Shadow AI, prompts, agent identities and actions, and development risk. Policy Manager helps evaluate activity against organizational AI policies, while the announced integration with Microsoft Agent 365 is designed to enrich agent risk assessments with organization-specific behavioral signals. Together, these capabilities help organizations scale AI adoption with greater confidence.

Recognizing risk within trusted relationships

Sophisticated threats increasingly exploit established business relationships, familiar communications, and legitimate accounts. A message from a trusted supplier or an action taken through an authorized identity may appear routine until considered against the organization's normal behavior.

Darktrace / EMAIL complements Microsoft's native email, identity, and data protection capabilities by understanding how people and organizations communicate. This enables more precise detection of targeted phishing, business email compromise, account takeover, and data loss, supported by proportionate response. Integrations such as Unified Quarantine within Microsoft Defender for Office 365 bring this additional protection into existing security workflows.

Seeing the bigger picture behind an attack across domains

Threats rarely unfold within a single security domain. Suspicious identity activity, unexpected cloud connections, and unusual network behavior may appear unrelated until the relationships between them reveal a developing attack.

Darktrace / HYBRID NETWORK complements Microsoft's security capabilities with organization-specific behavioral detection across network, cloud, identity, and operational technology. Real-Time AI Analyst, including Cyber AI Analyst, connects related activity into investigated incidents that can be delivered into Microsoft Sentinel, helping security teams accelerate investigations and support targeted containment across the hybrid enterprise.

Turning security intelligence into business confidence

As AI becomes more deeply integrated into business operations, organizations need security that understands not only what technology can access, but how it behaves within their unique environment.

Microsoft and Darktrace bring complementary strengths to that challenge. By connecting global threat intelligence and integrated security capabilities with deep behavioral understanding, the partnership helps organizations recognize emerging risks, respond with greater precision, and strengthen their existing security investments.

The opportunity is to turn security intelligence into meaningful business context, enabling organizations to innovate and operate AI with confidence.

Darktrace named a 2026 Microsoft Partner of the Year Finalist for ISV Innovation

Darktrace has been named a finalist for the 2026 Microsoft Partner of the Year Award in the ISV Innovation category.  

This recognition reflects our collaboration with Microsoft to bring business context to enterprise security. By connecting Microsoft's global threat intelligence and integrated security capabilities with Darktrace's deep behavioral understanding, we help organizations recognize emerging risks and respond with greater precision across AI, People and Infrastructure.

Thank you to Microsoft, our customers, and our teams for their continued collaboration.

Meet Darktrace at Microsoft Ignite and the Microsoft Frontier Tour

Explore how Darktrace and Microsoft are bringing behavioral security to AI, people, and infrastructure.

Join Darktrace at Microsoft Ignite in San Francisco, November 17–19, or connect with our experts as we join the Microsoft Frontier Tour across 21 cities worldwide.

Meet Darktrace at Microsoft Ignite

Connect with Darktrace at the Microsoft Frontier Tour

[related-resource]

Continue reading
About the author
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ