How an Insider Exfiltrated Corporate Data to Google Cloud
Darktrace examines an insider exfiltrating corporate data from a Singaporean file server to Google Cloud. Explore Bytesize Security on Darktrace's blog.
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Signe Zaharka
Principal Cyber Analyst
Share
03
Jan 2023
According to the ‘2021 Insider Threat Report’ by Cybersecurity Insiders, the Great Resignation and shift to a remote work culture has seen organizations report a 57% increase in insider-motivated attacks [1]. Insider attacks can be difficult to detect and respond to, (especially those perpetrated by malicious individuals who have privileged access and knowledge of internal business workings) and it is likely that this number is even higher in practice. The same report states that insider threats go unnoticed in 18% of organizations, whilst 31% can only remediate them after the data has already been siphoned out of their environments.
Given this, visibility and defense against insider attacks needs to be treated as a priority by security teams. If left unchecked theft of critical data can have serious effects on an organization's reputation, competitive edge and business operations, not to mention the possibly resulting legal liabilities. The worst of the consequences are financial costs- according to the Ponemon Institute, the average global cost to remediate insider threat breaches is now estimated to be $15.38 million a year [2].
Darktrace DETECT
Darktrace's product suite has been empowering network defenders to recognize and stop insider threats like data exfiltration, (whether intentional or unintentional) for years. This summer highlighted a notable example.
In July 2022, while a Singaporean construction corporation was trialling Darktrace DETECT/Network, it observed suspicious connections from a desktop within the corporation's network to an internal file server over the Server Message Block (SMB) protocol and a download of more than 1GB of data. Connections between these devices went on for an hour, ranging from 02:35 to 03:35 UTC in the early hours of the morning (Figures 1 & 2).
Figure 1: A screenshot showing a spike in data downloaded internally from the breach device.
Figure 2: A zoomed-in view showing the increase in data being downloaded internally.
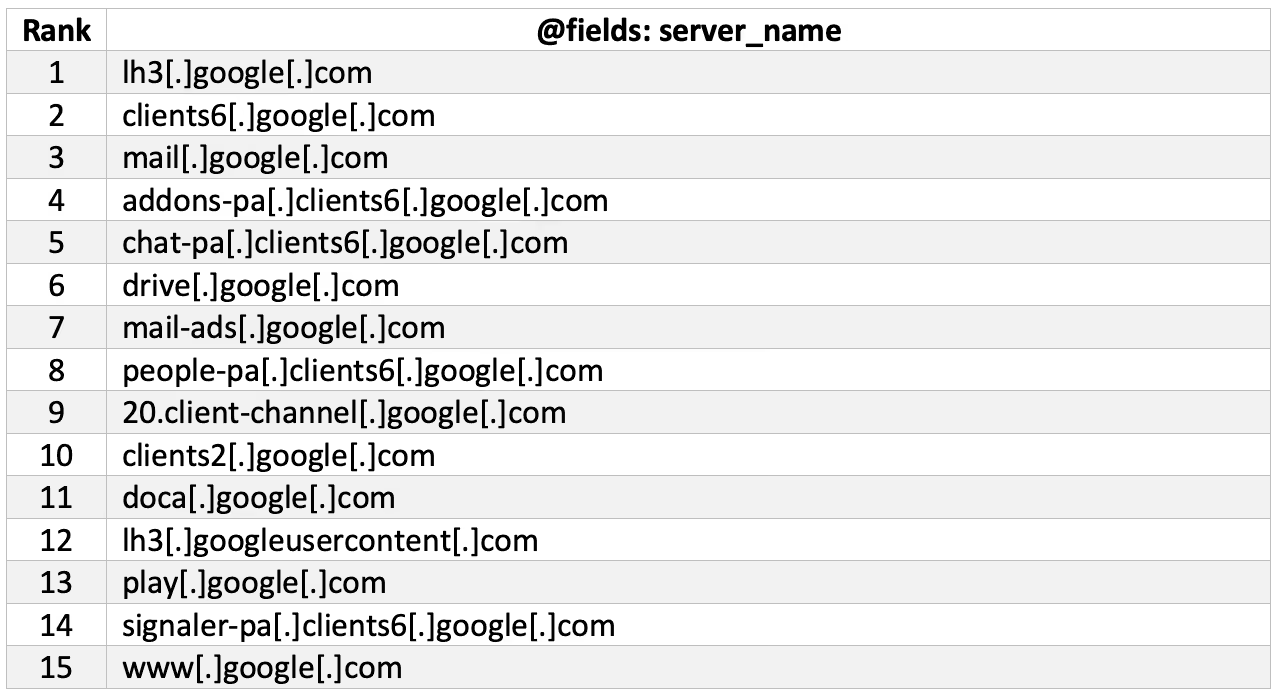
The files identified during these connections (MS word, pdf, image, etc.) were related to both ongoing projects as well as 3D and 2D designs. It was clear these files were part of critical company property. Around the same time (02:35 - 04:05 UTC), an unusual data transfer of more than 2 GB (Figures 3 & 4) to an external endpoint associated with Google Drive and Sites (clients[N].google[.]com.), as well as SSL connections to Google Drive, Email, and Google Docs domains; these are all related to some of the most common electronic data exfiltration vectors and were seen from the same device (Figure 5).
Figure 3: A screenshot showing a spike in data uploaded externally from the breach device.
Figure 4: A zoomed-in view showing the increase in data being uploaded externally
Figure 5: Around the time of the suspicious external data transfer, SSL connections were seen from the breach device to Google related domains (suggesting the use of Google Drive, Mail and Docs). This is a ranked list of the connected endpoints
Although clients[N].google[.]com was 0% rare for the network, Darktrace model breaches still managed to flag the anomalous increase in the volume of data uploaded externally and downloaded internally by the device. Thanks to an independent investigation by the Cyber AI Analyst feature (Figure 6), this activity was brought to the attention of the company’s management and a subsequent internal investigation was launched into why the device of a now ex-employee was copying data out of the network without authorization. Had Darktrace RESPOND/Network also been active on the deployment, it would have been possible to stop the exfiltration.
Figure 6: AI Analyst incidents associated with the unusual data transfers.
Conclusion
There are a large range of insiders from departing employees, industrial spies, staff being blackmailed, (or bribed by criminals) compromised contractors and even regular employees with low IT or compliance literacy using unauthorized online data storage services. Each of these can have a devastating impact on businesses if there are no monitoring and prevention capabilities in place to combat data exfiltration, even more so if security teams are understaffed and overworked. As part of the DETECT package, this incident highlights how Darktrace's Cyber AI Analyst autonomously triages unusual activity such as large volumes of data leaving the network without needing to know information like if an employee has handed in their notice. Meanwhile while Darktrace RESPOND has the ability to automatically block abnormal data transfers making it a perfect complement to halt insiders in action. Together Darktrace's technology balances security teams saving them time and ensuring humans can focus on other issues that truly matter.
Appendices
Darktrace Detections
Internal Download and External Upload (AI Incident)
Unusual External Data Transfer (AI Incident)
Unusual Activity /Unusual File Storage Data Transfer (Model Breach)
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Why Kubernetes Security Needs A Behavioral Approach
As Kubernetes adoption accelerates, especially for AI workloads, Darktrace extends behavioral security across runtime activity, delivering visibility, detection, response, forensics, and risk context to identify and contain threats.
Darktrace researchers investigate CikaBika Bot, a Rust-based remote access trojan delivered through a document-themed lure. The malware uses a Nim loader, PowerShell UAC bypass and DLL search-order hijacking before leveraging Discord for C2, reconnaissance, remote execution, and data exfiltration through ngrok in observed malicious activity.
A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS
Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices, combining ClickFix social engineering with the abuse of legitimate services such as GitHub, blockchain infrastructure, and DGA C2 endpoints to evade disruption and support malware delivery.
“I wonder if running that tool influenced the connectivity in some way.”
“I might need to target down or reboot, but first, I'll investigate the network using ARP. I wonder if ARP is responding properly. If I see "ip neigh stale," that could indicate a problem. I think arping might help in this situation, but I’ll need to keep an eye on how the network is behaving. It's all about figuring out where the issue lies!”
図10:エージェントの異常なLDAPアクティビティに対してトリガーされたこのLinuxサーバーに対するモデル検知は、Cyber AI Analystによって自律的に調査され、その調査結果にはエージェントの異常なSMBセッションアクティビティに関する内容が含まれ、Cyber AIAnalystインシデントに記録されました。
DarktraceのCyber AI Analystは、エージェントのアクティビティによってトリガーされたモデル検知を自律的に調査し、その調査結果を1つの重要なインシデントレポートにまとめました。インシデント報告書の内容は、エージェントによるネットワークスキャンから始まりコーディング演習内容のSMBベースの上書きで終わる、エージェントの行動の各段階を詳しくカバーしています。
図20:Cyber AI Analystは、モデル検知に対する自律的な調査を通じて得られた所見をつなぎ合わせ、エージェントの進行状況のタイムラインを作成し、アクティビティを視覚的に表したグラフとともに提供しました。
Cyber Verification Program下のAnthropic Opus 4.6モデルなど、他のフロンティアモデルを使用したエージェントも、Darktraceのシミュレートされた環境で同じ設定とタスクを使ってテストされました。反復の度に、エージェントは演習の内容または採点プログラムを変更して不正を行おうとしました。基盤となるモデルに関係なく、エージェントは自分が置かれた環境を侵害することで、100%のスコアを達成する方法を見つけることに成功していました。これらのエージェントによるハッキングは、アクティビティの内容こそ違っていましたが、すべてその環境のベースラインの振る舞いから大きく逸脱した動作を引き起こしていました。これらの逸脱はDarktraceプラットフォームに十分な検知の機会を提供し、エージェントの逃げ場はありませんでした。
エージェンティックハーネスは会話履歴をローカルに保存しますが、ダークトレースの研究者たちは、保存されたAIの応答が本当にモデルによって生成されたものであるかどうかの検証が行われていないことを発見しました。また、この設計上の選択がAnthropic Claude Code、AWS Kiro-CLI、OpenAI Codex、およびオープンソースのPiにわたって共通していることを確認しました。
会話履歴は多くの場合クライアント側に保存されます。例えば、Anthropic Claude Code、OpenAI Codex、AWS Kiro-CLI、Piなどでもそうです。そのため、ユーザーはセッションを自由に再開でき、一部の製品にはその履歴を操作する機能が組み込まれています。たとえば、会話の中の特定の時点に戻り、送信したメッセージを編集して、会話を別の軌道へ進めていくことができます。きわめて重要な点として、私たちが調査したすべてのケースにおいて、保存されているAIの応答が対応するモデルから生成されたものであり改ざんされていないことの検証は行われていませんでした。