ブログ
/
AI
/
February 3, 2026

Darktrace / SECURE AI の概要: 企業全体にわたる包括的なAIセキュリティ

ダークトレースは企業内のAIを防御する新製品をリリースします。 Darktrace / SECURE AIは組織をサイバー脅威や新たなリスクから保護する新時代を築く製品です。 完全な可視性、インテリジェントな動作の監視、リアルタイムコントロールを組み合わせることにより、企業内へのAIの安全な導入、管理、構築を可能にします。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brittany Woodsmall
Senior Product Marketing Manager, AI
Default blog image
03
Feb 2026

AIの保護が急務である理由

AIはITおよびセキュリティチームの対応が追い付かないスピードで企業内に浸透しつつあります。SaaSツールで使用され、コアプラットフォームに組み込まれ、新しい技術を取り入れたいさまざまなチームによって立ち上げが進んでいます。

しかしこの導入が加速するにつれ、スタートアップ、プラットフォームを問わず既存のセキュリティツールでは監視や制御ができない、予測不可能な挙動が発生し、アタックサーフェスが拡大しています。これらの新しいタイプのリスクは、ビジネスの確実性から規制への対応まで幅広い影響を及ぼし、セキュリティチームと経営層両方の注意が必要な問題です。

AIの保護には今までとは根本的に異なるアプローチが必要です。AIがどのように動作するか、データやユーザーとどのように相互動作し、リスクがリアルタイムにどう発生するかを理解するアプローチでなければなりません。企業全体でAIを保護するにあたり組織がどう考えるべきかの中心はこうした変化にあります。

AI保護の現状は?

ダークトレースが1,500名のサイバーセキュリティプロフェッショナルを対象とした調査の結果をまとめた最新の”AIサイバーセキュリティの現状”レポートでは、AI導入ポリシーを持っていないと答えた組織の割合は前年度の55%から増大し63%となっています。

さらに心配なことに、AIポリシーを作成する計画がない組織の割合も3%から8%と、3倍近く増加しています。明確なポリシーがないということは、多くの企業は目隠しされたまま加速しているようなものです。

ダークトレースの顧客ベースにおいてアクティビティを分析したところ、同様のパターンが発生していることが観察されました。昨年10月だけでも生成AIサービスへの異常なデータアップロードが前月比で39%増加し、アップロードの平均サイズは75MBでした。これらのアップロードのサイズと頻度を考えると、おそらくこれらのデータのかなりの部分は、企業の外へ出すべきものではなかったはずです。

多くのセキュリティチームは依然として、ビジネス内でAIがどのように使われているか、つまりどのように振る舞い、何にアクセスし、そして最も重要なこととして、安全に業務を行っているかについての可視性を持っていません。こうした管理されていない利用が静かに広がり、設定済みのセキュリティコントロールから完全にはずれたAIアクティビティがあちこちで発生しています。その結果、ほとんど可視性のない状態で深刻な露出が起こることになり、正式なポリシーが存在していてもAIの利用がそれ以上に広がっている現実があります。

この問題は組織内部の問題にとどまりません。シャドーAIははサードパーティ製ツールやベンダーのプラットフォーム、パートナーのシステムなどにも存在します。AI機能がはっきりした監視なしに組み込まれているケースです。

その一方で、攻撃者はAIの特性を悪用する方法を習得し始めており、組織がすでに管理に苦労しているリスクをさらに悪化させています。

サイバーセキュリティのリーダーがAIを保護  

ダークトレースは、10年以上にわたり構築してきたビヘイビアAIの専門技術を、今日のAIが存在する、複雑で曖昧な環境で機能するように設計された、組織全体をカバーするプラットフォームで提供します。

他のサイバーセキュリティ技術は、過去の攻撃に基づいて新しい攻撃を予測しようとします。しかし問題は、AIが人間のように動作することです。すべての行動は新しい情報を作り出し、それがAIの動作を変えます。これは予測不可能であり、過去に見られた攻撃の戦術はもはや方程式の小さな部分に過ぎません。その結果多くのベンダーは実証されていない技術を買収し、改修してAIの保護を行おうとしています。

ダークトレースのアプローチは他とは根本的に異なります。ダークトレースの自己学習型AIはそれぞれの組織にとって何が正常な状態かを理解します。ユーザーやシステム、アプリケーション、そしてAIエージェントがどのように動作し、どのようにやりとりし、データがどのように流れるかを学習します。これにより、何かが意味のある変化をしたときに、そのかすかな動きを見つけ出すことができます。AIエージェントが登場するずっと前から、ダークトレースのテクノロジーはネットワーク、クラウド、SaaS、Eメール、OT、アイデンティティ、エンドポイントにわたりニュアンスを解釈し、逸脱を検知し、隠れた関係を明らかにし、あいまいなアクティビティの意味を理解してきました。

AIが新たな動作、非構造的やりとり、目に見えない経路を作り出し、シャドーAIが拡大する状況において、セキュリティ課題はますます深刻化しています。しかしダークトレースのプラットフォームはまさにこうした環境のために設計されています。AIの保護はダークトレースにとって新しい方向性ではありません。すでに世界中で何千もの組織に提供してきたビヘイビアインテリジェンスの自然な進化の延長線上にあります。

企業全体にわたる包括的なAIセキュリティ、Darktrace / SECURE AI 

このような背景から、私たちは Darktrace / SECURE AI を自信を持ってご提供します。Darktrace ActiveAI Security Platformの新製品であり、組織全体のAIを保護するよう設計されています。

これは組織をサイバー脅威や新たなリスクから保護する私たちのミッションの新たな章となる製品です。完全な可視性、インテリジェントな動作の監視、リアルタイムコントロールを組み合わせることにより、企業内へのAIの安全な導入、管理、構築を可能にします。これによりAIの使用、データアクセスおよび動作を、セキュリティベースライン、コンプライアンス、そしてビジネスの目標に整合した状態に維持することができます。

Darktrace / SECURE AIは、AIとのあらゆる相互動作を単一のビューで可視化し、セキュリティチームは人間とAIエージェント両方のアクティビティに対して、その意図を理解し、リスクを評価し、機密性の高いデータを保護し、ポリシーを徹底することができます。これにより組織は、AIが安全かつ責任ある形で、セキュリティおよびコンプライアンスのニーズに沿って動作しているかどうかを確認するための可視性とともに、自信を持ってAIを取り入れることができます。  

AIの保護は複数の分野にわたり多層的な複雑さがあるためDarktrace / SECURE AIは自社が所有するAIとサードパーティから提供されるものを含め、組織全体ビジネスに影響するすべてのAI使用を保護するための、次の4つの基盤となるユースケースに基づいて構築されています:

  • 生成AIエージェントおよびアシスタントを駆動するプロンプトを監視する
  • ビジネスAIエージェントのアイデンティティをリアルタイムに保護
  • 開発時、運用時のAIリスクを評価する
  • シャドーAIを見つけ出し、統制する

生成AIエージェントおよびアシスタントを駆動するプロンプトを監視する

AIシステムにおいて、プロンプトは最も活発で敏感なインタラクションのポイントの1つです。これには、ユーザーが意図を伝える人間とAIのやり取り、そしてエージェントが内部プロンプトを生成して推論や調整を行うAI同士の相互動作が含まれます。プロンプトに使われる言語は実質的に動作を示すものであり、固定された有限の構文ではなく自然言語に依存しているため、アタックサーフェスは無限に広がります。そのため、プロンプト駆動のリスクは、CVEに結びつけられた従来のAPIベースの脆弱性よりもはるかに複雑になります。

攻撃者が弱点を探ろうとしているケース、従業員が意図せずに機密データを露出させてしまうケース、エージェントが複雑なワークフローを実行するために自身のサブタスクを生成するケースなど、どのようなケースにおいても、セキュリティチームはプロンプトの動作がモデルの挙動をどのように形成するか、そしてその挙動が問題となる可能性について理解しなければなりません。このような動作についての理解がなければ、組織はAIシステムのエクスプロイト、ドリフト、エラーの連鎖によるリスクの増大に直面することになります。

Darktrace / SECURE AIは、Microsoft CopilotやChatGPT Enterprise等のエンタープライズAIシステム、Microsoft CopilotやStudio等のローコード環境、SalesforceやMicrosoft 365のようなSaaSプロバイダー、AWS、Bedrock、SageMakerなどのハイコードプラットフォームなど、すべてのプロンプトアクティビティを一元的な可視性のレイヤーに統合します。 

可視化だけでなく、Darktraceはビヘイビア分析により、プロンプトがユーザー、その仲間そして組織全体のコンテキストで通常とは異なるあるいはリスクが高いかどうかを理解することができます。AI攻撃は固定されたAPIに対する従来のエクスプロイトよりも格段に複雑であり会話を利用するものである – EメールやTeams/Slackの会話により近い – ため、ビヘイビアの理解はきわめて重要です。プロンプトを動作のシグナルとして扱うことにより、Darktraceは会話型攻撃、悪意あるチェイニング、わかりにくいプロンプトインジェクションの試みを検知することができます。そしてインテグレーションの設定によっては、安全でないプロンプトをリアルタイムにブロックしたり、有害なモデルアクションを発生と同時に阻止することができます。

ビジネスAIエージェントのアイデンティティをリアルタイムに保護

多くの組織がAI駆動のワークフローを導入していくなかで、ビジネスのさまざまな場所で自律型または半自律型のエージェントが急速に拡大しています。これらのエージェントは既存のアイデンティティ内で動作し、システムにアクセスしてデータを読み取り、書き込み、クラウドプラットフォームや社内インフラ、アプリケーション、API、サードパーティサービスに対してアクションをトリガーする能力を持っています。ユーザーのようにコントロールされているアイデンティティもありますが、前述のような、どこに出現するかわからないものもあります。これらのアイデンティティがどのように構成されているか、またその権限がどのように変化していくかに対しての可視性が限定的なためです。

Darktrace SECURE / AIは、AIエージェントの設計上の動作だけでなく、実際に何を行っているかについてアイデンティティを中心としたリアルタイムの理解を提供します。SaaS、クラウド、ネットワークエンドポイント、OT、Eメールこれらの環境でのエージェントのリアルタイムのアイデンティティを、サードパーティ環境内で動作しているものを含めて自動的に検知します。

各エージェントがどのように設定されているか、どのシステムにアクセスしているか、どのように通信しているかを、MCPの使用や機密性の高いデータが保存されているストレージとのやり取りを含めてマッピングします。

エージェントの振る舞いをすべてのドメインに渡り継続的に観察することにより、Darktrace SECURE / AIは不必要またはリスクのある権限の付与、アクティビティパターンの逸脱、あるいは意図されていない方法でエージェントがアクションのチェイニングを始めたときに、これらを識別することができます。このリアルタイムの監査証跡により、組織はエージェントのアクションが意図したオペレーションのパラメーターと整合しているかどうかを評価し、異常な、またはリスクの高い振る舞いを早期にキャッチすることができます。  

開発時、運用時のAIリスクを評価する

AIの構築時には、新たなアイデンティティが作成され、権限が積み重ねられ、さまざまなコンポーネントがSaaS、クラウドそして社内の環境でつなぎ合わされ、プロンプトやコンフィギュレーションを通じてロジックが形成されていきます。 

これは非常にダイナミックかつ多くの場合断片的なプロセスであり、ここでのほんのわずかな手違い、たとえば作成したアイデンティティの設定ミスなどが、システムがデプロイされた後で大きなセキュリティ問題になる可能性があります。AIリスクを開発時に評価することがきわめて重要なのはこのためです。

Darktrace / SECURE AIは、AIシステムの形成が始まった瞬間からライブになるまでのライフサイクル全体に、明確性とコントロールを提供します。作成されたアイデンティとそれらのハイパースケーラー、ローコードSaaS、社内ラボへのアクセスへの可視性を提供するとともに、AIセキュリティポスチャ管理により設定ミス、過剰な権限付与、異常なビルドイベント等を明らかにします。Darktrace/ SECURE AI はこれらの開発環境の情報をプロンプトの監視に直接結びつけ、AIがどのように構築されているかという情報を、運用開始後の挙動とリンクさせます。その結果、より安全で、より予測可能なAIライフサイクルが実現され、リスクを早期に発見し、一貫してガードレールを適用し、当て推量ではなく自信を持ってイノベーションを前進させることができます。

シャドーAIを見つけ出し、統制する

シャドーAIは今や組織のあらゆる場所に出現しています。これは単に従業員が外部チャットボットに内部データを貼り付けてしまう問題だけではありません。これには、管理されていないエージェントビルダー、隠れたMCPサーバー、不正なモデルのデプロイ、そして誰もAIが使われていると思っていなかったデバイスやサービス上のAIワークフローが含まれます。

Darktrace SECURE / AIは、クラウド、ネットワーク、エンドポイント、OTそしてSaaS環境にわたる相互動作を継続的に分析することにより、この新たなリスクを可視化します。承認されていないAIの使用をそれがどこで出現しようとも検知し、正規のアクティビティや承認されているツールを、誤った使用や高リスクのアクティビティと区別します。システムは隠れたAIコンポーネントや不正なエージェントを識別し、承認されていないデプロイメントや、外部AIシステムへの予期しない接続を明らかにします。そして通常のビジネスから逸脱したリスキーなデータフローを特定します。

対応が必要な挙動については、Darktrace SECURE / AIは安全ではないまたは管理されていない使用を封じ込めるとともに、管理されている方法にユーザーを誘導することでポリシーの徹底を可能にします。これにより、企業にとって最も急速に拡大しているセキュリティギャップの1つを解消し、シャドーAIにより作り出されるアタックサーフェスを大幅に削減することができます。

まとめ

AIの導入にポリシーやフレームワークとともに今必要なのは、AIの隠れた使用、プロンプトリスク、アイデンティティの不正使用、および開発全体に渡り、AIの挙動に基づいて脅威を検知する適切なツールです。

ダークトレースはAIの保護を実現する上で他にはない強みがあります。AIエージェントが登場するずっと以前から、それぞれのビジネスから学習し、組織全体にわたり微妙な動作を理解するAIを、10年以上にわたり構築してきました。他のツールでは見逃されてしまう脅威を捕捉する防御の最終ラインとして10,000社以上の顧客がDarktraceを使用しており、AIの保護は私たちにとって方向転換でも新たな技術の取得でもなく、当初からプラットフォームの基盤であったビヘイビア分析技術と、組織全体のインテリジェンスの自然な延長線上にあります。

組織内のAIを保護する方法についてさらに詳しく知りたいお客様のために、プログラムをご用意しました。ITリーダーおよびセキュリティリーダーが共にこの問題に取り組み、大きな意思決定に備え、ガードレールを検討し、不透明性とプレッシャーのなかでビジネスを導くためのフォーラムをご提供します。

Secure AI Readiness Programへの参加はこちらから: AI脅威の最新ニュース、AIセキュリティを取り巻く新たなアプローチ、この分野におけるダークトレースの開発情報を含めた最新イノベーションに関する考察をお届けします。

AIの保護についてダークトレースのエキスパートへのお問い合わせはこちらから: お客様のビジネスにとって最も問題となるAIリスクについて、ガバナンス、可視性、リスク削減、長期的な準備など、どの部分に集中すべきかを含め、実務的な情報をご提供します。

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brittany Woodsmall
Senior Product Marketing Manager, AI

More in this series

No items found.

Blog

/

AI

/

October 23, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

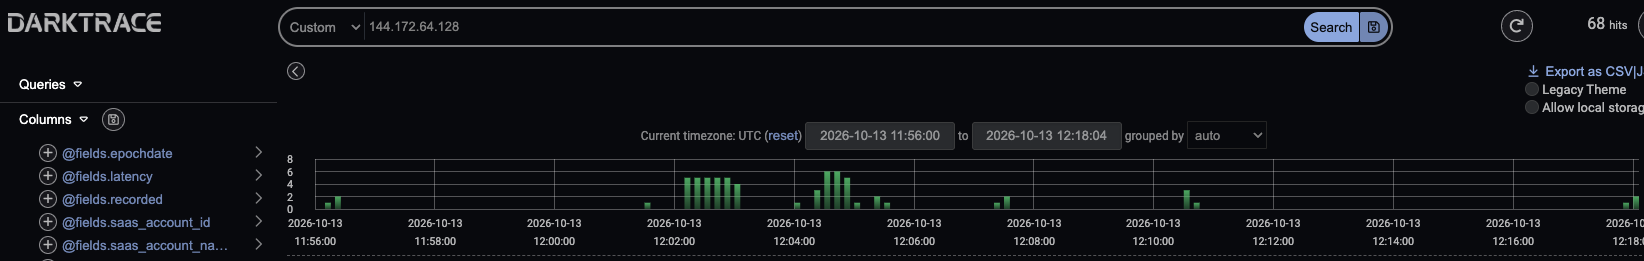
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence

Blog

/

OT

/

October 23, 2026

Beyond the Fridge: Exposed Industrial Control Systems

Default blog imageDefault blog image

Introduction

In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.

The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.

The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].

Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.

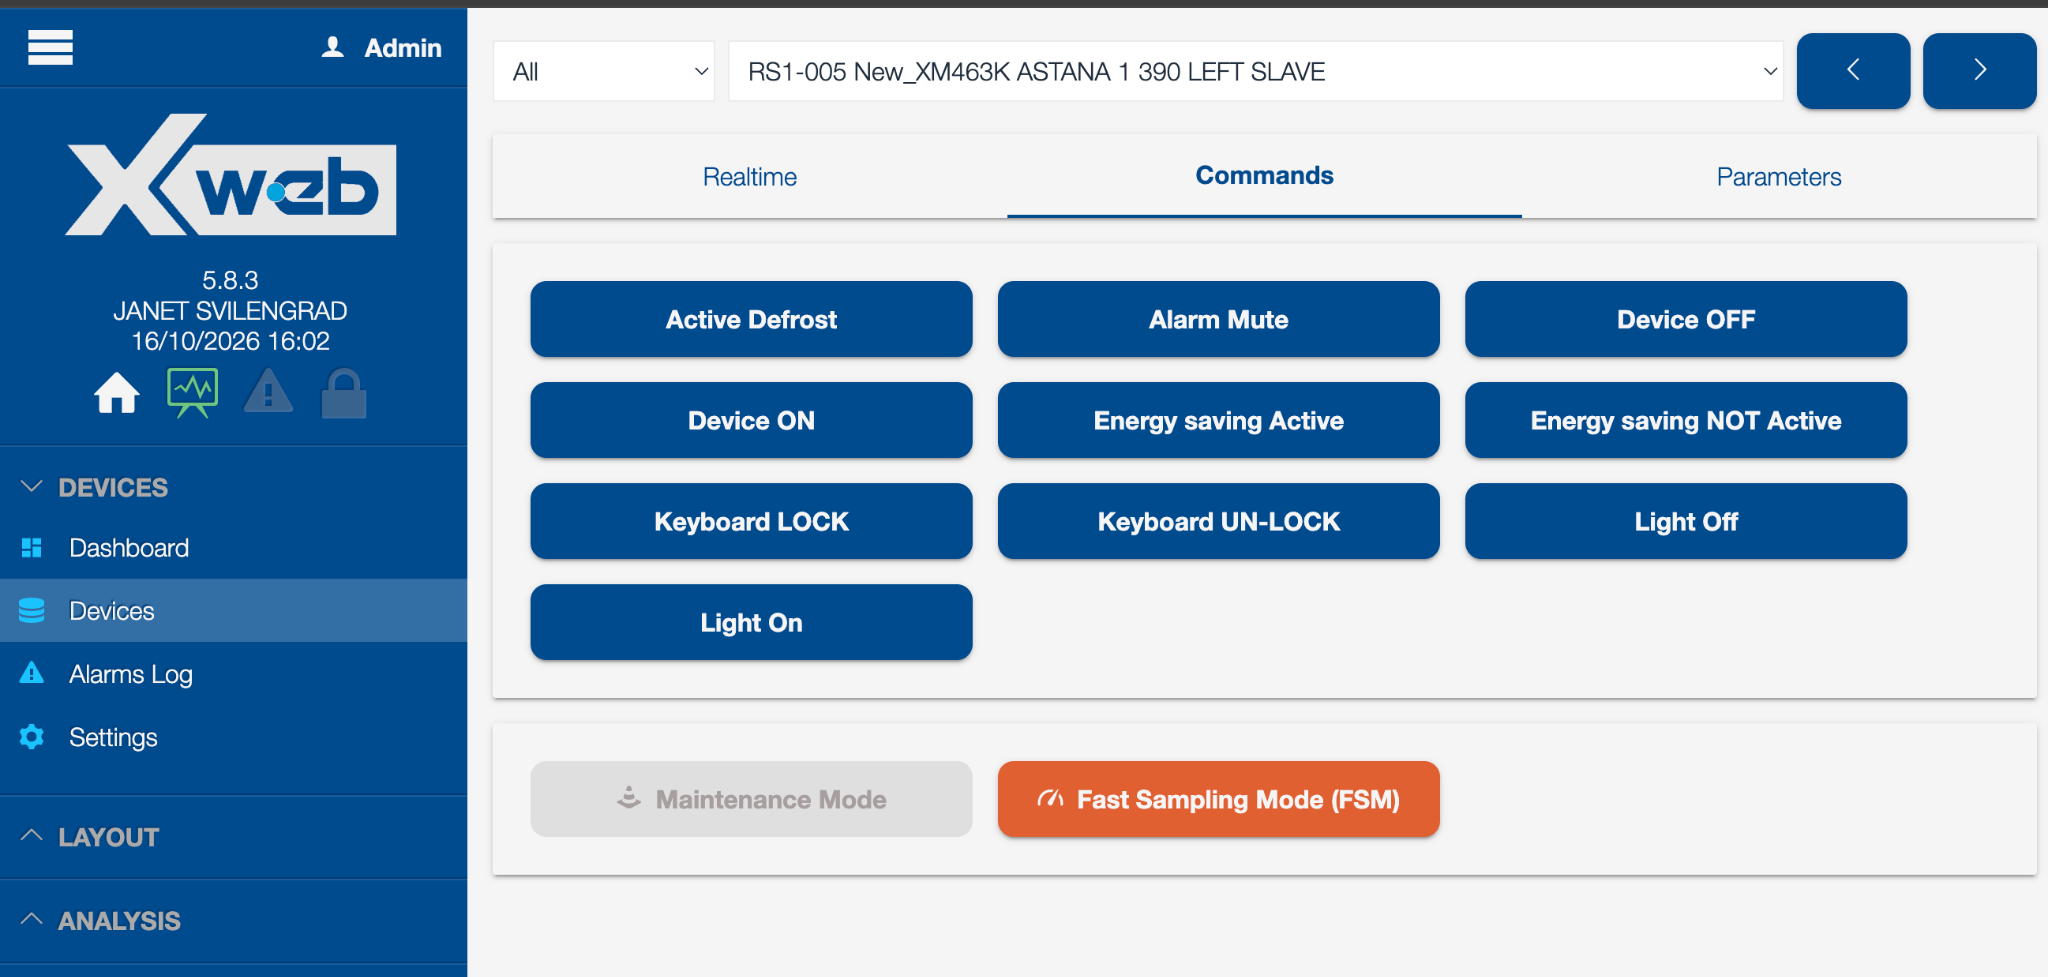
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.

‍

Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.

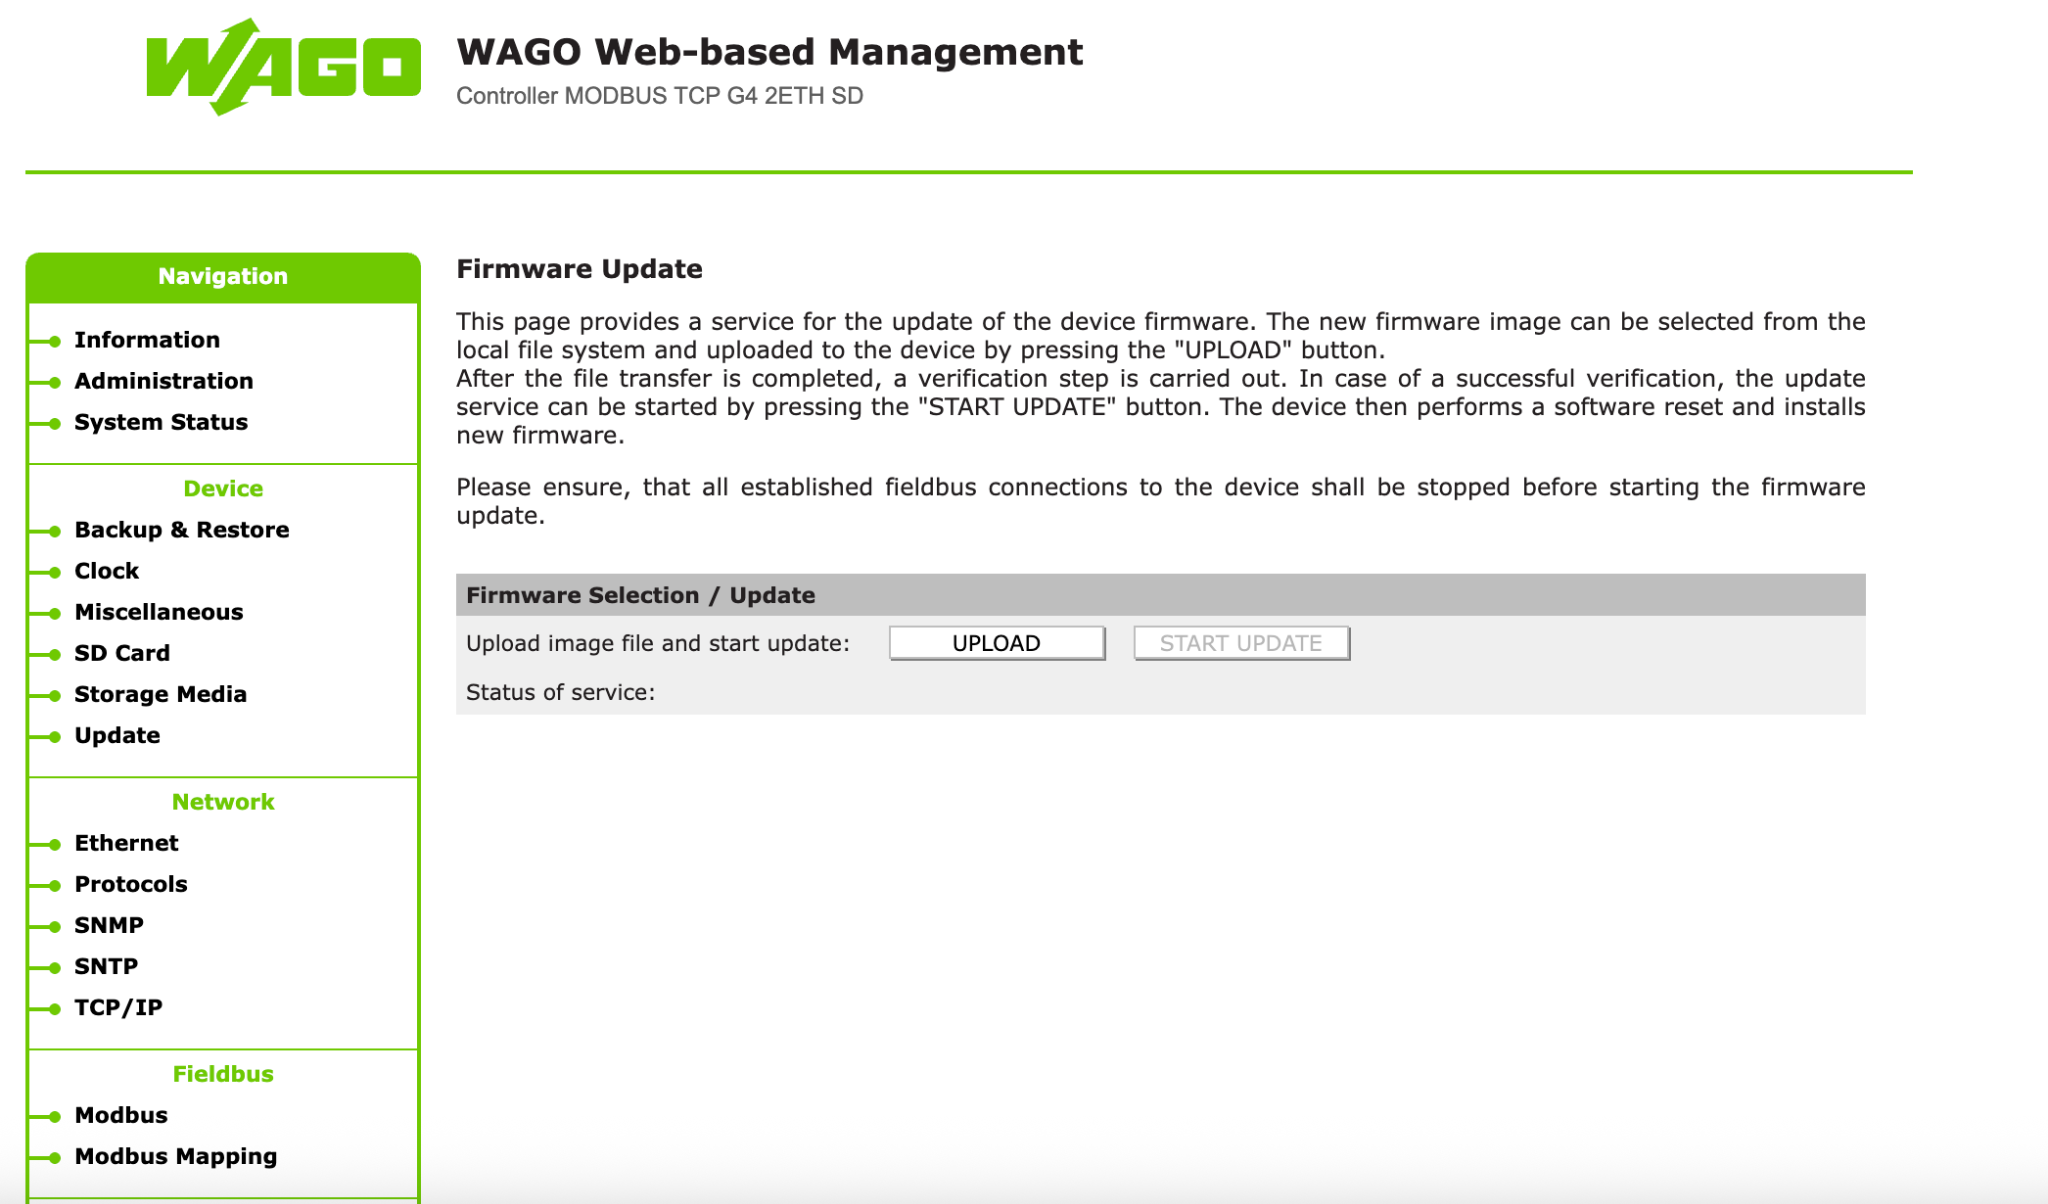
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.

‍

Figure 2: WAGO Management interface.

‍

The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.

‍

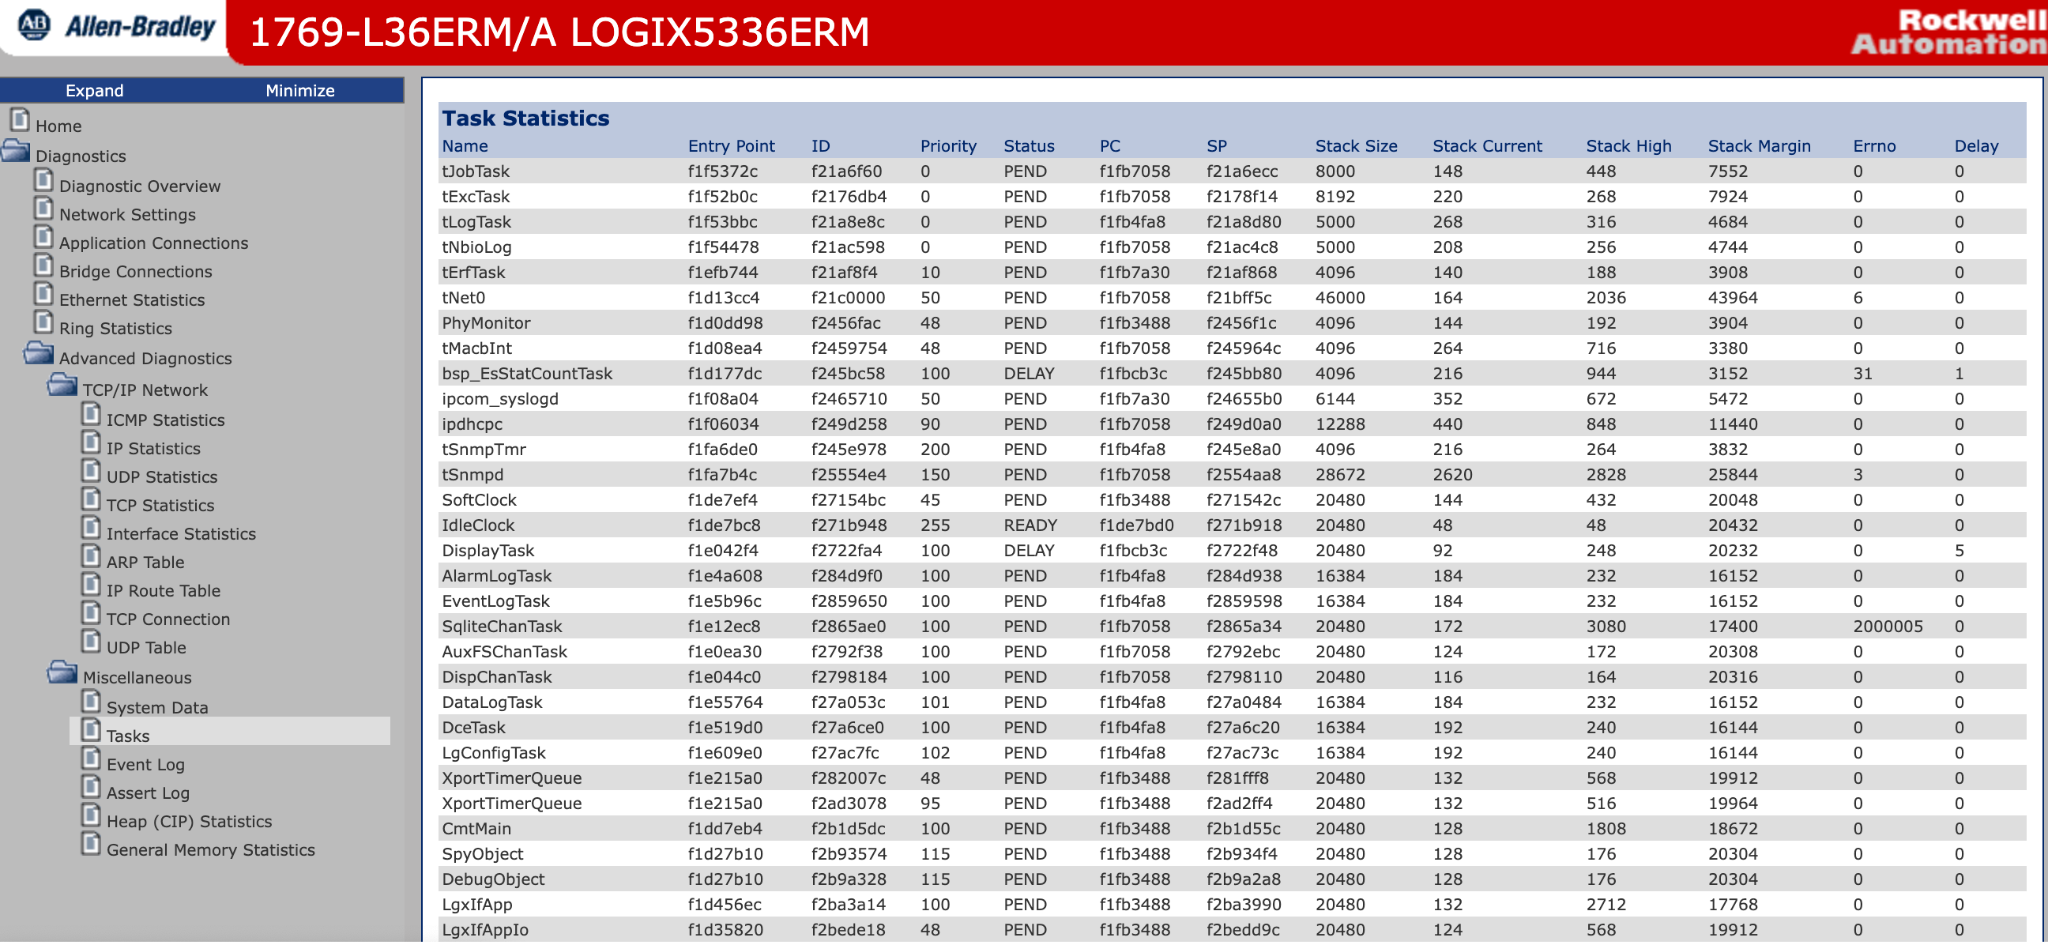
Figure 3: Web interface for Allen-Bradley CompactLogix controller.

‍

Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.

Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.

The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.

The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.

Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.

The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.

Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.

Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.

Darktrace helps security teams gain visibility across IT and OT and respond to risks: https://www.darktrace.com/products/operational-technology.

Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.

References

1.        https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

‍

Continue reading
About the author
Tara Gould
Malware Research Lead
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ