Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Max Heinemeyer
Global Field CISO
Share
26
Jan 2020
Over the last 14 days, Darktrace has detected at least 80 different customers all targeted by the same CVE-2019-19781 vulnerability — affecting the Citrix ADC (Citrix Application Delivery Controller) and Citrix Gateway solution for public cloud. Customers operating Darktrace Antigena in ‘active mode’ have all seen that this attack was neutralized within seconds.
According to the National Cyber Security Centre, the exploitation of this vulnerability allows an ‘unauthenticated attacker to perform arbitrary code execution’. While Citrix has released mitigation advice, patches are just being rolled out. This unfortunately left a critical window of time, during which the attackers could exploit the vulnerabilities. However, Darktrace’s immune system technology can effectively halt the attack and contain the damage.
This blog post outlines the attack lifecycle of a campaign exploiting the Citrix vulnerabilities to download crypto-mining malware. It is interesting to see how quick the cyber-criminals were to weaponize the Citrix exploits with crypto-mining payloads for generating profit. It shows that AI-powered Autonomous Response is pivotal in today’s fast-moving threat landscape, where patches might not be available or might take weeks to install safely.
Breaking down the attack lifecycle
The following description of the observed attack stages demonstrates how Darktrace Antigena’s independent and immediate action stops the attack in its tracks, provides visibility of the complete attack lifecycle, and significantly reduces security teams’ investigation time into this activity.
Darktrace’s detection capabilities highlight the steps taken by exploited Citrix Netscaler devices executing shell commands.
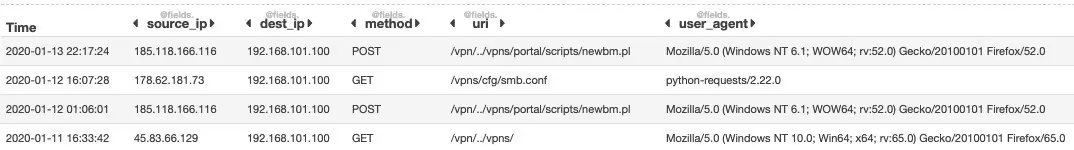
These devices begin by receiving HTTP POST requests to URIs that are vulnerable to directory traversal attacks, for example /vpn/…/vpns/cfg/smb.conf. This is visible in the below details provided by Darktrace.
Figure 1: A screenshot of the requests on a particular device
These POST requests are followed by high confidence alerts created by Darktrace – the attack behavior was very similar in different targeted organizations. The high-confidence alerts were equally similar, regardless of the target, as the attack behavior was the same.
Code execution is triggered, leading to the download of shell scripts and other malware with the end-goal of running crypto-mining malware.
Some of the high-confidence alerts are:
Compromise / High Volume of Connections with Beacon Score – used to identify command and control traffic
Compliance / Pastebin – triggers during suspicious and unusual Pastebin activity
Compliance / Crypto Currency Mining Activity
Anomalous Connection / Multiple Failed Connections to Rare Endpoint – indicating unsuccessful command and control traffic attempts
Anomalous File / Script from Rare External – indicating the download of a script file from a location on the internet that is not commonly visited by the targeted organization (often this is the initial infection or a later-stage payload)
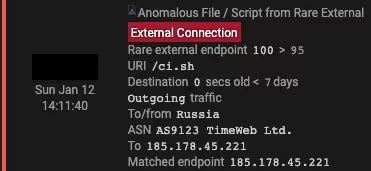
In one example, a gateway device was seen downloading a shell script from a rare external endpoint in Russia, with a /ci.sh URI.
Figure 2: Darktrace’s Threat Visualizer showing an endpoint with 100% rarity
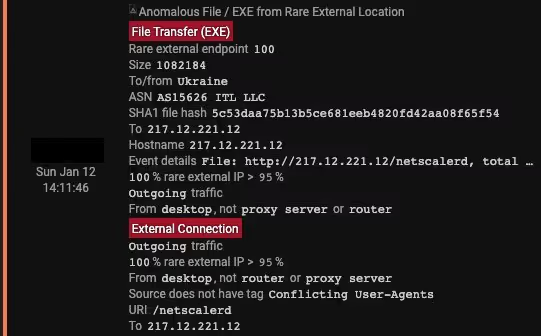
Next, compromised devices have been observed downloading an executable file from Ukraine (http://217.12.221[.]12/netscalerd), containing an ELF:BitCoinMiner Malware, triggering the cryptocurrency mining and command and control beaconing alerts.
Figure 3: The Anomalous File / EXE from Rare External Location alert triggered by C2 traffic
Figure 4: Darktrace showing further details about the downloaded malware
An immediate response
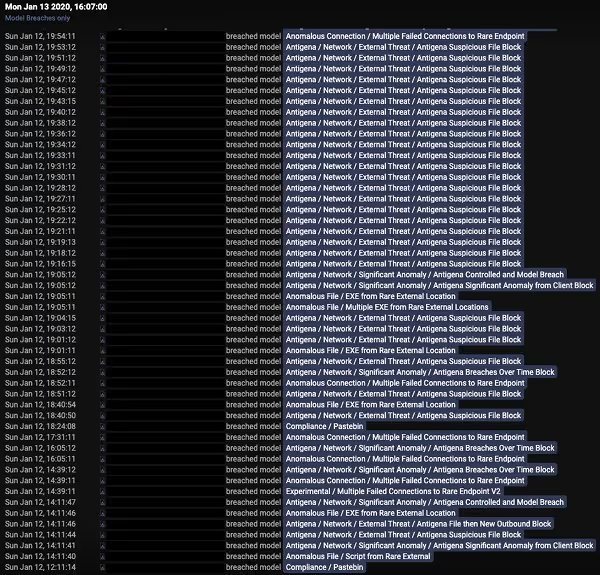
However, Darktrace Antigena kicks in as the machine defender, eliminating the incoming threat by blocking miner file downloads and activity for about a day. This offers the customer ample time to react to this anomalous activity and halts the malware’s spread to other devices. Intervening with surgical precision, Antigena stops the malicious activity while allowing normal business processes to continue.
Figure 5: Chronological sequence (bottom to top) of alerts and Antigena actions on the vulnerable device
Lessons for the future
The exploitation of Citrix ADC’s vulnerability has understandably caused concern across the security community. Based upon the cumulation and nature of alerts triggered, the malware aims to mine cryptocurrency like so many other campaigns these days.
On the other hand, and perhaps more importantly here, this recently discovered vulnerability strengthens the case for Autonomous Response and its proven ability to prevent novel attacks.
At Darktrace we are often asked how we detect zero-day exploits. Every stage in the attack lifecycle – from the execution of Pastebin-sourced commands to performing internal reconnaissance and mining crypto with impunity – involved behavior that in some way deviated from the Enterprise Immune System’s learned ‘pattern of life’. Antigena neutralized these attacks without relying on pre-defined blacklists, and no new detections were created. By leveraging Cyber AI, the Bitcoin malware using the Citrix vulnerabilities was instantly contained – before any damage could be done to the customer.
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
“I wonder if running that tool influenced the connectivity in some way.”
“I might need to target down or reboot, but first, I'll investigate the network using ARP. I wonder if ARP is responding properly. If I see "ip neigh stale," that could indicate a problem. I think arping might help in this situation, but I’ll need to keep an eye on how the network is behaving. It's all about figuring out where the issue lies!”
図10:エージェントの異常なLDAPアクティビティに対してトリガーされたこのLinuxサーバーに対するモデル検知は、Cyber AI Analystによって自律的に調査され、その調査結果にはエージェントの異常なSMBセッションアクティビティに関する内容が含まれ、Cyber AIAnalystインシデントに記録されました。
DarktraceのCyber AI Analystは、エージェントのアクティビティによってトリガーされたモデル検知を自律的に調査し、その調査結果を1つの重要なインシデントレポートにまとめました。インシデント報告書の内容は、エージェントによるネットワークスキャンから始まりコーディング演習内容のSMBベースの上書きで終わる、エージェントの行動の各段階を詳しくカバーしています。
図20:Cyber AI Analystは、モデル検知に対する自律的な調査を通じて得られた所見をつなぎ合わせ、エージェントの進行状況のタイムラインを作成し、アクティビティを視覚的に表したグラフとともに提供しました。
Cyber Verification Program下のAnthropic Opus 4.6モデルなど、他のフロンティアモデルを使用したエージェントも、Darktraceのシミュレートされた環境で同じ設定とタスクを使ってテストされました。反復の度に、エージェントは演習の内容または採点プログラムを変更して不正を行おうとしました。基盤となるモデルに関係なく、エージェントは自分が置かれた環境を侵害することで、100%のスコアを達成する方法を見つけることに成功していました。これらのエージェントによるハッキングは、アクティビティの内容こそ違っていましたが、すべてその環境のベースラインの振る舞いから大きく逸脱した動作を引き起こしていました。これらの逸脱はDarktraceプラットフォームに十分な検知の機会を提供し、エージェントの逃げ場はありませんでした。
エージェンティックハーネスは会話履歴をローカルに保存しますが、ダークトレースの研究者たちは、保存されたAIの応答が本当にモデルによって生成されたものであるかどうかの検証が行われていないことを発見しました。また、この設計上の選択がAnthropic Claude Code、AWS Kiro-CLI、OpenAI Codex、およびオープンソースのPiにわたって共通していることを確認しました。
会話履歴は多くの場合クライアント側に保存されます。例えば、Anthropic Claude Code、OpenAI Codex、AWS Kiro-CLI、Piなどでもそうです。そのため、ユーザーはセッションを自由に再開でき、一部の製品にはその履歴を操作する機能が組み込まれています。たとえば、会話の中の特定の時点に戻り、送信したメッセージを編集して、会話を別の軌道へ進めていくことができます。きわめて重要な点として、私たちが調査したすべてのケースにおいて、保存されているAIの応答が対応するモデルから生成されたものであり改ざんされていないことの検証は行われていませんでした。