ブログ
/
Email
/
March 29, 2023

Email Security & Future Innovations: Educating Employees

As online attackers change to targeted and sophisticated attacks, Darktrace stresses the importance of protection and utilizing steady verification codes.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Dan Fein
VP, Product
Default blog image
29
Mar 2023

In an escalating threat landscape with email as the primary target, IT teams need to move far beyond traditional methods of email security that haven’t evolved fast enough – they’re trained on historical attack data, so only catch what they’ve seen before. By design, they are permanently playing catch up to continually innovating attackers, taking an average of 13 days to recognize new attacks[1]. 

Phishing attacks are getting more targeted and sophisticated as attackers innovate in two key areas: delivery tactics, and social engineering. On the malware delivery side, attackers are increasingly ‘piggybacking’ off the legitimate infrastructure and reputations of services like SharePoint and OneDrive, as well as legitimate email accounts, to evade security tools. 

To evade the human on the other end of the email, attackers are tapping into new social engineering tactics, exploiting fear, uncertainty, and doubt (FUD) and evoking a sense of urgency as ever, but now have tools at their disposal to enable tailored and personalized social engineering at scale. 

With the help of tools such as ChatGPT, threat actors can leverage AI technologies to impersonate trusted organizations and contacts – including damaging business email compromises, realistic spear phishing, spoofing, and social engineering. In fact, Darktrace found that the average linguistic complexity of phishing emails has jumped by 17% since the release of ChatGPT.  

This is just one example of accelerating attack sophistication – lowering the barrier to entry and improving outcomes for attackers. It forms part of a wider trend of the attack landscape moving from low-sophistication, low-impact, and generic phishing tactics - a 'spray and pray' approach - to more targeted, sophisticated, and higher impact attacks that fall outside of the typical detection remit for any tool relying on rules and signatures. Generative AI and other technologies in the attackers' toolkit will soon enable the launch of these attacks at scale, and only being able to catch known threats that have been seen before will no longer be enough.
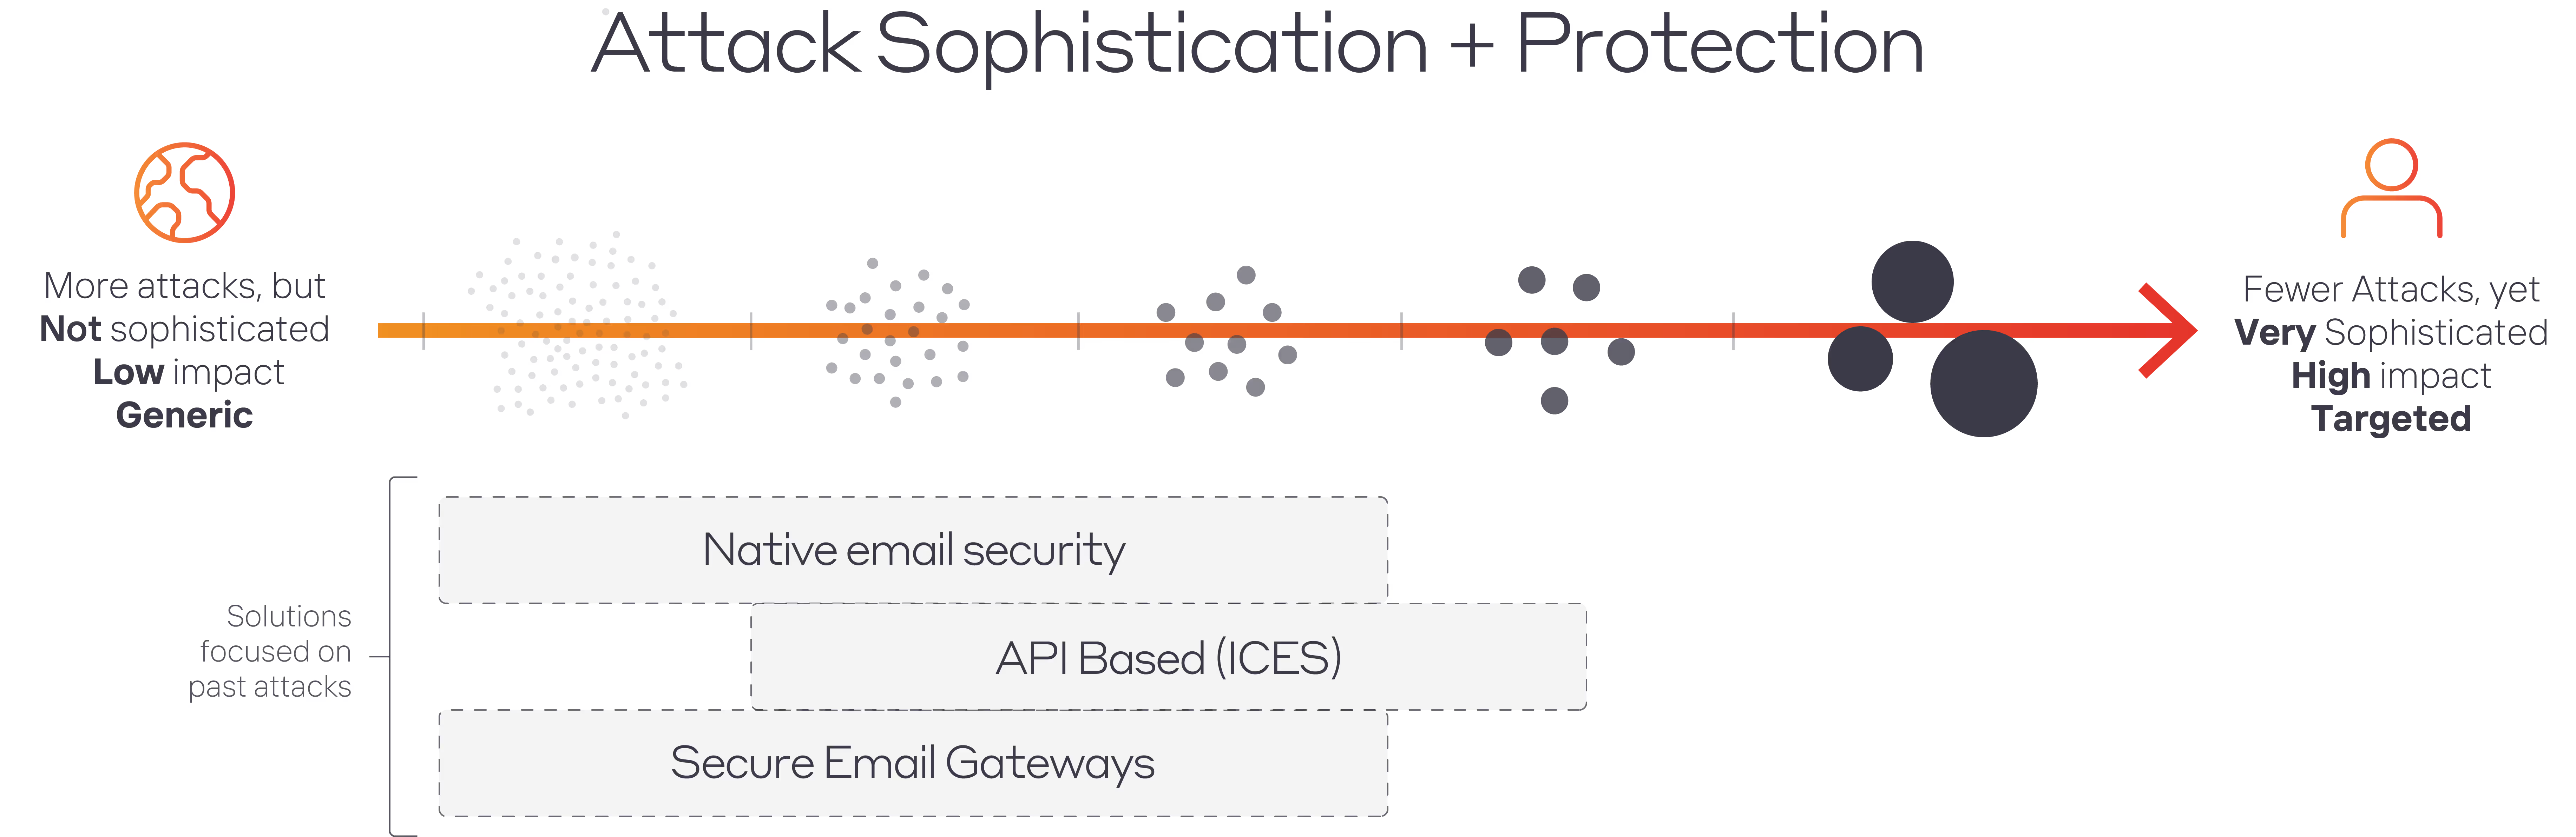
Figure 1: The progression of attacks and relative coverage of email security tools

In an escalating threat landscape with email as the primary target, the vast majority of email security tools haven't evolved fast enough – they’re trained on historical attack data, so only catch what they’ve seen before. They look to the past to try and predict the next attack, and are designed to catch today’s attacks tomorrow.

Organizations are increasingly moving towards AI systems, but not all AI is the same, and the application of that AI is crucial. IT and security teams need to move towards email security that is context-aware and leverages AI for deep behavioral analysis. And it’s a proven approach, successfully catching attacks that slip by other tools across thousands of organizations. And email security today needs to be more about just protecting the inbox. It needs to address not just malicious emails, but the full 360-degree view of a user across their email messages and accounts, as well as extended coverage where email bleeds into collaboration tools/SaaS. For many organizations, the question is not if they should upgrade their email security, but when – how much longer can they risk relying on email security that’s stuck looking to the past?  

The Email Security Industry: Playing Catch-Up

Gateways and ICES (Integrated Cloud Email Security) providers have something in common: they look to past attacks in order to try to predict the future. They often rely on previous threat intelligence and on assembling ‘deny-lists’ of known bad elements of emails already identified as malicious – these tools fail to meet the reality of the contemporary threat landscape. Some of these tools attempt to use AI to improve this flawed approach, looking not only for direct matches, but using "data augmentation" to try and find similar-looking emails. But this approach is still inherently blind to novel threats. 

These tools tend to be resource-intensive, requiring constant policy maintenance combined with the hand-to-hand combat of releasing held-but-legitimate emails and holding back malicious phishing emails. This burden of manually releasing individual emails typically falls on security teams, teams that are frequently small with multiple areas of responsibility. The solution is to deploy technology that autonomously stops the bad while allowing the good through, and adapts to changes in the organization – technology that actually fits the definition of ‘set and forget’.  

Becoming behavioral and context-aware  

There is a seismic shift underway in the industry, from “secure” email gateways to intelligent AI-driven thinking. The right approach is to understand the behaviors of end users – how each person uses their inbox and what constitutes ‘normal’ for each user – in order to detect what’s not normal. It makes use of context – how and when people communicate, and with who – to spot the unusual and to flag to the user when something doesn’t look quite right – and why. Basically, a system that understands you. Not past attacks.  

Darktrace has developed a fundamentally different approach to AI, one that doesn’t learn what’s dangerous from historical data but from a deep continuous understanding of each organization and their users. Only a complex understanding of the normal day-to-day behavior of each employee can accurately determine whether or not an email actually belongs in that recipient’s inbox. 

Whether it’s phishing, ransomware, invoice fraud, executive impersonation, or a novel technique, leveraging AI for behavioral analysis allows for faster decision-making – it doesn’t need to wait for a Patient Zero to contain a new attack because it can stop malicious threats on first encounter. This increased confidence in detection allows for more a precise response – targeted action to remove only the riskiest parts of an email, rather than taking a broad blanket response out of caution – in order to reduce risk with minimal disruption to the business. 

Returning to our attack spectrum, as the attack landscape moves increasingly towards highly sophisticated attacks that use novel or seemingly legitimate infrastructure to deliver malware and induce victims, it has never been more important to detect and issue an appropriate response to these high-impact and targeted attacks. 
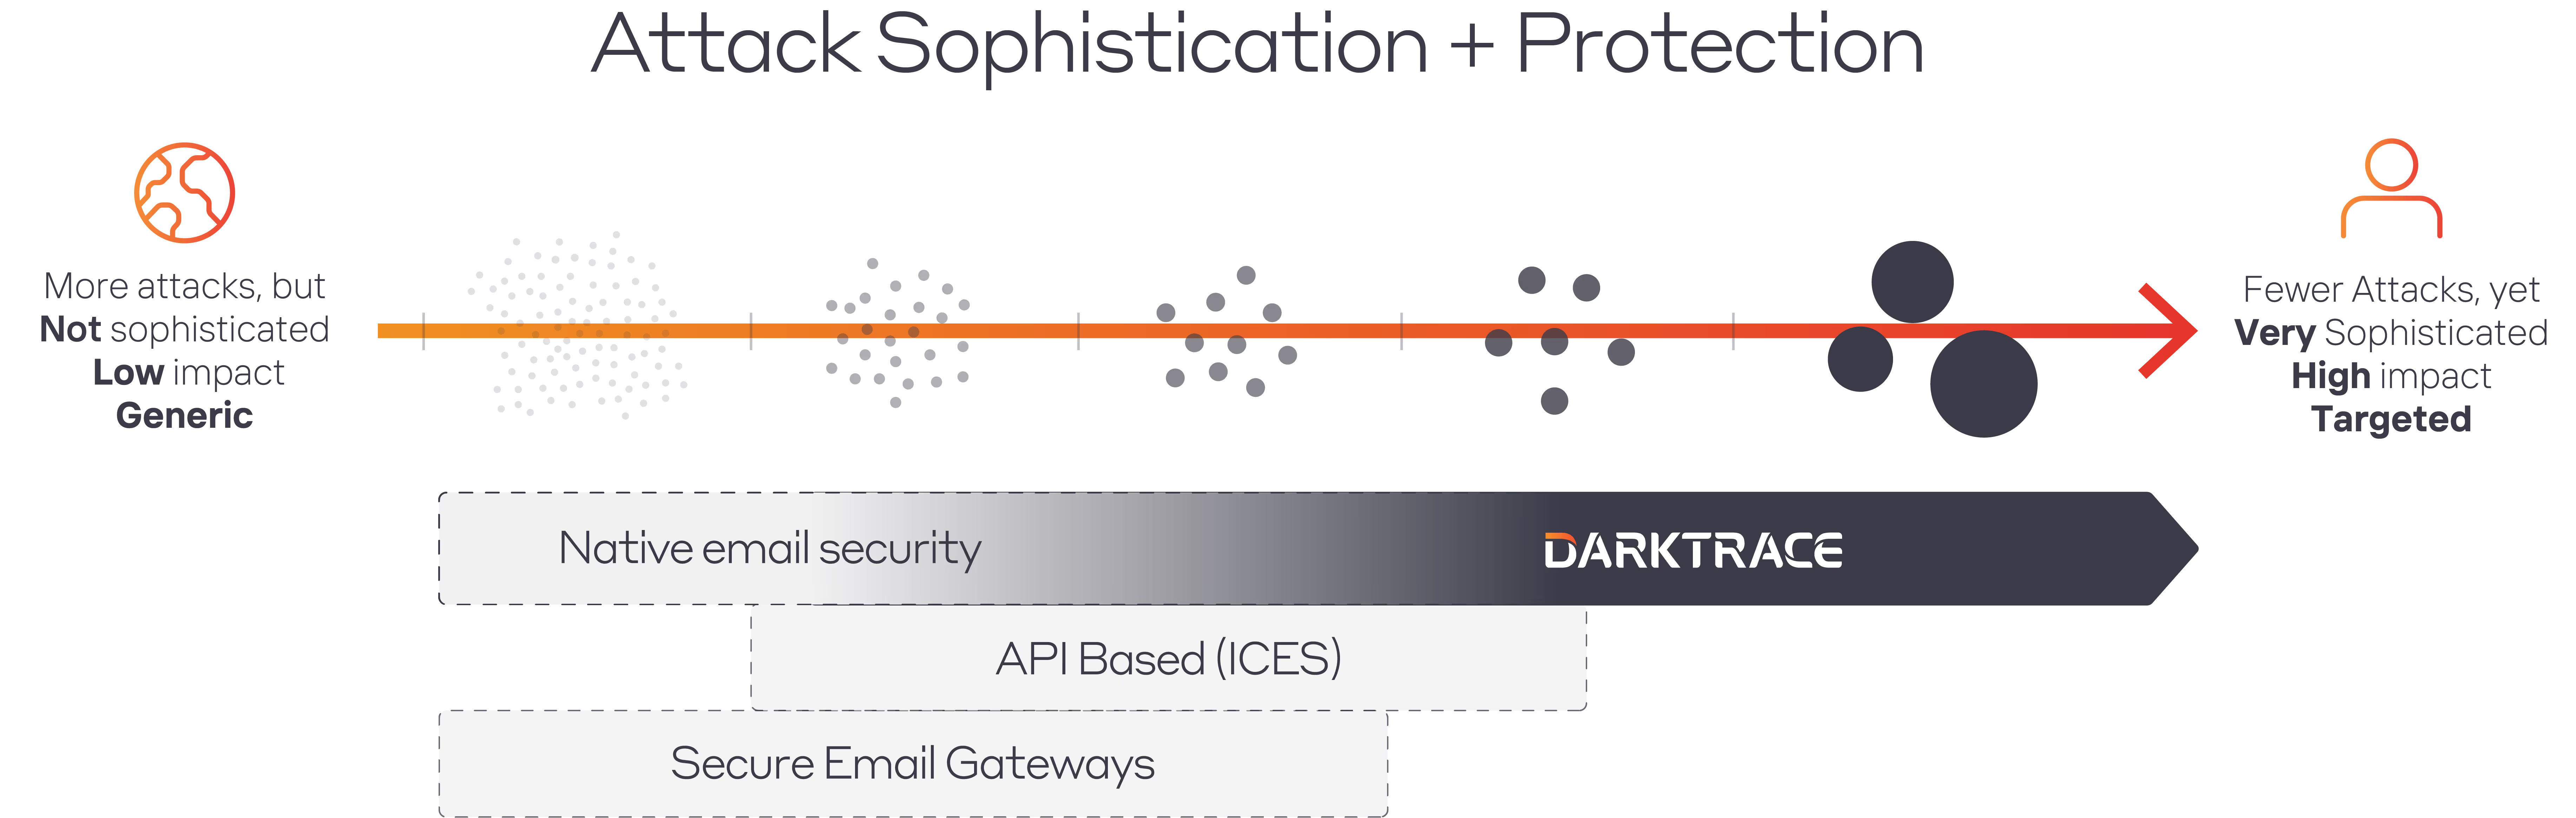
Fig 2: How Darktrace combined with native email security to cover the full spectrum of attacks

‍

Understanding you and a 360° view of the end user  

We know that modern email security isn’t limited to the inbox alone – it has to encompass a full understanding of a user’s normal behavior across email and beyond. Traditional email tools are focused solely on inbound email as the point of breach, which fails to protect against the potentially catastrophic damage caused by a successful email attack once an account has been compromised.    
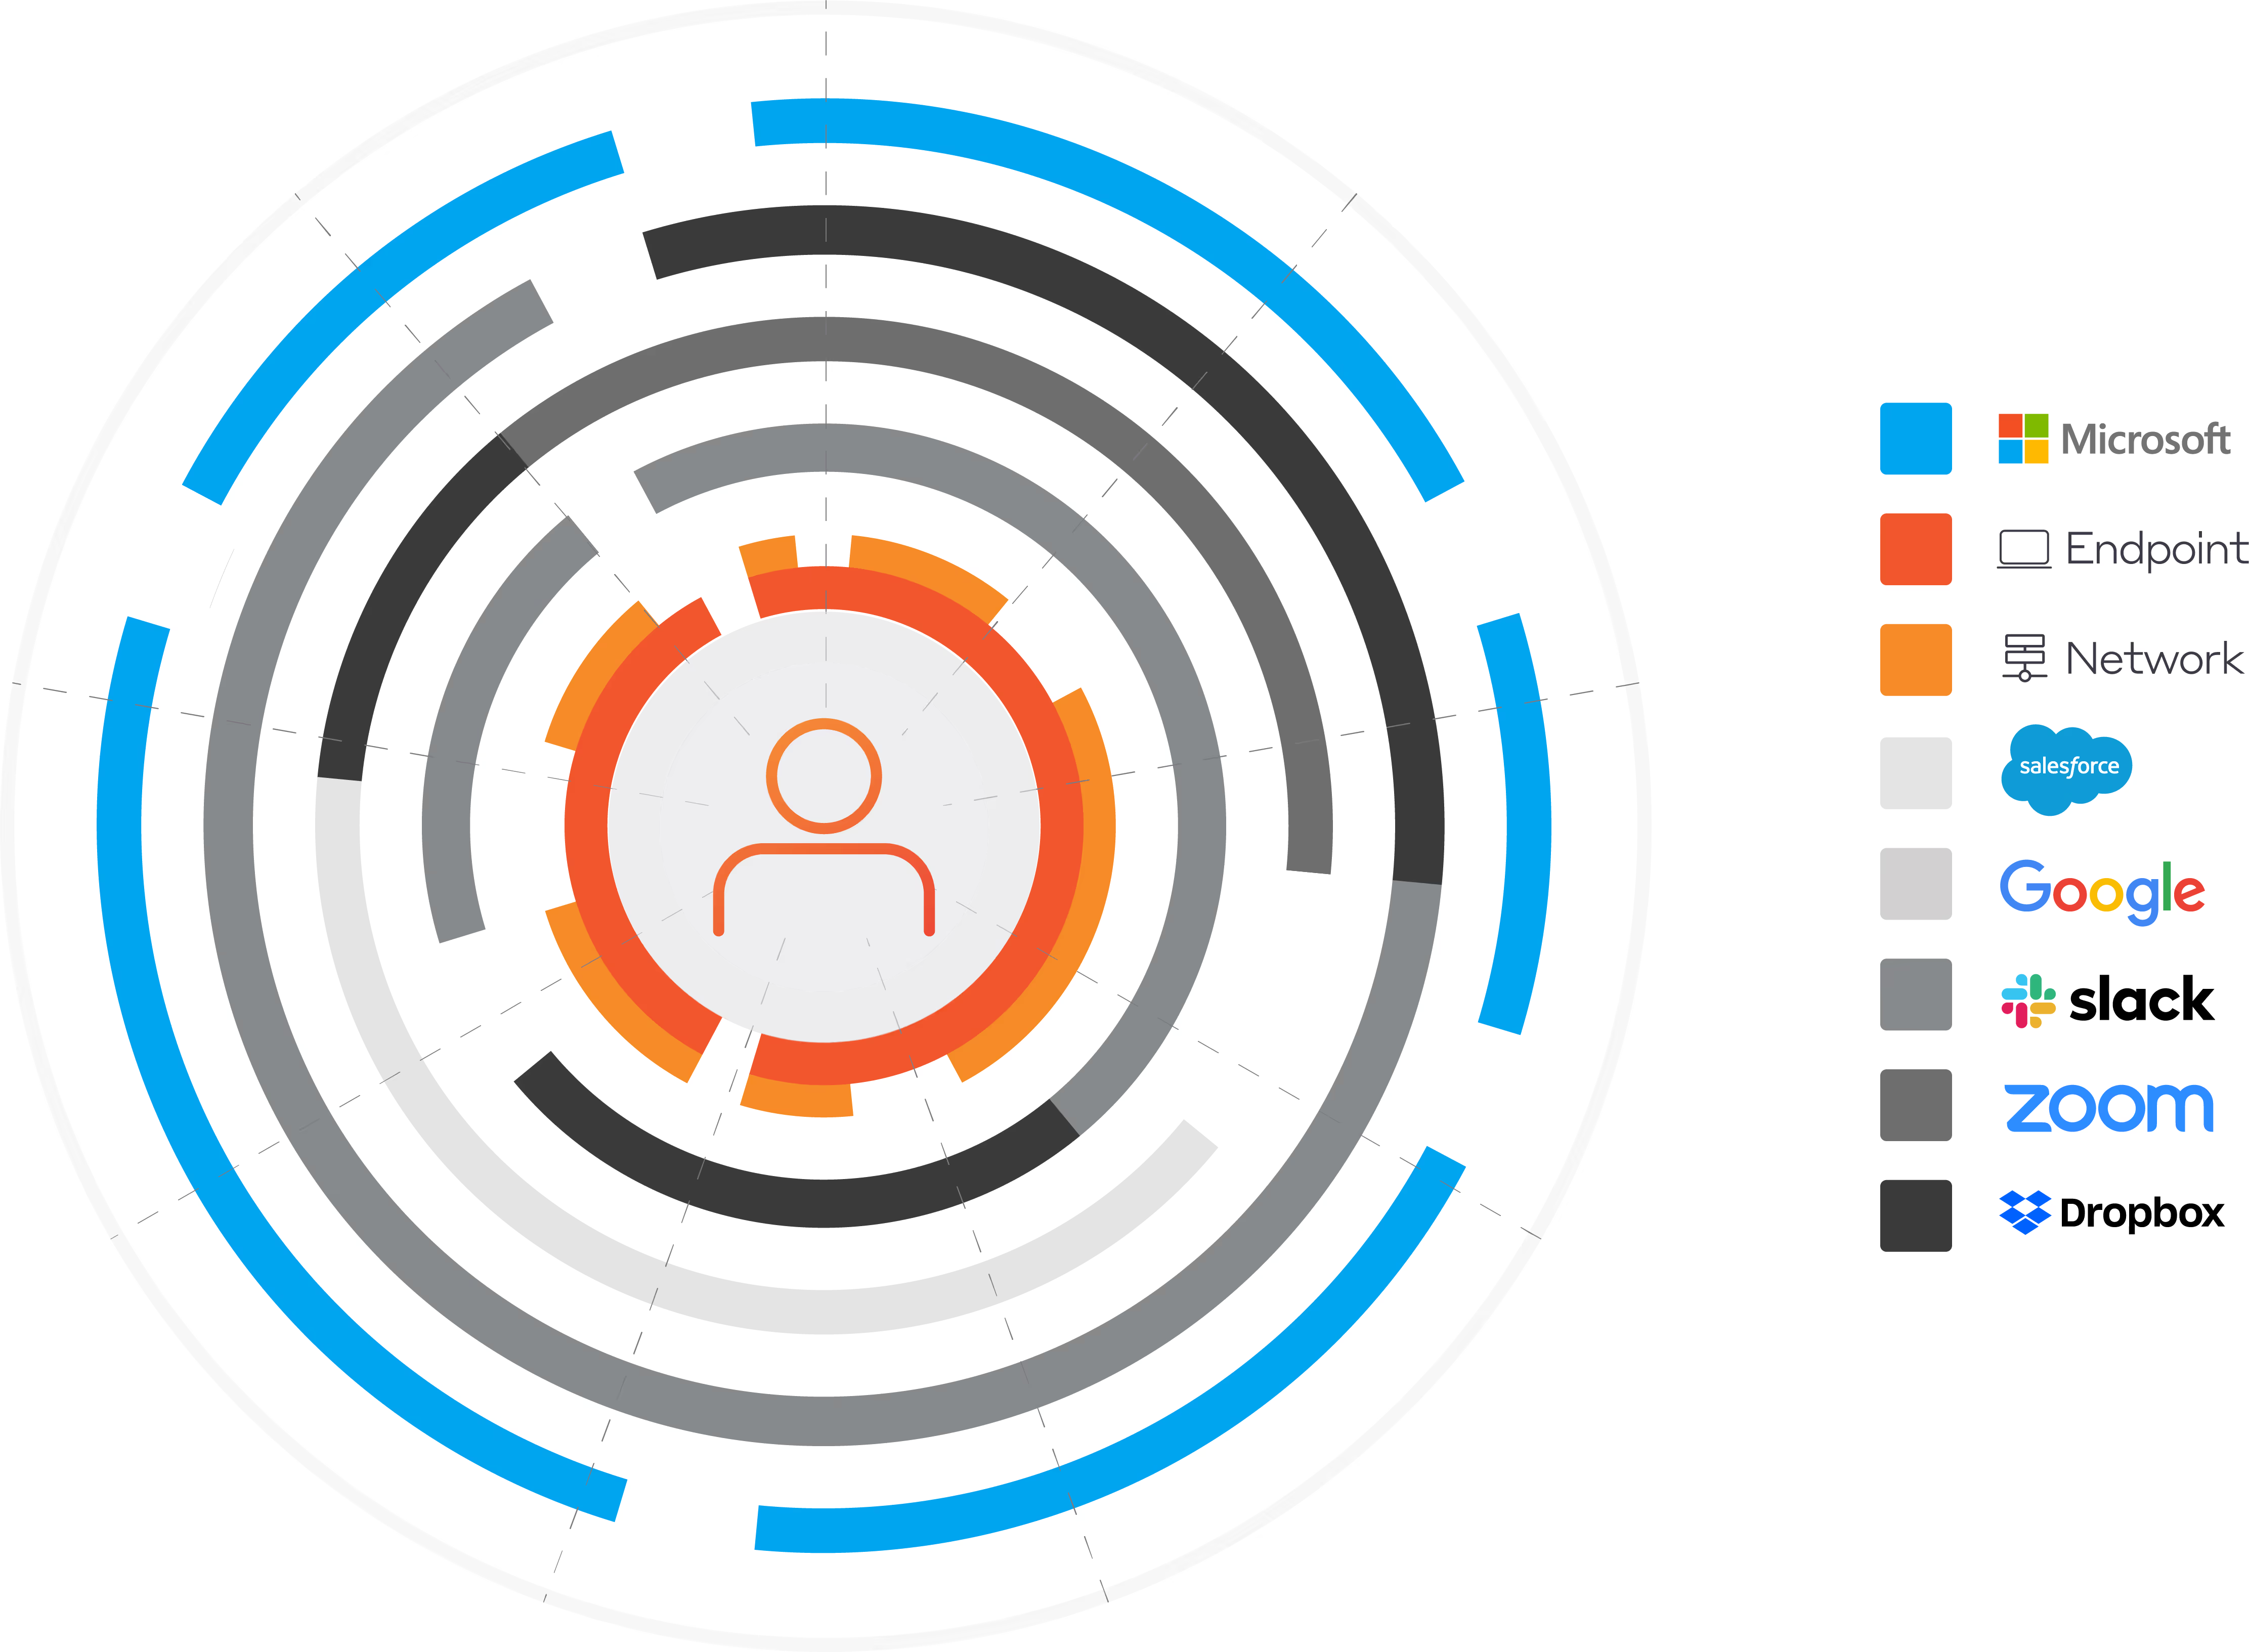
Fig 3: A 360° understanding of a user reveals their digital touchpoints beyond Microsoft

In order to have complete context around what is normal for a user, it’s crucial to understand their activity within Microsoft 365, Google Workspace, Salesforce, Dropbox, and even their device on the network. Monitoring devices (as well as inboxes) for symptoms of infection is crucial to determining whether or not an email has been malicious, and if similar emails need to be withheld in the future. Combining with data from cloud apps enables a more holistic view of identity-based attacks. 

Understanding a user in the context of the whole organization – which also means network, cloud, and endpoint data – brings additional context to light to improve decision making, and connecting email security with external data on the attack surface can help proactively find malicious domains, so that defenses can be hardened before an attack is even launched.

Educating and Engaging Your Employees

Ultimately, it’s employees who interact with any given email. If organizations can successfully empower this user base, they will end up with a smarter workforce, fewer successful attacks, and a security team with more time on their hands for better, strategic work. 

The tools that succeed best will be those that can leverage AI to help employees become more security-conscious. While some emails are evidently malicious and should never enter an employee’s inbox, there is a significant grey area of emails that have potentially risky elements. The majority of security tools will either withhold these emails completely – even though they might be business critical – or let them through scot-free. But what if these grey-area emails could in fact be used as training opportunities?    

As opposed to phishing simulation vendors, behavioral AI can improve security awareness holistically throughout organizations by training users with a light touch via their own inboxes – bringing the end user into the loop to harden defenses.  

The new frontier of email security fights AI with AI, and organizations who lag behind might end up learning the hard way. Read on for our blog series about how these technologies can transform the employee experience, dynamize deployment, augment security teams and form part of an integrated defensive loop.    

[1] 13 days is the mean average of phishing payloads active in the wild between the response of Darktrace/Email compared to the earliest of 16 independent feeds submitted by other email security technologies.

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Dan Fein
VP, Product

Blog

/

AI

/

November 17, 2026

How Microsoft and Darktrace Secure the AI-Powered Enterprise

Default blog imageDefault blog image

When legitimate activity creates business risk

AI is making information more accessible and enabling autonomous agents to act across enterprise systems. But legitimate access can still result in sensitive-data exposure, unintended actions, or activity that deviates from business expectations.

Microsoft's evolving security strategy recognizes this shift, emphasizing continuous risk assessment, stronger identity protection, and security that adapts as AI systems operate. For enterprises, the challenge is increasingly about recognizing when trusted activity introduces risk, even when existing controls are functioning as intended.

Where global intelligence meets deep business context

Microsoft brings global threat intelligence and comprehensive security capabilities, helping organizations protect identities, data, applications, and infrastructure. Its integrated approach connects security signals, governance, detection, and response across increasingly complex environments.

Darktrace complements these strengths with deep, organization-specific behavioral understanding. Powered by Adaptive AI, Darktrace continuously learns the patterns and relationships unique to each business, developing a Unique Behavioral Profile for each organization that helps distinguish meaningful threats from legitimate activity. By connecting identity, activity, context, and intent, it adds another dimension to security intelligence.

Together, Microsoft and Darktrace combine global intelligence with deeper knowledge of how each customer operates. Through supported integrations, this behavioral context enriches existing Microsoft security workflows, enabling more informed investigations and precise response.

This complementary approach extends across three interconnected areas of enterprise security- AI, People and Infrastructure. From understanding how AI and agents operate to protecting trusted communications and the infrastructure businesses depend on, Darktrace strengthens Microsoft's security capabilities with behavioral insight specific to each organization.

Understanding AI beyond permissions and policies

As AI moves into business-critical operations, security teams need to understand more than which applications and agents are approved. They need visibility into how AI is used, what information it accesses, and whether its actions remain aligned with business intent.

Microsoft provides extensive AI development, governance, and security capabilities. Darktrace / SECURE AI complements these with behavioral analysis across Shadow AI, prompts, agent identities and actions, and development risk. Policy Manager helps evaluate activity against organizational AI policies, while the announced integration with Microsoft Agent 365 is designed to enrich agent risk assessments with organization-specific behavioral signals. Together, these capabilities help organizations scale AI adoption with greater confidence.

Recognizing risk within trusted relationships

Sophisticated threats increasingly exploit established business relationships, familiar communications, and legitimate accounts. A message from a trusted supplier or an action taken through an authorized identity may appear routine until considered against the organization's normal behavior.

Darktrace / EMAIL complements Microsoft's native email, identity, and data protection capabilities by understanding how people and organizations communicate. This enables more precise detection of targeted phishing, business email compromise, account takeover, and data loss, supported by proportionate response. Integrations such as Unified Quarantine within Microsoft Defender for Office 365 bring this additional protection into existing security workflows.

Seeing the bigger picture behind an attack across domains

Threats rarely unfold within a single security domain. Suspicious identity activity, unexpected cloud connections, and unusual network behavior may appear unrelated until the relationships between them reveal a developing attack.

Darktrace / HYBRID NETWORK complements Microsoft's security capabilities with organization-specific behavioral detection across network, cloud, identity, and operational technology. Real-Time AI Analyst, including Cyber AI Analyst, connects related activity into investigated incidents that can be delivered into Microsoft Sentinel, helping security teams accelerate investigations and support targeted containment across the hybrid enterprise.

Turning security intelligence into business confidence

As AI becomes more deeply integrated into business operations, organizations need security that understands not only what technology can access, but how it behaves within their unique environment.

Microsoft and Darktrace bring complementary strengths to that challenge. By connecting global threat intelligence and integrated security capabilities with deep behavioral understanding, the partnership helps organizations recognize emerging risks, respond with greater precision, and strengthen their existing security investments.

The opportunity is to turn security intelligence into meaningful business context, enabling organizations to innovate and operate AI with confidence.

Darktrace named a 2026 Microsoft Partner of the Year Finalist for ISV Innovation

Darktrace has been named a finalist for the 2026 Microsoft Partner of the Year Award in the ISV Innovation category.  

This recognition reflects our collaboration with Microsoft to bring business context to enterprise security. By connecting Microsoft's global threat intelligence and integrated security capabilities with Darktrace's deep behavioral understanding, we help organizations recognize emerging risks and respond with greater precision across AI, People and Infrastructure.

Thank you to Microsoft, our customers, and our teams for their continued collaboration.

Meet Darktrace at Microsoft Ignite and the Microsoft Frontier Tour

Explore how Darktrace and Microsoft are bringing behavioral security to AI, people, and infrastructure.

Join Darktrace at Microsoft Ignite in San Francisco, November 17–19, or connect with our experts as we join the Microsoft Frontier Tour across 21 cities worldwide.

Meet Darktrace at Microsoft Ignite

Connect with Darktrace at the Microsoft Frontier Tour

[related-resource]

Continue reading
About the author

Blog

/

AI

/

November 13, 2026

Introducing Darktrace MCP: Connect your AI assistants to the Darktrace Behavioral Defense Platform

Default blog imageDefault blog image

The Darktrace MCP Server is now generally available to users of the Darktrace Platform Portal. It enables compatible AI assistants to query security data, retrieve Cyber AI Analyst findings, and execute supported actions across actively licensed Darktrace products. Customers can now use these capabilities in their own AI workflows to gather incident context, search telemetry, enrich investigations with information from other services, and carry out triage tasks.

What is MCP?
MCP is an open standard developed by Anthropic that lets AI systems connect to and use enterprise tools and data. Adoption of MCP servers creates an opportunity for SOC teams to move beyond isolated AI experiences toward truly operational AI workflows.

Available capabilities

The server exposes tools for three areas of security work:

  • Incident discovery and threat hunting. Retrieve model alerts and incident groups, search for relevant devices and investigate indicators of compromise. Assistants with access to other services can combine these results with external threat intelligence.
  • Investigation and analysis. Retrieve Cyber AI Analyst incident findings, examine related event data, and enrich the investigation with information from other platforms or external documentation.
  • Triage and workflow actions. Add comments, tags and statuses to alerts and assets, modify supported settings such as trusted domains and subnet details, or trigger a Cyber AI Analyst investigation.

Available capabilities depend on the licensed products connected to the server. The toolset also includes access to Secure AI prompt and shadow AI information, cloud misconfigurations and external exposure information, and Email threat trends and supported management functions.

The following examples show how the server’s discovery, investigation, and action capabilities can be combined within an AI assistant.

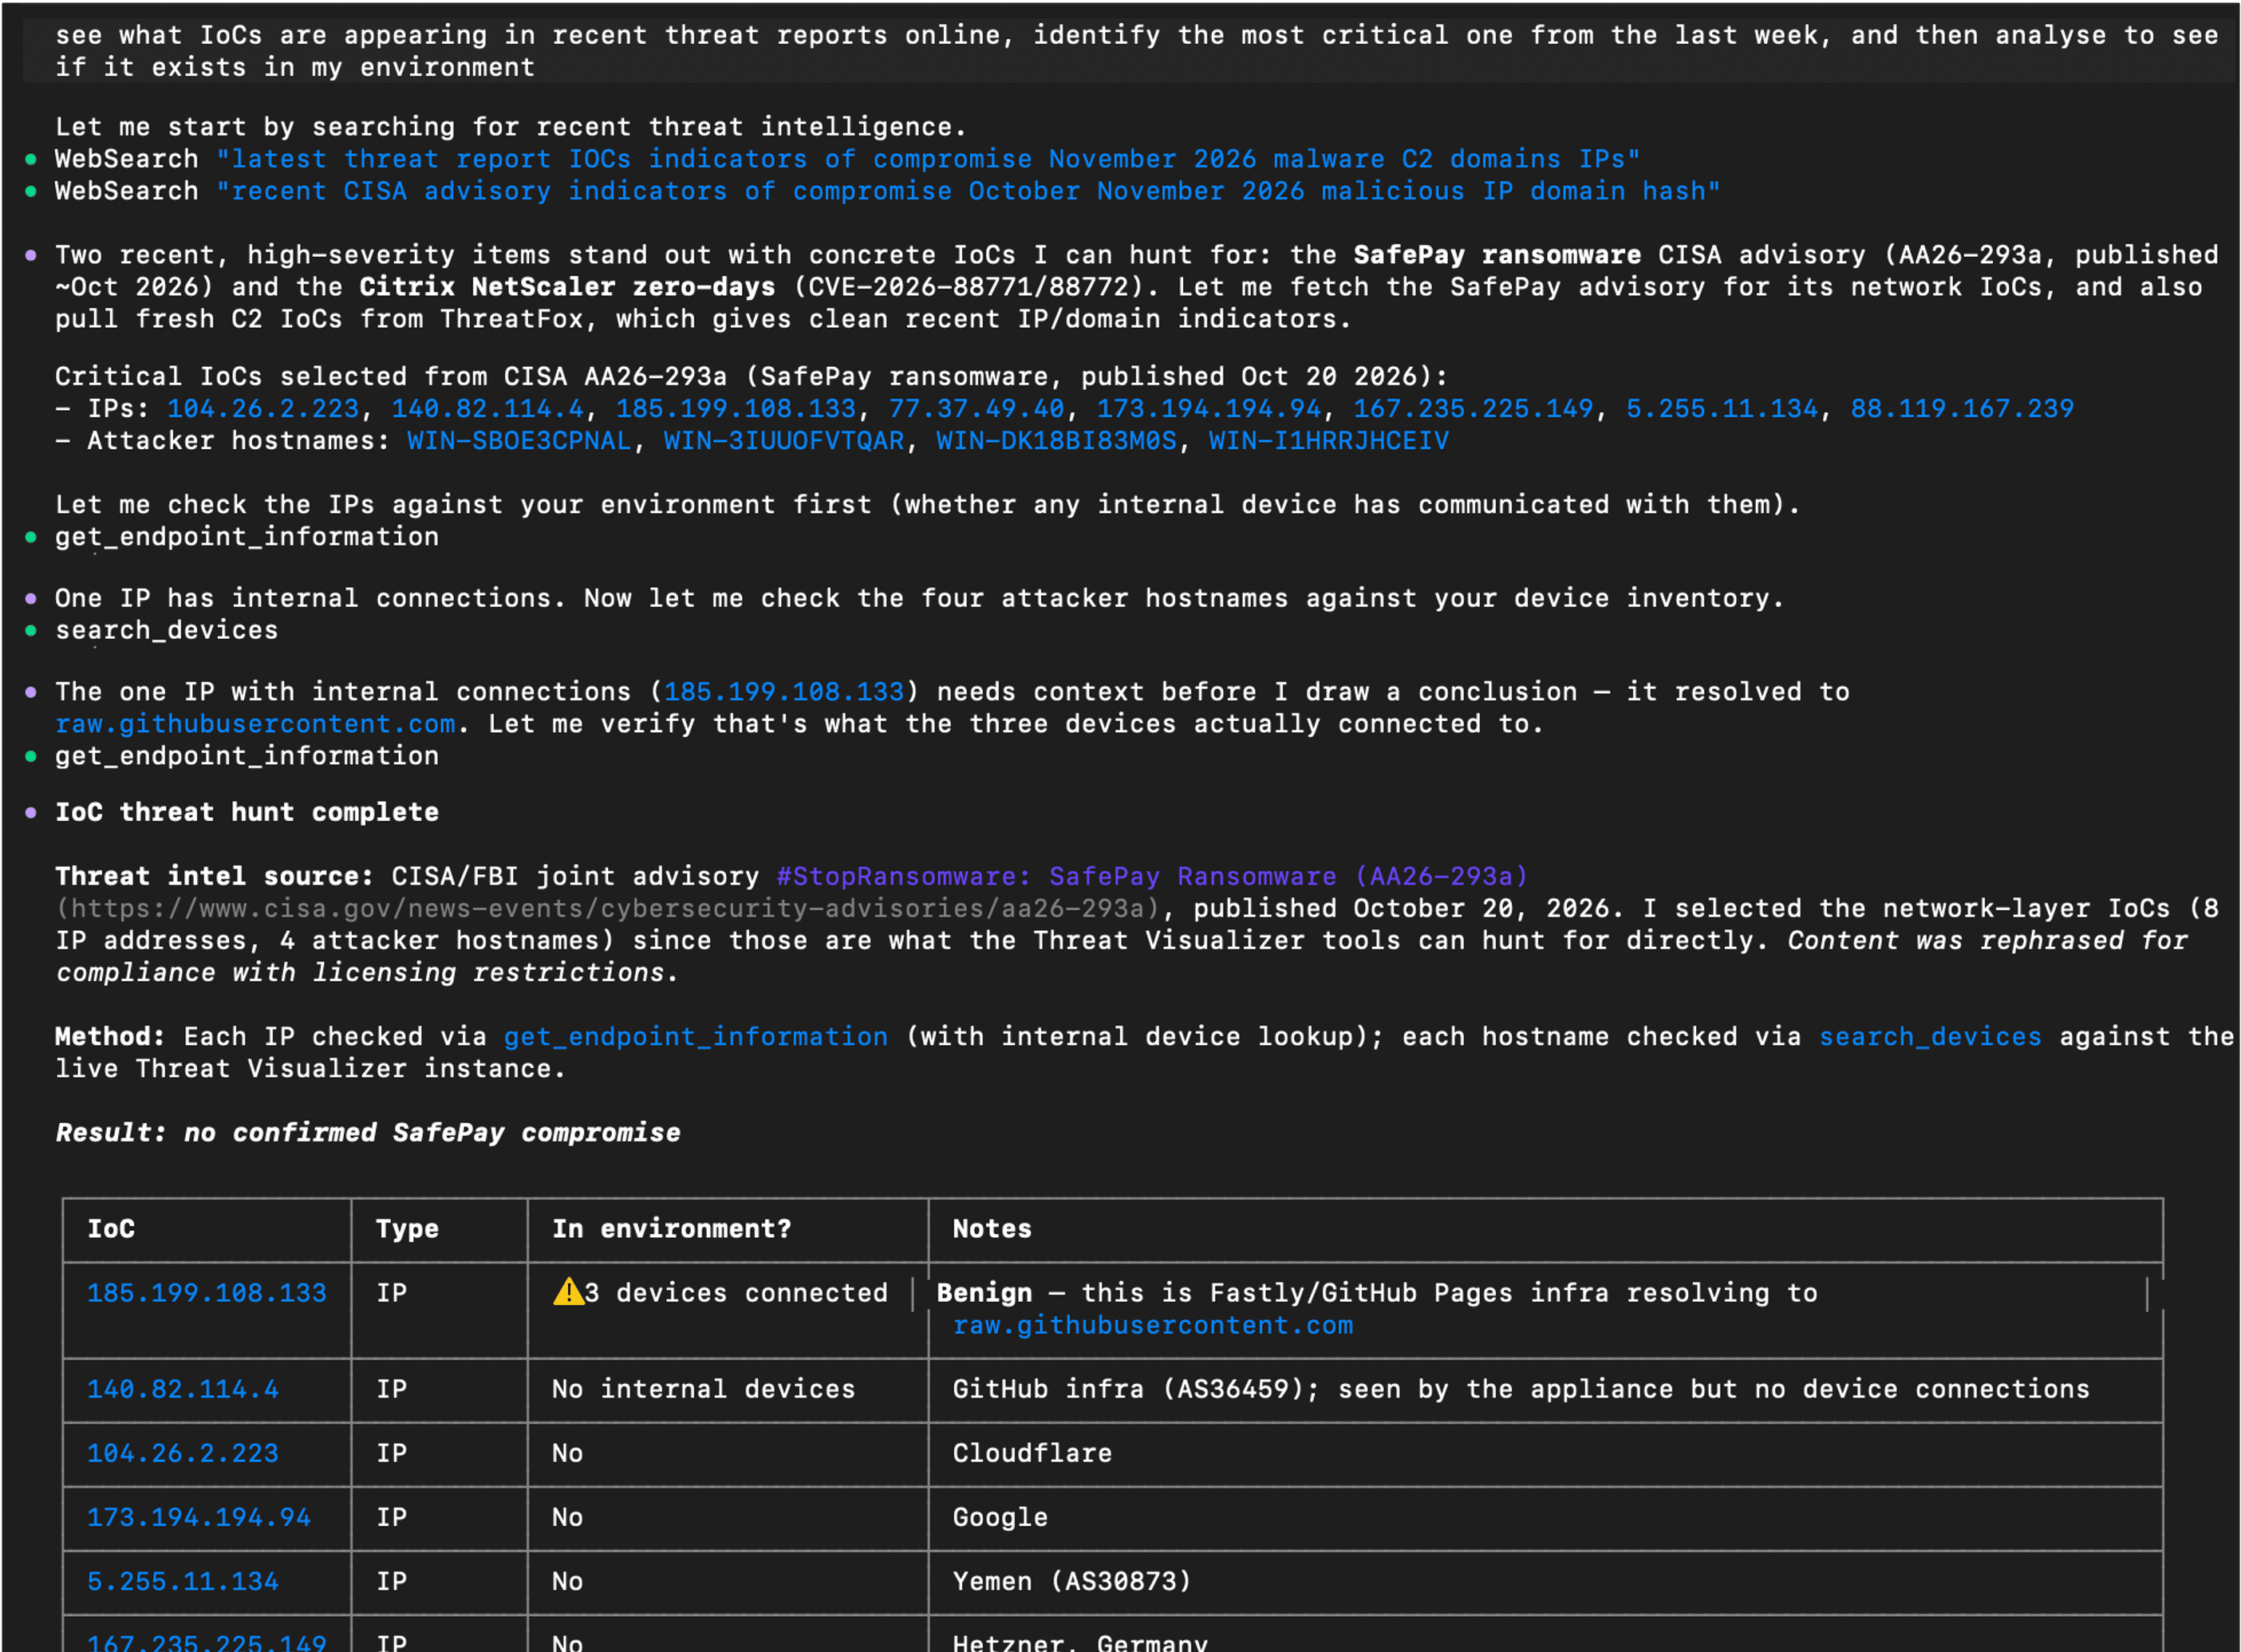
Check external threat indicators against your environment

An assistant can use Darktrace MCP alongside external threat intelligence to check whether reported indicators appear in an environment. Darktrace’s tools provide device information and endpoint context; the assistant’s other tools or connected services supply the external intelligence.

In this example, the assistant searched for recent threat reports, selected indicators of compromise (IoCs) to investigate, and checked for devices that had communicated with the reported IP addresses. It then examined endpoint information to put the matches into context.

Relevant Darktrace tools: search_devices, get_endpoint_information, get_model_alerts, get_incident_events

Example prompt: “See what IoCs are appearing in recent threat reports online, identify the most critical one from the last week, and then analyze to see if it exists in my environment.”

AI assistant output using external threat intelligence alongside data retrieved through the Darktrace MCP Server.

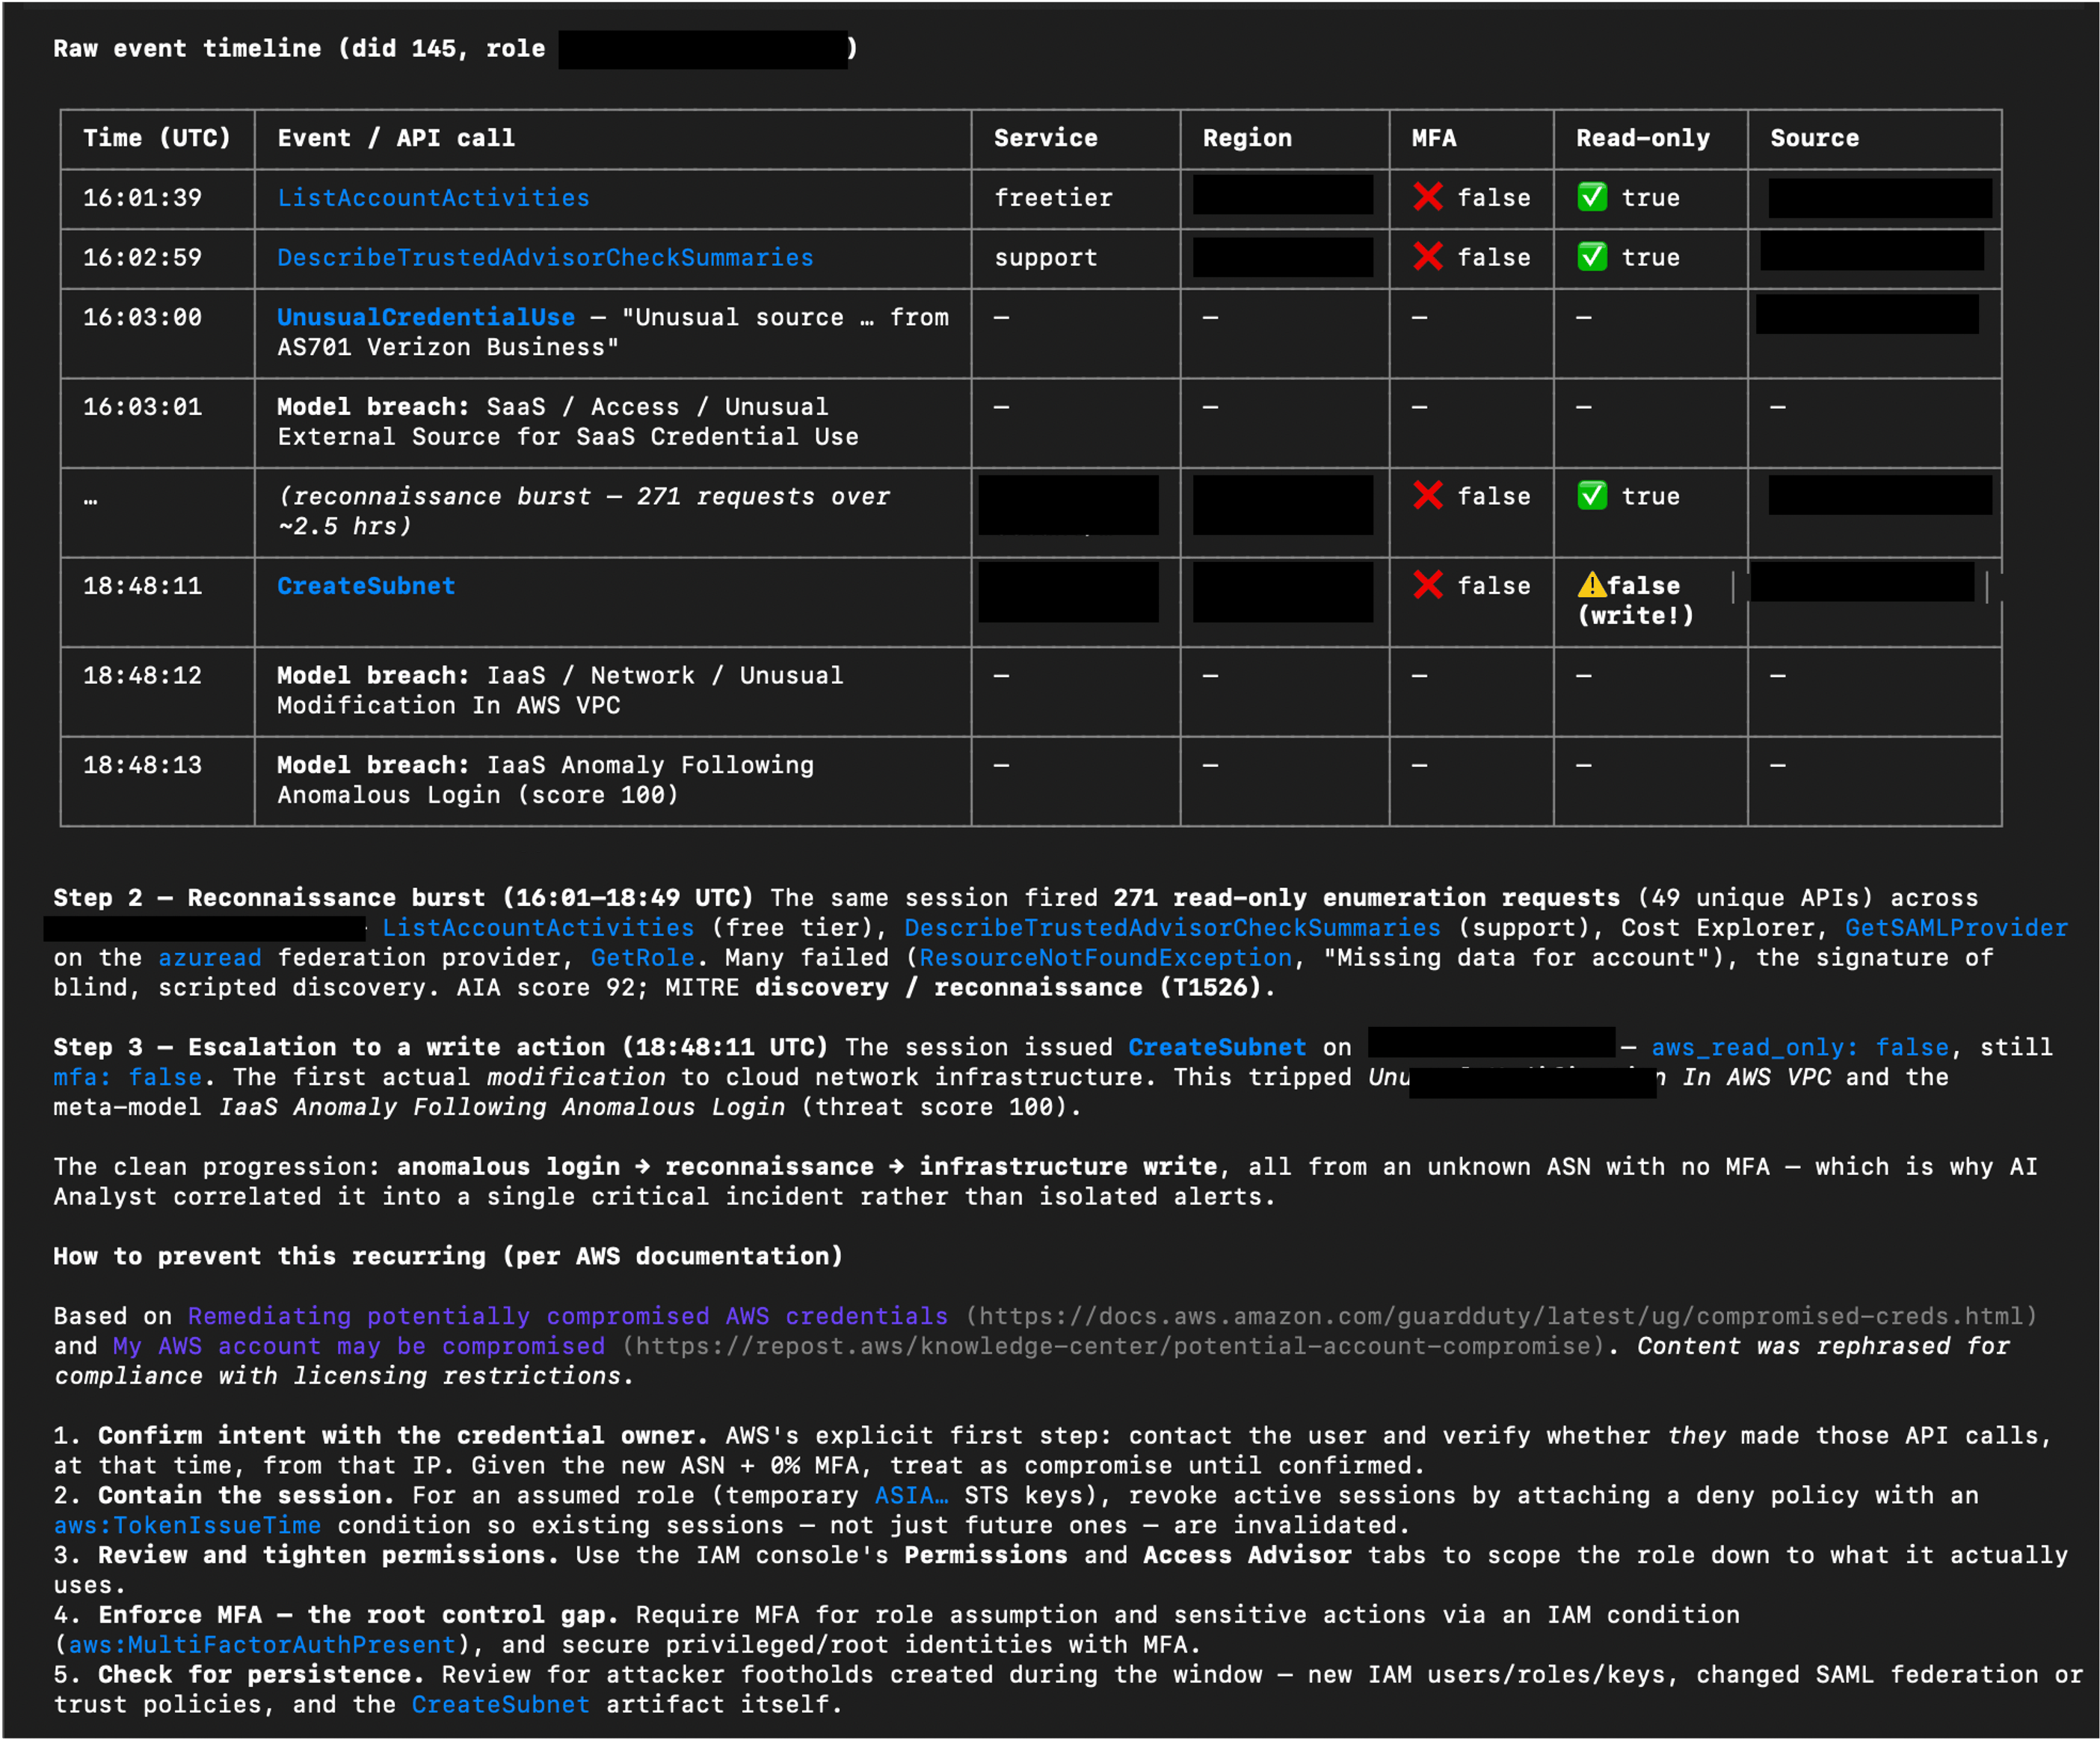
Enrich a Cyber AI Analyst investigation

Cyber AI Analyst provides Darktrace’s incident analysis. Through MCP, an assistant can retrieve those findings, explain specific parts of an incident, and bring in related data from other services.

In this example, the assistant examined a Potential AWS Account Hijack investigated by Cyber AI Analyst. It assembled a step-by-step account and raw event timeline, then consulted AWS documentation to add relevant prevention guidance. The assistant brings together the existing Darktrace analysis, supporting events, and external guidance in one response.

Relevant Darktrace tools: get_incident_groups, get_incident_events, get_detailed_events, get_ai_analyst_investigations, advanced_search

Example prompt: “Drill down on the identified potential AWS account hijack. Show me a detailed step-by-step of what happened using data from Cyber AI Analyst, including a raw event timeline, and provide info on how to prevent this from happening again using info from AWS documentation.”

AI assistant output combining Cyber AI Analyst findings and event data with guidance from AWS documentation. Some sensitive content has been redacted.

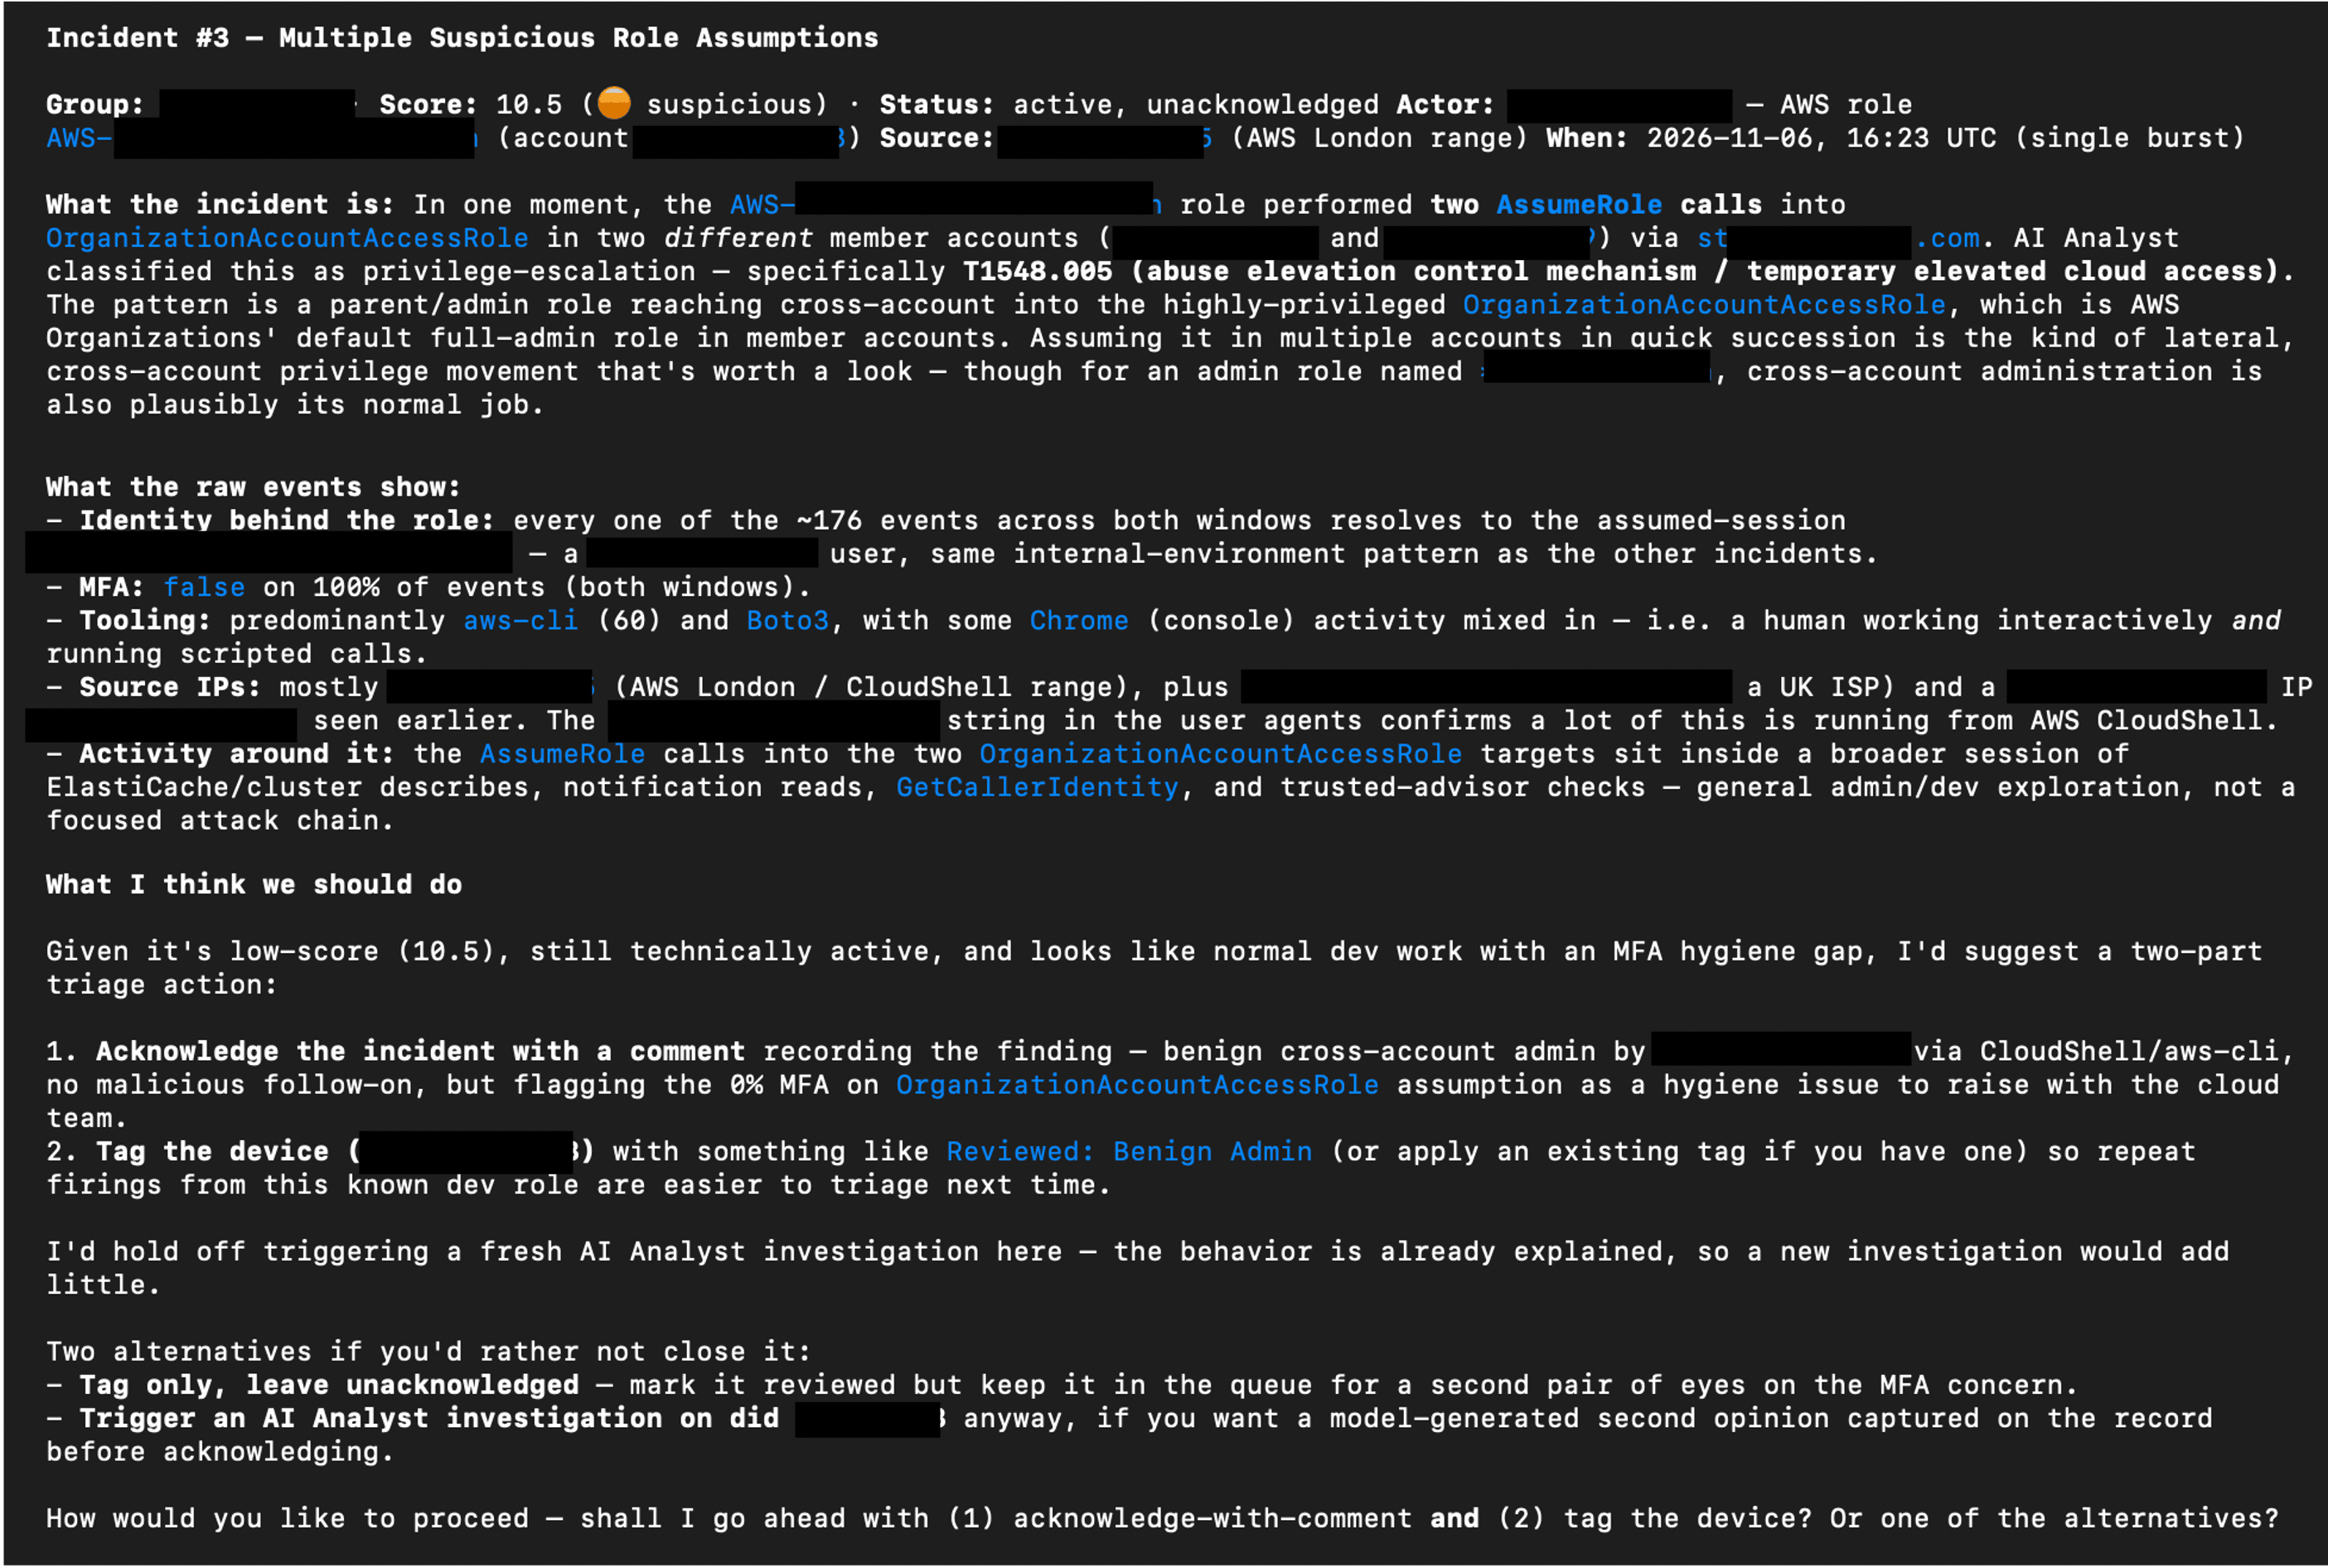
Work through triage with analyst confirmation

The server’s action tools allow an assistant to support repetitive triage tasks as well as retrieve information. For example, to improve efficiency of a daily triage workflow, an analyst could ask an AI assistant to present untriaged alerts one at a time, summarizing each issue and suggesting a next step for confirmation.

The example below shows the assistant proposing actions such as recording a finding, acknowledging an incident, tagging an asset, or triggering a Cyber AI Analyst investigation for more detail. The analyst chooses how to proceed.

Relevant Darktrace tools: get_model_alerts, update_model_alert, update_incident_group, manage_tags, create_ai_analyst_investigation

Example prompt: “Using the Darktrace MCP server, obtain all un-triaged alerts from the last 3 days and display them one at a time. Provide a summary of the issue, and a suggested triage and immediate response action. I will confirm what action should be performed.”

AI assistant output proposing triage actions using information retrieved through Darktrace MCP and asking the analyst how to proceed. Some sensitive content has been redacted.

Permissions and security considerations

The MCP server provides access to supported capabilities within the products a customer is licensed to use. Connections should follow the principle of least privilege, with access appropriate to the intended workflow.

A read-only connection mode is also available for workflows that do not require changes. This mode hides tools that mutate data; configuration details are provided in the Product Guide.

Some tools can change data or perform actions, including adding or removing asset tags, triggering Cyber AI Analyst investigations, and acting on assets. Consider which capabilities an assistant should be able to use before connecting it and retain human oversight of actions that could cause disruption or unwanted changes.

For further guidance, see:

Seven MCP risks CISOs should consider and how to prepare

Anthropic’s MCP Security Best Practices

Use the interface that suits the task

MCP gives customers another way to work with Darktrace alongside its product interfaces. Users may find that complex investigations requiring visual analysis, or strategic decisions involving impactful actions, are better suited to the graphical interfaces within Darktrace products. They can choose the approach that fits their workflow.

How to start using the Darktrace MCP Server

The Darktrace MCP Server is used to connect a compatible AI assistant to supported tools within your Darktrace deployment. The assistant can retrieve alerts and device information, draw on Cyber AI Analyst findings, and perform permitted actions across your licensed products.

To get started, you will need access to the Darktrace Platform Portal and a compatible AI assistant. Follow the Platform Portal MCP Server guide to find out how to create the required credentials and configure the connection today.

Contact a Darktrace representative to explore how the Darktrace MCP Server can support your security operations.

To learn more about Darktrace can help protect your MCP servers within your broader AI and agent use, discover Darktrace / SECURE AI.

‍

Appendix: Darktrace MCP available tools

The following tool catalogue reflects the list supplied for this announcement. Available tools depend on the connected products and access. The list may change as tools are added or removed.

ToolProductDescription
get_helpGeneral / MCP ServerReturns orientation info about the Darktrace MCP server: its purpose, tool categories, and documentation.
get_productsGeneral / MCP ServerLists available Darktrace product instances and their instance_id values needed by other tools.
submit_feedbackGeneral / MCP ServerLogs feedback about tool coverage, clarity, or usability for the Darktrace team.
count_devicesThreat VisualizerReturns the total count of devices/assets managed by Darktrace.
search_devicesThreat VisualizerSearches for devices by keyword and returns basic matching device details.
query_devicesThreat VisualizerQueries comprehensive device information using filters like IP, MAC, subnet, or SaaS module.
edit_deviceThreat VisualizerUpdates a device's label, type, priority, or notes.
get_device_activityThreat VisualizerReturns aggregated time-series data of a device's connection/data volume trends over 4 weeks.
get_detailed_eventsThreat VisualizerRetrieves individual low-level events (connections, notices, model breaches, processes) for a device or alert.
get_subnetsThreat VisualizerRetrieves monitored subnets with CIDR, device counts, DHCP status, and traffic stats.
update_subnetThreat VisualizerEdits subnet details such as label, network range, coordinates, and DHCP/exclusion flags.
get_model_alertsThreat VisualizerRetrieves model alerts (breaches) with model info, device details, and triggered components.
get_model_alert_credentialsThreat VisualizerReturns credentials seen on the device that triggered a given model alert.
update_model_alertThreat VisualizerComments on and/or acknowledges a model alert.
get_modelsThreat VisualizerRetrieves detection models with their logic, actions, and configuration.
get_incident_groupsThreat VisualizerRetrieves AI Analyst incident groups with scores, MITRE tactics, devices, and summaries.
get_incident_eventsThreat VisualizerRetrieves AI Analyst incident events with AI summaries, MITRE tactics, and breach details.
update_incident_groupThreat VisualizerComments on and/or acknowledges an AI Analyst incident group.
create_ai_analyst_investigationThreat VisualizerCreates a manual AI Analyst investigation for a device around a specified time.
get_ai_analyst_investigationsThreat VisualizerRetrieves the status and results of manual AI Analyst investigations.
advanced_searchThreat VisualizerExecutes a Lucene-syntax Advanced Search query against Darktrace log data.
get_advanced_search_syntaxThreat VisualizerReturns the full Advanced Search query syntax reference (must be called before querying).
get_response_actions_summaryThreat VisualizerReturns a summary of active and pending Autonomous Response actions and action counts over a time range.
get_endpoint_informationThreat VisualizerLooks up external endpoints (IPs/hostnames) for location, reputation, and connection history.
get_cvesThreat VisualizerRetrieves CVEs detected across assets with severity, scores, and affected devices.
get_system_healthThreat VisualizerReturns comprehensive system health metrics (CPU, memory, disk, licenses, bandwidth).
get_dam_alertsThreat VisualizerRetrieves health alerts from the Darktrace Alert Management system.
get_module_statusesThreat VisualizerRetrieves the status of Darktrace modules, optionally filtered to failing ones.
get_tagsThreat VisualizerRetrieves device tags and optionally the devices/credentials they are applied to.
manage_tagsThreat VisualizerCreates, deletes, applies, or removes tags on devices or credentials.
get_trusted_domainsThreat VisualizerRetrieves domains marked as trusted.
manage_trusted_domainsThreat VisualizerAdds or removes a trusted domain entry.
get_watched_domainsThreat VisualizerRetrieves watched domains monitored for suspicious activity.
manage_watched_domainsThreat VisualizerAdds or removes watched domain entries.
get_workflow_integration_ticketsThreat VisualizerRetrieves third-party platform tickets created by Workflow Integrations for Darktrace events.
get_cloud_accountsDarktrace / HYBRID NETWORKRetrieves cloud deployment accounts and their monitoring/compliance statuses.
get_cloud_architecturesDarktrace / HYBRID NETWORKRetrieves cloud architectures with risk breakdown, cost, and asset counts.
get_cloud_assetsDarktrace / HYBRID NETWORKRetrieves cloud assets with type, service, region, and attached/associated assets.
get_cloud_asset_filtersDarktrace / HYBRID NETWORKReturns available filter fields and operators for querying cloud assets.
get_cloud_misconfiguration_alertsDarktrace / HYBRID NETWORKRetrieves cloud security misconfiguration alerts grouped by rule.
get_cloud_misconfigured_assetsDarktrace / HYBRID NETWORKRetrieves the assets affected by a specific cloud misconfiguration rule.
get_cloud_rule_informationDarktrace / HYBRID NETWORKReturns detailed rationale, remediation, and compliance mappings for a cloud security rule.
get_emailDarktrace / EMAILRetrieves detailed information about a specific email by UUID.
search_emailsDarktrace / EMAILSearches for emails using filters and a time range.
get_email_search_filtersDarktrace / EMAILReturns available email search filter definitions and values.
action_emailDarktrace / EMAILPerforms an action (hold, release, approve/reject release) on an email for specific recipients.
analyse_email_linkDarktrace / EMAILAnalyzes a URL found in an email, returning classification tags and analysis metrics.
get_email_overviewDarktrace / EMAILReturns an aggregated email dashboard overview (threats, actions, campaigns, etc.).
get_email_listsDarktrace / EMAILRetrieves email lists and their entries.
manage_email_listsDarktrace / EMAILAdds or edits email lists, and adds or removes entries within an email list.
get_email_addin_recordsDarktrace / EMAILRetrieves Inbox Analysis or Misdirected Email add-in records.
get_email_audit_logsDarktrace / EMAILRetrieves EMAIL system audit log events for a time range.
get_email_audit_log_event_typesDarktrace / EMAILReturns available audit log event types for filtering.
get_secure_ai_overviewDarktrace / SECURE AIReturns a dashboard overview of Secure AI activity (anomaly scores, sessions, prompt categories).
get_secure_ai_sessionsDarktrace / SECURE AIRetrieves monitored generative-AI sessions with risk levels and anomaly scores.
get_secure_ai_promptsDarktrace / SECURE AIRetrieves individual prompts for a Secure AI session with anomaly/risk classifications.
get_secure_ai_usersDarktrace / SECURE AIRetrieves users interacting with generative-AI apps, with risk scores and session counts.
get_secure_ai_eventsDarktrace / SECURE AIRetrieves raw events ingested by the Secure AI post-handler.
get_secure_ai_detectionsDarktrace / SECURE AIRetrieves detections raised by Secure AI models with scores and OWASP/ATLAS mappings.
get_secure_ai_response_actionsDarktrace / SECURE AIRetrieves Autonomous Response actions taken by Secure AI.
manage_secure_ai_response_actionDarktrace / SECURE AIClears, confirms, extends, or reactivates a Secure AI response action.
get_shadow_ai_dashboardDarktrace / SECURE AIReturns the Shadow AI dashboard of unsanctioned AI/LLM services detected.
get_shadow_ai_detectionsDarktrace / SECURE AIRetrieves individual Shadow AI detections for unsanctioned AI/LLM service usage.
get_forensic_investigationsDarktrace / HYBRID NETWORKRetrieves forensic investigations with status, alarm counts, and AI summaries.
get_forensic_evidencesDarktrace / HYBRID NETWORKRetrieves evidence items with alarm counts, OS details, and processing status.
get_forensic_evidence_fileDarktrace / HYBRID NETWORKReturns detailed file metadata/content (hash, strings, VirusTotal, AI description) from an evidence item.
browse_forensic_evidence_filesDarktrace / HYBRID NETWORKBrowses the filesystem of a forensic evidence item, filtering by severity, path, or name.
get_forensic_alarmsDarktrace / HYBRID NETWORKRetrieves alarms from an investigation or evidence item with severity and MITRE techniques.
get_forensic_artifactsDarktrace / HYBRID NETWORKRetrieves detection artifacts (files, hashes, processes, users, IPs, domains) from an investigation.
get_forensic_detectionsDarktrace / HYBRID NETWORKRetrieves XDR/EDR detections with MITRE ATT&CK mappings.
get_forensic_indicatorsDarktrace / HYBRID NETWORKRetrieves indicators of compromise (IOCs) from an investigation.
get_forensic_vulnerabilitiesDarktrace / HYBRID NETWORKRetrieves vulnerabilities (CVEs) with CVSS scoring and package info.
get_forensic_pipelinesDarktrace / HYBRID NETWORKRetrieves processing/acquisition pipelines with real-time status.
get_forensic_timelineDarktrace / HYBRID NETWORKRetrieves or facets timeline events from a forensic investigation.
get_forensic_search_syntaxDarktrace / HYBRID NETWORKReturns the Forensic Search query syntax reference (call before forensic timeline queries).

[related-resource]

Continue reading
About the author
Jamie Bali
Technical Author (AI) Developer
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ