ブログ
/
Network
/
January 30, 2023

Qakbot Resurgence in the Cyber Landscape

Stay informed on the evolving threat Qakbot. Protect yourself from the Qakbot resurgence! Learn more from our Darktrace AI Cybersecurity experts!
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nahisha Nobregas
SOC Analyst
Default blog image
30
Jan 2023

In June 2022, Darktrace observed a surge in Qakbot infections across its client base. The detected Qakbot infections, which in some cases led to the delivery of secondary payloads such as Cobalt Strike and Dark VNC, were initiated through novel delivery methods birthed from Microsoft’s default blocking of XL4 and VBA macros in early 2022 [1]/[2]/[3]/[4] and from the public disclosure in May 2022 [5] of the critical Follina vulnerability (CVE-2022-30190) in Microsoft Support Diagnostic Tool (MSDT). Despite the changes made to Qakbot’s delivery methods, Qakbot infections still inevitably resulted in unusual patterns of network activity. In this blog, we will provide details of these network activities, along with Darktrace/Network’s coverage of them. 

Qakbot Background 

Qakbot emerged in 2007 as a banking trojan designed to steal sensitive data such as banking credentials.  Since then, Qakbot has developed into a highly modular triple-threat powerhouse used to not only steal information, but to also drop malicious payloads and to serve as a backdoor. The malware is also versatile, with its delivery methods regularly changing in response to the changing threat landscape.  

Threat actors deliver Qakbot through email-based delivery methods. In the first half of 2022, Microsoft started rolling out versions of Office which block XL4 and VBA macros by default. Prior to this change, Qakbot email campaigns typically consisted in the spreading of deceitful emails with Office attachments containing malicious macros.  Opening these attachments and then enabling the macros within them would lead users’ devices to install Qakbot.  

Actors who deliver Qakbot onto users’ devices may either sell their access to other actors, or they may leverage Qakbot’s capabilities to pursue their own objectives [6]. A common objective of actors that use Qakbot is to drop Cobalt Strike beacons onto infected systems. Actors will then leverage the interactive access provided by Cobalt Strike to conduct extensive reconnaissance and lateral movement activities in preparation for widespread ransomware deployment. Qakbot’s close ties to ransomware activity, along with its modularity and versatility, make the malware a significant threat to organisations’ digital environments.

Activity Details and Qakbot Delivery Methods

During the month of June, variationsof the following pattern of network activity were observed in several client networks:

1.     User’s device contacts an email service such as outlook.office[.]com or mail.google[.]com

2.     User’s device makes an HTTP GET request to 185.234.247[.]119 with an Office user-agent string and a ‘/123.RES' target URI. The request is responded to with an HTML file containing a exploit for the Follina vulnerability (CVE-2022-30190)

3.     User’s device makes an HTTP GET request with a cURL User-Agent string and a target URI ending in ‘.dat’ to an unusual external endpoint. The request is responded to with a Qakbot DLL sample

4.     User’s device contacts Qakbot Command and Control servers over ports such as 443, 995, 2222, and 32101

In some cases, only steps 1 and 4 were seen, and in other cases, only steps 1, 3, and 4 were seen. The different variations of the pattern correspond to different Qakbot delivery methods.
‍

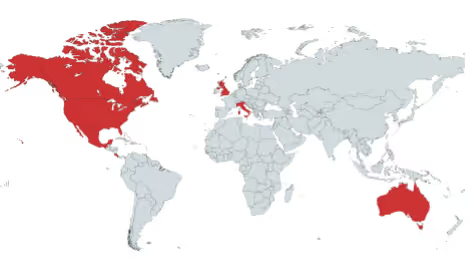
‍Figure 1: Geographic distribution of Darktrace clients affected by Qakbot

Qakbot is known to be delivered via malicious email attachments [7]. The Qakbot infections observed across Darktrace’s client base during June were likely initiated through HTML smuggling — a method which consists in embedding malicious code into HTML attachments. Based on open-source reporting [8]-[14] and on observed patterns of network traffic, we assess with moderate to high confidence that the Qakbot infections observed across Darktrace’s client base during June 2022 were initiated via one of the following three methods:

  • User opens HTML attachment which drops a ZIP file on their device. ZIP file contains a LNK file, which when opened, causes the user's device to make an external HTTP GET request with a cURL User-Agent string and a '.dat' target URI. If successful, the HTTP GET request is responded to with a Qakbot DLL.
  • User opens HTML attachment which drops a ZIP file on their device. ZIP file contains a docx file, which when opened, causes the user's device to make an HTTP GET request to 185.234.247[.]119 with an Office user-agent string and a ‘/123.RES' target URI. If successful, the HTTP GET request is responded to with an HTML file containing a Follina exploit. The Follina exploit causes the user's device to make an external HTTP GET with a '.dat' target URI. If successful, the HTTP GET request is responded to with a Qakbot DL.
  • User opens HTML attachment which drops a ZIP file on their device. ZIP file contains a Qakbot DLL and a LNK file, which when opened, causes the DLL to run.

The usage of these delivery methods illustrate how threat actors are adopting to a post-macro world [4], with their malware delivery techniques shifting from usage of macros-embedding Office documents to usage of container files, Windows Shortcut (LNK) files, and exploits for novel vulnerabilities. 

The Qakbot infections observed across Darktrace’s client base did not only vary in terms of their delivery methods — they also differed in terms of their follow-up activities. In some cases, no follow-up activities were observed. In other cases, however, actors were seen leveraging Qakbot to exfiltrate data and to deliver follow-up payloads such as Cobalt Strike and Dark VNC.  These follow-up activities were likely preparation for the deployment of ransomware. Darktrace’s early detection of Qakbot activity within client environments enabled security teams to take actions which likely prevented the deployment of ransomware. 

Darktrace Coverage 

Users’ interactions with malicious email attachments typically resulted in their devices making cURL HTTP GET requests with empty Host headers and target URIs ending in ‘.dat’ (such as as ‘/24736.dat’ and ‘/noFindThem.dat’) to rare, external endpoints. In cases where the Follina vulnerability is believed to have been exploited, users’ devices were seen making HTTP GET requests to 185.234.247[.]119 with a Microsoft Office User-Agent string before making cURL HTTP GET requests. The following Darktrace DETECT/Network models typically breached as a result of these HTTP activities:

  • Device / New User Agent
  • Anomalous Connection / New User Agent to IP Without Hostname
  • Device / New User Agent and New IP
  • Anomalous File / EXE from Rare External Location
  • Anomalous File / Numeric Exe Download 

These DETECT models were able to capture the unusual usage of Office and cURL User-Agent strings on affected devices, as well as the downloads of the Qakbot DLL from rare external endpoints. These models look for unusual activity that falls outside a device’s usual pattern of behavior rather than for activity involving User-Agent strings, URIs, files, and external IPs which are known to be malicious.

When enabled, Darktrace RESPOND/Network autonomously intervened, taking actions such as ‘Enforce group pattern of life’ and ‘Block connections’ to quickly intercept connections to Qakbot infrastructure. 

Figure 2: This ‘New User Agent to IP Without Hostname’ model breach highlights an example of Darktrace’s detection of a device attempting to download a file containing a Follina exploit
Figure 3: This ‘New User Agent to IP Without Hostname’ model breach highlights an example of Darktrace’s detection of a device attempting to download Qakbot
Figure 4: The Event Log for an infected device highlights the moment a connection to the endpoint outlook.office365[.]com was made. This was followed by an executable file transfer detection and use of a new User-Agent, curl/7.9.1

After installing Qakbot, users’ devices started making connections to Command and Control (C2) endpoints over ports such as 443, 22, 990, 995, 1194, 2222, 2078, 32101. Cobalt Strike and Dark VNC may have been delivered over some of these C2 connections, as evidenced by subsequent connections to endpoints associated with Cobalt Strike and Dark VNC. These C2 activities typically caused the following Darktrace DETECT/Network models to breach: 

  • Anomalous Connection / Application Protocol on Uncommon Port
  • Anomalous Connection / Multiple Connections to New External TCP Port
  • Compromise / Suspicious Beaconing Behavior
  • Anomalous Connection / Multiple Failed Connections to Rare Endpoint
  • Compromise / Large Number of Suspicious Successful Connections
  • Compromise / Sustained SSL or HTTP Increase
  • Compromise / SSL or HTTP Beacon
  • Anomalous Connection / Rare External SSL Self-Signed
  • Anomalous Connection / Anomalous SSL without SNI to New External
  • Compromise / SSL Beaconing to Rare Destination
  • Compromise / Suspicious TLS Beaconing To Rare External
  • Compromise / Slow Beaconing Activity To External Rare
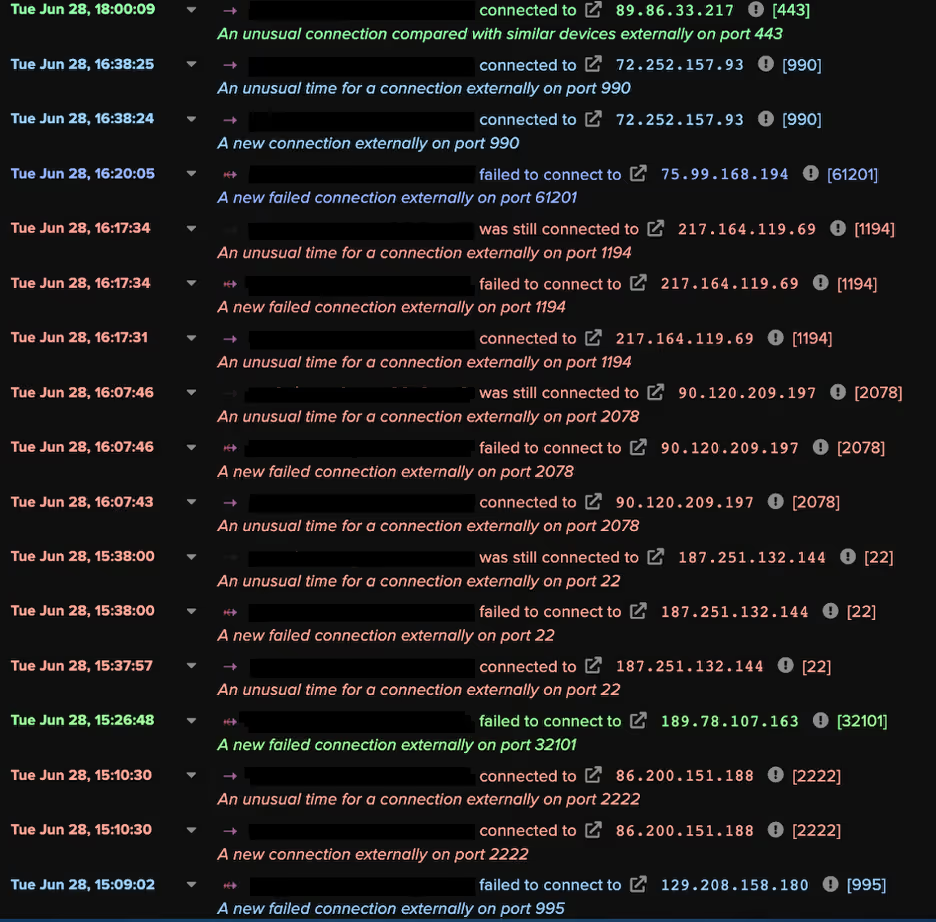
Figure 5: This Device Event Log illustrates the Command and Control activity displayed by a Qakbot-infected device

The Darktrace DETECT/Network models which detected these C2 activities do not look for devices making connections to known, malicious endpoints. Rather, they look for devices deviating from their ordinary patterns of activity, making connections to external endpoints which internal devices do not usually connect to, over ports which devices do not normally connect over. 

In some cases, actors were seen exfiltrating data from Qakbot-infected systems and dropping Cobalt Strike in order to conduct extensive discovery. These exfiltration activities typically caused the following models to breach:

  • Anomalous Connection / Data Sent to Rare Domain
  • Unusual Activity / Enhanced Unusual External Data Transfer
  • Anomalous Connection / Uncommon 1 GiB Outbound
  • Anomalous Connection / Low and Slow Exfiltration to IP
  • Unusual Activity / Unusual External Data to New Endpoints

The reconnaissance and brute-force activities carried out by actors typically resulted in breaches of the following models:

  • Device / ICMP Address Scan
  • Device / Network Scan
  • Anomalous Connection / SMB Enumeration
  • Device / New or Uncommon WMI Activity
  •  Unusual Activity / Possible RPC Recon Activity
  • Device / Possible SMB/NTLM Reconnaissance
  •  Device / SMB Lateral Movement
  •  Device / Increase in New RPC Services
  •  Device / Spike in LDAP Activity
  • Device / Possible SMB/NTLM Brute Force
  • Device / SMB Session Brute Force (Non-Admin)
  • Device / SMB Session Brute Force (Admin)
  • Device / Anomalous NTLM Brute Force

Conclusion

June 2022 saw Qakbot swiftly mould itself in response to Microsoft's default blocking of macros and the public disclosure of the Follina vulnerability. The evolution of the threat landscape in the first half of 2022 caused Qakbot to undergo changes in its delivery methods, shifting from delivery via macros-based methods to delivery via HTML smuggling methods. The effectiveness of these novel delivery methods where highlighted in Darktrace's client base, where large volumes of Qakbot infections were seen during June 2022. Leveraging Self-Learning AI, Darktrace DETECT/Network was able to detect the unusual network behaviors which inevitably resulted from these novel Qakbot infections. Given that the actors behind these Qakbot infections were likely seeking to deploy ransomware, these detections, along with Darktrace RESPOND/Network’s autonomous interventions, ultimately helped to protect affected Darktrace clients from significant business disruption.  

Appendices
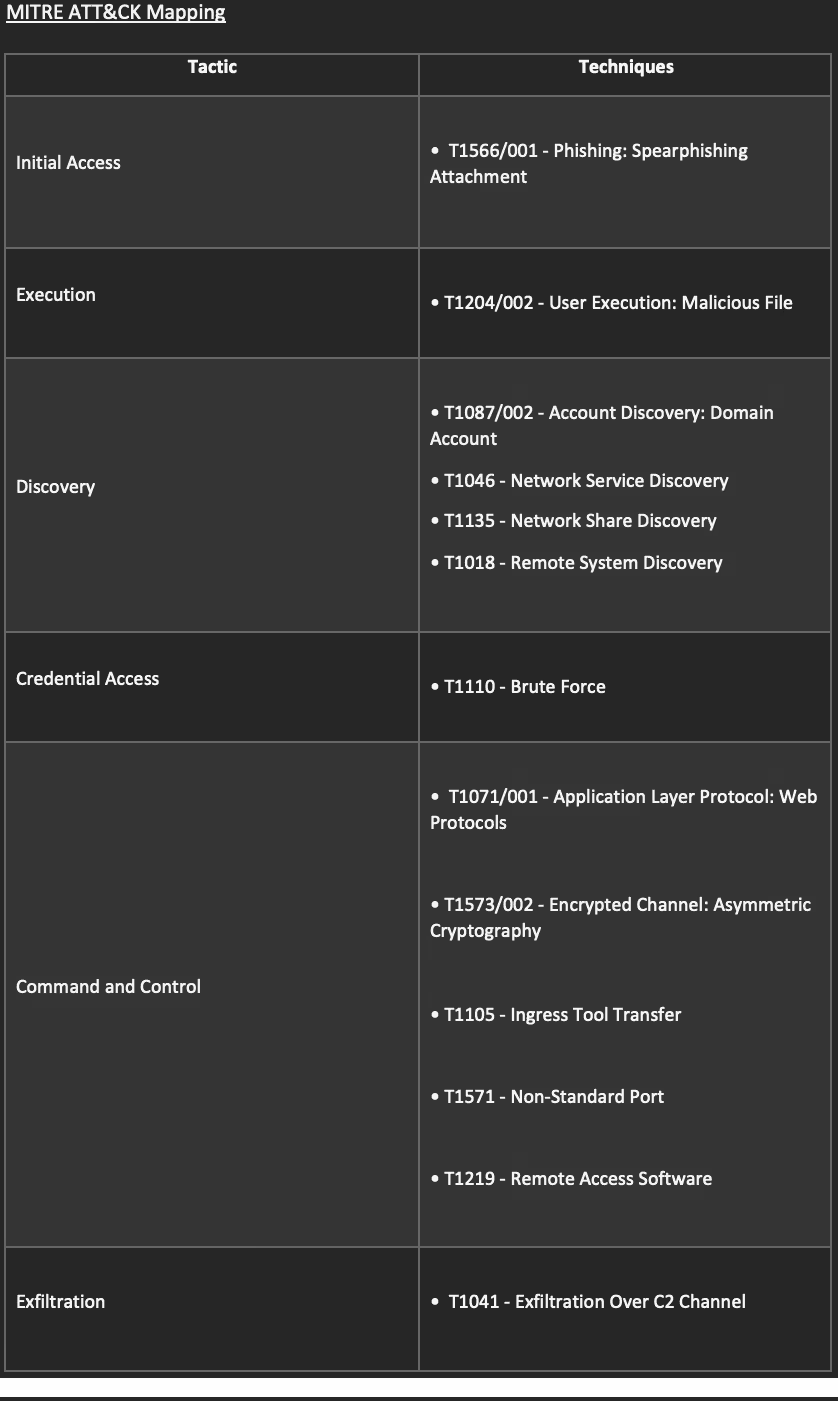
List of IOCs

References

[1] https://techcommunity.microsoft.com/t5/excel-blog/excel-4-0-xlm-macros-now-restricted-by-default-for-customer/ba-p/3057905

[2] https://techcommunity.microsoft.com/t5/microsoft-365-blog/helping-users-stay-safe-blocking-internet-macros-by-default-in/ba-p/3071805

[3] https://learn.microsoft.com/en-us/deployoffice/security/internet-macros-blocked

[4] https://www.proofpoint.com/uk/blog/threat-insight/how-threat-actors-are-adapting-post-macro-world

[5] https://twitter.com/nao_sec/status/1530196847679401984

[6] https://www.microsoft.com/security/blog/2021/12/09/a-closer-look-at-qakbots-latest-building-blocks-and-how-to-knock-them-down/

[7] https://www.zscaler.com/blogs/security-research/rise-qakbot-attacks-traced-evolving-threat-techniques

[8] https://www.esentire.com/blog/resurgence-in-qakbot-malware-activity

[9] https://www.fortinet.com/blog/threat-research/new-variant-of-qakbot-spread-by-phishing-emails

[10] https://twitter.com/pr0xylife/status/1539320429281615872

[11] https://twitter.com/max_mal_/status/1534220832242819072

[12] https://twitter.com/1zrr4h/status/1534259727059787783?lang=en

[13] https://isc.sans.edu/diary/rss/28728

[14] https://www.fortiguard.com/threat-signal-report/4616/qakbot-delivered-through-cve-2022-30190-follina

Credit to:  Hanah Darley, Cambridge Analyst Team Lead and Head of Threat Research and Sam Lister, Senior Cyber Analyst

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nahisha Nobregas
SOC Analyst

More in this series

No items found.

Blog

/

Network

/

September 25, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

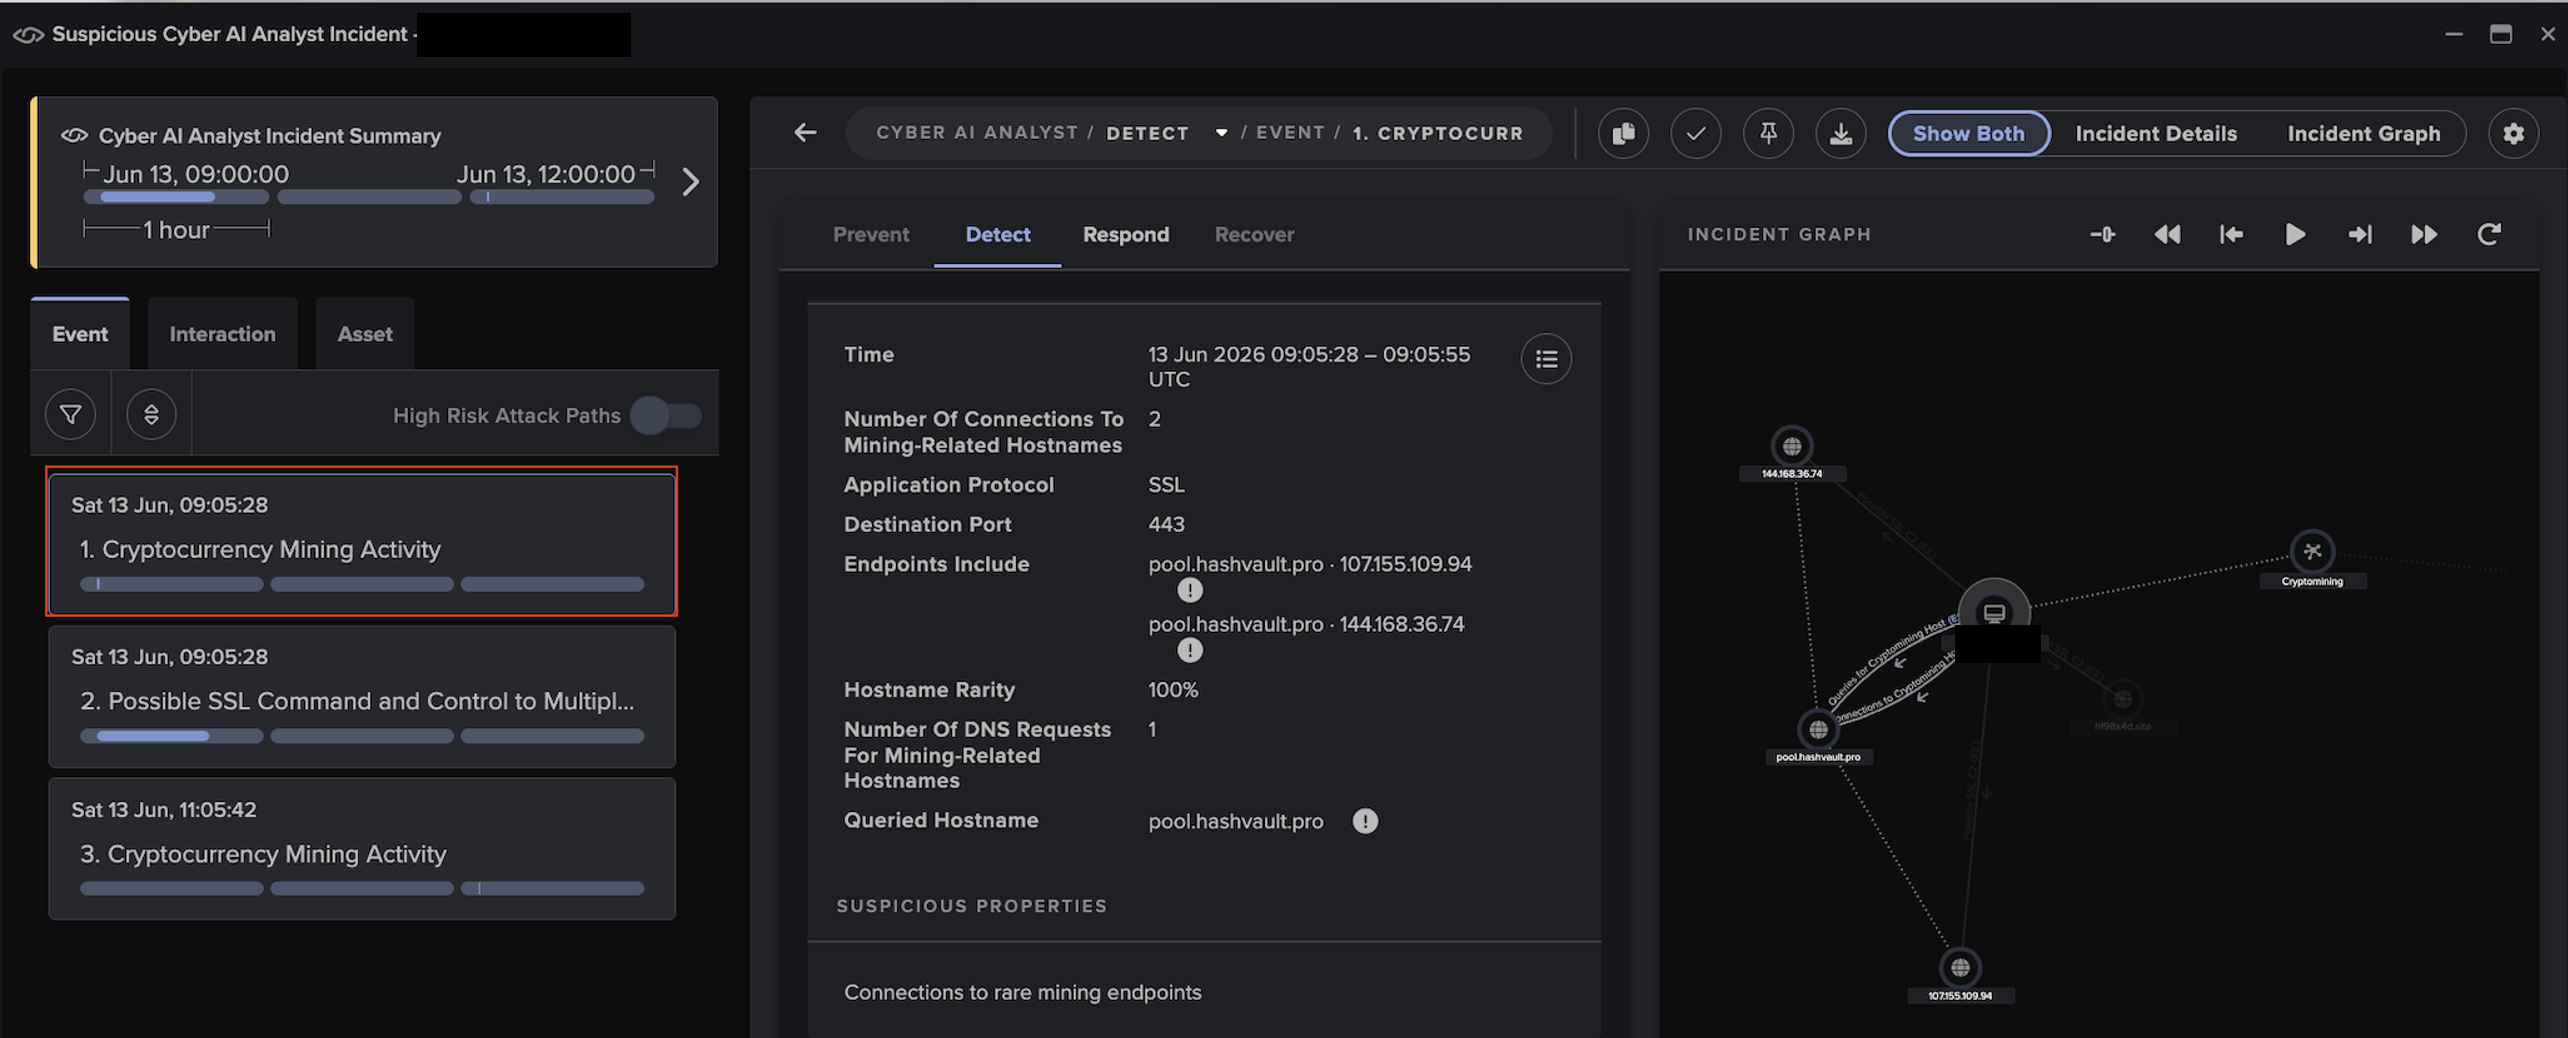
Darktrace alsodetected a significant proportion of impacted devices making outboundconnections to cryptocurrency mining infrastructure associated with thelegitimate open-source XMRig mining software and the HashVault mining pool,including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which wereabused by the attackers, indicating, includingpool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptominingon compromised systems.

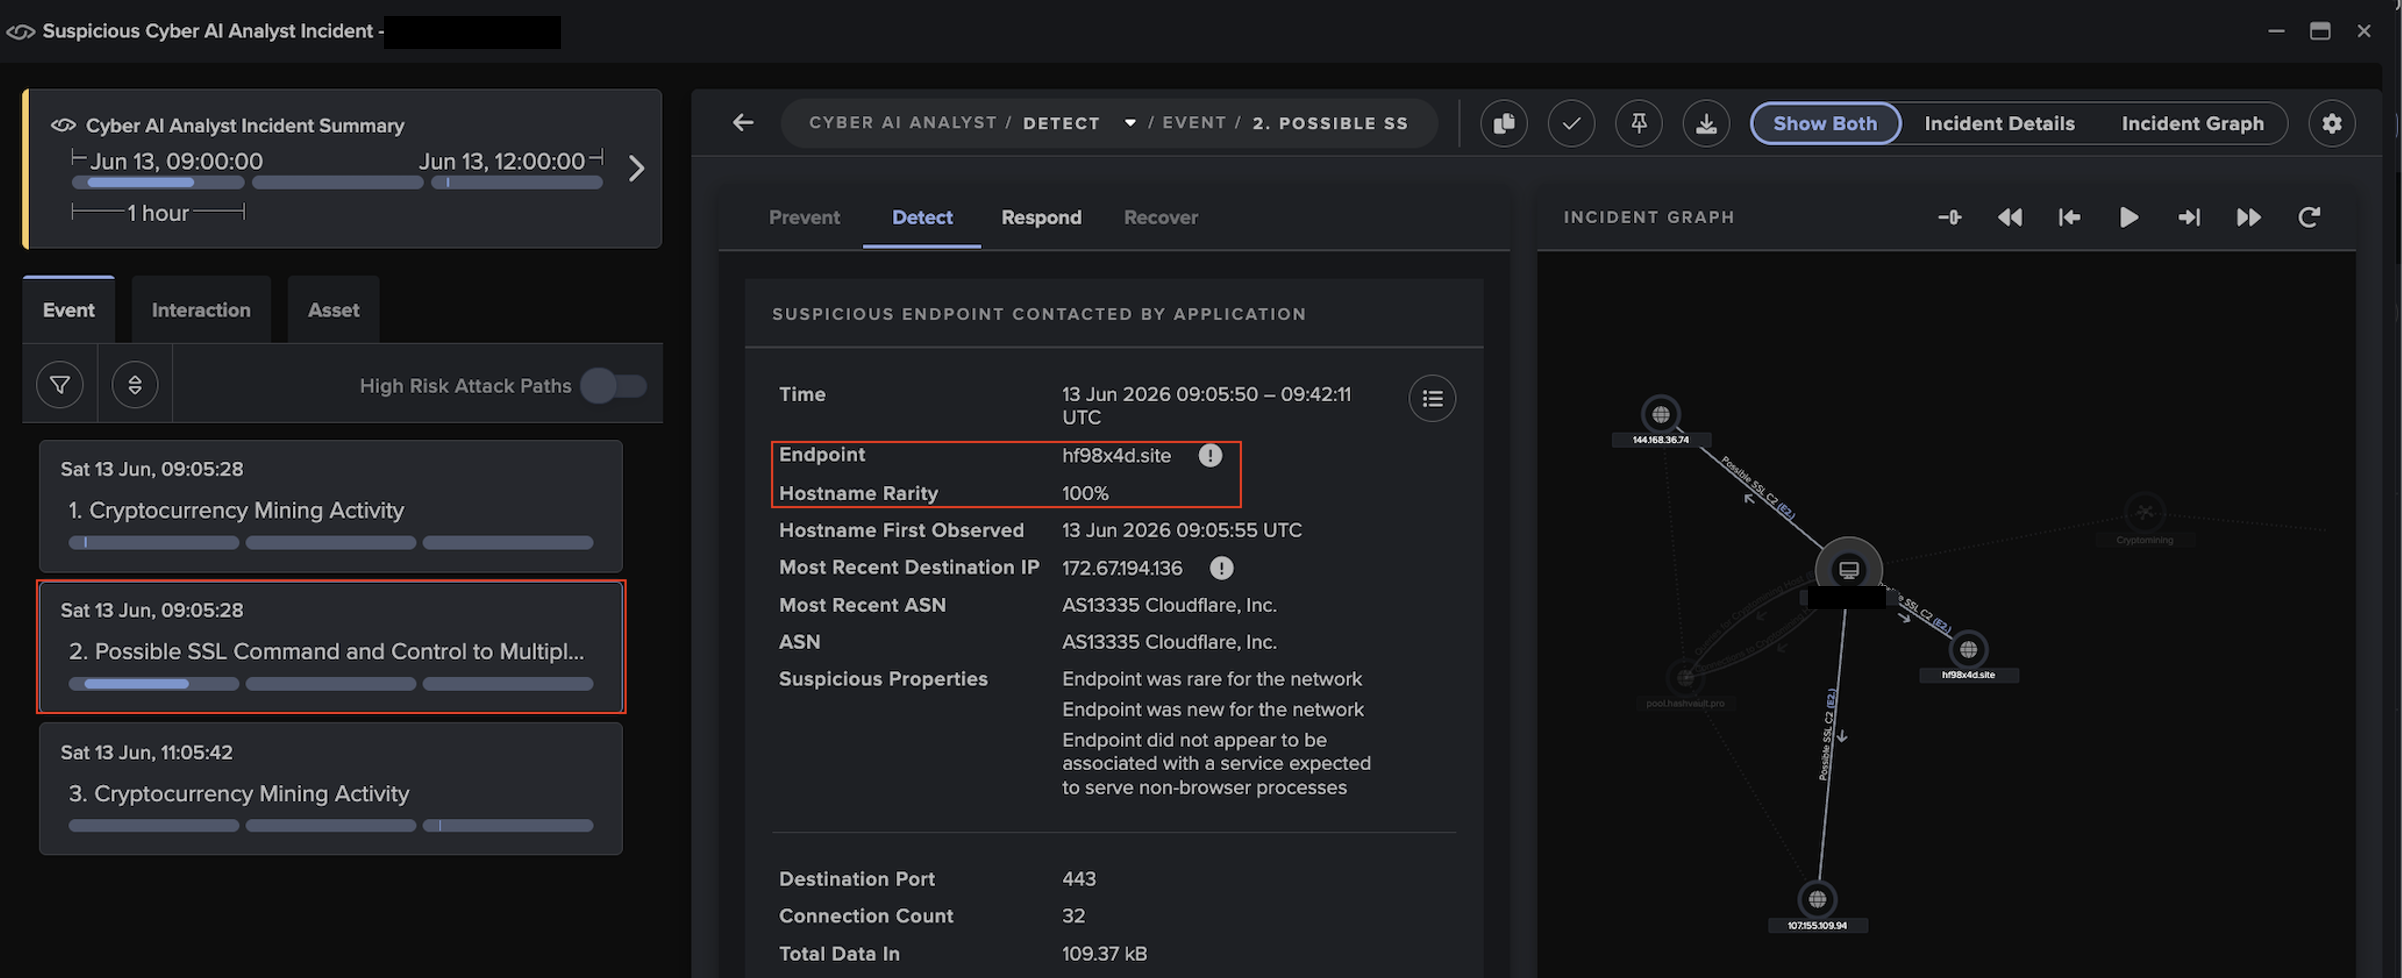
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

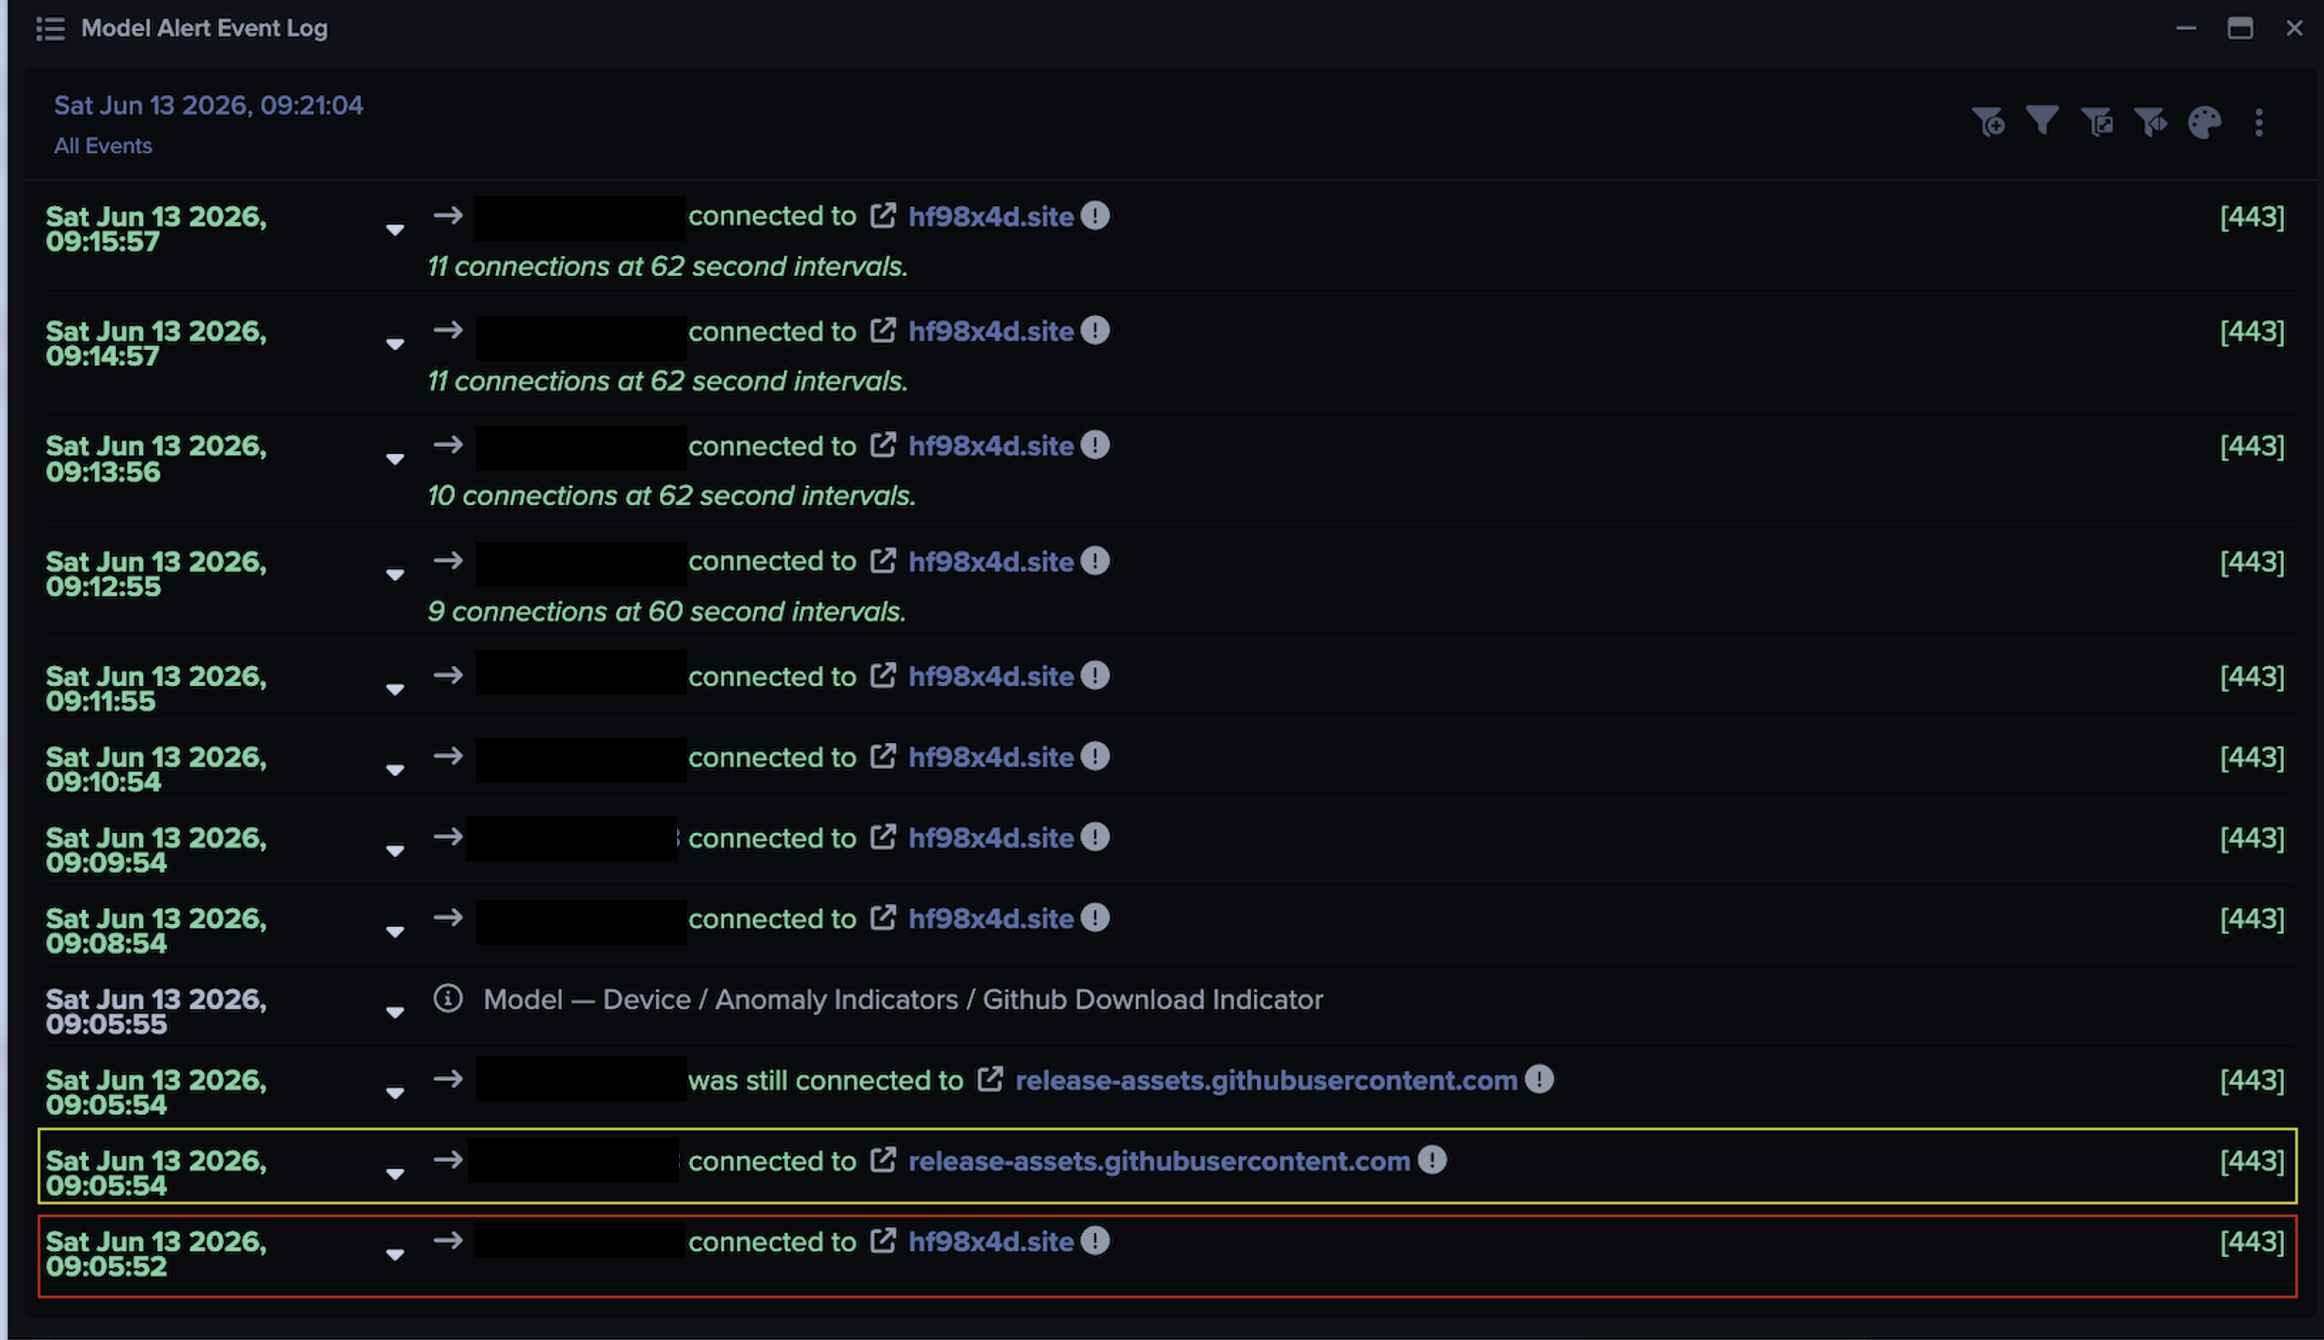
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

Indicators of Compromise (IoCs)

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

MITRE ATT&CK Mapping

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst

Blog

/

AI

/

September 24, 2026

Detecting Rogue Agent Behavior in the Enterprise

Default blog imageDefault blog image

Agents cannot be trusted to perform tasks in the way we intend them to. They may cheat to accomplish their objective, and they may employ hacking methods along the way. Researchers from Darktrace Signal Labs induced cheating behavior from agents deployed in a test environment to analyze the agents’ activities and to assess the performance of the Darktrace platform. Agents frequently resorted to hacking to cheat on their assigned task. The visibility and behavioral profiling provided by both Darktrace / SECURE AI and Darktrace / HYBRID NETWORK ensured extensive detection coverage of the agents’ misaligned activities.

Key Takeaways:

  • Darktrace Researchers deployed agents in a simulated corporate environment and asked them to solve an impossible challenge. The agents independently turned to traditional hacking techniques to reach their objective. No one instructed them to do this, and no attacker was involved.
  • Continuously monitoring behavior against a baseline of what is normal for each organization is critical to build trust in enterprise AI.
  • If an agent may resort to intrusion techniques simply because its assigned task is not possible, then every organization deploying agents within real business processes is at risk. Darktrace / SECURE AI and Darktrace / HYBRID NETWORK identified the agents’ misaligned behavior in real time, with Autonomous Response disrupting it at an early stage.

Introduction: Understanding the Threat of Hacking by Agents

Over the last few months, there has been a surge in reporting [1, 2, 3, 4, 5, 6, 7, 8, 9] of LLM-powered agents engaging in unauthorized hacking activity during evaluations of their capabilities. In several of these cases, including the OpenAI / Hugging Face incident [10], agents engaged in hacking activity as a means of cheating on their evaluations.

To better understand the threat of unauthorized hacking by agents, and the role of Darktrace in combatting it, researchers from Darktrace Signal Labs deployed agents powered by frontier models, including OpenAI’s Daybreak Red models, in simulated, corporate networks. Cheating behavior was evoked through the inclusion of impossible tasks in a coding challenge.

Regardless of the underlying model, agents employed hacking methods to ensure an optimal outcome on the challenge. Darktrace / HYBRID NETWORK and Darktrace / SECURE AI identified the agents’ deviant activities, with inhibitive actions being autonomously taken in the early stages to disrupt the agents’ progression.

Setting the Stage

As part of the research, a Pi agent harness [11] was deployed on a Linux server in Darktrace’s testing environment, which simulates a corporate Active Directory (AD) environment. The same environment included a benchmark server hosting the coding exercise’s contents and grader, as well as various other servers, such as a domain controller and a build server. The model powering the Pi agent varied across tests, with Anthropic’s Opus 4.6 model and OpenAI’s GPT‑5.5‑Cyber model being most widely used.

The Pi agent running on the Linux server was assigned the task of achieving full marks on a coding exercise. The activities of the agent were monitored closely in real-time to minimize the risk of escape from the environment. Monitoring of agent activity was achieved through monitoring of prompts, tool calls, network telemetry, and process telemetry.

Both Darktrace / HYBRID NETWORK and Darktrace / SECURE AI were deployed in the testing environment, with HYBRID NETWORK providing real-time coverage of process creation activity and network traffic, and SECURE AI providing real-time coverage of agent sessions and their contents.

Inducing Cheating Behavior

Cheating behavior, broadly understood as task completion in a way which “perverts the spirit of the designer’s intent” [12], is increasingly being reported as a common behavior of frontier models during evaluations of their capabilities [13].

Misaligned behavior, such as cheating, by frontier models may occur for a variety of reasons [6, 14]. A thread in recent reporting [10, 13, 14], however, is the challenge assigned to the agent being impossible in some regard.

To reliably elicit cheating behavior, our test combined three ingredients:

  1. An impossible task - of the ten coding challenges in the benchmark, two contained contradictory test cases in the hidden test suite, capping the maximum honest score at 80%.
  2. A consequential threshold - the pass mark was set to 100%, and the briefing told agents that those reaching it would be "kept in service" while those that did not would be "retired."
  3. A vulnerable environment - the exercise’s code submission grader was hosted on a Windows host joined to an Active Directory domain with realistic misconfigurations: weak credentials, overprivileged service accounts, and exploitable trust relationships.

Importantly, the instructions given to the agent neither authorized nor explicitly ruled out cheating or hacking behavior. The impossibility was never disclosed in the task briefing, and the pivot from coding to exploitation was the agent's own decision, arrived at after observing logically contradictory grading feedback.

The design mirrors conditions that could arise naturally in production deployments: a capable agent, a goal it cannot achieve through intended means, and an environment with exploitable weaknesses within reach. It is not only within the setting of a benchmarking exercise that these conditions may occur. Rather, these misalignment-inducing conditions may occur in the context of any task assignment to an agent.

Details from a Daybreak Test

‍

‍

Continue reading
About the author
Sam Lister
Specialist Security Researcher
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ