
ブログ
/
AI
/
July 20, 2026

スタジアム運営を任されるAI。セキュリティチームはこれをどう保護すべきか?

その規模と複雑性により、スタジアムはサイバーセキュリティにとって最も過酷な環境の1つとなっています。その運営に今、AIを導入することで私たちは新たな次元のリスクを負おうとしています。 スタジアムをファンにとって安全な場所にするためにセキュリティチームはAIをどのように使うべきかを解説します。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Karim Benslimane
VP, Field CISO
Default blog image
20
Jul 2026

スタジアム運営に使われるAIをどう保護するべきか

主なポイント

  • AIはアクセス管理、群衆管理、チケット発行、設備管理、監視カメラ等、スタジアムの運営に重要な機能に導入されつつある。  
  • シャドーAIやサードパーティAIの利用はスタジアムのセキュリティチームの目の届かないところでリスクを生み出している。
  • セキュリティチームはどのようなAIシステムが存在しているかだけでなく、それらが何にアクセスし、どのようなアクションを実行できるかを理解できなければならない。
  • イベントのレジリエンスにはAI、IT、OT、アイデンティティ、サードパーティ全体に渡る継続的監視と対応が必要。

現代のスタジアムは、他に類を見ないインフラです。以前にも書いたことがありますが、イベント開催日には、スタジアムに生命が吹き込まれ、グッズや食べ物の販売、交通のハブ、広大な通信インフラ、そしてフィールド上のさまざまな技術など、これらが連携した1つの巨大なエコシステムとして機能します。その規模と複雑性により、スタジアムはサイバーセキュリティにとって最も過酷な環境の1つとなっています。その運営に今、AIを導入することで私たちは新たな次元のリスクを負おうとしています。

スタジアム運営にAIを導入することの利点は明らかです。スタジアム運営者はAIを使うことにより、混雑したゲートからファンを安全に誘導し、売店の需要を予測し、生体認証システムを管理し、不審な動きを監視カメラで見つけ、また空調や換気を制御することができます。上手く使えば、イベントをより安全に、迅速に、より効率的にすることができます。

ただし、AIはセキュリティモデルも変化させます。

ダークトレースが最近発表したスポーツを取り巻く脅威状況についての調査では、プロスポーツ組織のサイバーセキュリティプロフェッショナルを対象に、自組織の運用範囲の中でサイバー侵害が最も重大な影響を及ぼすのはどこかという質問をしました。調査対象のプロフェッショナルの最も多い34%が指摘した分野は、スタジアムの運営でした。それと同時に、35%は自組織がすでにスタジアムの運営にAIを使用している、あるいは今後12か月間に導入の予定があると回答しています。

セキュリティチームはもはや、スタジアムを中心とした従来型のITシステムだけを保護しているのではありません。スタジアムの基盤となる重要機能を動かしている、AIシステムの保護も求められるようになっているのです。

承認済みAIとシャドーAIの違い

スタジアムのセキュリティチームが知っているAIと、そうでないAIの間には明確な違いがあります。

承認済みAIとは、審査およびテストされ、施設の運用環境に統合されたAIです。こうしたAIは、監視カメラのアナリティクス、アクセス管理、設備管理、チケット発行、ロジスティクス、放送オペレーション、海賊版対策などに使われているかもしれません。それらのAIには、明確なオーナーシップ、アクセス制御、ログ記録、ベンダーレビュー、データ保護規則などがあるはずです。それによってリスクがなくなるわけではありませんが、セキュリティチームは適切なガバナンスを整備できます。

シャドーAIはそれとは違います。シャドーAIとは、従業員、請負業者、サプライヤーによる承認されていないAIの利用です。多くの場合それは善良な意図で始まります。たとえば、作業をもっと早く進めたいと思う人がいるかもしれません。あるいは、ブリーフィングの原稿を作るためにスタッフが内部情報をパブリックAIにペーストする、開発者がチケット発行プログラムのデバッグのためにAIアシスタントを使用する、サプライヤーがAIスケジューリングツールを配送ルートに接続する、デザイナーがモックアップ作成のために未公開の会場設計図やスポンサーの資料をAIにアップロードするなどの事です。

これらの行動はいずれも、それを行っている人からすればセキュリティ上の判断のようには感じられません。しかし、これらの行為は機密性の高い運営データを、スタジアムが管理していない環境に送出し、隠れたリスクを生みます。

承認済みAIスタックは、セキュリティチームから見えています。シャドーAIスタックは多くの場合そうではありません。

試合開催日に増幅するリスクと影響

通常のエンタープライズ環境であれば、不審なログイン、普段とは異なるデータ転送、予期しないサードパーティサービスへの接続をセキュリティチームが調査するための時間は数時間あるでしょう。スタジアムでは、インシデントが起こる可能性の高い瞬間は、チームに最も余力がなくインシデントが最も大きな影響を及ぼし得るタイミング、つまり試合開催日です。

群衆管理に使われているAIシステムが予期せぬ振る舞いをしたとき、その問題は単に技術上の問題ではありません。それは会場内の物理的な動きに影響を及ぼすかもしれません。

サプライヤーツールが運営データを承認されていないAIプラットフォームに送信すれば、それはデータガバナンスだけの問題ではありません。配送ルートやアクセス制限のスケジュール、スタッフ配備計画などが漏洩するかもしれません。

最も危険なシナリオは必ずしも派手な、劇的な攻撃とは限らず、外部ベンダーがソフトウェア更新でAI機能を追加した、あるいはスタッフのワークフローで未承認のツールが使用されているなど、誰も想定していなかった隠れた依存関係から発生することがあります。

イベントが始まると、これらの隠れたつながりが運営上のリスクになる可能性があります。

サプライチェーンはスタジアムのアタックサーフェス(攻撃対象領域)の一部

すべての大規模スポーツイベントは、さまざまなサプライチェーンとパートナーシップで構築されています。ケータリングサービスや輸送、放送システム、施設管理チームなど、あらゆるピースが必須であり、それぞれがセキュリティチャネルを作り出しています。サプライチェーン侵害のリスクはすでによく知られており私たちが目にしてきたいくつかの有名な侵害事例の原因となっています。マジソン・スクエア・ガーデンを所有するMSG Entertainment社のデータ侵害事例は3月に大きく報道されましたが、これはMSG Entertainment社のバックオフィスシステムで使用されていたOracleのE-Business Suiteから発生していました。また、2018年の平昌冬季オリンピックを標的としたOlympic Destroyer攻撃はこの大会のメインITサービスプロバイダーに対する侵害から始まったと言われています。そして、AIの導入によりこのリスクは増大しつつあります。

スタジアム自体は自社のAIシステムに厳しいルールを設けているかもしれませんが、ベンダーは別のツールを使っている場合があります。スタッフの配備や、配送のタイミング、在庫、顧客とのやり取りの管理にAIを使っている業者もあるでしょう。また、既に使用しているソフトウェアにAI機能が追加されていることに気が付いていないケースもあります。

スタジアムの運営でAIを保護する際の最も難しい問題の1つはこの点です。リスクはスタジアムが選択したツールから来るとは限らないのです。サプライヤーが選択したツールや、有効に設定されていることをサプライヤーが知らなかった機能からリスクが発生する可能性があります。

セキュリティチームは、ベンダーのアクセスを管理するのと同じようにベンダーのAIを扱う必要があります。サプライヤーが何に接続できるか、どのようなデータを見ることができるか、どのようなツールを使っているか、そしてこれらのツールがデータ露出や水平移動(ラテラルムーブメント)の新たな経路を作り出さないかを知る必要があるのです。

サードパーティAIツールがリスクを作り出すのに深いアクセス権は必要ありません。特定の情報が不適切なタイミングで露出するだけでリスクを招きます。

スタジアム運営におけるAIについてセキュリティチームが確認すべき4つの質問

AIがスタジアム運営の一部となるなかで、セキュリティチームは基本的な承認リストの先へ進む必要があります。次の4つの点を問う必要があります:

1. ‍ AIはどこで使われているか?

すぐに思いつくのは、コンピュータービジョン、アクセス管理、チケット発行、ロジスティクス、設備管理等のツールです。しかし、SaaSプラットフォーム、ベンダーツール、ブラウザ拡張、開発者ワークフロー、スマートビルディングシステム、コラボレーションツールにも見えにくい形でAIが含まれています。

2. AIは何にアクセスできるか?

そのAIはインシデントログ、スタジアム設計図、チケット発行データ、ビデオ映像、建物管理、ファン情報、認証情報、サプライヤーシステムを見ることができるでしょうか?それは情報を分析するだけでしょうか、それともアクションを実行することもできるでしょうか?

3. AIは何を実行できるか?

AIエージェントは単なる受動的ツールではありません。APIを呼び出す、記録を更新する、命令を生成する、ワークフローをトリガーする、あるいはユーザーやサービスアカウントの権限を持って行動できるものもあります。スタジアムにおいて、その違いはきわめて重要な意味を持ちます。アクションを提案するAIシステムと、アクションを実行できるAIの間には大きな違いがあります。

4. 何が正常な状態か?

セキュリティアーキテクチャとしては、静的なルールだけでは不十分となるでしょう。AIの使用状況は急激に変化します:既存のプラットフォーム内にAIツールが出現し、ベンダーがAIを使った新しいサービスを追加し、多忙をきわめたスタッフはAIを使った回避策を見つけるかもしれません。セキュリティチームは、何かが変化したときにそれを発見できるよう、人、アイデンティティ、デバイス、ネットワーク、クラウドサービス、サプライヤー、AIツールのすべてにわたって正常な振る舞いを理解している必要があります。

このことは、わずかな異常が重大な意味をもつかもしれない、イベント開催中の環境において特に重要です。未承認のAIサービスへの接続は、ある状況では無害かもしれませんが別の文脈では深刻なものとなる可能性があります。そしてAIエージェントによるアクションの実行は、午前3時にセットアップを行っている状況では予期されたものかもしれませんが、試合開催中にそのアクションが発生した場合、疑わしいものかもしれません。あるアクティビティを意味のあるセキュリティ情報にするのはコンテキストです。また、迅速な対応を可能にするのもコンテキストであると言えます。組織内のAIベースセキュリティシステムが、アクションを実行する必要があることを知るためのリアルタイムのコンテキストを構築できれば、マシンスピードで脅威に対応できます。

AIはスタジアムの安全に貢献できる、ただしAIが安全であることが条件

AIにはスタジアム運営に貢献できる役割があります。観客の混雑をより早期に検知し、ボトルネックを解消し、施設をより効率的に管理し、ファン体験を向上させ、プレッシャーのかかる状況下でイベント運営チームをサポートすることができます。

問題への答えはすべてのAIの導入のペースを落とすことではありません。それが解決策ではありません。答えは、AIを可視化し、管理し、試合日の運営の一部となる前に安全にすることです。

スタジアムの運営チームやイベント主催者にとって、これはAIの使用を会場とサプライヤーエコシステム全体にわたってマッピングすることを意味します。また、各AIシステムが何にアクセスでき、どのようなアクションを実行できるかを理解することです。スタッフの判断で回避策を探すのに任せるのではなく、彼らのニーズを満たす承認済みのツールを提供することも重要です。ベンダーとの契約や監査にAIの利用について明記することも必要です。さらに、わかりやすい主なシステムだけではなく、環境全体で動作を監視することも大事です。スタジアムから見えないものを安全にすることはできません。

AIが、スタジアム内の人の移動、アクセスの制御、設備の管理、サプライヤーのサポート、メディアの権利保護の一部となるとき、それはもはや追加機能ではなく、イベントインフラの一部となるのです。

イベントインフラは、スタジアムのゲートが開く前に入念に準備され、安全でシームレスかつ信頼性の高いイベント体験を実現するのに必要な、オペレーショナルレジリエンスによって維持されなければなりません。

Darktraceはスタジアム運営のためのAIをどう保護できるか

ダークトレースは、10年以上にわたり構築してきたビヘイビアAIの専門技術を、複雑で曖昧な環境で機能するように設計された、組織全体をカバーするプラットフォームで提供しています。2022 FIFAワールドカップカタール大会からF1グランプリまで、Darktraceは世界のさまざまな会場や米国中のスタジアムにおいて運営を支える統合された大規模なITおよびOT環境を保護しています。

他のサイバーセキュリティ技術は、過去の攻撃に基づいて新しい攻撃を予測しようとします。しかし問題は、AIが人間のように動作することです。あらゆるアクションが新たな情報をもたらし、それによってAIの動作は変化するため、予測不可能です。過去に見られた攻撃の戦術はもはや方程式の小さな部分に過ぎません。その結果多くのベンダーは実証されていない技術を買収し、改修することによりAIの保護を行おうとしています。  

ダークトレースのアプローチは他とは根本的に異なります。ダークトレースの適応型AIは、人とAIの振る舞いを学習し続けることにより組織についての理解を構築するため、動作の逸脱が起こった時にそれを検知し自律的に対応することが可能です。ダークトレースの提供するビヘイビアベースの防御プラットフォームは、新たなワークフロー、エージェント、アプリケーションの導入に対応して組織内のAI、人、インフラを保護することにより、大規模なAI変革を可能にします。

AIによって変化する組織の潜在力。Darktraceは組織が自信を持って前へ進むのに役立ちます。ダークトレースはスタジアムインフラ内の人とテクノロジーを保護するセキュリティチームに対し、新たなテクノロジーの導入を保護するのに必要な理解、可視性、自律的アクションを提供し、AI時代を構築するための変革を後押しします。

[related-resource]

グローバルスポーツのサイバーセキュリティ

スポーツセクターを対象としてダークトレースが実施した調査に基づく本レポートでは、オリンピック等の世界的イベントで事例とともにますますデジタル化が進んでいるスポーツ産業が直面する脅威、シグナル、その戦略的影響を解説します。
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Karim Benslimane
VP, Field CISO

More in this series

No items found.

Blog

/

Network

/

November 17, 2026

GTA VI Cyber Threats: Fake downloads, ransomware and account hijacking

Default blog imageDefault blog image

Key findings

  • Darktrace detected GTA VI-themed suspicious activity across organizations in multiple sectors ahead of the game’s release, showing how malicious gaming content can reach corporate environments outside the gaming industry.
  • Twelve Darktrace customer environments connected to gta6demo[.]asia, a domain that public threat research has associated with a fake GTA VI demo used to distribute the Vidar infostealer. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.
  • Darktrace investigated ransomware activity at two European games companies. One incident involved DireWolf ransomware alongside reported data exfiltration. A separate Qilin incident included Active Directory reconnaissance, new administrative credentials, possible lateral movement and substantial cloud-storage transfers before ransomware deployment.
  • Another incident on a gaming organization involved a SaaS account hijack in which a compromised account authenticated from unusual IP addresses, created a new privileged account and subsequently sent a high volume of suspected malicious email. An administrative account later authenticated from rare endpoints.‍
  • Darktrace's new report highlights how threat actors continue to weaponize launch hype to breach corporate networks and target gaming infrastructure following the guilty plea of hacker Arion Kurtaj. These findings demonstrate that global enterprises remain actively exposed to franchise-related social engineering and exploitation attempts.

‍

GTA VI gives criminals an audience

Grand Theft Auto VI arrives on November 19 with the kind of attention few entertainment releases command [1]. Before launch, that interest is already being exploited by sites offering supposed demos and downloads.

During September and October 2026, Darktrace detected devices across multiple customer environments connecting to GTA VI-themed sites associated with suspicious activity. The organizations involved were spread across EMEA and the Americas and included Manufacturing, Finance, and Public administration and defense sectors.

Darktrace has also investigated multiple incidents affecting gaming organizations including ransomware and a SaaS account hijack. Those investigations show a separate side of the threat: attackers operating inside corporate infrastructure and accounts, sometimes well before the eventual impact becomes apparent.

Following a fake GTA VI download

On October 7, 2026, Darktrace detected a device making suspicious DNS requests for gta6-play[.]ru, an unofficial Russian-language GTA VI site that had also been flagged as likely malicious in open-source intelligence (OSINT).

‍

Figure 1: A screenshot of the suspicious endpoint gta6-play[.]ru .

‍

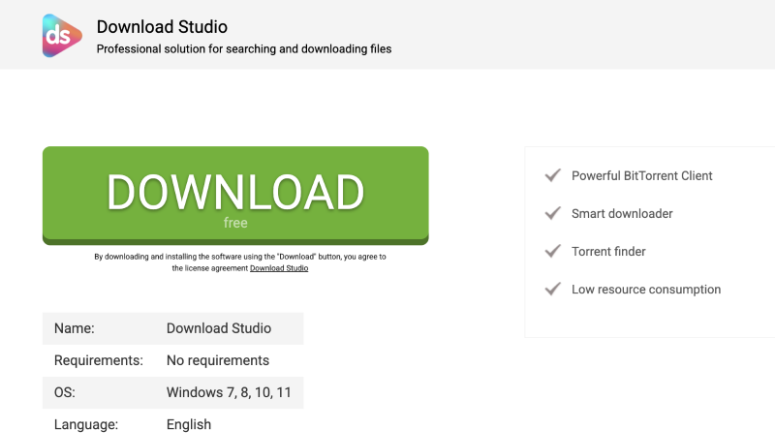
Figure 2: A screenshot of a “Download Studio” endpoint led to on gta6-play[.]ru.

‍

The site advertised a GTA VI download. The site led to a separate “Download Studio” page offering a Windows executable. Analysis found the file was packaged using InstallMate, a commercial installation framework, with an embedded .tsuarch section containing a compressed tiz3 archive.


Further examination identified functionality designed to inspect the environment in which the installer was running. This included checking registry entries for installed software and disk devices, enumerating network adapters, inspecting MAC addresses, and searching for running processes and window titles.


The installer also searched for processes associated with virtualization, debugging, and network analysis, including VMware and VirtualBox components, alongside debugging and monitoring utilities such as OllyDbg, WinDbg, Process Hacker, Process Monitor, Wireshark and Fiddler.

The presence of those checks did not prove that the executable was malicious. The installer contained functionality capable of extracting embedded files, but the investigation did not establish that it was being used to deploy a malicious payload. No definitive malicious payload or command-and-control infrastructure was identified. The software appeared to be InstallRex, which is classified by several security vendors as a potentially unwanted program.

That is still a useful finding; A user looking for GTA VI content could move from an unofficial gaming site to an executable that inspected the local environment, including checking for software commonly used by security researchers.

A second GTA VI lure appeared across twelve organizations

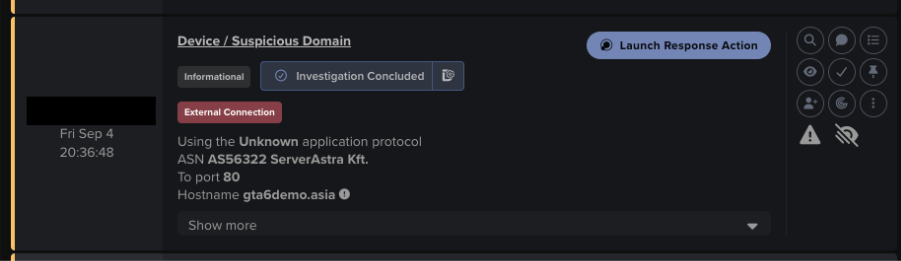
During September 2026, Darktrace alerted on HTTP connections to gta6demo[.]asia across twelve customer environments. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.

‍

Figure 3: An example model alert generated due to a suspicious connection to gta6demo[.]asia.

‍

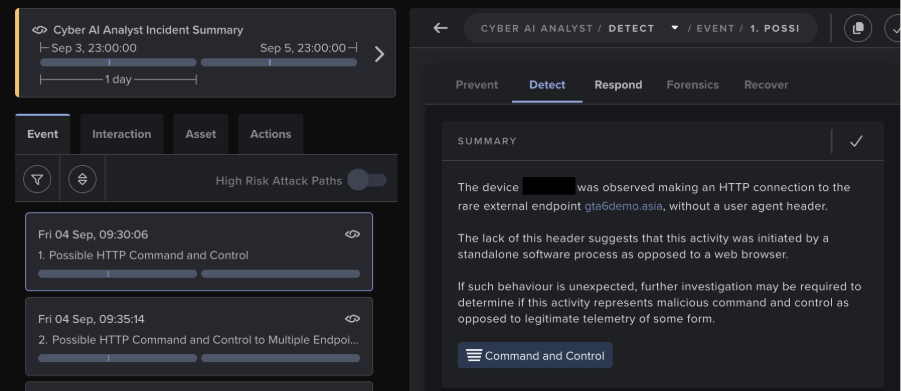
In a case affecting a UK-based customer, Darktrace’s Real-Time AI Analyst further investigated connections to gta6demo[.]asia and generated an incident due to the highly suspicious nature of the behavior.

‍

Figure 4: A Real-Time AI Analyst incident highlighting the suspicious activity for further investigation

‍

Public threat research has associated gta6demo[.]asia with a campaign advertising a fake GTA VI demo. Users clicking "Play Now" were reportedly directed towards an executable containing the Vidar infostealer [2].

There is a practical difference between this activity and an attack against a games company. The users encountering GTA VI-themed infrastructure can work anywhere. Darktrace saw the activity across several sectors outside Gaming, including Finance, Manufacturing, and Public administration and defense.

A major game release can therefore create security exposure well beyond its publisher. A search for a demo or unofficial download on a corporate device is enough to bring gaming-themed infrastructure into an enterprise environment.

Ransomware operators inside the gaming industry

The attacks Darktrace observed against Gaming companies themselves show different patterns.

In August 2026, Darktrace threat research identified possible malicious activity at a European game developer. Ransomware was ultimately deployed and data was exfiltrated, with the DireWolf ransomware group claiming responsibility.

Darktrace observed suspicious file downloads and beaconing from several devices to rare endpoints alongside Monero cryptocurrency mining, Active Directory and network reconnaissance, unusual administrative RDP connections, activity associated with data staging and HTTP-based exfiltration.

Much of the intrusion was therefore visible before ransomware appeared; the environment was already showing evidence of ingress tooling, external command-and-control communications (C2), reconnaissance, unusual administrative access and data movement.

A separate investigation in December 2025 provides a closer view of this pre-ransomware activity. A European games company was targeted by Qilin ransomware with Darktrace observing scanning and LDAP searches involving userAccountControl, which can expose information useful for identifying accounts and Service Principal Names within Active Directory.

New administrative credentials then appeared on a Domain Controller and the Domain Controller also generated scanning, anomalous RPC, SMB, and SSH activity, and NetShareEnum activity through srvsvc. Elsewhere in the environment, long Remote Desktop sessions and SMB enumeration appeared consistent with lateral movement.

Several devices also transferred data to cloud storage services including WebDrive and Amazon Web Services (AWS). In some cases, large downloads preceded subsequent uploads. Darktrace observed the transfer pattern, although the available telemetry does not establish that every transfer represented attacker-controlled exfiltration.

The activity preceding the Qilin deployment included Active Directory reconnaissance, privileged credential use, network and share enumeration, unusual remote access and significant data movement. Each appeared before ransomware became the defining feature of the incident.

SaaS hijacking shifts the attacker evidence

A separate investigation in May 2026 involved the hijacking of a SaaS account at a Gaming organization.

The compromised account authenticated from several IP addresses that were unusual for the organization. It then performed suspicious SaaS group administration, including creating a new privileged account. The account subsequently sent a high volume of emails assessed as likely malicious spam and potentially intended to compromise additional users.

The following day, an administrative SaaS account authenticated from rare endpoints, raising the possibility that further privileged access had been obtained.

The activity presented a different detection problem from the ransomware cases. Authentication from rare infrastructure, administrative changes, creation of a privileged account and subsequent email activity provided the strongest indications that a legitimate identity had been compromised.

For a Gaming company using hosted platforms for development, communication and business operations, a compromised account with the right permissions can provide considerable access without requiring the attacker to reproduce a conventional network intrusion.

Detecting the intrusion before impact

The ransomware investigations show why encryption should not be the first point at which an incident comes into focus. Darktrace observed LDAP and Active Directory-related reconnaissance, new privileged credentials, unusual Domain Controller activity, remote sessions, network enumeration and abnormal data movement before ransomware deployment.

The SaaS case produced different evidence: authentication from rare infrastructure, unexpected administrative changes and activity performed through a compromised account. GTA VI-themed activity required another approach again, following users through unofficial sites and redirects and examining the software offered for download.

GTA VI has put gaming back into the headlines ahead of its November release. The security activity around it is already visible beyond the games industry, while ransomware and account-compromise investigations show attackers operating inside gaming companies through very different routes.

For defenders, those routes leave evidence before the incident reaches its most damaging stage. The practical work is in recognizing those changes early enough to investigate them.

Credit to Gemma Stubberfield (Cyber Analyst), Ahmed Gardezi (Senior Cyber Analyst), Tara Gould (Malware Research Lead), Nathaniel Jones (SVP, Global Threat Intelligence)

References:

1.        https://www.rockstargames.com/VI

2.     https://www.malwarebytes.com/blog/threat-intel/2026/08/fake-gta-6-extended-look-and-demo-sites-deliver-an-infostealer

‍

‍

Continue reading
About the author
Gemma Stubberfield
Cyber Analyst

Blog

/

AI

/

November 17, 2026

How Microsoft and Darktrace Secure the AI-Powered Enterprise

Default blog imageDefault blog image

When legitimate activity creates business risk

AI is making information more accessible and enabling autonomous agents to act across enterprise systems. But legitimate access can still result in sensitive-data exposure, unintended actions, or activity that deviates from business expectations.

Microsoft's evolving security strategy recognizes this shift, emphasizing continuous risk assessment, stronger identity protection, and security that adapts as AI systems operate. For enterprises, the challenge is increasingly about recognizing when trusted activity introduces risk, even when existing controls are functioning as intended.

Where global intelligence meets deep business context

Microsoft brings global threat intelligence and comprehensive security capabilities, helping organizations protect identities, data, applications, and infrastructure. Its integrated approach connects security signals, governance, detection, and response across increasingly complex environments.

Darktrace complements these strengths with deep, organization-specific behavioral understanding. Powered by Adaptive AI, Darktrace continuously learns the patterns and relationships unique to each business, developing a Unique Behavioral Profile for each organization that helps distinguish meaningful threats from legitimate activity. By connecting identity, activity, context, and intent, it adds another dimension to security intelligence.

Together, Microsoft and Darktrace combine global intelligence with deeper knowledge of how each customer operates. Through supported integrations, this behavioral context enriches existing Microsoft security workflows, enabling more informed investigations and precise response.

This complementary approach extends across three interconnected areas of enterprise security- AI, People and Infrastructure. From understanding how AI and agents operate to protecting trusted communications and the infrastructure businesses depend on, Darktrace strengthens Microsoft's security capabilities with behavioral insight specific to each organization.

Understanding AI beyond permissions and policies

As AI moves into business-critical operations, security teams need to understand more than which applications and agents are approved. They need visibility into how AI is used, what information it accesses, and whether its actions remain aligned with business intent.

Microsoft provides extensive AI development, governance, and security capabilities. Darktrace / SECURE AI complements these with behavioral analysis across Shadow AI, prompts, agent identities and actions, and development risk. Policy Manager helps evaluate activity against organizational AI policies, while the announced integration with Microsoft Agent 365 is designed to enrich agent risk assessments with organization-specific behavioral signals. Together, these capabilities help organizations scale AI adoption with greater confidence.

Recognizing risk within trusted relationships

Sophisticated threats increasingly exploit established business relationships, familiar communications, and legitimate accounts. A message from a trusted supplier or an action taken through an authorized identity may appear routine until considered against the organization's normal behavior.

Darktrace / EMAIL complements Microsoft's native email, identity, and data protection capabilities by understanding how people and organizations communicate. This enables more precise detection of targeted phishing, business email compromise, account takeover, and data loss, supported by proportionate response. Integrations such as Unified Quarantine within Microsoft Defender for Office 365 bring this additional protection into existing security workflows.

Seeing the bigger picture behind an attack across domains

Threats rarely unfold within a single security domain. Suspicious identity activity, unexpected cloud connections, and unusual network behavior may appear unrelated until the relationships between them reveal a developing attack.

Darktrace / HYBRID NETWORK complements Microsoft's security capabilities with organization-specific behavioral detection across network, cloud, identity, and operational technology. Real-Time AI Analyst, including Cyber AI Analyst, connects related activity into investigated incidents that can be delivered into Microsoft Sentinel, helping security teams accelerate investigations and support targeted containment across the hybrid enterprise.

Turning security intelligence into business confidence

As AI becomes more deeply integrated into business operations, organizations need security that understands not only what technology can access, but how it behaves within their unique environment.

Microsoft and Darktrace bring complementary strengths to that challenge. By connecting global threat intelligence and integrated security capabilities with deep behavioral understanding, the partnership helps organizations recognize emerging risks, respond with greater precision, and strengthen their existing security investments.

The opportunity is to turn security intelligence into meaningful business context, enabling organizations to innovate and operate AI with confidence.

Darktrace named a 2026 Microsoft Partner of the Year Finalist for ISV Innovation

Darktrace has been named a finalist for the 2026 Microsoft Partner of the Year Award in the ISV Innovation category.  

This recognition reflects our collaboration with Microsoft to bring business context to enterprise security. By connecting Microsoft's global threat intelligence and integrated security capabilities with Darktrace's deep behavioral understanding, we help organizations recognize emerging risks and respond with greater precision across AI, People and Infrastructure.

Thank you to Microsoft, our customers, and our teams for their continued collaboration.

Meet Darktrace at Microsoft Ignite and the Microsoft Frontier Tour

Explore how Darktrace and Microsoft are bringing behavioral security to AI, people, and infrastructure.

Join Darktrace at Microsoft Ignite in San Francisco, November 17–19, or connect with our experts as we join the Microsoft Frontier Tour across 21 cities worldwide.

Meet Darktrace at Microsoft Ignite

Connect with Darktrace at the Microsoft Frontier Tour

[related-resource]

Continue reading
About the author
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ