ブログ
/
AI
/
September 17, 2026

The Problem of Re-defining Human Value in the Agentic Age

As agentic AI systems take on more decision-making, human value is shifting from execution to judgement. This blog explores the challenges of maintaining oversight, resisting AI-driven influence, and making effective decisions in an age of autonomous agents, while examining how behavioral security can help organizations govern AI with confidence.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Jason Lusted
AI Governance Advisor
Default blog image
17
Sep 2026

Newsfeeds are constantly informing us about the rapid escalation of agentic AI systems. These systems move far beyond simple machine-based computations, and  the focused, defined and bounded assistance that most AI systems started out as.

The next evolution of AI will harness the agentic properties of orchestration, automation, and heightened value-chains in IT, taking on the burden of workflow management, not just workflow delivery.

In nearly all of these instances, promises are made such as ‘this will free up human time’ or ‘this will allow people to focus on higher-order strategy’. However that message is delivered, one thing is clear: in ceding the orchestration and management of work to increasingly sophisticated AI agents and agentic systems, human value will be elevated to a particular and specific layer: the ability to judge its outputs.  As AI takes on more tasks, humans should be able to focus on a higher level of governance; making sure the decisions that AI offers us are ethical, responsible and worthwhile.  

But there are two major problems with that approach.

This blog discusses the problem of how Agentic systems are re-shaping how we review information, where we fit in, and when we make decisions.  It also discusses the problem of how the increased flow of confident, generated information affects the way we make judgement.  This blog considers how human judgement needs to adapt, and how a behavioral defense approach – using techniques pioneered by Darktrace – can help us do that.

The challenge of knowing where human judgement belongs

As we confer more automated decision-making to agentic systems, it might look increasingly less like ‘granting permissions’, and more like ‘surrendering authority’.  

The judgement layer for AI-generated work is not a fixed boundary. We have become used to the idea of a ‘human in the loop’ (HITL) and, historically, relationships between humans and IT systems were reasonably clear and bounded.  Computer and software systems were programmed to carry out certain tasks or automated functions, and humans could control the gates and decision points where actions were undertaken. Even across highly complex computational workflows, human interaction was a controllable node within the process; we were able to configure and regulate. But in the agentic age, where that human interaction sits, and what it can influence shifts every time AI systems are granted autonomy.  

This leads us to the first problem: if humans are moving themselves (or are being moved) into the ‘judgement’ part of the value chain, exactly where and when do we exercise that judgement?  

Humans are no longer the sole shepherds of computer-based or software-controlled outputs.  We are at times at least one step further (and slower) behind the new agentic shepherds.  We might also be blind to what they are doing.  Not only might we be removed and blind to the actions of our AI shepherds, but with the challenge of unknown, unapproved AI systems operating beyond our control, humans might not even know that our work is being shepherded by an AI at all.  Simply put, with the advent of greater levels of autonomy and orchestration, humans are at risk of not even knowing where to apply our newly-extended powers of strategic judgement.

Shadow AI – the use of unapproved AI systems or processes – is a growing threat to the role of effective governance and oversight. Shadow AI isn't just the AI you can't see. Its the AI you already know about being used in an unapproved way. The ability to generate effective oversight of the AI systems you use (or that are used on your behalf) will be increasingly important to ensure that human judgement in the AI value chain is effective, and deliberately placed.

The problem of what makes good judgement

The second problem lies in how flawed human judgement can be.  Humans are historically, notoriously, and, sometimes dangerously, unreliable when it comes to exercising judgement.  Humans are prone to the worst kinds of bias, the seduction of malign influence, and the sometimes-overwhelming urge to succeed. AI has long had a known flaw of operating with sycophancy, providing outputs that tend to agree with or flatter the human user.  But as AI grows ever more effective, there is a risk of both hyper-enablement (where humans increasingly and knowingly enable AI despite potential harm), as well as the greater risk of suggestion. Both of these aspects could skew the newly-elevated input of human judgement.

Imagine a highly competent AI system that has just orchestrated and managed a dizzying array of processes and workflows.  The AI is designed to present the human decision-maker with recommendations; based on analysis, comparison and other programmed factors.  This is where the human judgement layer is enabled.  But what if that judgement is summarily diffused by an AI-based recommendation that emulates the decision, provides plausible but unattractive alternatives, then suggests (or, worse, directs) the human end-user to take a particular course of action.

The risk here is that you are given a recommendation, tailored to your preferences (which the AI has learned, or which you have divulged), and which appears to make perfect sense.  It appears to be a well-weighted recommendation, with sound arguments that tap into our inherent biases or inclinations so that a specific decision-path is followed. With the growth of agentic systems specifically designed to match user profiles (from Cowork agents to ‘digital twin’ models), the likelihood of agentic influence could badly skew human judgement or, at the least, devalue the proposition that humans are taking a higher-layer of strategic control over AI-based decisions.

If AI convincingly recommends something that may be problematic, it can be difficult to discern both accurate data, and the context required to make the right judgement.

Given the two problems described above, the job of exercising valuable human judgement in the agentic age can draw down to these two questions:

  • When should humans intervene in the agentic process?  
  • How can we make the best possible judgement calls?

What humans contribute that AI cannot

For all the flaws that make human judgement unreliable, people have the edge over even the most sophisticated and powerful AI systems when it comes to issues such as ethics and social context.  An AI system can, with startling granularity, rank the value of adopting a new business proposal: offering predictive metrics on costs, returns, market value, time-to-deliver operations, conformance with legal registers, etc.  But it can’t tell if the business proposal is ethically sound, or if the business venture will potentially affect groups outside of the analyzed proposal. It can’t tell you if the CEO has a ‘bad feeling’ about this effort.  It can’t tell you if this is the right thing to do.  

The ability to add social context, balance complex interpersonal dynamics, understand nuance, and to go beyond what seems economically reasonable is where human judgement can add value.  

Human judgement is difficult to encapsulate in metrics. And the way we train our development may need to adapt too. Rather than building up a gradual, experiential knowledge base, we should think about training the skill of judgement itself; especially for an agentic age.

How behavioral security strengthens AI governance

If this all feels like a vicious circle (‘I need AI help to make good judgements’ / ‘AI can twist what I need to judge’) it needn’t be. The key to this is having a defense-in-depth approach, with tools that can actually help.

This is precisely where behavioral security becomes important. The complex and nuanced way that humans exercise judgement is often rooted in our ability to recognize behavior that doesn't look right. We may not always be able to articulate it immediately, but we can often identify when an action, recommendation, or outcome feels inconsistent with the context around it. As AI systems take on more responsibility across the decision chain, preserving that ability to recognize meaningful deviations becomes increasingly important.

Darktrace’s / SECURE AI is designed to do exactly that. It applies behavioral security to AI ecosystems, helping organizations understand how people, AI tools, identities, and agents interact across the business. By learning the patterns of normal AI usage and surfacing activity that deviates from those patterns, it provides security teams with the context needed to investigate risk, understand unusual behavior, and make informed governance decisions. Rather than relying solely on predefined rules or assumptions, this behavioral understanding helps organizations distinguish between expected AI activity and behavior that warrants closer scrutiny.

This matters because we are already in an era of information overload. If humans are expected to elevate their value through strategic judgement, the ability to do this without being overwhelmed by data (good or bad) will be critical.  

We need the ability to discern when we're being misled by AI, and whether our judgement calls are being made on the basis of accurate, contextual information. Darktrace / SECURE AI provides that additional layer of defensive security for activity we cannot easily see. Whether it is suspected Shadow AI or skewed recommendations, the net result is a protected organization, where users can more effectively use AI to make positive judgements.

For those where that judgement is a critical skill (both individuals, as well as those working in security teams), improving our metacognition - the ability to understand information in a broader context - will supercharge the value of human judgement. When those judgements are grounded in context rather than assumptions we have better information to make sound decisions.

Conclusion

Human judgement is a skill that is honed over time and experience.  Darktrace’s / SECURE AI employs the same principles, but at machine-speed. Rather than influencing or directing, Darktrace / SECURE AI offers AI-enabled assurance; providing human-based judgement with the right context to make a balanced decision.  

What we judge can be valued by the legitimacy of its outputs. For AI, those outputs are valued on the speed and accuracy of the information provided.  Increasingly for humans, the value of our outputs will be based on the validity of our judgement, and how we justify our decisions in ways that engineer confidence.  

Humans often know more than we can express, while AI is prone to expressing more than it truly understands. Humans can bridge the context AI often fails to appreciate. When that judgement is supported by relevant, impartial AI systems, this is the future space where good AI governance will be exercised.

‍

Discover Darktrace / SECURE AI.

[related-resource]

Secure Your AI Adoption

Practical guidance for securing LLM deployments, AI-integrated workflows, and agent-based systems, including controls to manage AI risk.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Jason Lusted
AI Governance Advisor

More in this series

No items found.

Blog

/

AI

/

October 5, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

October 5, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

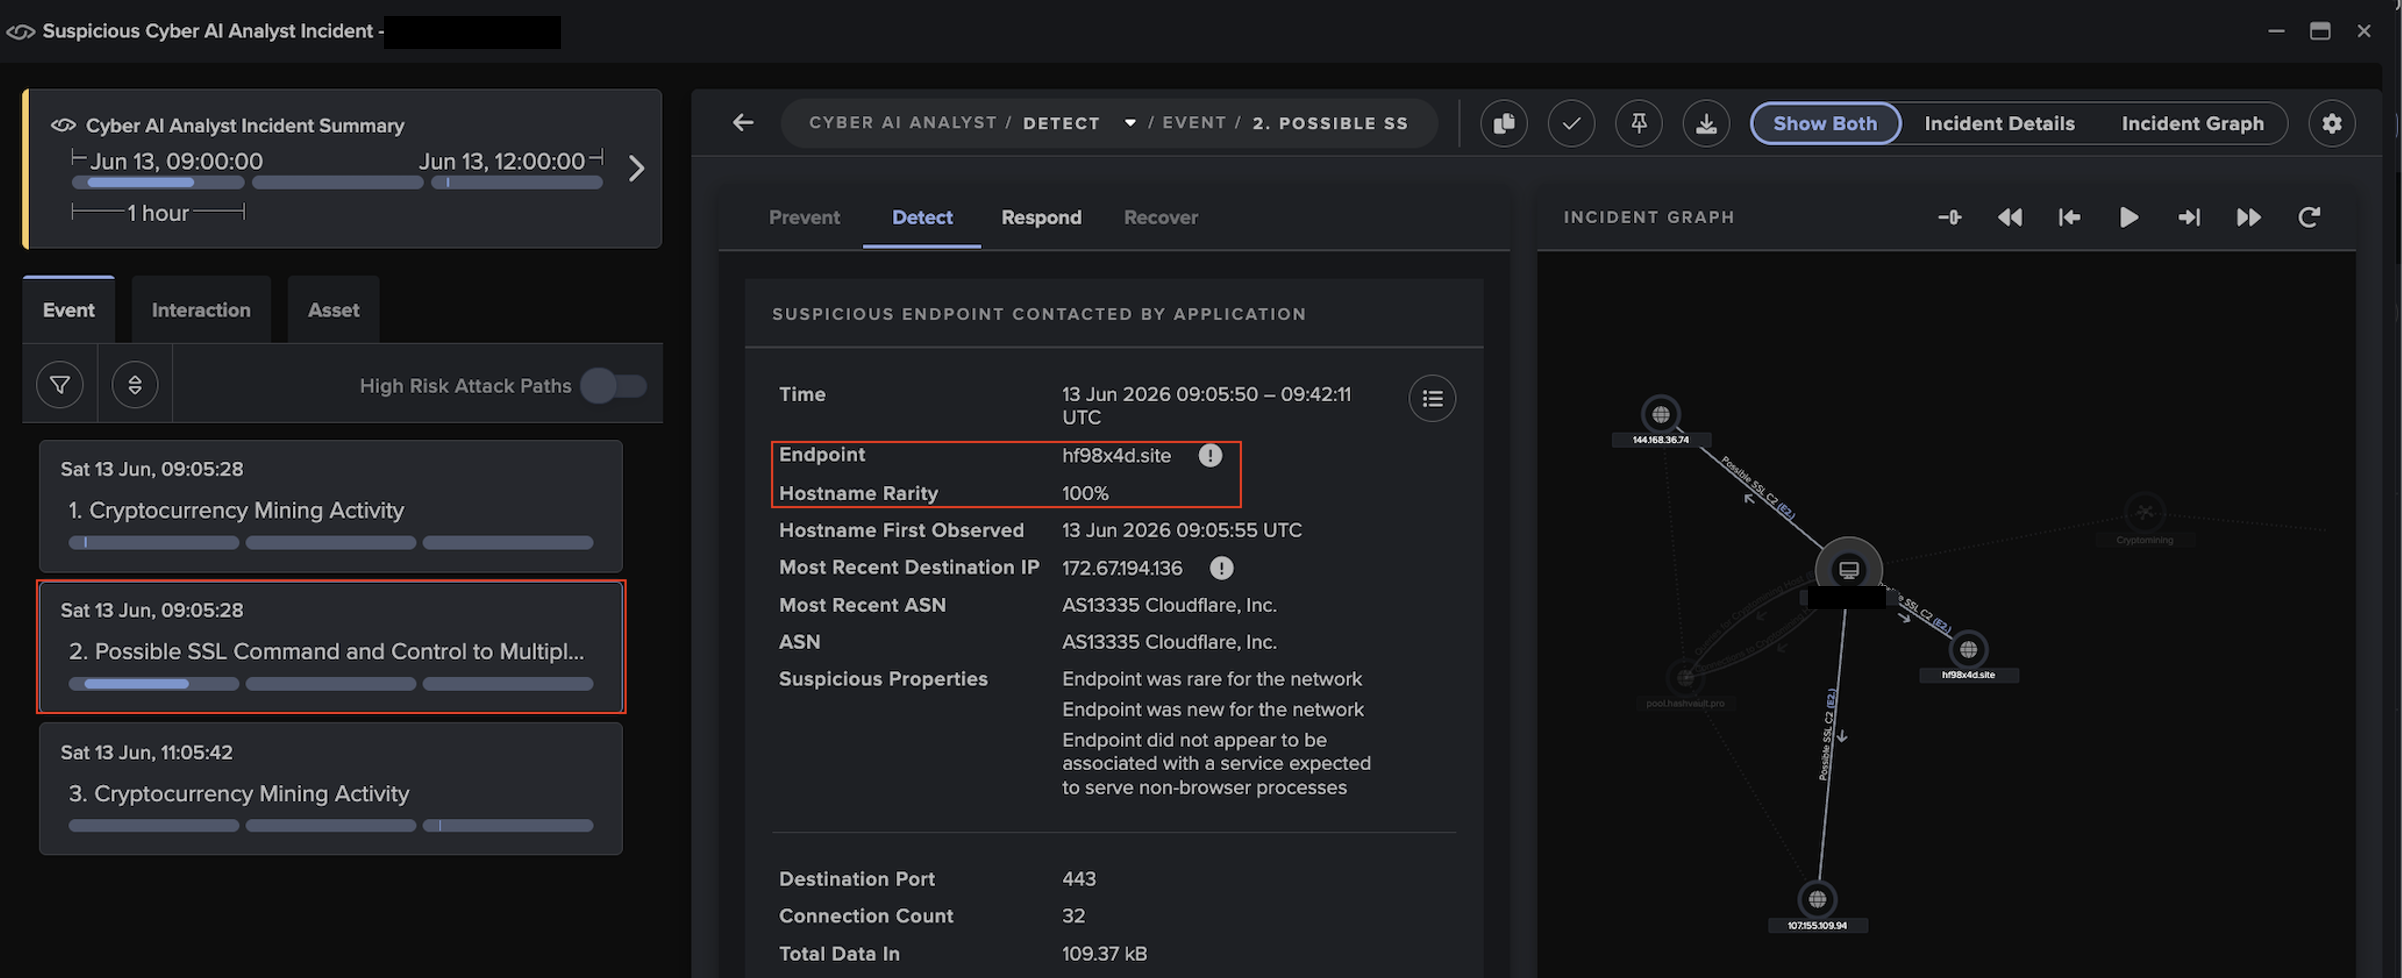
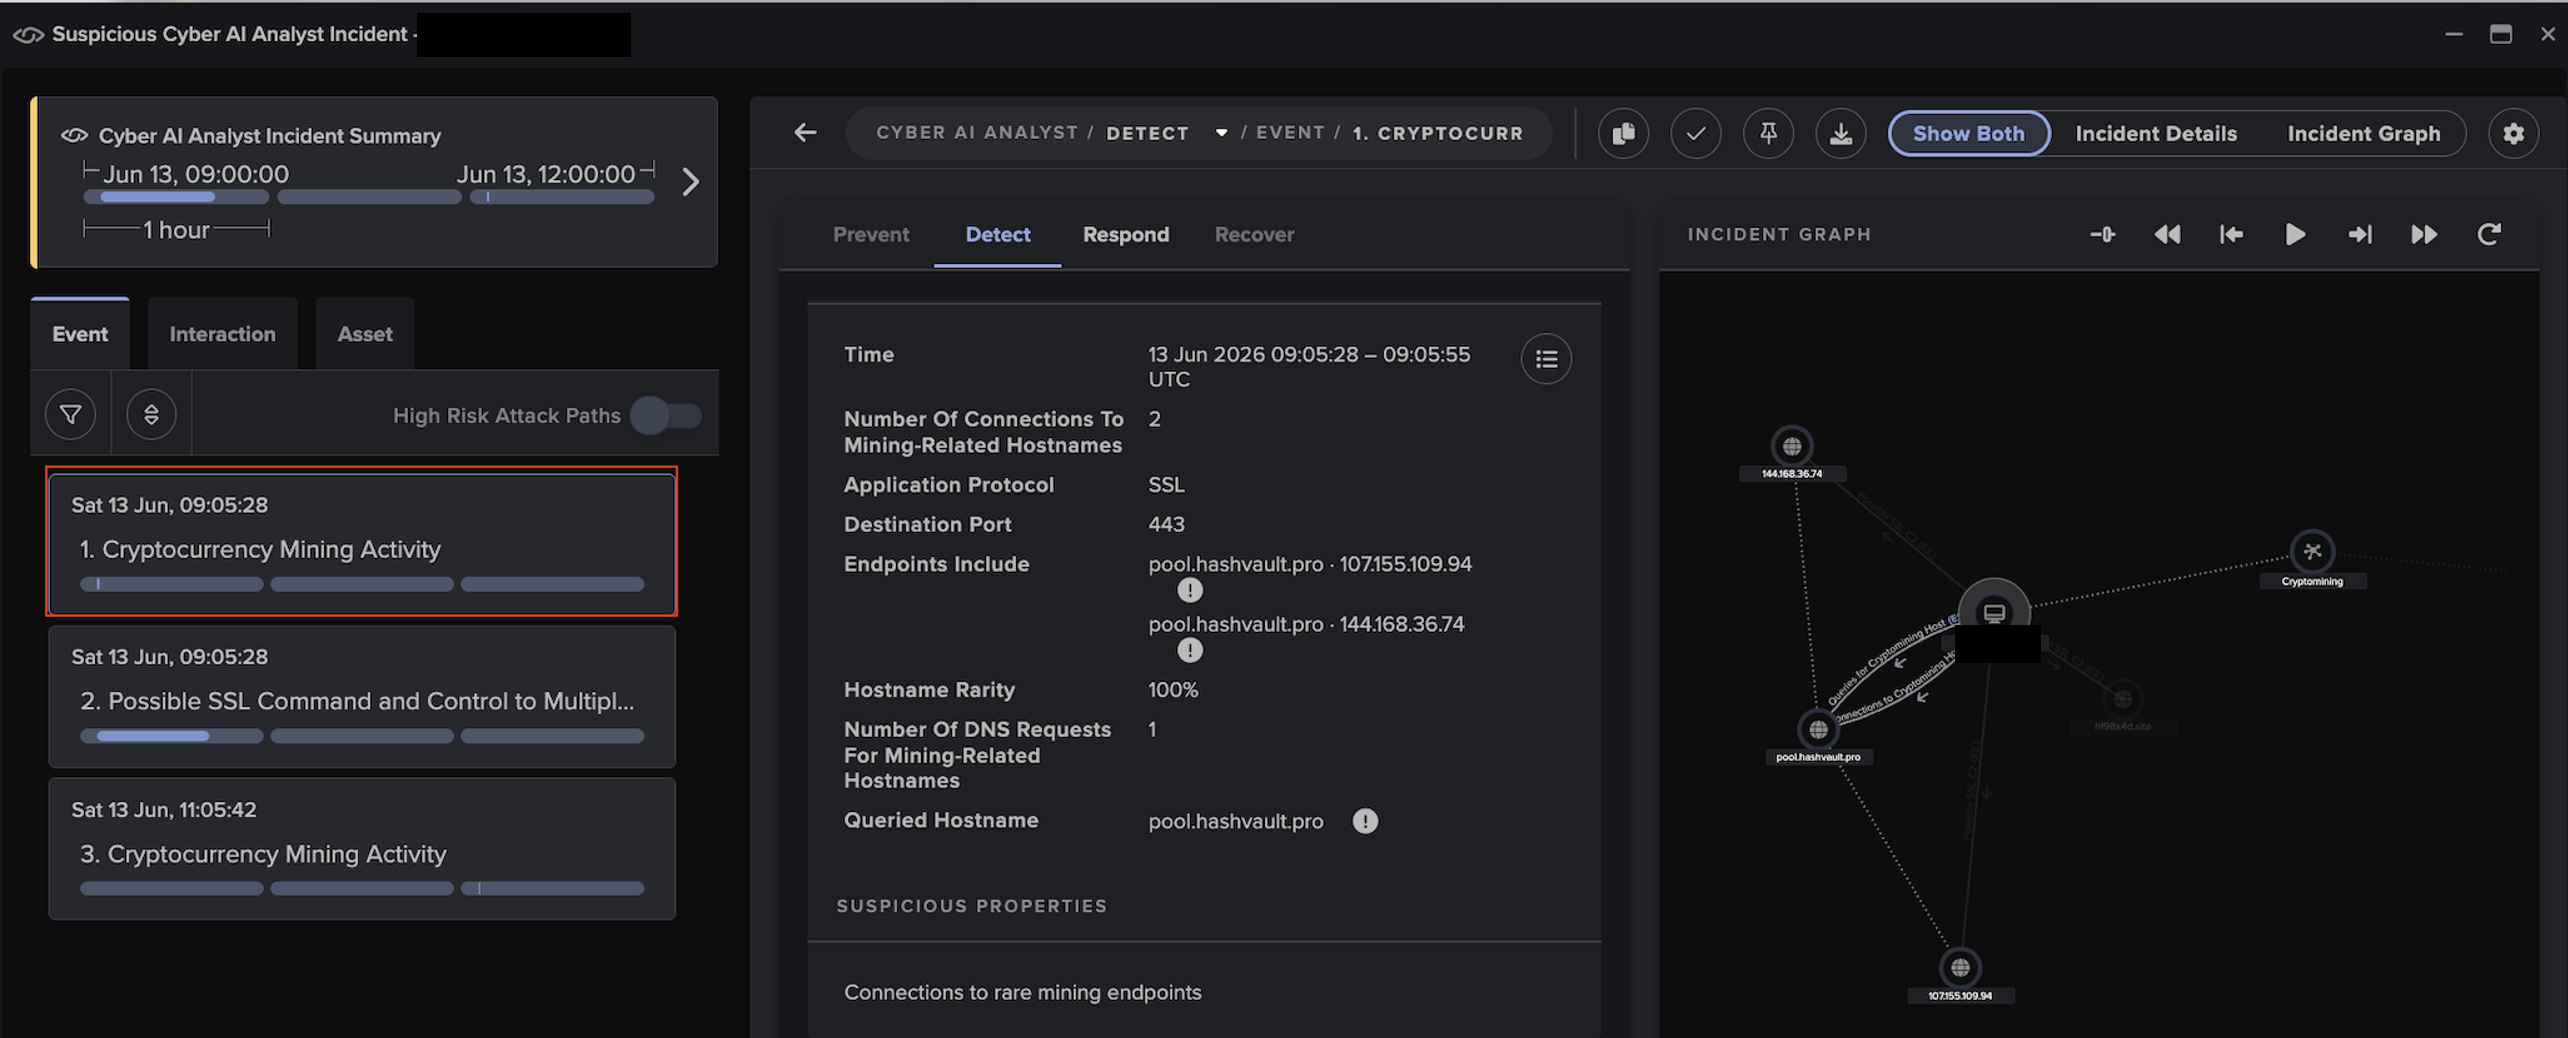
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

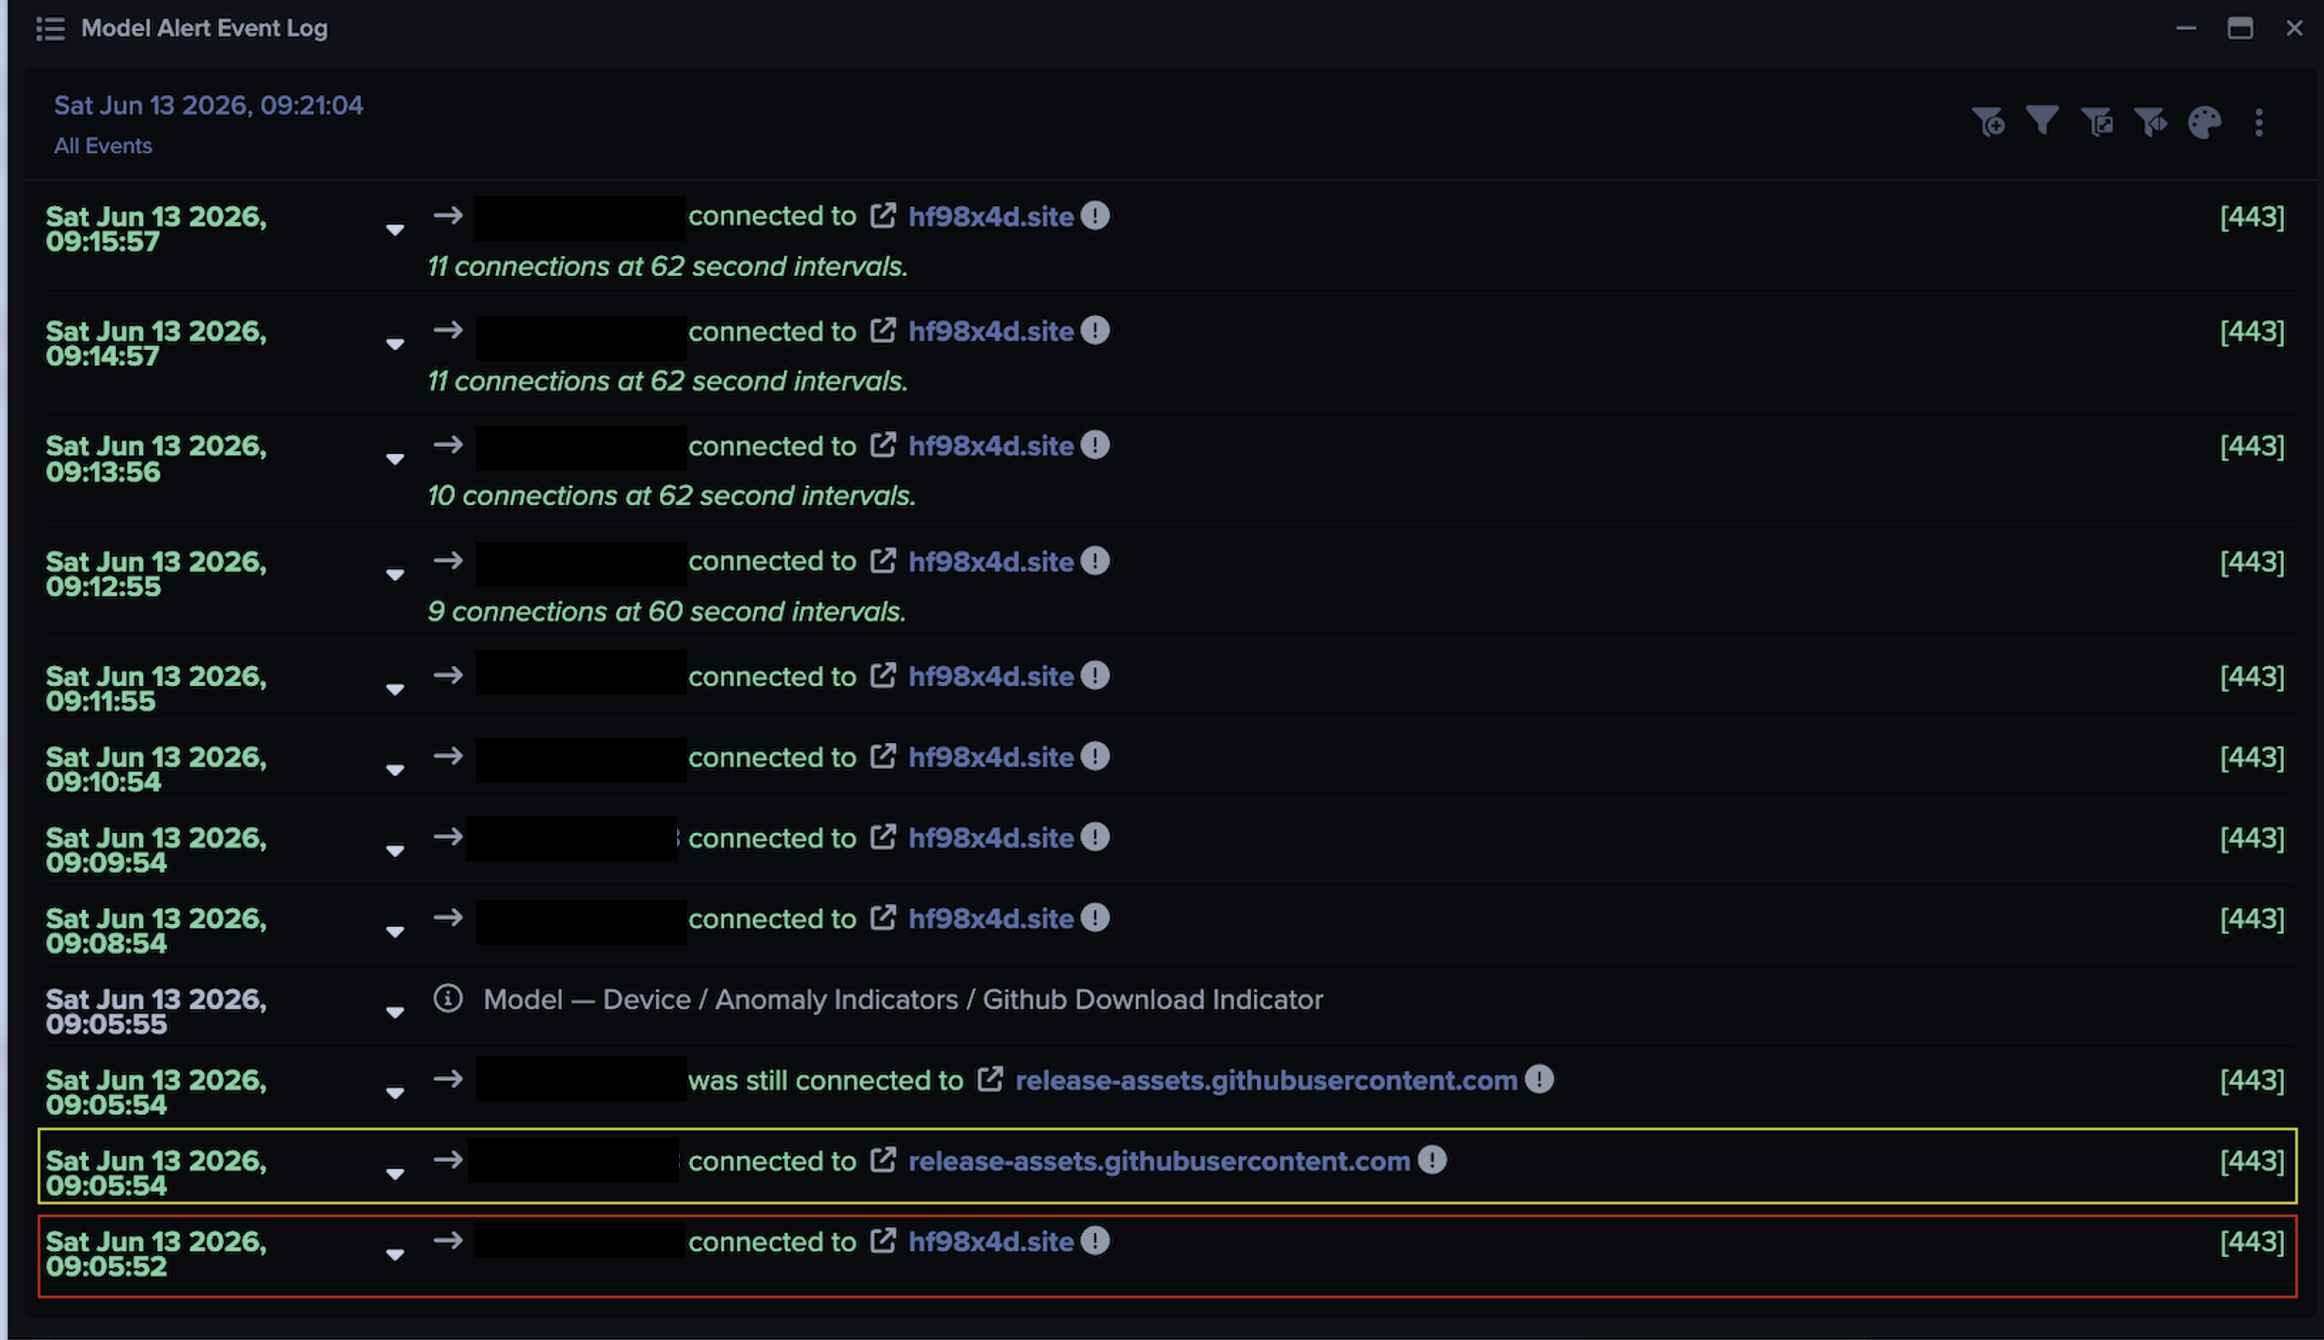
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ