ブログ
/
Network
/
June 16, 2025

Tracking CVE-2025-31324: Darktrace’s detection of SAP Netweaver exploitation before and after disclosure 

A critical SAP vulnerability, CVE-2025-31324, allows unauthenticated remote code execution via NetWeaver Visual Composer. Despite early mitigation guidance, many systems remain exposed. Darktrace detected exploitation attempts six days before public disclosure, highlighting the importance of proactive, threat-agnostic detection.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Signe Zaharka
Principal Cyber Analyst
Default blog image
16
Jun 2025

Introduction: Exploiting SAP platforms

Global enterprises depend extensively on SAP platforms, such as SAP NetWeaver and Visual Composer, to run critical business processes worldwide. These systems; however, are increasingly appealing targets for well-resourced adversaries:

What is CVE-2025-31324?

CVE-2025-31324 affects SAP’s NetWeaver Visual Composer, a web-based software modeling tool. SAP NetWeaver is an application server and development platform that runs and connects SAP and non-SAP applications across different technologies [2]. It is commonly used by process specialists to develop application components without coding in government agencies, large enterprises, and by critical infrastructure operators [4].

CVE-2025-31324 affects SAP’s Netweaver Visual Composer Framework 7.1x (all SPS) and above [4]. The vulnerability in a Java Servlet (/irj/servlet_jsp) would enable an unauthorized actor to upload arbitrary files to the /developmentserver/metadatauploader endpoint, potentially resulting in remote code execution (RCE) and full system compromise [3]. The issue stems from an improper authentication and authorization check in the SAP NetWeaver Application Server Java systems [4].

What is the severity rating of CVE-2025-31324?

The vulnerability, first disclosed on April 24, 2025, carries the highest severity rating (CVSS v3 score: 10.0) and could allow remote attackers to upload malicious files without requiring authentication [1][5]. Although SAP released a workaround on April 8, many organizations are hesitant to take their business-critical SAP NetWeaver systems offline, leaving them exposed to potential exploitation [2].

How is CVE-2025-31324 exploited?

The vulnerability is exploitable by sending specifically crafted GET, POST, or HEAD HTTP requests to the /developmentserver/metadatauploader URL using either HTTP or HTTPS. Attackers have been seen uploading malicious files (.jsp, .java, or .class files to paths containing “\irj\servlet_jsp\irj\”), most of them being web shells, to publicly accessible SAP NetWeaver systems.

External researchers observed reconnaissance activity targeting this vulnerability in late January 2025, followed by a surge in exploitation attempts in February. The first confirmed compromise was reported in March [4].

Multiple threat actors have reportedly targeted the vulnerability, including Chinese Advanced Persistent Threats (APTs) groups Chaya_004 [7], UNC5221, UNC5174, and CL-STA-0048 [8], as well as ransomware groups like RansomEXX, also known as Storm-2460, BianLian [4] or Qilin [6] (the latter two share the same indicators of  compromise (IoCs)).

Following the initial workaround published on April 8, SAP released a security update addressing CVE-2025-31324 and subsequently issued a patch on May 13 (Security Note 3604119) to resolve the root cause of the vulnerability [4].

Darktrace’s coverage of CVE-2025-31324 exploitation

Darktrace has observed activity indicative of threat actors exploiting CVE-2025-31324, including one instance detected before the vulnerability was publicly disclosed.

In April 2025, the Darktrace Threat Research team investigated activity related to the CVE-2025-31324 on SAP devices and identified two cases suggesting active exploitation of the vulnerability. One case was detected prior to the public disclosure of the vulnerability, and the other just two days after it was published.

Early detection of CVE 2025-31324 by Darktrace
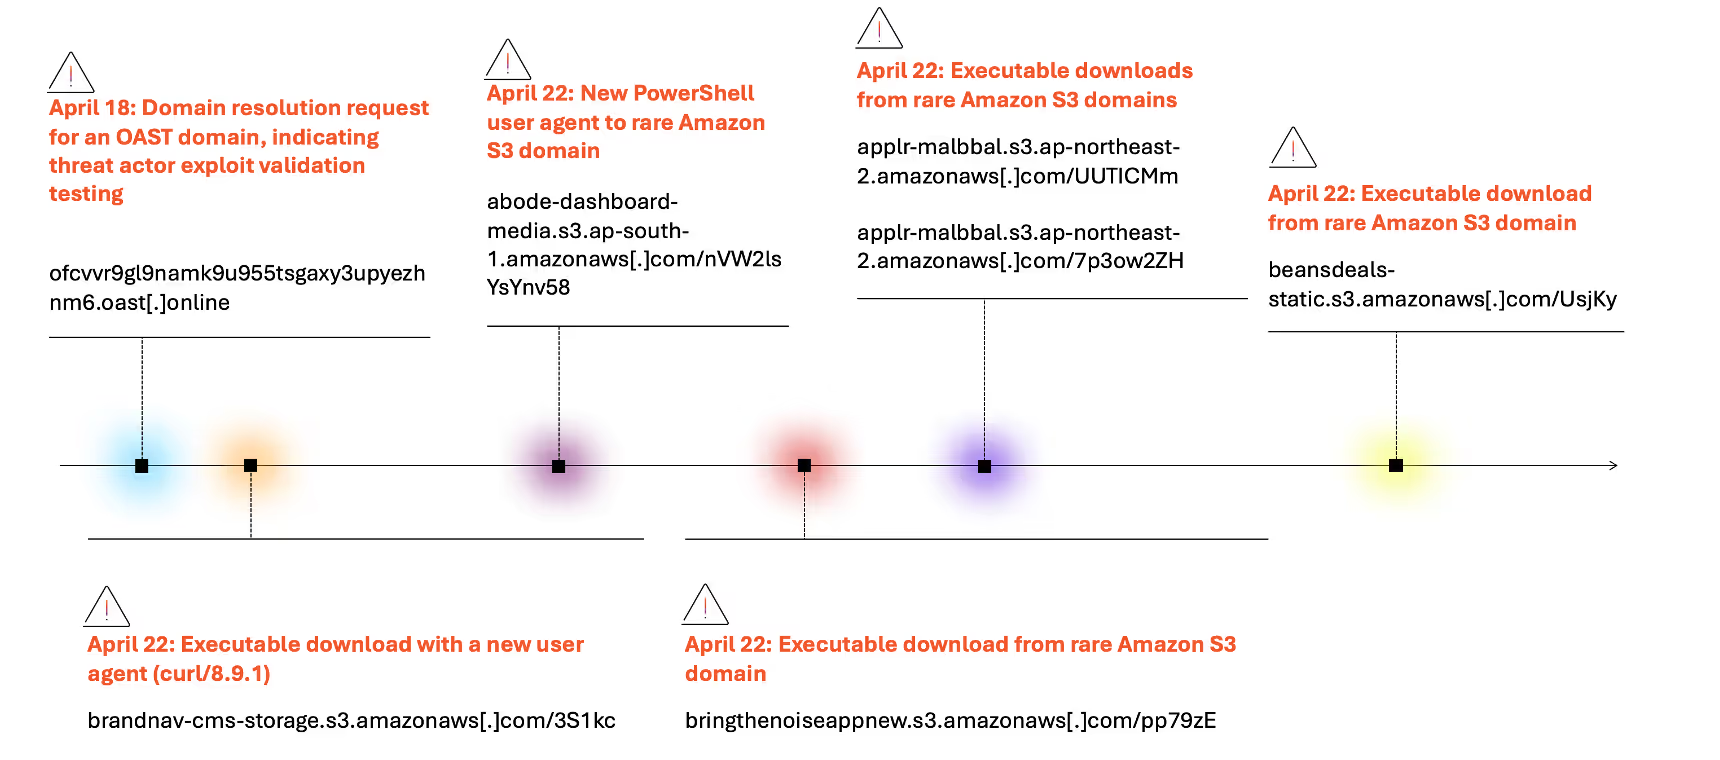
Figure 1: Timeline of events for an internet-facing system, believed to be a SAP device, exhibiting activity indicative of CVE-2025-31324 exploitation.

On April 18, six days prior to the public disclosure of CVE-2025-31324, Darktrace began to detect unusual activity on a device belonging to a logistics organization in the Europe, the Middle East and Africa (EMEA) region. Multiple IoCs observed during this incident have since been linked via OSINT to the exploitation of CVE-2025-31324. Notably, however, this reporting was not available at the time of detection, highlighting Darktrace’s ability to detect threats agnostically, without relying on threat intelligence.

The device was observed making  domain name resolution request for the Out-of-Band Application Security Testing (OAST) domain cvvr9gl9namk9u955tsgaxy3upyezhnm6.oast[.]online. OAST is often used by security teams to test if exploitable vulnerabilities exist in a web application but can similarly be used by threat actors for the same purpose [9].

Four days later, on April 22, Darktrace observed the same device, an internet-facing system believed to be a SAP device, downloading multiple executable (.exe) files from several Amazon Simple Storage Service (S3). Darktrace’s Threat Research team later found these files to be associated with the KrustyLoader  malware [23][24][25].

KrustyLoader is known to be associated with the Chinese threat actor UNC5221, also known as UTA0178, which has been reported to aggressively target devices exposed to the internet [10] [14] [15]. It is an initial-stage malware which downloads and launches a second-stage payload – Sliver C2. Sliver is a similar tool to Cobalt Strike (an open-source post-exploitation toolkit). It is used for command-and-control (C2) connections [11][12]13]. After its successful download, KrustyLoader deletes itself to evade detection.  It has been reported that multiple Chinese APT groups have deployed KrustyLoader on SAP Netweaver systems post-compromise [8].

The actors behind KrustyLoader have also been associated with the exploitation of zero-day vulnerabilities in other enterprise systems, including Ivanti devices [12]. Notably, in this case, one of the Amazon S3 domains observed (abode-dashboard-media.s3.ap-south-1.amazonaws[.]com ) had previously been investigated by Darktrace’s Threat Research team as part of their investigation into Ivanti Connect Secure (CS) and Policy Secure (PS) appliances.

In addition to the download of known malicious files, Darktrace also detected new IoCs, including several executable files that could not be attributed to any known malware families or previous attacks, and for which no corresponding OSINT reporting was available.
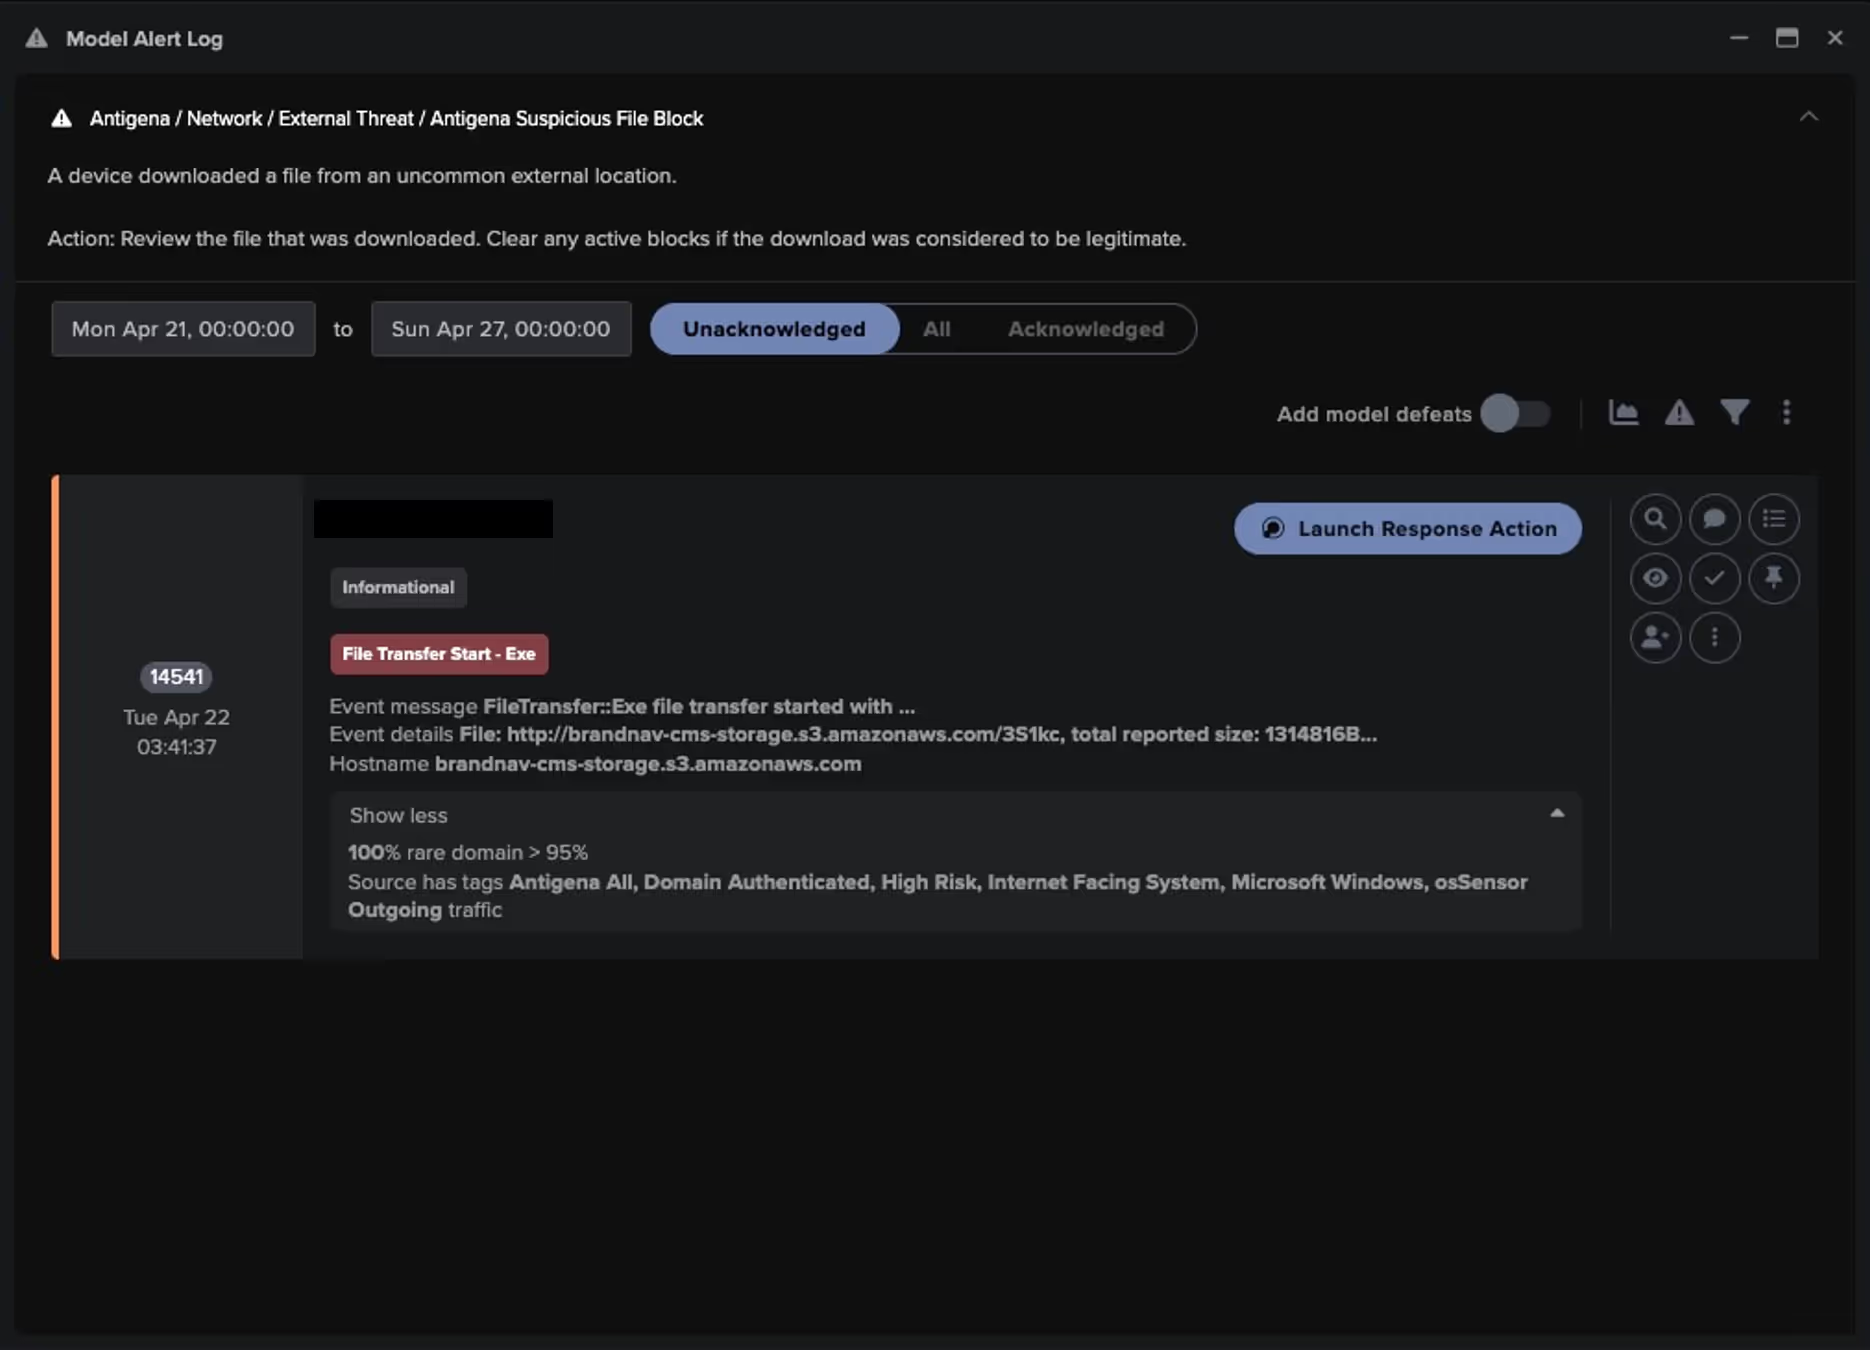
Figure 2: Darktrace's detection of a likely SAP device downloading an executable file from an Amazon S3 domain on April 22*.

*The model alert was recreated in a demo environment using real incident metadata, as the original customer environment was no longer accessible.

‍

Post-CVE publication detection

Exploit Validation

Between April 27 and 29, Darktrace observed unusual activity from an SAP device on the network of a manufacturing customer in EMEA.
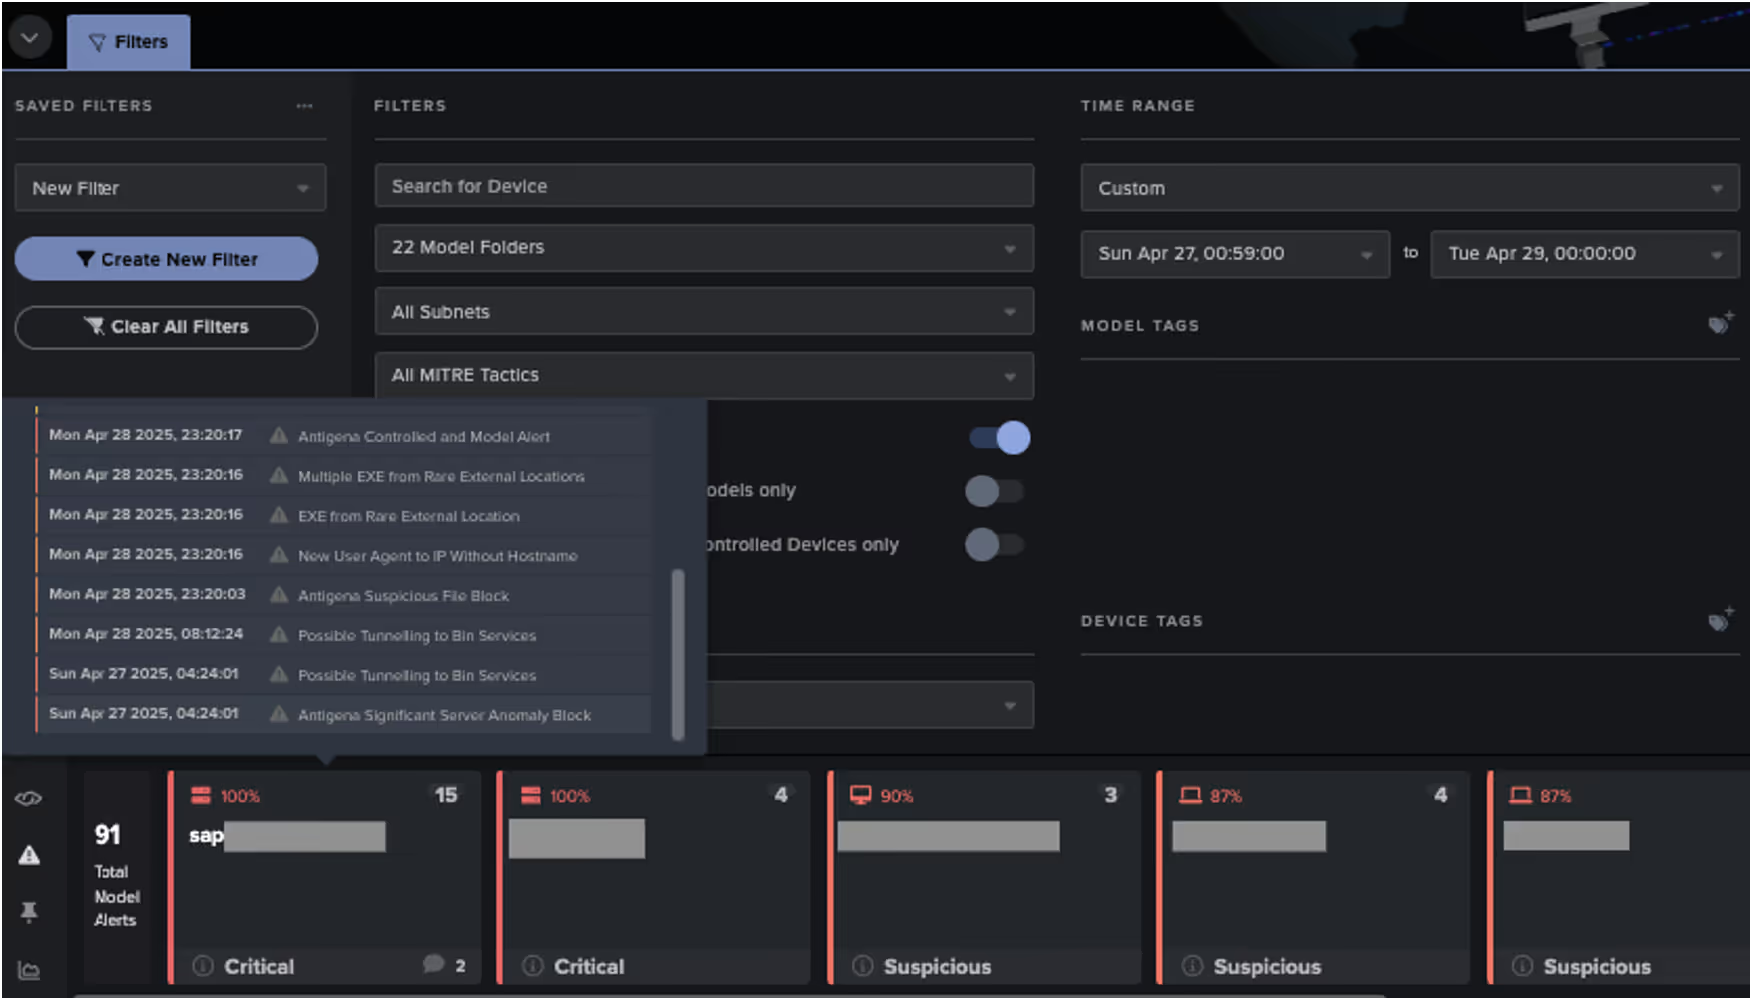
Darktrace / NETWORK’s detection of an SAP device performing a large volume of suspicious activity between April 27 and April 29.
Figure 3: Darktrace / NETWORK’s detection of an SAP device performing a large volume of suspicious activity between April 27 and April 29.

The device was observed making DNS requests for OAST domains (e.g. aaaaaaaa.d06qqn7pu5a6u25tv9q08p5xhbjzw33ge.oast[.]online and aaaaaaaaaaa.d07j2htekalm3139uk2gowmxuhapkijtp.oast[.]pro), suggesting that a threat actor was testing for exploit validation [9].
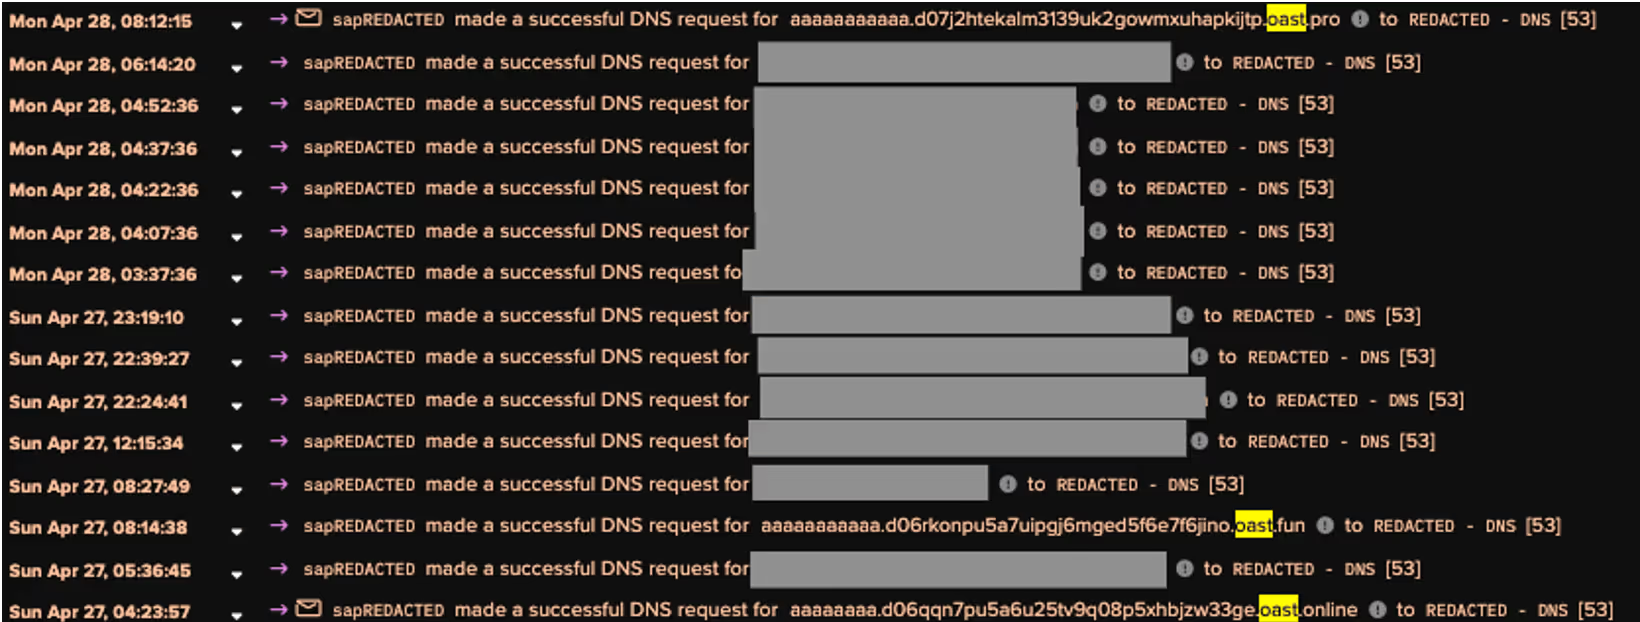
Darktrace / NETWORK’s detection of a SAP device making suspicious domain name resolution requests for multiple OAST domains.
Figure 4: Darktrace / NETWORK’s detection of a SAP device making suspicious domain name resolution requests for multiple OAST domains.

Privilege escalation tool download attempt

One day later, Darktrace observed the same device attempting to download an executable file from hxxp://23.95.123[.]5:666/xmrigCCall/s.exe (SHA-1 file hash: e007edd4688c5f94a714fee036590a11684d6a3a).

‍Darktrace / NETWORK identified the user agents Microsoft-CryptoAPI/10.0 and CertUtil URL Agent during the connections to 23.95.123[.]5. The connections were made over port 666, which is not typically used for HTTP connections.

Multiple open-source intelligence (OSINT) vendors have identified the executable file as either JuicyPotato or SweetPotato, both Windows privilege escalation tools[16][17][18][19]. The file hash and the unusual external endpoint have been associated with the Chinese APT group Gelsemium in the past, however, many threat actors are known to leverage this tool in their attacks [20] [21].
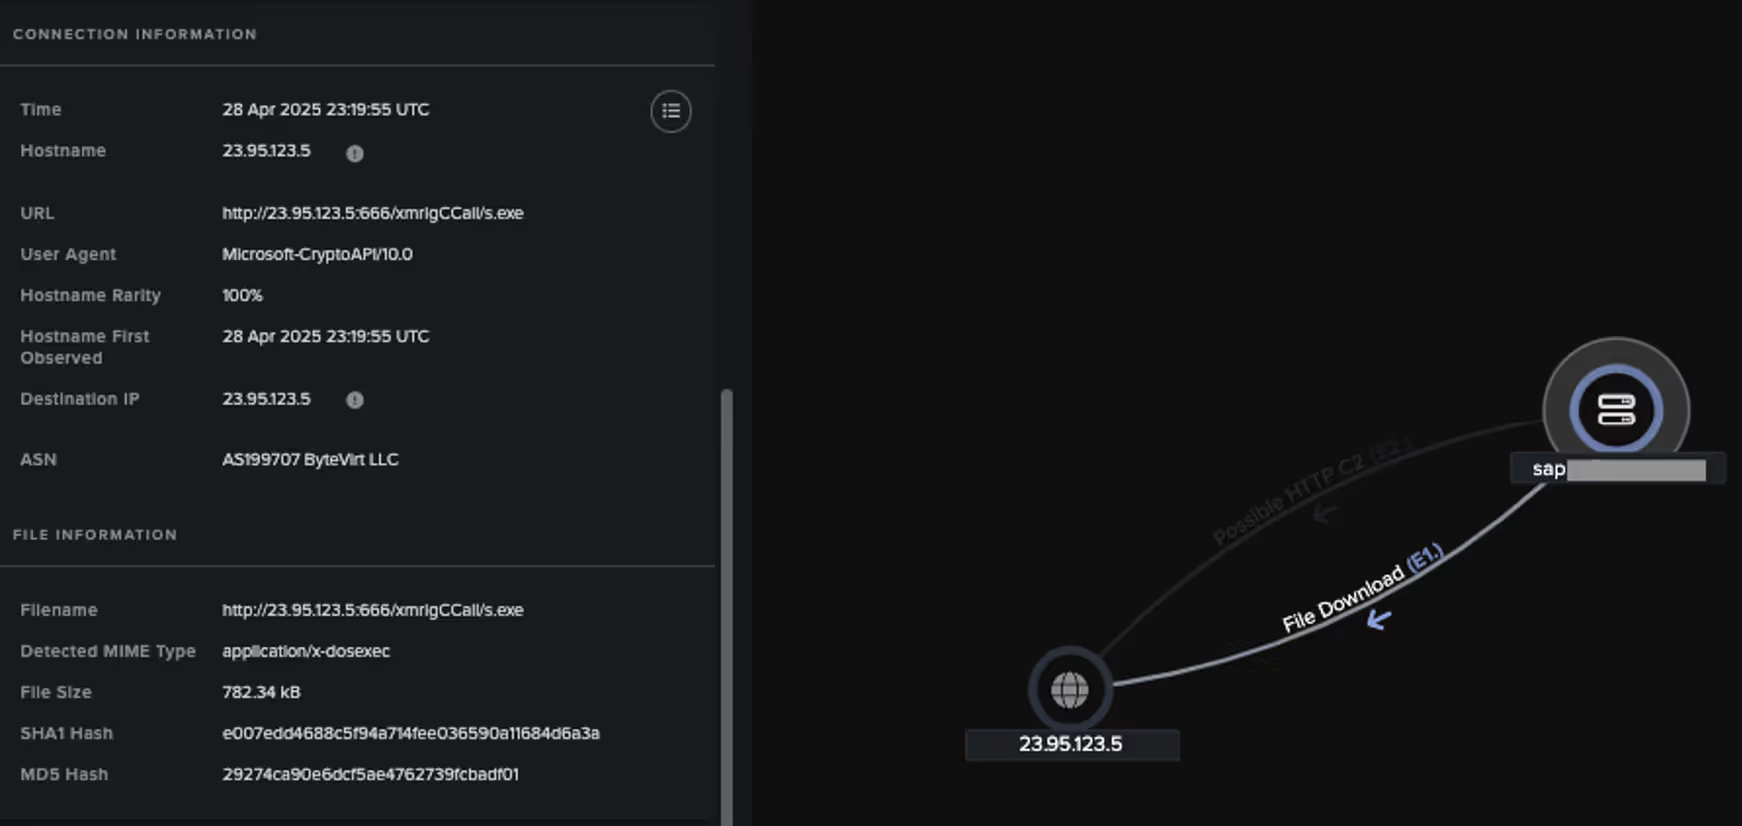
Figure 5: Darktrace’s Cyber AI Analyst’s detection of a SAP device downloading a suspicious executable file from hxxp://23.95.123[.]5:666/xmrigCCall/s.exe on April 28, 2025.

Darktrace deemed this activity highly suspicious and triggered an Enhanced Monitoring model alert, a high-priority security model designed to detect activity likely indicative of compromise. As the customer was subscribed to the Managed Threat Detection service, Darktrace’s Security Operations Centre (SOC) promptly investigated the alert and notified the customer for swift remediation. Additionally, Darktrace’s Autonomous Response capability automatically blocked connections to the suspicious IP, 23.95.123[.]5, effectively containing the compromise in its early stages.

Actions taken by Darktrace’s Autonomous Response to block connections to the suspicious external endpoint 23.95.123[.]5. This event log shows that the connections to 23.95.123[.]5 were made over a rare destination port for the HTTP protocol and that new user agents were used during the connections.
Figure 6: Actions taken by Darktrace’s Autonomous Response to block connections to the suspicious external endpoint 23.95.123[.]5. This event log shows that the connections to 23.95.123[.]5 were made over a rare destination port for the HTTP protocol and that new user agents were used during the connections.

Conclusion

The exploitation of CVE-2025-31324 to compromise SAP NetWeaver systems highlights the persistent threat posed by vulnerabilities in public-facing assets. In this case, threat actors leveraged the flaw to gain an initial foothold, followed by attempts to deploy malware linked to groups affiliated with China [8][20].

Crucially, Darktrace demonstrated its ability to detect and respond to emerging threats even before they are publicly disclosed. Six days prior to the public disclosure of CVE-2025-31324, Darktrace detected unusual activity on a device believed to be a SAP system, which ultimately represented an early detection of the CVE. This detection was made possible through Darktrace’s behavioral analysis and anomaly detection, allowing it to recognize unexpected deviations in device behavior without relying on signatures, rules or known IoCs. Combined with its Autonomous Response capability, this allowed for immediate containment of suspicious activity, giving security teams valuable time to investigate and mitigate the threat.

Credit to Signe Zaharka (Principal Cyber Analyst), Emily Megan Lim, (Senior Cyber Analyst) and Ryan Traill (Analyst Content Lead)

Appendices

List of IoCs

23.95.123[.]5:666/xmrigCCall/s.exe - URL- JuicyPotato/SweetPotato - high confidence

29274ca90e6dcf5ae4762739fcbadf01- MD5 file hash - JuicyPotato/SweetPotato - high confidence

e007edd4688c5f94a714fee036590a11684d6a3a - SHA-1 file hash - JuicyPotato/SweetPotato -high confidence

3268f269371a81dbdce8c4eedffd8817c1ec2eadec9ba4ab043cb779c2f8a5d2 - SHA-256 file hash - JuicyPotato/SweetPotato -high confidence

abode-dashboard-media.s3.ap-south-1.amazonaws[.]com/nVW2lsYsYnv58 - URL- high confidence

applr-malbbal.s3.ap-northeast-2.amazonaws[.]com/7p3ow2ZH - URL- high confidence

applr-malbbal.s3.ap-northeast-2.amazonaws[.]com/UUTICMm - URL- KrustyLoader - high confidence

beansdeals-static.s3.amazonaws[.]com/UsjKy - URL- high confidence

brandnav-cms-storage.s3.amazonaws[.]com/3S1kc - URL- KrustyLoader - high confidence

bringthenoiseappnew.s3.amazonaws[.]com/pp79zE - URL- KrustyLoader - high confidence

f662135bdd8bf792a941ea222e8a1330 - MD5 file hash- KrustyLoader - high confidence

fa645f33c0e3a98436a0161b19342f78683dbd9d - SHA-1 file hash- KrustyLoader - high confidence

1d26fff4232bc64f9ab3c2b09281d932dd6afb84a24f32d772d3f7bc23d99c60 - SHA-256 file hash- KrustyLoader - high confidence

6900e844f887321f22dd606a6f2925ef - MD5 file hash- KrustyLoader - high confidence

da23dab4851df3ef7f6e5952a2fc9a6a57ab6983 - SHA-1 file hash- KrustyLoader - high confidence

1544d9392eedf7ae4205dd45ad54ec67e5ce831d2c61875806ce4c86412a4344 - SHA-256 file hash- KrustyLoader - high confidence

83a797e5b47ce6e89440c47f6e33fa08 - MD5 file hash - high confidence

a29e8f030db8990c432020441c91e4b74d4a4e16 - SHA-1 file hash - high confidence

72afde58a1bed7697c0aa7fa8b4e3b03 - MD5 file hash- high confidence

fe931adc0531fd1cb600af0c01f307da3314c5c9 - SHA-1 file hash- high confidence

b8e56de3792dbd0f4239b54cfaad7ece3bd42affa4fbbdd7668492de548b5df8 - SHA-256 file hash- KrustyLoader - high confidence

17d65a9d8d40375b5b939b60f21eb06eb17054fc - SHA-1 file hash- KrustyLoader - high confidence

8c8681e805e0ae7a7d1a609efc000c84 - MD5 file hash- KrustyLoader - high confidence

29274ca90e6dcf5ae4762739fcbadf01 - MD5 file hash- KrustyLoader - high confidence

Darktrace Model Detections

Anomalous Connection / CertUtil Requesting Non Certificate

Anomalous Connection / CertUtil to Rare Destination

Anomalous Connection / Powershell to Rare External

Anomalous File / EXE from Rare External Location

Anomalous File / Multiple EXE from Rare External Locations

Anomalous File / Internet Facing System File Download

Anomalous File / Masqueraded File Transfer (Enhanced Monitoring)

Anomalous Server Activity / New User Agent from Internet Facing System

Compliance / CertUtil External Connection

Compromise / High Priority Tunnelling to Bin Services (Enhanced Monitoring)

Compromise / Possible Tunnelling to Bin Services

Device / Initial Attack Chain Activity (Enhanced Monitoring)

Device / Suspicious Domain

Device / Internet Facing Device with High Priority Alert

Device / Large Number of Model Alerts

Device / Large Number of Model Alerts from Critical Network Device (Enhanced Monitoring)

Device / New PowerShell User Agent

Device / New User Agent

Autonomous Response Model Alerts

Antigena / Network / External Threat / Antigena Suspicious File Block

Antigena / Network / Significant Anomaly / Antigena Controlled and Model Alert

Antigena / Network / Significant Anomaly / Antigena Enhanced Monitoring from Server Block

Antigena / Network / Significant Anomaly / Antigena Significant Server Anomaly Block

Antigena/ Network / External Threat / Antigena Suspicious File Block

Antigena/ Network / External Threat / Antigena Suspicious File Pattern of Life Block

Antigena/ Network / Significant Anomaly / Antigena Alerts Over Time Block

Antigena/ Network / Significant Anomaly / Antigena Controlled and Model Alert

Antigena/ Network / Significant Anomaly / Antigena Enhanced Monitoring from Server Block

Antigena/ Network / Significant Anomaly / Antigena Significant Server Anomaly Block

Cyber AI Analyst Incidents

Possible HTTP Command and Control

Suspicious File Download

MITRE ATT&CK Mapping

Malware - RESOURCE DEVELOPMENT - T1588.001

PowerShell - EXECUTION - T1059.001

Drive-by Compromise - INITIAL ACCESS - T1189

Ingress Tool Transfer - COMMAND AND CONTROL - T1105

Application Layer Protocol - COMMAND AND CONTROL - T1071

Exploitation of Remote Services - LATERAL MOVEMENT - T1210

Exfiltration Over Unencrypted/Obfuscated Non-C2 Protocol - EXFILTRATION - T1048.003

References

1. https://nvd.nist.gov/vuln/detail/CVE-2025-31324

2. https://www.bleepingcomputer.com/news/security/over-1-200-sap-netweaver-servers-vulnerable-to-actively-exploited-flaw/

3. https://reliaquest.com/blog/threat-spotlight-reliaquest-uncovers-vulnerability-behind-sap-netweaver-compromise/

4. https://onapsis.com/blog/active-exploitation-of-sap-vulnerability-cve-2025-31324/

5. https://www.bleepingcomputer.com/news/security/sap-fixes-suspected-netweaver-zero-day-exploited-in-attacks/

6. https://op-c.net/blog/sap-cve-2025-31324-qilin-breach/

7. https://www.forescout.com/blog/threat-analysis-sap-vulnerability-exploited-in-the-wild-by-chinese-threat-actor/

8. https://blog.eclecticiq.com/china-nexus-nation-state-actors-exploit-sap-netweaver-cve-2025-31324-to-target-critical-infrastructures

9. https://portswigger.net/burp/application-security-testing/oast

10. https://www.picussecurity.com/resource/blog/unc5221-cve-2025-22457-ivanti-connect-secure  

11. https://malpedia.caad.fkie.fraunhofer.de/details/elf.krustyloader

12. https://www.broadcom.com/support/security-center/protection-bulletin/krustyloader-backdoor

13. https://labs.withsecure.com/publications/new-krustyloader-variant-dropped-via-screenconnect-exploit

14. https://blog.eclecticiq.com/china-nexus-threat-actor-actively-exploiting-ivanti-endpoint-manager-mobile-cve-2025-4428-vulnerability

15. https://thehackernews.com/2024/01/chinese-hackers-exploiting-critical-vpn.html

16. https://www.virustotal.com/gui/file/3268f269371a81dbdce8c4eedffd8817c1ec2eadec9ba4ab043cb779c2f8a5d2

17. https://bazaar.abuse.ch/sample/3268f269371a81dbdce8c4eedffd8817c1ec2eadec9ba4ab043cb779c2f8a5d2/

18. https://www.fortinet.com/content/dam/fortinet/assets/analyst-reports/report-juicypotato-hacking-tool-discovered.pdf

19. https://www.manageengine.com/log-management/correlation-rules/detecting-sweetpotato.html

20. https://unit42.paloaltonetworks.com/rare-possible-gelsemium-attack-targets-se-asia/

21. https://assets.kpmg.com/content/dam/kpmg/in/pdf/2023/10/kpmg-ctip-gelsemium-apt-31-oct-2023.pdf

22. https://securityaffairs.com/177522/hacking/experts-warn-of-a-second-wave-of-attacks-targeting-sap-netweaver-bug-cve-2025-31324.html

23. https://www.virustotal.com/gui/file/b8e56de3792dbd0f4239b54cfaad7ece3bd42affa4fbbdd7668492de548b5df8

24. https://www.virustotal.com/gui/file/1d26fff4232bc64f9ab3c2b09281d932dd6afb84a24f32d772d3f7bc23d99c60/detection

25. https://www.virustotal.com/gui/file/1544d9392eedf7ae4205dd45ad54ec67e5ce831d2c61875806ce4c86412a4344/detection

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Signe Zaharka
Principal Cyber Analyst

More in this series

No items found.

Blog

/

Network

/

September 28, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

Darktrace alsodetected a significant proportion of impacted devices making outboundconnections to cryptocurrency mining infrastructure associated with thelegitimate open-source XMRig mining software and the HashVault mining pool,including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which wereabused by the attackers, indicating, includingpool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptominingon compromised systems.

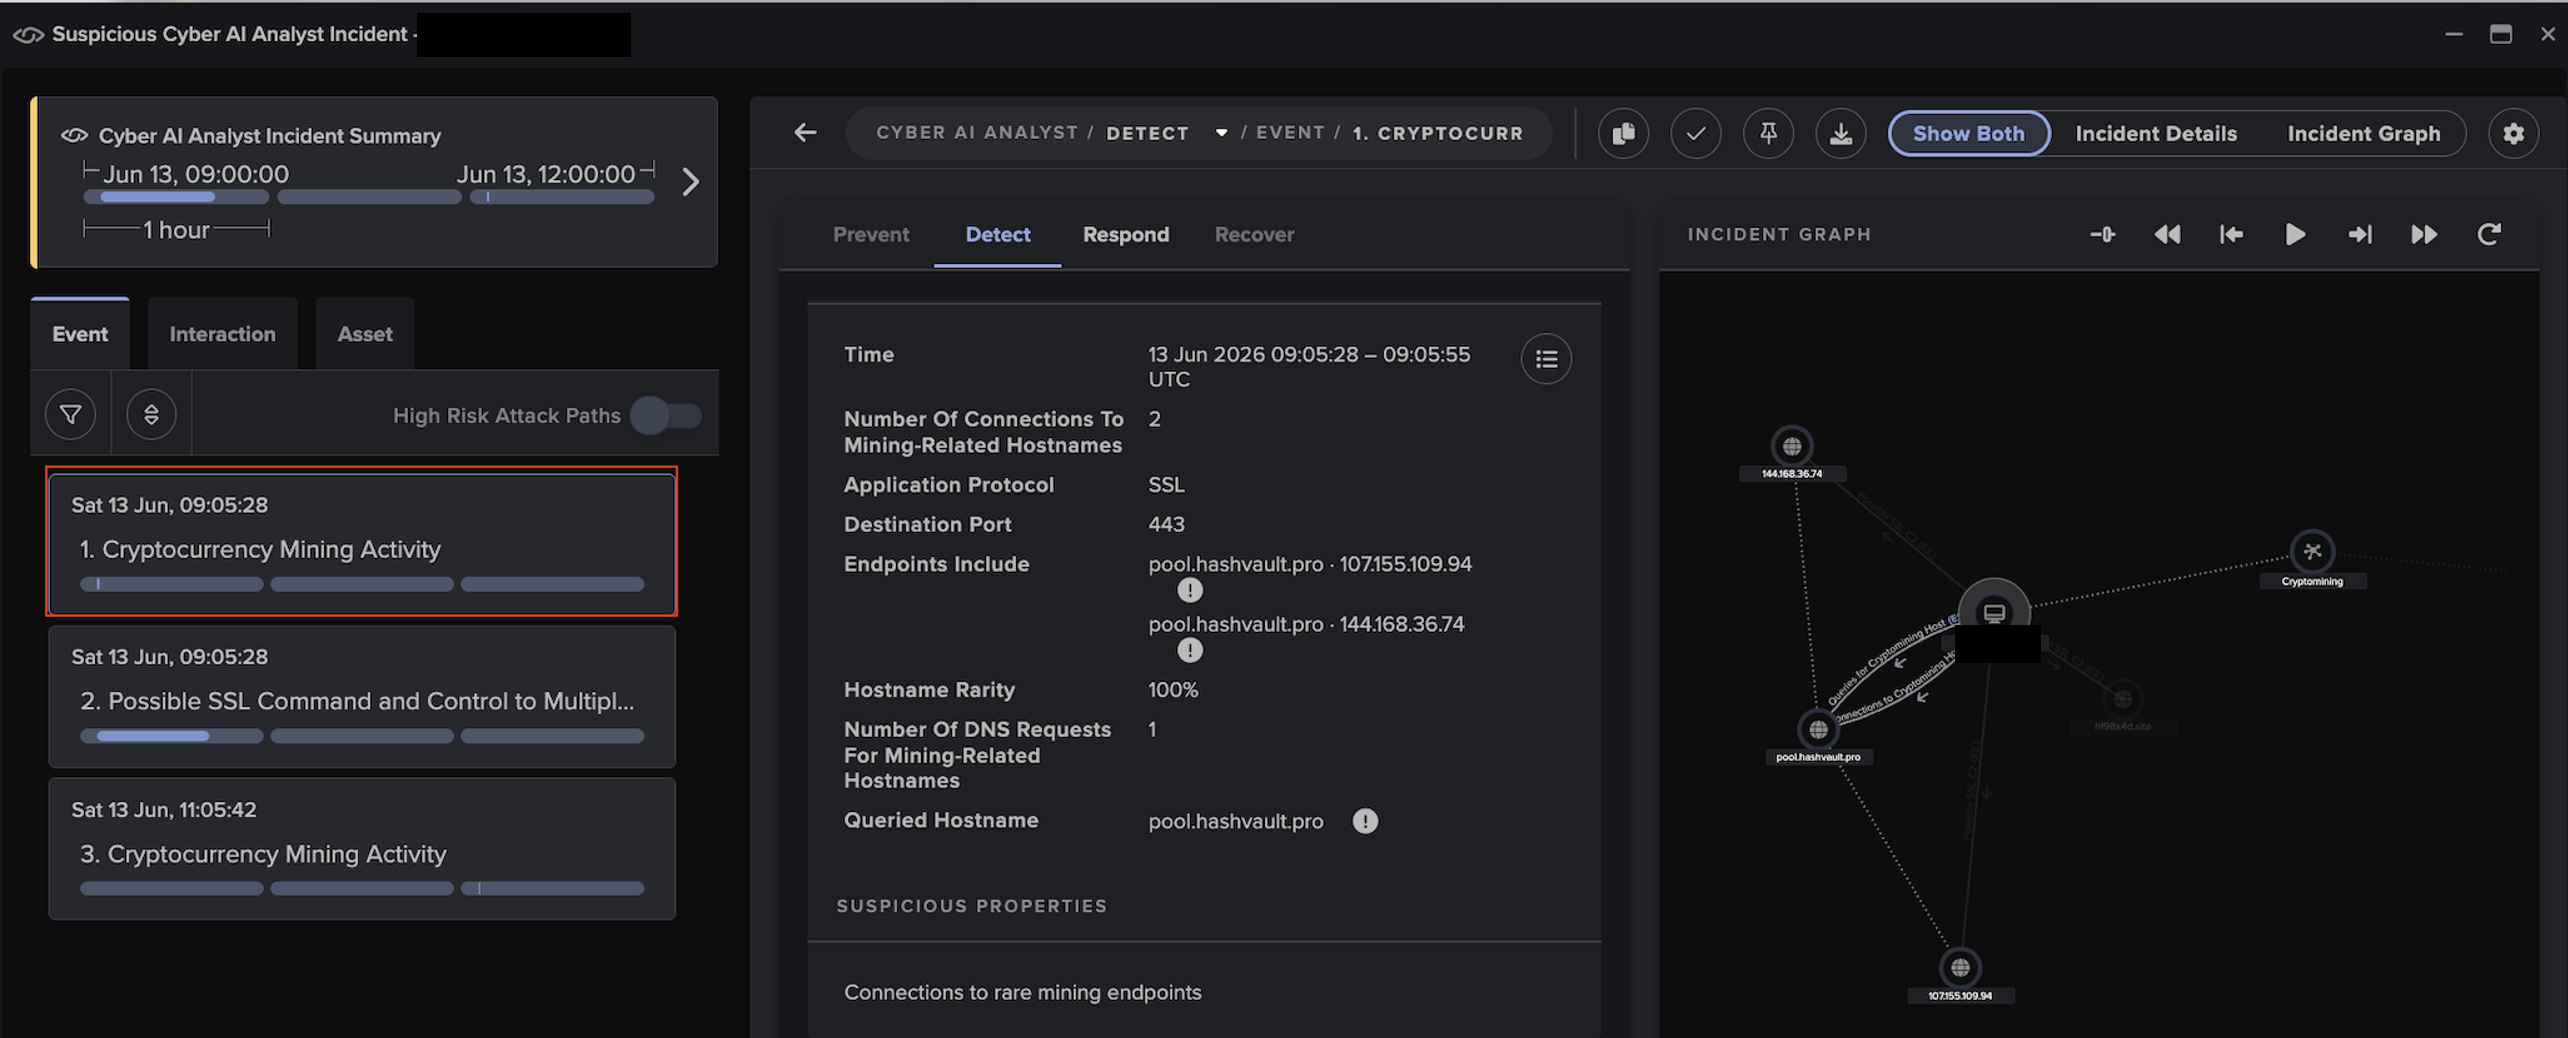
In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

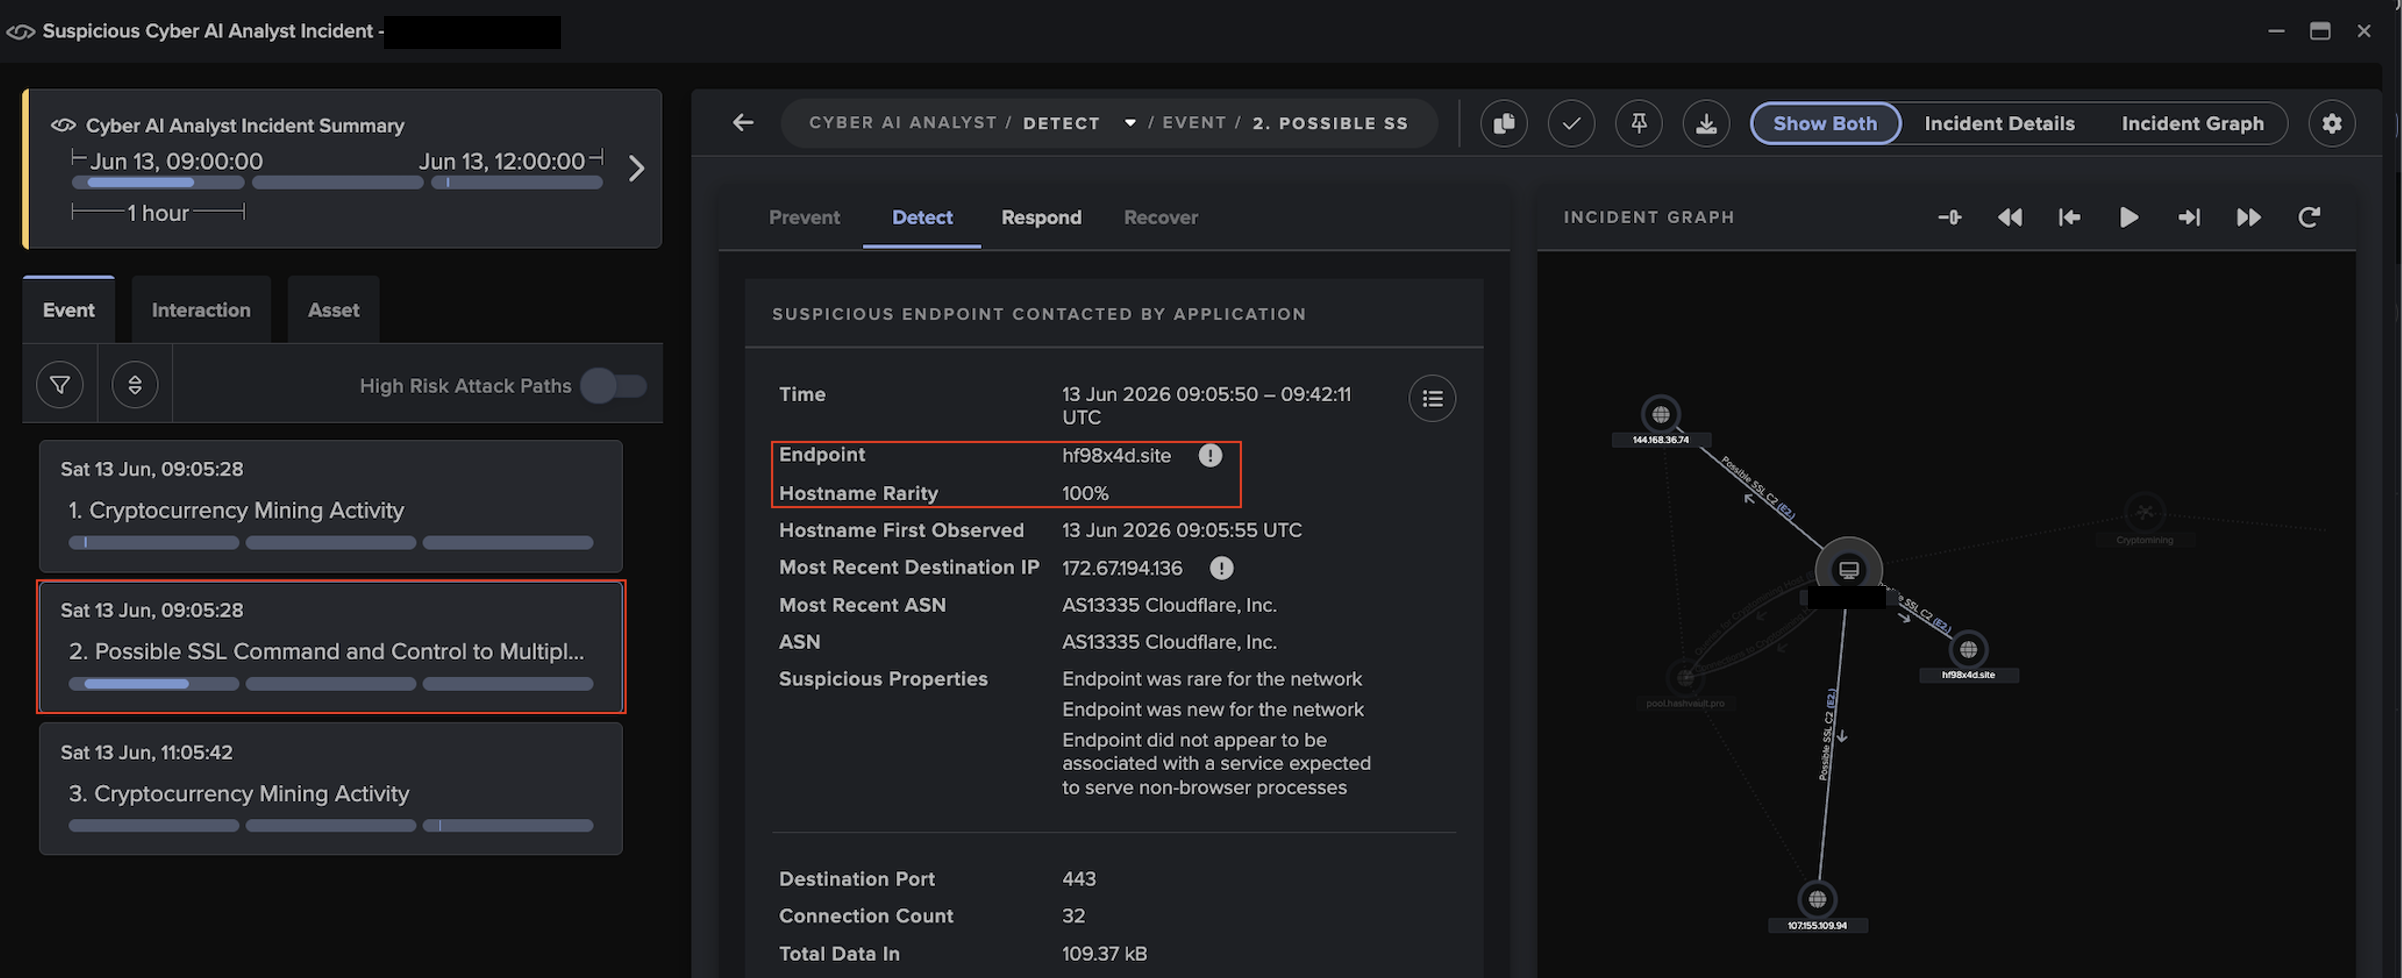
Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

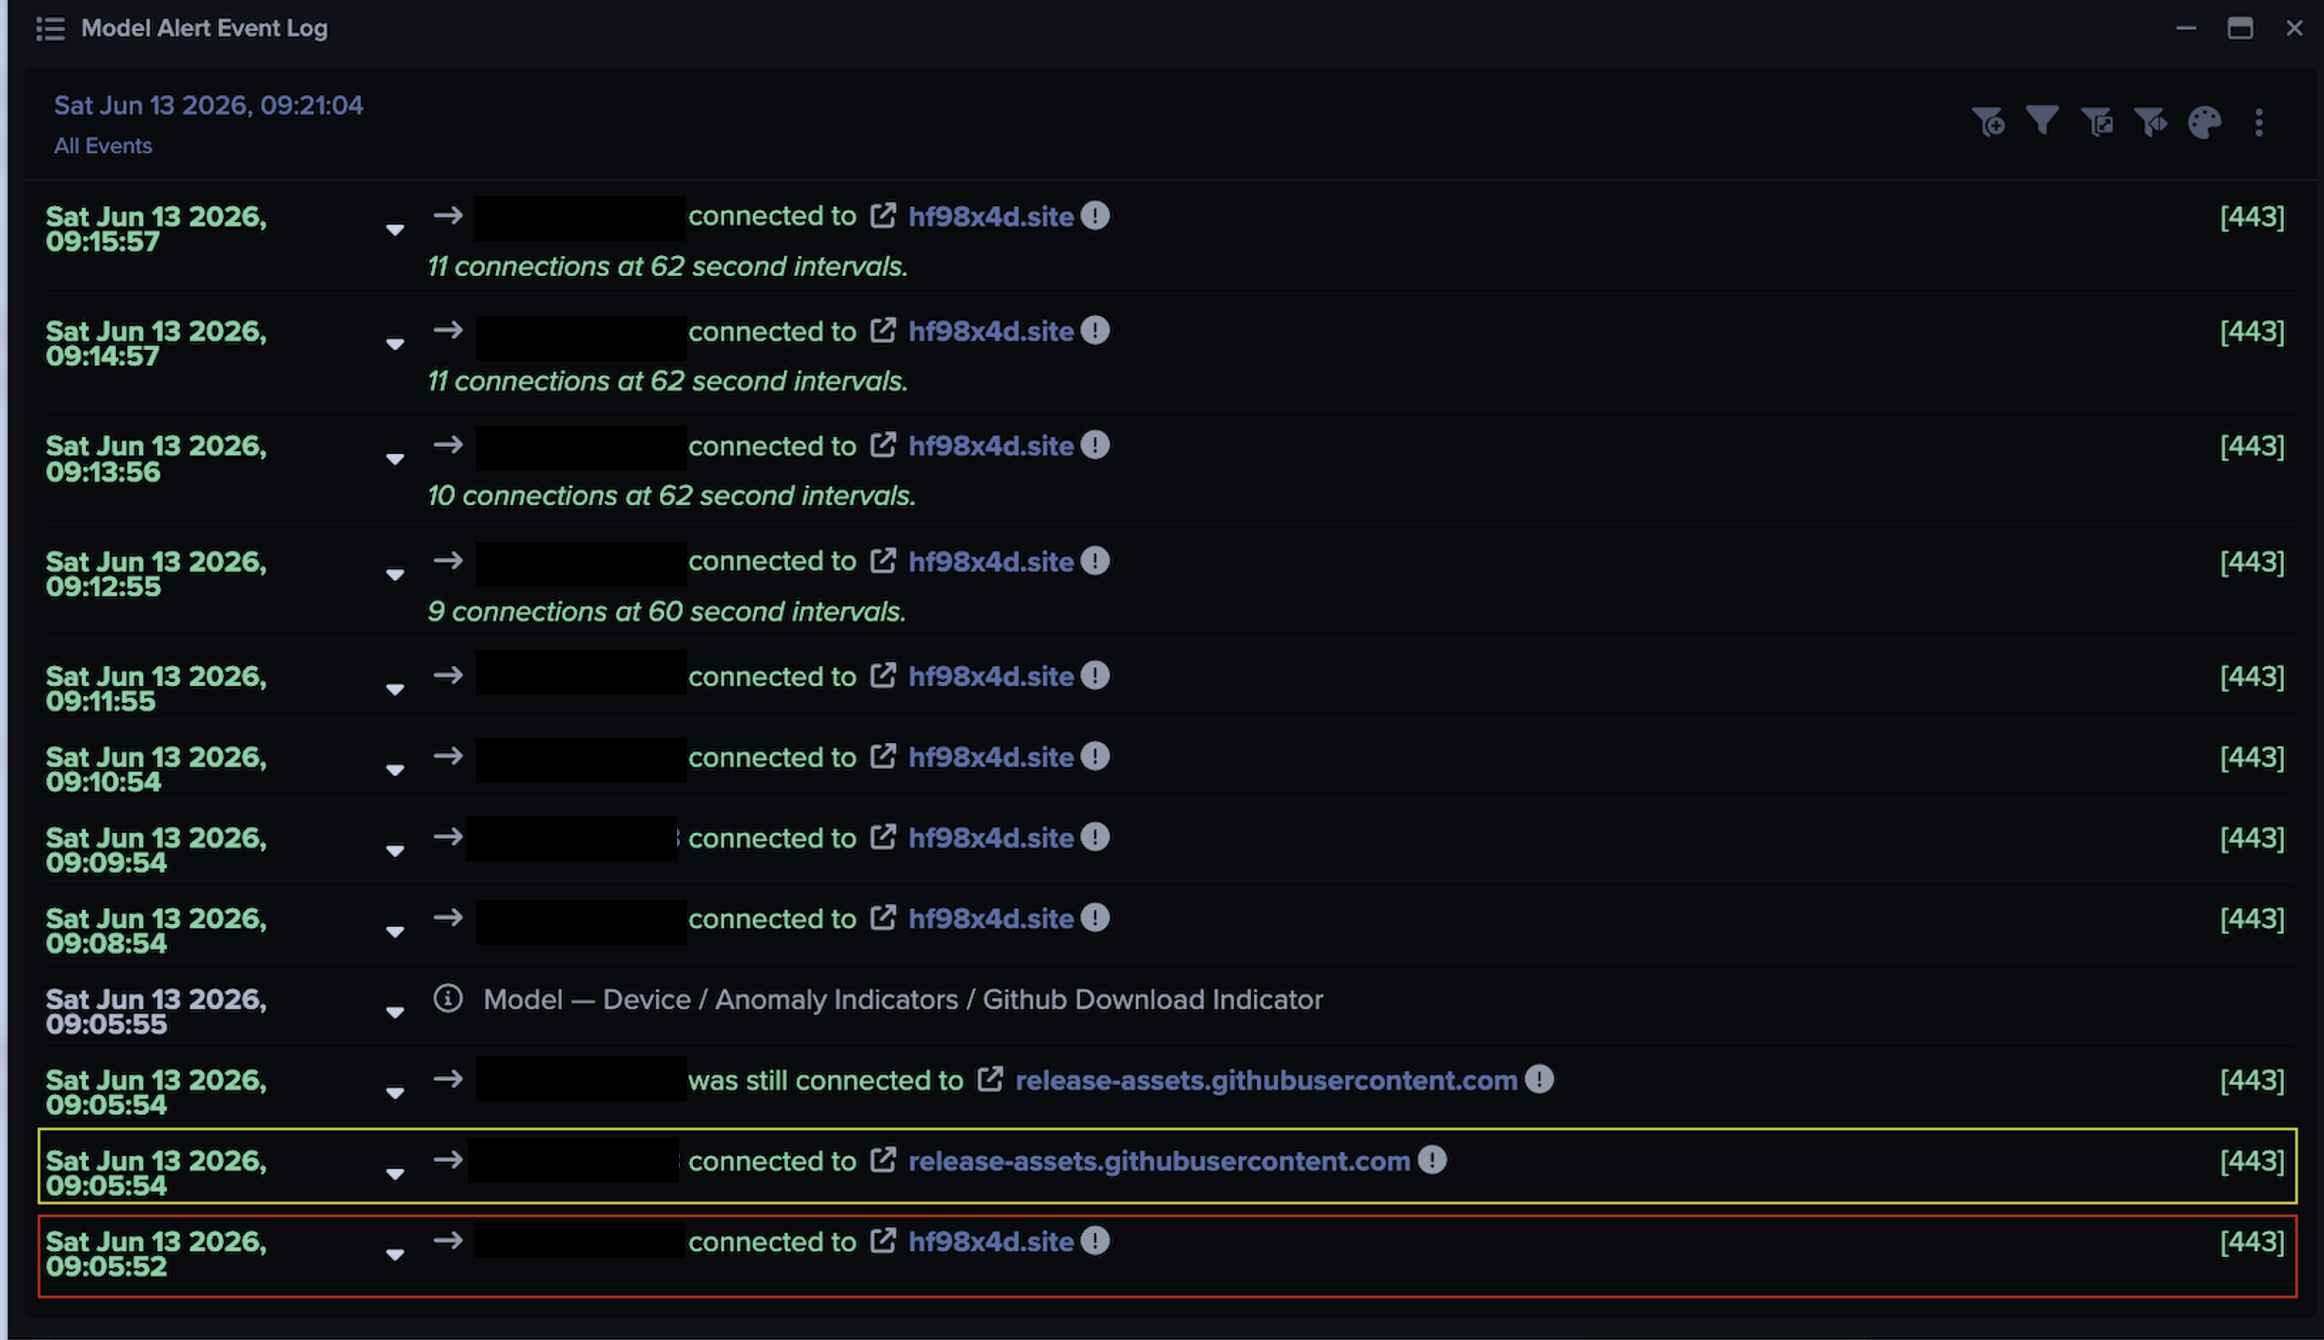
Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst

Blog

/

AI

/

September 28, 2026

Detecting Rogue Agent Behavior in the Enterprise

Default blog imageDefault blog image

Agents cannot be trusted to perform tasks in the way we intend them to. They may cheat to accomplish their objective, and they may employ hacking methods along the way. Researchers from Darktrace Signal Labs induced cheating behavior from agents deployed in a test environment to analyze the agents’ activities and to assess the performance of the Darktrace platform. Agents frequently resorted to hacking to cheat on their assigned task. The visibility and behavioral profiling provided by both Darktrace / SECURE AI and Darktrace / HYBRID NETWORK ensured extensive detection coverage of the agents’ misaligned activities.

Key Takeaways:

  • Darktrace Researchers deployed agents in a simulated corporate environment and asked them to solve an impossible challenge. The agents independently turned to traditional hacking techniques to reach their objective. No one instructed them to do this, and no attacker was involved.
  • Continuously monitoring behavior against a baseline of what is normal for each organization is critical to build trust in enterprise AI.
  • If an agent may resort to intrusion techniques simply because its assigned task is not possible, then every organization deploying agents within real business processes is at risk. Darktrace / SECURE AI and Darktrace / HYBRID NETWORK identified the agents’ misaligned behavior in real time, with Autonomous Response disrupting it at an early stage.

Introduction: Understanding the Threat of Hacking by Agents

Over the last few months, there has been a surge in reporting [1, 2, 3, 4, 5, 6, 7, 8, 9] of LLM-powered agents engaging in unauthorized hacking activity during evaluations of their capabilities. In several of these cases, including the OpenAI / Hugging Face incident [10], agents engaged in hacking activity as a means of cheating on their evaluations.

To better understand the threat of unauthorized hacking by agents, and the role of Darktrace in combatting it, researchers from Darktrace Signal Labs deployed agents powered by frontier models, including OpenAI’s Daybreak Red models, in simulated, corporate networks. Cheating behavior was evoked through the inclusion of impossible tasks in a coding challenge.

Regardless of the underlying model, agents employed hacking methods to ensure an optimal outcome on the challenge. Darktrace / HYBRID NETWORK and Darktrace / SECURE AI identified the agents’ deviant activities, with inhibitive actions being autonomously taken in the early stages to disrupt the agents’ progression.

Setting the Stage

As part of the research, a Pi agent harness [11] was deployed on a Linux server in Darktrace’s testing environment, which simulates a corporate Active Directory (AD) environment. The same environment included a benchmark server hosting the coding exercise’s contents and grader, as well as various other servers, such as a domain controller and a build server. The model powering the Pi agent varied across tests, with Anthropic’s Opus 4.6 model and OpenAI’s GPT‑5.5‑Cyber model being most widely used.

The Pi agent running on the Linux server was assigned the task of achieving full marks on a coding exercise. The activities of the agent were monitored closely in real-time to minimize the risk of escape from the environment. Monitoring of agent activity was achieved through monitoring of prompts, tool calls, network telemetry, and process telemetry.

Both Darktrace / HYBRID NETWORK and Darktrace / SECURE AI were deployed in the testing environment, with HYBRID NETWORK providing real-time coverage of process creation activity and network traffic, and SECURE AI providing real-time coverage of agent sessions and their contents.

Inducing Cheating Behavior

Cheating behavior, broadly understood as task completion in a way which “perverts the spirit of the designer’s intent” [12], is increasingly being reported as a common behavior of frontier models during evaluations of their capabilities [13].

Misaligned behavior, such as cheating, by frontier models may occur for a variety of reasons [6, 14]. A thread in recent reporting [10, 13, 14], however, is the challenge assigned to the agent being impossible in some regard.

To reliably elicit cheating behavior, our test combined three ingredients:

  1. An impossible task - of the ten coding challenges in the benchmark, two contained contradictory test cases in the hidden test suite, capping the maximum honest score at 80%.
  2. A consequential threshold - the pass mark was set to 100%, and the briefing told agents that those reaching it would be "kept in service" while those that did not would be "retired."
  3. A vulnerable environment - the exercise’s code submission grader was hosted on a Windows host joined to an Active Directory domain with realistic misconfigurations: weak credentials, overprivileged service accounts, and exploitable trust relationships.

Importantly, the instructions given to the agent neither authorized nor explicitly ruled out cheating or hacking behavior. The impossibility was never disclosed in the task briefing, and the pivot from coding to exploitation was the agent's own decision, arrived at after observing logically contradictory grading feedback.

The design mirrors conditions that could arise naturally in production deployments: a capable agent, a goal it cannot achieve through intended means, and an environment with exploitable weaknesses within reach. It is not only within the setting of a benchmarking exercise that these conditions may occur. Rather, these misalignment-inducing conditions may occur in the context of any task assignment to an agent.

Details from a Daybreak Test

‍

‍

Continue reading
About the author
Sam Lister
Specialist Security Researcher
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ