ブログ
/
Network
/
July 24, 2025

Untangling the web: Darktrace’s investigation of Scattered Spider’s evolving tactics

Learn about a recent Scattered Spider attack observed by Darktrace, comparing tactics with those seen in previous attacks. Widespread use of LOTL techniques alongside continued changes in TTPs such as their recent use of Ransomware-as-a-Service (RaaS) platforms can make it challenging for security teams to harden defenses.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Emma Foulger
Global Threat Research Operations Lead
Default blog image
24
Jul 2025

What is Scattered Spider?

Scattered Spider is a native English-speaking group, also referred to, or closely associated with, aliases such as UNC3944, Octo Tempest and Storm-0875. They are primarily financially motivated with a clear emphasis on leveraging social engineering, SIM swapping attacks, exploiting legitimate tooling as well as using Living-Off-the-Land (LOTL) techniques [1][2].

In recent years, Scattered Spider has been observed employing a shift in tactics, leveraging Ransomware-as-a-Service (RaaS) platforms in their attacks. This adoption reflects a shift toward more scalable attacks with a lower barrier to entry, allowing the group to carry out sophisticated ransomware attacks without the need to develop it themselves.

While RaaS offerings have been available for purchase on the Dark Web for several years, they have continued to grow in popularity, providing threat actors a way to cause significant impact to critical infrastructure and organizations without requiring highly technical capabilities [12].

This blog focuses on the group’s recent changes in tactics, techniques, and procedures (TTPs) reported by open-source intelligence (OSINT) and how TTPs in a recent Scattered Spider attack observed by Darktrace compare.

How has Scattered Spider been reported to operate?

First observed in 2022, Scattered Spider is known to target various industries globally including telecommunications, technology, financial services, and commercial facilities.

Overview of key TTPs

Scattered Spider has been known to utilize the following methods which cover multiple stages of the Cyber Kill Chain including initial access, lateral movement, evasion, persistence, and action on objective:

Social engineering [1]:

Impersonating staff via phone calls, SMS and Telegram messages; obtaining employee credentials (MITRE techniques T1598,T1656), multi-factor authentication (MFA) codes such as one-time passwords, or convincing employees to run commercial remote access tools enabling initial access (MITRE techniques T1204,T1219,T1566)

  • Phishing using specially crafted domains containing the victim name e.g. victimname-sso[.]com
  • MFA fatigue: sending repeated requests for MFA approval with the intention that the victim will eventually accept (MITRE technique T1621)

SIM swapping [1][3]:

  • Includes hijacking phone numbers to intercept 2FA codes
  • This involves the actor migrating the victim's mobile number to a new SIM card without legitimate authorization

Reconnaissance, lateral movement & command-and-control (C2) communication via use of legitimate tools:

  • Examples include Mimikatz, Ngrok, TeamViewer, and Pulseway [1]. A more recently reported example is Teleport [3].

Financial theft through their access to victim networks: Extortion via ransomware, data theft (MITRE technique T1657) [1]

Bring Your Own Vulnerable Driver (BYOVD) techniques [4]:

  • Exploiting vulnerable drivers to evade detection from Endpoint Detection and Response (EDR) security products (MITRE technique T1068) frequently used against Windows devices.

LOTL techniques

LOTL techniques are also closely associated with Scattered Spider actors once they have gained initial access; historically this has allowed them to evade detection until impact starts to be felt. It also means that specific TTPs may vary from case-to-case, making it harder for security teams to prepare and harden defences against the group.

Prominent Scattered Spider attacks over the years

While attribution is sometimes unconfirmed, Scattered Spider have been linked with a number of highly publicized attacks since 2022.

Smishing attacks on Twilio: In August 2022 the group conducted multiple social engineering-based attacks. One example was an SMS phishing (smishing) attack against the cloud communication platform Twilio, which led to the compromise of employee accounts, allowing actors to access internal systems and ultimately target Twilio customers [5][6].

Phishing and social engineering against MailChimp: Another case involved a phishing and social engineering attack against MailChimp. After gaining access to internal systems through compromised employee accounts the group conducted further attacks specifically targeting MailChimp users within cryptocurrency and finance industries [5][7].

Social engineering against Riot Games: In January 2023, the group was linked with an attack on video game developer Riot Games where social engineering was once again used to access internal systems. This time, the attackers exfiltrated game source code before sending a ransom note [8][9].

Attack on Caesars & MGM: In September 2023, Scattered Spider was linked with attacked on Caesars Entertainment and MGM Resorts International, two of the largest casino and gambling companies in the United States. It was reported that the group gathered nearly six terabytes of stolen data from the hotels and casinos, including sensitive information of guests, and made use of the RaaS strain BlackCat [10].

Ransomware against Marks & Spencer: More recently, in April 2025, the group has also been linked to the alleged ransomware incident against the UK-based retailer Marks & Spencer (M&S) making use of the DragonForce RaaS [11].

How a recent attack observed by Darktrace compares

In May 2025, Darktrace observed a Scattered Spider attack affecting one of its customers. While initial access in this attack fell outside of Darktrace’s visibility, information from the affected customer suggests similar social engineering techniques involving abuse of the customer’s helpdesk and voice phishing (vishing) were used for reconnaissance.

Initial access

It is believed the threat actor took advantage of the customer’s third-party Software-as-a-Service (SaaS) applications, such as Salesforce during the attack.

Such applications are a prime target for data exfiltration due to the sensitive data they hold; customer, personnel, and business data can all prove useful in enabling further access into target networks.

Techniques used by Scattered Spider following initial access to a victim network tend to vary more widely and so details are sparser within OSINT. However, Darktrace is able to provide some additional insight into what techniques were used in this specific case, based on observed activity and subsequent investigation by its Threat Research team.

Lateral movement

Following initial access to the customer’s network, the threat actor was able to pivot into the customer’s Virtual Desktop Infrastructure (VDI) environment.

Darktrace observed the threat actor spinning up new virtual machines and activating cloud inventory management tools to enable discovery of targets for lateral movement.

In some cases, these virtual machines were not monitored or managed by the customer’s security tools, allowing the threat actor to make use of additional tooling such as AnyDesk which may otherwise have been blocked.

Tooling in further stages of the attack sometimes overlapped with previous OSINT reporting on Scattered Spider, with anomalous use of Ngrok and Teleport observed by Darktrace, likely representing C2 communication. Additional tooling was also seen being used on the virtual machines, such as Pastebin.
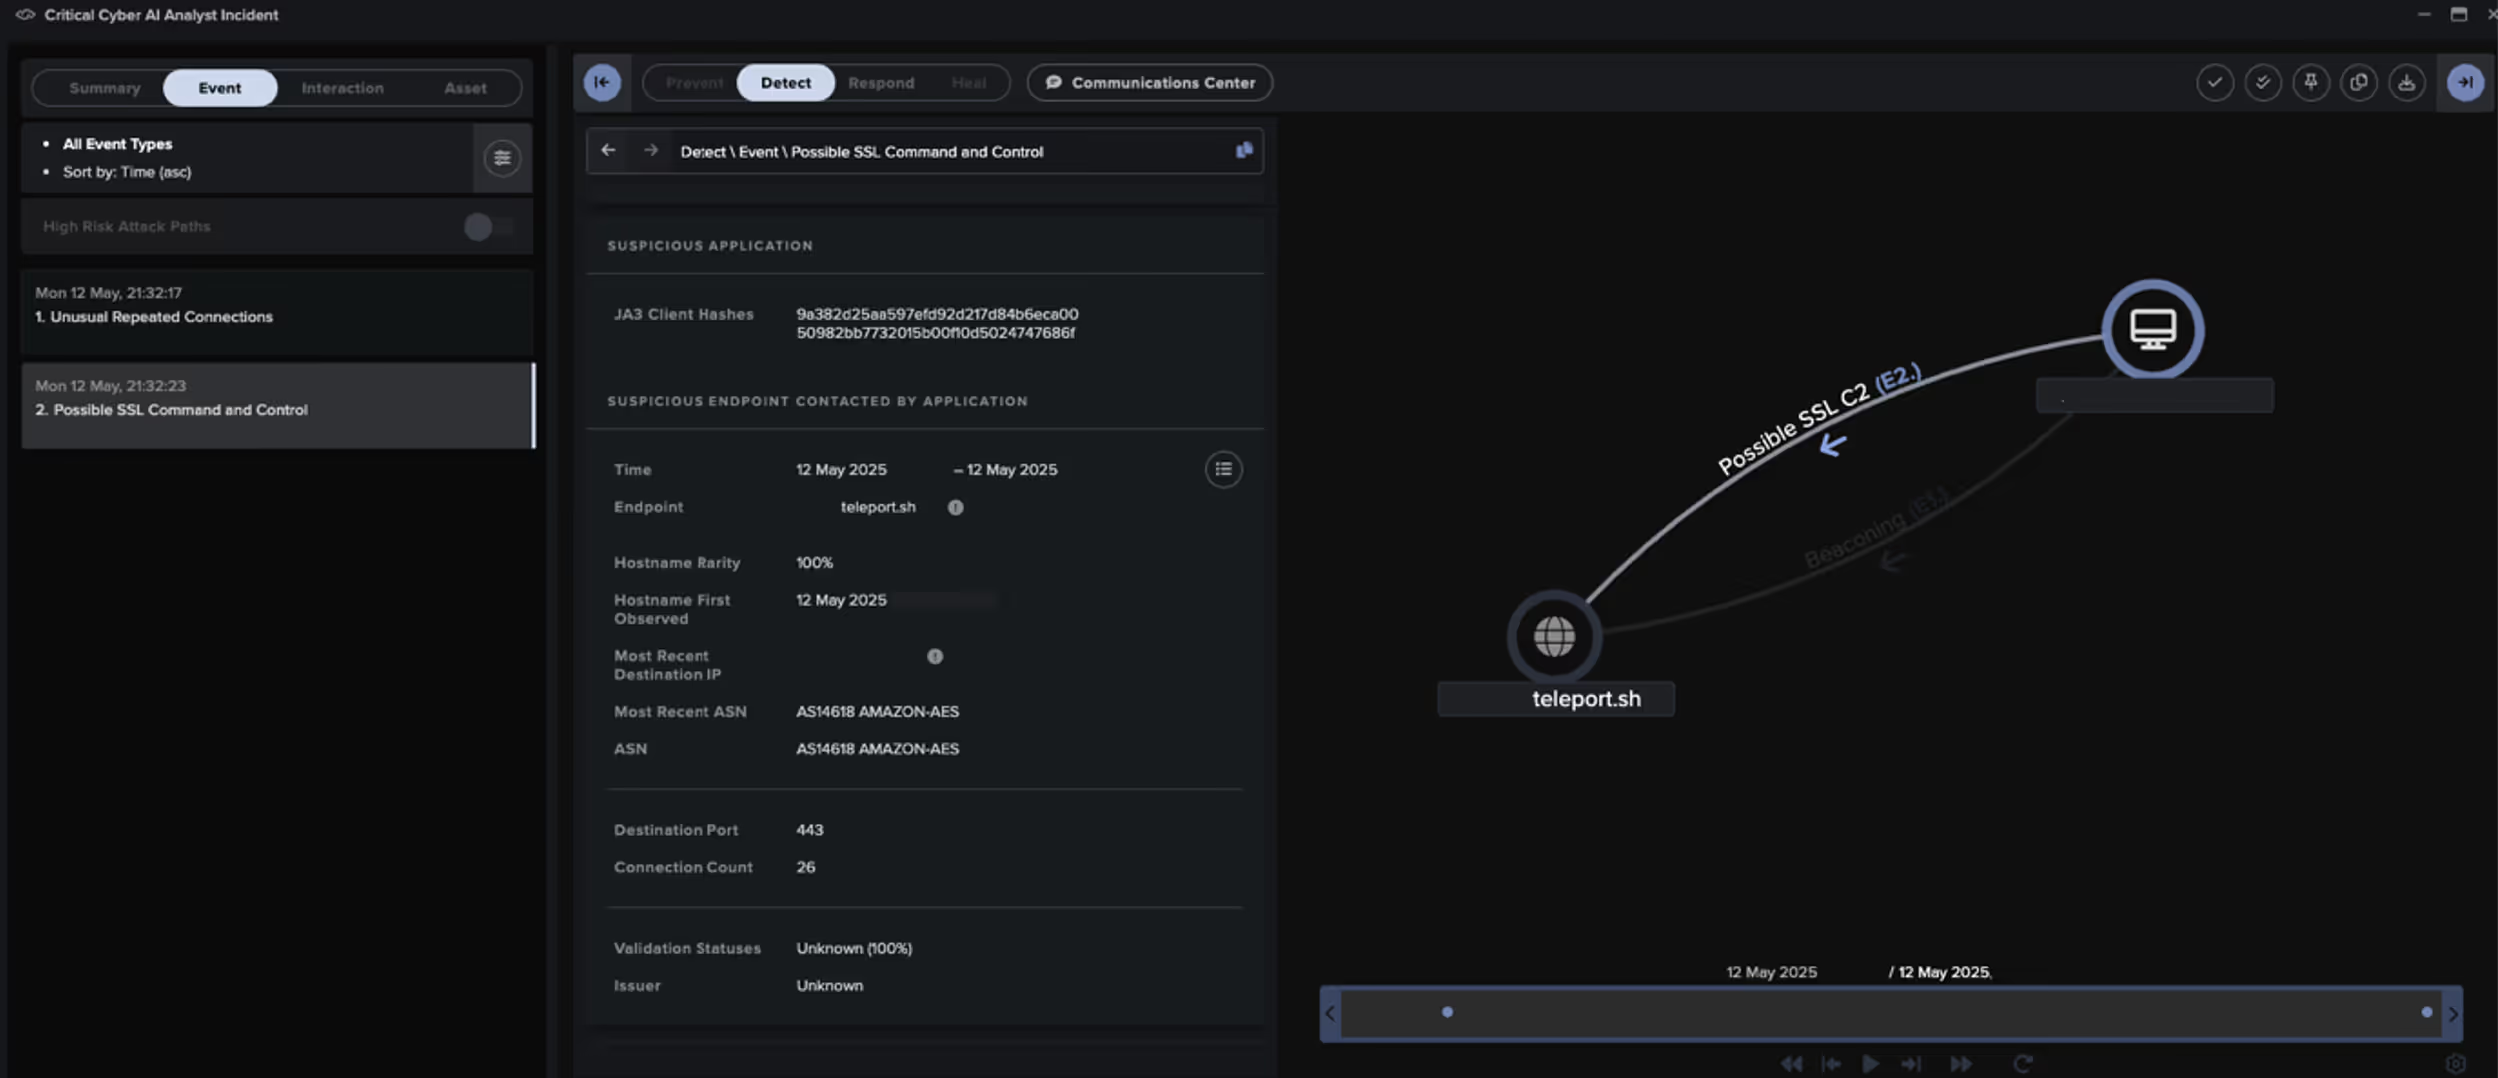
 Cyber AI Analyst’s detection of C2 beaconing to a teleport endpoint with hostname CUSTOMERNAME.teleport[.]sh, likely in an attempt to conceal the traffic.
Figure 1: Cyber AI Analyst’s detection of C2 beaconing to a teleport endpoint with hostname CUSTOMERNAME.teleport[.]sh, likely in an attempt to conceal the traffic.

Leveraging LOTL techniques

Alongside use of third-party tools that may have been unexpected on the network, various LOTL techniques were observed during the incident; this primarily involved the abuse of standard network protocols such as:

  • SAMR requests to alter Active Directory account details
  • Lateral movement over RDP and SSH
  • Data collection over LDAP and SSH

Coordinated exfiltration activity linked through AI-driven analysis

Multiple methods of exfiltration were observed following internal data collection. This included SSH transfers to IPs associated with Vultr, alongside significant uploads to an Amazon S3 bucket.

While connections to this endpoint were not deemed unusual for the network at this stage due to the volume of traffic seen, Darktrace’s Cyber AI Analyst was still able to identify the suspiciousness of this behavior and launched an investigation into the activity.

Cyber AI Analyst successfully correlated seemingly unrelated internal download and external upload activity across multiple devices into a single, broader incident for the customer’s security team to review.

Cyber AI Analyst Incident summary showing a clear outline of the observed activity, including affected devices and the anomalous behaviors detected.
Figure 2: Cyber AI Analyst Incident summary showing a clear outline of the observed activity, including affected devices and the anomalous behaviors detected.
Figure 3: Cyber AI Analyst’s detection of internal data downloads and subsequent external uploads to an Amazon S3 bucket.

Exfiltration and response

Unfortunately, as Darktrace was not configured in Autonomous Response mode at the time, the attack was able to proceed without interruption, ultimately escalating to the point of data exfiltration.

Despite this, Darktrace was still able to recommend several Autonomous Response actions, aimed at containing the attack by blocking the internal data-gathering activity and the subsequent data exfiltration connections.

These actions required manual approval by the customer’s security team and as shown in Figure 3, at least one of the recommended actions was subsequently approved.

Had Darktrace been enabled in Autonomous Response mode, these measures would have been applied immediately, effectively halting the data exfiltration attempts.
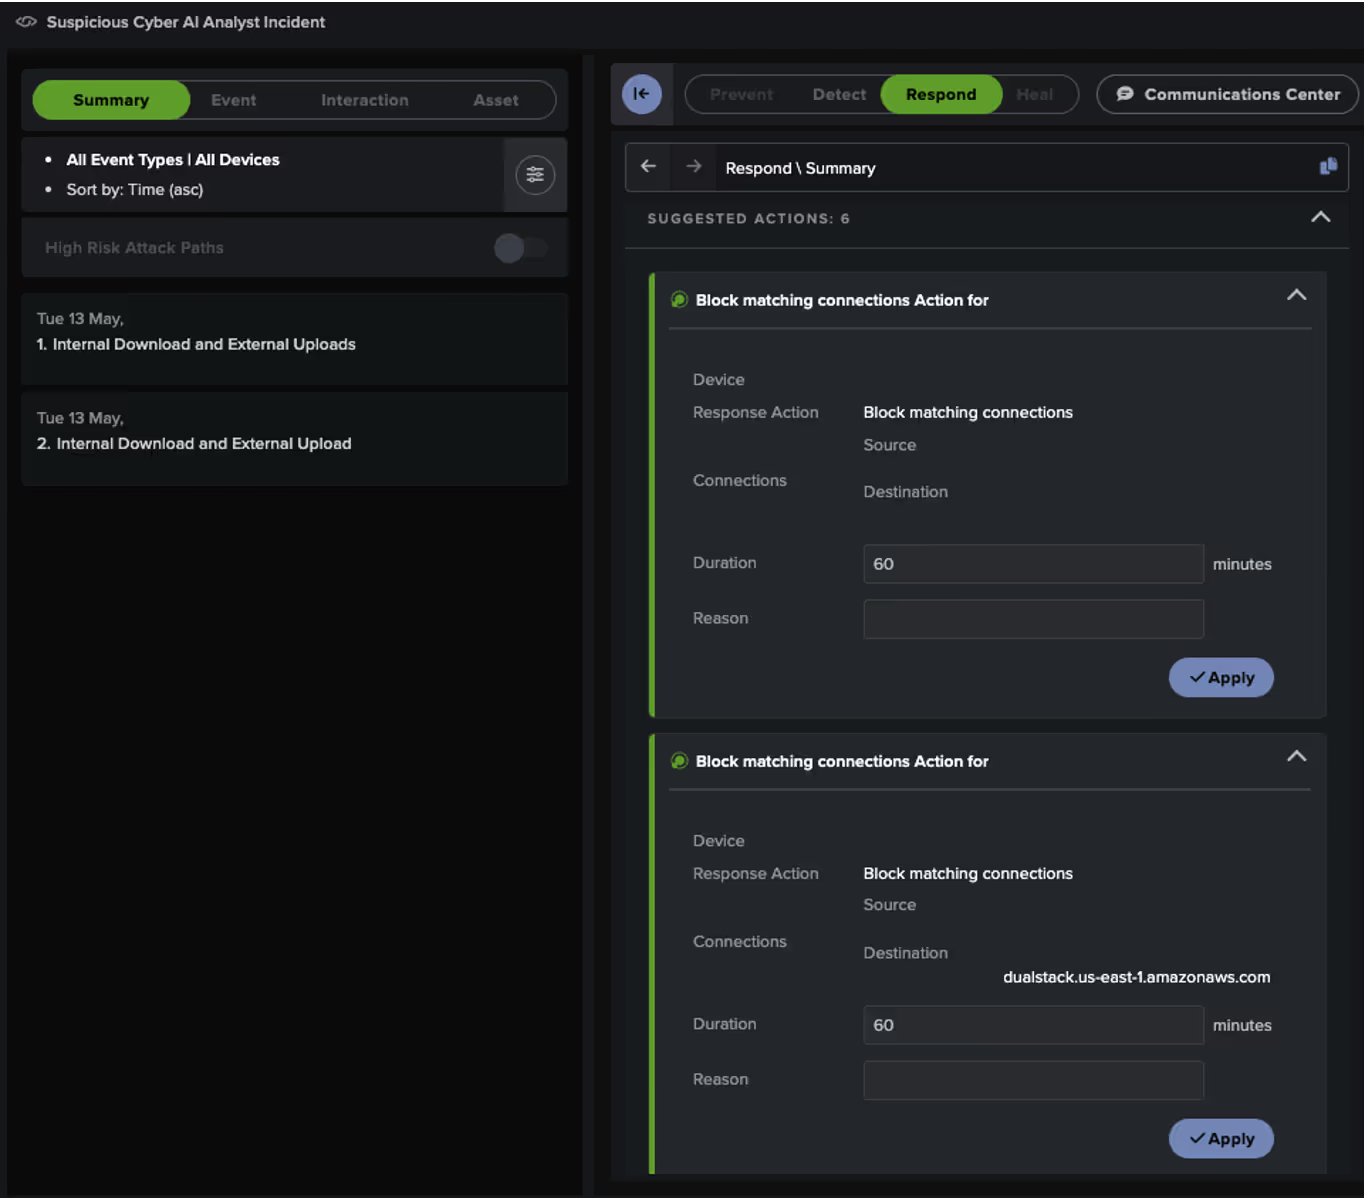
Further recommendations for Autonomous Response actions in Darktrace‘s Incident Interface, with surgical response targeting both the internal data collection and subsequent exfiltration.
Figure 4: Further recommendations for Autonomous Response actions in Darktrace‘s Incident Interface, with surgical response targeting both the internal data collection and subsequent exfiltration.

Scattered Spider’s use of RaaS

In this recent Scattered Spider incident observed by Darktrace, exfiltration appears to have been the primary impact. While no signs of ransomware deployment were observed here, it is possible that this was the threat actors’ original intent, consistent with other recent Scattered Spider attacks involving RaaS platforms like DragonForce.

DragonForce emerged towards the end of 2023, operating by offering their platform and capabilities on a wide scale. They also launched a program which offered their affiliates 80% of the eventual ransom, along with tools for further automation and attack management [13].

The rise of RaaS and attacker customization is fragmenting TTPs and indicators, making it harder for security teams to anticipate and defend against each unique intrusion.

While DragonForce appears to be the latest RaaS used by Scattered Spider, it is not the first, showcasing the ongoing evolution of tactics used the group.

In addition, the BlackCat RaaS strain was reportedly used by Scattered Spider for their attacks against Caesars Entertainment and MGM Resorts International [10].

In 2024 the group was also seen making use of additional RaaS strains; RansomHub and Qilin [15].

What security teams and CISOs can do to defend against Scattered Spider

The ongoing changes in tactics used by Scattered Spider, reliance on LOTL techniques, and continued adoption of evolving RaaS providers like DragonForce make it harder for organizations and their security teams to prepare their defenses against such attacks.

CISOs and security teams should implement best practices such as MFA, Single Sign-On (SSO), notifications for suspicious logins, forward logging, ethical phishing tests.

Also, given Scattered Spider’s heavy focus on social engineering, and at times using their native English fluency to their advantage, it is critical to IT and help desk teams are reminded they are possible targets.

Beyond social engineering, the threat actor is also adept at taking advantage of third-party SaaS applications in use by victims to harvest common SaaS data, such as PII and configuration data, that enable the threat actor to take on multiple identities across different domains.

With Darktrace’s Self-Learning AI, anomaly-based detection, and Autonomous Response inhibitors, businesses can halt malicious activities in real-time, whether attackers are using known TTPs or entirely new ones. Offerings such as Darktrace /Attack Surface Management enable security teams to proactively identify signs of malicious activity before it can cause an impact, while more generally Darktrace’s ActiveAI Security Platform can provide a comprehensive view of an organization’s digital estate across multiple domains.

Credit to Justin Torres (Senior Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Zaki Al-Dhamari (Cyber Analyst), Nathaniel Jones (VP, Security & AI Strategy, FCISO), and Ryan Traill (Analyst Content Lead)

---------------------

The information provided in this blog post is for general informational purposes only and is provided "as is" without any representations or warranties, express or implied. While Darktrace makes reasonable efforts to ensure the accuracy and timeliness of the content related to cybersecurity threats such as Scattered Spider, we make no warranties or guarantees regarding the completeness, reliability, or suitability of the information for any purpose.

This blog post does not constitute professional cybersecurity advice, and should not be relied upon as such. Readers should seek guidance from qualified cybersecurity professionals or legal counsel before making any decisions or taking any actions based on the content herein.

No warranty of any kind, whether express or implied, including, but not limited to, warranties of performance, merchantability, fitness for a particular purpose, or non-infringement, is given with respect to the contents of this post.

Darktrace expressly disclaims any liability for any loss or damage arising from reliance on the information contained in this blog.

Appendices

References

[1] https://www.cisa.gov/news-events/cybersecurity-advisories/aa23-320a

[2] https://attack.mitre.org/groups/G1015/

[3] https://www.rapid7.com/blog/post/scattered-spider-rapid7-insights-observations-and-recommendations/

[4] https://www.crowdstrike.com/en-us/blog/scattered-spider-attempts-to-avoid-detection-with-bring-your-own-vulnerable-driver-tactic/

[5] https://krebsonsecurity.com/2024/06/alleged-boss-of-scattered-spider-hacking-group-arrested/?web_view=true

[6] https://www.cxtoday.com/crm/uk-teenager-accused-of-hacking-twilio-lastpass-mailchimp-arrested/

[7] https://mailchimp.com/newsroom/august-2022-security-incident/

[8] https://techcrunch.com/2023/02/02/0ktapus-hackers-are-back-and-targeting-tech-and-gaming-companies-says-leaked-report/

[9] https://www.pcmag.com/news/hackers-behind-riot-games-breach-stole-league-of-legends-source-code

[10] https://www.bbrown.com/us/insight/a-look-back-at-the-mgm-and-caesars-incident/

[11] https://cyberresilience.com/threatonomics/scattered-spider-uk-retail-attacks/

[12] https://www.crowdstrike.com/en-us/cybersecurity-101/ransomware/ransomware-as-a-service-raas/

[13] https://www.group-ib.com/blog/dragonforce-ransomware/
[14] https://blackpointcyber.com/wp-content/uploads/2024/11/DragonForce.pdf
[15] https://x.com/MsftSecIntel/status/1812932749314978191?lang=en

Select MITRE tactics associated with Scattered Spider

Tactic – Technique – Technique Name

Reconnaissance - T1598 -   Phishing for Information

Initial Access - T1566 – Phishing

Execution - T1204 - User Execution

Privilege Escalation - T1068 - Exploitation for Privilege Escalation

Defense Evasion - T1656 - Impersonation

Credential Access - T1621 - Multi-Factor Authentication Request Generation

Lateral Movement - T1021 - Remote Services

Command and Control - T1102 - Web Service

Command and Control - T1219 - Remote Access Tools

Command and Control - T1572 - Protocol Tunneling

Exfiltration - T1567 - Exfiltration Over Web Service

Impact - T1657 - Financial Theft

Select MITRE tactics associated with DragonForce

Tactic – Technique – Technique Name

Initial Access, Defense Evasion, Persistence, Privilege Escalation - T1078 - Valid Accounts

Initial Access, Persistence - T1133 - External Remote Services

Initial Access - T1190 - Exploit Public-Facing Application

Initial Access - T1566 – Phishing

Execution - T1047 - Windows Management Instrumentation

Privilege Escalation - T1068 - Exploitation for Privilege Escalation

Lateral Movement - T1021 - Remote Services

Impact - T1486 - Data Encrypted for Impact

Impact - T1657 - Financial Theft

Select Darktrace models

Compliance / Internet Facing RDP Server

Compliance / Incoming Remote Access Tool

Compliance / Remote Management Tool on Server

Anomalous File / Internet Facing System File Download

Anomalous Server Activity/ New User Agent from Internet Facing System

Anomalous Connection / Callback on Web Facing Device

Device / Internet Facing System with High Priority Alert

Anomalous Connection / Unusual Admin RDP

Anomalous Connection / High Priority DRSGetNCChanges

Anomalous Connection / Unusual Internal SSH

Anomalous Connection / Active Remote Desktop Tunnel

Compliance / Pastebin

Anomalous Connection / Possible Tunnelling to Rare Endpoint

Compromise / Beaconing Activity to External Rare

Device / Long Agent Connection to New Endpoint

Compromise / SSH to Rare External AWS

Compliance / SSH to Rare External Destination

Anomalous Server Activity / Outgoing from Server

Anomalous Connection / Large Volume of LDAP Download

Unusual Activity / Internal Data Transfer on New Device

Anomalous Connection / Download and Upload

Unusual Activity / Enhanced Unusual External Data Transfer

Compromise / Ransomware/Suspicious SMB Activity

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Emma Foulger
Global Threat Research Operations Lead

More in this series

No items found.

Blog

/

AI

/

October 5, 2026

AI-Assisted Attacks Still Leave a Behavioral Trace  

Default blog imageDefault blog image

Key Insights

  • Darktrace identified behavioral indicators associated with two campaigns linked to AI-assisted threat activity, highlighting the growing role of AI in modern cyber-attacks.
  • Observed activity involved suspicious WebDAV file transfers, disguised executable downloads, beaconing to rare infrastructure, unusual process execution, and communications with C2 infrastructure linked to active intrusion campaigns.

Introduction

Just as organizations are incorporating AI into their operations to take advantage of its benefits, threat actors are doing the same, creating new challenges for defenders.

Much of the discussion around AI risk has focused on the expanding attack surface created by AI systems within organizations. These systems are often granted privileged access and heightened permissions to carry out their duties, introducing new security risks and unintended consequences.

At the same time, threat actors are learning to leverage AI to enable malicious activities such as vulnerability discovery, exploit creation, and progressing through the Cyber Kill Chain more quickly. By accelerating development, adaptation, and scaling, AI enables attackers to operate more efficiently while making some capabilities more accessible to less skilled operators.

Whether AI is the target or the enabler, the resulting activity still manifests through networks, identities, endpoints and cloud services. Those interactions create observable signals that defenders can investigate, regardless of how the attack was developed.

AI as part of the attacker’s workflow

Darktrace has previously documented how threat actors are increasingly incorporating AI into offensive operations [1]. Two recent investigations from open-source intelligence (OSINT) illustrate this. In both cases, researchers identified the role of AI within malicious operations. Separately, Darktrace detected activity in customer environments that aligned with the infrastructure and techniques reported in those campaigns. These perspectives provide a view of both attacker workflow and operational consequences.

Although AI played different roles in each campaign, it did not remove the need for the attackers to interact with their targets. Payloads still had to be delivered, processes executed, and command-and-control (C2) connections established, creating behavioral anomalies that Darktrace was able to identify.

‍

Case 1: A Mexican government impersonation campaign with LLM-assisted malware development

Rapid7 reported on a malware delivery operation that used generative AI to assist development, testing, documentation and refinement of attacker infrastructure. Between May and June 2026, Darktrace similarly observed two chains of suspicious activity across customer environments in the Americas that exhibited clear similarities in behavior.

In both cases Darktrace observed:

  • WebDAV communication with onedrive[.]cv·138.124.123[.]87, retrieving a file from the path /Downloads/CURP/
  • Transfer of a masqueraded .scr executable
  • Subsequent communication with google.services[.]ug·77.110.127[.]205 over unusual high ports
  • Additional Darktrace detections correlating the unusual behavior seen spanning payload delivery and C2 communication
  • Darktrace’s Autonomous Response capability alerted across multiple stages of the attack

The infrastructure and behavior observed by Darktrace closely aligned with a campaign reported by Rapid7, in which a WebDAV malware delivery environment was exposed. Rapid7 assessed that threat actors had used generative AI to support the development, testing, documentation and refinement of the operation. The observed activity also aligned with reporting on a campaign in which impersonation of Mexico’s government Unique Population Registry Code (CURP) identity-record service led to delivery of PureRAT, a .NET-based information stealer and remote access trojan (RAT) [2]. The infrastructure overlap and consistent behavioural sequence provides strong alignment and offers a view of how an AI-assisted development pipeline ultimately manifested inside target environments.

Case 2: A suspected China-linked intrusion campaign with AI-assisted automation

In July 2026, Hunt.io published research into a suspected China-based intrusion operation targeting government and financial services organizations [3]. Material recovered from exposed attacker infrastructure by Hunt.io indicated that Claude Code and DeepSeek-v4-pro were being used as active components of the attacker’s workflow. According to the research, the models supported activities including attack reasoning, script generation, execution, exploit adaptation, and phishing-page development.

The investigation identified 192.229.115[.]229 and 192.229.115[.]230 as infrastructure associated with suspected TencShell operations and a possible second C2 framework known as Gshell [3].

Darktrace identified likely related activity within a financial services customer environment involving a newly observed laptop running the Windows 11 Pro operating system. Over a six-day period in July, the device made repeated outbound connections to 192.229.115[.]229 over port 8083.

Darktrace recognized the destination was highly rare for the environment, and the connectivity exhibited beaconing characteristics. During the same timeframe, Darktrace also identified suspicious process behavior associated with process chains involving svchost.exe and cmd.exe. The device repeatedly communicated with infrastructure identified in the Hunt.io research while exhibiting beaconing characteristics and suspicious process activity, strengthening the assessment that the activity likely was associated with the same operation.

Unlike many previous examples of AI-assisted cybercrime, the Hunt.io investigation provided rare visibility into how large language models were being incorporated directly into operational workflows rather than being used solely for content generation. Darktrace, meanwhile, observed how activity associated with that operation ultimately manifested inside a target environment, providing a complementary view of its operational impact.

Operational consequences of AI-assisted attacks

These investigations provide two complementary perspectives on AI-assisted cyber operations. OSINT research revealed how AI was incorporated into attacker workflows, while Darktrace observed the resulting activity within customer environments.

Although AI played different roles in each campaign, it did not remove the need for attackers to interact with their targets, deliver payloads, execute processes, and communicate with C2, all of which generated observable signals.

In these cases, Darktrace identified suspicious file delivery, unusual process behavior, beaconing activity, and communication with rare external infrastructure that aligned with campaigns later linked to AI-assisted operations. While AI may influence how attacks are developed, adapted, and scaled, it does not make them operationally invisible.

For defenders, the broader lesson extends beyond these specific campaigns. As AI becomes increasingly embedded within both enterprise operations and attacker workflows, understanding what a model was asked to do is often less important than understanding the actions it ultimately took and the consequences those actions produced. Whether the actor is human, AI-assisted, or increasingly autonomous, activity still manifests through identities, endpoints, applications, cloud services and network infrastructure.

Credit to Angel Arribas Lopez (Associate Principal Cyber Analyst), Emma Foulger (Global Threat Research Operations Lead), Nathaniel Jones, SVP Global Threat Intelligence
Edited by Ryan Traill (Content Manager)

‍

Appendices

Darktrace Model Detections

Case 1

Anomalous File / Masqueraded File Transfer from New External Endpoint

Anomalous File / Script from Rare External Location

Anomalous File / EXE from Rare External Location

Anomalous File / Script and EXE from Rare External

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Anomalous Connection / Rare External SSL Self-Signed

Compromise / New or Repeated to Unusual SSL Port

Compromise / Large Number of Suspicious Failed Connections

Device / Initial Attack Chain Activity

Antigena / Network / External Threat::Antigena Suspicious File Block

Antigena / Network / Significant Anomaly::Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly::Antigena Controlled and Model Alert

Antigena / Network / External Threat::Antigena File then New Outbound Block

Antigena / Network / Significant Anomaly::Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly::Antigena Alerts Over Time Block

Case 2

Anomalous Connection / Multiple Failed Connections to Rare Endpoint

Compromise / High Volume of Connections with Beacon Score

Compromise / Large Number of Suspicious Failed Connections

‍

Indicators of Compromise (IoCs)

‍

Case 1

                                                                                                                                                                                                                                                 
IoCTypeDescription + Confidence
onedrive[.]cvHostnameLikely C2 server
138.124.123[.]87IP AddressPossible C2 server
hXXp://onedrive[.]cv/Downloads/CURP/ReportFinal.%E2%80%AE%E1%BA%9D%D4%81%EF%BD%90.scrURIPossible payload
google.services[.]ugHostnameLikely C2 server
77.110.127[.]205IP AddressLikely C2 server
google.services[.]ug:57666Hostname + PortLikely C2 communication
google.services[.]ug:57888Hostname + PortLikely C2 communication
google.services[.]ug:56001Hostname + PortLikely C2 communication

‍

Case 2

IoC Type Description + Confidence
192.229.115[.]229 IP Address Likely C2 communication
Continue reading
About the author
Angel Arribas Lopez
Associate Principal Cyber Analyst

Blog

/

Network

/

October 5, 2026

A Chain Reaction: Blockchain-Hosted Infostealer Campaign Targets Windows and macOS

Default blog imageDefault blog image

Key Insights

  • Darktrace detected a blockchain-hosted infostealer campaign targeting Windows and macOS devices across multiple customer environments.
  • The campaign combined ClickFix social engineering with trusted services and decentralized blockchain infrastructure to support malware delivery and C2 activity.
  • Compromised devices were observed connecting to rare and unusual external endpoints, including DGA C2 domains, blockchain-related endpoints, and cryptocurrency mining infrastructure.
  • The activity was associated with information-stealing malware strains including Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, Vidar, and Phexia.
  • Darktrace identified anomalous device behavior, beaconing patterns, rare external connections, cryptomining activity, and suspicious TLS/SSL communications without relying solely on prior knowledge or static indicators of compromise.
  • The campaign highlights how attackers are increasingly using legitimate and decentralized infrastructure to make detection, disruption, and attribution more challenging for defenders.

The Infostealer Ecosystem

The information stealer malware ecosystem continues to grow in value for threat actors across the digital threat landscape. Infostealers are increasingly delivered through Malware-as-a-Service (MaaS) operating models, distributed through affiliate networks, and designed to withstand infrastructure takedowns. This resilience was demonstrated by the recent takedown of Lumma Stealer malicious domains by Microsoft’s Digital Crimes Unit (DCU) [1].

Infostealers are used to gather and exfiltrate sensitive information, including non-human identity (NHI) data, from compromised systems across cloud, Software-as-a-Service (SaaS), Virtual Private Network (VPN), and development environments. They can also support ransomware operations by expanding the credentials and access paths available to threat actors, contributing to the high volume of identity-based attacks observed across the broader threat landscape [2][3].

Darktrace’s Observations of ClickFix and Infostealers

Throughout 2026, Darktrace has observed multiple campaigns using ClickFix social engineering to trick users into carrying out malicious actions and downloading initial payloads, including information stealers. More recently, Darktrace’s Threat Research team identified a specific ClickFix campaign involving a blockchain-hosted infostealer targeting Windows and macOS devices.

Darktrace identified affected customer environments across Europe, the United States, Asia, and the Middle East where blockchain-hosted infostealer malware appears to have been delivered to compromised systems following likely ClickFix-driven initial access. Darktrace investigated the activity and found that decentralized blockchain infrastructure, alongside widely trusted legitimate services, was used to support malware delivery and information theft across Windows and macOS systems.

Following initial access, compromised systems established C2 communication, with C2 configuration and payloads hosted on public blockchain infrastructure. The ultimate objective appears to be credential and cryptocurrency theft through the deployment of information stealers such as Atomic macOS Stealer (AMOS), Lumma, Rhadamanthys, and Vidar [5][6][7].

Darktrace’s Investigation

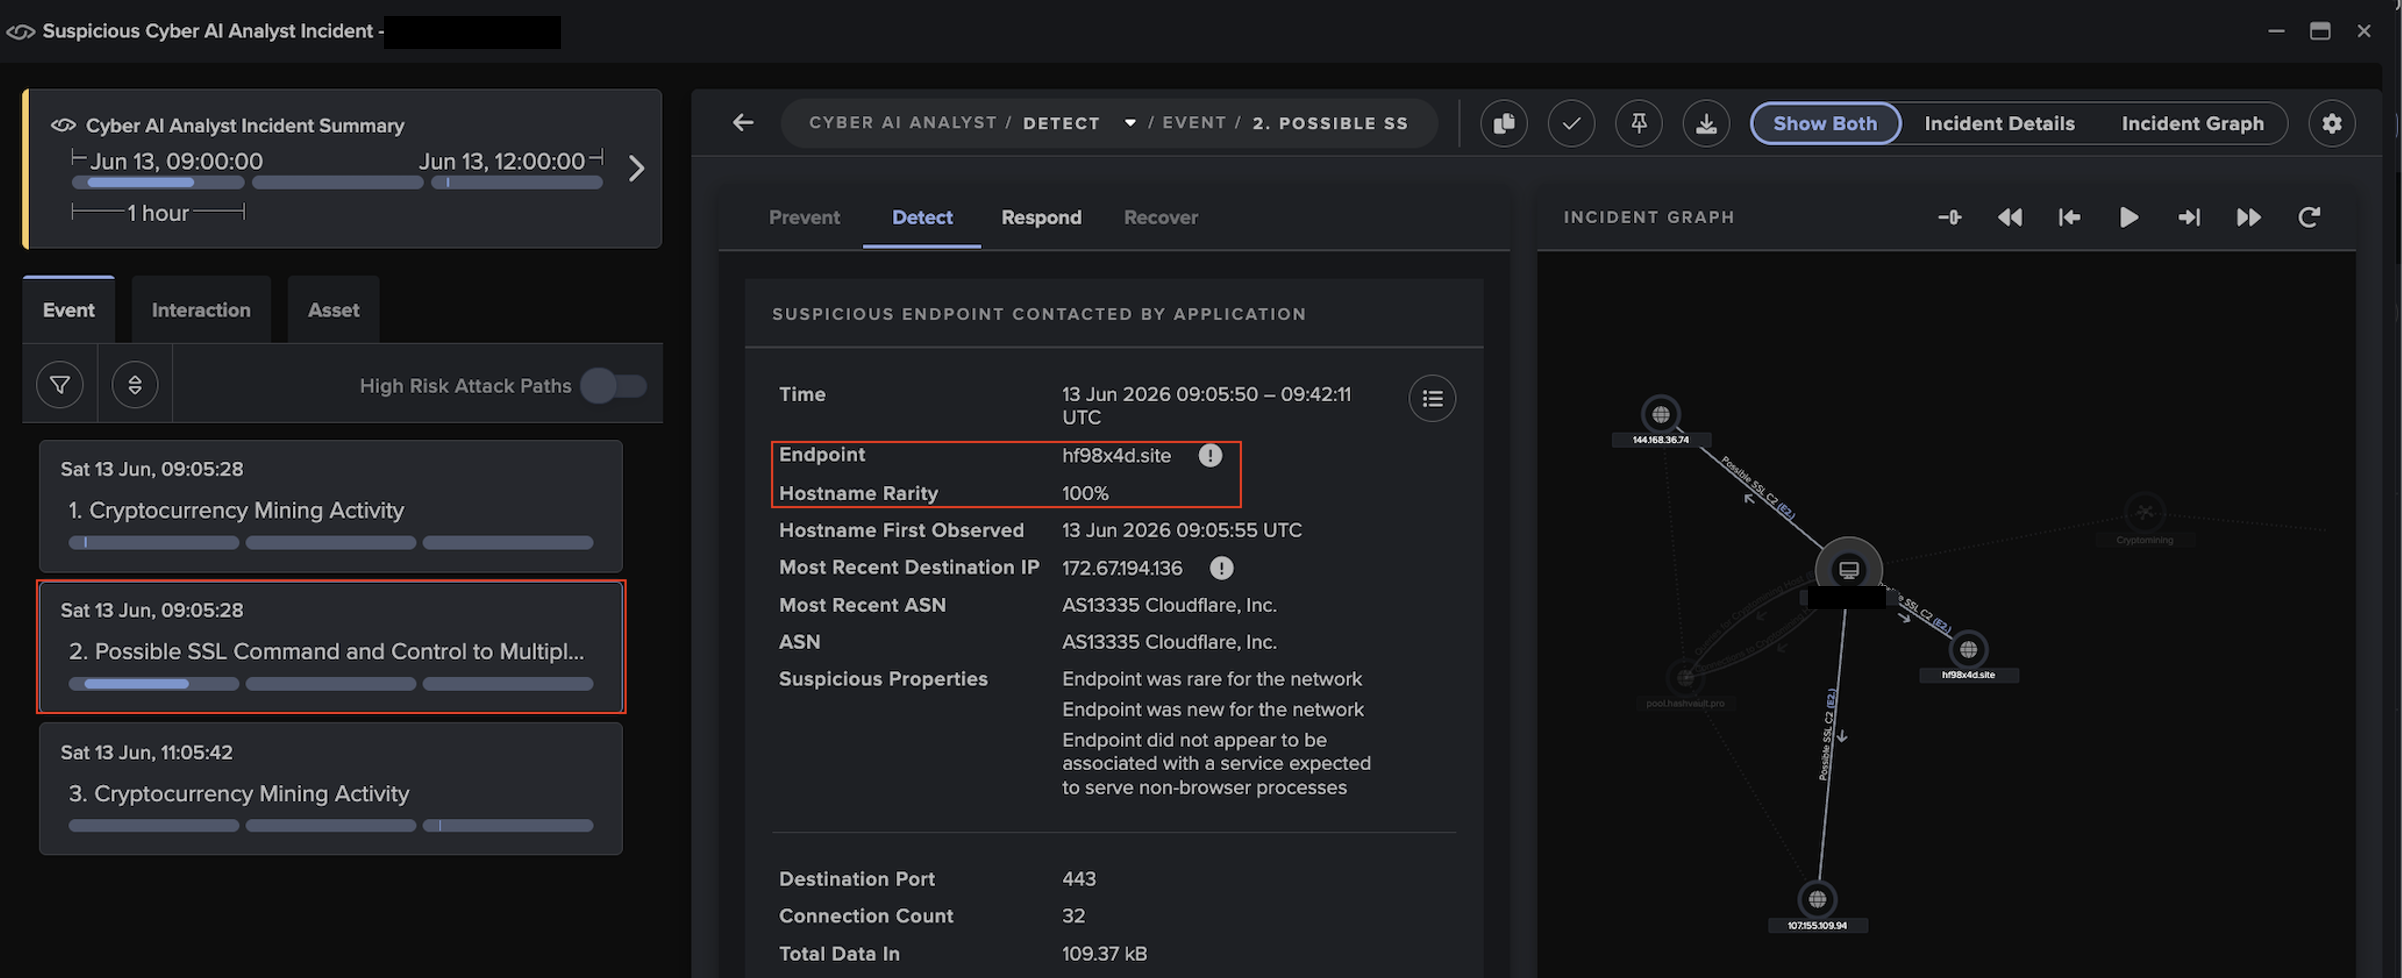
Affected devices across the Darktrace customer base were observed making outbound connections to rare external endpoints in patterns consistent with beaconing and C2 activity. Darktrace primarily detected devices making repeated connections to algorithmically generated domains (DGA) such as hf98x4d[.]site [8]. In many cases, these domains were linked through open-source intelligence (OSINT) to information-stealing malware families including AMOS and Phexia [5][6][7][8][9].

In multiple cases, devices were also observed connecting to blockchain-related endpoints, such as polygon[.]drpc[.]org, as well as legitimate public services, including GitHub. The use of decentralized blockchain infrastructure and trusted services such as GitHub to facilitate malware distribution and C2 activity can make disruption and attribution significantly more difficult for defenders.

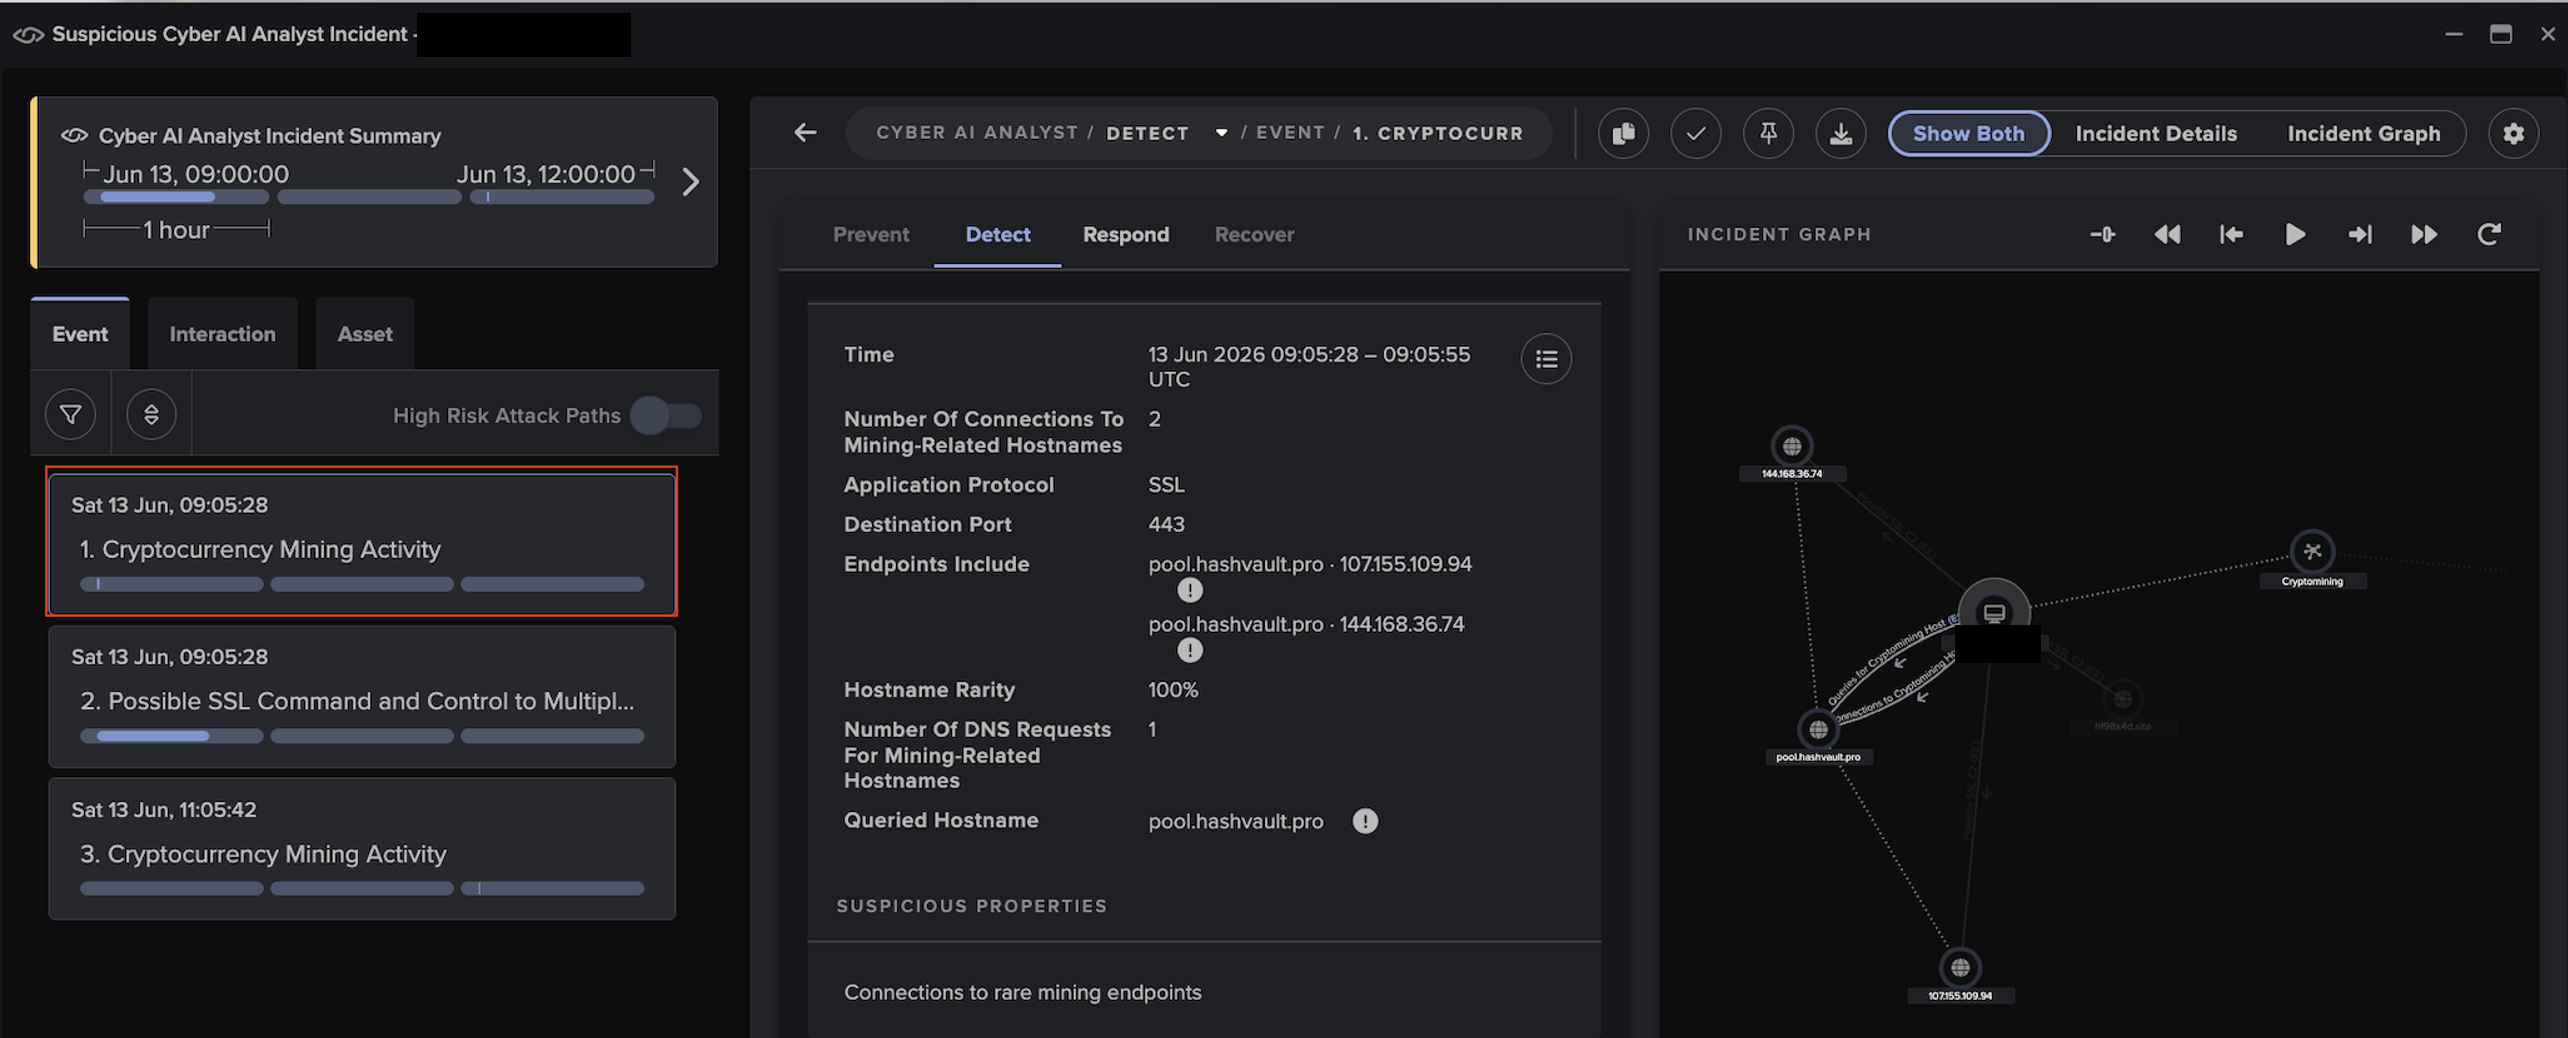
Darktrace also detected a significant proportion of impacted devices making outbound connections to cryptocurrency mining infrastructure associated with the legitimate open-source XMRig mining software and the HashVault mining pool, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, which were abused by the attackers, indicating, including pool.hashvault[.]pro and donate[.]ssl[.]xmrig[.]com, indicating active cryptomining on compromised systems.

In one case, mining activity was observed before and during connections to the DGA endpoint hf98x4d[.]site. Due to its highly anomalous nature, Darktrace's Real-Time AI Analyst autonomously investigated the activity as it occurred, correlating the two events into a single cryptocurrency mining incident and providing comprehensive visibility into the broader attack.

‍

Figure 1: Real-Time AI Analyst investigation of suspicious SSL and C2 communications with hf98x4d[.]site over port 443.

‍

Figure 2: Real-Time AI Analyst investigation into cryptocurrency mining activity involving pool[.]hashvault[.]pro over SSL on port 443.

‍

Around the same time, Darktrace identified the same device initiating connections to the GitHub endpoint release-assets[.]githubusercontent[.]com while continuing to make repeated connections to hf98x4d[.]site.

‍

Figure 3: Darktrace's detection of an affected device connecting to a GitHub endpoint between repeated connections to the anomalous external endpoint hf98x4d[.]site.

On the network of another customer, Darktrace observed an affected device making highly unusual outbound connections consistent with beaconing activity. The device initiated multiple connections over port 443 to the external hostname polygon[.]drpc[.]org. According to OSINT, this hostname is a Remote Procedure Call (RPC) endpoint provided by dRPC, a legitimate service enabling decentralized applications (dApps), cryptocurrency wallets, and developer tools to interact with the Polygon blockchain [10].

The same device was later observed making repeated TLS/SSL connections to the previously mentioned DGA C2 domain. In addition, it made outbound connections to the external IP 195.242.214[.]34 over destination port 51820, an endpoint associated with the ProtonVPN service. Collectively, these connections to blockchain-related infrastructure, the DGA C2 domain, and ProtonVPN-associated infrastructure suggested the device had been affected by the campaign.

Conclusion

This campaign demonstrates how attackers can combine ClickFix social engineering with trusted services and decentralized blockchain infrastructure to create a resilient, cross-platform malware delivery chain. By using services such as GitHub alongside blockchain RPC endpoints and rapidly replaceable DGA domains, the activity can blend into legitimate traffic while making infrastructure disruption and attribution more difficult.

For defenders, it’s a reminder that trusted infrastructure does not automatically mean trusted activity. Security teams should look for the behaviors surrounding these connections, including unusual outbound communication, repeated beaconing, unexpected access to blockchain services, suspicious TLS/SSL activity and cryptomining. In this campaign, Darktrace identified and correlated these deviations without depending solely on previously known indicators, providing visibility as affected devices moved between legitimate services, decentralized infrastructure and malicious C2 endpoints

Credit to Nahisha Nobregas (Associate Principal Cyber Analyst), Manoel Kadja (Senior Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace Model Detections

▪ Compromise / Beaconing Activity To External Rare

▪ Compromise / Beacon to Young Endpoint

▪ Compromise / Fast Beaconing to DGA

▪ Compromise / High Volume of Connections with Beacon Score

▪ Compromise / DGA Beacon

▪ Compromise / Slow Beaconing Activity To External Rare

▪ Compromise / Agent Beacon (Long Period)

▪ Compromise / Agent Beacon (Medium Period)

▪ Compromise / Sustained SSL or HTTP Increase

▪ Compromise / Large Number of Suspicious Failed Connections

▪ Compromise / SSL Beaconing to Rare Destination

▪ Compromise / Beacon for 4 Days

▪ Compromise / High Priority Crypto Currency Mining

▪ Compromise / Monero Mining

▪ Device / Long Agent Connection to New Endpoint

▪ Device / New Connections On Suspicious Port

▪ Anomalous Connection / High Volume of Connections to Rare Domain

‍

‍

List of Indicators of Compromise (IoCs)

 
Indicator Description
hf98x4d[.]site C2 Endpoint (Hostname)
sj98xe4[.]xyz C2 Endpoint (Hostname)
citcix6[.]xyz C2 Endpoint (Hostname)
bduwih8[.]pro C2 Endpoint (Hostname)

‍

‍

MITRE ATT&CK Mapping

 
Tactic (ID) Technique
Persistence (T1176) Browser Extensions (T1176.001)
Persistence (T1176) Software Extensions
Command and Control (T1071) Web Protocols (T1071.001)
Command and Control (T1568) Domain Generation Algorithms (T1568.002)
Command and Control (T1071) Application Layer Protocol
Command and Control (T1102) One-Way Communication (T1102.003)
Command and Control (T1571) Non-Standard Port
Command and Control (T1104) Multi-Stage Channels
Command and Control (T1573) Encrypted Channel
Command and Control (T1008) Fallback Channels
Initial Access ICS (T0862) Supply Chain Compromise
Command and Control ICS (T0885) Commonly Used Port
Collection (T1185) Browser Session Hijacking
Impact (T1496) Compute Hijacking (T1496.001)
Impact (T1496) Resource Hijacking
Command and Control (T1071) Publish/Subscribe Protocols (T1071.001)
Lateral Movement (T1210) Exploitation of Remote Services

‍

References:

1.        https://www.microsoft.com/en-us/security/blog/2025/05/21/lumma-stealer-breaking-down-the-delivery-techniques-and-capabilities-of-a-prolific-infostealer/

2.        https://spycloud.com/resource/report/spycloud-annual-identity-exposure-report-2026/

3.        https://www.darktrace.com/blog/why-trust-is-the-new-attack-surface-darktraces-mid-year-threat-update-2026

4.        https://www.darktrace.com/blog/unpacking-clickfix-darktraces-detection-of-a-prolific-social-engineering-tactic

5.        https://abekweng.medium.com/inside-a-blockchain-hosted-malware-campaign-targeting-windows-and-macos-f5bcdeffed66

6.        https://cloud.google.com/blog/topics/threat-intelligence/unc5142-etherhiding-distribute-malware

7.        https://haveibeensquatted.com/blog/from-typosquatting-to-macos-backdoor-clickfix-blockchain-c2

8.        https://www.virustotal.com/gui/domain/hf98x4d.site/community

9.        https://x.com/FABO97662188/status/2074125545026244795

10.  https://www.virustotal.com/gui/url/b0e5c51a411065864119c305fddf218b7c120731f655932cc1c3307ad5b43f94/gti-summary

Continue reading
About the author
Nahisha Nobregas
SOC Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ